
web由http升级为https搭建
nginx实现http访问
   server {

        listen        default_server;

        listen       [::]: default_server;

        server_name  _;

        root         /usr/share/nginx/html;

        # Load configuration files for the default server block.

        include /etc/nginx/default.d/*.conf;

        location / {

          proxy_pass http://10.10.137.5:8080/;

        }

       error_page 404 /404.html;

            location = /40x.html {

        }

        error_page 500 502 503 504 /50x.html;

            location = /50x.html {

        }

    }
nginx.conf
nginx由http升级为https
.创建服务器证书密钥文件 server.key:

openssl genrsa -des3 -out server.key

输入密码,确认密码,自己随便定义,但是要记住,后面会用到。

.创建服务器证书的申请文件 server.csr

openssl req -new -key server.key -out server.csr

输出内容为:

Enter pass phrase for root.key: ← 输入前面创建的密码

Country Name ( letter code) [AU]:CN ← 国家代号,中国输入CN

State or Province Name (full name) [Some-State]:BeiJing ← 省的全名,拼音

Locality Name (eg, city) []:BeiJing ← 市的全名,拼音

Organization Name (eg, company) [Internet Widgits Pty Ltd]:MyCompany Corp. ← 公司英文名

Organizational Unit Name (eg, section) []: ← 可以不输入

Common Name (eg, YOUR name) []: ← 此时不输入

Email Address []:admin@mycompany.com ← 电子邮箱,可随意填

Please enter the following ‘extra’ attributes

to be sent with your certificate request

A challenge password []: ← 可以不输入

An optional company name []: ← 可以不输入

.备份一份服务器密钥文件

cp server.key server.key.org

.去除文件口令

openssl rsa -in server.key.org -out server.key

.生成证书文件server.crt

openssl x509 -req -days  -in server.csr -signkey server.key -out server.crt
生成证书和私钥
[root@hz]# cd /etc/nginx/key

[root@hz]# openssl genrsa -des3 -out server.key

Generating RSA private key,  bit long modulus

..........................................++++++

....................++++++

e is  (0x10001)

Enter pass phrase for server.key:

Verifying - Enter pass phrase for server.key:

[root@hz-ds-itstool--- key]# ls

server.key

[root@hz-ds-itstool--- key]# openssl req -new -key server.key -out server.csr

Enter pass phrase for server.key:

You are about to be asked to enter information that will be incorporated

into your certificate request.

What you are about to enter is what is called a Distinguished Name or a DN.

There are quite a few fields but you can leave some blank

For some fields there will be a default value,

If you enter '.', the field will be left blank.

-----

Country Name ( letter code) [XX]:CN

State or Province Name (full name) []:beijing

Locality Name (eg, city) [Default City]:beijing

Organization Name (eg, company) [Default Company Ltd]:beijing

Organizational Unit Name (eg, section) []:

Common Name (eg, your name or your server's hostname) []:

Email Address []:

Please enter the following 'extra' attributes

to be sent with your certificate request

A challenge password []:

An optional company name []:

[root@hz-ds-itstool--- key]# cp server.key server.key.org

[root@hz-ds-itstool--- key]# openssl rsa -in server.key.org -out server.key

Enter pass phrase for server.key.org:

writing RSA key

[root@hz-ds-itstool--- key]# openssl x509 -req -days  -in server.csr -signkey server.key -out server.crt

Signature ok

subject=/C=CN/ST=beijing/L=beijing/O=beijing

Getting Private key

[root@hz-ds-itstool--- key]# ls

server.crt  server.csr  server.key  server.key.org
实例生成配置
# For more information on configuration, see:

#   * Official English Documentation: http://nginx.org/en/docs/

#   * Official Russian Documentation: http://nginx.org/ru/docs/

user nginx;

worker_processes auto;

error_log /var/log/nginx/error.log;

pid /run/nginx.pid;

# Load dynamic modules. See /usr/share/nginx/README.dynamic.

include /usr/share/nginx/modules/*.conf;

events {

    worker_connections 1024;

}

http {

    log_format  main  '$remote_addr - $remote_user [$time_local] "$request" '

                      '$status $body_bytes_sent "$http_referer" '

                      '"$http_user_agent" "$http_x_forwarded_for"';

    access_log  /var/log/nginx/access.log  main;

    sendfile            on;

    tcp_nopush          on;

    tcp_nodelay         on;

    keepalive_timeout   65;

    types_hash_max_size 2048;

    include             /etc/nginx/mime.types;

    default_type        application/octet-stream;

    # Load modular configuration files from the /etc/nginx/conf.d directory.

    # See http://nginx.org/en/docs/ngx_core_module.html#include

    # for more information.

    include /etc/nginx/conf.d/*.conf;

    server {

        listen       80 default_server;

        listen       [::]:80 default_server;

        server_name  _;

        root         /usr/share/nginx/html;

        # Load configuration files for the default server block.

        include /etc/nginx/default.d/*.conf;

        location / {

          proxy_pass http://10.199.137.5:8095/;

        }

        error_page 404 /404.html;

            location = /40x.html {

        }

        error_page 500 502 503 504 /50x.html;

            location = /50x.html {

        }

    }

# Settings for a TLS enabled server.

#

server {

  listen 443;  # https默认使用443端口

  server_name 10.199.137.5;  # 将0.0.0.0替换为你的网站域名或ip

  ssl on;

  ssl_certificate /etc/nginx/key/server.crt;

  ssl_certificate_key /etc/nginx/key/server.key;

  ssl_session_timeout 5m;

  ssl_protocols SSLv2 SSLv3 TLSv1;

  ssl_ciphers ALL:!ADH:!EXPORT56:RC4+RSA:+HIGH:+MEDIUM:+LOW:+SSLv2:+EXP;

  ssl_prefer_server_ciphers on;

  location / {

       proxy_pass http://10.199.137.5:8095/;

   }

 }

}
实例nginx.conf
http和https共存访问
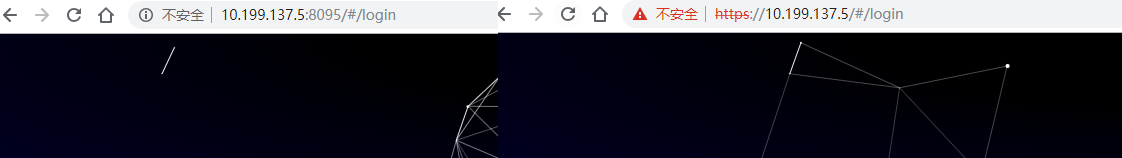
强制https访问
server {

        listen ;

        server_name localhost_tp.com;//注意改为自己的域名

        rewrite ^(.*)$  https://$host$1 permanent;

}
配置项
# For more information on configuration, see:

#   * Official English Documentation: http://nginx.org/en/docs/

#   * Official Russian Documentation: http://nginx.org/ru/docs/

user nginx;

worker_processes auto;

error_log /var/log/nginx/error.log;

pid /run/nginx.pid;

# Load dynamic modules. See /usr/share/nginx/README.dynamic.

include /usr/share/nginx/modules/*.conf;

events {

    worker_connections 1024;

}

http {

    log_format  main  '$remote_addr - $remote_user [$time_local] "$request" '

                      '$status $body_bytes_sent "$http_referer" '

                      '"$http_user_agent" "$http_x_forwarded_for"';

    access_log  /var/log/nginx/access.log  main;

    sendfile            on;

    tcp_nopush          on;

    tcp_nodelay         on;

    keepalive_timeout   65;

    types_hash_max_size 2048;

    include             /etc/nginx/mime.types;

    default_type        application/octet-stream;

    # Load modular configuration files from the /etc/nginx/conf.d directory.

    # See http://nginx.org/en/docs/ngx_core_module.html#include

    # for more information.

    include /etc/nginx/conf.d/*.conf;

    server {

        listen       80 default_server;

        listen       [::]:80 default_server;

        server_name  10.199.137.5;

        rewrite ^(.*)$  https://$host$1 permanent;

        # Load configuration files for the default server block.

        include /etc/nginx/default.d/*.conf;

        location / {

          proxy_pass http://10.199.137.5:8095/;

        }

        error_page 404 /404.html;

            location = /40x.html {

        }

        error_page 500 502 503 504 /50x.html;

            location = /50x.html {

        }

    }

# Settings for a TLS enabled server.

#

server {

  listen 443 ssl;   # https默认使用443端口

  server_name 10.199.137.5;  # 将0.0.0.0替换为你的网站域名或ip

  ssl_certificate /etc/nginx/key/server.crt;

  ssl_certificate_key /etc/nginx/key/server.key;

  ssl_session_timeout 5m;

  ssl_protocols SSLv2 SSLv3 TLSv1;

  ssl_ciphers ALL:!ADH:!EXPORT56:RC4+RSA:+HIGH:+MEDIUM:+LOW:+SSLv2:+EXP;

  ssl_prefer_server_ciphers on;

  location / {

       proxy_pass http://10.199.137.5:8095/;

  }

 }

}
nginx.conf
配置后输入http地址后自动跳转到https访问地址
web由http升级为https搭建的更多相关文章
- Go语言及Web框架Beego环境无脑搭建
[原]Go语言及Web框架Beego环境无脑搭建 本文涉及软件均以截至到2013年10月12日的最新版本为准 1. 相关软件准备: 1) go1.2rc1.windows-386.msi,对应32位w ...
- 从 http 升级到 https 过程中遇到的一些问题
Apple 2017年1月1号起要求Appstore 上线的应用都必须使用 https 加密请求协议,在二月份又改为建议 从 http 升级为 https 协议,此为背景. 公司做的APP同时在App ...
- 网站通信协议升级到HTTPS&HTTP2
为何要升级到HTTPS和HTTP2? http://baijiahao.baidu.com/s?id=1602041305989767011&wfr=spider&for=pc htt ...
- Http升级到Https (本地测试,无须域名和认证)
在之前的语音识别的项目中,一切都在本地进行得很顺利,然后把写的Demo部署到服务器上给老大看的时候,通过IP访问(http://192.168.145.170:8080这样的形式)时,从一开始就坏掉了 ...
- Nginx http升级到https
http和https的区别是 有的网站,http打开的时候,页面提示不安全,比如你点击下面的网站 [其实是同一个网站] http://www.511easy.com/bug/login http:// ...
- office web apps安装部署,配置https,负载均衡(七)配置过程中遇到的问题详细解答
该篇文章,是这个系列文章的最后一篇文章,该篇文章将详细解答owa在安装过程中常见的问题. 如果您没有搭建好office web apps,您可以查看前面的一系列文章,查看具体步骤: office we ...
- nodejs从http升级到https(阿里云证书的使用)
升级原因 1.各大搜索引擎中,https的网页的权重比一般的http的网页权重要高. 2.从用户体验的角度,一个老是被浏览器提醒该网页不可信的网页,总不会让用户感到安心 所以将网站从http升级为ht ...
- 全站从http升级到https(WordPress博客)
最近几年HTTPS取代HTTP已经成为大趋势,HTTP是超文本传输协议,信息是明文传输的,而HTTPS是安全超文本传输协议,需要证书和提供安全连接,换句话说,HTTPS是嵌套了SSL加密的HTTP连接 ...
- 基于RHCS的web双机热备集群搭建
基于RHCS的web双机热备集群搭建 RHCS集群执行原理及功能介绍 1. 分布式集群管理器(CMAN) Cluster Manager.简称CMAN.是一个分布式集群管理工具.它执行在集群的各个节 ...
随机推荐
- 用ant.design的设计注意点---表单
设计的时候,输入表单项 最好放在一起,不要散落在页面各处,会导致表单项穿插存储数据,穿插验证表单,表单的样式设计要严格按照ant的版来,因为表单是交互最多最容易出错的地方,否则浪费太多工作量 持续集成 ...
- xshell跳转设置 Xshell代理设置
本机------->A(中转)------>B(目标服务器) 本机---------XXXXX------>B(目标服务器) 本机无法直接连接B服务器 第一步:本机连接中转服务器A, ...
- python3 mqtt 添加用户名以及密码
import paho.mqtt.client as mqtt client = mqtt.Client(client_id, transport='tcp') client.username_pw_ ...
- makefile小计
1. makefile格式如下,想要生成code.o,就要指定它依赖哪些东西.比如这里是依赖code.cpp这个文件 然后如何生成,换行+tab(与python类似,通过tab区分下面的是生成的命令) ...
- Unix/Linux小计
1. centos查看cpu信息 cat /proc/cpuinfo processor有几个就是有几个cpu,每一列是每个cpu的信息 每个processor中的cores是当前cpu中有几个核心. ...
- jenkins pipeline使用方式
pipeline 使用 使用groovy的一种DSL语言,流程控制 pipeline脚本同其他脚本语言一样,从上到下顺序执行,它的流程控制取决于Groovy表达式,为jenkins用户提供了更巨大的灵 ...
- 《Linux就该这么学》自学笔记_ch22_使用openstack部署云计算服务环境
<Linux就该这么学>自学笔记_ch22_使用openstackb部署云计算服务环境 文章主要内容: 了解云计算 Openstack项目 服务模块组件详解 安装Openstack软件 使 ...
- C语言学习系列笔记
1.小甲鱼 C语言教程系列
- 从有序矩阵M x N中找出是否包含某一个数,要求时间复杂度为O(M+N)
有序指的是每行从左到右依次变大,每列从上到下依次变大 思路: 从右上顶点开始依次判断当前值与给定值的大小,往左下顶点移动,结束条件是下标超过范围 public class FindNumInOrder ...
- 【C语言】获得数组长度
c语言中,定义数组后可以用sizeof命令获取数组的长度(可容纳元素个数): 如: { int data[5]; int length; length=sizeof(data)/sizeof(data ...