
Django(62)自定义认证类
前言
如果我们不用使用drf那套认证规则,我们想自定义认证类,那么我们首先要知道,drf本身是如何定义认证规则的,也就是要查看它的源码是如何写的
源码分析
源码的入口在APIView.py文件下的dispatch方法下的self.initial方法中的self.perform_authentication(request),点击查看后如下
  def perform_authentication(self, request):

      """

        Perform authentication on the incoming request.

        Note that if you override this and simply 'pass', then authentication

        will instead be performed lazily, the first time either

        `request.user` or `request.auth` is accessed.

      """

      request.user
返回了一个request的user方法,request代表的是drf的Request,所以我们进入drf的Request类中查找user方法属性,源码如下:
    def user(self):

        """

        Returns the user associated with the current request, as authenticated

        by the authentication classes provided to the request.

        """

        if not hasattr(self, '_user'):

            with wrap_attributeerrors():

                self._authenticate()

        return self._user
上述代码的意思是:返回与当前请求关联的用户,由提供给请求的身份验证类进行身份验证。如果没有用户,我们需要通过_authenticate方法验证,我们查看下它的源码
def _authenticate(self):

    """

    尝试依次使用每个身份验证实例对请求进行身份验证。

    """

    for authenticator in self.authenticators:

        try:

            user_auth_tuple = authenticator.authenticate(self)

        except exceptions.APIException:

            self._not_authenticated()

            raise

        if user_auth_tuple is not None:

            self._authenticator = authenticator

            self.user, self.auth = user_auth_tuple

            return

    self._not_authenticated()
我们可以看到self.authenticators验证器其实是调用父类APIView的authenticators,APIView的authenticators在源码initialize_request方法下的get_authenticators,我们查看源码
def get_authenticators(self):

    """

    Instantiates and returns the list of authenticators that this view can use.

    """

    return [auth() for auth in self.authentication_classes]
再点击authentication_classes查看
authentication_classes = api_settings.DEFAULT_AUTHENTICATION_CLASSES
我们就知道了drf默认的认证器在settings文件下的DEFAULT_AUTHENTICATION_CLASSES类下面
'DEFAULT_AUTHENTICATION_CLASSES': [

        'rest_framework.authentication.SessionAuthentication',

        'rest_framework.authentication.BasicAuthentication'

    ],
我们发现drf默认有2个认证类一个基础的认证,另一个session认证,这两个认证类都继承自BaseAuthentication,我们来看下源码
class BaseAuthentication:

    """

    所有的认证类都继承自BaseAuthentication.

    """

    def authenticate(self, request):

        """

         认证请求返回一个二元组(user, token),并且此方法必须重写,否则抛出异常

        """

        raise NotImplementedError(".authenticate() must be overridden.")

    def authenticate_header(self, request):

        """

        Return a string to be used as the value of the `WWW-Authenticate`

        header in a `401 Unauthenticated` response, or `None` if the

        authentication scheme should return `403 Permission Denied` responses.

        """

        pass
接下来我们看下BasicAuthentication如何写的,后续我们依葫芦画瓢
class BasicAuthentication(BaseAuthentication):

    """

    针对用户名密码的 HTTP 基本身份验证

    """

    www_authenticate_realm = 'api'

    def authenticate(self, request):

        """

        如果使用 HTTP 基本身份验证提供了正确的用户名和密码,则返回“User”。否则返回“None”。

        """

        # 获取请求头中`HTTP_AUTHORIZATION`,并进行分割

        auth = get_authorization_header(request).split()

        # 如果没有auth或者auth的第一个索引值的小写不等于basic,则返回None

        if not auth or auth[0].lower() != b'basic':

            return None

        # auth列表的长度必须等于2,格式['basic', 'abc.xyz.123']

        # 如果auth的长度等于1,则抛出异常

        if len(auth) == 1:

            msg = _('Invalid basic header. No credentials provided.')

            raise exceptions.AuthenticationFailed(msg)

        # 如果长度大于2,也抛出异常

        elif len(auth) > 2:

            msg = _('Invalid basic header. Credentials string should not contain spaces.')

            raise exceptions.AuthenticationFailed(msg)

        try:

            try:

                # auth[1]解码格式为utf-8

                auth_decoded = base64.b64decode(auth[1]).decode('utf-8')

            except UnicodeDecodeError:

                auth_decoded = base64.b64decode(auth[1]).decode('latin-1')

            auth_parts = auth_decoded.partition(':')

        except (TypeError, UnicodeDecodeError, binascii.Error):

            msg = _('Invalid basic header. Credentials not correctly base64 encoded.')

            raise exceptions.AuthenticationFailed(msg)

        userid, password = auth_parts[0], auth_parts[2]

        return self.authenticate_credentials(userid, password, request)

    def authenticate_credentials(self, userid, password, request=None):

        """

        Authenticate the userid and password against username and password

        with optional request for context.

        """

        credentials = {

            get_user_model().USERNAME_FIELD: userid,

            'password': password

        }

        user = authenticate(request=request, **credentials)

        if user is None:

            raise exceptions.AuthenticationFailed(_('Invalid username/password.'))

        if not user.is_active:

            raise exceptions.AuthenticationFailed(_('User inactive or deleted.'))

        return (user, None)

    def authenticate_header(self, request):

        return 'Basic realm="%s"' % self.www_authenticate_realm
自定义认证类
- 创建继承BaseAuthentication的认证类
- 实现authenticate方法
- 实现体根据认证规则 确定 游客 正常用户 非法用户
- 进行全局或局部配置(一般采用全局配置)
认证规则
- 没有认证信息,返回
None(游客) - 有认证信息认证失败,抛异常(非法用户)
- 有认证信息认证成功,返回用户和认证信息的元组(合法用户)
我们创建一个文件夹authentications,写入如下代码
from rest_framework.authentication import BaseAuthentication

from rest_framework.exceptions import AuthenticationFailed

from api.models import User

class MyAuthentications(BaseAuthentication):

    def authenticate(self, request):

        # 前台在请求头携带认证信息

        # 且默认规范用Authorization字段携带认证信息

        # 后台固定在请求对象的META字段中的HTTP_AUTHORIZATION获取

        auth = request.META.get('HTTP_AUTHORIZATION', None)

        # 处理游客

        if auth is None:

            return None

        auth_list = auth.split()

        if not len(auth_list) == 2 and auth_list[0].lower() == "auth":

            raise AuthenticationFailed("认证信息有误,非法用户")

        # 合法的用户还需要从auth_list[1]中解析出来

        # 注:假设一种情况,信息为xx.yy.zz,就可以解析出admin用户:实际开发,该逻辑一定是校验用户的正常逻辑

        if auth_list[1] != 'xx.yy.zz':  # 校验失败

            raise AuthenticationFailed("用户校验失败,非法用户")

        user = User.objects.filter(username='jkc').first()

        print(user)

        if not user:

            raise AuthenticationFailed("用户数据有误,非法用户")

        return user, None
然后在settings.py中配置全局的自定义认证类
REST_FRAMEWORK = {

    'DEFAULT_AUTHENTICATION_CLASSES': [

        'api.authentications.MyAuthentications'

    ],

}
最后写入视图函数
class TestView(APIView):

    def get(self, request, *args, **kwargs):

        return APIResponse(data_msg="drf get ok")
然后我们访问视图,在headers中不传Authorization 代表游客,游客可以访问成功
{

    "statusCode": 0,

    "message": "drf get ok"

}
接着我们在请求头中只传auth
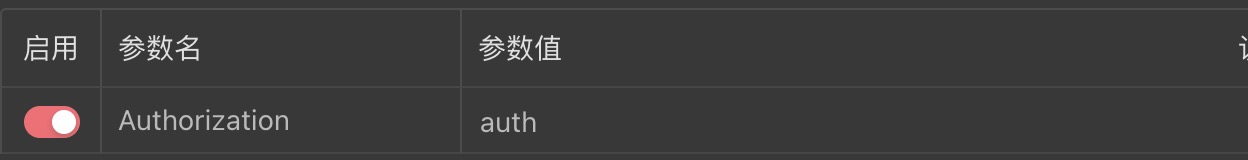
访问视图会抛出异常信息
{

    "detail": "认证信息有误,非法用户"

}
然后我们在请求头中传入错误的认证,auth 111
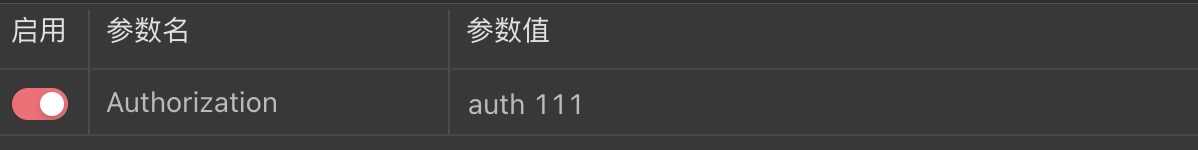
访问视图会抛出异常信息
{

    "detail": "用户校验失败,非法用户"

}
最后我们在请求头中传入正确的认证,auth xx.yy.zz,这次会得到正确的返回结果
{

    "statusCode": 0,

    "message": "drf get ok"

}
以上的测试,就代表我们自定义的认证类起作用了
Django(62)自定义认证类的更多相关文章
- DRF JWT的用法 & Django的自定义认证类 & DRF 缓存
JWT 相关信息可参考: https://www.jianshu.com/p/576dbf44b2ae DRF JWT 的使用方法: 1. 安装 DRF JWT # pip install djang ...
- 自定义user表签发token、自定义认证类、simpleui模块使用
今日内容概要 自定义User表,签发token 自定义认证类 simpleui的使用 多方式登陆接口(后面也写 内容详细 1.自定义User表,签发token # 如果项目中的User表使用auth的 ...
- [py][mx]django自定义认证类-实现邮箱作为用户名登录
创建自定义验证用户名密码类CustomBackend users/views.py from django.contrib.auth import authenticate, login from d ...
- django 实现自定义认证
1.Django自带用户认证系统 Django自带用户认证系统,这个系统支持访问控制.注册用户.关联创建者和内容等:在开发用户认证功能时的时候,可以使用Django自带用户认证系统实现: A.相关表 ...
- The Django Book(自定义ModelAdmi类)
默认的,管理界面下显示的东西只是 python2:def __unicode__(self): 和 python3:def __str__(self): 中返回的字段内容 想要让它更加的多元化的话 c ...
- Django:RestFramework之-------认证
3 restframework-认证 3.1APIView 认证: 认证是否已经登陆,如果已经登陆返回元组,如果没有登陆报错 源码流程: 执行dispatch方法: def dispatch(self ...
- Django REST framework —— 认证组件源码分析
我在前面的博客里已经讲过了,我们一般编写API的时候用的方式 class CoursesView(ViewSetMixin,APIView): pass 这种方式的有点是,灵活性比较大,可以根据自己的 ...
- drf三大认证:认证组件-权限组件-权限六表-自定义认证组件的使用
三大认证工作原理简介 认证.权限.频率 源码分析: from rest_framework.views import APIView 源码分析入口: 内部的三大认证方法封装: 三大组件的原理分析: 权 ...
- DRF认证、自定义认证和权限、自定义权限
源码分析 """ 1)APIView的dispath(self, request, *args, **kwargs) 2)dispath方法内 self.initial( ...
随机推荐
- JQuery跨站脚本漏洞
原理: jQuery中过滤用户输入数据所使用的正则表达式存在缺陷,可能导致 location.hash 跨站漏洞 影响版本: jquery-1.7.1~1.8.3 jquery-1.6.min.js, ...
- 学习Canvas绘图与动画基础 制作弧和圆(五)
1 <!DOCTYPE html> 2 <html> 3 <head lang="en"> 4 <meta charset="U ...
- jQuery数组($.grep,$.each,$.inArray,$.map)处理函数详解
1.jQuery.grep( array, function(elementOfArray, indexInArray) [, invert ] ) 描述: 查找满足过滤函数的数组元素.原始数组不受影 ...
- LeetCode---11. 盛最多水的容器(Java)
11. 盛最多水的容器 题目地址:https://leetcode-cn.com/problems/container-with-most-water/ 给你 n 个非负整数 a1,a2,...,an ...
- 【js】Leetcode每日一题-解码异或后数组
[js]Leetcode每日一题-解码异或后数组 [题目描述] 未知 整数数组 arr 由 n 个非负整数组成. 经编码后变为长度为 n - 1 的另一个整数数组 encoded ,其中 encode ...
- Vulnerability: Cross Site Request Forgery (CSRF)
CSRF跨站请求伪造 这是一种网络攻击方式,也被称为one-click attack或者session riding 攻击原理 CSRF攻击利用网站对于用户网页浏览器的信任,挟持用户当前已登陆的Web ...
- JavaWeb——反射、注解
单元测试.反射.注解 1. Junit单元测试 2. 反射 3. 注解 Junit单元测试: * 测试分类: 1. 黑盒测试:不需要写代码,给输入值,看程序是否能够输出期望的值. 2. 白盒测试:需要 ...
- GDI编程基础
窗口和视口 视口是基于设备的采用的是设备坐标(单位:像素),窗口是基于程序的采用的是逻辑坐标(单位:像素/毫米/厘米等). 在默认的映射模式下,视口是与窗口等同的.但是如果改变其映射模式,则其对应的单 ...
- Govern Service 基于 Redis 的服务治理平台
Govern Service 基于 Redis 的服务治理平台(服务注册/发现 & 配置中心) Govern Service 是一个轻量级.低成本的服务注册.服务发现. 配置服务 SDK,通过 ...
- CRM帮助B2B企业持续改善战略决策「下篇」
尽管数据早已深入人心,但依然有相当比率的B2B企业在管理和战略决策时依赖直觉而不是客户数据.不停变化的B2B市场表明了以客户为中心的趋向和格局,CRM客户管理系统能够协助您更好的使用客户数据并最大限度 ...