
NSSCTF Round#17 Basic CRYPTO
Level_1
题目
Level_1.py(我把参数整理了一下,看着舒服)
#真签到题

from Crypto.Util.number import bytes_to_long, getPrime

from secret import getflag

p = getPrime(1024)

q = getPrime(1024)

n = p * q

m = bytes_to_long(getflag().encode())

c1 = pow(m, p, n)

c2 = pow(m, q, n)

print(n)

print(c1)

print(c2)

print(p)

print(q)

# n = 22517647586235353449147432825948355885962082318127038138351524894369583539246623545565501496312996556897362735789505076324197072008392656511657262430676945685471397862981216472634785622155317188784494912316440866051402627470561626691472280850273482836308002341429493460677206562201947000047718275995355772707947408688836667011206588727438261189233517003341094758634490421007907582147392858070623641389171229435187248184443645883661560636995548332475573072064240073037558031928639832259001407585962782698021735648128101459118863015844905452823095147248865104102562991382119836061161756978764495337874807458182581421229

# c1 = 1432393096266401187029059077791766305797845826173887492889260179348416733820890797101745501984437201566364579129066414005659742104885321270122634155922766503333859812540068278962999824043206496595825886026095484801291802992082454776271149083516187121160475839108002133113254134626407840182541809478892306748590016896975053434021666376203540725254480252049443975835307793528287818262102688334515632062552114342619781840154202525919769192765621085008206581226486157149883898548933475155236509073675387541466324512294079413938239828341890576923100769181401944289365386552139418728492565319685207500539721582552448971814

# c2 = 13299679392897297864252207869444022461237574801991239380909482153705185317634241850084078027230394830079554676426505967970943836811048777462696506309466535820372917756458083553031417406403895116557560548183674144457502601887632495739472178857537011190162283185735114683172731936834993707871636782206418680404006299140864001776588991141011500807549645227520128216130966268810165946959810884593793452437010902774726405217517557763322690215690606067996057037379898630878638483268362526985225092000670251641184960698506349245915816808028210142606700394584541282682338561482561343076218115042099753144875658666459825545602

# p = 155861690390761931560700906834977917646203451142415617638229284868013723431003139974975998354830978765979365632120896717380895021936387027045347260400512396388028781862427862974453223157509702913026222541667006325100878113871620322023188372501930117363623076837619478555007555970810681502521309925774889678793

# q = 144471983652821947847253052623701746810204736865723159569786739658583884214397562204788127484897909964898113250509653721265240138487697822089282456150238116811225975640330930854549232972314642221382625614304415750165289831040623741828600283778523993251940904896081111235859249916040849697146542311990869696453
secret.py
def getflag():

    return 'NSSCTF{Y0u_want_what!!!}'
我的解答:
签到题,真的是签到嘿嘿嘿,看很多师傅用的共模攻击,其实也不用,都是对同一旗帜进行的加密,我们用一组即可。
比如我们看第一组,这里的加密指数e其实就是p,我们可知p,q,n,e,c都已知,直接梭即可
exp:
import gmpy2

from Crypto.Util.number import *

p = 155861690390761931560700906834977917646203451142415617638229284868013723431003139974975998354830978765979365632120896717380895021936387027045347260400512396388028781862427862974453223157509702913026222541667006325100878113871620322023188372501930117363623076837619478555007555970810681502521309925774889678793

q = 144471983652821947847253052623701746810204736865723159569786739658583884214397562204788127484897909964898113250509653721265240138487697822089282456150238116811225975640330930854549232972314642221382625614304415750165289831040623741828600283778523993251940904896081111235859249916040849697146542311990869696453

n = 22517647586235353449147432825948355885962082318127038138351524894369583539246623545565501496312996556897362735789505076324197072008392656511657262430676945685471397862981216472634785622155317188784494912316440866051402627470561626691472280850273482836308002341429493460677206562201947000047718275995355772707947408688836667011206588727438261189233517003341094758634490421007907582147392858070623641389171229435187248184443645883661560636995548332475573072064240073037558031928639832259001407585962782698021735648128101459118863015844905452823095147248865104102562991382119836061161756978764495337874807458182581421229

c1 = 1432393096266401187029059077791766305797845826173887492889260179348416733820890797101745501984437201566364579129066414005659742104885321270122634155922766503333859812540068278962999824043206496595825886026095484801291802992082454776271149083516187121160475839108002133113254134626407840182541809478892306748590016896975053434021666376203540725254480252049443975835307793528287818262102688334515632062552114342619781840154202525919769192765621085008206581226486157149883898548933475155236509073675387541466324512294079413938239828341890576923100769181401944289365386552139418728492565319685207500539721582552448971814

phi = (p-1)*(q-1)

d = gmpy2.invert(p,phi)

m = pow(c1,d,n)

print(long_to_bytes(m))

#NSSCTF{Y0u_Hav3_S01v3d_Crypt0_Leve1_i}
Level_2
题目
hint:e is a common eLevel_2.py
# 猜猜我是谁 猜对了直接秒出flag喔

from Crypto.Util.number import bytes_to_long, getPrime

from secret import getflag

p = ***

q = getPrime(1024)

e = you guess!

n = p * q

m = bytes_to_long(getflag().encode())

c=pow(m, e, n)

print(q)

print(c)

#p=one of ps

#q=145721736470529261146573065574028992352505611489859183763269215489708531333597694809923949026781460438320576519639268582565188719134157402292313959218961804213310847081787824780075530751842057663327444602428455144829447776271394663729996984613471623158126083062443634493708467568220146024273763894704649472957

#c=17441814714407189483380175736850663249578989775568187792928771544069162420510939242665830363276698262009780462912108642025299275146709817979705069095332726251759039923303627023610865046363171692163473939115438686877494878334016463787558794121885354719336139401336137097548305393030069499625065664884238710759260231321106291200849044147840392021931720902340003746946851806025722944795391356835342258387797980787437188976704677008092850181043891802072500430200735973581081228711070923822341261809453662427341958883142789220800541626034573952425948295446202775198692920613709157662831071515700549093766182579873408465779

#flag=NSSCTF{*}
secret.py
def getflag():

    return 'NSSCTF{You_Open_Me_Again!!!}'
ps.txt(内容太多这里就不写完了)
112570061288378069698095973797005529770680093845875223894997231628336829949265892727685350018077594566290824268610648959971872907584202027357045022857069974808762471714819971890294050173438079696242727451386551493649076611880968665058995978923502888694810161303133554247010154982747490401927615698764244575641

160390345706816858928712766237430683880617356868344036698358703998333407749759520169301916333739046480408394559790599973541103169787850665278836627642898619297749297488964496319606975452596625244508217477776522963045377479261162883238162733599875452839053545655376526116053288991549884653357989658618517105739

135274466561036154078983088599958139019086085585949467588985205105812446898435696006770477951085211474194015652753723608465972758093765295013977480077536663462359246172027648236195047543583386559597971108147534622182729246605513241519170365324169846986609310875122877897274699603690766660965072311242257844683

138911436184035411312080317190170788684424368688033129106939678172112294080712687220545748826015533434613777107494802659423833111286512824438806541791135385865106570037291005668611521376293259246116906155604890821875736413366752183442187739338638604045391231977875571324580145808190681511754014953150411573749

109003763690498543195236746159436380771897695450387210983374093441017415764628099371078873895655589281703285655726042956360681700927592983338522453278912601255567126713963945252430830834993483396585689829542246058662932613423243445885667303835965706012503101194446739723698993285990913911596033955033953763147

.......
我的解答:
签到升级版,还是签到。。根据提示可知e=65537
还说了p是ps.txt文件内容里的其中一个,q,c,e已知,我们只需要遍历p就可以了。
exp1:
from Crypto.Util.number import *

import gmpy2

# 从文件中读取可能的p值

with open("ps.txt", "r") as file:

    p_values = file.readlines()

# 遍历每个 p 值

for p_str in p_values:

    p = int(p_str.strip()) #记得转换类型

    q = 145721736470529261146573065574028992352505611489859183763269215489708531333597694809923949026781460438320576519639268582565188719134157402292313959218961804213310847081787824780075530751842057663327444602428455144829447776271394663729996984613471623158126083062443634493708467568220146024273763894704649472957

    c = 17441814714407189483380175736850663249578989775568187792928771544069162420510939242665830363276698262009780462912108642025299275146709817979705069095332726251759039923303627023610865046363171692163473939115438686877494878334016463787558794121885354719336139401336137097548305393030069499625065664884238710759260231321106291200849044147840392021931720902340003746946851806025722944795391356835342258387797980787437188976704677008092850181043891802072500430200735973581081228711070923822341261809453662427341958883142789220800541626034573952425948295446202775198692920613709157662831071515700549093766182579873408465779

    n = p * q

    e = 65537

    phi = (p - 1) * (q - 1)

    d = gmpy2.invert(e,phi)

    m = pow(c, d, n)

    flag = long_to_bytes(m).decode('latin1')

    if "NSS" in flag:

        print(flag)

#NSSCTF{Y0u_g0t_1t!!!}
当然还有一种方法,反正是猜嘛那就猜测flag不太长,直接在模q下解即可
exp2:
import gmpy2

from Crypto.Util.number import *

q=145721736470529261146573065574028992352505611489859183763269215489708531333597694809923949026781460438320576519639268582565188719134157402292313959218961804213310847081787824780075530751842057663327444602428455144829447776271394663729996984613471623158126083062443634493708467568220146024273763894704649472957

c= 17441814714407189483380175736850663249578989775568187792928771544069162420510939242665830363276698262009780462912108642025299275146709817979705069095332726251759039923303627023610865046363171692163473939115438686877494878334016463787558794121885354719336139401336137097548305393030069499625065664884238710759260231321106291200849044147840392021931720902340003746946851806025722944795391356835342258387797980787437188976704677008092850181043891802072500430200735973581081228711070923822341261809453662427341958883142789220800541626034573952425948295446202775198692920613709157662831071515700549093766182579873408465779

e = 65537

d = gmpy2.invert(e, q-1)

m = pow(c, d, q)

print(long_to_bytes(m))

#NSSCTF{Y0u_g0t_1t!!!}
Level_3
题目
自动化RSA?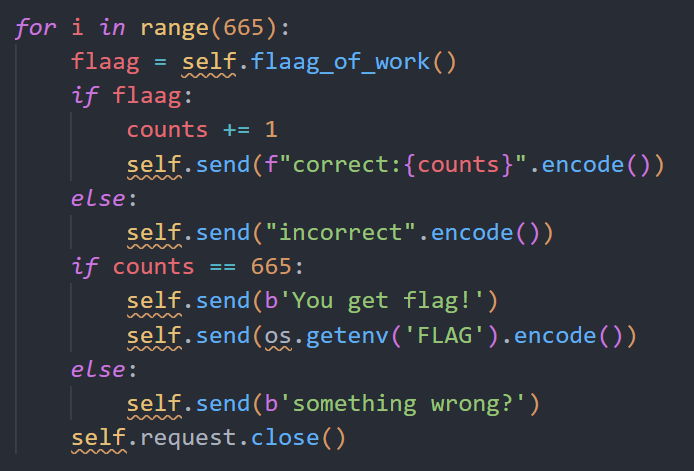
我的解答:
题目给了一张图片,发现要拿到flag要进行665次
先连接靶机看看是啥情况。
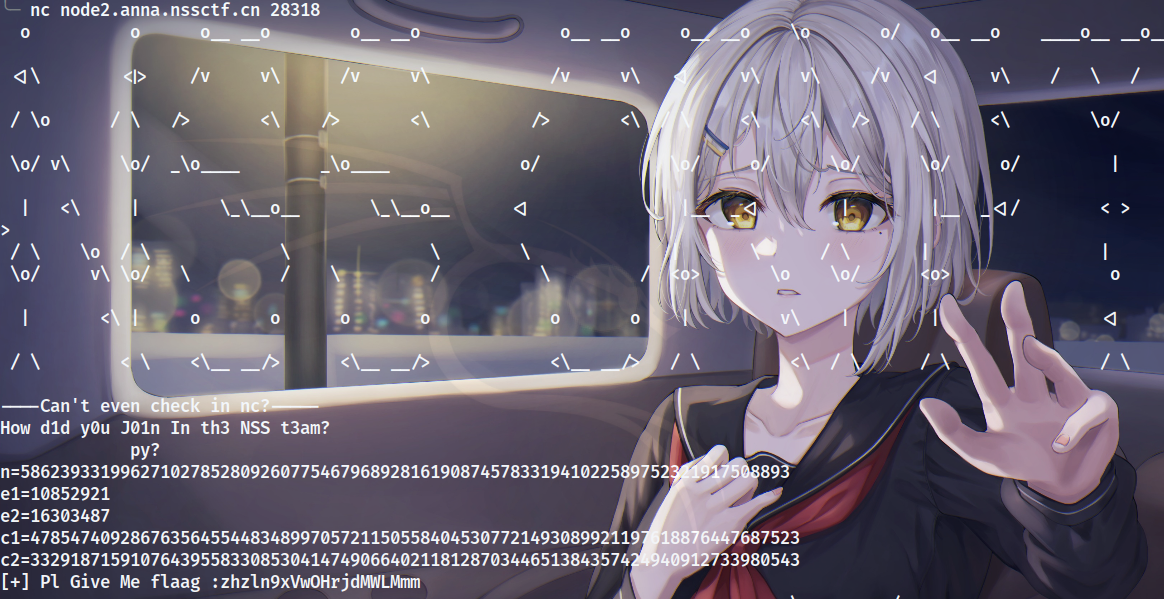
试了一下是共模攻击(共n),也就是说本题是一个共模攻击交互题。那就好办了,写交互就行了。
exp:
from Crypto.Util.number import *

import gmpy2

from pwn import *

from tqdm import *

def decode(n,e1,e2,c1,c2):

    t = gmpy2.gcd(e1,e2)

    if t == 1:

        s,x,y = gmpy2.gcdext(e1,e2)

        m = (pow(c1,x,n)*pow(c2,y,n))%n

        flag = long_to_bytes(m)

        return flag

    else:

        s,x,y = gmpy2.gcdext(e1,e2)

        k = 0

        while 1:

            m = gmpy2.iroot((pow(c1,x,n)*pow(c2,y,n)+k*n)%n,t)

            if m[1]:

                print(long_to_bytes(m[0]))

                break

            else:

                k += 1

sh = remote("IP",端口号)

#这里需要666次,试了试665次打不出来

for i in trange(666):

    data = sh.recvuntil(b" y0u J01n In th3 NSS t3am?\n             py?\n")

    n = eval(sh.recvline().decode().strip().split("=")[-1])

    e1 = eval(sh.recvline().decode().strip().split("=")[-1])

    e2 = eval(sh.recvline().decode().strip().split("=")[-1])

    c1 = eval(sh.recvline().decode().strip().split("=")[-1])

    c2 = eval(sh.recvline().decode().strip().split("=")[-1])

    flag = decode(n,e1,e2,c1,c2)

    sh.sendlineafter(b"[+] Pl Give Me flaag :",flag)

sh.interactive()
NSSCTF Round#17 Basic CRYPTO的更多相关文章
- CH Round #17 舞动的夜晚
舞动的夜晚 CH Round #17 描述 L公司和H公司举办了一次联谊晚会.晚会上,L公司的N位员工和H公司的M位员工打算进行一场交际舞.在这些领导中,一些L公司的员工和H公司的员工之间是互相认识的 ...
- “玲珑杯”线上赛 Round #17 河南专场
闲来无事呆在寝室打打题,没有想到还有中奖这种操作,超开心的 玲珑杯”线上赛 Round #17 河南专场 Start Time:2017-06-24 12:00:00 End Time:2017-06 ...
- Codeforces Beta Round #17 D. Notepad (数论 + 广义欧拉定理降幂)
Codeforces Beta Round #17 题目链接:点击我打开题目链接 大概题意: 给你 \(b\),\(n\),\(c\). 让你求:\((b)^{n-1}*(b-1)\%c\). \(2 ...
- Educational Codeforces Round 17
Educational Codeforces Round 17 A. k-th divisor 水题,把所有因子找出来排序然后找第\(k\)大 view code //#pragma GCC opti ...
- Codeforces Global Round 17
Codeforces Global Round 17 A. Anti Light's Cell Guessing 坑点:\(n=1,m=1\) 时答案为 \(0\) . 其他情况:当 \(n=1\) ...
- [题解]Codeforces Round #709 (Div. 1, based on Technocup 2021 Final Round) - A. Basic Diplomacy
[题目] A. Basic Diplomacy [描述] Aleksey有n个朋友,有一个m天的假期,每天都需要一个朋友来陪他.给出每天有空的朋友的编号,要求同一个朋友来的天数不能超过m/2上取整.求 ...
- Codeforces Beta Round #17 C. Balance DP
C. Balance 题目链接 http://codeforces.com/contest/17/problem/C 题面 Nick likes strings very much, he likes ...
- Codeforces Beta Round #17 A - Noldbach problem 暴力
A - Noldbach problem 题面链接 http://codeforces.com/contest/17/problem/A 题面 Nick is interested in prime ...
- hdu 5101 Select(Bestcoder Round #17)
Select Time Limit: 4000/2000 MS (Java/Others) ...
- [Educational Round 17][Codeforces 762F. Tree nesting]
题目连接:678F - Lena and Queries 题目大意:给出两个树\(S,T\),问\(S\)中有多少连通子图与\(T\)同构.\(|S|\leq 1000,|T|\leq 12\) 题解 ...
随机推荐
- 广告策划师如何做 AB 测试
更多技术交流.求职机会,欢迎关注字节跳动数据平台微信公众号,回复[1]进入官方交流群 近年来,随着消费者的心理需求逐步趋向于精神层面.科技的迭代迅速以及市场环境的复杂性逐步上升,我国的广告行业逐步展开 ...
- SQL SERVER 查询表结构,导出到Excel 生成代码用
查询所有表 select * from information_schema.tables SQL SERVER 查询表结构,导出到Excel 生成代码用 --快速查看表结构字段(比较全面的) SEL ...
- MyBatis Mapper.XML 标签使用说明
直接将值返回给对象 <select id="list" resultType="com.vipsoft.base.entity.UserInfo"> ...
- gunicorn 高性能wsgi服务器
参考: https://zhuanlan.zhihu.com/p/102716258 Gunicorn是什么 Gunicorn Green Unicorn 是一个 UNIX 下的 WSGI HTTP ...
- 【Django drf】认证类 权限类 频率类 过滤类 排序类 分页类
目录 认证类 前期准备 自定义认证类 配置认证类 全局配置 局部禁用 认证组件使用步骤 基于类中方法的认证(了解) 权限类 前期准备 重写has_permission() 添加权限不足信息 权限组件使 ...
- 0.o?让我看看怎么个事儿之SpringBoot自动配置
学习 SpringBoot 自动配置之前我们需要一些前置知识点: Java注解,看完就会用 学会@ConfigurationProperties月薪过三千 不是银趴~是@Import! @Condit ...
- 获取标准报表CJI3的ALV数据
1.CJI3 运行标准程序CJI3,获取对象和业务货币值,在其他程序中展示 2.代码展示 CJI3对应程序名rkpep003,最终展示的ALV结构可以再程序中找到. 因为本实例只获取其中两个字段的值, ...
- SpringBoot 项目实战 | 瑞吉外卖 优化篇 Day01
该系列将记录一份完整的实战项目的完成过程,该篇属于优化篇第一天,主要负责完成缓存优化问题 案例来自B站黑马程序员Java项目实战<瑞吉外卖>,请结合课程资料阅读以下内容 该篇我们将完成以下 ...
- 2014年第五届蓝桥杯【C++省赛B组】
第一题:啤酒和饮料 啤酒每罐2.3元,饮料每罐1.9元.小明买了若干啤酒和饮料,一共花了82.3元. 我们还知道他买的啤酒比饮料的数量少,请你计算他买了几罐啤酒. 注意:答案是一个整数.请通过浏览器提 ...
- 1 Englishi 词根
1 ab 离去,相反, 不 (负能量的) abnormal abuse 2 anti 反对,相反 antiwar antiaging antiforeign antinoise 3 co-/col ...