
WPA/WPA2四次握手
WPA/WPA2四次握手
官方文档:https://en.wikipedia.org/wiki/IEEE_802.11i-2004
The four-way handshake is designed so that the access point (or authenticator) and wireless client (or supplicant) can independently prove to each other that they know the PSK/PMK, without ever disclosing the key. Instead of disclosing the key, the access point & client each encrypt messages to each other—that can only be decrypted by using the PMK that they already share—and if decryption of the messages was successful, this proves knowledge of the PMK. The four-way handshake is critical for protection of the PMK from malicious access points—for example, an attacker's SSID impersonating a real access point—so that the client never has to tell the access point its PMK.
T The PMK is designed to last the entire session and should be exposed as little as possible; therefore, keys to encrypt the traffic need to be derived. A four-way handshake is used to establish another key called the Pairwise Transient Key (PTK).
WPA/WPA2使用4次握手的方式来产生所需要的密钥。即通过一系列的交互,从PMK(Pairwise Master Key)生成PTK(Pairwise Transient Key)。
PTK(Pairwise Transient Key)简介
PTK包含3个部分,KCK(Key Confirmation Key),KEK(Key Encryption Key),TK(Temporal Key)。
PTK的总长度根据加密方式不同而不同。
当加密方式是TKIP时,PTK长512位,按顺序分别为KCK占128位,KEK占128位,TK占256位。
当加密方式是CCMP时,PTK长384位,按顺序分别为KCK占128位,KEK占128位,TK占128位。
KEK和KCK是给EAPOL-Key,也就是四次握手时,加密和完整性验证用的。TK用于后续的数据加密。
生成PTK,需要5个必要元素,PMK,ANonce(Nonce 1),SNonce(Nonce 2),Authenticate MAC(MAC 1),Supplicant MAC(MAC 2)。如下图:

2个Nonce分别是Authenticator和Supplicant生成的随机数。
这张图里的输出包含4个部分,其实Data Encr和Data MIC合起来就是前面提到的TK。而EAPOL Encr/MIC分别对应前面的KEK和KCK。
PMK 简介(Pairwise Master Key)
密钥的生成是从主密钥开始。在成对密钥体系中,主密钥成为成对主密钥(pairwise master key)。
为了得到临时密钥,必须使用预先定义好的伪随机函数来展开PMK。为了使数据更为随机,此展开过程是根据预主密钥(pre-master key)、申请者与认证者(supplicant and authenticator)的MAC地址以及两个座位四次握手的随机nonce值。
TKIP与CCMP都会使用伪随机函数将256位的PMK展开为成对临时密钥。
PSK简介(pre-shared key)
四次握手的过程
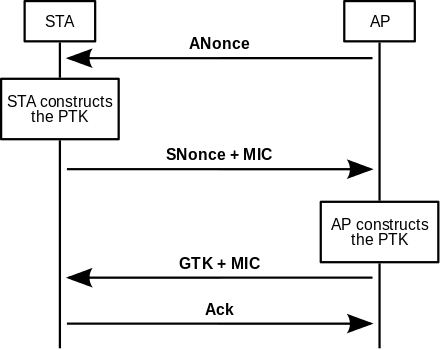
1. The AP sends a nonce-value to the STA (ANonce). The client now has all the attributes to construct the PTK.因为1/4里同时也包含了Authenticator的MAC地址。
2. The STA sends its own nonce-value (SNonce) to the AP together with a MIC, including authentication, which is really a Message Authentication and Integrity Code (MAIC).Supplicant计算出PTK,把SNonce和自己的MAC地址送给Authenticator。同时,从2/4报文开始,后面的每个报文都会有MIC(消息完整性校验)。1/4没有。
3. The AP constructs and sends the GTK and a sequence number together with another MIC. This sequence number will be used in the next multicast or broadcast frame, so that the receiving STA can perform basic replay detection.
4. The STA sends a confirmation to the AP. 仅是对3/4的一个ACK。说明PTK已经装好,后面的数据可以加密了。
WPA的GTK会在4次握手完成以后进行安装,而WPA2的GTK则是在4次握手的过程中就进行了安装;如下图:
wpa四次握手

WPA:2-way handshake (GTK)

wpa2四次握手
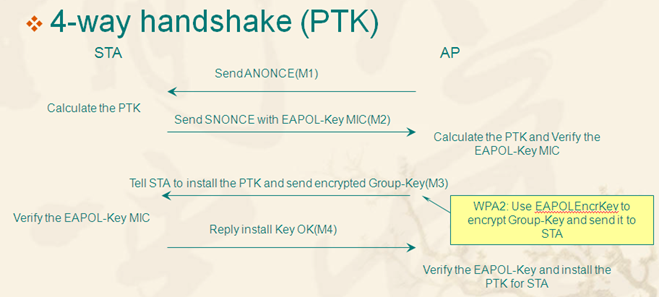
The group key handshake
参考链接:
http://blog.chinaunix.net/uid-20514606-id-2955929.html
WPA/WPA2四次握手的更多相关文章
- 关于WPA/WPA2 4次握手
简单描述一下WPA/WPA2的4次握手中的一些关键词: WPA/WPA2使用4次握手的方式来产生所需要的密钥.四次握手通过一系列的交互,从PMK(Pairwise Master Key)生成PTK(P ...
- 无线网络wifi (WPA/WPA2)密码破解方法
无线网络password破解WPA/WPA2教程 本教程用于探索无线路由安全漏洞,禁止用于非法用途,违者法律必究(与我无关) 在动手破解WPA/WPA2前,应该先了解一下基础知识,本文适合新手阅读 首 ...
- Final——无线网络密码破解——WPA/WPA2
Final--无线网络密码破解--WPA/WPA2 20154305 齐帅 ↓ ↓ ↓ * # % & 郑 重 声 明 & % # * ↓ ↓ ↓ 本实验教程用于探索无线路由安全漏洞, ...
- Aircrack-ng破解WPA/WPA2加密WiFi教程(Kali)
一.说明 以前学Kali,很多人都笑赞“WiFi破解神器”.我很烦,一是我不会破解二是我觉得他们也不会破解三是我隐约觉得所谓的WiFi破解不是什么技术性的操作. 后来基础知识充分了然后弄了个无线网卡, ...
- Aircrack-ng: (2) WEP & WPA/WPA2 破解
作者:枫雪庭 出处:http://www.cnblogs.com/FengXueTing-px/ 欢迎转载 目录 一. WEP 破解 二. wpa/wpa2 破解 一. WEP 破解 注:步骤前,确保 ...
- 使用 Aircrack-ng 破解 WEP 和 WPA/WPA2 加密的 Wi-Fi 密码。(转)
1.首先请不要使用此方法去搞破坏,去蹭Wi-Fi,因为不装逼地说,我认为技术本身的价值很大,尤其是在学习这个技术的过程中解决遇到的问题,当经过重重困难最后终于成功之后的喜悦又怎么能拿去蹭网呢.我在此过 ...
- WPA/WPA2加密破解
WPA/WPA2无线密码破解这里主要介绍两种方法:穷举PIN码.穷举密码 穷举PIN码(共11000种组合)破解速度快,需要一些条件(路由器支持WPS.QSS功能),路由器信号良好.无论密码多复杂,条 ...
- Android wpa_supplicant 四次握手 流程分析
记录wpa_supplicant四次握手的过程. 相关log:https://www.cnblogs.com/helloworldtoyou/p/9633603.html 接收到第一次握手,会设置一个 ...
- Android WiFi 日志记录(四次握手)
记录一下四次握手的log. PMK: PMK(Pairwise Master Key,成对主密钥 STA和AP得到PMK后,将进行密匙派生以得到PTK.最后,PTK被设置到硬件中, 用于数据的加解密. ...
随机推荐
- python中split函数的使用
最近学习python,对split函数做了下总结,内容如下:
- 【转】【Android】开源项目汇总-备用
第一部分 个性化控件(View) 主要介绍那些不错个性化的View,包括ListView.ActionBar.Menu.ViewPager.Gallery.GridView.ImageView.Pro ...
- Ugly Numbers
Ugly Numbers Time Limit: 1000MS Memory Limit: 10000K Total Submissions: 21918 Accepted: 9788 Descrip ...
- 山东理工大学第七届ACM校赛-学区房问题 分类: 比赛 2015-06-26 10:23 89人阅读 评论(0) 收藏
Time Limit: 1000ms Memory limit: 65536K 有疑问?点这里^_^ 题目描述 铁牌狗在学区B有一套面积为S1平方米的房子,现在他为了让后代进化成金牌狗,决定在学区A购 ...
- Javascript正则表达式笔记
一.字符类 将单独的直接字符放进[]内,就组成了字符类.一个字符类和它所包含的任何字符都匹配. 例如:/[abc]/ 与abc三个字母的任意一个匹配. 同时,还可以定义否定字符类.利用^字符.例如:/ ...
- 数字证书私钥sign及验证
package com.epay.bank.test.encrypt; import java.io.FileInputStream; import java.security.KeyStore; i ...
- 集合、ArrayList 集合。Stack集合。Queue集合。以及Hashtable集合
arrayList 首先复制Colections加 : 创建arrayList ar =new arrayList(); //ArrayList al=new ArrayList(); ...
- config文件 反射方法
string testPropertyName = "MainFormText"; Properties.Settings setting = Properties.Settin ...
- 查看C语言的方法名
1,打开 Visual Studio 2008 x64 Win64 命令提示 2,查看dumpbin –exports [C动态库的路径]
- 无法为表空间 XX 中的段创建 INITIAL 区
select * from dba_data_files where TABLESPACE_NAME='XX'--找到表空间文件 alter database datafile '/opt/app/o ...