
使用BGP的虚拟下一跳实现IGP的路由负载
网络拓扑:
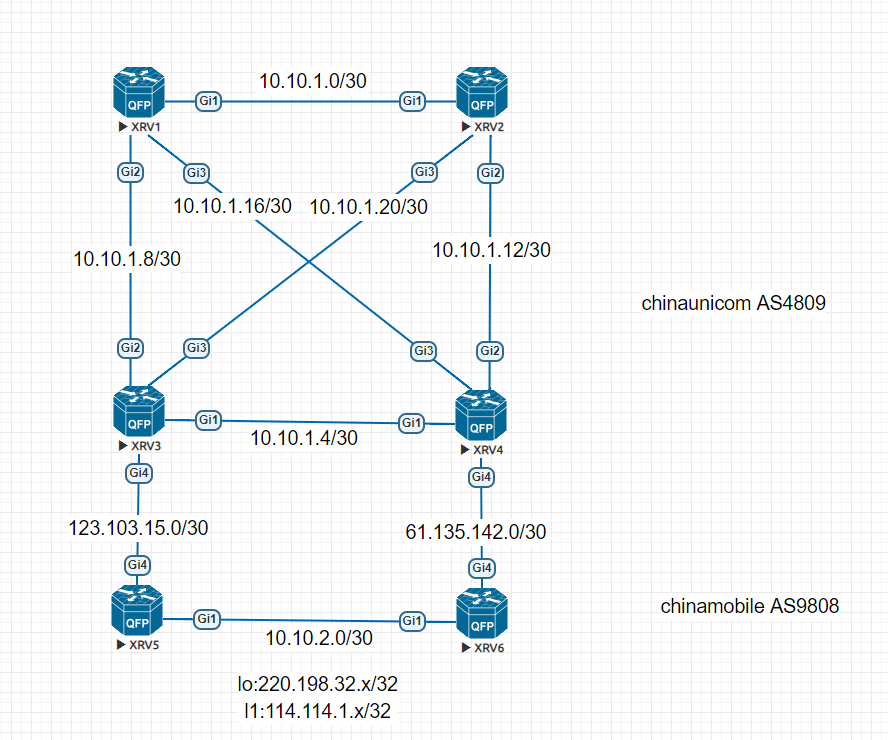
XRV1
==============================================================
!
hostname XRV1
!
interface Loopback0
ip address 220.198.32.1 255.255.255.255
ip router isis 100
!
interface Loopback1
ip address 114.114.1.1 255.255.255.255
!
interface GigabitEthernet1
ip address 10.10.1.1 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet2
ip address 10.10.1.9 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet3
ip address 10.10.1.17 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
router isis 100
net 49.0000.2201.9832.1000.00
is-type level-2-only
!
router bgp 4809
bgp router-id 220.198.32.1
bgp log-neighbor-changes
bgp graceful-restart restart-time 120
bgp graceful-restart stalepath-time 360
bgp graceful-restart
network 114.114.1.1 mask 255.255.255.255
neighbor internal peer-group
neighbor internal password cisco
neighbor internal update-source Loopback0
neighbor 220.198.32.2 remote-as 4809
neighbor 220.198.32.2 peer-group internal
neighbor 220.198.32.3 remote-as 4809
neighbor 220.198.32.3 peer-group internal
neighbor 220.198.32.4 remote-as 4809
neighbor 220.198.32.4 peer-group internal
!
XRV2
==============================================================
hostname XRV2
!
interface Loopback0
ip address 220.198.32.2 255.255.255.255
ip router isis 100
!
interface Loopback1
ip address 114.114.1.2 255.255.255.255
!
interface GigabitEthernet1
ip address 10.10.1.2 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet2
ip address 10.10.1.13 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet3
ip address 10.10.1.21 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
router isis 100
net 49.0000.2201.9832.2000.00
is-type level-2-only
!
router bgp 4809
bgp router-id 220.198.32.2
bgp log-neighbor-changes
bgp graceful-restart restart-time 120
bgp graceful-restart stalepath-time 360
bgp graceful-restart
network 114.114.1.2 mask 255.255.255.255
neighbor internal peer-group
neighbor internal password cisco
neighbor internal update-source Loopback0
neighbor 220.198.32.1 remote-as 4809
neighbor 220.198.32.1 peer-group internal
neighbor 220.198.32.3 remote-as 4809
neighbor 220.198.32.3 peer-group internal
neighbor 220.198.32.4 remote-as 4809
neighbor 220.198.32.4 peer-group internal
!
XRV3
==============================================================
!
hostname XRV3
!
interface Loopback0
ip address 220.198.32.3 255.255.255.255
ip router isis 100
!
interface Loopback1
ip address 114.114.1.3 255.255.255.255
!
interface GigabitEthernet1
ip address 10.10.1.5 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet2
ip address 10.10.1.10 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet3
ip address 10.10.1.22 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet4
ip address 123.103.15.1 255.255.255.252
negotiation auto
bfd interval 250 min_rx 250 multiplier 3
!
router isis 100
net 49.0000.2201.9832.3000.00
is-type level-2-only
redistribute static ip
!
router isis 1200
!
router bgp 4809
bgp router-id 220.198.32.3
bgp log-neighbor-changes
bgp graceful-restart restart-time 120
bgp graceful-restart stalepath-time 360
bgp graceful-restart
network 114.114.1.3 mask 255.255.255.255
neighbor internal peer-group
neighbor internal password cisco
neighbor internal update-source Loopback0
neighbor internal next-hop-self
neighbor internal route-map external-import out
neighbor 123.103.15.2 remote-as 9808
neighbor 123.103.15.2 password cisco
neighbor 123.103.15.2 fall-over bfd
neighbor 220.198.32.1 remote-as 4809
neighbor 220.198.32.1 peer-group internal
neighbor 220.198.32.2 remote-as 4809
neighbor 220.198.32.2 peer-group internal
neighbor 220.198.32.4 remote-as 4809
neighbor 220.198.32.4 peer-group internal
!
!
virtual-service csr_mgmt
!
ip forward-protocol nd
!
no ip http server
no ip http secure-server
ip route 108.108.108.1 255.255.255.255 123.103.15.2
!
!
ip prefix-list external-import seq 5 permit 114.114.1.5/32
ip prefix-list external-import seq 10 permit 114.114.1.6/32
!
route-map external-import permit 10
match ip address prefix-list external-import
set ip next-hop 108.108.108.1
!
route-map external-import permit 20
!
XRV4
==============================================================
!
hostname XRV4
!
interface Loopback0
ip address 220.198.32.4 255.255.255.255
ip router isis 100
!
interface Loopback1
ip address 114.114.1.4 255.255.255.255
!
interface GigabitEthernet1
ip address 10.10.1.6 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet2
ip address 10.10.1.14 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet3
ip address 10.10.1.18 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet4
ip address 61.135.142.1 255.255.255.252
negotiation auto
bfd interval 250 min_rx 250 multiplier 3
!
router isis 100
net 49.0000.2201.9832.4000.00
is-type level-2-only
redistribute static ip
!
router bgp 4809
bgp router-id 220.198.32.4
bgp log-neighbor-changes
bgp graceful-restart restart-time 120
bgp graceful-restart stalepath-time 360
bgp graceful-restart
network 114.114.1.4 mask 255.255.255.255
neighbor internal peer-group
neighbor internal password cisco
neighbor internal update-source Loopback0
neighbor internal next-hop-self
neighbor internal route-map external-import out
neighbor 61.135.142.2 remote-as 9808
neighbor 61.135.142.2 password cisco
neighbor 61.135.142.2 fall-over bfd
neighbor 220.198.32.1 remote-as 4809
neighbor 220.198.32.1 peer-group internal
neighbor 220.198.32.2 remote-as 4809
neighbor 220.198.32.2 peer-group internal
neighbor 220.198.32.3 remote-as 4809
neighbor 220.198.32.3 peer-group internal
!
!
virtual-service csr_mgmt
!
ip forward-protocol nd
!
no ip http server
no ip http secure-server
ip route 108.108.108.1 255.255.255.255 61.135.142.2
!
!
ip prefix-list external-import seq 5 permit 114.114.1.5/32
ip prefix-list external-import seq 10 permit 114.114.1.6/32
!
route-map external-import permit 10
match ip address prefix-list external-import
set ip next-hop 108.108.108.1
!
route-map external-import permit 20
!
XRV5
==============================================================
!
hostname XRV5
!
interface Loopback0
ip address 220.198.32.5 255.255.255.255
ip router isis 100
!
interface Loopback1
ip address 114.114.1.5 255.255.255.255
!
interface GigabitEthernet1
ip address 10.10.2.1 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet4
ip address 123.103.15.2 255.255.255.252
negotiation auto
bfd interval 250 min_rx 250 multiplier 3
!
router isis 100
net 49.0000.2201.9832.5000.00
is-type level-2-only
!
router bgp 9808
bgp router-id 220.198.32.5
bgp log-neighbor-changes
bgp graceful-restart restart-time 120
bgp graceful-restart stalepath-time 360
bgp graceful-restart
network 114.114.1.5 mask 255.255.255.255
neighbor 123.103.15.1 remote-as 4809
neighbor 123.103.15.1 password cisco
neighbor 123.103.15.1 fall-over bfd
neighbor 220.198.32.6 remote-as 9808
neighbor 220.198.32.6 password cisco
neighbor 220.198.32.6 update-source Loopback0
neighbor 220.198.32.6 next-hop-self
!
XRV6
==============================================================
!
hostname XRV6
interface Loopback0
ip address 220.198.32.6 255.255.255.255
ip router isis 100
!
interface Loopback1
ip address 114.114.1.6 255.255.255.255
!
interface GigabitEthernet1
ip address 10.10.2.2 255.255.255.252
ip router isis 100
negotiation auto
isis circuit-type level-2-only
!
interface GigabitEthernet4
ip address 61.135.142.2 255.255.255.252
negotiation auto
bfd interval 250 min_rx 250 multiplier 3
!
router isis 100
net 49.0000.2201.9832.6000.00
is-type level-2-only
!
router bgp 9808
bgp router-id 220.198.32.6
bgp log-neighbor-changes
bgp graceful-restart restart-time 120
bgp graceful-restart stalepath-time 360
bgp graceful-restart
network 114.114.1.6 mask 255.255.255.255
neighbor 61.135.142.1 remote-as 4809
neighbor 61.135.142.1 password cisco
neighbor 61.135.142.1 fall-over bfd
neighbor 220.198.32.5 remote-as 9808
neighbor 220.198.32.5 password cisco
neighbor 220.198.32.5 update-source Loopback0
neighbor 220.198.32.5 next-hop-self
!
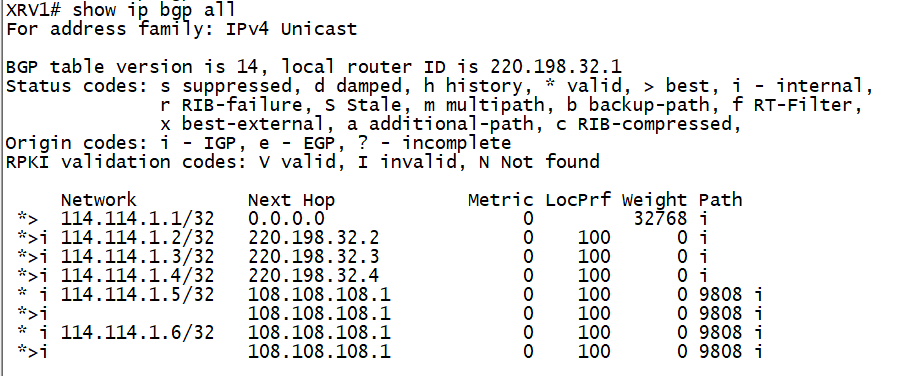
在XRV1上使用show ip bgp 查看BGP路由表
==============================================================
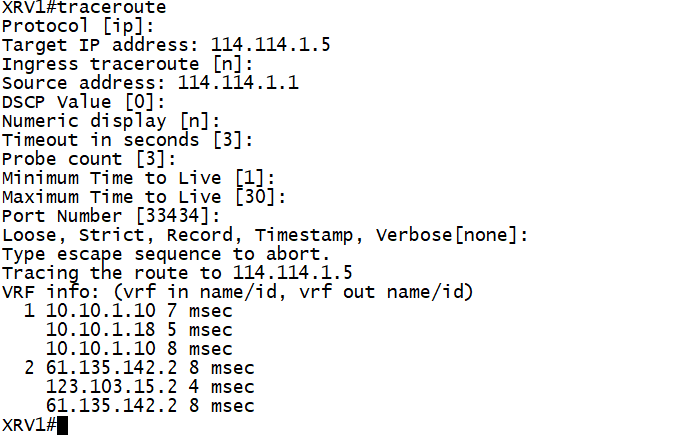
在XRV1上使用tracert跟踪路由,源为XRV1的l1地址,目标为XRV5的l1地址
==============================================================
配置要点:
1.在两个ISP的边界上写一条下一跳并非真实存在的路由,下一跳指向友商的真实的EBGP的接口地址
2.将上述静态路由重分布进ISIS路由
3.在边界上通过前缀列表匹配需要进行IBGP负载的友商的路由
4.通过route-map进行修改需要进行IBGP负载的友商的路由的下一跳为1的静态的目标路由
5.在边界上通过neighbor调用route-map修改下一跳后发布给IBGP
6.IBGP邻居受到从EBGP学习到的路由后即可实现负载
使用BGP的虚拟下一跳实现IGP的路由负载的更多相关文章
- 利用BGP虚拟下一跳实现链路负载均衡
最近针对BGP链路负载均衡方案“虚拟下一跳”进行了总结,现将总结的PPT贴上来.
- Linux3.5内核以后的路由下一跳缓存
在Linux3.5版本号(包括)之前.存在一个路由cache.这个路由cache的初衷是美好的,可是现实往往是令人遗憾的.下面是陈列得出的两个问题:1.面临针对hash算法的ddos问题(描写叙述该问 ...
- linux 接口地址全部清除才清理从此接口发出的下一跳路由
接口地址全部清除才清理从此接口发出的下一跳路由 如: eth7配置两个地址 eth7: 192.168.1.1 10.1.1.1 添加一条路由: route add -net 2.2.2.0/24 g ...
- 等价路由在路由器和CE交换机上默认的行为是不同的,路由器总是走第一个下一跳,CE交换机是逐包。
结论: 1.在eNSP中实验,路由器和CE交换机对于等价路由的默认转发行为是不同的, 路由器:默认是基于流的转发形态,更准确的来讲,ping两个不同的下一跳,都是走等价路由的第一个路由,不走第二条路由 ...
- 配置多个相同网段的ECMP下一跳,配合NQA健康检查实现高可靠性
1.一般情况下,ECMP常用的常见是,针对很远的目的地址,下一跳分别是路由器的不同出端口,而路由器的不同端口是不同网段的,也就是说,下一跳是不同的网段地址. 但是,在连接到终端服务器时,常常会采用多个 ...
- route -A inet6 增加下一跳 提示错误 SIOCADDRT: No route to host
1.增加前路由表: 2. route -A inet6 增加下一跳 提示错误 SIOCADDRT: No route to host 3.删除已有的下一条路由表项: 4.再次尝试 route -A i ...
- IBGP的自己下一跳,指定源命令。
neighbor router-id update-source loopback int 当两者并不是以物理接口为搭建邻居的时候,就得使用指定源,充当TCP接口. neighbor router-i ...
- ensp的基础路由命令,接口,下一跳的配置,入门必备
关于ensp入门事情,第一件事当是安装必备三件套:而后,应该是接触路由和PC机了,最烦人满屏代码,眼花缭乱: 今天写一篇零基础接触ensp的首次操作,PC-路由-路由-PC的互通实验: 实验要拉出两台 ...
- 【Azure API 管理】APIM集成内网虚拟网络后,启用自定义路由管理外出流量经过防火墙(Firewall),遇见APIs加载不出来问题
问题描述 使用 Azure 虚拟网络,Azure APIM 可以管理无法通过 Internet 访问的 API,达到以保护企业内部的后端API的目的.在虚拟网络中,启用网络安全组(NSG:Networ ...
随机推荐
- Android6.0动态申请权限那些坑--以及避免用户选择不再提示后无法获取权限的问题
Android 6.0 为了保护用户隐私,将一些权限的申请放在了应用运行的时候去申请, 比如以往的开发中,开发人员只需要将需要的权限在清单文件中配置即可,安装后用户可以在设置中的应用信息中看到:XX应 ...
- 【codeforces 750F】New Year and Finding Roots
time limit per test2 seconds memory limit per test256 megabytes inputstandard input outputstandard o ...
- MKNetWorkKit的使用(1)
在整个程序中只有一个全局队列 MKNetWorkKit中主要有两个类,MKNetworkEngine和 MKNetworkOperation,MKNetworkOperation就是一个操作,是NSO ...
- 【BZOJ 1021】[SHOI2008]Debt 循环的债务
[题目链接]:http://www.lydsy.com/JudgeOnline/problem.php?id=1021 [题意] [题解] 设f[i][j][k]表示前i种面值的钱币; 第一个人当前的 ...
- 【 D3.js 高级系列 — 2.0 】 机械图 + 人物关系图
机械图(力路线图)结合老百姓的关系图中的生活,这是更有趣. 本文将以此为证据,所列的如何图插入外部的图像和文字的力学. 在[第 9.2 章]中制作了一个最简单的力学图.其后有非常多朋友有疑问,基本的问 ...
- git如何更新fork的repository(Fork一个别人的repository,做了一些改动,再合并别人的更新)
Fork一个别人的repository,做了一些改动,想提交pull request的时候,发现原先别人的repository已经又有了一些更新了,这个时候想使得自己fork出的repository也 ...
- java写文件时往末尾追加文件(而不是覆盖原文件),的两种方法总结
代码如下: import java.io.FileWriter; import java.io.IOException; import java.io.RandomAccessFile; public ...
- WPF中PasswordBox控件的Password属性的数据绑定
原文:WPF中PasswordBox控件的Password属性的数据绑定 英文原文:http://www.wpftutorial.net/PasswordBox.html 中文原文:http://bl ...
- Android之消息推送实现
在开发Android和iPhone应用程序时,我们往往需要从服务器不定的向手机客户端即时推送各种通知消息,iPhone上已经有了比较简单的和完美的推送通知解决方案,可是Android平台上实现起来却相 ...
- WPF依赖属性(续)(2)依赖属性与附加属性的区别
原文:WPF依赖属性(续)(2)依赖属性与附加属性的区别 接上篇,感谢各位的评论,都是认为依赖属性的设计并不是为了节省内存,从大的方面而讲是如此.样式,数据绑定,动画样样都离不开它.这篇 ...