
PAM认证机制详情
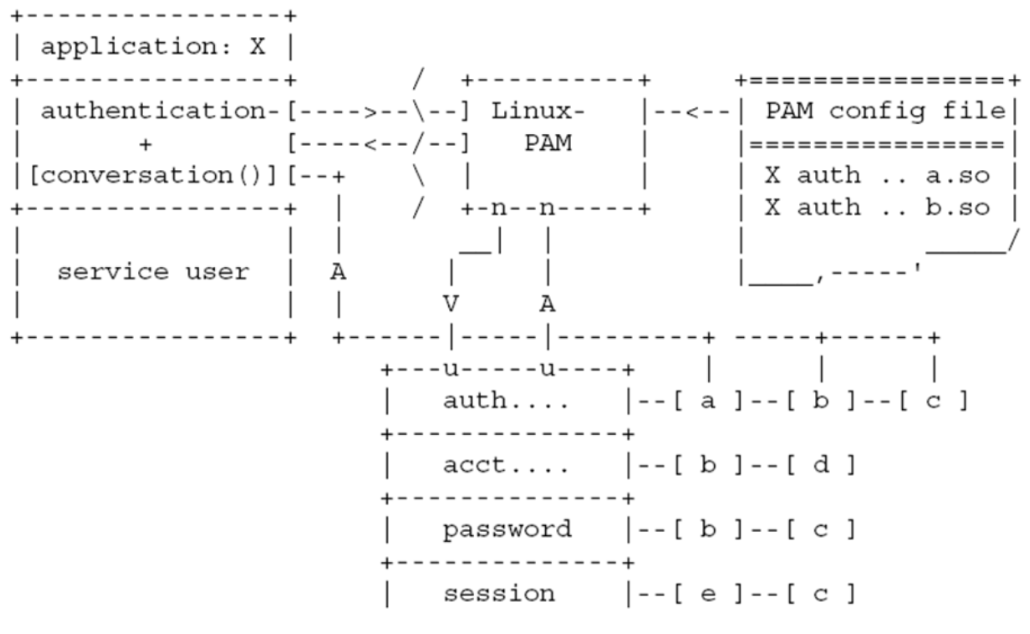
 [root@yinzhengjie ~]# more /etc/pam.d/su | grep  pam_rootok.so

 #auth           sufficient      pam_rootok.so

 [root@yinzhengjie ~]#

 [root@yinzhengjie ~]# su yinzhengjie

 Password:

 [yinzhengjie@yinzhengjie root]$ exit

 exit

 [root@yinzhengjie ~]#

 [root@yinzhengjie ~]# more /etc/pam.d/su | grep  pam_rootok.so

 auth            sufficient      pam_rootok.so

 [root@yinzhengjie ~]# su yinzhengjie

 [yinzhengjie@yinzhengjie root]$

 [yinzhengjie@yinzhengjie root]$ exit

 exit

 [root@yinzhengjie ~]#
案例展示:(限制root切换用户也需要密码)
 [root@yinzhengjie ~]# more /etc/pam.d/sshd | grep pam_access.so

 auth       required     pam_access.so

 [root@yinzhengjie ~]#

 [root@yinzhengjie ~]# tail - /etc/security/access.conf

 #Add by yinzhengjie

 -:root:ALL EXCEPT 10.0.0.0/            #只让root从10.0.0./24的网段访问

 #-:root:10.0.0.0/                    #拒绝从10.0.0./24这个C的地址访问过来。

 #-:root:ALL EXCEPT 10.10.0.161        #拒绝从10.10.0.161这个IP访问过来。

 [root@yinzhengjie ~]#
案例展示:(控制访问的源IP地址)
 [root@yinzhengjie ~]# grep listfile /etc/pam.d/sshd

 auth       required     pam_listfile.so item=user sense=allow file=/etc/yinzhengjie_ssh_users onerr=fail             #注意,“onerr=fail”表示当文件“/etc/yinzhengjie_ssh_users”不存在时,默认为fail。

 [root@yinzhengjie ~]# > /var/log/secure

 [root@yinzhengjie ~]# tail -10f /var/log/secure

 Feb   :: yinzhengjie sshd[]: reverse mapping checking getaddrinfo for bogon [10.0.0.161] failed - POSSIBLE BREAK-IN ATTEMPT!

 Feb   :: yinzhengjie sshd[]: pam_listfile(sshd:auth): Couldn't open /etc/yinzhengjie_ssh_users

 Feb   :: yinzhengjie sshd[]: Failed password for root from 10.0.0.161 port  ssh2

 Feb   :: yinzhengjie sshd[]: Received disconnect from 10.0.0.161: : The user canceled authentication.

 ^C

 [root@yinzhengjie ~]# echo root > /etc/yinzhengjie_ssh_users

 [root@yinzhengjie ~]#

 [root@yinzhengjie ~]# tail -10f /var/log/secure

 Feb   :: yinzhengjie sshd[]: reverse mapping checking getaddrinfo for bogon [10.0.0.161] failed - POSSIBLE BREAK-IN ATTEMPT!

 Feb   :: yinzhengjie sshd[]: pam_listfile(sshd:auth): Couldn't open /etc/yinzhengjie_ssh_users

 Feb   :: yinzhengjie sshd[]: Failed password for root from 10.0.0.161 port  ssh2

 Feb   :: yinzhengjie sshd[]: Received disconnect from 10.0.0.161: : The user canceled authentication.

 Feb   :: yinzhengjie sshd[]: Accepted password for root from 10.0.0.161 port  ssh2

 Feb   :: yinzhengjie sshd[]: pam_unix(sshd:session): session opened for user root by (uid=)

 ^C

 [root@yinzhengjie ~]#
案例展示:(sshd的黑名单或白名单)
 [root@yinzhengjie ~]# tail - /etc/security/time.conf

 #Add by yinzhengjie

 sshd;*;*;SaSu0900-        #表示sshd服务的所有终端的所有用户只能在8-18点可以正登陆。

 [root@yinzhengjie ~]#
案例展示:(基于时间限制sshd的访问)
 [root@yinzhengjie ~]# grep pam_tally2.so /etc/pam.d/sshd

 auth       required     pam_tally2.so deny= even_deny_root root_unlock_time= unlock_time=   #表示当用户输入次数超过2次时,锁定用户60秒,因此这里的“even_deny_root ”表示包括root用户,“root_unlock_time”表示root用户锁定的时间,“unlock_time”表示其他用户锁定的时间。

 [root@yinzhengjie ~]#

 [root@yinzhengjie ~]# pam_tally2 --reset -u root            #这里表示手动解锁。

 Login           Failures Latest failure     From

 root

 [root@yinzhengjie ~]#
案例展示:(实现防止对sshd暴力破解)
 [root@yinzhengjie ~]# ulimit -a

 core file size          (blocks, -c)

 data seg size           (kbytes, -d) unlimited

 scheduling priority             (-e)

 file size               (blocks, -f) unlimited

 pending signals                 (-i)

 max locked memory       (kbytes, -l)

 max memory size         (kbytes, -m) unlimited

 open files                      (-n)

 pipe size            ( bytes, -p)

 POSIX message queues     (bytes, -q)

 real-time priority              (-r)

 stack size              (kbytes, -s)

 cpu time               (seconds, -t) unlimited

 max user processes              (-u)

 virtual memory          (kbytes, -v) unlimited

 file locks                      (-x) unlimited

 [root@yinzhengjie ~]# ulimit -n

 [root@yinzhengjie ~]#

 [root@yinzhengjie ~]# tail - /etc/security/limits.conf

 #Add by yinzhengjie

 *               soft    nofile

 *               hard    nofile

 *               soft    nproc

 *               soft    cpu

 [root@yinzhengjie ~]#

 [root@yinzhengjie ~]# exit

 logout

 Last login: Sun Feb   ::  from 10.0.0.161

 [root@yinzhengjie ~]# ulimit -n

 [root@yinzhengjie ~]#
案例展示:(调整最大打开的文件数)
 [root@yinzhengjie ~]# which sshd

 /usr/sbin/sshd

 [root@yinzhengjie ~]# which login

 /bin/login

 [root@yinzhengjie ~]# ldd /usr/sbin/sshd | grep pam

         libpam.so. => /lib64/libpam.so. (0x00007f2c196cf000)

 [root@yinzhengjie ~]#

 [root@yinzhengjie ~]# ldd `which login` | grep pam        #注意,ldd命令是查看进程文件支持的动态库,而ldconfig是可以查看已经加载的动态库。我们可以用“ldconfig -p”来打印当前操作系统已经加载的动态库。

         libpam.so. => /lib64/libpam.so. (0x000000323b200000)

         libpam_misc.so. => /lib64/libpam_misc.so. (0x0000003230a00000)

 [root@yinzhengjie ~]#
PAM认证机制详情的更多相关文章
- PAM认证机制
PAM:Pluggable Authentication Modules 认证库:文本文件,MySQL,NIS,LDAP等 Sun公司于1995 年开发的一种与认证相关的通用框架机制 PAM 是关注如 ...
- CentOS-pam认证机制简介
前言 linux下PAM模块全称是Pluggable Authentication Module for linux(可插入式授权管理模块),该由Sun公司提供,在Linux中,PAM是可动态配置的, ...
- AIDE,sudo,TCP_Wrappers,PAM认证等系统安全访问机制
AIDE 高级入侵检测环境:是一个入侵检测工具,主要用途是检查文件的完整性,审计计算机上的那些文件被更改过了. AIDE能够构造一个指定文件的数据库,它使用aide.conf作为其配置文件.AIDE数 ...
- PAM认证
PAM认证 摘自: http://www.cnblogs.com/shenxm/p/8451889.html PAM(Pluggable Authentication Modules) Sun公司于1 ...
- 什么是PAM认证
PAM(Pluggable Authentication Modules )是由 Sun 提出的一种用于实现应用程序的认证机制.其核心是一套共享库,目的是提供一个框架和一套编程接口,将认证工作由程序员 ...
- Atitit HTTP 认证机制基本验证 (Basic Authentication) 和摘要验证 (Digest Authentication)attilax总结
Atitit HTTP认证机制基本验证 (Basic Authentication) 和摘要验证 (Digest Authentication)attilax总结 1.1. 最广泛使用的是基本验证 ( ...
- WPS 认证机制
WPS 认证机制 WPS(Wi-Fi Protected Setup,Wi-Fi保护设置)(有的叫做AOSS.有的叫做QSS,不过功能都一致.)是由Wi-Fi联盟组织实施的认证项目,主要致力于简化无线 ...
- 基于Token的WEB后台认证机制
几种常用的认证机制 HTTP Basic Auth HTTP Basic Auth简单点说明就是每次请求API时都提供用户的username和password,简言之,Basic Auth是配合RES ...
- HTTP中的摘要认证机制
引子: 指定和服务器端交互的HTTP方法,URL地址,即其他请求信息: Method:表示http请求方法,一般使用"GET","POST". url:表示请求 ...
随机推荐
- Flask学习-Flask基础之WSGI
一.WSGI为什么会出现? 在学习一个东西之前,我们肯定想知道:它为什么会出现?那么,WSGI为什么会出现呢? 我们知道,部署一个web应用,经常需要使用nginx.apache或者IIS等web服务 ...
- docker之Dokcerfile 常用指令
一.Docker语法 Docker语法: FROM 基础镜像base image RUN 执行命令 ADD 添加文件 COPY 拷贝文件 CMD 执行命令 EXPOSE 执行命令 WORKDIR 指定 ...
- GitHub 新手教程 三,Git Bash
1,通过 开始菜单 启动 Git Bash,或者 在 cmd 下执行以下命令: D:\SoftWare\Git\git-bash.exe --cd-to-home (D:\SoftWare\Git 是 ...
- PTA (Advanced Level) 1002 A+B for Polynomials
1002 A+B for Polynomials This time, you are supposed to find A+B where A and B are two polynomials. ...
- DES的加密与解密算法(Python实现)
DES的加密与解密算法(Python实现) 密码学实验:实现了DES的简单的加密和解密算法,DES算法的相关资料网上很多,这里不再赘述,仅仅贴出源代码给大家分享,源码中包含很多汉字注释,相信大家都是可 ...
- C/C+ 感触
1. C/C++语言开发的首选利器- C++Test 以前在windows平台下的开发,使用的框架主要是MFC,以及console工程(基于win32SDK),属于纯C/C++ ...
- “数学口袋精灵”第二个Sprint计划(第四天)
“数学口袋精灵”第二个Sprint计划----第四天进度 任务分配: 冯美欣:欢迎界面的背景音乐完善 吴舒婷:游戏界面的动作条,选择答案后的音效 林欢雯:代码算法设计 进度: 冯美欣:欢迎界面背景 ...
- 分析code
1 using System; //跟系统说明一下可能会用到这个dll里面的东西 using System.Collections.Generic; //引用集合类命名空间 using System. ...
- 原生 js 封装get ,post, delete 请求
现在的项目中都在用VUE 以及react 等MVC, MVVM 框架. 丢弃了原始的JQ .不可能为了个$.ajax();而把JQ引进来吧. 在vue1的开发中 提供了 vueResouce, vu ...
- [转帖] mysql 用户 权限 密码等操作记录
前言 From :https://blog.csdn.net/yu12377/article/details/78214336 mysql5.7版本中用户管理与以前版本略有不同,在此记录,以备忘 登陆 ...