
web赛题3
2019--21省赛
wp:https://xz.aliyun.com/t/6458
2019-11-22蚂蚁金服(南邮)wp有了,微信
https://platform.d3ctf.io/#/
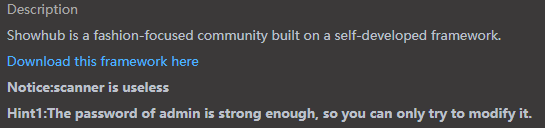
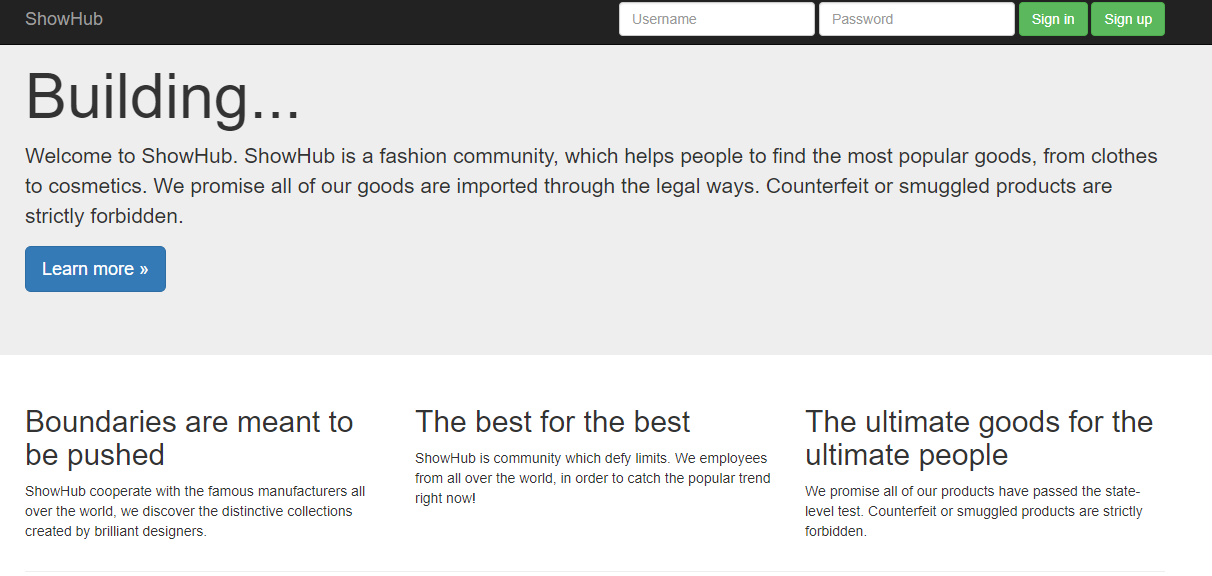
@d3ctf-Showhub
@d3ctf-EasyWeb
hint:source code is in attachments
注册成功
@d3ctf- d3guestbook
聊天题该死的流行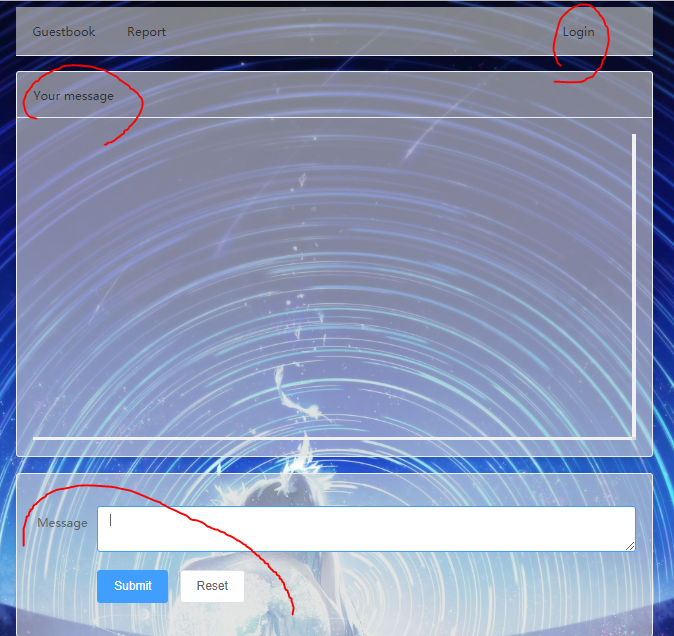
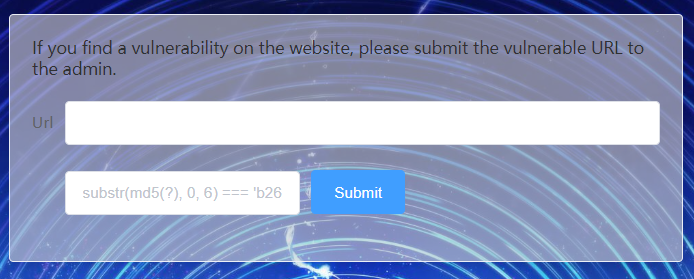
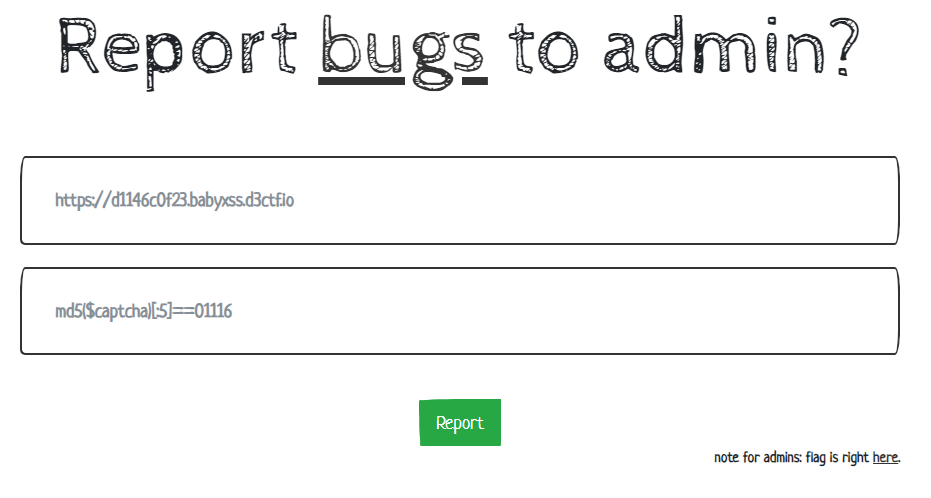
report:
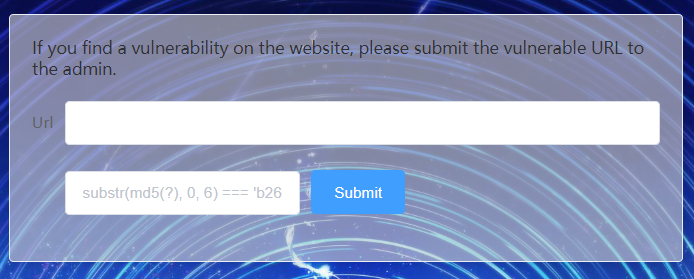

@d3ctf-babyxss
@d3ctf-fake onelinephp
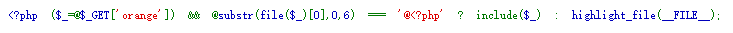
<?php ($_=@$_GET['orange']) && @substr(file($_)[0],0,6) === '@<?php' ? include($_) : highlight_file(__FILE__);
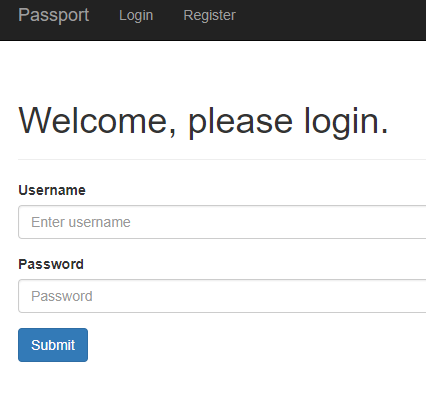
@d3ctf-ezts

@d3ctf-ezupload
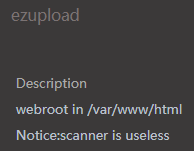
打开就只有这个php代码
<?php
class dir{
    public $userdir;
    public $url;
    public $filename;
    public function __construct($url,$filename) {
        $this->userdir = "upload/" . md5($_SERVER["HTTP_X_REAL_IP"]);
        $this->url = $url;
        $this->filename  =  $filename;
        if (!file_exists($this->userdir)) {
            mkdir($, true);
        }
    }
    public function checkdir(){
        if ($this->userdir != "upload/" . md5($_SERVER["HTTP_X_REAL_IP"])) {
            die('hacker!!!');
        }
    }
    public function checkurl(){
        $r = parse_url($this->url);
        if (!isset($r['scheme']) || preg_match("/file|php/i",$r['scheme'])){
            die('hacker!!!');
        }
    }
    public function checkext(){
        if (stristr($this->filename,'..')){
            die('hacker!!!');
        }
        if (stristr($this->filename,'/')){
            die('hacker!!!');
        }
        $ext = substr($);
        if (preg_match("/ph/i", $ext)){
            die('hacker!!!');
        }
    }
    public function upload(){
        $this->checkdir();
        $this->checkurl();
        $this->checkext();
        $content = file_get_contents($,);
        if (preg_match("/\<\?|value|on|type|flag|auto|set|\\\\/i", $content)){
            die('hacker!!!');
        }
        file_put_contents($this->userdir."/".$this->filename,$content);
    }
    public function remove(){
        $this->checkdir();
        $this->checkext();
        if (file_exists($this->userdir."/".$this->filename)){
            unlink($this->userdir."/".$this->filename);
        }
    }
    public function count($dir) {
        if ($dir === ''){
            $num = count(scandir($;
        }
        else {
            $num = count(scandir($dir)) - ;
        }
        ) {
            return "you have $num files";
        }
        else{
            return "you don't have file";
        }
    }
    public function __toString() {
        return implode(" ",scandir(__DIR__."/".$this->userdir));
    }
    public function __destruct() {
        $string = "your file in : ".$this->userdir;
        file_put_contents($this->filename.".txt", $string);
        echo $string;
    }
}

if (!isset($_POST['action']) || !isset($_POST['url']) || !isset($_POST['filename'])){
    highlight_file(__FILE__);
    die();
}

$dir = new dir($_POST['url'],$_POST['filename']);
if($_POST['action'] === "upload") {
    $dir->upload();
}
elseif ($_POST['action'] === "remove") {
    $dir->remove();
}
elseif ($_POST['action'] === "count") {
    if (!isset($_POST['dir'])){
        echo $dir->count('');
    } else {
        echo $dir->count($_POST['dir']);
    }
}
安洵杯 2019-11-30
比赛:http;s://axb.d0g3.cn
题解+复盘:https://github.com/D0g3-Lab/i-SOON_CTF_2019
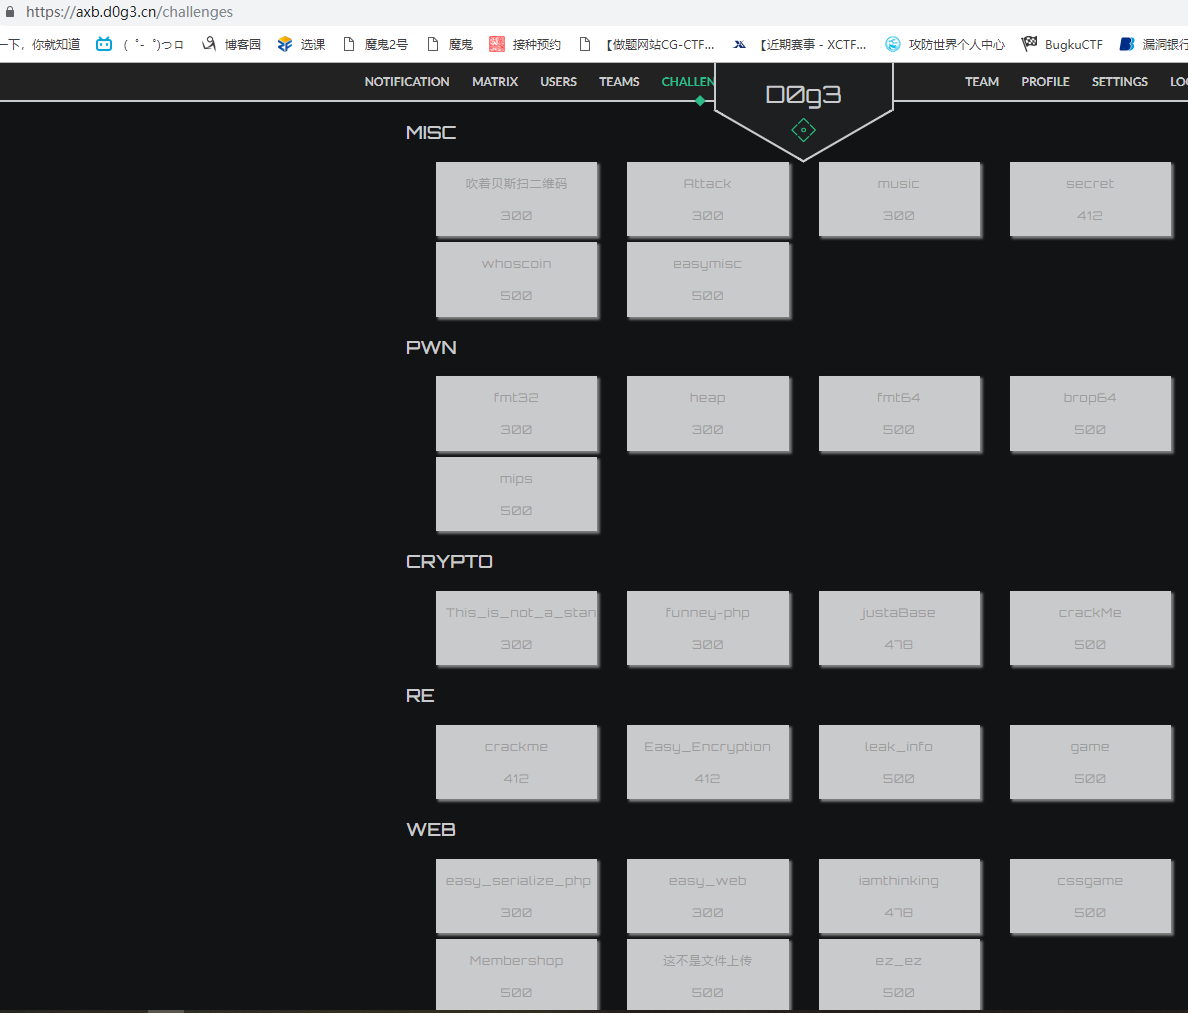
@安洵杯-easy_serialize_php
hint:反序列化
点击sourcecode,得到php代码

<?php

$function = @$_GET['f'];

function filter($img){
    $filter_arr = array('php','flag','php5','php4','fl1g');
    $filter = '/'.implode('|',$filter_arr).'/i';
    return preg_replace($filter,'',$img);
}

if($_SESSION){
    unset($_SESSION);
}

$_SESSION["user"] = 'guest';
$_SESSION['function'] = $function;

extract($_POST);

if(!$function){
    echo '<a href="index.php?f=highlight_file">source_code</a>';
}

if(!$_GET['img_path']){
    $_SESSION['img'] = base64_encode('guest_img.png');
}else{
    $_SESSION['img'] = sha1(base64_encode($_GET['img_path']));
}

$serialize_info = filter(serialize($_SESSION));

if($function == 'highlight_file'){
    highlight_file('index.php');
}else if($function == 'phpinfo'){
    eval('phpinfo();'); //maybe you can find something in here!
}else if($function == 'show_image'){
    $userinfo = unserialize($serialize_info);
    echo file_get_contents(base64_decode($userinfo['img']));
}
尝试url访问guest_img.png
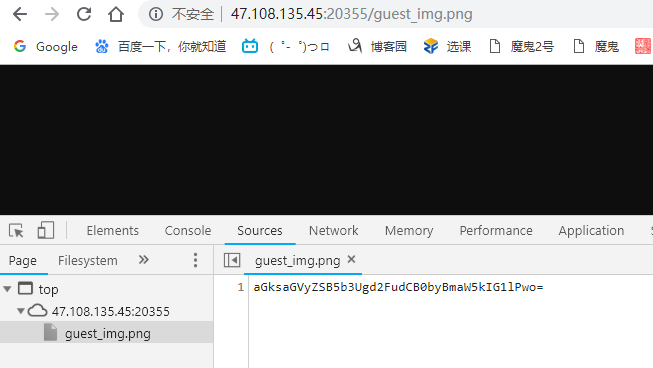
一个base64,解码出来一句hi,here you want to find me?
没啥用
再尝试urlhttp://47.108.135.45:20355/?img_path=‘guest_img.png'还是不行

@安洵杯-easy_web
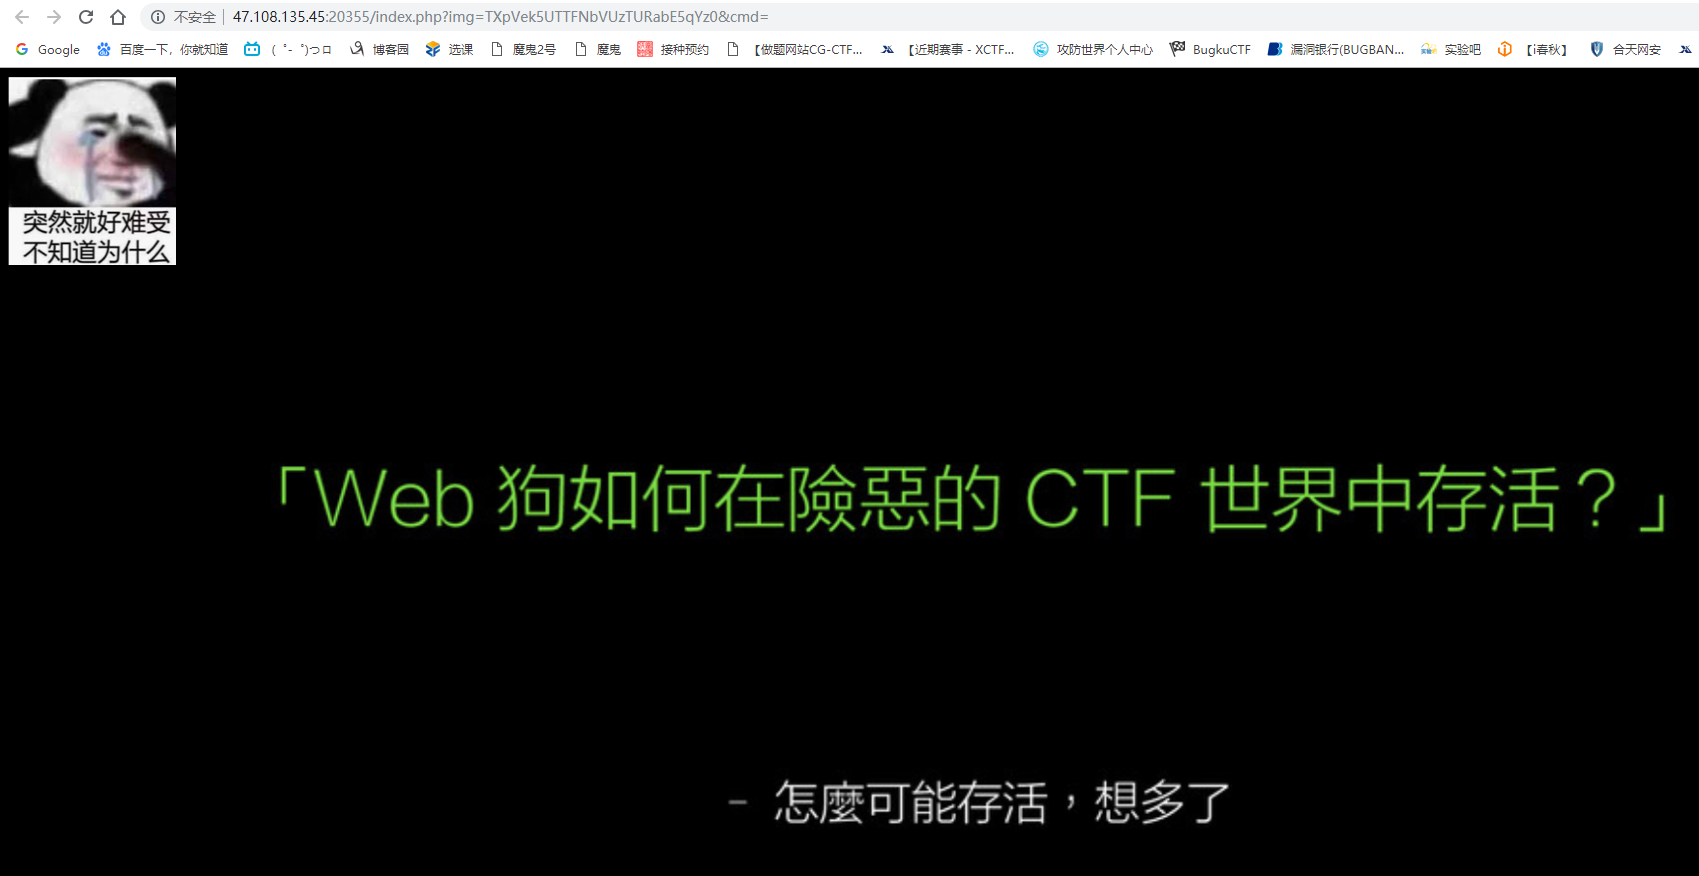
源代码,左上表情包图片是一段base64


这一大串屁用没有,每张图都这样的,图片编码成base64而已,接出来前面一个PNG说明是png文件,别一看见==就激动解码,要解的是url里的那串
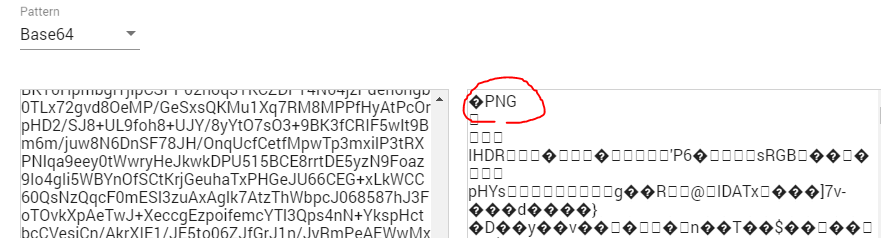
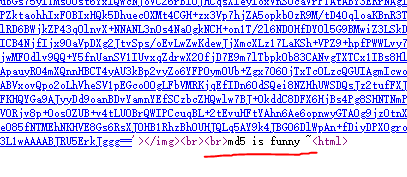 最后提示md5
思路应该是:首先扫一下目录,扫出一个img,555.png
http://47.108.135.45:20355/index.php?img=TXpVek5UTTFNbVUzTURabE5qYz0&cmd= z这一段加上=或者俩=,两次base64,然后ascii,解码出一个555.png,然后不知怎么能得到原码,然后开始代码审计
@安洵杯-iamthinking
根据hint的/public/访问
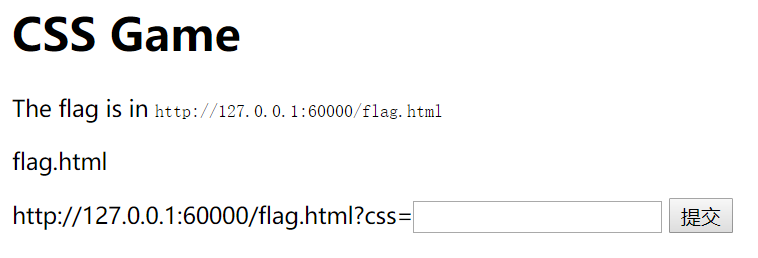
@安洵杯-cssgame
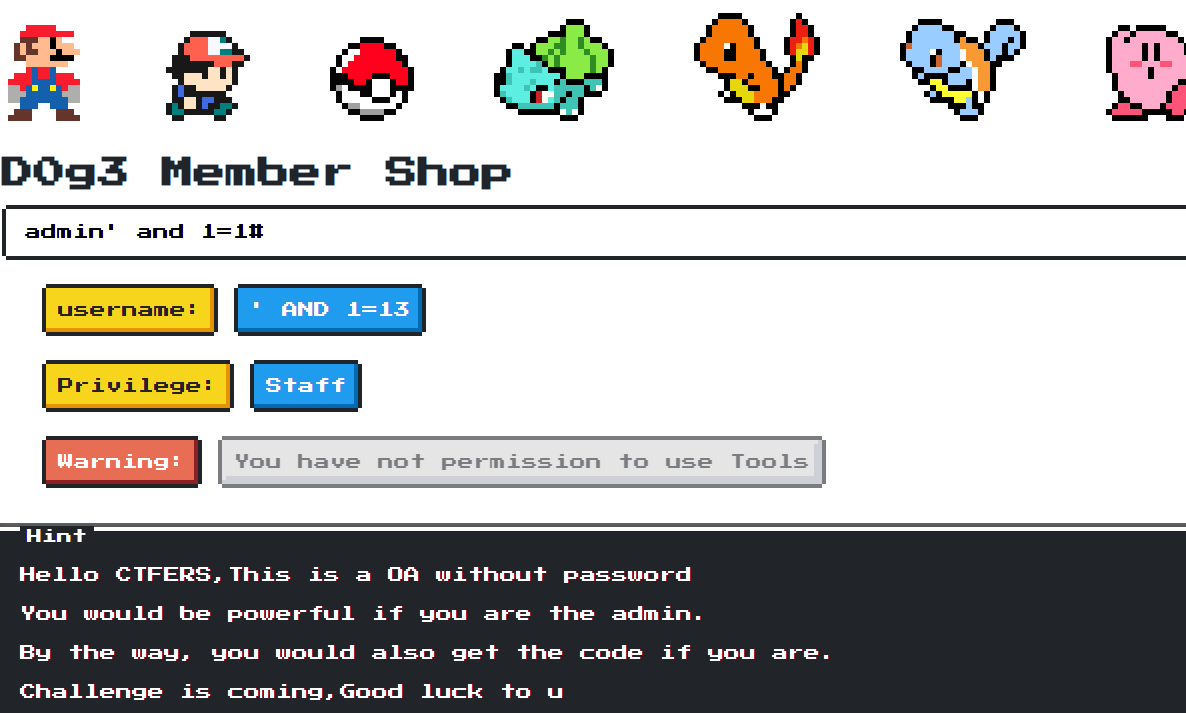
@安洵杯-Membershop

简单注入一波
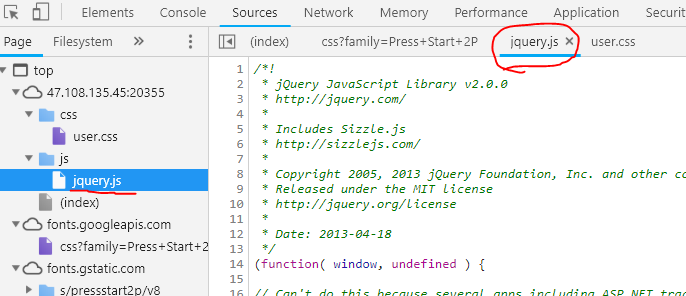
该页面js代码
<script>
$(document).keyup(function (e) {
    ) {
        var userName = $("#member").val();
        window.location.href='/login?userName='+userName;
    }
});
</script>
该页面另一段超长js
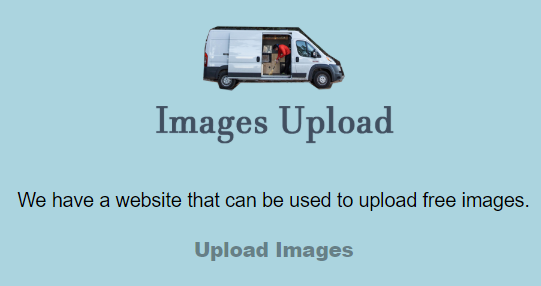
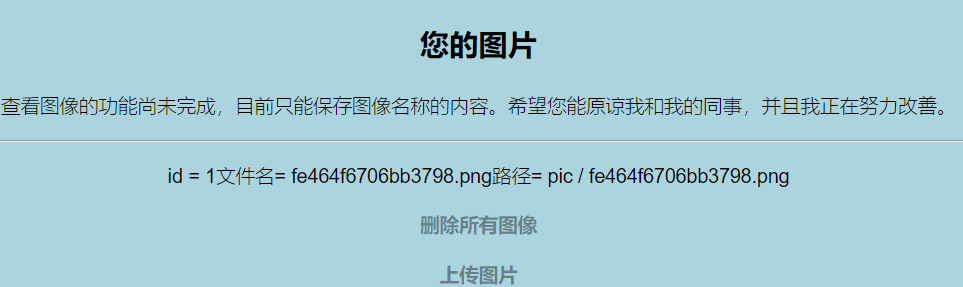
@安洵杯-这不是文件上传
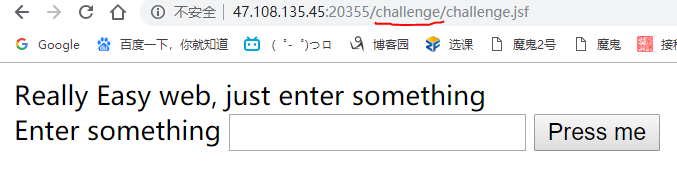
@安洵杯-ez_ez

web赛题3的更多相关文章
- web赛题2
@上海赛wp 微信 和 https://www.ctfwp.com/articals/2019unctf.html 后续公告https://unctf.buuoj.cn/notice.html 必看! ...
- web赛题
@php反序列化漏洞https://www.freebuf.com/news/172507.html @巅峰极客wp https://www.anquanke.com/post/id/189142 @ ...
- 【天池大数据赛题解析】资金流入流出预测(附Top4答辩ppt)
http://mp.weixin.qq.com/s?__biz=MzA3MDg0MjgxNQ==&mid=208451006&idx=1&sn=532e41cf020a0673 ...
- Hitcon 2016 Pwn赛题学习
PS:这是我很久以前写的,大概是去年刚结束Hitcon2016时写的.写完之后就丢在硬盘里没管了,最近翻出来才想起来写过这个,索性发出来 0x0 前言 Hitcon个人感觉是高质量的比赛,相比国内的C ...
- CSDN 轻松周赛赛题:能否被8整除
轻松周赛赛题:能否被8整除 题目详情 给定一个非负整数,问能否重排它的全部数字,使得重排后的数能被8整除. 输入格式: 多组数据,每组数据是一个非负整数.非负整数的位数不超过10000位. 输出格式 ...
- O准备如何苟进复赛圈?华为软挑开挂指南(附赛题预测)
事先声明,这不是华为软挑的软广,我也不是海军. 这篇文章纯粹是心血来潮,原因是去年上传到github的参赛代码,前几天又有两个人star和fork了. 记得star热潮还是去年4月复赛刚结束的那几天, ...
- kaggle赛题Digit Recognizer:利用TensorFlow搭建神经网络(附上K邻近算法模型预测)
一.前言 kaggle上有传统的手写数字识别mnist的赛题,通过分类算法,将图片数据进行识别.mnist数据集里面,包含了42000张手写数字0到9的图片,每张图片为28*28=784的像素,所以整 ...
- 天池新闻推荐比赛1:赛题理解+baseline
天池新闻推荐比赛1:赛题理解+baseline 一.比赛信息 比赛链接: https://tianchi.aliyun.com/competition/entrance/531842/inform ...
- 攻防世界Web刷题记录(进阶区)
攻防世界Web刷题记录(进阶区) 1.baby_web 发现去掉URLhttp://111.200.241.244:51461/1.php后面的1.php,还是会跳转到http://111.200.2 ...
随机推荐
- spark-聚合算子aggregatebykey
spark-聚合算子aggregatebykey Aggregate the values of each key, using given combine functions and a neutr ...
- retrying failed action with response code: 403 错误解决
[2019-06-10T06:52:51,610][INFO ][logstash.outputs.elasticsearch] retrying failed action with respons ...
- msyql round函数隐藏问题
1.背景 在用mysql round进行四舍五入计算的时候如果参与计算的字段为float,则最终计算出的四舍五入效果会有很大出入.例子我就不列举了 2.原因 mysql官方文档中关于ROUND函数的部 ...
- javascript JSON.parse and JSON.stringify
var jstu = '{"name": "xiaoqiang", "age": 18}'; console.log(jstu); var ...
- const 与指针 的用法
请找出下面程序中有哪些错误: 1 2 3 4 5 6 7 8 9 10 11 12 13 int main() { int i=10; int j=1; const int *p1; ...
- JavaWeb_(Spring框架)在Struts+Hibernate框架中引入Spring框架
spring的功能:简单来说就是帮我们new对象,什么时候new对象好,什么时候销毁对象. 在MySQL中添加spring数据库,添加user表,并添加一条用户数据 使用struts + hibern ...
- mysql 日期字符串互转
字符串转日期select str_to_date('2008-4-2 15:3:28','%Y-%m-%d %H:%i:%s');select str_to_date('2008-08-09 08:9 ...
- 最小n个和(优先队列)
给出两个包含 nn 个整数的数组 AA,BB.分别在 AA, BB 中任意出一个数并且相加,可以得到 n^2n2个和.求这些和中最小的 nn 个. 输入格式输入第一行一个整数 n(1 \le n \l ...
- 预处理、const、static与sizeof-static全局变量与普通的全局变量有什么区别
1:全局变量的说明之前再加上static就构成了静态的全局变量.全局变量本身就是静态存储方式,静态全局变量当然也是静态存储方式.这两者在存储方式上并无不同.这两者的区别在于,非静态全局变量的作用域是整 ...
- Leetcode题目121.买卖股票的最佳时机(简单)
题目描述: 给定一个数组,它的第 i 个元素是一支给定股票第 i 天的价格. 如果你最多只允许完成一笔交易(即买入和卖出一支股票),设计一个算法来计算你所能获取的最大利润. 注意你不能在买入股票前卖出 ...