
DVWA学习记录 PartⅡ
Command Injection
1. 题目
Command Injection,即命令注入,是指通过提交恶意构造的参数破坏命令语句结构,从而达到执行恶意命令的目的。
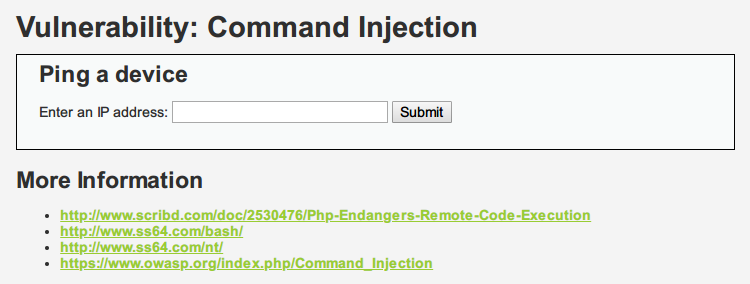
2. Low
a. 代码分析
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Get input

    $target = $_REQUEST[ 'ip' ];

    // Determine OS and execute the ping command.

    if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

        // Windows

        $cmd = shell_exec( 'ping  ' . $target );

    }

    else {

        // linux

        $cmd = shell_exec( 'ping  -c 4 ' . $target );

    }

    // Feedback for the end user

    echo "<pre>{$cmd}</pre>";

}

?>
stristr() 函数搜索字符串在另一字符串中的第一次出现,并返回字符串的剩余部分。
注释:该函数是二进制安全的。
注释:该函数是不区分大小写的。如需进行区分大小写的搜索,请使用 strstr() 函数。
php_uname ([ string $mode = "a" ] ) : string

    php_uname — 返回运行 PHP 的系统的有关信息

    'a':此为默认。包含序列 "s n r v m" 里的所有模式。

    's':操作系统名称。例如: FreeBSD。

    'n':主机名。例如: localhost.example.com。

    'r':版本名称,例如: 5.1.2-RELEASE。

    'v':版本信息。操作系统之间有很大的不同。

    'm':机器类型。例如:i386。
可以看到,服务器通过判断操作系统执行不同ping命令,但是对ip参数并未做任何的过滤,导致了严重的命令注入漏洞。
b. 漏洞利用
%0a 、%0d 、; 、& 、| 、&&、||均可用来执行多条命令
127.0.0.1&&net user
3. Medium
a. 代码分析
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Get input

    $target = $_REQUEST[ 'ip' ];

    // Set blacklist

    $substitutions = array(

        '&&' => '',

        ';'  => '',

    );

    // Remove any of the charactars in the array (blacklist).

    $target = str_replace( array_keys( $substitutions ), $substitutions, $target );

    // Determine OS and execute the ping command.

    if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

        // Windows

        $cmd = shell_exec( 'ping  ' . $target );

    }

    else {

        // linux

        $cmd = shell_exec( 'ping  -c 4 ' . $target );

    }

    // Feedback for the end user

    echo "<pre>{$cmd}</pre>";

}

?>
代码过滤了&&、;,仍有其他符号可以使用
b. 漏洞利用
127.0.0.1&net user
4. High
a. 代码分析
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Get input

    $target = trim($_REQUEST[ 'ip' ]);

    // Set blacklist

    $substitutions = array(

        '&'  => '',

        ';'  => '',

        '| ' => '',

        '-'  => '',

        '$'  => '',

        '('  => '',

        ')'  => '',

        '`'  => '',

        '||' => '',

    );

    // Remove any of the charactars in the array (blacklist).

    $target = str_replace( array_keys( $substitutions ), $substitutions, $target );

    // Determine OS and execute the ping command.

    if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

        // Windows

        $cmd = shell_exec( 'ping  ' . $target );

    }

    else {

        // *nix

        $cmd = shell_exec( 'ping  -c 4 ' . $target );

    }

    // Feedback for the end user

    echo "<pre>{$cmd}</pre>";

}

?>
相比Medium级别的代码,High级别的代码进一步完善了黑名单,但由于黑名单机制的局限性,我们依然可以绕过。
b. 漏洞利用
黑名单看似过滤了所有的非法字符,但仔细观察到是把|(空格) 替换为空字符,于是|成了“漏网之鱼”。
127.0.0.1|net user
5. impossible
a. 代码分析
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Check Anti-CSRF token

    checkToken( $_REQUEST[ 'user_token' ], $_SESSION[ 'session_token' ], 'index.php' );

    // Get input

    $target = $_REQUEST[ 'ip' ];

    $target = stripslashes( $target );

    // Split the IP into 4 octects

    $octet = explode( ".", $target );

    // Check IF each octet is an integer

    if( ( is_numeric( $octet[0] ) ) && ( is_numeric( $octet[1] ) ) && ( is_numeric( $octet[2] ) ) && ( is_numeric( $octet[3] ) ) && ( sizeof( $octet ) == 4 ) ) {

        // If all 4 octets are int's put the IP back together.

        $target = $octet[0] . '.' . $octet[1] . '.' . $octet[2] . '.' . $octet[3];

        // Determine OS and execute the ping command.

        if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

            // Windows

            $cmd = shell_exec( 'ping  ' . $target );

        }

        else {

            // linux

            $cmd = shell_exec( 'ping  -c 4 ' . $target );

        }

        // Feedback for the end user

        echo "<pre>{$cmd}</pre>";

    }

    else {

        // Ops. Let the user name theres a mistake

        echo '<pre>ERROR: You have entered an invalid IP.</pre>';

    }

}

// Generate Anti-CSRF token

generateSessionToken();

?>
相关函数介绍
stripslashes(string)
stripslashes函数会删除字符串string中的反斜杠,返回已剥离反斜杠的字符串。
explode(separator,string,limit)
把字符串打散为数组,返回字符串的数组。参数separator规定在哪里分割字符串,参数string是要分割的字符串,可选参数limit规定所返回的数组元素的数目。
is_numeric(string)
检测string是否为数字或数字字符串,如果是返回TRUE,否则返回FALSE。
可以看到,Impossible级别的代码加入了Anti-CSRF token,同时对参数ip进行了严格的限制,只有诸如“数字.数字.数字.数字”的输入才会被接收执行,因此不存在命令注入漏洞。
DVWA学习记录 PartⅡ的更多相关文章
- DVWA学习记录 PartⅦ
SQL Injection 1. 题目 SQL Injection,即SQL注入,是指攻击者通过注入恶意的SQL命令,破坏SQL查询语句的结构,从而达到执行恶意SQL语句的目的. 2. Low a. ...
- DVWA学习记录 PartⅤ
File Upload 1. 题目 File Upload,即文件上传漏洞,通常是由于对上传文件的类型.内容没有进行严格的过滤.检查,使得攻击者可以通过上传木马获取服务器的webshell权限,因此文 ...
- DVWA学习记录 PartⅣ
File Inclusion 1. 题目 File Inclusion,意思是文件包含(漏洞),是指当服务器开启allow_url_include选项时,就可以通过php的某些特性函数(include ...
- DVWA学习记录 PartⅢ
CSRF 1. 题目 CSRF,全称Cross-site request forgery,翻译过来就是跨站请求伪造,是指利用受害者尚未失效的身份认证信息(cookie.会话等),诱骗其点击恶意链接或者 ...
- DVWA学习记录 PartⅠ
DVWA介绍 DVWA(Damn Vulnerable Web Application)是一个用来进行安全脆弱性鉴定的PHP/MySQL Web应用,旨在为安全专业人员测试自己的专业技能和工具提供合法 ...
- DVWA学习记录 PartⅨ
XSS(DOM) 1. 题目 XSS,全称Cross Site Scripting,即跨站脚本攻击,某种意义上也是一种注入攻击,是指攻击者在页面中注入恶意的脚本代码,当受害者访问该页面时,恶意代码会在 ...
- DVWA学习记录 PartⅧ
Weak Session IDs 1. 题目 用户访问服务器的时候,为了区别多个用户,服务器都会给每一个用户分配一个 session id .用户拿到 session id 后就会保存到 cookie ...
- DVWA学习记录 PartⅥ
Insecure CAPTCHA 1. 题目 Insecure CAPTCHA(全自动区分计算机和人类的图灵测试),意思是不安全的验证码. 指在进行验证的过程中,出现了逻辑漏洞,导致验证码没有发挥其应 ...
- Quartz 学习记录1
原因 公司有一些批量定时任务可能需要在夜间执行,用的是quartz和spring batch两个框架.quartz是个定时任务框架,spring batch是个批处理框架. 虽然我自己的小玩意儿平时不 ...
随机推荐
- 一台电脑如何使用多个git账号?
git相信大家都在用,一般公司有一个账号,放公司自己架的服务器中,员工自己还有一个github或者gitee的账号,存放自己的一些私有代码.本篇文章总结一下,本人在公司开发机上,使用多个git账号的干 ...
- php使用json_encode中遇见问题?
注:php版本5.4下,不支持json_encode对中文的处理,要么升级php版本. json_encode($value,$options) 其中有2个比较常用到的参数: 1.JSON_UNESC ...
- [转] linux操作系统下c语言编程入门--基础知识
点击阅读原文 这篇文章介绍在LINUX下进行C语言编程所需要的基础知识.在这篇文章当中,我们将会学到以下内容: 1. 源程序编译 2. Makefile的编写 3. 程序库 ...
- @atcoder - CODE FESTIVAL 2017 Elimination Tournament Round 3 F@ Unicyclic Graph Counting
目录 @description@ @solution@ @accpeted code@ @details@ @description@ 求有多少 n 点 n 边的无向连通图,满足第 i 个点的度数为 ...
- Node.js 学习笔记(一)
node.js说白了就是JavaScript. node.js的性能是php的86倍(大概). 在下载完后可以用命令行打开及运行. 什么是 Web 服务器? Web服务器一般指网站服务器,是指驻留 ...
- CentOS7.5搭建Hadoop2.7.6完全分布式集群
一 完全分布式集群搭建 Hadoop官方地址:http://hadoop.apache.org/ 1 准备3台客户机 1.2 关闭防火墙,设置静态IP,主机名 关闭防火墙,设置静态IP,主机名此处略 ...
- matplotlib浅析
首先放出matplotlib的中英文文档: 中文:https://www.matplotlib.org.cn/ 英文:https://matplotlib.org/3.1.1/index.html M ...
- APP——python——自动化环境搭建01
前提:python以及pycharm安装完成. ---------------------------------------------------------------------------- ...
- .Net Core踩坑记:读取txt中文乱码
迁移.net framework的项目,有块读取txt中文转码的问题,普通的不能再普通的代码,想都没想直接copy过去,也没测,结果今天就被坑了.Core是3.1版本,这是原来的代码: string ...
- 06 . Jenkins分布式构建和Pipline
Pipline简介 pipline 是帮助 Jenkins 实现 CI 到 CD 转变的重要角色,是运行在 jenkins 2.X 版本的核心插件,简单来 说 Pipline 就是一套运行于 Jenk ...