
DVWA Command Injection 解析
命令注入,即 Command Injection。是指通过提交恶意构造的参数破坏命令语句结构,从而达到执行恶意命令的目的。
在Web应用中,有时候会用到一些命令执行的函数,如php中system、exec、shell_exec等,当对用户输入的命令没有进行限制或者过滤不严导致用户可以执行任意命令时,就会造成命令执行漏洞。
Low
服务端核心代码如下:
<?php

if( isset( $_POST[ 'submit' ] ) ) {

    $target = $_REQUEST[ 'ip' ];

    // Determine OS and execute the ping command.

    if (stristr(php_uname('s'), 'Windows NT')) {

        $cmd = shell_exec( 'ping  ' . $target );

        echo '<pre>'.$cmd.'</pre>';

    } else {

        $cmd = shell_exec( 'ping  -c 3 ' . $target );

        echo '<pre>'.$cmd.'</pre>';

    }

}

?>
函数首先判断环境下的系统,如果是win则执行第一个命令,若是linux执行的命令加上-c选项,以为linux中ping命令是一直执行的。只有加了-c指定发送的跳数才能停止。
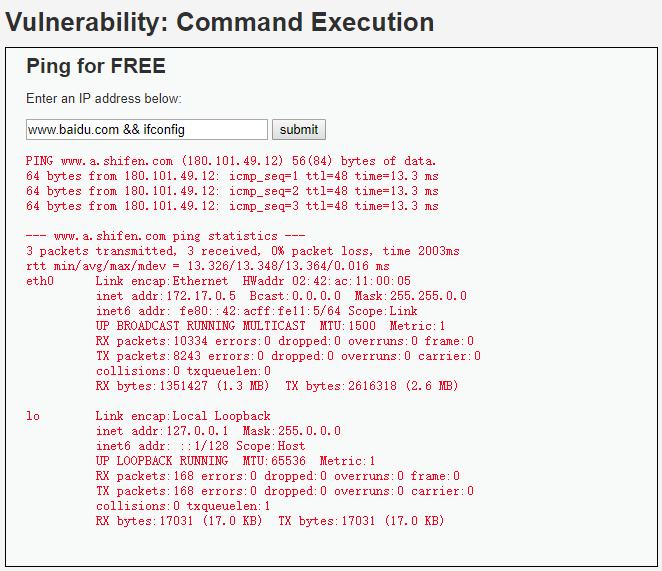
可以看到在接收用户输入的地方,对用户的输入没有做任何的处理。不难看出这就是一个典型的命令注入漏洞,输入恶意构造的语句 www.baidu.com && ifconfig会把后面的语句也一并执行,如果把命令换成其他恶意的攻击语句,就会造成严重后果
执行结果:
Medium
服务端核心代码如下:
<?php

if( isset( $_POST[ 'submit'] ) ) {

    $target = $_REQUEST[ 'ip' ];

    // Remove any of the charactars in the array (blacklist).

    $substitutions = array(

        '&&' => '',

        ';' => '',

    );

    $target = str_replace( array_keys( $substitutions ), $substitutions, $target );

    // Determine OS and execute the ping command.

    if (stristr(php_uname('s'), 'Windows NT')) {

        $cmd = shell_exec( 'ping  ' . $target );

        echo '<pre>'.$cmd.'</pre>';

    } else {

        $cmd = shell_exec( 'ping  -c 3 ' . $target );

        echo '<pre>'.$cmd.'</pre>';

    }

}

?>
Str_replace()函数的作用是以其他字符替换字符串中的一些字符(区分大小写)。
$target = str_replace( array_keys( $substitutions ), $substitutions, $target );将用户输入的内容,含有“&&”或“;”的替换为空。
其他的部分基本和low相差不大。
这里的源码对用户的输入进行了初步的过滤,过滤掉了一些能够同时执行命令的符号,但是我们知道,拥有同样作用的符号不止“&&”和“;”。所以依然可以进行命令注入。
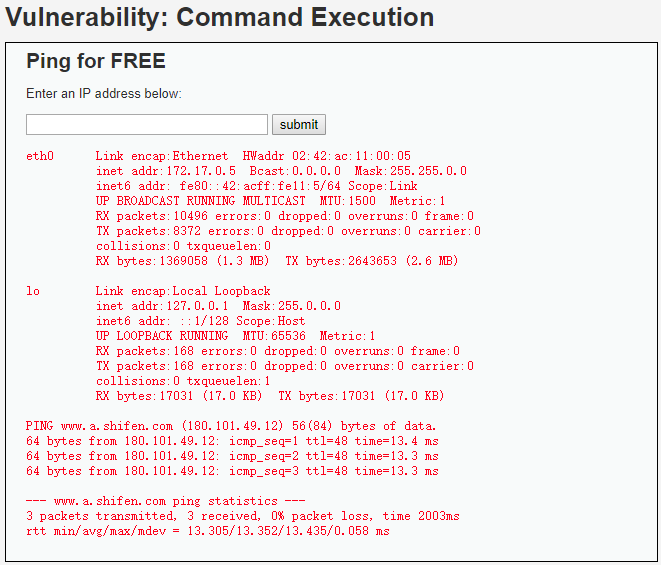
构造语句: www.baidu.com & ifconfig
& 是前面命令执行后,接着执行后面的命令
执行结果:
High
服务端核心代码如下:
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Get input

    $target = trim($_REQUEST[ 'ip' ]);

    // Set blacklist

    $substitutions = array(

        '&'  => '',

        ';'  => '',

        '| ' => '',

        '-'  => '',

        '$'  => '',

        '('  => '',

        ')'  => '',

        '`'  => '',

        '||' => '',

    );

    // Remove any of the charactars in the array (blacklist).

    $target = str_replace( array_keys( $substitutions ), $substitutions, $target );

    // Determine OS and execute the ping command.

    if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

        // Windows

        $cmd = shell_exec( 'ping  ' . $target );

    }

    else {

        // *nix

        $cmd = shell_exec( 'ping  -c 4 ' . $target );

    }

    // Feedback for the end user

    echo "<pre>{$cmd}</pre>";

}

?>
这个级别的源码和medium级别的源码相差不大,只是将更多的符号加入黑名单。通过这样的确实能够有效的防御之前的诸多思路。但是只是做黑名单的话,总是不够安全的,只要黑名单不够完整,就不是很安全。即使你认为名单已经很完整了。可能还有你不知道的存在可以利用。
黑名单看似过滤了所有的非法字符,但仔细观察到是把”| ”(注意这里|后有一个空格)替换为空字符,但是并没有过滤“|”。
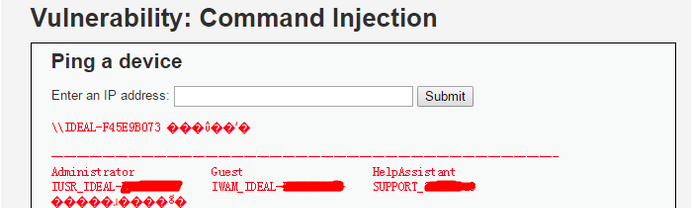
构造语句:127.0.0.1|net user
“|”是管道符,表示将Command 1的输出作为Command 2的输入,并且只打印Command 2执行的结果。
执行结果:
Impossible
服务端核心代码如下:
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Check Anti-CSRF token

    checkToken( $_REQUEST[ 'user_token' ], $_SESSION[ 'session_token' ], 'index.php' );

    // Get input

    $target = $_REQUEST[ 'ip' ];

    $target = stripslashes( $target );

    // Split the IP into 4 octects

    $octet = explode( ".", $target );

    // Check IF each octet is an integer

    if( ( is_numeric( $octet[0] ) ) && ( is_numeric( $octet[1] ) ) && ( is_numeric( $octet[2] ) ) && ( is_numeric( $octet[3] ) ) && ( sizeof( $octet ) == 4 ) ) {

        // If all 4 octets are int's put the IP back together.

        $target = $octet[0] . '.' . $octet[1] . '.' . $octet[2] . '.' . $octet[3];

        // Determine OS and execute the ping command.

        if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

            // Windows

            $cmd = shell_exec( 'ping  ' . $target );

        }

        else {

            // *nix

            $cmd = shell_exec( 'ping  -c 4 ' . $target );

        }

        // Feedback for the end user

        echo "<pre>{$cmd}</pre>";

    }

    else {

        // Ops. Let the user name theres a mistake

        echo '<pre>ERROR: You have entered an invalid IP.</pre>';

    }

}

// Generate Anti-CSRF token

generateSessionToken();

?>
stripslashes(string)
stripslashes函数会删除字符串string中的反斜杠,返回已剥离反斜杠的字符串。
explode(separator,string,limit)
把字符串打散为数组,返回字符串的数组。参数separator规定在哪里分割字符串,参数string是要分割的字符串,可选参数limit规定所返回的数组元素的数目。
is_numeric(string)
检测string是否为数字或数字字符串,如果是返回TRUE,否则返回FALSE。
可以看到,Impossible级别的代码加入了Anti-CSRF token,同时对参数ip进行了严格的限制,只有诸如“数字.数字.数字.数字”的输入才会被接收执行,因此不存在命令注入漏洞。
DVWA Command Injection 解析的更多相关文章
- DVWA Command Injection 通关教程
Command Injection 介绍 命令注入(Command Injection),对一些函数的参数没有做过滤或过滤不严导致的,可以执行系统或者应用指令(CMD命令或者bash命令)的一种注入攻 ...
- 安全性测试入门:DVWA系列研究(二):Command Injection命令行注入攻击和防御
本篇继续对于安全性测试话题,结合DVWA进行研习. Command Injection:命令注入攻击. 1. Command Injection命令注入 命令注入是通过在应用中执行宿主操作系统的命令, ...
- DVWA之命令注入(command injection)
Command injection就是指通过提交恶意构造的参数破坏命令语句结构,从而达到执行恶意命令的目的 LOW 无论是Windows还是Linux,都可以使用&&连接多个命令 执行 ...
- DVWA之Command Injection
Command Injection Command Injection,即命令注入,是指通过提交恶意构造的参数破坏命令语句结构,从而达到执行恶意命令的目的.PHP命令注入攻击漏洞是PHP应用程序中常见 ...
- DVWA靶场练习-Command Injection命令注入
Command Injection 原理 攻击者通过构造恶意参数,破坏命令的语句结构,从而达到执行恶意命令的目的.
- DVWA(四):Command Injection 全等级命令注入
Command Injection : 命令注入(Command Injection),对一些函数的参数没有做好过滤而导致用户可以控制输入的参数,使其恶意执行系统命令或这cmd.bash指令的一种注入 ...
- DVWA靶场之Command Injection(命令行注入)通关
Command Injection Low: <?php if( isset( $_POST[ 'Submit' ] ) ) { // Get input $target = $_REQUES ...
- Linux Command Line 解析
Linux Command Line 解析 0 处理模型 Linux kernel的启动包括很多组件的初始化和相关配置,这些配置参数一般是通过command line进行配置的.在进行后续分析之前,先 ...
- RT-SA-2019-005 Cisco RV320 Command Injection Retrieval
Advisory: Cisco RV320 Command Injection RedTeam Pentesting discovered a command injection vulnerabil ...
随机推荐
- in与exist , not in与not exist 的区别
in和exists in 是把外表和内表作hash 连接,而exists是对外表作loop循环,每次loop循环再对内表进行查询.一直以来认为exists比in效率高的说法是不准确的. ...
- [洛谷P4549] [模板] 裴蜀定理
18.10.03模拟赛T1. 出题人xcj(Mr.Handsome)十分良心,给了一道送分题...... 互测题好久没有出现送分题了.xcj真棒. 题目传送门 幸亏之前看过,否则真的是送分题都拿不到. ...
- URL与URI与URN的区别与联系
1.什么是URL? 统一资源定位符(或称统一资源定位器/定位地址.URL地址等[1],英语:Uniform Resource Locator,常缩写为URL),有时也被俗称为网页地址(网址).如同在网 ...
- Jenkins之邮件通知
Jenkins默认有一个邮件通知功能,但功能比较单一,能自定义的东西很少,一般使用Extended E-mail Notification插件来发送邮件,EXT Email插件功能比较多,但设置也比较 ...
- js编写trim()函数
1.js中本身是没有trim函数的,不过你可以自己写一个 function trim(str) { var newStr = str.replace(/^\s*$/g,'') retr ...
- Jmeter之Beanshell---使用Java处理JSON块
原文出处:https://www.cnblogs.com/xpp142857/p/7374281.html [环境] ①Jmeter版本:3.1,JDK:1.7 ②前置条件:将json.jar包置于. ...
- 【转载】python3安装scrapy之windows32位爬坑
python3安装scrapy之windows32位爬坑 原创 2016年11月06日 01:38:08 标签: scrapy / windows / python / 开源框架 / 网络爬虫 早 ...
- Selenium2自动化——初体验
一.Windows下的环境搭建 1.安装Python 访问Python官网:https://www.python.org/ 2.安装setuptools与pip setuptools是Python e ...
- 查漏补缺:Vector中去重
对于STL去重,可以使用<algorithm>中提供的unique()函数. unique()函数用于去除相邻元素中的重复元素(所以去重前需要对vector进行排序),只留下一个.返回去重 ...
- 强制迁移、合区 APP太强势伤害用户同时是否违法?
APP太强势伤害用户同时是否违法?" title="强制迁移.合区 APP太强势伤害用户同时是否违法?"> 对于经常混迹在国内各大手游的玩家来说,"合区& ...