
All about Using Burp Suite
1、how to use burpsuite
I can't thank them enough for allowing us to test web application ,making sure they are secure against threats . if you ues it another way ,all duty afford yousleves.
this version is 2.0.04 before load running ,you should function the key burp-loader-keygen-jas502n,because the authentic burpsuite not cheap , besids ,burp offers many options for only 350USD per year . we can use burp differentiate the real vulnerabilities from the false ones.
2、if you use the perburpSuite ,you can you commands : java -jar -Xmx2G /[path ]/[burp.jar] fireStart
3、Visualizing the application structure using Burp Suite
The Burpsuite offers the following function :
Visualize , Scope 、 Search the web hindder contents 、 lists comments 、scripts 、analyze 、report
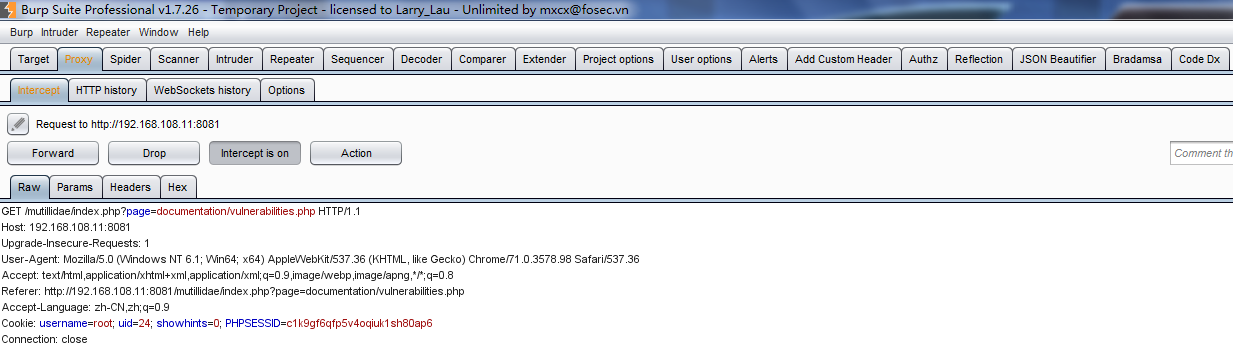
4、we can se the burp Proxy it as a man-in-the-middle between your browser and destination wen servers ,it let you intercept,inspect and modify the raw trafficc passing in the bouth directions.
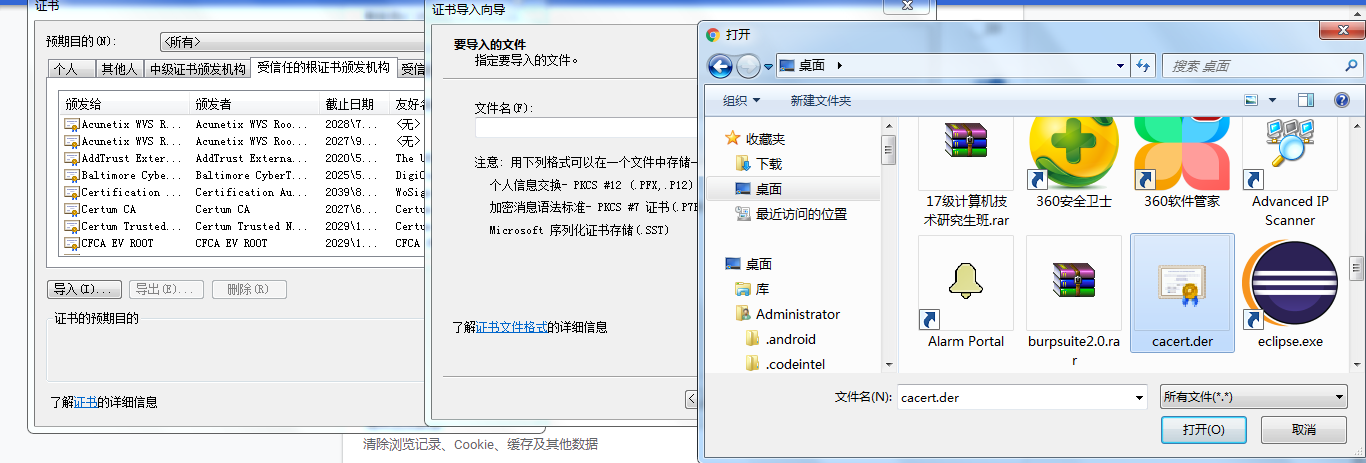
take notes: if you penetration with the https website you should install Burp's CA cerficate .an follow

5、Crawling the web application using Burp Splider
ususlly speaking Spider the website there is therr ways :
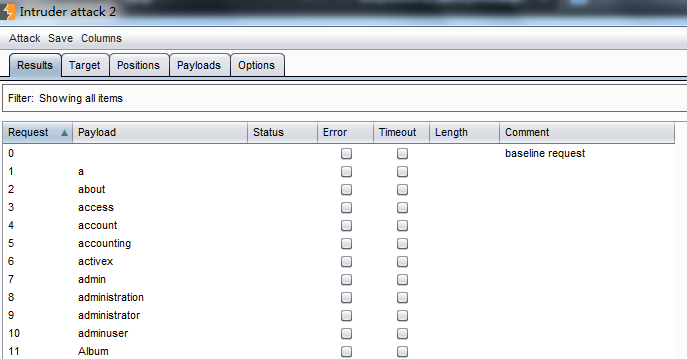
the first: Manually crawing by use the Intruder tool ; the second Automatically Crawing by use Spider ; finally use the Discover Content tool
if you want a manual as follow (the aims is to find intersting directions )
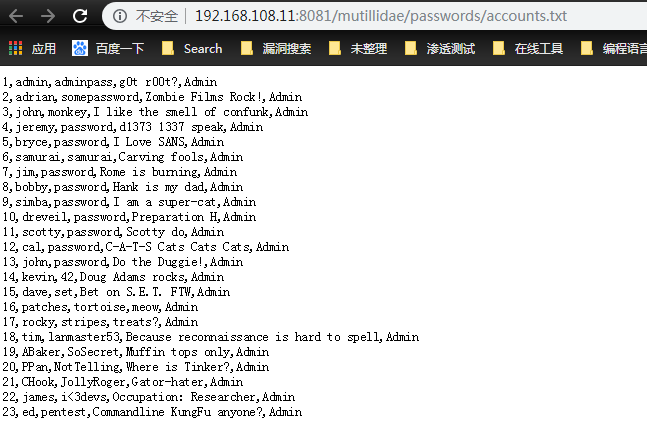
besides it , another way automated crawing and finding hidden spots,but ,you should be careful ,and it can cause the site to malfunction

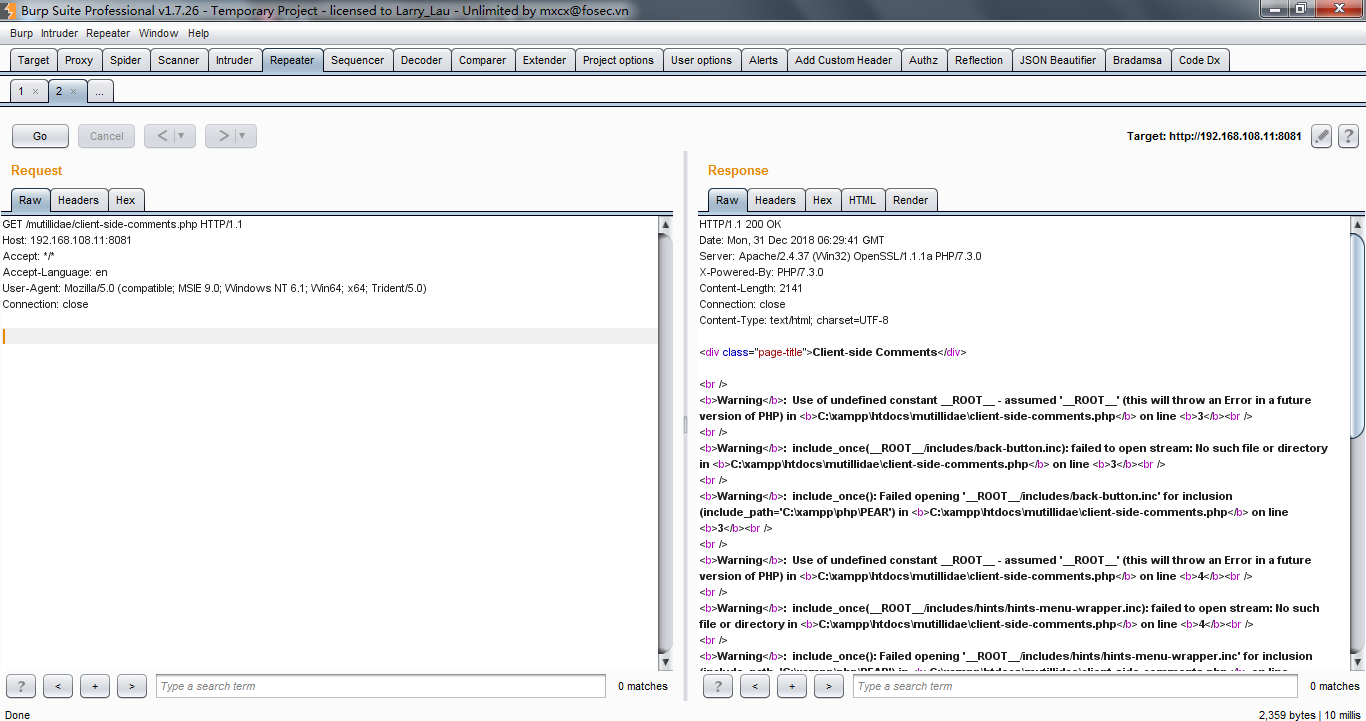
6、looking for the web vulnerablities using the Scanner,you can use the repeater to make sure that there's not a false positive
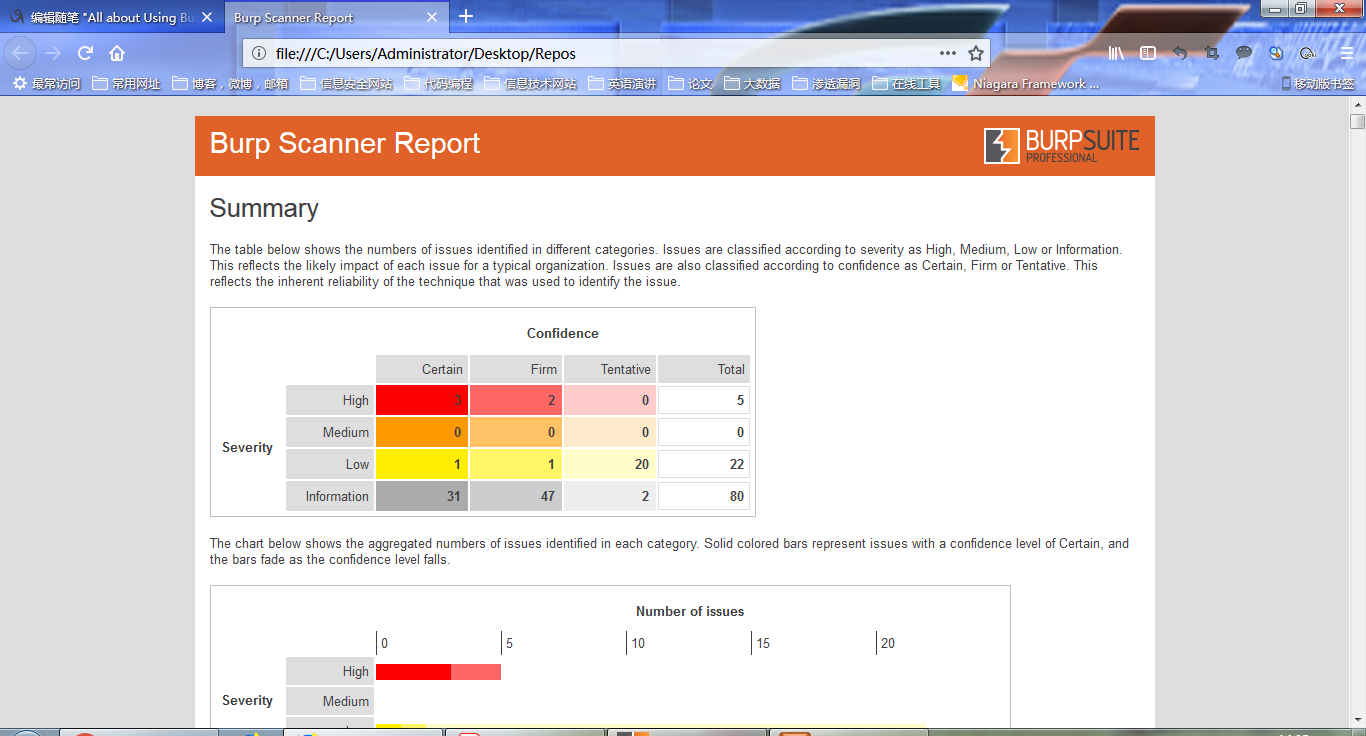
finally it's time to generate a report ,back the Target tab select the aim target host and selece issue,report the issue.
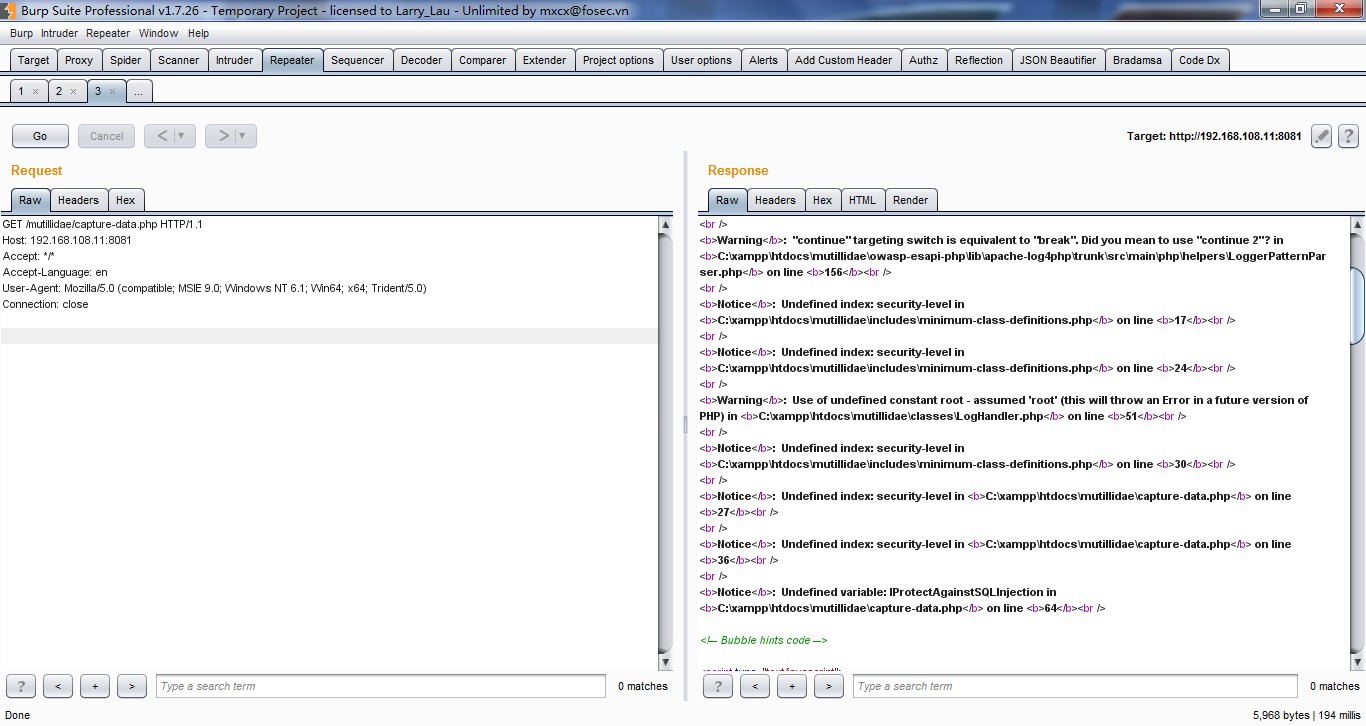
7、replaying web requests using the repeater tab
I usually check the parameter ,changing the parameter values (for example, testing input-based vulnerabilities )
8、Fuzzing web requesting using the Intruder tab
Brup inttruder use for automation and it can enumerate 、fuzz、and harvest data form the target web application . when i started using Burp ,the first thing that I lerned was to burp—force login credentials .
so let see the Intreder attack types:
Sniper ------> you can use it for only one payload ,you can use for fuzzing direction names.fuzzing the query string value,fuzzing the product name in the url
Battering Ram --------> this uses a single payload ,it alows sb palce the same payload into all defined position
Cluster bomb-------> this ones can use multiple payloads foe each position (maximum is 20 )
Pitchfork---------> this attack is used when an attack requries different ,but related, input to be inserted in multiple places in the request
9、installing third-party apps using Burp Extender
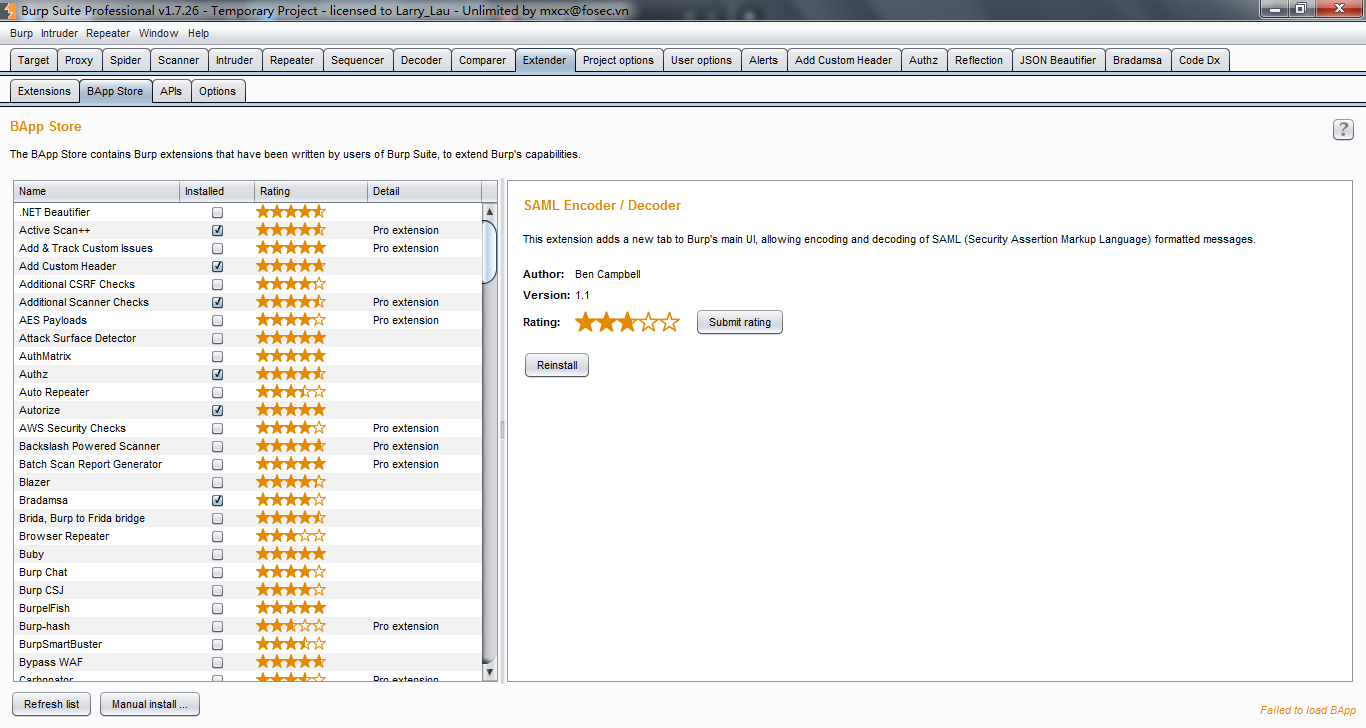
as this section if you use the proBurpSuite you can install third-party apps
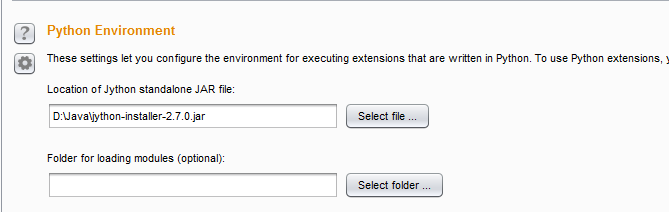
but before you install ,you need configure a library an follow,(Some of these libraries need to be turned over )
All about Using Burp Suite的更多相关文章
- Burp Suite新手指南
Burp Suite想必大家都用过,但是大家未必知道它的所有功能.因此,本文的主要目的就是尽量深入介绍各种功能.BurpSuite有以下这些功能: 截获代理– 让你审查修改浏览器和目标应用间的流量. ...
- Burp Suite使用详解一
本文由阿德马翻译自国外网站,请尊重劳动成果,转载注明出处 Burp Suite是Web应用程序测试的最佳工具之一,其多种功能可以帮我们执行各种任务.请求的拦截和修改,扫描web应用程序漏洞,以暴力破解 ...
- Burp Suite 使用教程(上传突破利器)
Burp Suite是一个免费的网站攻击工具. 它包括proxy.spider.intruder.repeater四项功能.该程序使用Java写成,需要 JRE 1.4 以上版本 下载该程序的源代码, ...
- 初识 Burp Suite
Burp Suite 是用于攻击web 应用程序的集成平台.它包含了许多工具,并为这些工具设计了许多接口,以促进加快攻击应用程序的过程. 所有的工具都共享一个能处理并显示HTTP 消息, ...
- 安卓APP测试之使用Burp Suite实现HTTPS抓包方法
APP的测试重点小部分在APP本身,大部分还是在网络通信上(单机版除外).所以在安卓APP测试过程中,网络抓包非常重要,一般来说,app开发会采用HTTP协议.Websocket.socket协议,一 ...
- burp suite 使用教程详解(外文翻译转)
Burp Suite是Web应用程序测试的最佳工具之一,其多种功能可以帮我们执行各种任务.请求的拦截和修改,扫描web应用程序漏洞,以暴力破解登陆表单,执行会话令牌等多种的随机性检查.本文将做一个Bu ...
- Burp Suite使用
Burp Suite是Web应用程序测试的最佳工具之一,其多种功能可以帮我们执行各种任务.请求的拦截和修改,扫描web应用程序漏洞,以暴力破解登陆表单,执行会话令牌等多种的随机性检查.本文将做一个Bu ...
- Burp Suite安装及详细使用教程-Intruder模块详解
01 介绍 安装要求: Java 的V1.5 + 安装( 推荐使用最新的JRE ), 可从这里免费 http://java.sun.com/j2se/downloads.html Burp Suite ...
- Burp Suite使用介绍
Burp Suite使用介绍(一) 22人收藏 收藏 2014/05/01 19:54 | 小乐天 | 工具收集 | 占个座先 Getting Started Burp Suite 是用于攻击web ...
- Burp Suite详细使用教程
Burp Suite详细使用教程-Intruder模块详解 最近迷上了burp suite 这个安全工具,百度了关于这个工具的教程还卖900rmb...ohno.本来准备买滴,但是大牛太高傲了,所以没 ...
随机推荐
- Linux 默认连接数
Linux 默认连接数 - 国内版 Binghttps://cn.bing.com/search?FORM=U227DF&PC=U227&q=Linux+%E9%BB%98%E8%AE ...
- SpringMVC整合freeMarker实现页面静态化+SpringMVC配置多视图
一.背景 1.什么是FreeMarker FreeMarker是一个模板引擎,一个基于模板生成文本输出的通用工具,使用纯Java编写 FreeMarker被设计用来生成HTML Web页面,特别是基于 ...
- jQuery 事件对象的属性
jQuery 在遵循 W3C 规范的情况下,对事件对象的常用属性进行了封装,使得事件处理在各大浏览器下都可以正常运行而不需要进行浏览器类型判断. (1) event.type 该方法的作用是可以获取到 ...
- $router和$route的区别
在路由跳转的时候除了用router-link标签以外需要在script标签在事件里面跳转,所以有个方法就是在script标签里面写this.$router.push('要跳转的路径名'), 在写的时候 ...
- Tensorflow 大规模数据集训练方法
本文转自:Tensorflow]超大规模数据集解决方案:通过线程来预取 原文地址:https://blog.csdn.net/mao_xiao_feng/article/details/7399178 ...
- springdata find立即加载 get延迟加载 get返回的是一个动态代理对象 特点是 用的时候才会查询 否则不查询
- java基础3之IO
流 流是一个很形象的概念,当程序需要读取数据的时候,就会开启一个通向数据源的流,这个数据源可以是文件,内存,或是网络连接.类似的,当程序需要写入数据的时候,就会开启一个通向目的地的流. 流的种类 字符 ...
- 在本机使用虚拟机安装一个linux系统,并搭建ftp服务器
一.Linux基础使用:linux服务器环境搭建(FTP服务器), 在本机使用虚拟机安装一个linux系统,并搭建ftp服务器,要求能使用ftp服务将本机文件到保存linux虚拟机上 资料: VMwa ...
- [十二省联考2019]异或粽子——可持久化trie树+堆
题目链接: [十二省联考2019]异或粽子 求前$k$大异或区间,可以发现$k$比较小,我们考虑找出每个区间. 为了快速得到一个区间的异或和,将原序列做前缀异或和. 对于每个点作为右端点时,我们维护出 ...
- 第六十四天 JS基础操作
一.分支结构 1.if语句 if基础语句 if(条件表达式){ 代码块: } // 当条件表达式结果为true,会执行代码块:反之不执行 // 条件表达式可以为普通表达式 // 0.undefined ...