
Spring Security验证流程剖析及自定义验证方法
Spring Security本质上是一连串的Filter, 然后又以一个独立的Filter的形式插入到Filter Chain里,其名为FilterChainProxy。 如图所示。
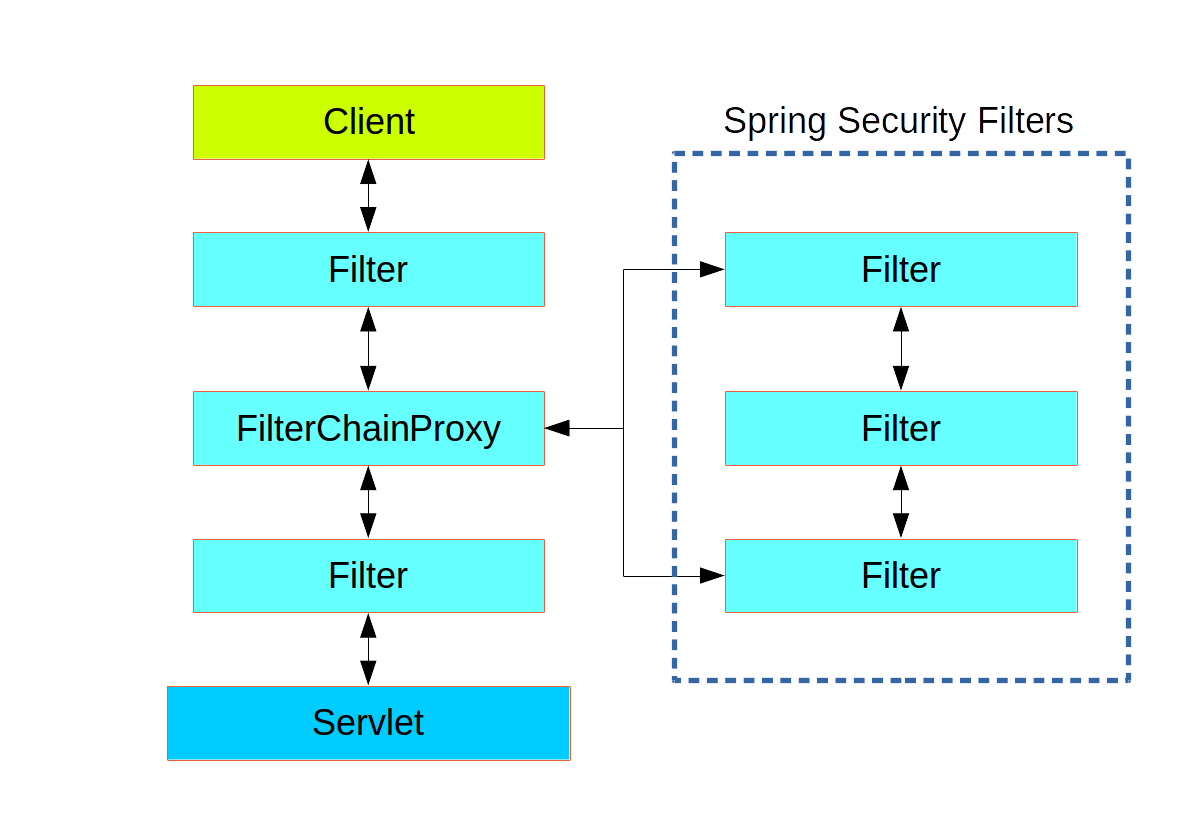
实际上FilterChainProxy下面可以有多条Filter Chain,来针对不同的URL做验证,而Filter Chain中所拥有的Filter则会根据定义的服务自动增减。所以无需要显示再定义这些Filter,除非想要实现自己的逻辑。

关键类
Authentication
Authentication是一个接口,用来表示用户认证信息,在用户登录认证之前相关信息会封装为一个Authentication具体实现类的对象,在登录认证成功之后又会生成一个信息更全面,包含用户权限等信息的Authentication对象,然后把它保存在 SecurityContextHolder所持有的SecurityContext中,供后续的程序进行调用,如访问权限的鉴定等。
AuthenticationManager
用来做验证的最主要的接口为AuthenticationManager,这个接口只有一个方法:
public interface AuthenticationManager {

  Authentication authenticate(Authentication authentication)

    throws AuthenticationException;

}
其中authenticate()方法运行后可能会有三种情况:
- 验证成功,返回一个带有用户信息的
Authentication。 - 验证失败,抛出一个
AuthenticationException异常。 - 无法判断,返回
null。
ProviderManager
ProviderManager是上面的AuthenticationManager最常见的实现,它不自己处理验证,而是将验证委托给其所配置的AuthenticationProvider列表,然后会依次调用每一个 AuthenticationProvider进行认证,这个过程中只要有一个AuthenticationProvider验证成功,就不会再继续做更多验证,会直接以该认证结果作为ProviderManager的认证结果。

认证过程
- 用户使用用户名和密码进行登录。
Spring Security将获取到的用户名和密码封装成一个Authentication接口的实现类,比如常用的UsernamePasswordAuthenticationToken。- 将上述产生的
Authentication对象传递给AuthenticationManager的实现类ProviderManager进行认证。 ProviderManager依次调用各个AuthenticationProvider进行认证,认证成功后返回一个封装了用户权限等信息的Authentication对象。- 将
AuthenticationManager返回的Authentication对象赋予给当前的SecurityContext。
自定义验证
有了以上的知识储备后就可以来自定义验证方法了。通过上面可以看出,实际上真正来做验证操作的是一个个的AuthenticationProvider,所以如果要自定义验证方法,只需要实现一个自己的AuthenticationProvider然后再将其添加进ProviderManager里就行了。
自定义AuthenticationProvider
@Component

public class CustomAuthenticationProvider

  implements AuthenticationProvider {

    @Override

    public Authentication authenticate(Authentication authentication)

      throws AuthenticationException {

        String name = authentication.getName();

        String password = authentication.getCredentials().toString();

        if (shouldAuthenticateAgainstThirdPartySystem()) {

            // use the credentials

            // and authenticate against the third-party system

            return new UsernamePasswordAuthenticationToken(

              name, password, new ArrayList<>());

        } else {

            return null;

        }

    }

    @Override

    public boolean supports(Class<?> authentication) {

        return authentication.equals(

          UsernamePasswordAuthenticationToken.class);

    }

}
其中的supports()方法接受一个authentication参数,用来判断传进来的authentication是不是该AuthenticationProvider能够处理的类型。
注册AuthenticationProvider
现在再将刚创建的AuthenticationProvider在与ProviderManager里注册,所有操作就完成了。
@Configuration

@EnableWebSecurity

@ComponentScan("org.baeldung.security")

public class SecurityConfig extends WebSecurityConfigurerAdapter {

    @Autowired

    private CustomAuthenticationProvider authProvider;

    @Override

    protected void configure(

      AuthenticationManagerBuilder auth) throws Exception {

        auth.authenticationProvider(authProvider);

    }

    @Override

    protected void configure(HttpSecurity http) throws Exception {

        http.authorizeRequests().anyRequest().authenticated()

            .and()

            .httpBasic();

    }

}
参考资料
Spring Security验证流程剖析及自定义验证方法的更多相关文章
- Spring Security入门(2-3)Spring Security 的运行原理 4 - 自定义登录方法和页面
参考链接,多谢作者: http://blog.csdn.net/lee353086/article/details/52586916 http元素下的form-login元素是用来定义表单登录信息的. ...
- spring boot集成mybatis-plus插件进行自定义sql方法开发时报nested exception is org.apache.ibatis.binding.BindingException: Invalid bound statement (not found):
spring boot集成mybatis-plus插件进行自定义sql方法开发时报nested exception is org.apache.ibatis.binding.BindingExcept ...
- Spring Security框架下Restful Token的验证方案
项目使用Restful的规范,权限内容的访问,考虑使用Token验证的权限解决方案. 验证方案(简要概括): 首先,用户需要登陆,成功登陆后返回一个Token串: 然后用户访问有权限的内容时需要上传T ...
- spring security使用hibernate进行查询数据库验证
前面查询数据库采用的都是jdbc方式,如果系统使用的是hibernate,该如何进行呢,下面就是实现步骤,关键还是实现自定义的UserDetailsService 项目结构如下: 使用hibernat ...
- Spring Security OAuth2之resource_id配置与验证
一.resource_id的作用 Spring Security OAuth2 架构上分为Authorization Server认证服务器和Resource Server资源服务器.我们可以为每一个 ...
- Spring Security认证流程分析--练气后期
写在前面 在前一篇文章中,我们介绍了如何配置spring security的自定义认证页面,以及前后端分离场景下如何获取spring security的CSRF Token.在这一篇文章中我们将来分析 ...
- Spring Security OAuth2 微服务认证中心自定义授权模式扩展以及常见登录认证场景下的应用实战
一. 前言 [APP 移动端]Spring Security OAuth2 手机短信验证码模式 [微信小程序]Spring Security OAuth2 微信授权模式 [管理系统]Spring Se ...
- 03 spring security执行流程分析
spring security主要是依赖一系列的Filter来实现权限验证的,责任链设计模式是跑不了的.下面简单记录一下spring操作这些Filter的过程. 1. WebSecurityConfi ...
- 【权限管理】Spring Security 执行流程
转自:https://blog.csdn.net/weixin_37689658/article/details/92752890 1.基本配置使用 (1)创建配置类 创建一个配置类SecurityC ...
随机推荐
- Using Custom Domains With IIS Express In Asp.Net Core
IIS Express是一个Mini版的IIS,能够支持所有的Web开发任务,但是这种设计有一些缺陷,例如只能通过localhost:<port>的方式来访问我们的应用程序,看起来就有点不 ...
- HBase Filter及对应Shell--转
http://www.cnblogs.com/skyl/p/4807793.html 比较运算符 CompareFilter.CompareOp比较运算符用于定义比较关系,可以有以下几类值供选择: E ...
- 如何解决Linux 系统下 ifconfig 命令无网络接口 ens33
今天我在做Redis的哨兵集群模式的时候,以前都是好的,也不知道从什么时候开始就无法连接Redis服务器了,就是运行如下命令,没有效果:redis-server redis.conf,然后在通过命令查 ...
- HDU [P1704] Rank
传递闭包裸题 但是本题的Floyd一定要优化,不然会T cpp #include <iostream> #include <cstdio> #include <cstri ...
- win2012 配置wamp的若干错误
转自群友 VC2015.VC14 在 Windows 2012 R2 安装失败,0x80240017 - 未指定的错误,解决办法据朋友反应VC2013一样存在这个问题--查资料说是没有安装 KB299 ...
- ettercap+urlsnarf+driftnet+wireshark监听妹子上网
搞事肯定得确认目标.所以我们得先确认一个目标 确认目标这种事情不多说. 1.开启IP转发 echo 1 > /proc/sys/net/ipv4/ip_forward 然后ettercap ...
- 豹哥嵌入式好讲堂:ARM Cortex-M调试过程探析(1)- 4线接口标准(JTAG)
大家好,我是豹哥,猎豹的豹,犀利哥的哥.今天豹哥给大家讲的是嵌入式调试里的接口标准JTAG. 在结束<ARM Cortex-M开发文件详解>系列文章之后,豹哥修整了一小段时间,但是讲课的心 ...
- Go基础之--排序和查找操作
排序操作主要都在sort包中,导入就可以使用了import("sort") 常用的操作 sort.Ints:对整数进行排序sort.Strings:对字符串进行排序sort.Flo ...
- javaweb重定向的两种方式
第一种 import java.io.IOException; import javax.servlet.ServletException; import javax.servlet.http.Htt ...
- 升级gitlab
https://gitlab.com/gitlab-org/gitlab-ce/tree/master/doc/update https://about.gitlab.com/update/#cent ...