
Centos7 防火墙常用配置及说明
一、 Centos7和Centos6 防火墙的区别:
使用的工具不一样了。Centos6 使用的是iptables ,Centos7 使用的是filewall
iptables 用于过滤数据包,属于网络层防火墙。
firewall 能够允许哪些服务可用,那些端口可用...属于更高一层的防火墙。
二、常用命令:
vi /usr/lib/firewalld/services/ssh.xml
vi /usr/lib/firewalld/services/html.xml
systemctl enable firewalld.service
systemctl restart firewalld.service
firewall-cmd --state
firewall-cmd --list-all
firewall-cmd --zone=public --permanent --add-port=8502/tcp
vi /etc/firewalld/zones/public.xml
<port protocol="tcp" port="8502"/>
systemctl restart firewalld.service
三、firewall 配置
The configuration for firewalld is stored in various XML files
in /usr/lib/firewalld and /etc/firewalld
注意:以下firewalld 的操作只有重启之后才有效:service firewalld restart
1、系统配置目录
/usr/lib/firewalld/services
目录中存放定义好的网络服务和端口参数,系统参数,不能修改。

2、用户配置目录
/etc/firewalld/
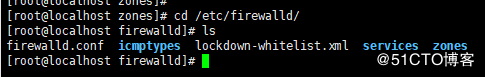
3、如何自定义添加端口
用户可以通过修改配置文件的方式添加端口,也可以通过命令的方式添加端口,注意:修改的内容会在/etc/firewalld/目录下的配置文件中体现。
3.1 、命令的方式添加端口:
firwall-cmd --permanent --add-port=9527/tcp
参数介绍:
1、firwall-cmd:是Linux提供的操作firewall的一个工具;2、--permanent:表示设置为持久;3、--add-port:标识添加的端口;
另外,firewall中有Zone的概念,可以将具体的端口制定到具体的zone配置文件中。
例如:添加8010端口
firewall-cmd --zone=public --permanent --add-port=8010/tcp
--zone=public:指定的zone为public;
如果–zone=dmz 这样设置的话,会在dmz.xml文件中新增一条。
l 3.2、修改配置文件的方式添加端口
<?xml version="1.0" encoding="utf-8"?>

<zone>

<short>Public</short>

<description>For use in public areas.</description>
<rule family="ipv4">
  <source address="122.10.70.234"/>
  <port protocol="udp" port="514"/>
  <accept/>
</rule>

<rule family="ipv4">

  <source address="123.60.255.14"/>

  <port protocol="tcp" port="10050-10051"/>

  <accept/>

</rule>

<rule family="ipv4">

  <source address="192.249.87.114"/> 放通指定ip,指定端口、协议

  <port protocol="tcp" port="80"/>

  <accept/>

</rule>

<rule family="ipv4"> 放通任意ip访问服务器的9527端口

  <port protocol="tcp" port="9527"/>

  <accept/>

</rule>

</zone>
上述的一个配置文件可以很好的看出:
1、添加需要的规则,开放通源ip为122.10.70.234,端口514,协议tcp; 2、开放通源ip为123.60.255.14,端口10050-10051,协议tcp;/3、开放通源ip为任意,端口9527,协议tcp;
四、firewall常用命令
1、重启、关闭、开启、firewalld.serverice 服务
Service firewalld restart 重启
Service firewalld start 开启
Service firewalld stop 关闭
systemctl status firewalld
systemctl stop firewalld 关闭
systemctl start firewalld 开启
systemctl restart firewalld 重启
systemctl disable firewalld 关闭开机启动
2、查看状态
firewall-cmd --state
3、查看防火墙规则
firewall-cmd --list-all
五、Centos 切换为iptables防火墙
切换到iptables首先应该关掉默认的firewalld,然后安装iptables服务。
1、关闭firewall:
service firewalld stop systemctl disable firewalld.service #禁止firewall开机启动
2、安装iptables防火墙
yum install iptables-services #安装
3、编辑iptables防火墙配置
vi /etc/sysconfig/iptables #编辑防火墙配置文件
下边是一个完整的配置文件:
Firewall configuration written by system-config-firewall  Manual customization of this file is not recommended.

*filter  :INPUT ACCEPT [0:0]  :FORWARD ACCEPT [0:0]  :OUTPUT ACCEPT [0:0]

-A INPUT -m state --state ESTABLISHED,RELATED -j ACCEPT

-A INPUT -p icmp -j ACCEPT  -A INPUT -i lo -j ACCEPT

-A INPUT -m state --state NEW -m tcp -p tcp --dport 22 -j ACCEPT

-A INPUT -m state --state NEW -m tcp -p tcp --dport 80 -j ACCEPT

-A INPUT -m state --state NEW -m tcp -p tcp --dport 3306 -j ACCEPT

-A INPUT -j REJECT --reject-with icmp-host-prohibited

-A FORWARD -j REJECT --reject-with icmp-host-prohibited

COMMIT
:wq! #保存退出
service iptables start #开启systemctl enable iptables.service #设置防火墙开机启动
Centos7 防火墙常用配置及说明的更多相关文章
- centOS7.2防火墙常用配置(转)
centOS7.2防火墙常用配置 firewall-cmd --state #查看默认防火墙状态(关闭后显示not running,开启后显示running) systemctl stop fir ...
- Ubuntu 防火墙常用配置操作(ufw)【适用于 Debian 及其衍生版---Linux Mint、Deepin 等】-转
Ubuntu 防火墙常用配置操作(ufw)[适用于 Debian 及其衍生版---Linux Mint.Deepin 等] 点击访问
- Iptables 防火墙常用配置
转至:https://blog.csdn.net/lswzw/article/details/87971259 Iptables 防火墙常用配置 概念 命令行模式 查看 & 命令 -n:直接显 ...
- Centos7防火墙常用命令
有些人安装的linux的系统默认防火墙不是iptables,而是firewall,那就得使用以下方式关闭防火墙了. >>>关闭防火墙 systemctl stop firewalld ...
- iptables防火墙常用配置介绍
参考地址 http://www.cnblogs.com/metoy/p/4320813.html http://netfilter.org/ iptables http://man.chinaunix ...
- Centos7 防火墙firewalld配置
开启80端口 firewall-cmd --zone=public --add-port=80/tcp --permanent 出现success表明添加成功 移除某个端口 firewall-cmd ...
- Centos7防火墙常用命令及mask锁定不能添加端口问题
一.开放端口 sudo firewall-cmd --zone=public --add-port=3000/tcp --permanent sudo firewall-cmd --reload 二. ...
- Centos7 防火墙常用命令 开启 关闭防火墙
如果你的系统上没有安装使用命令安装 #yum install firewalld //安装firewalld 防火墙 开启服务 # systemctl start firewalld.service ...
- Centos7下常用配置命令
1.禁用ipv6 Step 1: add this rule in /etc/sysctl.conf : net.ipv6.conf.all.disable_ipv6=1 Step 2: add th ...
随机推荐
- zabbix 添加被监控主机
点击 configured > host > create host 主机名:输入主机名,允许使用字母数字,空格,点,破折号和下划线 组:从右侧选择框中选择一个或多个组,然后单击 « 将其 ...
- C++构造函数初始化列表与构造函数中的赋值的区别
C++类中成员变量的初始化有两种方式:构造函数初始化列表和构造函数体内赋值. 一.内部数据类型(char,int……指针等) class Animal { public: Animal(int wei ...
- VC++ 使用attributes定义接口
1.定义预处理命令_ATL_ATTRIBUTES 2.在一个全局的Cpp文件里面配置module的attribute [module(dll, uuid = "{3845951F-15B ...
- Revit API创建标注NewTag
start ; ) { eId = item; } ...
- svn与git操作对比 (未来有空做一个 svn与git实战对比 )
svn是集中式的,git是分布式的,但是我们日常使用的都是按照集中式唯一服务器仓库的方式来去做的,最终我们的代码都要提交到一个唯一仓库中. 他们最大的区别是本地工作拷贝的工作方式不同, 一.svn本地 ...
- 如何用C#动态编译、执行代码
在开始之前,先熟悉几个类及部分属性.方法:CSharpCodeProvider.ICodeCompiler.CompilerParameters.CompilerResults.Assembly. 一 ...
- Spark2.2(三十三):Spark Streaming和Spark Structured Streaming更新broadcast总结(一)
背景: 需要在spark2.2.0更新broadcast中的内容,网上也搜索了不少文章,都在讲解spark streaming中如何更新,但没有spark structured streaming更新 ...
- Mysql高效插入/更新数据
从tushare抓取到的财务数据,最开始只是想存下来,用的办法想简单点,是:插入--报错-update 但发现这个方法太蠢,异常会导致大量无效连接,改为: for idx,row in d2.iter ...
- 如何用 async 控制流程
来自: http://larry850806.github.io/2016/05/31/async/ [Javascript] 如何用 async 控制流程 (一) 31 May 2016 async ...
- Android系统资源图标android.R.drawable
Android™ 2.1 android.R.drawable Icon Resources Android™ 1.5 android.R.drawable Icon Resources Androi ...