
ShiroFilterFactoryBean分析
创建核心Filter
同其他框架一样,都有个切入点,这个核心Filter就是拦截所有请求的。
通过web.xml中配置的Filer进入,执行init方法获取这个instance,调用下面的createInstance方法创建核心Filter:
protected AbstractShiroFilter createInstance() throws Exception {

    log.debug("Creating Shiro Filter instance.");

    SecurityManager securityManager = getSecurityManager();

    if (securityManager == null) {

        String msg = "SecurityManager property must be set.";

        throw new BeanInitializationException(msg);

    }

    if (!(securityManager instanceof WebSecurityManager)) {

        String msg = "The security manager does not implement the WebSecurityManager interface.";

        throw new BeanInitializationException(msg);

    }

    FilterChainManager manager = createFilterChainManager();

    //Expose the constructed FilterChainManager by first wrapping it in a

    // FilterChainResolver implementation. The AbstractShiroFilter implementations

    // do not know about FilterChainManagers - only resolvers:

    PathMatchingFilterChainResolver chainResolver = new PathMatchingFilterChainResolver();

    chainResolver.setFilterChainManager(manager);

    //Now create a concrete ShiroFilter instance and apply the acquired SecurityManager and built

    //FilterChainResolver.  It doesn't matter that the instance is an anonymous inner class

    //here - we're just using it because it is a concrete AbstractShiroFilter instance that accepts

    //injection of the SecurityManager and FilterChainResolver:

    return new SpringShiroFilter((WebSecurityManager) securityManager, chainResolver);

}
createFilterChainManager方法比较重要,包含以下必要操作:
DefaultFilterChainManager对象的创建
defaultFilters的获取和相关url的填充
自定义filters的获取和相关url的填充
获取FilterChainDefinitionMap (这个就是配置文件中的filterChainDefinitions的映射关系)
- 对url和权限的映射关系作处理
默认的DefaultFilter枚举中包含以下filter类:
anon(AnonymousFilter.class),

authc(FormAuthenticationFilter.class),

authcBasic(BasicHttpAuthenticationFilter.class),

logout(LogoutFilter.class),

noSessionCreation(NoSessionCreationFilter.class),

perms(PermissionsAuthorizationFilter.class),

port(PortFilter.class),

rest(HttpMethodPermissionFilter.class),

roles(RolesAuthorizationFilter.class),

ssl(SslFilter.class),

user(UserFilter.class);
执行doFilter方法
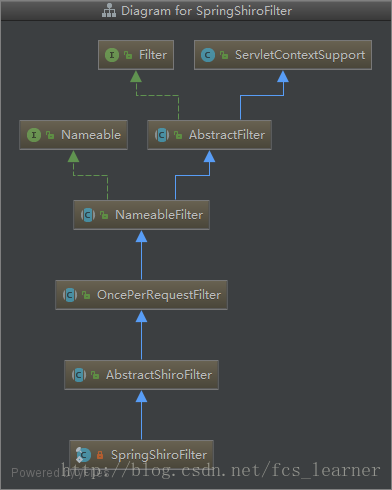
看下内部类 SpringShiroFilter:
private static final class SpringShiroFilter extends AbstractShiroFilter {

    protected SpringShiroFilter(WebSecurityManager webSecurityManager, FilterChainResolver resolver) {

        super();

        if (webSecurityManager == null) {

            throw new IllegalArgumentException("WebSecurityManager property cannot be null.");

        }

        setSecurityManager(webSecurityManager);

        if (resolver != null) {

            setFilterChainResolver(resolver);

        }

    }

}
在org.apache.shiro.web.servlet.OncePerRequestFilter中实现了doFilter方法:
public final void doFilter(ServletRequest request, ServletResponse response, FilterChain filterChain)

        throws ServletException, IOException {

    String alreadyFilteredAttributeName = getAlreadyFilteredAttributeName();

    if ( request.getAttribute(alreadyFilteredAttributeName) != null ) {

        log.trace("Filter '{}' already executed.  Proceeding without invoking this filter.", getName());

        filterChain.doFilter(request, response);

    } else //noinspection deprecation

        if (/* added in 1.2: */ !isEnabled(request, response) ||

            /* retain backwards compatibility: */ shouldNotFilter(request) ) {

        log.debug("Filter '{}' is not enabled for the current request.  Proceeding without invoking this filter.",

                getName());

        filterChain.doFilter(request, response);

    } else {

        // Do invoke this filter...

        log.trace("Filter '{}' not yet executed.  Executing now.", getName());

        request.setAttribute(alreadyFilteredAttributeName, Boolean.TRUE);

        try {

            doFilterInternal(request, response, filterChain);

        } finally {

            // Once the request has finished, we're done and we don't

            // need to mark as 'already filtered' any more.

            request.removeAttribute(alreadyFilteredAttributeName);

        }

    }

}
三种情况,分为两条路线:
1. filterChain.doFilter(request, response); 直接放行
2. doFilterInternal(request, response, filterChain); 走子类实现
在org.apache.shiro.web.servlet.AbstractShiroFilter实现doFilterInternal:
protected void doFilterInternal(ServletRequest servletRequest, ServletResponse servletResponse, final FilterChain chain)

        throws ServletException, IOException {

    Throwable t = null;

    try {

        final ServletRequest request = prepareServletRequest(servletRequest, servletResponse, chain);

        final ServletResponse response = prepareServletResponse(request, servletResponse, chain);

        final Subject subject = createSubject(request, response);

        //noinspection unchecked

        subject.execute(new Callable() {

            public Object call() throws Exception {

                updateSessionLastAccessTime(request, response);

                executeChain(request, response, chain);

                return null;

            }

        });

    } catch (ExecutionException ex) {

        t = ex.getCause();

    } catch (Throwable throwable) {

        t = throwable;

    }

    if (t != null) {

        if (t instanceof ServletException) {

            throw (ServletException) t;

        }

        if (t instanceof IOException) {

            throw (IOException) t;

        }

        //otherwise it's not one of the two exceptions expected by the filter method signature - wrap it in one:

        String msg = "Filtered request failed.";

        throw new ServletException(msg, t);

    }

}
将HttpServletRequest和HttpServletResponse包装成shiro自己的ShiroHttpServletRequest和ShiroHttpServletResponse。
利用包装后的对象创建Subject。
然后是执行subject的execute的方法。
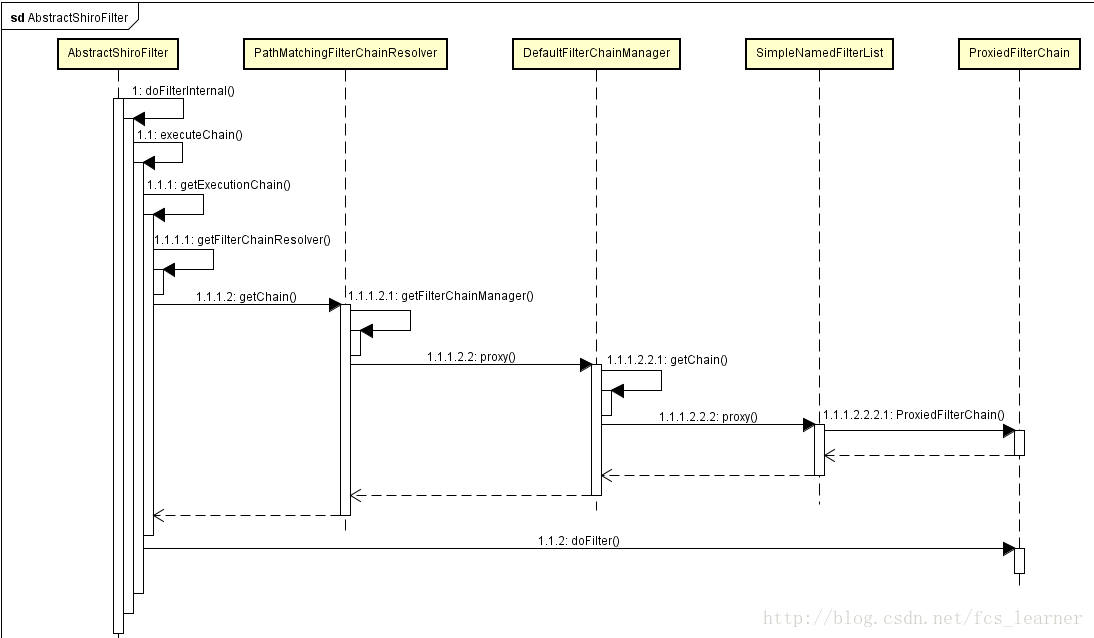
protected void executeChain(ServletRequest request, ServletResponse response, FilterChain origChain)

        throws IOException, ServletException {

    FilterChain chain = getExecutionChain(request, response, origChain);

    chain.doFilter(request, response);

}
获取的FilterChain是一个代理的ProxiedFilterChain,持有自己的Filter集合,重写doFilter方法:取自己持有的Filter集合,一个个执行其doFilter方法,当所有的Filter都执行完后,再执行servlet的FilterChain。
后面的过程就是一个原始的FilterChain的执行过程。
可以想象,原生的Filter链似乎也是这样一个执行过程,遍历web.xml中配置的所有Filter。
整个过程就是代理模式的运用。
ShiroFilterFactoryBean分析的更多相关文章
- shiro实现无状态的会话,带源码分析
转载请在页首明显处注明作者与出处 朱小杰 http://www.cnblogs.com/zhuxiaojie/p/7809767.html 一:说明 在网上都找不到相关的信息,还是翻了大半天 ...
- Spring-shiro源码陶冶-DelegatingFilterProxy和ShiroFilterFactoryBean
阅读源码有助于陶冶情操,本文旨在简单的分析shiro在Spring中的使用 简单介绍 Shiro是一个强大易用的Java安全框架,提供了认证.授权.加密和会话管理等功能 web.xml配置Shiro环 ...
- Shiro源码分析
1.入口类:AbstractAuthenticator 用户输入的登录信息经过其authenticate方法: public final AuthenticationInfo authenticate ...
- Shiro的Filter机制详解---源码分析
Shiro的Filter机制详解 首先从spring-shiro.xml的filter配置说起,先回答两个问题: 1, 为什么相同url规则,后面定义的会覆盖前面定义的(执行的时候只执行最后一个). ...
- Shiro的Filter机制详解---源码分析(转)
Shiro的Filter机制详解 首先从spring-shiro.xml的filter配置说起,先回答两个问题: 1, 为什么相同url规则,后面定义的会覆盖前面定义的(执行的时候只执行最后一个). ...
- alias导致virtualenv异常的分析和解法
title: alias导致virtualenv异常的分析和解法 toc: true comments: true date: 2016-06-27 23:40:56 tags: [OS X, ZSH ...
- 火焰图分析openresty性能瓶颈
注:本文操作基于CentOS 系统 准备工作 用wget从https://sourceware.org/systemtap/ftp/releases/下载最新版的systemtap.tar.gz压缩包 ...
- 一起来玩echarts系列(一)------箱线图的分析与绘制
一.箱线图 Box-plot 箱线图一般被用作显示数据分散情况.具体是计算一组数据的中位数.25%分位数.75%分位数.上边界.下边界,来将数据从大到小排列,直观展示数据整体的分布情况. 大部分正常数 ...
- 应用工具 .NET Portability Analyzer 分析迁移dotnet core
大多数开发人员更喜欢一次性编写好业务逻辑代码,以后再重用这些代码.与构建不同的应用以面向多个平台相比,这种方法更加容易.如果您创建与 .NET Core 兼容的.NET 标准库,那么现在比以往任何时候 ...
随机推荐
- 51Nod 1344 走格子 | 贪心
Input示例 5 1 -2 -1 3 4 Output示例 2 贪心 #include <bits/stdc++.h> using namespace std; typedef long ...
- vijos 1655 萌萌的糖果博弈 博弈
背景 用糖果来引诱小朋友学习是最常用的手法,绵羊爸爸就是用糖果来引诱萌萌学习博弈的. 描述 他把糖果分成了两堆,一堆有A粒,另一堆有B粒.他让萌萌和他一起按照下面的规则取糖果:每次可以任意拿走其中一堆 ...
- LightOJ 1340 - Story of Tomisu Ghost 阶乘分解素因子
http://www.lightoj.com/volume_showproblem.php?problem=1340 题意:问n!在b进制下至少有t个后缀零,求最大的b. 思路:很容易想到一个数通过分 ...
- Codeforces Round #380 (Div. 2)/729B Spotlights 水题
Theater stage is a rectangular field of size n × m. The director gave you the stage's plan which act ...
- [洛谷P3460] [POI2007]TET-Tetris Attack
洛谷题目链接:[POI2007]TET-Tetris Attack 题目描述 A puzzle called "Tetris Attack" has lately become a ...
- PowerDesigner16 用例图
用例图主要用来描述角色以及角色与用例之间的连接关系.说明的是谁要使用系统,以及他们使用该系统可以做些什么.一个用例图包含了多个模型元素,如系统.参与者和用例,并且显示这些元素之间的各种关系,如泛化.关 ...
- [cerc2012][Gym100624B]20181013
- 如何设计一个优雅健壮的Android WebView?(上)
转:如何设计一个优雅健壮的Android WebView?(上) 前言 Android应用层的开发有几大模块,其中WebView是最重要的模块之一.网上能够搜索到的WebView资料可谓寥寥,Gith ...
- 【洛谷 P1073】 最优贸易 (Tarjan缩点+拓扑排序)
题目链接 先\(Tarjan\)缩点,记录每个环内的最大值和最小值. 然后跑拓扑排序,\(Min[u]\)表示到\(u\)的最小值,\(ans[u]\)表示到\(u\)的答案,\(Min\)和\(an ...
- 【转】png文件格式
前言 我们都知道,在进行J2ME的手机应用程序开发的时候,在图片的使用上,我们可以使用PNG格式的图片(甚至于在有的手机上,我们只可以使用PNG 格式的图片),尽管使用图片可以为我们的应用程序增加不少 ...