
OD: Exploit Me - Overwrite Nearby Varible
实验代码:
 #include<stdio.h>

 #include<string.h>

 #define PASSWORD "1234567"

 int verify_password(char *password)

 {

     int authenticated;

     char buffer[];     // add local buf to be overflowed

     authenticated=strcmp(password,PASSWORD);

     strcpy(buffer, password);  // overflow here

     return authenticated;

 }

 int main()

 {

     int valid_flag=;

     char password[];

     while(){

         printf("Please input password: ");

         scanf("%s",password);

         valid_flag=verify_password(password);

         if(valid_flag){

             printf("Incorrect password!\n\n");

         }

         else

         {

             printf("Congratulation! You have passed the verification!\n\n\n");

             break;

         }

     }

     return ;

 }
注意以上第 8 行和第 10 行的代码,对于猜测变量在内存的相对位置和溢出尝试有用。
栈帧
程序执行到 int verify_password(char *password) 时的栈帧如图:
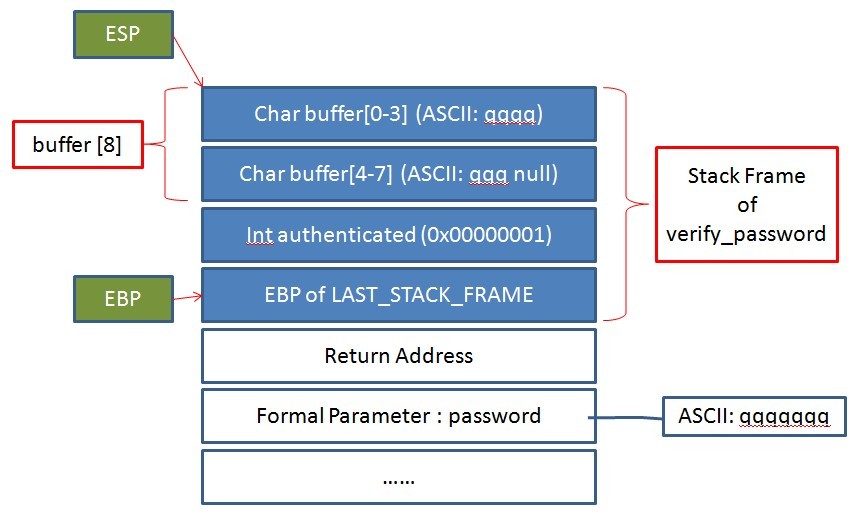
(变量在内存中的位置可能因编译优化而与上图不一致)
可见 authenticated (int 类型,内存中为 DWORD,占 4 字节)恰在 buffer 的 “下方”,如果 buffer 越界,那么 buffer[8..11] 刚好能覆盖 authenticated !
如果输入的字符超过 7 个字符(null 会占第 8 个字符),则越界字符会覆盖 authenticated。若 authenticated 被覆盖为 0,则溢出成功。
TIPS:用 OllyDBG 调试时可在栈区用【右键→Go to EBP】快速定位当前的 EBP,如图:
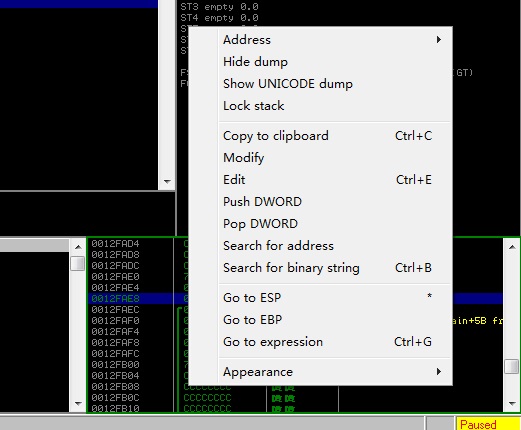
TIPS:用 OllyDBG 调试时可用 F2 设置断点。
OllyDbg 调试可见,输入 8 位密码 12345678,当程序执行完第 10 行后,authenticated 的值恰好被 password 的第九位字符串结束符 \0 覆盖为 0x00000000
但需注意 authenticated 的值来源于第 9 行的 strcpy,如果输入的密码是 01234567,则 strcpy 返回 -1,authenticated 为 -1 的补码 0xFFFFFFFF,此时溢出后不能欺骗成功。
OD: Exploit Me - Overwrite Nearby Varible的更多相关文章
- OD: Exploit Me - Overwrite Return Address
修改邻接变量的方法对代码环境限制比较多,更通用.更强大的方法是修改 EBP.返回地址等状态值. 为了方便调试,修改之前的代码如下: #include<stdio.h> #include&l ...
- OD: Exploit Me - Inject Instruction
修改之前的代码: #include<stdio.h> #include<stdlib.h> #include<string.h> #include<windo ...
- OD: Shellcode / Exploit & DLL Trampolining
看到第五章了. 标题中 Dll Tramplining(跳板)名字是从如下地址找到的,写的很好: http://en.wikipedia.org/wiki/Buffer_overflow#The_ju ...
- OD: Kernel Exploit - 2 Programming
本节接前方,对 exploitme.sys 进行利用. exploitme.sys 存在任意地址写任意内容的内核漏洞,现在采用执行 Ring0 Shellcode 的方式进行利用. 获取 HalDis ...
- OD: Kernel Exploit - 1
第 22 章,内核漏洞利用技术 首先编写具有漏洞的驱动 exploitme.sys,再展开内核漏洞利用思路和方法: /***************************************** ...
- OD: Heap Exploit : DWORD Shooting & Opcode Injecting
堆块分配时的任意地址写入攻击原理 堆管理系统的三类操作:分配.释放.合并,归根到底都是对堆块链表的修改.如果能伪造链表结点的指针,那么在链表装卸的过程中就有可能获得读写内存的机会.堆溢出利用的精髓就是 ...
- struts2 CVE-2012-0392 S2-008 Strict DMI does not work correctly allows remote command execution and arbitrary file overwrite
catalog . Description . Effected Scope . Exploit Analysis . Principle Of Vulnerability . Patch Fix 1 ...
- gdb windbg and od use
gdb aslr -- 显示/设置 gdb 的 ASLR asmsearch -- Search for ASM instructions in memory asmsearch "int ...
- An iOS zero-click radio proximity exploit odyssey
NOTE: This specific issue was fixed before the launch of Privacy-Preserving Contact Tracing in iOS 1 ...
随机推荐
- oracle单行函数之通用函数
NVL (a,b) --当a=null时,返回b,否则返回a NVL2 (a, b, c) -- 当a=null时,返回c,否则返回b NULLIF (expr1, expr2) --当a=b时,返回 ...
- gui界面2048小游戏
坑的地方 JLabel色块要调透明 方向键要用press方法 主界面 package game; import java.awt.BorderLayout; import java.awt.Event ...
- C#操作Excel开发报表系列整理(转)
C#操作Excel进行报表开发系列共写了七篇,也已经有很久没有新东西了,现在整理一下,方便以后查阅,如果有写新的,会同时更新.需要注意的是因为Office的版本不同,实际的代码可能会有所不同,但是都是 ...
- 微软office MIME类型
后缀 MIME 類型 .docx application/vnd.openxmlformats-officedocument.wordprocessingml.document .docm app ...
- hql 多表查询
sql 单表/多表查询去除重复记录单表distinct多表group by select h from Hytxbz as h,Tgbzk as t where h.hytxbzid=t.hytxbz ...
- ioctl函数,可以获取ip地址,修改ip地址,网卡地址等
部分转自http://www.cnblogs.com/zht-blog/p/4025903.html #include <sys/types.h>#include <sys/sock ...
- c#使用UIA进行模拟点击操作
之前,我写过一篇c#使用spy进行模拟操作的文章,有朋友在留言中提到了UIA进行操作,今天也使用UIA重新实现一次对vnc窗体的控制测试. 实现目标 在server框内填入192.168.2.200 ...
- android反编译工具 ApkDec-Release-0.1
(1 )使用帮助 1. 选择 all 全部编译内容包括jar .xml .及其他资源文件 2. 选择 jar 只反编译并打成jar 包 3. 反编译后你可以使用jd-gui.ex ...
- 获取Map API Key
开发人员在基于Google Maps服务进行开发之前,需要申请一组验证过的Map API Key,这样才可以使用Google Maps服务.申请过程如下:1.在Eclipse中打开“Window”|“ ...
- BaseFragment
public abstract class BaseFragment extends Fragment { public FragmentActivity mActivity; /** * 此方法可以 ...