
ASP.net MVC 基于角色的权限控制系统的实现
一、引言
我们都知道ASP.net mvc权限控制都是实现AuthorizeAttribute类的OnAuthorization方法。
下面是最常见的实现方式:
 public class CustomAuthorizeAttribute : AuthorizeAttribute

    {

        public override void OnAuthorization(AuthorizationContext filterContext)

        {

           if (!filterContext.RequestContext.HttpContext.Request.IsAuthenticated)

            {

                filterContext.Result = new RedirectToRouteResult(new RouteValueDictionary(new { controller = "account", action = "login", returnUrl = filterContext.HttpContext.Request.Url, returnMessage = "您无权查看." }));

                return;

            }

          base.OnAuthorization(filterContext);

        }

}
然后在需要验证的Action上打上[CustomAuthorize]标签就可以了。
这种方式是比较粗粒度的解决方案,由于是已经将定义好(约定好的)权限hard code带对应的Action上,所以无法实现用户自定义权限控制。
看一下代码:
using System;

using System.Collections.Generic;

using System.Linq;

using System.Web;

using System.Web.Mvc;

namespace Deepleo.Role.Controllers

{

    public class UserController : Controller

    {

        [UserAuthorize]

        public ActionResult Index()

        {

            return View();

        }

       [AdminAuthorize]

        public ActionResult Admin()

        {

            return View();

        }

        [UserAuthorize]

        public ActionResult Detail()

        {

            return View();

        }

    }

}
我们有一个UserController,他有3个Action:Index,Admin,Detail.其中Admin需要系统管理员权限,其他两个值需要User权限。这样就需要建立AdminAuthorizeAttribute和UserAuthorizeAttribute.这样做就无法实现用户自定义权限。
二、基于角色的权限控制系统
基于角色的权限控制系统RBAC(Role Based Access Control)是目前最流行,也是最通用的权限控制系统。
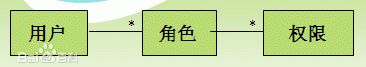
对于ASP.NET MVC来说,这套系统很容易实现:Controller下的每一个Action可以看作是一个权限,角色就相当于多个权限的组合。
然后我们新建一个RoleAuthorizeAttribute,即对角色的属性描述。
2.1 如何鉴权
这个RoleAuthorizeAttribute的关键在于如何拿到ControllerName和ActionName,查阅msdn其实很容易就实现了,不多说,直接上代码:
using System;

using System.Collections.Generic;

using System.Linq;

using System.Web;

using System.Web.Security;

using System.Web.Mvc;

using System.Web.Routing;

using Deepleo.Role.Services;

namespace Deepleo.Role.Attributes

{

    public class RoleAuthorizeAttribute : AuthorizeAttribute

    {

        public override void OnAuthorization(AuthorizationContext filterContext)

        {

            var isAuth = false;

            if (!filterContext.RequestContext.HttpContext.Request.IsAuthenticated)

            {

                isAuth = false;

            }

            else

            {

                if (filterContext.RequestContext.HttpContext.User.Identity != null)

                {

                    var roleService = new RoleService();

                    var actionDescriptor = filterContext.ActionDescriptor;

                    var controllerDescriptor = actionDescriptor.ControllerDescriptor;

                    var controller = controllerDescriptor.ControllerName;

                    var action = actionDescriptor.ActionName;

                    var ticket = (filterContext.RequestContext.HttpContext.User.Identity as FormsIdentity).Ticket;

                    var role = roleService.GetById(ticket.Version);

                    if (role != null)

                    {

                        isAuth = role.Permissions.Any(x => x.Permission.Controller.ToLower() == controller.ToLower() && x.Permission.Action.ToLower() == action.ToLower());

                    }

                }

            }

            if (!isAuth)

            {

                filterContext.Result = new RedirectToRouteResult(new RouteValueDictionary(new { controller = "account", action = "login", returnUrl = filterContext.HttpContext.Request.Url, returnMessage = "您无权查看." }));

                return;

            }

            else

            {

                base.OnAuthorization(filterContext);

            }

        }

    }

}
注意:这里用Ticket的Version存储RoleId(最好不要这样,原因看我的另一篇博文:http://www.cnblogs.com/deepleo/p/iso_cookies_formsAuthenticationTicket_version.html)。你也可以用其他方式。
主要是用到了 filterContext.ActionDescriptor和filterContext.ActionDescriptor。
2.2 如何生成权限控制列表
前面的role.Permissions的集合已经是定义好的权限列表。
Permissions类的定义如下:
using System;

using System.Collections.Generic;

using System.Linq;

using System.Text;

namespace Deepleo.Role.Entities

{

    public class PermissionDefinition

    {

        public virtual int Id

        {

            set;

            get;

        }

        public virtual int ActionNo

        {

            set;

            get;

        }

        public virtual int ControllerNo

        {

            set;

            get;

        }

        public virtual string Name

        {

            set;

            get;

        }

        public virtual string ControllerName

        {

            set;

            get;

        }

        public virtual string Controller

        {

            set;

            get;

        }

        public virtual string Action

        {

            set;

            get;

        }

        public virtual DateTime AddDate

        {

            set;

            get;

        }

    }

}
属性Controller和Action记录的是权限,ControllerName和ActionName用于显示UI,ControllerNo和ActionNo用于显示顺序控制。
这里你可以手工将所有Action录入数据库中,然后实现RolService即可。但是显然这种方法实在是太笨了,我们其实可以用反射+Attribute机制实现自动化载入权限控制表。原理很简单,我就直接上关键代码了。
以下是反射的代码:
using System;

using System.Collections.Generic;

using System.Linq;

using System.Web;

using System.Web.Mvc;

using Deepleo.Role.Services;

using Deepleo.Role.Attributes;

using Deepleo.Role.Entities;

namespace Deepleo.Role.Controllers

{

    public class InstallController : Controller

    {

        public ActionResult Index()

        {

            return View();

        }

        [HttpPost]

        public ActionResult Index()

        {

            try

            {

                var roleService = new RoleService();

                #region init permission

                createPermission(new UserController());

                #endregion

                var allDefinedPermissions = roleService.GetDefinedPermissions();

                #region 超级管理员角色初始化

                var adminPermissions = new List<RolePermissionInfo>();

                foreach (var d in allDefinedPermissions)

                {

                    adminPermissions.Add(new RolePermissionInfo { AddDate = DateTime.Now, Permission = d, });

                }

                int adminRoleId = roleService.AddRole(new Entities.RoleInfo

                {

                    AddDate = DateTime.Now,

                    Description = "",

                    Name = "超级管理员",

                    Permissions = adminPermissions

                });

                #endregion

                return RedirectToAction("Admin", "User");

            }

            catch (Exception ex)

            {

                ModelState.AddModelError("", ex.Message);

                return View();

            }

        }

        private void createPermission(Controller customController)

        {

            var roleService = new RoleService();

            var controllerName = "";

            var controller = ""; var controllerNo = ;

            var actionName = ""; var action = ""; var actionNo = ;

            var controllerDesc = new KeyValuePair<string, int>();

            var controllerType = customController.GetType();

            controller = controllerType.Name.Replace("Controller", "");//remobe controller posfix

            controllerDesc = getdesc(controllerType);

            if (!string.IsNullOrEmpty(controllerDesc.Key))

            {

                controllerName = controllerDesc.Key;

                controllerNo = controllerDesc.Value;

                foreach (var m in controllerType.GetMethods())

                {

                    var mDesc = getPropertyDesc(m);

                    if (string.IsNullOrEmpty(mDesc.Key)) continue;

                    action = m.Name;

                    actionName = mDesc.Key;

                    actionNo = mDesc.Value;

                    roleService.CreatePermissions(actionNo, controllerNo, actionName, controllerName, controller, action);

                }

            }

        }

        private KeyValuePair<string, int> getdesc(Type type)

        {

            var descriptionAttribute = (DescriptionAttribute)(type.GetCustomAttributes(false).FirstOrDefault(x => x is DescriptionAttribute));

            if (descriptionAttribute == null) return new KeyValuePair<string, int>();

            return new KeyValuePair<string, int>(descriptionAttribute.Name, descriptionAttribute.No);

        }

        private KeyValuePair<string, int> getPropertyDesc(System.Reflection.MethodInfo type)

        {

            var descriptionAttribute = (DescriptionAttribute)(type.GetCustomAttributes(false).FirstOrDefault(x => x is DescriptionAttribute));

            if (descriptionAttribute == null) return new KeyValuePair<string, int>();

            return new KeyValuePair<string, int>(descriptionAttribute.Name, descriptionAttribute.No);

        }

    }

}
以下是DescriptionAttribute的代码:
using System;

using System.Collections.Generic;

using System.Linq;

using System.Web;

namespace Deepleo.Role.Attributes

{

    public class DescriptionAttribute : Attribute

    {

        public string Name

        {

            set;

            get;

        }

        public int No

        {

            set;

            get;

        }

    }

}
然后在UserController打上DescriptionAttribute标签就可以了,如下所示:
using System;

using System.Collections.Generic;

using System.Linq;

using System.Web;

using System.Web.Mvc;

using Deepleo.Role.Attributes;

namespace Deepleo.Role.Controllers

{

    [Description(No = , Name = "用户")]

    public class UserController : Controller

    {

        [RoleAuthorize]

        [Description(No = , Name = "用户首页")]

        public ActionResult Index()

        {

            return View();

        }

        [RoleAuthorize]

        [Description(No = , Name = "用户管理")]

        public ActionResult Admin()

        {

            return View();

        }

        [RoleAuthorize]

        [Description(No = , Name = "用户详情")]

        public ActionResult Detail()

        {

            return View();

        }

    }

}
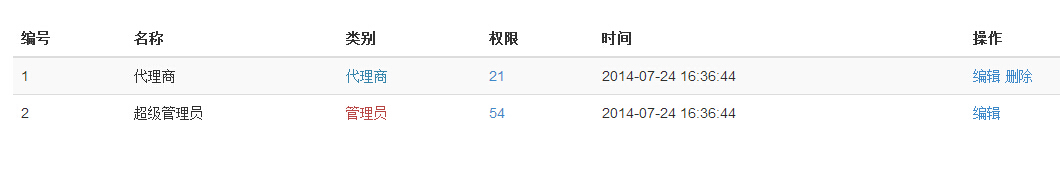
这样在网站安装的时候直接执行Install就可以完全自动化创建权限。
这样就可以精确到每个Action的用户自定义权限控制了。
看看我的劳动成果:

写在最后:对于同名的Action的HttpGET和HttpPOST分成两个权限还没有实现。比如说:New[HttpGet],和New[HttpPOST]。主要是觉得这样没有太大的意义,当然如果你的业务需求必须这样,我觉得应该很容易就能扩展。
完整代码下载:http://files.cnblogs.com/deepleo/RoleSolution.rar
PS:代码只有关键代码,没有实现RoleService方法,请自行根据自己的实际情况实现。
ASP.net MVC 基于角色的权限控制系统的实现的更多相关文章
- ASP.NET MVC 基于角色的权限控制系统的示例教程
上一次在 .NET MVC 用户权限管理示例教程中讲解了ASP.NET MVC 通过AuthorizeAttribute类的OnAuthorization方法讲解了粗粒度控制权限的方法,接下来讲解基于 ...
- 基于角色的权限控制系统(role-based access control)
role-based access control(rbac),指对于不同角色的用户,拥有不同的权限 .用户对应一个角色,一个角色拥有若干权限,形成用户-角色-权限的关系,如下图所示.当一个用户进行访 ...
- ASP.NET MVC 基于页面的权限管理
菜单表 namespace AspNetMvcAuthDemo1.Models { public class PermissionItem { public int ID { set; get; } ...
- MVC基于角色权限控制--数据库设计
在网站后台设计过程中都会遇上权限控制这一问题 当前较为流行的解决方案是基于角色的权限管理 基本思路如下 分别建立 用户信息表.角色信息表.权限信息表 让用户和角色关联,角色和权限关联,当用户访问时,通 ...
- Asp.net core IdentityServer4与传统基于角色的权限系统的集成
写在前面 因为最近在忙别的,好久没水文了 今天来水一篇: 在学习或者做权限系统技术选型的过程中,经常有朋友有这样的疑问 : "IdentityServer4的能不能做到与传统基于角色的权限系 ...
- FineAdmin.Mvc 使用ok-admin+ASP.NET MVC搭建的通用权限后台管理系统
FineAdmin.Mvc 介绍 使用ok-admin+ASP.NET MVC搭建的通用权限后台管理系统RightControl后台layui模板不太好看,换成ok-admin v2.0重写一遍.项目 ...
- ASP.NET MVC基于标注特性的Model验证:将ValidationAttribute应用到参数上
原文:ASP.NET MVC基于标注特性的Model验证:将ValidationAttribute应用到参数上 ASP.NET MVC默认采用基于标准特性的Model验证机制,但是只有应用在Model ...
- ASP.NET MVC基于标注特性的Model验证:一个Model,多种验证规则
原文:ASP.NET MVC基于标注特性的Model验证:一个Model,多种验证规则 对于Model验证,理想的设计应该是场景驱动的,而不是Model(类型)驱动的,也就是对于同一个Model对象, ...
- C 实现基于角色的权限系统
本文demo下载地址:http://www.wisdomdd.cn/Wisdom/resource/articleDetail.htm?resourceId=1068 实例使用C# 实现基于角色的权限 ...
随机推荐
- Leetcode 659.分割数组为连续子序列
分割数组为连续子序列 输入一个按升序排序的整数数组(可能包含重复数字),你需要将它们分割成几个子序列,其中每个子序列至少包含三个连续整数.返回你是否能做出这样的分割? 示例 1: 输入: [1,2,3 ...
- Spring 笔记(四)AOP
前言 横切关注点 使用 @AspectJ 定义切面. 同时还需要在配置类上应用 @EnableAspectJAutoProxy 注解,启用 AOP 自动代理.(不添加它的话,@AspectJ 注解的类 ...
- HDU 4109 Instrction Arrangement(DAG上的最长路)
把点编号改成1-N,加一点0,从0点到之前任意入度为0的点之间连一条边权为0的边,求0点到所有点的最长路. SPFA模板留底用 #include <cstdio> #include < ...
- PHP路径相关 dirname,realpath,__FILE__
比如:程序根目录在:E:\wamp\www 中 1. __FILE__ 当前文件的绝对路径 如果在index.php中调用 则返回 E:\wamp\www\index.php 下面再看一 ...
- 201621123034 《Java程序设计》第7周学习总结
作业07-Java GUI编程 1. 本周学习总结 1.1 思维导图:Java图形界面总结 1.2 可选:使用常规方法总结其他上课内容. 2.书面作业 1. GUI中的事件处理 1.1 写出事件处理模 ...
- 201621123033 《Java程序设计》第2周学习总结
1. 本周学习总结 ·学习了String类的特点,以及其与字符数组的关系等等. ·常量池的相关概念. ·包装类的特点. 2. 书面作业 1. String-使用Eclipse关联jdk源代码 1.1 ...
- 多线程 线程组 ThreadGroup
package org.zln.thread; import java.util.Date; /** * Created by sherry on 000024/6/24 22:30. */ publ ...
- Codeforces Round #384 (Div. 2) 734E(二分答案+状态压缩DP)
题目大意 给定一个序列an,序列中只有1~8的8个整数,让你选出一个子序列,满足下列两个要求 1.不同整数出现的次数相差小于等于1 2.子序列中整数分布是连续的,即子序列的整数必须是1,1,1.... ...
- BZOJ1180 [CROATIAN2009]OTOCI 【LCT】
题目 给出n个结点以及每个点初始时对应的权值wi.起始时点与点之间没有连边.有3类操作: 1.bridge A B:询问结点A与结点B是否连通.如果是则输出"no".否则输出&qu ...
- 提取URL字符串的搜索字符串中的参数
function urlArgs() { var args = []; var query = location.search.substring(1); var paris = query.spli ...