
Guided Hacking DLL Injector 3.3
Guided Hacking DLL Injector 3.3
https://guidedhacking.com/resources/guided-hacking-dll-injector.4/
Injection Methods:
- LoadLibrary
- LdrLoadDll Stub
- Manual Mapping
Launch Methods:
- NtCreateThreadEx
- Thread Hijacking
- SetWindowsHookEx
- QueueUserAPC
Compatible with both 32-bit and 64-bit programs running on Windows XP or higher. Settings of the GUI are saved to a local ini file. Processes can be selected by name or process ID and by the fancy process picker.
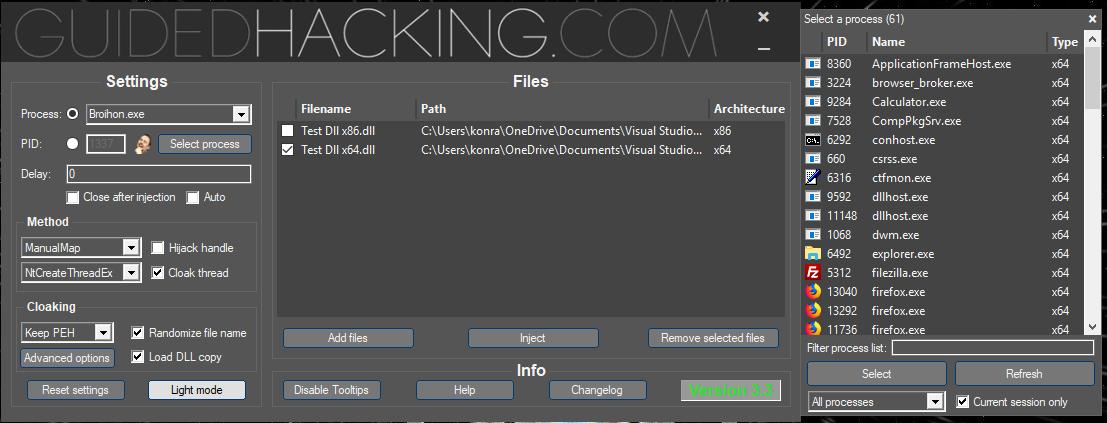
Since GH Injector V3.0 the actual injector has been converted in to a library
To use it in your applications you can either use InjectA (ansi) or InjectW (unicode) which are the two functions exported by the "GH Injector - x86.dll"/"GH Injector - x64.dll". These functions take a pointer to a INJECTIONDATAA/INJECTIONDATAW structure. For more the struct definition / enums / flags check "Injection.h".
Rake's dank video tutorial for v2.4 showing how to use it's features and a source code review:
Credits
For the Manual Mapping a lot of credits go to Joachim Bauch. You can visit his website here.
I highly recommend you to go there and take a look if you're interested in Manual Mapping and the PE format itself.
The windows structures I use for the unlinking process are mostly inspired by this site which is also a very interesting read. I also want to credit Anton Bruckner and Dmitri Shostakovich because most of the time coding this I listened to their fantastic music which is probably one of the reasons why this took me way too long
Last but not least credits go to Rake's mom for keeping me motivated during hard times (no pun intended).
Also checkout the loader made by Traxin:Release - GHLoader v2.0 (Source Included)
Guided Hacking DLL Injector 3.3的更多相关文章
- 【资源分享】Dll Injector(DLL注入器)
*----------------------------------------------[下载区]----------------------------------------------* ...
- Windows Dll Injection、Process Injection、API Hook、DLL后门/恶意程序入侵技术
catalogue 1. 引言2. 使用注册表注入DLL3. 使用Windows挂钩来注入DLL4. 使用远程线程来注入DLL5. 使用木马DLL来注入DLL6. 把DLL作为调试器来注入7. 使用c ...
- 系统安全攻防战:DLL注入技术详解
DLL注入是一种允许攻击者在另一个进程的地址空间的上下文中运行任意代码的技术.攻击者使用DLL注入的过程中如果被赋予过多的运行特权,那么攻击者就很有可能会在DLL文件中嵌入自己的恶意攻击代码以获取更高 ...
- DLL Injection with Delphi(转载)
原始链接 I had recently spent some time playing around with the simple to use DelphiDetours package from ...
- 关于dll劫持我的奇思妙想(一)
0x00 前言 前段时间在研究着windows底层的一些东西,发现这个dll劫持一直没有做过,根据倾旋师傅的视频和文章做了一系列的研究,然后就突发来了兴致研究一些dll劫持提权. 0x01 了解 ...
- How to Hack Unity Games using Mono Injection Tutorial
https://guidedhacking.com/threads/how-to-hack-unity-games-using-mono-injection-tutorial.11674/ Unity ...
- 通用 C# DLL 注入器injector(注入dll不限)
为了方便那些不懂或者不想用C++的同志,我把C++的dll注入器源码转换成了C#的,这是一个很简单实用的注入器,用到了CreateRemoteThread,WriteProcessMemory ,Vi ...
- 给返回的injector增加了一个invoke方法
我们知道,这里swap只需交换指针指向就可以,所以我们可以写出如下自定义版本的swap函数: 首先,它把一个独立的文件看成一个模块,比如上面的 hello.js 文件,就可以当成一个模块.模块的名称就 ...
- 人手一份核武器 - Hacking Team 泄露(开源)资料导览手册
https://zhuanlan.zhihu.com/p/20102713 author:蒸米 0x00 序 事先声明本人并不是全栈安全工程师,仅仅是移动安全小菜一枚,所以对泄漏资料的分析难免会有疏忽 ...
随机推荐
- Nginx记录post body内容
nginx在记录http的body内容时,会将中文转义为16进制 在nginx 1.11.8 以上版本中log_format 增加了escape=json 参数,可以不转义变量内容: log_form ...
- centos7开启80端口及其他端口
首先centos7的防火墙由iptables改为了firewalld 1. 执行命令:firewall-cmd --zone=public --add-port=80/tcp --permanent ...
- 0001-代码仓库-mvn
暂缺 基本介绍 web管理 ifsvnadmin
- requests-html模块(下)
render方法 我们先理一下关系requests和的作者是同一个人,pyppeteer是nodejs中puppeteer的非官方实现 requests-html调用的pyppeteer与浏览器进行交 ...
- 使用Cloudera Manager部署HUE
使用Cloudera Manager部署HUE 作者:尹正杰 版权声明:原创作品,谢绝转载!否则将追究法律责任. 一.添加HUE服务 1>.进入CM服务安装向导 2>.选择需要安装的h ...
- HTML&CSS基础-属性选择器
HTML&CSS基础-属性选择器 作者:尹正杰 版权声明:原创作品,谢绝转载!否则将追究法律责任. 一.html源代码 <!DOCTYPE html> <html> & ...
- springboot错误: 找不到或无法加载主类
一:当在eclipse启动spring boot项目时出现问题: springboot错误: 找不到或无法加载主类 解决办法: 1,通过cmd命令行,进入项目目录进行,mvn clean instal ...
- 28.XSD(XML Schema Definition)用法实例介绍以及C#使用xsd文件验证XML格式
转自https://www.cnblogs.com/gdjlc/archive/2013/09/08/3308229.html XML Schema 语言也称作 XML Schema 定义(XML S ...
- Python练习题---判断回文数
设n是一个任意自然数,如果n的各位数字反向排序所得的自然数与n相等,则n被称为回文数,从键盘输入一个5位数字 ,请编写程序判断这个数字是不是回文数. 思路:先获取一个字符串,再判断该字符串是否满足是自 ...
- 大数据之路week07--day05 (一个基于Hadoop的数据仓库建模工具之一 HIve)
什么是Hive? 我来一个短而精悍的总结(面试常问) 1:hive是基于hadoop的数据仓库建模工具之一(后面还有TEZ,Spark). 2:hive可以使用类sql方言,对存储在hdfs上的数据进 ...