
Shiro03
1、shiro授权角色、权限
2、Shiro的注解式开发
shiro权限思路

授权
ShiroUserMapper中定义两个方法
//    通过用户ID查询角色

    Set<String> getRolesByUserId(Integer userId);

//    通过用户ID查询权限

    Set<String> getPersByUserId(Integer userId);
在ShiroUserMapper.xml中新增内容
  <select id="getRolesByUserId" resultType="java.lang.String" parameterType="java.lang.Integer">

  select r.roleid from t_shiro_user u,t_shiro_user_role ur,t_shiro_role r

    where u.userid = ur.userid and ur.roleid = r.roleid

    and u.userid = #{userId}

</select>

  <select id="getPersByUserId" resultType="java.lang.String" parameterType="java.lang.Integer">

  select p.permission from t_shiro_user u,t_shiro_user_role ur,t_shiro_role_permission rp,t_shiro_permission p

  where u.userid = ur.userid and ur.roleid = rp.roleid and rp.perid = p.perid

  and u.userid = #{userId}

</select>
Service层
package com.liuwenwu.service.impl;

import com.liuwenwu.mapper.ShiroUserMapper;

import com.liuwenwu.model.ShiroUser;

import com.liuwenwu.service.ShiroUserService;

import org.springframework.beans.factory.annotation.Autowired;

import org.springframework.stereotype.Service;

import java.util.Set;

/**

 * @author LWW

 * @site www.lww.com

 * @company

 * @create 2019-10-13 16:14

 */

@Service("shiroUserService")

public class ShiroUserServiceImpl implements ShiroUserService {

    @Autowired

    private ShiroUserMapper shiroUserMapper;

    @Override

    public ShiroUser queryByName(String uname) {

        return shiroUserMapper.queryByName(uname);

    }

    /**

     * 新增用户

     * @param record

     * @return

     */

    @Override

    public int insert(ShiroUser record) {

        return shiroUserMapper.insert(record);

    }

    /**

     * 通过用户ID查询角色

     * @param userId

     * @return

     */

    @Override

    public Set<String> getRolesByUserId(Integer userId) {

        return shiroUserMapper.getRolesByUserId(userId);

    }

    /**

     * 通过用户ID查询权限

     * @param userId

     * @return

     */

    @Override

    public Set<String> getPersByUserId(Integer userId) {

        return shiroUserMapper.getPersByUserId(userId);

    }

}
ShiroUserServiceImpl
package com.liuwenwu.service.impl;

import com.liuwenwu.mapper.ShiroUserMapper;

import com.liuwenwu.model.ShiroUser;

import com.liuwenwu.service.ShiroUserService;

import org.springframework.beans.factory.annotation.Autowired;

import org.springframework.stereotype.Service;

import java.util.Set;

/**

 * @author LWW

 * @site www.lww.com

 * @company

 * @create 2019-10-13 16:14

 */

@Service("shiroUserService")

public class ShiroUserServiceImpl implements ShiroUserService {

    @Autowired

    private ShiroUserMapper shiroUserMapper;

    @Override

    public ShiroUser queryByName(String uname) {

        return shiroUserMapper.queryByName(uname);

    }

    /**

     * 新增用户

     * @param record

     * @return

     */

    @Override

    public int insert(ShiroUser record) {

        return shiroUserMapper.insert(record);

    }

    /**

     * 通过用户ID查询角色

     * @param userId

     * @return

     */

    @Override

    public Set<String> getRolesByUserId(Integer userId) {

        return shiroUserMapper.getRolesByUserId(userId);

    }

    /**

     * 通过用户ID查询权限

     * @param userId

     * @return

     */

    @Override

    public Set<String> getPersByUserId(Integer userId) {

        return shiroUserMapper.getPersByUserId(userId);

    }

}
重写自定义MyRealm中的授权方法
    /**

     * 授权

     * @param principals

     * @return

     */

    @Override

    protected AuthorizationInfo doGetAuthorizationInfo(PrincipalCollection principals) {

//        当前登录的用户

        ShiroUser shiroUser = this.shiroUserService.queryByName(principals.getPrimaryPrincipal().toString());

        Set<String> rolrids = this.shiroUserService.getRolesByUserId(shiroUser.getUserid());

        Set<String> perdis = this.shiroUserService.getPersByUserId(shiroUser.getUserid());

        SimpleAuthorizationInfo info =new SimpleAuthorizationInfo();

        info.setRoles(rolrids);

        info.setStringPermissions(perdis);

        return info;

    }
注解式开发
常用注解介绍
@RequiresAuthenthentication:表示当前Subject已经通过login进行身份验证;即 Subject.isAuthenticated()返回 true
@RequiresUser:表示当前Subject已经身份验证或者通过记住我登录的
@RequiresGuest:表示当前Subject没有身份验证或者通过记住我登录过,即是游客身份
@RequiresRoles(value = {"admin","user"},logical = Logical.AND):表示当前Subject需要角色admin和user
@RequiresPermissions(value = {"user:delete","user:b"},logical = Logical.OR):表示当前Subject需要权限user:delete或者user:b
ShiroUserController
    /**

     * 身份认证的注解

     * @param req

     * @param resp

     * @return

     */

    @RequiresUser

    @RequestMapping("/passUser")

    public String passUser(HttpServletRequest req, HttpServletResponse resp){

        return "admin/addUser";

    }

    /**

     * 角色认证的注解

     * @param req

     * @param resp

     * @return

     * 当前方法必须同时具备1、4的角色ID才能被访问

     */

    @RequiresRoles(value = {"1","4"},logical = Logical.OR)

    @RequestMapping("/passRole")

    public String passPole(HttpServletRequest req, HttpServletResponse resp){

        return "admin/listUser";

    }

    /**

     * 权限认证的注解

     * @param req

     * @param resp

     * @return

     */

    @RequiresPermissions(value = {"user:update","user:view"},logical = Logical.OR)

    @RequestMapping("/passPer")

    public String passPer(HttpServletRequest req, HttpServletResponse resp){

        return "admin/resetPwd";

    }
springmvc-servlet.xml
 <bean class="org.springframework.aop.framework.autoproxy.DefaultAdvisorAutoProxyCreator"

          depends-on="lifecycleBeanPostProcessor">

        <property name="proxyTargetClass" value="true"></property>

    </bean>

    <bean class="org.apache.shiro.spring.security.interceptor.AuthorizationAttributeSourceAdvisor">

        <property name="securityManager" ref="securityManager"/>

    </bean>

    <!--错误请求映射路径-->

    <bean id="exceptionResolver" class="org.springframework.web.servlet.handler.SimpleMappingExceptionResolver">

        <property name="exceptionMappings">

            <props>

                <prop key="org.apache.shiro.authz.UnauthorizedException">

                    unauthorized

                </prop>

            </props>

        </property>

        <property name="defaultErrorView" value="unauthorized"/>

    </bean>
main.jsp
<ul>

    shiro注解测试

    <li>

        <a href="${pageContext.request.contextPath}/passUser">身份认证</a>

    </li>

    <li>

        <a href="${pageContext.request.contextPath}/passRole">角色认证</a>

    </li>

    <li>

        <a href="${pageContext.request.contextPath}/passPer">权限认证</a>

    </li>

</ul>
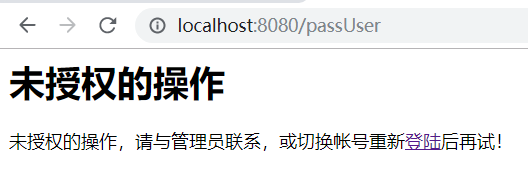
效果: 没通过验证会跳到 unauthorized.jsp页面
通过验证:
Shiro03的更多相关文章
- Shiro与Spring整合
Shiro引入Spring 添加jar包/maven配置 <!-- shiro支持 --> <dependency> <groupId>org.apache.shi ...
- springboot shiro 基本整合
springboot shiro 基本整合 https://www.w3cschool.cn/shiro/c52r1iff.html http://shiro.apache.org/configura ...
随机推荐
- js 数据存入数组
var tag = []; $('.deltag').each(function(){ if($(this).attr("checked")== 'checked'){ tag.p ...
- 【LeetCode】81. 搜索旋转排序数组 II
81. 搜索旋转排序数组 II 知识点:数组,二分查找: 题目描述 已知存在一个按非降序排列的整数数组 nums ,数组中的值不必互不相同. 在传递给函数之前,nums 在预先未知的某个下标 k(0 ...
- sort,uniq,tr,cut,eval命令
目录 一.排序命令sort 1.格式 2.常用选项 3.例子 二.去除重复行操作命令uniq 1.格式 2.常用选项 3.示例 三.字符转换命令tr 1.格式 2.常用选项 3.参数 4.示例 四.数 ...
- 2020年度钻石C++C学习笔记(1)《博学谷》
1.C语言概述 1.1 什么是C语言 一提到语言这个词语,自然会想到的是像英语.汉语等这样的自然语言,因为它是人和人交换信息不可缺少的工具. 而今天计算机遍布了我们生活的每一个角落,除了人和人的相互交 ...
- [洛谷P3376题解]网络流(最大流)的实现算法讲解与代码
[洛谷P3376题解]网络流(最大流)的实现算法讲解与代码 更坏的阅读体验 定义 对于给定的一个网络,有向图中每个的边权表示可以通过的最大流量.假设出发点S水流无限大,求水流到终点T后的最大流量. 起 ...
- OpenFaaS实战之九:终篇,自制模板(springboot+maven+jdk8)
欢迎访问我的GitHub https://github.com/zq2599/blog_demos 内容:所有原创文章分类汇总及配套源码,涉及Java.Docker.Kubernetes.DevOPS ...
- Vulhub-DC-2靶场
Vulhub-DC-2靶场 前言 最近一直忙于学习代码审计和内网渗透,所以靶场这方面的文章一直未更新,但是计划是更新完DC系列靶场的,这个不会鸽. DC-2的靶场是很简单的一共5个flag. 正文 f ...
- RHCSA_DAY02
Linux:一切皆文件 分区:/boot:做引导盘 /swap:虚拟内存----最大20gb /data:自己放文件用 /:根分区 - 图形界面: - Ctrl+Shift +号 //调整命令 ...
- C++ //运算符重载 +号
1 #include <iostream> 2 #include <string> 3 using namespace std; 4 5 //1.成员函数重载 +号 6 cla ...
- 跟Waf斗智斗勇的一天
差点心态爆炸 幸亏整出来了... 最近快放寒假了..临近高考不到最后一星期绝对不学习.. 挖下SRC 这家自带的waf头疼死我了 想几次Fuzz全都撞壁了 然后发现了这家waf的规则 信息搜集不说了 ...