
Spring Security 实战干货:理解AuthenticationManager
1. 前言
我们上一篇介绍了UsernamePasswordAuthenticationFilter的工作流程,留下了一个小小的伏笔,作为一个Servlet Filter应该存在一个doFilter实现方法,而它却没有,其实它的父类AbstractAuthenticationProcessingFilter提供了具体的实现。稍后我们会根据这个实现引出今天的主角AuthenticationManager,来继续介绍用户的认证过程。
2. AbstractAuthenticationProcessingFilter
我们来看看AbstractAuthenticationProcessingFilter的核心方法doFilter的实现:
public void doFilter(ServletRequest req, ServletResponse res, FilterChain chain)

      throws IOException, ServletException {

   HttpServletRequest request = (HttpServletRequest) req;

   HttpServletResponse response = (HttpServletResponse) res;

    // 先通过请求的uri来判断是否需要认证,比如默认的/login

   if (!requiresAuthentication(request, response)) {

      chain.doFilter(request, response);

      return;

   }

   if (logger.isDebugEnabled()) {

      logger.debug("Request is to process authentication");

   }

   Authentication authResult;

   try {

       // 接着就是执行子类钩子方法attemptAuthentication来获取认证结果对象Authentication ,这个对象不能是空 否则直接返回

      authResult = attemptAuthentication(request, response);

      if (authResult == null) {

         // return immediately as subclass has indicated that it hasn't completed

         // authentication

         return;

      }

       // 处理session 策略,这里默认没有任何策略

      sessionStrategy.onAuthentication(authResult, request, response);

   }

   catch (InternalAuthenticationServiceException failed) {

      logger.error(

            "An internal error occurred while trying to authenticate the user.",

            failed);

       // 如果遇到异常 就会交给认证失败处理器 AuthenticationFailureHandler 来处理

      unsuccessfulAuthentication(request, response, failed);

      return;

   }

   catch (AuthenticationException failed) {

      // Authentication failed

      unsuccessfulAuthentication(request, response, failed);

      return;

   }

   //  认证成功后继续其它过滤器链 并最终交给认证成功处理器 AuthenticationSuccessHandler 处理

   if (continueChainBeforeSuccessfulAuthentication) {

      chain.doFilter(request, response);

   }

   successfulAuthentication(request, response, chain, authResult);

}
大部分逻辑这里是清晰的,关键在于attemptAuthentication方法,这个我们已经在上一文分析了是通过AuthenticationManager的authenticate方法进行认证逻辑的处理,接下来我们将重点分析这个接口来帮助我们了解Spring Seucirty的认证过程。
3. AuthenticationManager
AuthenticationManager这个接口方法非常奇特,入参和返回值的类型都是Authentication。该接口的作用是对用户的未授信凭据进行认证,认证通过则返回授信状态的凭据,否则将抛出认证异常AuthenticationException。
3.1 AuthenticationManager的初始化流程
那么AbstractAuthenticationProcessingFilter中的 AuthenticationManager 是在哪里配置的呢? 看过Spring Security 实战干货系列应该知道WebSecurityConfigurerAdapter中的void configure(AuthenticationManagerBuilder auth)是配置AuthenticationManager 的地方, 我根据源码总结了一下AuthenticationManager 的初始化流程,相信可以帮助你去阅读相关的源码:
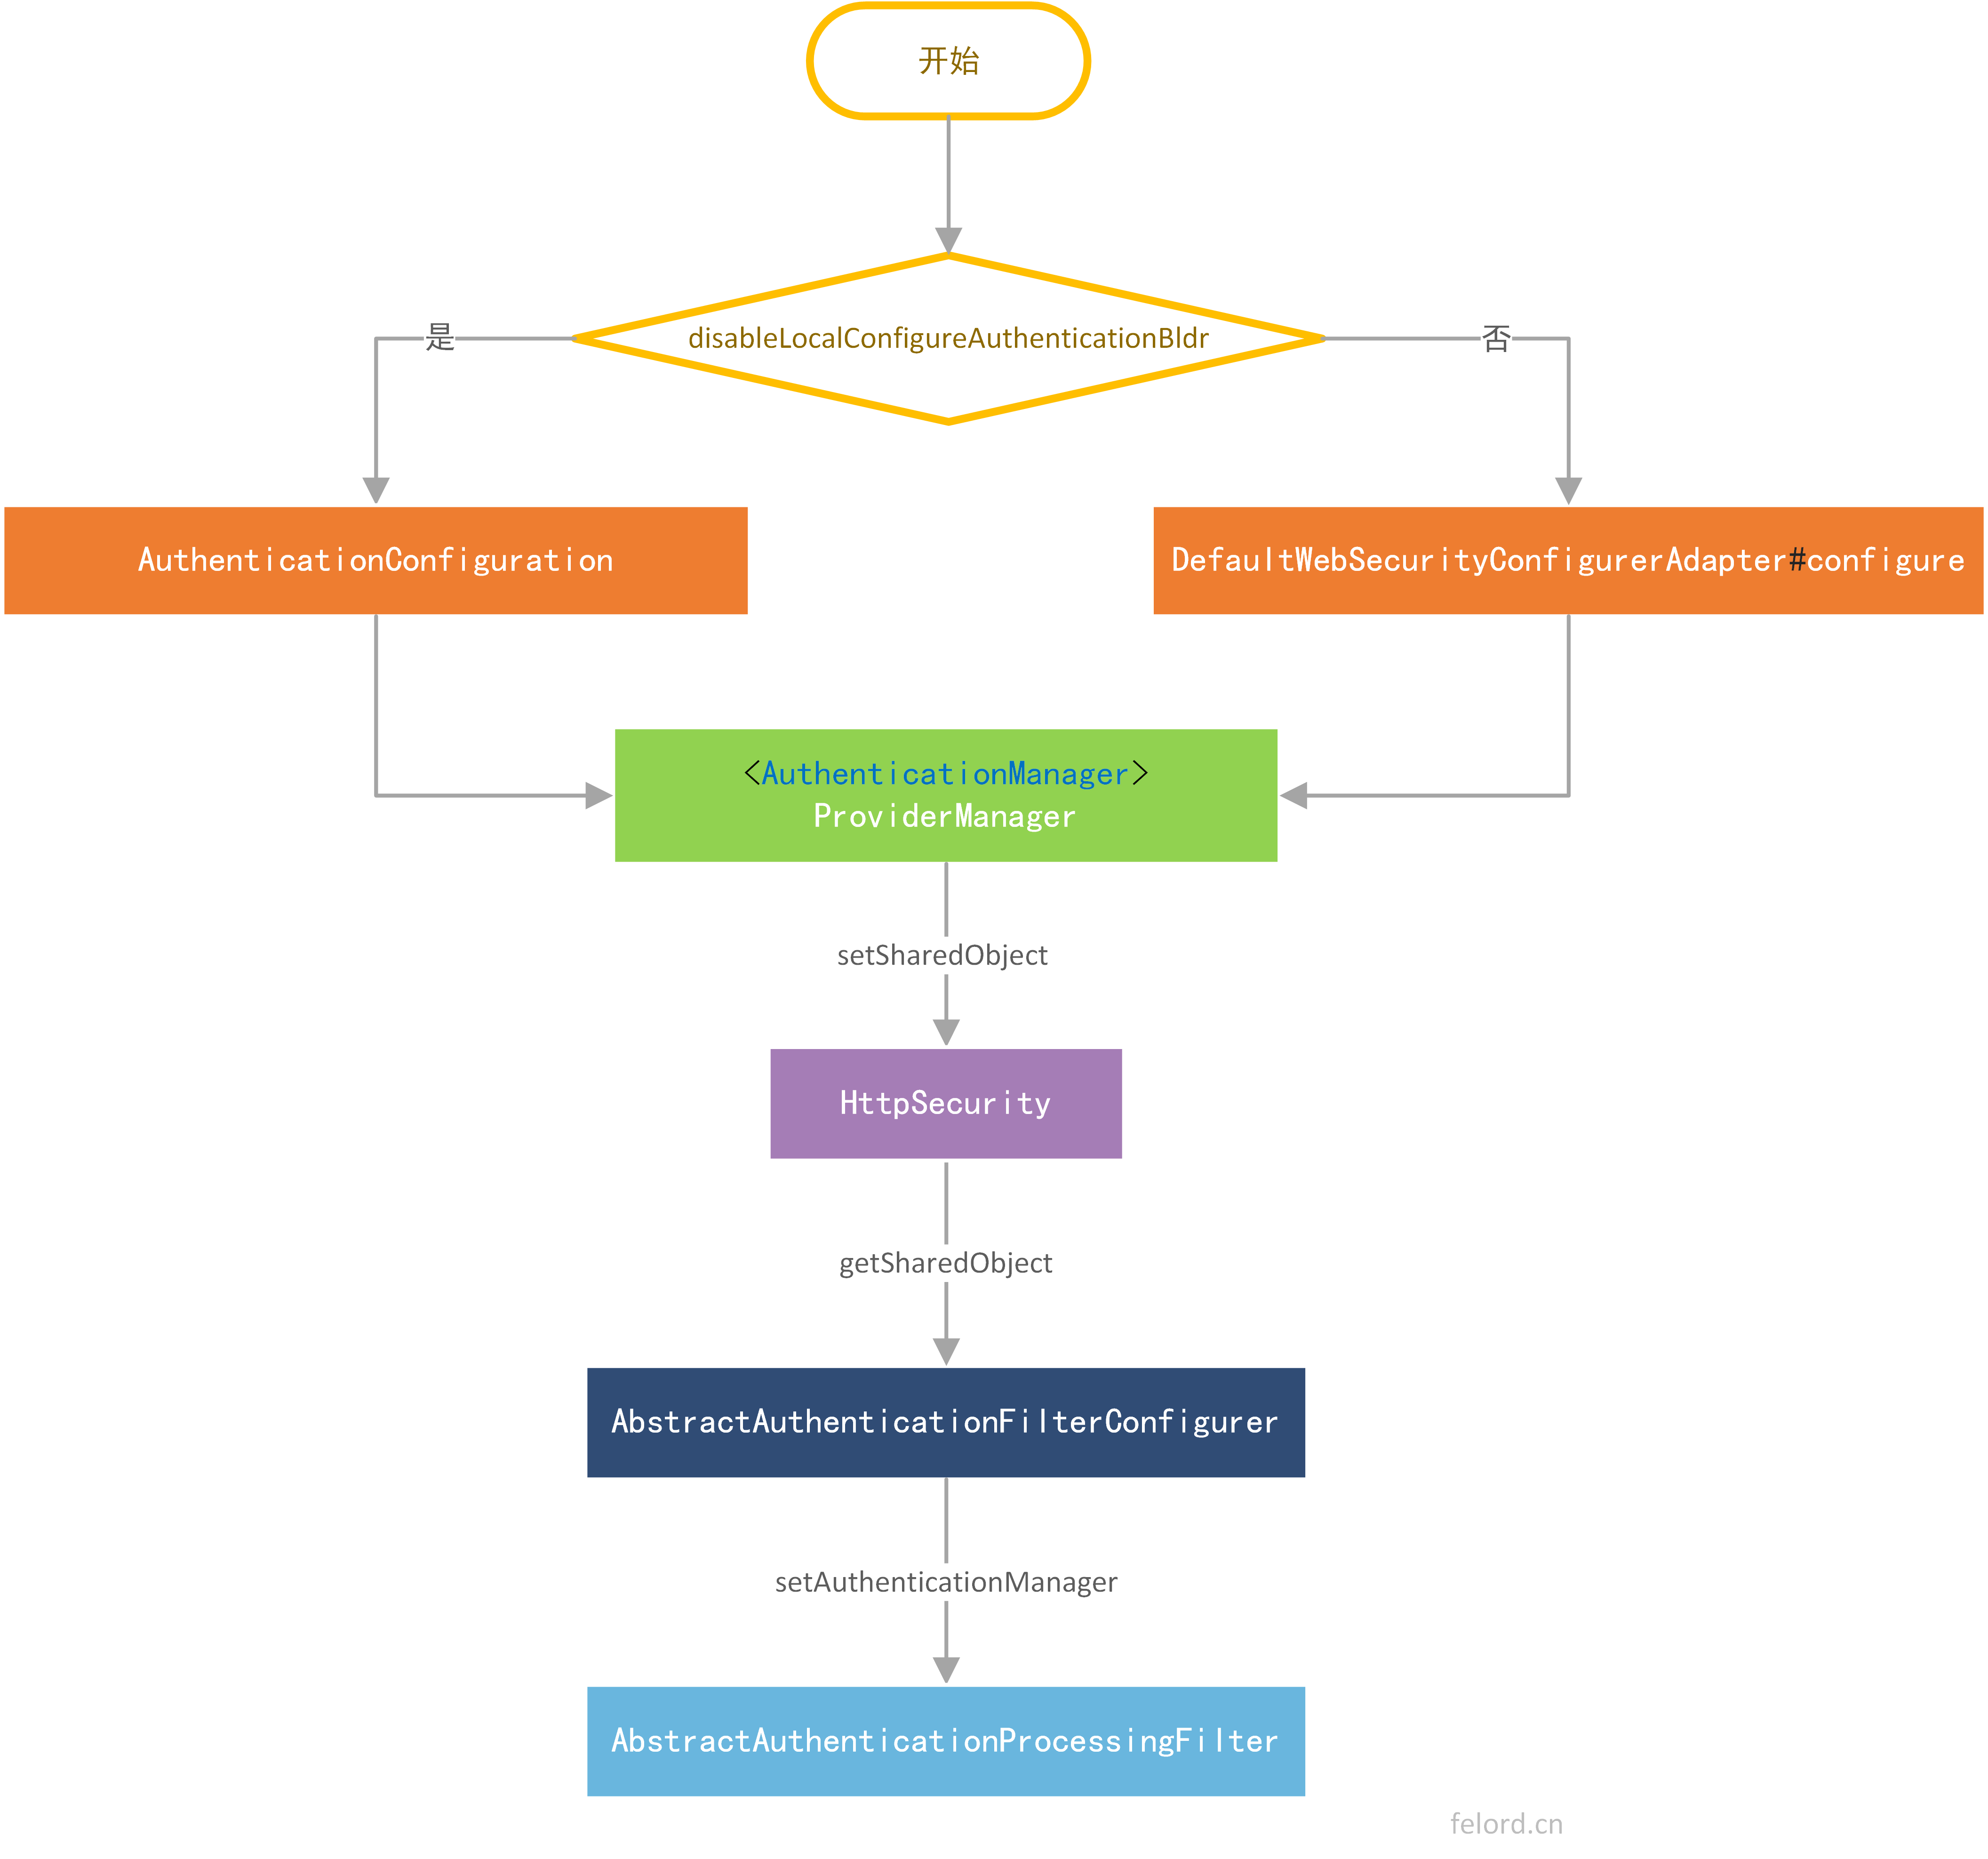
需要注意的是如果我们使用自定义配置一定不能按照类似下面的错误示范:
@Override

protected void configure(AuthenticationManagerBuilder auth) throws Exception {

    DaoAuthenticationProvider daoAuthenticationProvider = new DaoAuthenticationProvider();

    daoAuthenticationProvider.setUserDetailsService(weChatSecurityConfigProperties.getUserDetailsService());

    daoAuthenticationProvider.setPasswordEncoder(multiPasswordEncoder());

    auth.authenticationProvider(daoAuthenticationProvider);

    // 调用 super 将导致不生效 所以下面语句不要写

    super.configure(auth);

}
3.2 AuthenticationManager的认证过程
AuthenticationManager的实现ProviderManager管理了众多的AuthenticationProvider。每一个AuthenticationProvider都只支持特定类型的Authentication,如果不支持将会跳过。另一个作用就是对适配的Authentication进行认证,只要有一个认证成功,那么就认为认证成功,所有的都没有通过才认为是认证失败。认证成功后的Authentication就变成授信凭据,并触发认证成功的事件。认证失败的就抛出异常触发认证失败的事件。
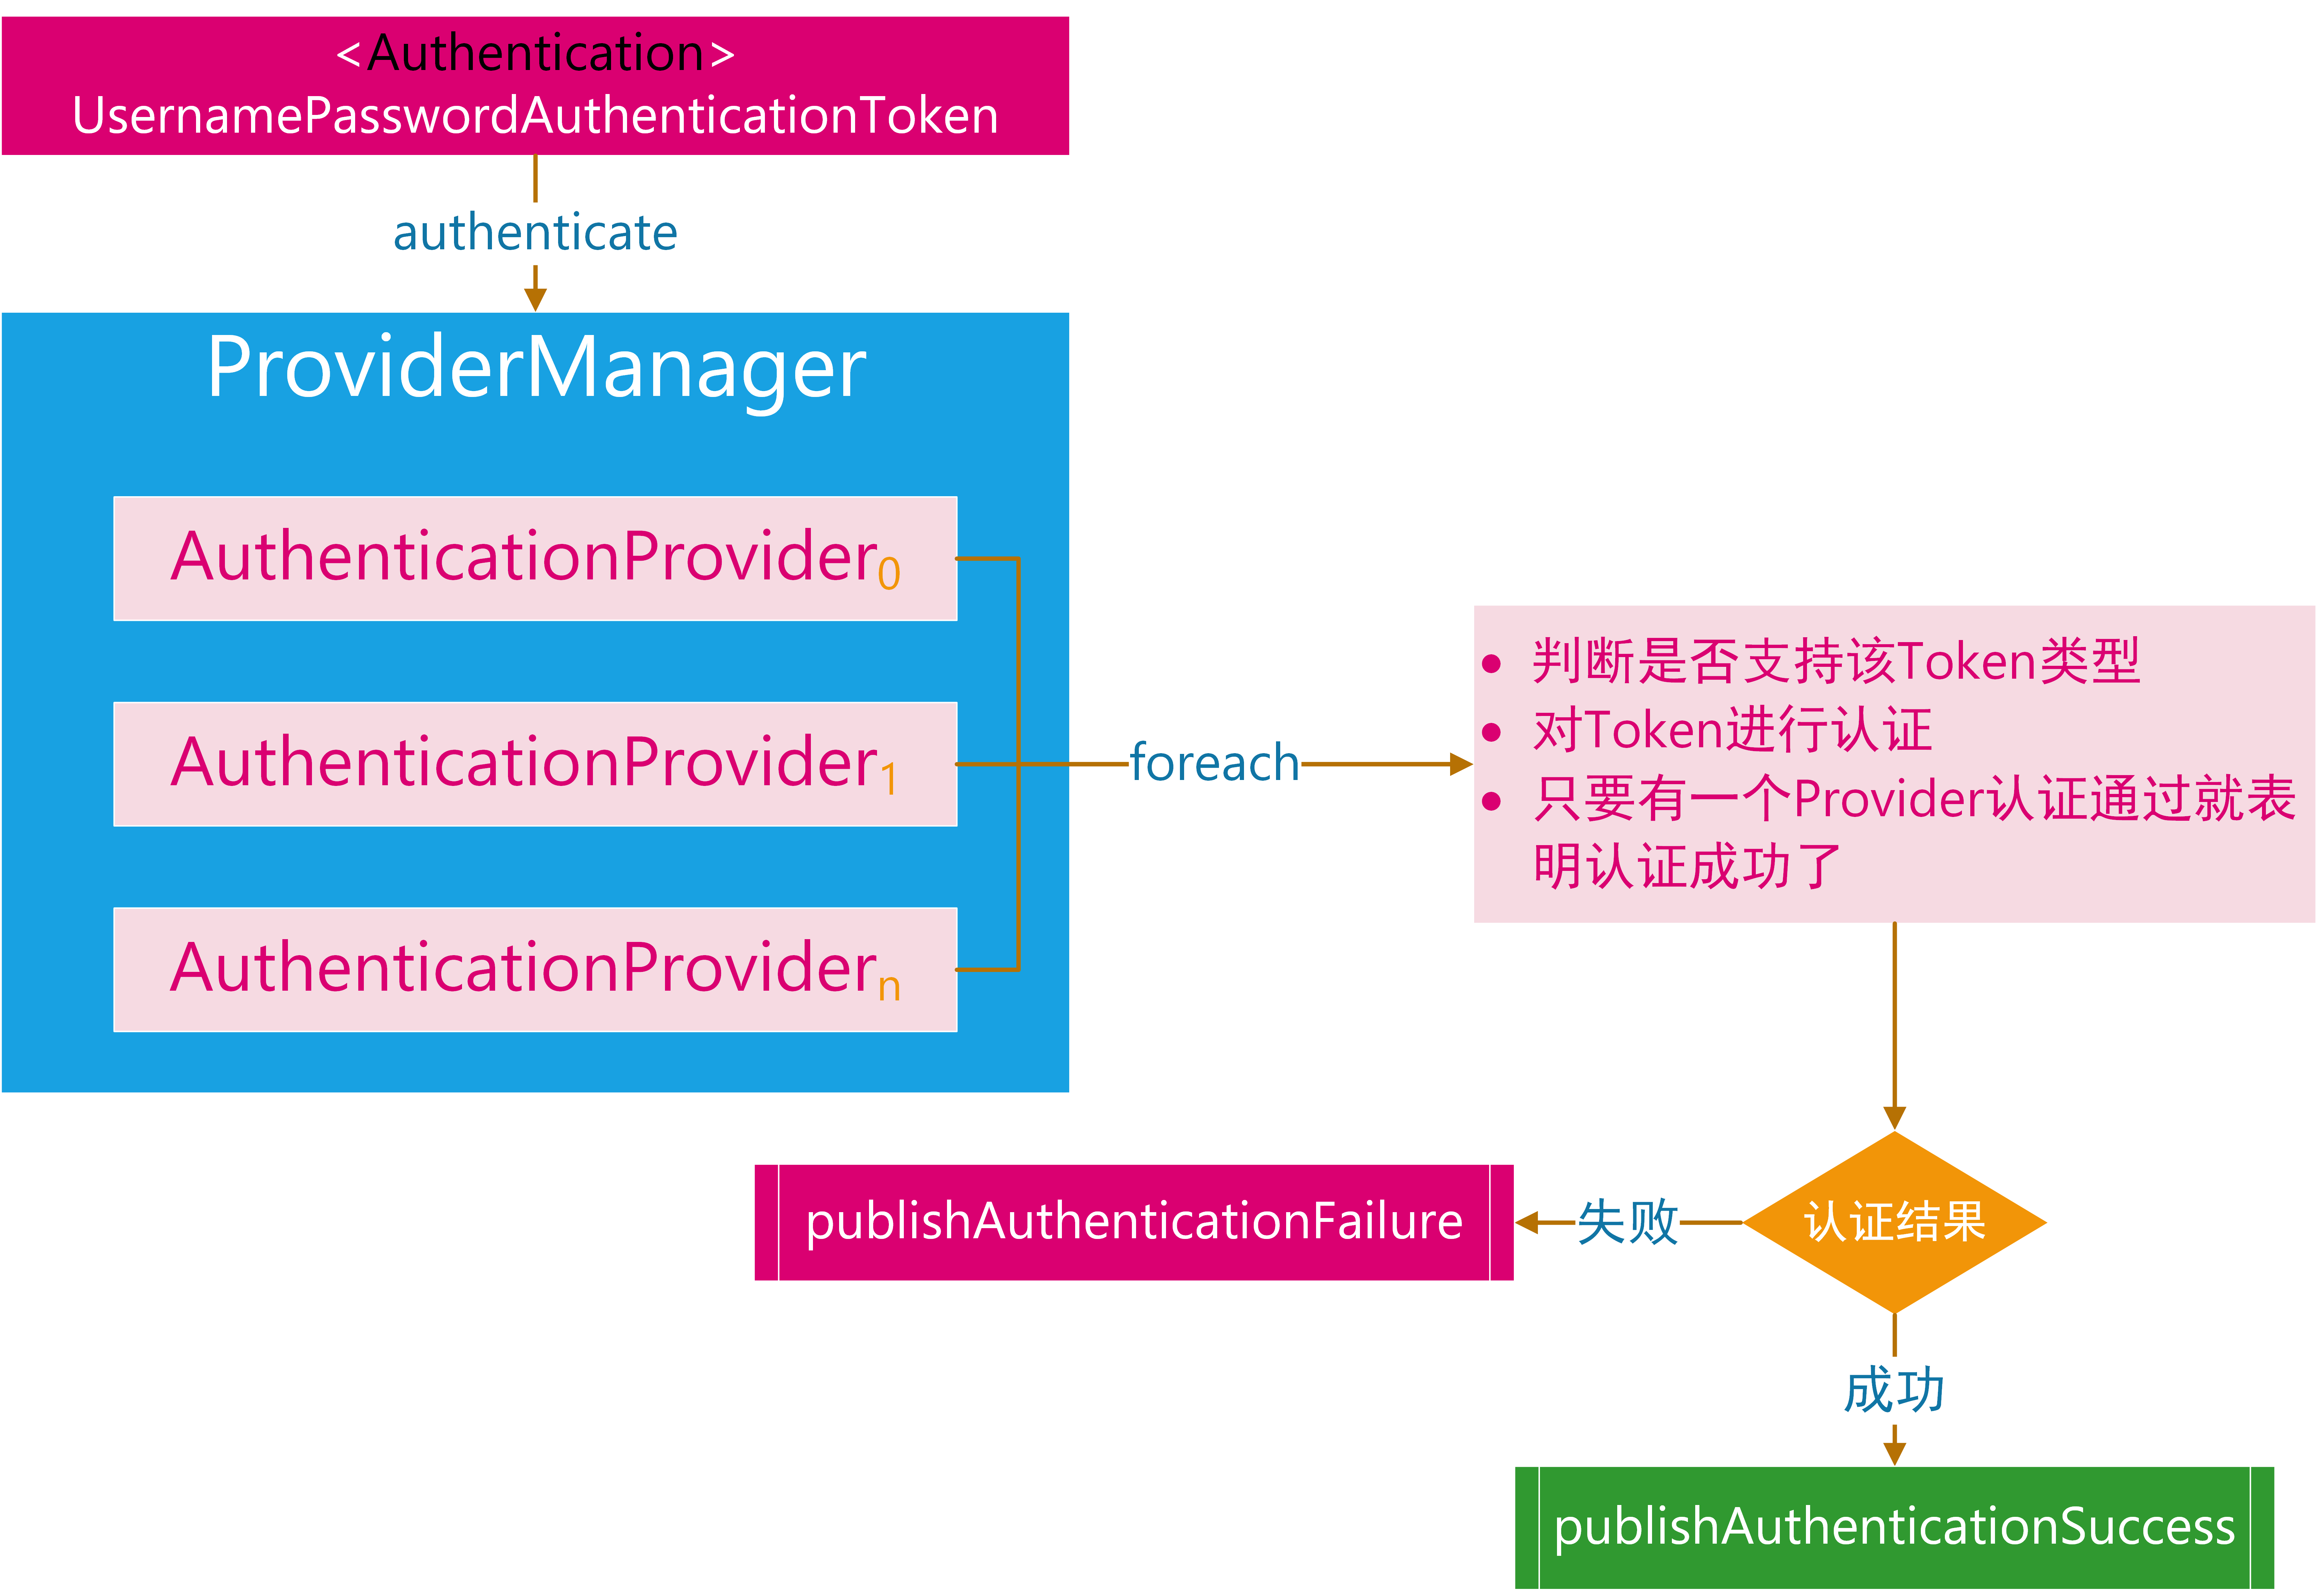
从这里我们可以看出认证管理器AuthenticationManager针对特定的Authentication提供了特定的认证功能,我们可以借此来实现多种认证并存。
4. 总结
通过本文我们对Spring Security认证管理器AuthenticationManager的初始化过程和认证过程进行了分析,如果你熟悉了AuthenticationManager的逻辑可以实现多种认证方式的并存等能力,实现很多有用的逻辑,这对集成Spring Security到项目中非常重要。多多关注:码农小胖哥 获取更多的原创干货。
关注公众号:Felordcn 获取更多资讯
Spring Security 实战干货:理解AuthenticationManager的更多相关文章
- Spring Security 实战干货:AuthenticationManager的初始化细节
1. 前言 今天有个同学告诉我,在Security Learning项目的day11分支中出现了一个问题,验证码登录和其它登录不兼容了,出现了No Provider异常.还有这事?我赶紧跑了一遍还真是 ...
- Spring Security 实战干货:图解用户是如何登录的
1. 前言 欢迎阅读Spring Security 实战干货系列文章,在集成Spring Security安全框架的时候我们最先处理的可能就是根据我们项目的实际需要来定制注册登录了,尤其是Http登录 ...
- Spring Security 实战干货: 简单的认识 OAuth2.0 协议
1.前言 欢迎阅读 Spring Security 实战干货 系列文章 .OAuth2.0 是近几年比较流行的授权机制,对于普通用户来说可能每天你都在用它,我们经常使用的第三方登录大都基于 OAuth ...
- Spring Security 实战干货:OAuth2第三方授权初体验
1. 前言 Spring Security实战干货系列 现在很多项目都有第三方登录或者第三方授权的需求,而最成熟的方案就是OAuth2.0授权协议.Spring Security也整合了OAuth2. ...
- Spring Security 实战干货:OAuth2授权请求是如何构建并执行的
在Spring Security 实战干货:客户端OAuth2授权请求的入口中我们找到了拦截OAuth2授权请求入口/oauth2/authorization的过滤器OAuth2Authorizati ...
- Spring Security 实战干货:使用 JWT 认证访问接口
(转载)原文链接:https://my.oschina.net/10000000000/blog/3127268 1. 前言 欢迎阅读Spring Security 实战干货系列.之前我讲解了如何编写 ...
- Spring Security 实战干货:如何实现不同的接口不同的安全策略
1. 前言 欢迎阅读 Spring Security 实战干货 系列文章 .最近有开发小伙伴提了一个有趣的问题.他正在做一个项目,涉及两种风格,一种是给小程序出接口,安全上使用无状态的JWT Toke ...
- Spring Security 实战干货:图解Spring Security中的Servlet过滤器体系
1. 前言 我在Spring Security 实战干货:内置 Filter 全解析对Spring Security的内置过滤器进行了罗列,但是Spring Security真正的过滤器体系才是我们了 ...
- Spring Security 实战干货:实现自定义退出登录
文章目录 1. 前言 2. 我们使用 Spring Security 登录后都做了什么 2. 退出登录需要我们做什么 3. Spring Security 中的退出登录 3.1 LogoutFilte ...
随机推荐
- 入门大数据---Spark开发环境搭建
一.安装Spark 1.1 下载并解压 官方下载地址:http://spark.apache.org/downloads.html ,选择 Spark 版本和对应的 Hadoop 版本后再下载: 解压 ...
- 源码剖析@contextlib.contextmanager
示例 @contextlib.contextmanager def result(a): print('before') yield print('after') 外层装饰源码 包装func函数,真实 ...
- 关于线上一次DDOS攻击和阿里云DDOS防护相关内容
问题 最近我们的一台阿里云服务器 (ECS,有公网IP,Nginx 服务器,开放了80,443),遭受到了DDOS攻击,主要攻击的行为是 攻击我们443 端口.发起大量的请求. 但是我们在 Nginx ...
- 分布式配置中心(Native - Config)
本章只讲 Spring Cloud 本地配置方式,可以很方便的高可用集群,且存在良好通讯,不用担心云服务器与内网之间GIT带来的不便,GIT(网上GIT教程一搜一大把了….) - 快速开始 Sprin ...
- 数据解析_bs进行数据解析
1.bs4进行数据解析 数据解析的原理 1.标签定位 2.提取标签,标签属性中存储的数据值 bs4数据解析的原理 1.实例化一个BeautifulSoup对象,并且将页面源码数据加载到该对象中 2.通 ...
- pycharm中连接MySql出现 Exception in thread "main" java.lang.ClassNotFoundException: com.mysql.jdbc.的错误解决
具体异常如下: 这个异常特别烦人,是mysql连接驱动的问题,可以用二步解决: 第一步 从网上下载驱动,从mysql-connector-java_8.0.16-1ubuntu16.04_all.de ...
- Linux必须要掌握的命令
Linux必须要掌握的命令 文件目录操作命令 ls 命令格式:ls [选项] [目录名] 命令功能:列出目标目录中所有的子目录和文件 常用参数:-a,-l,-R, 例1:列出/home/peidach ...
- Spring笔记(3) - debug源码AOP原理解析
案例 @EnableAspectJAutoProxy//开启基于注解的aop模式 @Configuration public class AOPConfig { //业务逻辑类加入容器中 @Bean ...
- Java1.8的HashMap源码解析
java1.8是现在用的最多的版本,hashmap是现在用的最多的map,今天我们试图分析一下源码. 数据结构 首先我们注意到数据是存放在一个Node数组里面 transient Node<K, ...
- gRPC by .net core 3.x——概念、语法、编译
什么是grpc? grpc来自大名鼎鼎的谷歌,孵化于CNCF基金会(docker.k8s同样出自这个基金会).它是一款高性能.开源.通用的rpc框架,你可以通过它来定义rpc的请求和响应.它基于htt ...