
Spring Security构建Rest服务-1204-Spring Security OAuth开发APP认证框架之Token处理
token处理之一基本参数配置
处理token时间、存储策略,客户端配置等
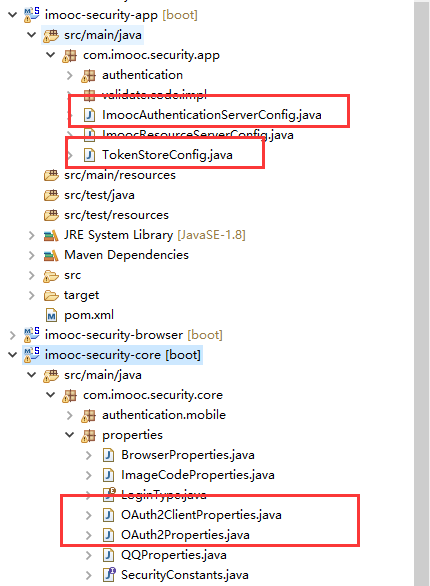
以前的都是spring security oauth默认的token生成策略,token默认在org.springframework.security.oauth2.provider.token.DefaultTokenServices 类里生成的,感兴趣可以看看
/**

 * 认证服务器

 * ClassName: ImoocAuthenticationServerConfig

 * @Description: TODO

 * @author lihaoyang

 * @date 2018年3月12日

 */

@Configuration

@EnableAuthorizationServer //这个注解就是实现了一个认证服务器

public class ImoocAuthenticationServerConfig {

}
是uuid,现在做自定义token,token是在认证服务器里生成的,需要在认证服务器也就是ImoocAuthenticationServerConfig 里写代码。
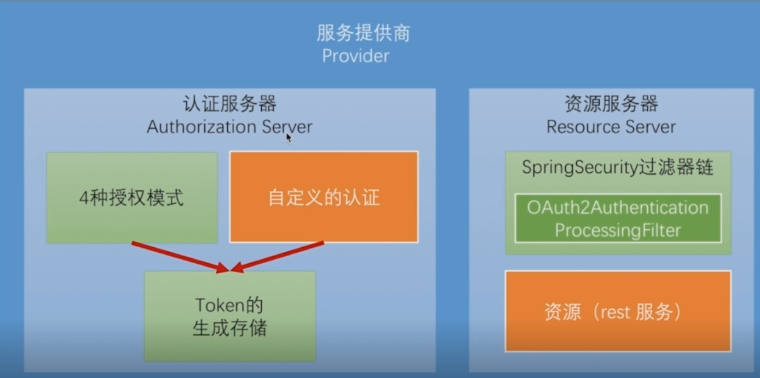
认证服务器配置:
/**

 * 认证服务器

 * ClassName: ImoocAuthenticationServerConfig

 * @Description:

 * extends AuthorizationServerConfigurerAdapter 自定义token生成

 * @author lihaoyang

 * @date 2018年3月12日

 */

@Configuration

@EnableAuthorizationServer //这个注解就是实现了一个认证服务器

public class ImoocAuthenticationServerConfig extends AuthorizationServerConfigurerAdapter{

    /*

     * 不继承AuthorizationServerConfigurerAdapter,这些bean会自己找,配了,就要自己实现

     */

    @Autowired

    private AuthenticationManager authenticationManager;

    @Autowired

    private  UserDetailsService userDetailsService;

    //配置文件

    @Autowired

    private SecurityProperties securityProperties;

    //token存在redis,默认是在内存

    @Autowired

    private TokenStore tokenStore;

    /**

     * 配置TokenEndpoint 是  /oauth/token处理的入口点

     */

    @Override

    public void configure(AuthorizationServerEndpointsConfigurer endpoints) throws Exception {

        endpoints.tokenStore(tokenStore)

                 .authenticationManager(authenticationManager)

                 .userDetailsService(userDetailsService);

    }

    /**

     * 功能:认证服务器会给哪些第三方应用发令牌

     *        覆盖了该方法,application.properties里配置的

     *                 security.oauth2.client.clientId = imooc

     *                security.oauth2.client.clientSecret = imoocsecret

     *     就失效了

     */

    @Override

    public void configure(ClientDetailsServiceConfigurer clients) throws Exception {

        //1,写死

//        clients.jdbc(dataSource)就是qq场景用的,有第三方公司注册过来,目前场景是给自己的应用提供接口,所以用内存就行

//        clients.inMemory()

//                //~========================== 在这里配置和写配置文件一样================

//                .withClient("imooc") //第三方应用用户名

//                .secret("imoocsecret") //密码

//                .accessTokenValiditySeconds(7200)//token有效期

//                .authorizedGrantTypes("password","refresh_token") //支持的授权模式

//                .scopes("all","read","write") //相当于oauth的权限,这里配置了,请求里的必须和这里匹配

//                //~=======如果有多个client,这里继续配置

//                .and()

//                .withClient("xxxxx");

        //2,读取配置文件

        InMemoryClientDetailsServiceBuilder builder = clients.inMemory();

        //判断是否配置了客户端

        if(ArrayUtils.isNotEmpty(securityProperties.getOauth2().getClients())){

            for (OAuth2ClientProperties config : securityProperties.getOauth2().getClients()) {

                builder.withClient(config.getClientId())

                        .secret(config.getClientSecret())

                        .accessTokenValiditySeconds(config.getAccessTokenValiditySeconds())

                        .authorizedGrantTypes("password","refresh_token") //这些也可以配置也可以写死,看心情

                        .scopes("all","read","write");

            }

        }

    }

}
Token默认是存在内存的,这样服务器重启后,就需要重新登录,所以存在redis,(先有个redis,我是装了个windows版的)比存在数据库好,需要配置:
/**

 * token存储到redis,默认是在内存不行

 * ClassName: TokenStoreConfig

 * @Description:  token存储策略

 * @author lihaoyang

 * @date 2018年3月15日

 */

@Configuration

public class TokenStoreConfig {

    @Autowired

    private RedisConnectionFactory redisConnectionFactory;

    @Bean

    public TokenStore redisTokenStore(){

        return new RedisTokenStore(redisConnectionFactory);

    }

}
OAuth相关配置类:
package com.imooc.security.core.properties;

/**

 * 接口授权客户端配置 ClassName: OAuth2ClientProperties

 *

 * @Description: 接口授权客户端配置

 * @author lihaoyang

 * @date 2018年3月15日

 */

public class OAuth2ClientProperties {

    private String clientId;

    private String clientSecret;

    private int accessTokenValiditySeconds = 3600; //没配置就用默认值

    // xxxxx在这里扩展配置

    public String getClientId() {

        return clientId;

    }

    public void setClientId(String clientId) {

        this.clientId = clientId;

    }

    public String getClientSecret() {

        return clientSecret;

    }

    public void setClientSecret(String clientSecret) {

        this.clientSecret = clientSecret;

    }

    public int getAccessTokenValiditySeconds() {

        return accessTokenValiditySeconds;

    }

    public void setAccessTokenValiditySeconds(int accessTokenValiditySeconds) {

        this.accessTokenValiditySeconds = accessTokenValiditySeconds;

    }

}
package com.imooc.security.core.properties;

/**

 * 多个接口客户端,是数组,只有一个的话就不用这个了

 * ClassName: OAuth2Properties

 * @Description: TODO

 * @author lihaoyang

 * @date 2018年3月15日

 */

public class OAuth2Properties {

    private OAuth2ClientProperties[] clients = {};

    public OAuth2ClientProperties[] getClients() {

        return clients;

    }

    public void setClients(OAuth2ClientProperties[] clients) {

        this.clients = clients;

    }

}
这样只需要在application.properties里配置客户端,可以配置fuo
#第三方应用client_id
imooc.security.oauth2.clients[0].clientId = imooc
imooc.security.oauth2.clients[0].clientSecret = imoocsecret
#token失效时间
imooc.security.oauth2.clients[0].accessTokenValiditySeconds = 3600
imooc.security.oauth2.clients[1].clientId = test
imooc.security.oauth2.clients[1].clientSecret = test
启动demo项目,测试:
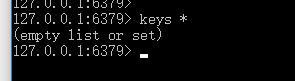
redis是空的:
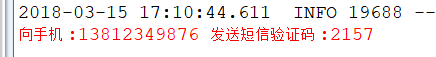
1,模拟获取手机验证码

2,手机验证码登录
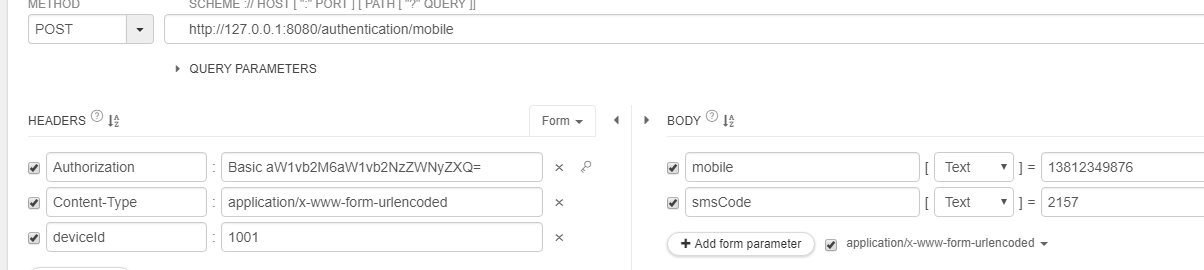
响应:
{

"access_token": "ca7417ef-2792-4c81-b441-519f29046cae",

"token_type": "bearer",

"refresh_token": "f32a845b-5b2b-4761-ab0e-ec076c6c0280",

"expires_in": 3599,

"scope": "all read write"

}
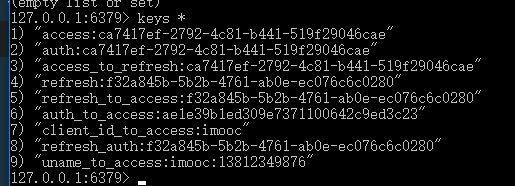
redis中存了很多key:
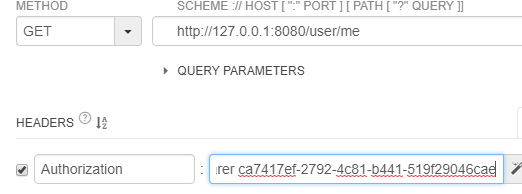
拿token访问用户信息:
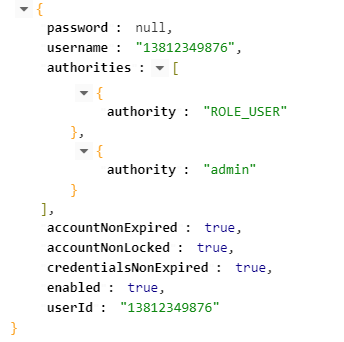
响应
总结:
1,认证服务器 ImoocAuthenticationServerConfig 需要继承 AuthorizationServerConfigurerAdapter ,来自定义token的存储、客户端的配置。
2,自定义TokenStoreConfig配置类,存储token在redis中。
2,token默认存在内存中,这样不行,一般存在redis中,所以需要一个redis
存在问题,token失效的时候,redis中的key还存在,怎么给删除了呢?
具体代码在github:https://github.com/lhy1234/spring-security
下一步自定义token的生成策略,用JWT
Spring Security构建Rest服务-1204-Spring Security OAuth开发APP认证框架之Token处理的更多相关文章
- Spring Security构建Rest服务-1205-Spring Security OAuth开发APP认证框架之Token处理
token处理之二使用JWT替换默认的token JWT(Json Web Token) 特点: 1,自包含:jwt token包含有意义的信息 spring security oauth默认生成的t ...
- Spring Security构建Rest服务-1300-Spring Security OAuth开发APP认证框架之JWT实现单点登录
基于JWT实现SSO 在淘宝( https://www.taobao.com )上点击登录,已经跳到了 https://login.taobao.com,这是又一个服务器.只要在淘宝登录了,就能直接访 ...
- Spring Security构建Rest服务-1201-Spring Security OAuth开发APP认证框架之实现服务提供商
实现服务提供商,就是要实现认证服务器.资源服务器. 现在做的都是app的东西,所以在app项目写代码 认证服务器: 新建 ImoocAuthenticationServerConfig 类,@Ena ...
- Spring Security构建Rest服务-1200-SpringSecurity OAuth开发APP认证框架
基于服务器Session的认证方式: 前边说的用户名密码登录.短信登录.第三方登录,都是普通的登录,是基于服务器Session保存用户信息的登录方式.登录信息都是存在服务器的session(服务器的一 ...
- Spring Security构建Rest服务-1202-Spring Security OAuth开发APP认证框架之重构3种登录方式
SpringSecurityOAuth核心源码解析 蓝色表示接口,绿色表示类 1,TokenEndpoint 整个入口点,相当于一个controller,不同的授权模式获取token的地址都是 /oa ...
- Spring Security构建Rest服务-1203-Spring Security OAuth开发APP认证框架之短信验证码登录
浏览器模式下验证码存储策略 浏览器模式下,生成的短信验证码或者图形验证码是存在session里的,用户接收到验证码后携带过来做校验. APP模式下验证码存储策略 在app场景下里是没有cookie信息 ...
- Spring Cloud构建微服务架构(三)消息总线
注:此文不适合0基础学习者直接阅读,请先完整的将作者关于微服务的博文全部阅读一遍,如果还有疑问,可以再来阅读此文,地址:http://blog.csdn.net/sosfnima/article/d ...
- 构建微服务:Spring boot
构建微服务:Spring boot 在上篇文章构建微服务:Spring boot 提高篇中简单介绍了一下spring data jpa的基础性使用,这篇文章将更加全面的介绍spring data jp ...
- Spring Cloud构建微服务架构(二)服务消费者
Netflix Ribbon is an Inter Process Communication (IPC) cloud library. Ribbon primarily provides clie ...
随机推荐
- UVaLive 6525 Attacking rooks (二分图最大匹配)
题意:给定一个 n * n的图,X是卒, . 是空位置,让你放尽量多的车,使得他们不互相攻击. 析:把每行连续的 . 看成X集体的一个点,同理也是这样,然后求一个最大匹配即可. 代码如下: #prag ...
- 如何设置vim中tab键缩进---配置初始化设置
转载自:http://blog.51cto.com/xuding/1725376:加了一些补充说明 问题: Linux系统下,Tab键默认为8个字符,需呀将其修改为4个字符的方式使用 步骤: 1.在用 ...
- java基础-day4
第04天 java基础语法 今日内容介绍 u Random u 数组 第1章 Random 1.1 产生整数随机数 1.1.1 Random的使用步骤 我们想产生1~100(包含1 ...
- Codeforces777B Game of Credit Cards 2017-05-04 17:19 29人阅读 评论(0) 收藏
B. Game of Credit Cards time limit per test 2 seconds memory limit per test 256 megabytes input stan ...
- sublime text 插件 -- 获取文件名到剪贴板
日常开发使用 sublime text 有好长一段时间了,有时候想拷贝当前正在编辑的文件名时发现没有很快捷的方法,一般都是先点击右键菜单栏中的 Reveal in Side Bar 对文件进行定位(在 ...
- Python学习-32.Python中os模块的一些方法
首先肯定是要引入os模块了. import os getcwd方法: print(os.getcwd()) 上面的语句将会输出当前的工作目录,相当于C#中的Environment.CurrentDir ...
- Python学习-17.Python中的错误处理(二)
错误是多种多样的,在 except 语句中,可以捕获指定的异常 修改代码如下: import io path = r'' mode = 'w' try: file = open(path,mode) ...
- Jesery客户端工具类
public class JerseyClientUtil { public static<T> T sendMsg(String url,Object object,Class<T ...
- 《JavaScript高级程序设计》3.7 函数
位于return语句之后的代码不会执行; return语句也可以不带有任何返回值. 这种情况下, 函数在停止执行后会返回undefined值. 这种用法一般用在需要提前停止函数执行而又不需要返回值的情 ...
- OpenStack qemu-guest-agent 使用
What is qemu-ga 我个人认为qemu-ga是在虚拟机中安装的一个agent,宿主机host通过通道(unix socket)与虚拟机vm内部的agent进行通信,这样宿主机就有了一种从外 ...