
Shiftdel walkthrough Intermediate
点击查看代码
nmap -p- -A 192.168.167.174

Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-11-12 00:09 UTC

Nmap scan report for 192.168.167.174

Host is up (0.071s latency).

Not shown: 65532 closed tcp ports (reset)

PORT     STATE SERVICE VERSION

22/tcp   open  ssh     OpenSSH 7.9p1 Debian 10+deb10u2 (protocol 2.0)

| ssh-hostkey:

|   2048 74:ba:20:23:89:92:62:02:9f:e7:3d:3b:83:d4:d9:6c (RSA)

|   256 54:8f:79:55:5a:b0:3a:69:5a:d5:72:39:64:fd:07:4e (ECDSA)

|_  256 7f:5d:10:27:62:ba:75:e9:bc:c8:4f:e2:72:87:d4:e2 (ED25519)

80/tcp   open  http    Apache httpd 2.4.38 ((Debian))

|_http-generator: WordPress 4.9.6

|_http-server-header: Apache/2.4.38 (Debian)

|_http-title: Shiftdel

8888/tcp open  http    Apache httpd 2.4.38 ((Debian))

|_http-title: phpMyAdmin

|_http-server-header: Apache/2.4.38 (Debian)

| http-robots.txt: 1 disallowed entry

|_/

No exact OS matches for host (If you know what OS is running on it, see https://nmap.org/submit/ ).

TCP/IP fingerprint:

OS:SCAN(V=7.94SVN%E=4%D=11/12%OT=22%CT=1%CU=33279%PV=Y%DS=4%DC=T%G=Y%TM=673

OS:29D05%P=x86_64-pc-linux-gnu)SEQ(SP=108%GCD=1%ISR=10B%TI=Z%II=I%TS=A)OPS(

OS:O1=M551ST11NW7%O2=M551ST11NW7%O3=M551NNT11NW7%O4=M551ST11NW7%O5=M551ST11

OS:NW7%O6=M551ST11)WIN(W1=FE88%W2=FE88%W3=FE88%W4=FE88%W5=FE88%W6=FE88)ECN(

OS:R=Y%DF=Y%T=40%W=FAF0%O=M551NNSNW7%CC=Y%Q=)T1(R=Y%DF=Y%T=40%S=O%A=S+%F=AS

OS:%RD=0%Q=)T2(R=N)T3(R=N)T4(R=N)T5(R=Y%DF=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0

OS:%Q=)T6(R=N)T7(R=N)U1(R=Y%DF=N%T=40%IPL=164%UN=0%RIPL=G%RID=G%RIPCK=G%RUC

OS:K=F4D9%RUD=G)IE(R=Y%DFI=N%T=40%CD=S)
探测phpmyadmin版本
whatweb http://192.168.167.174:8888/

http://192.168.167.174:8888/ [200 OK] Apache[2.4.38], Content-Security-Policy[default-src 'self' ;options inline-script eval-script;referrer no-referrer;img-src 'self' data:  *.tile.openstreetmap.org;object-src 'none';,default-src 'self' ;script-src 'self'  'unsafe-inline' 'unsafe-eval';referrer no-referrer;style-src 'self' 'unsafe-inline' ;img-src 'self' data:  *.tile.openstreetmap.org;object-src 'none';], Cookies[phpMyAdmin,pma_lang], Country[RESERVED][ZZ], HTML5, HTTPServer[Debian Linux][Apache/2.4.38 (Debian)], HttpOnly[phpMyAdmin,pma_lang], IP[192.168.167.174], JQuery, PasswordField[pma_password], Script[text/javascript], Title[phpMyAdmin], UncommonHeaders[x-ob_mode,referrer-policy,content-security-policy,x-content-security-policy,x-webkit-csp,x-content-type-options,x-permitted-cross-domain-policies,x-robots-tag], X-Frame-Options[DENY], X-UA-Compatible[IE=Edge], X-XSS-Protection[1; mode=block], phpMyAdmin[4.8.1]
用wpscan 枚举用户
点击查看代码
┌──(root㉿kali)-[~]

└─# wpscan --url http://192.168.167.174/ -eu --api-token + 自己的token

_______________________________________________________________

         __          _______   _____

         \ \        / /  __ \ / ____|

          \ \  /\  / /| |__) | (___   ___  __ _ _ __

           \ \/  \/ / |  ___/ \___ \ / __|/ _` | '_ \

            \  /\  /  | |     ____) | (__| (_| | | | |

             \/  \/   |_|    |_____/ \___|\__,_|_| |_|

         WordPress Security Scanner by the WPScan Team

                         Version 3.8.27

       Sponsored by Automattic - https://automattic.com/

       @_WPScan_, @ethicalhack3r, @erwan_lr, @firefart

_______________________________________________________________

[i] It seems like you have not updated the database for some time.

[?] Do you want to update now? [Y]es [N]o, default: [N]

[+] URL: http://192.168.167.174/ [192.168.167.174]

[+] Started: Tue Nov 12 00:11:29 2024

Interesting Finding(s):

[+] Headers

 | Interesting Entry: Server: Apache/2.4.38 (Debian)

 | Found By: Headers (Passive Detection)

 | Confidence: 100%

[+] WordPress readme found: http://192.168.167.174/readme.html

 | Found By: Direct Access (Aggressive Detection)

 | Confidence: 100%

[+] Upload directory has listing enabled: http://192.168.167.174/wp-content/uploads/

 | Found By: Direct Access (Aggressive Detection)

 | Confidence: 100%

[+] The external WP-Cron seems to be enabled: http://192.168.167.174/wp-cron.php

 | Found By: Direct Access (Aggressive Detection)

 | Confidence: 60%

 | References:

 |  - https://www.iplocation.net/defend-wordpress-from-ddos

 |  - https://github.com/wpscanteam/wpscan/issues/1299

[+] WordPress version 4.9.6 identified (Insecure, released on 2018-05-17).

 | Found By: Emoji Settings (Passive Detection)

 |  - http://192.168.167.174/, Match: 'wp-includes\/js\/wp-emoji-release.min.js?ver=4.9.6'

 | Confirmed By: Meta Generator (Passive Detection)

 |  - http://192.168.167.174/, Match: 'WordPress 4.9.6'

 |

 | [!] 64 vulnerabilities identified:

 |

 | [!] Title: WordPress <= 4.9.6 - Authenticated Arbitrary File Deletion

 |     Fixed in: 4.9.7

 |     References:

 |      - https://wpscan.com/vulnerability/42ab2bd9-bbb1-4f25-a632-1811c5130bb4

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-12895

 |      - https://blog.ripstech.com/2018/wordpress-file-delete-to-code-execution/

 |      - http://blog.vulnspy.com/2018/06/27/Wordpress-4-9-6-Arbitrary-File-Delection-Vulnerbility-Exploit/

 |      - https://github.com/WordPress/WordPress/commit/c9dce0606b0d7e6f494d4abe7b193ac046a322cd

 |      - https://wordpress.org/news/2018/07/wordpress-4-9-7-security-and-maintenance-release/

 |      - https://www.wordfence.com/blog/2018/07/details-of-an-additional-file-deletion-vulnerability-patched-in-wordpress-4-9-7/

 |

 | [!] Title: WordPress <= 5.0 - Authenticated File Delete

 |     Fixed in: 4.9.9

 |     References:

 |      - https://wpscan.com/vulnerability/e3ef8976-11cb-4854-837f-786f43cbdf44

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-20147

 |      - https://wordpress.org/news/2018/12/wordpress-5-0-1-security-release/

 |

 | [!] Title: WordPress <= 5.0 - Authenticated Post Type Bypass

 |     Fixed in: 4.9.9

 |     References:

 |      - https://wpscan.com/vulnerability/999dba5a-82fb-4717-89c3-6ed723cc7e45

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-20152

 |      - https://wordpress.org/news/2018/12/wordpress-5-0-1-security-release/

 |      - https://blog.ripstech.com/2018/wordpress-post-type-privilege-escalation/

 |

 | [!] Title: WordPress <= 5.0 - PHP Object Injection via Meta Data

 |     Fixed in: 4.9.9

 |     References:

 |      - https://wpscan.com/vulnerability/046ff6a0-90b2-4251-98fc-b7fba93f8334

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-20148

 |      - https://wordpress.org/news/2018/12/wordpress-5-0-1-security-release/

 |

 | [!] Title: WordPress <= 5.0 - Authenticated Cross-Site Scripting (XSS)

 |     Fixed in: 4.9.9

 |     References:

 |      - https://wpscan.com/vulnerability/3182002e-d831-4412-a27d-a5e39bb44314

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-20153

 |      - https://wordpress.org/news/2018/12/wordpress-5-0-1-security-release/

 |

 | [!] Title: WordPress <= 5.0 - Cross-Site Scripting (XSS) that could affect plugins

 |     Fixed in: 4.9.9

 |     References:

 |      - https://wpscan.com/vulnerability/7f7a0795-4dd7-417d-804e-54f12595d1e4

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-20150

 |      - https://wordpress.org/news/2018/12/wordpress-5-0-1-security-release/

 |      - https://github.com/WordPress/WordPress/commit/fb3c6ea0618fcb9a51d4f2c1940e9efcd4a2d460

 |

 | [!] Title: WordPress <= 5.0 - User Activation Screen Search Engine Indexing

 |     Fixed in: 4.9.9

 |     References:

 |      - https://wpscan.com/vulnerability/65f1aec4-6d28-4396-88d7-66702b21c7a2

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-20151

 |      - https://wordpress.org/news/2018/12/wordpress-5-0-1-security-release/

 |

 | [!] Title: WordPress <= 5.0 - File Upload to XSS on Apache Web Servers

 |     Fixed in: 4.9.9

 |     References:

 |      - https://wpscan.com/vulnerability/d741f5ae-52ca-417d-a2ca-acdfb7ca5808

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-20149

 |      - https://wordpress.org/news/2018/12/wordpress-5-0-1-security-release/

 |      - https://github.com/WordPress/WordPress/commit/246a70bdbfac3bd45ff71c7941deef1bb206b19a

 |

 | [!] Title: WordPress 3.7-5.0 (except 4.9.9) - Authenticated Code Execution

 |     Fixed in: 4.9.9

 |     References:

 |      - https://wpscan.com/vulnerability/1a693e57-f99c-4df6-93dd-0cdc92fd0526

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-8942

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-8943

 |      - https://blog.ripstech.com/2019/wordpress-image-remote-code-execution/

 |      - https://www.rapid7.com/db/modules/exploit/multi/http/wp_crop_rce

 |

 | [!] Title: WordPress 3.9-5.1 - Comment Cross-Site Scripting (XSS)

 |     Fixed in: 4.9.10

 |     References:

 |      - https://wpscan.com/vulnerability/d150f43f-6030-4191-98b8-20ae05585936

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-9787

 |      - https://github.com/WordPress/WordPress/commit/0292de60ec78c5a44956765189403654fe4d080b

 |      - https://wordpress.org/news/2019/03/wordpress-5-1-1-security-and-maintenance-release/

 |      - https://blog.ripstech.com/2019/wordpress-csrf-to-rce/

 |

 | [!] Title: WordPress <= 5.2.2 - Cross-Site Scripting (XSS) in URL Sanitisation

 |     Fixed in: 4.9.11

 |     References:

 |      - https://wpscan.com/vulnerability/4494a903-5a73-4cad-8c14-1e7b4da2be61

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-16222

 |      - https://wordpress.org/news/2019/09/wordpress-5-2-3-security-and-maintenance-release/

 |      - https://github.com/WordPress/WordPress/commit/30ac67579559fe42251b5a9f887211bf61a8ed68

 |      - https://hackerone.com/reports/339483

 |

 | [!] Title: WordPress <= 5.2.3 - Stored XSS in Customizer

 |     Fixed in: 4.9.12

 |     References:

 |      - https://wpscan.com/vulnerability/d39a7b84-28b9-4916-a2fc-6192ceb6fa56

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17674

 |      - https://wordpress.org/news/2019/10/wordpress-5-2-4-security-release/

 |      - https://blog.wpscan.com/wordpress/security/release/2019/10/15/wordpress-524-security-release-breakdown.html

 |

 | [!] Title: WordPress <= 5.2.3 - Unauthenticated View Private/Draft Posts

 |     Fixed in: 4.9.12

 |     References:

 |      - https://wpscan.com/vulnerability/3413b879-785f-4c9f-aa8a-5a4a1d5e0ba2

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17671

 |      - https://wordpress.org/news/2019/10/wordpress-5-2-4-security-release/

 |      - https://blog.wpscan.com/wordpress/security/release/2019/10/15/wordpress-524-security-release-breakdown.html

 |      - https://github.com/WordPress/WordPress/commit/f82ed753cf00329a5e41f2cb6dc521085136f308

 |      - https://0day.work/proof-of-concept-for-wordpress-5-2-3-viewing-unauthenticated-posts/

 |

 | [!] Title: WordPress <= 5.2.3 - Stored XSS in Style Tags

 |     Fixed in: 4.9.12

 |     References:

 |      - https://wpscan.com/vulnerability/d005b1f8-749d-438a-8818-21fba45c6465

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17672

 |      - https://wordpress.org/news/2019/10/wordpress-5-2-4-security-release/

 |      - https://blog.wpscan.com/wordpress/security/release/2019/10/15/wordpress-524-security-release-breakdown.html

 |

 | [!] Title: WordPress <= 5.2.3 - JSON Request Cache Poisoning

 |     Fixed in: 4.9.12

 |     References:

 |      - https://wpscan.com/vulnerability/7804d8ed-457a-407e-83a7-345d3bbe07b2

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17673

 |      - https://wordpress.org/news/2019/10/wordpress-5-2-4-security-release/

 |      - https://github.com/WordPress/WordPress/commit/b224c251adfa16a5f84074a3c0886270c9df38de

 |      - https://blog.wpscan.com/wordpress/security/release/2019/10/15/wordpress-524-security-release-breakdown.html

 |

 | [!] Title: WordPress <= 5.2.3 - Server-Side Request Forgery (SSRF) in URL Validation

 |     Fixed in: 4.9.12

 |     References:

 |      - https://wpscan.com/vulnerability/26a26de2-d598-405d-b00c-61f71cfacff6

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17669

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17670

 |      - https://wordpress.org/news/2019/10/wordpress-5-2-4-security-release/

 |      - https://github.com/WordPress/WordPress/commit/9db44754b9e4044690a6c32fd74b9d5fe26b07b2

 |      - https://blog.wpscan.com/wordpress/security/release/2019/10/15/wordpress-524-security-release-breakdown.html

 |

 | [!] Title: WordPress <= 5.2.3 - Admin Referrer Validation

 |     Fixed in: 4.9.12

 |     References:

 |      - https://wpscan.com/vulnerability/715c00e3-5302-44ad-b914-131c162c3f71

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17675

 |      - https://wordpress.org/news/2019/10/wordpress-5-2-4-security-release/

 |      - https://github.com/WordPress/WordPress/commit/b183fd1cca0b44a92f0264823dd9f22d2fd8b8d0

 |      - https://blog.wpscan.com/wordpress/security/release/2019/10/15/wordpress-524-security-release-breakdown.html

 |

 | [!] Title: WordPress <= 5.3 - Authenticated Improper Access Controls in REST API

 |     Fixed in: 4.9.13

 |     References:

 |      - https://wpscan.com/vulnerability/4a6de154-5fbd-4c80-acd3-8902ee431bd8

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-20043

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-16788

 |      - https://wordpress.org/news/2019/12/wordpress-5-3-1-security-and-maintenance-release/

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-g7rg-hchx-c2gw

 |

 | [!] Title: WordPress <= 5.3 - Authenticated Stored XSS via Crafted Links

 |     Fixed in: 4.9.13

 |     References:

 |      - https://wpscan.com/vulnerability/23553517-34e3-40a9-a406-f3ffbe9dd265

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-20042

 |      - https://wordpress.org/news/2019/12/wordpress-5-3-1-security-and-maintenance-release/

 |      - https://hackerone.com/reports/509930

 |      - https://github.com/WordPress/wordpress-develop/commit/1f7f3f1f59567e2504f0fbebd51ccf004b3ccb1d

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-xvg2-m2f4-83m7

 |

 | [!] Title: WordPress <= 5.3 - Authenticated Stored XSS via Block Editor Content

 |     Fixed in: 4.9.13

 |     References:

 |      - https://wpscan.com/vulnerability/be794159-4486-4ae1-a5cc-5c190e5ddf5f

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-16781

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-16780

 |      - https://wordpress.org/news/2019/12/wordpress-5-3-1-security-and-maintenance-release/

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-pg4x-64rh-3c9v

 |

 | [!] Title: WordPress <= 5.3 - wp_kses_bad_protocol() Colon Bypass

 |     Fixed in: 4.9.13

 |     References:

 |      - https://wpscan.com/vulnerability/8fac612b-95d2-477a-a7d6-e5ec0bb9ca52

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-20041

 |      - https://wordpress.org/news/2019/12/wordpress-5-3-1-security-and-maintenance-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/b1975463dd995da19bb40d3fa0786498717e3c53

 |

 | [!] Title: WordPress < 5.4.1 - Password Reset Tokens Failed to Be Properly Invalidated

 |     Fixed in: 4.9.14

 |     References:

 |      - https://wpscan.com/vulnerability/7db191c0-d112-4f08-a419-a1cd81928c4e

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-11027

 |      - https://wordpress.org/news/2020/04/wordpress-5-4-1/

 |      - https://core.trac.wordpress.org/changeset/47634/

 |      - https://www.wordfence.com/blog/2020/04/unpacking-the-7-vulnerabilities-fixed-in-todays-wordpress-5-4-1-security-update/

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-ww7v-jg8c-q6jw

 |

 | [!] Title: WordPress < 5.4.1 - Unauthenticated Users View Private Posts

 |     Fixed in: 4.9.14

 |     References:

 |      - https://wpscan.com/vulnerability/d1e1ba25-98c9-4ae7-8027-9632fb825a56

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-11028

 |      - https://wordpress.org/news/2020/04/wordpress-5-4-1/

 |      - https://core.trac.wordpress.org/changeset/47635/

 |      - https://www.wordfence.com/blog/2020/04/unpacking-the-7-vulnerabilities-fixed-in-todays-wordpress-5-4-1-security-update/

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-xhx9-759f-6p2w

 |

 | [!] Title: WordPress < 5.4.1 - Authenticated Cross-Site Scripting (XSS) in Customizer

 |     Fixed in: 4.9.14

 |     References:

 |      - https://wpscan.com/vulnerability/4eee26bd-a27e-4509-a3a5-8019dd48e429

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-11025

 |      - https://wordpress.org/news/2020/04/wordpress-5-4-1/

 |      - https://core.trac.wordpress.org/changeset/47633/

 |      - https://www.wordfence.com/blog/2020/04/unpacking-the-7-vulnerabilities-fixed-in-todays-wordpress-5-4-1-security-update/

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-4mhg-j6fx-5g3c

 |

 | [!] Title: WordPress < 5.4.1 - Cross-Site Scripting (XSS) in wp-object-cache

 |     Fixed in: 4.9.14

 |     References:

 |      - https://wpscan.com/vulnerability/e721d8b9-a38f-44ac-8520-b4a9ed6a5157

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-11029

 |      - https://wordpress.org/news/2020/04/wordpress-5-4-1/

 |      - https://core.trac.wordpress.org/changeset/47637/

 |      - https://www.wordfence.com/blog/2020/04/unpacking-the-7-vulnerabilities-fixed-in-todays-wordpress-5-4-1-security-update/

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-568w-8m88-8g2c

 |

 | [!] Title: WordPress < 5.4.1 - Authenticated Cross-Site Scripting (XSS) in File Uploads

 |     Fixed in: 4.9.14

 |     References:

 |      - https://wpscan.com/vulnerability/55438b63-5fc9-4812-afc4-2f1eff800d5f

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-11026

 |      - https://wordpress.org/news/2020/04/wordpress-5-4-1/

 |      - https://core.trac.wordpress.org/changeset/47638/

 |      - https://www.wordfence.com/blog/2020/04/unpacking-the-7-vulnerabilities-fixed-in-todays-wordpress-5-4-1-security-update/

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-3gw2-4656-pfr2

 |      - https://hackerone.com/reports/179695

 |

 | [!] Title: WordPress 4.7-5.7 - Authenticated Password Protected Pages Exposure

 |     Fixed in: 4.9.17

 |     References:

 |      - https://wpscan.com/vulnerability/6a3ec618-c79e-4b9c-9020-86b157458ac5

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2021-29450

 |      - https://wordpress.org/news/2021/04/wordpress-5-7-1-security-and-maintenance-release/

 |      - https://blog.wpscan.com/2021/04/15/wordpress-571-security-vulnerability-release.html

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-pmmh-2f36-wvhq

 |      - https://core.trac.wordpress.org/changeset/50717/

 |      - https://www.youtube.com/watch?v=J2GXmxAdNWs

 |

 | [!] Title: WordPress 3.7 to 5.7.1 - Object Injection in PHPMailer

 |     Fixed in: 4.9.18

 |     References:

 |      - https://wpscan.com/vulnerability/4cd46653-4470-40ff-8aac-318bee2f998d

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-36326

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-19296

 |      - https://github.com/WordPress/WordPress/commit/267061c9595fedd321582d14c21ec9e7da2dcf62

 |      - https://wordpress.org/news/2021/05/wordpress-5-7-2-security-release/

 |      - https://github.com/PHPMailer/PHPMailer/commit/e2e07a355ee8ff36aba21d0242c5950c56e4c6f9

 |      - https://www.wordfence.com/blog/2021/05/wordpress-5-7-2-security-release-what-you-need-to-know/

 |      - https://www.youtube.com/watch?v=HaW15aMzBUM

 |

 | [!] Title: WordPress < 5.8 - Plugin Confusion

 |     Fixed in: 5.8

 |     References:

 |      - https://wpscan.com/vulnerability/95e01006-84e4-4e95-b5d7-68ea7b5aa1a8

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2021-44223

 |      - https://vavkamil.cz/2021/11/25/wordpress-plugin-confusion-update-can-get-you-pwned/

 |

 | [!] Title: WordPress < 5.8.3 - SQL Injection via WP_Query

 |     Fixed in: 4.9.19

 |     References:

 |      - https://wpscan.com/vulnerability/7f768bcf-ed33-4b22-b432-d1e7f95c1317

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2022-21661

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-6676-cqfm-gw84

 |      - https://hackerone.com/reports/1378209

 |

 | [!] Title: WordPress < 5.8.3 - Author+ Stored XSS via Post Slugs

 |     Fixed in: 4.9.19

 |     References:

 |      - https://wpscan.com/vulnerability/dc6f04c2-7bf2-4a07-92b5-dd197e4d94c8

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2022-21662

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-699q-3hj9-889w

 |      - https://hackerone.com/reports/425342

 |      - https://blog.sonarsource.com/wordpress-stored-xss-vulnerability

 |

 | [!] Title: WordPress 4.1-5.8.2 - SQL Injection via WP_Meta_Query

 |     Fixed in: 4.9.19

 |     References:

 |      - https://wpscan.com/vulnerability/24462ac4-7959-4575-97aa-a6dcceeae722

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2022-21664

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-jp3p-gw8h-6x86

 |

 | [!] Title: WordPress < 5.8.3 - Super Admin Object Injection in Multisites

 |     Fixed in: 4.9.19

 |     References:

 |      - https://wpscan.com/vulnerability/008c21ab-3d7e-4d97-b6c3-db9d83f390a7

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2022-21663

 |      - https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-jmmq-m8p8-332h

 |      - https://hackerone.com/reports/541469

 |

 | [!] Title: WordPress < 5.9.2 - Prototype Pollution in jQuery

 |     Fixed in: 4.9.20

 |     References:

 |      - https://wpscan.com/vulnerability/1ac912c1-5e29-41ac-8f76-a062de254c09

 |      - https://wordpress.org/news/2022/03/wordpress-5-9-2-security-maintenance-release/

 |

 | [!] Title: WP < 6.0.2 - Reflected Cross-Site Scripting

 |     Fixed in: 4.9.21

 |     References:

 |      - https://wpscan.com/vulnerability/622893b0-c2c4-4ee7-9fa1-4cecef6e36be

 |      - https://wordpress.org/news/2022/08/wordpress-6-0-2-security-and-maintenance-release/

 |

 | [!] Title: WP < 6.0.2 - Authenticated Stored Cross-Site Scripting

 |     Fixed in: 4.9.21

 |     References:

 |      - https://wpscan.com/vulnerability/3b1573d4-06b4-442b-bad5-872753118ee0

 |      - https://wordpress.org/news/2022/08/wordpress-6-0-2-security-and-maintenance-release/

 |

 | [!] Title: WP < 6.0.2 - SQLi via Link API

 |     Fixed in: 4.9.21

 |     References:

 |      - https://wpscan.com/vulnerability/601b0bf9-fed2-4675-aec7-fed3156a022f

 |      - https://wordpress.org/news/2022/08/wordpress-6-0-2-security-and-maintenance-release/

 |

 | [!] Title: WP < 6.0.3 - Stored XSS via wp-mail.php

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/713bdc8b-ab7c-46d7-9847-305344a579c4

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/abf236fdaf94455e7bc6e30980cf70401003e283

 |

 | [!] Title: WP < 6.0.3 - Open Redirect via wp_nonce_ays

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/926cd097-b36f-4d26-9c51-0dfab11c301b

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/506eee125953deb658307bb3005417cb83f32095

 |

 | [!] Title: WP < 6.0.3 - Email Address Disclosure via wp-mail.php

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/c5675b59-4b1d-4f64-9876-068e05145431

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/5fcdee1b4d72f1150b7b762ef5fb39ab288c8d44

 |

 | [!] Title: WP < 6.0.3 - Reflected XSS via SQLi in Media Library

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/cfd8b50d-16aa-4319-9c2d-b227365c2156

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/8836d4682264e8030067e07f2f953a0f66cb76cc

 |

 | [!] Title: WP < 6.0.3 - CSRF in wp-trackback.php

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/b60a6557-ae78-465c-95bc-a78cf74a6dd0

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/a4f9ca17fae0b7d97ff807a3c234cf219810fae0

 |

 | [!] Title: WP < 6.0.3 - Stored XSS via the Customizer

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/2787684c-aaef-4171-95b4-ee5048c74218

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/2ca28e49fc489a9bb3c9c9c0d8907a033fe056ef

 |

 | [!] Title: WP < 6.0.3 - Stored XSS via Comment Editing

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/02d76d8e-9558-41a5-bdb6-3957dc31563b

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/89c8f7919460c31c0f259453b4ffb63fde9fa955

 |

 | [!] Title: WP < 6.0.3 - Content from Multipart Emails Leaked

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/3f707e05-25f0-4566-88ed-d8d0aff3a872

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/3765886b4903b319764490d4ad5905bc5c310ef8

 |

 | [!] Title: WP < 6.0.3 - SQLi in WP_Date_Query

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/1da03338-557f-4cb6-9a65-3379df4cce47

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/d815d2e8b2a7c2be6694b49276ba3eee5166c21f

 |

 | [!] Title: WP < 6.0.3 - Stored XSS via RSS Widget

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/58d131f5-f376-4679-b604-2b888de71c5b

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/929cf3cb9580636f1ae3fe944b8faf8cca420492

 |

 | [!] Title: WP < 6.0.3 - Data Exposure via REST Terms/Tags Endpoint

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/b27a8711-a0c0-4996-bd6a-01734702913e

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/wordpress-develop/commit/ebaac57a9ac0174485c65de3d32ea56de2330d8e

 |

 | [!] Title: WP < 6.0.3 - Multiple Stored XSS via Gutenberg

 |     Fixed in: 4.9.22

 |     References:

 |      - https://wpscan.com/vulnerability/f513c8f6-2e1c-45ae-8a58-36b6518e2aa9

 |      - https://wordpress.org/news/2022/10/wordpress-6-0-3-security-release/

 |      - https://github.com/WordPress/gutenberg/pull/45045/files

 |

 | [!] Title: WP <= 6.2 - Unauthenticated Blind SSRF via DNS Rebinding

 |     References:

 |      - https://wpscan.com/vulnerability/c8814e6e-78b3-4f63-a1d3-6906a84c1f11

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2022-3590

 |      - https://blog.sonarsource.com/wordpress-core-unauthenticated-blind-ssrf/

 |

 | [!] Title: WP < 6.2.1 - Directory Traversal via Translation Files

 |     Fixed in: 4.9.23

 |     References:

 |      - https://wpscan.com/vulnerability/2999613a-b8c8-4ec0-9164-5dfe63adf6e6

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2023-2745

 |      - https://wordpress.org/news/2023/05/wordpress-6-2-1-maintenance-security-release/

 |

 | [!] Title: WP < 6.2.1 - Thumbnail Image Update via CSRF

 |     Fixed in: 4.9.23

 |     References:

 |      - https://wpscan.com/vulnerability/a03d744a-9839-4167-a356-3e7da0f1d532

 |      - https://wordpress.org/news/2023/05/wordpress-6-2-1-maintenance-security-release/

 |

 | [!] Title: WP < 6.2.1 - Contributor+ Stored XSS via Open Embed Auto Discovery

 |     Fixed in: 4.9.23

 |     References:

 |      - https://wpscan.com/vulnerability/3b574451-2852-4789-bc19-d5cc39948db5

 |      - https://wordpress.org/news/2023/05/wordpress-6-2-1-maintenance-security-release/

 |

 | [!] Title: WP < 6.2.2 - Shortcode Execution in User Generated Data

 |     Fixed in: 4.9.23

 |     References:

 |      - https://wpscan.com/vulnerability/ef289d46-ea83-4fa5-b003-0352c690fd89

 |      - https://wordpress.org/news/2023/05/wordpress-6-2-1-maintenance-security-release/

 |      - https://wordpress.org/news/2023/05/wordpress-6-2-2-security-release/

 |

 | [!] Title: WP < 6.2.1 - Contributor+ Content Injection

 |     Fixed in: 4.9.23

 |     References:

 |      - https://wpscan.com/vulnerability/1527ebdb-18bc-4f9d-9c20-8d729a628670

 |      - https://wordpress.org/news/2023/05/wordpress-6-2-1-maintenance-security-release/

 |

 | [!] Title: WP < 6.3.2 - Denial of Service via Cache Poisoning

 |     Fixed in: 4.9.24

 |     References:

 |      - https://wpscan.com/vulnerability/6d80e09d-34d5-4fda-81cb-e703d0e56e4f

 |      - https://wordpress.org/news/2023/10/wordpress-6-3-2-maintenance-and-security-release/

 |

 | [!] Title: WP < 6.3.2 - Subscriber+ Arbitrary Shortcode Execution

 |     Fixed in: 4.9.24

 |     References:

 |      - https://wpscan.com/vulnerability/3615aea0-90aa-4f9a-9792-078a90af7f59

 |      - https://wordpress.org/news/2023/10/wordpress-6-3-2-maintenance-and-security-release/

 |

 | [!] Title: WP < 6.3.2 - Contributor+ Comment Disclosure

 |     Fixed in: 4.9.24

 |     References:

 |      - https://wpscan.com/vulnerability/d35b2a3d-9b41-4b4f-8e87-1b8ccb370b9f

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2023-39999

 |      - https://wordpress.org/news/2023/10/wordpress-6-3-2-maintenance-and-security-release/

 |

 | [!] Title: WP < 6.3.2 - Unauthenticated Post Author Email Disclosure

 |     Fixed in: 4.9.24

 |     References:

 |      - https://wpscan.com/vulnerability/19380917-4c27-4095-abf1-eba6f913b441

 |      - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2023-5561

 |      - https://wpscan.com/blog/email-leak-oracle-vulnerability-addressed-in-wordpress-6-3-2/

 |      - https://wordpress.org/news/2023/10/wordpress-6-3-2-maintenance-and-security-release/

 |

 | [!] Title: WordPress < 6.4.3 - Deserialization of Untrusted Data

 |     Fixed in: 4.9.25

 |     References:

 |      - https://wpscan.com/vulnerability/5e9804e5-bbd4-4836-a5f0-b4388cc39225

 |      - https://wordpress.org/news/2024/01/wordpress-6-4-3-maintenance-and-security-release/

 |

 | [!] Title: WordPress < 6.4.3 - Admin+ PHP File Upload

 |     Fixed in: 4.9.25

 |     References:

 |      - https://wpscan.com/vulnerability/a8e12fbe-c70b-4078-9015-cf57a05bdd4a

 |      - https://wordpress.org/news/2024/01/wordpress-6-4-3-maintenance-and-security-release/

 |

 | [!] Title: WordPress < 6.5.5 - Contributor+ Stored XSS in HTML API

 |     Fixed in: 4.9.26

 |     References:

 |      - https://wpscan.com/vulnerability/2c63f136-4c1f-4093-9a8c-5e51f19eae28

 |      - https://wordpress.org/news/2024/06/wordpress-6-5-5/

 |

 | [!] Title: WordPress < 6.5.5 - Contributor+ Stored XSS in Template-Part Block

 |     Fixed in: 4.9.26

 |     References:

 |      - https://wpscan.com/vulnerability/7c448f6d-4531-4757-bff0-be9e3220bbbb

 |      - https://wordpress.org/news/2024/06/wordpress-6-5-5/

 |

 | [!] Title: WordPress < 6.5.5 - Contributor+ Path Traversal in Template-Part Block

 |     Fixed in: 4.9.26

 |     References:

 |      - https://wpscan.com/vulnerability/36232787-754a-4234-83d6-6ded5e80251c

 |      - https://wordpress.org/news/2024/06/wordpress-6-5-5/

[+] WordPress theme in use: twentyfifteen

 | Location: http://192.168.167.174/wp-content/themes/twentyfifteen/

 | Last Updated: 2024-07-16T00:00:00.000Z

 | Readme: http://192.168.167.174/wp-content/themes/twentyfifteen/readme.txt

 | [!] The version is out of date, the latest version is 3.8

 | Style URL: http://192.168.167.174/wp-content/themes/twentyfifteen/style.css?ver=4.9.6

 | Style Name: Twenty Fifteen

 | Style URI: https://wordpress.org/themes/twentyfifteen/

 | Description: Our 2015 default theme is clean, blog-focused, and designed for clarity. Twenty Fifteen's simple, st...

 | Author: the WordPress team

 | Author URI: https://wordpress.org/

 |

 | Found By: Css Style In Homepage (Passive Detection)

 |

 | Version: 2.0 (80% confidence)

 | Found By: Style (Passive Detection)

 |  - http://192.168.167.174/wp-content/themes/twentyfifteen/style.css?ver=4.9.6, Match: 'Version: 2.0'

[+] Enumerating Users (via Passive and Aggressive Methods)

 Brute Forcing Author IDs - Time: 00:00:00 <====================================================================================================================> (10 / 10) 100.00% Time: 00:00:00

[i] User(s) Identified:

[+] intern

 | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection)

 | Confirmed By: Login Error Messages (Aggressive Detection)

[+] admin

 | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection)

 | Confirmed By: Login Error Messages (Aggressive Detection)

[+] WPScan DB API OK

 | Plan: free

 | Requests Done (during the scan): 2

 | Requests Remaining: 23

[+] Finished: Tue Nov 12 00:11:37 2024

[+] Requests Done: 57

[+] Cached Requests: 5

[+] Data Sent: 14.018 KB

[+] Data Received: 305.227 KB

[+] Memory used: 188.043 MB

[+] Elapsed time: 00:00:07
看了hint以后才知道突破口 其实就是没一个一个找exp
搜索到这篇文章
https://www.anquanke.com/post/id/190111
找到密码
IntraPersonalVision349
然后进去界面
之后就用这个漏洞
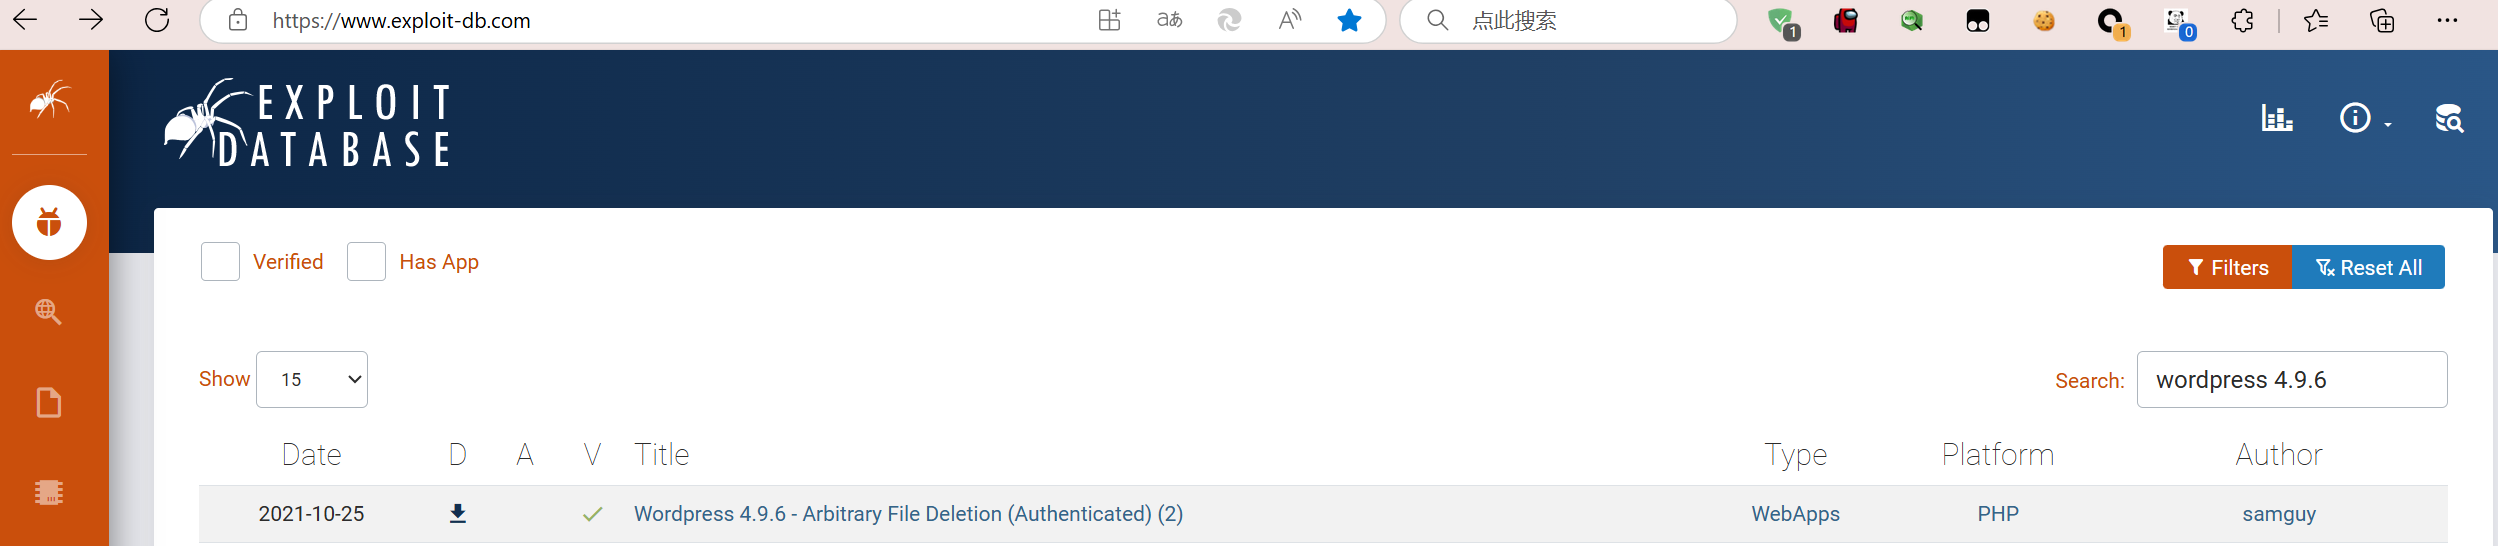
但是我按照他的步骤死活删除不掉他的./htaccess文件
直接看wp了 wp也是这个步骤但是他就删除成功了 不知道啥原因
可能靶场有点小问题 回头再战
Shiftdel walkthrough Intermediate的更多相关文章
- Bootstap datetimepicker报错TypeError: intermediate value
Bootstrap datetimepicker有多个版本,官方的链接中,只是datepicker,没有时间的选择,原版的datetimepicker也不再更新,不能用新版的jquery.现在http ...
- c++错误——intermediate.manifest : general error c1010070很傻的错
.\Debug\sadf.exe.intermediate.manifest : general error c1010070: Failed to load and parse the manife ...
- Jquery报错:Uncaught TypeError: ((m.event.special[e.origType] || (intermediate value)).handle || e.handler).apply is not a function
页面中出现了Jquery报错:Uncaught TypeError: ((m.event.special[e.origType] || (intermediate value)).handle || ...
- Bootstap datetimepicker报错TypeError: intermediate value(转)
原文转自:http://blog.chinaunix.net/uid-20332519-id-5733546.html Bootstrap datetimepicker有多个版本,官方的链接中,只是d ...
- Walkthrough: Arranging Controls on Windows Forms Using Snaplines
https://msdn.microsoft.com/en-us/library/t5b5kc41(v=vs.110).aspx Spacing and Aligning Controls Using ...
- 处理11gR2 RAC集群资源状态异常INTERMEDIATE,CHECK TIMED OUT
注意节点6,7的磁盘CRSDG的状态明显不正常.oracle@ZJHZ-PS-CMREAD-SV-RPTDW06-DB-SD:~> crsctl status resource -t |less ...
- Walkthrough: Creating and Using a Dynamic Link Library (C++)
Original Link: http://msdn.microsoft.com/zh-cn/library/ms235636.aspx Following content is only used ...
- Burp Suite Walkthrough(英文版)
Burp Suite is one of the best tools available for web application testing. Its wide variety of featu ...
- Burp Suite Walkthrough
Burp Suite is one of the best tools available for web application testing. Its wide variety of featu ...
- IL(Intermediate Language)
释义: IL是.NET框架中中间语言(Intermediate Language)的缩写.使用.NET框架提供的编译器可以直接将源程序编译为.exe或.dll文件,但此时编译出来的程序代码并不是CPU ...
随机推荐
- 零基础入门Hadoop:IntelliJ IDEA远程连接服务器中Hadoop运行WordCount
今天我们来聊一聊大数据,作为一个Hadoop的新手,我也并不敢深入探讨复杂的底层原理.因此,这篇文章的重点更多是从实际操作和入门实践的角度出发,带领大家一起了解大数据应用的基本过程.我们将通过一个经典 ...
- Java Study For Five Day( 面向对象一)
面向对象 1.面向对象的概念 2.理解面向对象 *面向对象其实是相对面向过程而言的,面向对象和面向过程都是一种思想,它们所强调的内容不一样. *面向对象:强调的是功能的行为,将功能进行了封装成了对象, ...
- ArrayList removeRange方法分析
<ArrayList原码分析>一文中提到了"为什么removeRange(int fromIndex,int toIndex)是protected的?" 先给出remo ...
- rocketMQ集群部署
RocketMQ集群部署 RocketMQ是一款非常优秀的消息中间件,运用的场景也是非常丰富,且在各大公司运用中也非常广泛.但是它是如何进行部署的呢,以及它的高可用是如何实现的呢.那么就由我来为大家讲 ...
- PowerShell一键下载Nuget某个包的所有版本
一转眼好几年没有写博客了,来博客园冒个泡,最近由于工作需要,内网办公,幸运的是只需要上传一个*.nupkg一个包信息就可以在私有nuget下载到了,下面就用PowerShell编写下载脚本,需要注意的 ...
- 获取Map中选择的要素
<span style="font-family: Arial, Helvetica, sans-serif; background-color: rgb(255, 255, 255) ...
- Bugku-CTF getshell
题目: <?php define('pfkzYUelxEGmVcdDNLTjXCSIgMBKOuHAFyRtaboqwJiQWvsZrPhn', __FILE__); $cPIHjUYxDZVB ...
- SpringBoot结合Liquibase实现数据库变更管理
https://juejin.cn/post/7171232605478584328 https://juejin.cn/post/7170857098538909732 前言 研发过程中经常涉及到数 ...
- java -jar命令运行jar包时指定外部依赖jar包
你们都知道一个java应用项目能够打包成一个jar,固然你必须指定一个拥有main函数的main class做为你这个jar包的程序入口.具体的方法是修改jar包内目录META-INF下的MANIFE ...
- H2数据库用户自定义函数方法及范例
H2数据库,是Java实现的内存数据库.可使用它作为嵌入式内存数据库,但就其特性还用更多值得应用在实际项目中的意义.之前的一篇Blog中已经描述过其使用方法及丰富的连接数据库方式. 官方主页:http ...