
Openssl req命令
一、简介
req指令用来创建和处理PKCS#10格式的证书
二、语法
openssl req [-inform PEM|DER] [-outform PEM|DER] [-in filename] [-out filename] [-text] [-pubkey] [-noout] [-verify] [-modulus] [-nodes] [-subject] [-passin arg] [-passout arg] [-key filename] [-keyform PEM|DER] [-keyout filename] [-rand file(s)] [-newkey rsa:bits] [-newkey dsa:file] [-newkey ec:file] [-digest] [-config filename] [-subj arg] [-multivalue-rdn] [-new] [-batch] [-x509] [-days n] [-set_serial n] [-newhdr][-asn1-kludge][ -no-asn1-kludge][-extensions section] [-reqexts section] [-utf8] [-nameopt option] [-reqopt option][-verbose] [engine id]
选项
 -inform arg    input format - DER or PEM

 -outform arg   output format - DER or PEM

 -in arg        input file

 -out arg       output file

 -text          text form of request

 -pubkey        output public key

 -noout         do not output REQ

 -verify        verify signature on REQ

 -modulus       RSA modulus

 -nodes         don't encrypt the output key

 -engine e      use engine e, possibly a hardware device

 -subject       output the request's subject

 -passin        private key password source

 -key file      use the private key contained in file

 -keyform arg   key file format

 -keyout arg    file to send the key to

 -rand file:file:...

                load the file (or the files in the directory) into

                the random number generator

 -newkey rsa:bits generate a new RSA key of 'bits' in size

 -newkey dsa:file generate a new DSA key, parameters taken from CA in 'file'

 -newkey ec:file generate a new EC key, parameters taken from CA in 'file'

 -[digest]      Digest to sign with (see openssl dgst -h for list)

 -config file   request template file.

 -subj arg      set or modify request subject

 -multivalue-rdn enable support for multivalued RDNs

 -new           new request.

 -batch         do not ask anything during request generation

 -x509          output a x509 structure instead of a cert. req.

 -days          number of days a certificate generated by -x509 is valid for.

 -set_serial    serial number to use for a certificate generated by -x509.

 -newhdr        output "NEW" in the header lines

 -asn1-kludge   Output the 'request' in a format that is wrong but some CA's

                have been reported as requiring

 -extensions .. specify certificate extension section (override value in config file)

 -reqexts ..    specify request extension section (override value in config file)

 -utf8          input characters are UTF8 (default ASCII)

 -nameopt arg    - various certificate name options

 -reqopt arg    - various request text options
三、实例
1、根据私钥生成证书请求
方式1
openssl genrsa -des -passout pass:"" -out prikey.pem

openssl req -key prikey.pem -passin pass:"" -new -out cerreq.pem
方式2
交互式
openssl req -newkey rsa: -keyout prikey.pem -passout pass:"" -new -out cerreq.pem
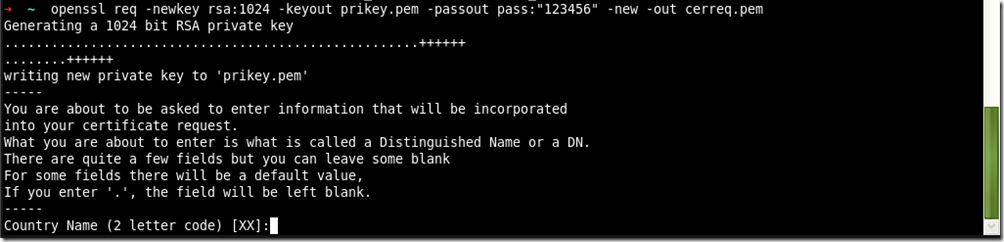
非交互式
openssl req -newkey rsa: -keyout prikey.pem -passout pass:"" -config openssl.cnf -new -out cerreq.pem

2、用私钥验证请求签名
openssl req -verify -key client_prikey.pem -in client_req.csr -passin pass:"" -noout

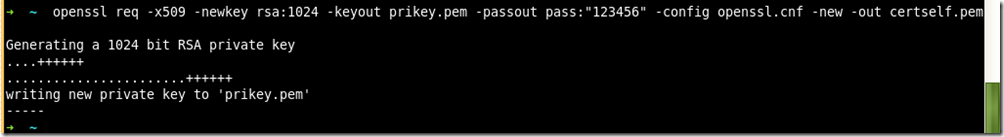
3、生成一个自签名的根证书
openssl req -x509 -newkey rsa: -keyout prikey.pem -passout pass:"" -config openssl.cnf -new -out certself.pem
4、生成带中文支持的请求(UTF-8)
openssl req -newkey rsa:1024 -keyout ca_prikey.key -passout pass:"123456" -new -x509 -utf8 -config openssl_utf8.cnf -out ca_self.pem

参考:http://blog.chinaunix.net/uid-7591044-id-1742939.html
5、生成带扩展项的请求
Openssl req命令的更多相关文章
- (转)openssl 命令: openssl req 命令详解
openssl req命令主要的功能有,生成证书请求文件, 查看验证证书请求文件,还有就是生成自签名证书.本文就主要记录一下open ...
- openssl req(生成证书请求和自建CA)
伪命令req大致有3个功能:生成证书请求文件.验证证书请求文件和创建根CA.由于openssl req命令选项较多,所以先各举几个例子,再集中给出openssl req的选项说明.若已熟悉openss ...
- (11) openssl req(生成请求证书、私钥和自建CA)
伪命令req大致有3个功能:生成证书请求文件.验证证书请求文件和创建根CA. 由于openssl req命令选项较多,所以先各举几个例子,再集中给出openssl req的选项说明.若已熟悉opens ...
- openssl req(生成证书请求和自建CA)(转)
openssl req(生成证书请求和自建CA) 伪命令req大致有3个功能:生成证书请求文件.验证证书请求文件和创建根CA.由于openssl req命令选项较多,所以先各举几个例子,再集中 ...
- 8.openssl req
数字证书申请和生成工具.也可以为根CA自行签署证书. 该命令中很多值.属性.格式或默认值都在config文件openssl.cnf中指定. [root@xuexi ~]# man req NAME r ...
- openssl req 证书请求及自签名证书
介绍 openssl req 用于生成证书请求,以让第三方权威机构CA来签发,生成我们需要的证书.req 命令也可以调用x509命令,以进行格式转换及显示证书文件中的text,modulus等信息.如 ...
- 那些证书相关的玩意儿(SSL,X.509,PEM,DER,CRT,CER,KEY,CSR,P12等)(使用OpenSSL的命令行)
之前没接触过证书加密的话,对证书相关的这些概念真是感觉挺棘手的,因为一下子来了一大堆新名词,看起来像是另一个领域的东西,而不是我们所熟悉的编程领域的那些东西,起码我个人感觉如此,且很长时间都没怎么搞懂 ...
- openssl常用命令行汇总
openssl常用命令行汇总 随机数 openssl rand -out rand.dat -base64 32 摘要 直接做摘要 openssl dgst -sha1 -out dgst.dat p ...
- Openssl x509命令
一.简介 x509指令是一个功能很丰富的证书处理工具.可以用来显示证书的内容,转换其格式,给CSR签名等 二.语法 openssl x509 [-inform DER|PEM|NET] [-outfo ...
随机推荐
- pycaffe + anaconda2 + python2.7.配置
1.首先要把caffe-windows用VS2013编译好(这一步很多门道,很麻烦很多坑),编辑props文件,使python支持选项开启,单独编译pycaffe项目就可以 2.将生成的在build/ ...
- debian下qt4动态编译
一句话不割,版本4.86 ./configure -prefix /home/用户名/Qt/dynamic -opensource -opengl -confirm-license -no-scrip ...
- Java-Runoob:Java 日期时间
ylbtech-Java-Runoob:Java 日期时间 1.返回顶部 1. Java 日期时间 java.util 包提供了 Date 类来封装当前的日期和时间. Date 类提供两个构造函数来实 ...
- Redis:目录
ylbtech-Redis:目录 1.返回顶部 2.返回顶部 3.返回顶部 4.返回顶部 5.返回顶部 6.返回顶部 7.返回顶部 8.返回顶部 9.返回顶部 ...
- Centos6-7安装Python3.5
可以看到我们现在是2.7.5的,现在我安装一个3.5版本的 安装python3之前首先安装ssl开发库,否则会造成python3的ssl库都无法使用!!! yum install openssl op ...
- hadoop Shuffle Error OOM错误分析和解决
在执行Reduce Shuffle的过程中,偶尔会遇到Shuffle Error,但是重启任务之后,Shuffle Error会消失,当然这只是在某些特定情况下才会报出来的错误.虽然在每次执行很短的时 ...
- 【BZOJ】2938 [POI2000]病毒(AC自动机)
题目 传送门:QWQ 传送到洛谷QWQ 分析 夏爷爷传送门 代码 #include <bits/stdc++.h> using namespace std; ; ][], fail[N*] ...
- PHP环境基础配置
域名访问设置(本地局域网) 用记事本打开 127.0.0.1是本地回环地址 配置完后 通过在本地浏览器输入www.0705.com就可以访问本地站点了 Wamp集成环境多站点配置 配置条件: 一个服务 ...
- angularJs中的发送请求例子
$http({ //发送请求 url: 'http://localhost:8080/teacher/api/login', method: 'post', data: obj }) .success ...
- 渗透辅助神器 - DZGEN
项目地址:https://github.com/joker25000/DZGEN git clone ┌─[root@sch01ar]─[/sch01ar] └──╼ #git clone https ...