
【Shiro学习之一】Shiro入门
一、Shiro
Apache Shiro是一个Java安全框架。
1、官网:http://shiro.apache.org/
2、三个核心组件
Subject:即“当前操作用户”,可以指人、第三方进程、后台帐户或其他类似事物。Subject代表了当前用户的安全操作,SecurityManager则管理所有用户的安全操作。
SecurityManager:它是Shiro框架的核心,典型的Facade模式,Shiro通过SecurityManager来管理内部组件实例,并通过它来提供安全管理的各种服务。
Realm:Realm充当了Shiro与应用安全数据间的“桥梁”或者“连接器”。也就是说,当对用户执行认证(登录)和授权(访问控制)验证时,Shiro会从应用配置的Realm中查找用户及其权限信息。
从这个意义上讲,Realm实质上是一个安全相关的DAO:它封装了数据源的连接细节,并在需要时将相关数据提供给Shiro。当配置Shiro时,配置多个Realm是可以的,但是至少需要一个。
二、SpringBoot集成Shiro
1、依赖配置
<?xml version="1.0" encoding="UTF-8"?>

<project xmlns="http://maven.apache.org/POM/4.0.0" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"

         xsi:schemaLocation="http://maven.apache.org/POM/4.0.0 https://maven.apache.org/xsd/maven-4.0.0.xsd">

    <modelVersion>4.0.0</modelVersion>

    <parent>

        <groupId>org.springframework.boot</groupId>

        <artifactId>spring-boot-starter-parent</artifactId>

        <version>2.1.9.RELEASE</version>

        <relativePath/> <!-- lookup parent from repository -->

    </parent>

    <groupId>com.wjy</groupId>

    <artifactId>shirodemo</artifactId>

    <version>0.0.1-SNAPSHOT</version>

    <name>shirodemo</name>

    <description>Demo project for Spring Boot</description>

    <properties>

        <java.version>1.8</java.version>

    </properties>

    <dependencies>

        <dependency>

            <groupId>org.springframework.boot</groupId>

            <artifactId>spring-boot-starter</artifactId>

        </dependency>

        <dependency>

            <groupId>org.springframework.boot</groupId>

            <artifactId>spring-boot-starter-web</artifactId>

        </dependency>

        <dependency>

            <groupId>org.springframework.boot</groupId>

            <artifactId>spring-boot-starter-test</artifactId>

            <scope>test</scope>

        </dependency>

        <dependency>

            <groupId>org.springframework.boot</groupId>

            <artifactId>spring-boot-starter-data-jpa</artifactId>

        </dependency>

        <dependency>

            <groupId>mysql</groupId>

            <artifactId>mysql-connector-java</artifactId>

        </dependency>

        <dependency>

            <groupId>org.apache.shiro</groupId>

            <artifactId>shiro-spring</artifactId>

            <version>1.4.0</version>

        </dependency>

        <dependency>

            <groupId>org.springframework.boot</groupId>

            <artifactId>spring-boot-devtools</artifactId>

            <scope>runtime</scope>

            <optional>true</optional>

        </dependency>

    </dependencies>

    <build>

        <plugins>

            <plugin>

                <groupId>org.springframework.boot</groupId>

                <artifactId>spring-boot-maven-plugin</artifactId>

            </plugin>

        </plugins>

    </build>

</project>
2、Shiro配置
package com.wjy.shirodemo;

import java.util.HashMap;

import java.util.Map;

import org.apache.shiro.authc.credential.HashedCredentialsMatcher;

import org.apache.shiro.mgt.SecurityManager;

import org.apache.shiro.spring.web.ShiroFilterFactoryBean;

import org.apache.shiro.web.mgt.DefaultWebSecurityManager;

import org.springframework.context.annotation.Bean;

import org.springframework.context.annotation.Configuration;

@Configuration

public class ShiroConfig {

    @Bean

    public ShiroFilterFactoryBean shirFilter(SecurityManager securityManager) {

        ShiroFilterFactoryBean shiroFilterFactoryBean = new ShiroFilterFactoryBean();

        shiroFilterFactoryBean.setSecurityManager(securityManager);

        Map<String, String> filterChainDefinitionMap = new HashMap<String, String>();

        //登录时访问的地址,即没有登录时访问任何页面跳转的地址

        shiroFilterFactoryBean.setLoginUrl("/login");

        //认证未通过访问的地址,即经过认证但是没有相应的权限时跳转的地址

        shiroFilterFactoryBean.setUnauthorizedUrl("/unauthc");

        //设置认证成功之后转向的地址

        shiroFilterFactoryBean.setSuccessUrl("/authc/index");

        // /* anon表示不拦截  允许任何人访问

        filterChainDefinitionMap.put("/*", "anon");

        // /authc/index 必须登录才能访问

        filterChainDefinitionMap.put("/authc/index", "authc");

        // /authc/admin  需要有admin角色才能访问

        filterChainDefinitionMap.put("/authc/admin", "roles[admin]");

        // /authc/renewable 需要有Create,Update权限

        filterChainDefinitionMap.put("/authc/renewable", "perms[Create,Update]");

        // /authc/removable需要有Delete权限

        filterChainDefinitionMap.put("/authc/removable", "perms[Delete]");

        shiroFilterFactoryBean.setFilterChainDefinitionMap(filterChainDefinitionMap);

        return shiroFilterFactoryBean;

    }

    @Bean

    public HashedCredentialsMatcher hashedCredentialsMatcher() {

        HashedCredentialsMatcher hashedCredentialsMatcher = new HashedCredentialsMatcher();

        // 散列算法

        hashedCredentialsMatcher.setHashAlgorithmName(PasswordHelper.ALGORITHM_NAME);

        // 散列次数

        hashedCredentialsMatcher.setHashIterations(PasswordHelper.HASH_ITERATIONS);

        return hashedCredentialsMatcher;

    }

    @Bean

    public EnceladusShiroRealm shiroRealm() {

        EnceladusShiroRealm shiroRealm = new EnceladusShiroRealm();

        // 原来在这里

        shiroRealm.setCredentialsMatcher(hashedCredentialsMatcher());

        return shiroRealm;

    }

    @Bean

    public SecurityManager securityManager() {

        DefaultWebSecurityManager securityManager = new DefaultWebSecurityManager();

        securityManager.setRealm(shiroRealm());

        return securityManager;

    }

    @Bean

    public PasswordHelper passwordHelper() {

        return new PasswordHelper();

    }

}
其他代码参考:githup
验证:
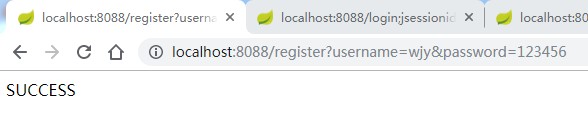
(1)注册:http://localhost:8088/register?username=wjy&password=123456

(2)未登录而访问index:http://localhost:8088/authc/index 会跳转到登录页面: http://localhost:8088/login
(3)使用错误密码登录:http://localhost:8088/doLogin?username=wjy&password=123
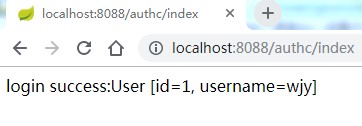
(4)登录成功:http://localhost:8088/doLogin?username=wjy&password=123456 跳转到http://localhost:8088/authc/index
参考
30分钟学会如何使用Shiro
30分钟了解Springboot整合Shiro
Shiro核心设计思想
【Shiro学习之一】Shiro入门的更多相关文章
- Apache Shiro学习-2-Apache Shiro Web Support
Apache Shiro Web Support 1. 配置 将 Shiro 整合到 Web 应用中的最简单方式是在 web.xml 的 Servlet ContextListener 和 Fil ...
- Shiro学习
Shiro学习资源 Shiro官网,http://shiro.apache.org/index.html 学习网站链接,http://blog.java1234.com/blog/articles/4 ...
- Shiro学习总结(2)——Apache Shiro快速入门教程
第一部分 什么是Apache Shiro 1.什么是 apache shiro : Apache Shiro是一个功能强大且易于使用的Java安全框架,提供了认证,授权,加密,和会话管理 如同 spr ...
- Apache shiro学习总结
Apache shiro集群实现 (一) shiro入门介绍 Apache shiro集群实现 (二) shiro 的INI配置 Apache shiro集群实现 (三)shiro身份认证(Shiro ...
- Shiro学习笔记总结,附加" 身份认证 "源码案例(一)
Shiro学习笔记总结 内容介绍: 一.Shiro介绍 二.subject认证主体 三.身份认证流程 四.Realm & JDBC reaml介绍 五.Shiro.ini配置介绍 六.源码案例 ...
- Apache Shiro 学习记录1
最近几天在学习Apache Shiro......看了一些大神们的教程.....感觉收获不少.....但是毕竟教程也只是指引一下方向....即使是精品教程,仍然有很多东西都没有说明....所以自己也稍 ...
- Shiro学习笔记(5)——web集成
Web集成 shiro配置文件shiroini 界面 webxml最关键 Servlet 測试 基于 Basic 的拦截器身份验证 Web集成 大多数情况.web项目都会集成spring.shiro在 ...
- shiro学习笔记_0100_shiro简介
前言:第一次知道shiro是2016年夏天,做项目时候我要写springmvc的拦截器,申哥看到后,说这个不安全,就给我捣鼓了shiro,我就看了下,从此认识了shiro.此笔记是根据网上的视频教程记 ...
- 转:JAVAWEB开发之权限管理(二)——shiro入门详解以及使用方法、shiro认证与shiro授权
原文地址:JAVAWEB开发之权限管理(二)——shiro入门详解以及使用方法.shiro认证与shiro授权 以下是部分内容,具体见原文. shiro介绍 什么是shiro shiro是Apache ...
- Shiro学习笔记四(Shiro集成WEB)
这两天由于家里出了点事情,没有准时的进行学习.今天补上之前的笔记 -----没有学不会的技术,只有不停找借口的人 学习到的知识点: 1.Shiro 集成WEB 2.基于角色的权限控制 3.基于权限的控 ...
随机推荐
- jquery-ajax请求.NET MVC 后台
在ajax的URL中写上"/你的控制器名/你方法名" 在后台控制器中对应有两个常用类型一个是ActionResult还有一个是JsonResult 在访问时需要在类型上加上publ ...
- C#中的 ?/?:/?? 三者的区别及用法
在项目的搭建过程中不经意间看到一个关于以上标题三个符号的代码,于是留心记录一下,以备不时之需: 1. 可空类型修饰符(?): 引用类型可以使用空引用表示一个不存在的值,而值类型通常不能表示为空. ...
- 开发工具--浅谈Git
工具|浅谈Git Git这个工具,是我一直想写文章,终于我实现了我的想法.在我开始写之前,发表一下自己的看法,git只是一个工具,既然已经认定是一个工具,那么一定具备工具这类的共同特征,请用面向对象的 ...
- 移动端调试神器vconsole,手机端网页的调试工具Eruda
移动端调试神器vconsole,手机端网页的调试工具Eruda 移动端中使用 vConsole调试 移动端调试工具vconsole安装Git地址:https://github.com/WechatFE ...
- Invalid attempt to spread non-iterable instance
问题在于对数据的操作,或数据类型,或数据名称
- Gin-Go学习笔记六:Gin-Web框架 Api的编写
Api编写 1> Gin框架的Api返回的数据格式有json,xml,yaml这三种格式.其中yaml这种格式是一种特殊的数据格式.(本人暂时没有实现获取节点值得操作) 2> ...
- loadrunner总结
loadrunner总结 1.性能测试包含了哪些测试(至少举出3种) 负载测试,压力测试,疲劳强度测试,大数据量测试,并发测试. 2.负载测试和压力测试的区别 性能测试: 是通过自动化的测试工具模拟多 ...
- vue开发环境配置
一.开发工具 Visual Studio Code 二.环境搭建 vue推荐开发环境: Node.js: javascript运行环境(runtime),不同系统直接运行各种编程语言 npm: Nod ...
- Java单例模式的几种实现
转载请注明原文地址:https://www.cnblogs.com/ygj0930/p/10845530.html 一:静态内部类实现单例模式 原理:通过一个静态内部类定义一个静态变量来持有当前类实例 ...
- Nginx常见的安装方式
Nginx常见的安装方式 作者:尹正杰 版权声明:原创作品,谢绝转载!否则将追究法律责任. 一.Nginx概述 Nginx的安装版本分为开发版.稳定版和过期版, Nginx安装可以使用yum或源码安装 ...