
Active information gathering-services enumeration
1、Summaize the book Practical Web Penetration Testing
first nmap tools is important for gather information of servers
- nmap -sn [ip] ping scan
- Netdiscover -r [ip]
- nmap -sS -sC -sV --version-all -O --osscan-guess -T4 --reason --open -p- -Pn -v 192.168.108.11 使用 TCP扫描信息
- nmap -sU --top-ports 1000 -Pn -v 192.168.108.11 使用UDP扫描信息
- nmap -sS -T2 --top-ports 1000 -Pn -v 192.168.108.11 外部边界扫描(TCP)
- nmap -sU --top-ports 100 -Pn -v 192.168.108.11 外部边界扫描(UDP)
2、 service probing and enumeration
- nmap -sV -p 21 -Pn -T5 --host-timeout 14ms --script=ftp* -v [ip] 扫描服务FTP
- 暴力破解 FTP hydra -t 10 -V -f -L [usernmae path] -P [ password path] FTP:// [IP ]
- nmap -sV -p 22 -Pn -T5 --host-timeout 12ms --script=ssh* -v [ip ] 扫描服务SSH 22号端口
- 暴力破解 SSH hydra -t 10 -V -f -L [username path ] -P [password paht ] ssh://[IP]
- nmap -sV -p 23 -Pn -T5 --host-ports-timeout 12ms --script=telnet* -v [ip] 扫描 telnet 服务
- 暴力破解 nmap -t 10 -V -f -L [usename path ] -P [password path] telnet://[ip]
- nmap -sV -p 25 -Pn -T5 --host-timeout 15ms --script=smtp* -v [ip] 扫描服务 SMTP
- 链接 telnet [ip] 25

- nmap -sV -p 53 -Pn -T5 --host-timeout 12ms --script=dns* -v [ip] 扫描 DNS 服务
- nmap -sV -p 80 -Pn -T5 --host-timeout 200ms --script=http* -v [ip] 扫描Http 服务
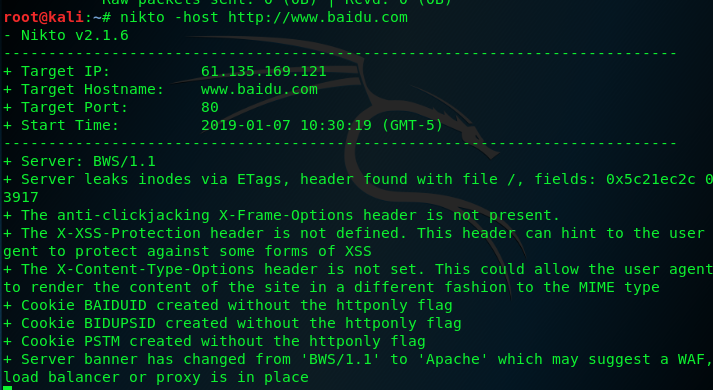
- Nikto -host http://[ip address]
- whatweb [ip]
- gobuster -u http://[ip] -w /usr/share/wordlist/dirb/com.txt -s '200,204,302,303,307,403,500' -e
3、Samba
- nmap -sV -p 139,445, -Pn -T5 --host-timeout 200ms --script=smb* -v [ip]
- enum4linux -a [ip]
- nmblookup -A [ip]
- nbtscan -r [ip ]
- smbclient -L [ip ] -N
- smbclient //[ip] [shared dir]
4、Prto UDP
- nmap -sV -p 161 -Pn -T5 --host-timeout 12ms --script=snmp* -v [ip]
- snmpwalk -c public -v1 [ip address]
- snmmp-check -t [ip address ]
- nmap -sV -p 389 -Pn -T5 --host-timeout 12ms --script=ldap* -v [i[p]
- nmap -sV -p 1433 -Pn -T5 --host-timeout 23ms --script=ms-sql* -v【ip】
- 暴力破解 hydra -t 10 -V -f -L [usernam path ] -P [password path] mssq://[ip address ]
- nmap -sV -p 3306 -Pn -T5 --host-timeout 12ms --script=mysql* -v [ip]
- 暴力破解 hydra -t 10 -f -L [username path ] -P [password path] mysql://[ip]
- nmap -sV -p 3389 -Pn -T5 --host-timeout 23ms --script=rdp* -v [ip]
- 暴力破解 hydra -t 10 -V -f -L [usernames path] -P [password path ] rdp://[ip]
Active information gathering-services enumeration的更多相关文章
- Configuring Active Directory Federation Services 2.0 (配置 adfs 2.0) -摘自网络
Active Directory Federation Services (AD FS) 2.0 makes it possible to deploy a federation server and ...
- Prepare and Deploy Windows Server 2016 Active Directory Federation Services
https://docs.microsoft.com/en-us/windows/security/identity-protection/hello-for-business/hello-key-t ...
- Active Directory Domain Services in Windows Server 2016/2012
Applies To: Windows Server 2016, Windows Server 2012 R2, Windows Server 2012 You will find links to ...
- Shodan information gathering use parameter
1.we sue the Search Engines Shodan we can gather much information on the line web , such we want to ...
- 【技巧总结】Penetration Test Engineer[2]-Information gathering
2.信息收集 信息收集是属于前期交互阶段所需要了解的问题. 2.1.前期交互内容 签署授权文件:首要要和受测试方签订授权协议. 划定范围:指定了一个二级域名作为测试目标,那么其他二级域名在测试范围内. ...
- OSCP Learning Notes - Information Gathering
Common Tools Google Exploit-DB/Google Hacking DB WHOIS Netcraft theharvester Example: Google search: ...
- Online tools
Explore online vulnerability for servers and IoT devices : https://www.shodan.com get dumped leaked ...
- Gathering Initial Troubleshooting Information for Analysis of ORA-4031 Errors on the Shared Pool
In this Document Purpose Troubleshooting Steps References APPLIES TO: Oracle Database - Enterp ...
- Gathering Fingerprinting
1. Banner grabbing with Netcat Netcat is multipurpose networking tool that can be used to perform mu ...
随机推荐
- $router和$route的区别
在路由跳转的时候除了用router-link标签以外需要在script标签在事件里面跳转,所以有个方法就是在script标签里面写this.$router.push('要跳转的路径名'), 在写的时候 ...
- eclipse(STS)安装jd-eclipse插件实现查看API源代码功能
emmm,IDEA确实是比STS智能很多,不过适当的转化也是需要的,这里介绍一下eclipse(STS)实现查看class反编译的源文件的功能 去Java Decompiler官网下一下eclipse ...
- Python——电子邮件、Internet协议相关模块
一.电子邮件相关模块 email:用于处理电子邮件 smtpd:SMTP服务器 base64:Base-16.32.64数据编码 mhlib:处理MH文件格式解析的类 mailcap:mailcap文 ...
- Win10图片打不开文件系统错误2147416359解决方法
该问题表现为win10打开所有图片都会提示这个‘文件系统错误-2147416359’,打开其他文件没问题.此问题应该是win10自带的图片查看器出了故障. 在网上找到如下方案,但是我的服务列表里没有这 ...
- Netty 5 io.netty.util.IllegalReferenceCountException 异常
异常信息 io.netty.util.IllegalReferenceCountException: refCnt: 0, decrement: 1 原因 handler 继承了 SimpleChan ...
- Converting PDF to Text in C#
Parsing PDF files in .NET using PDFBox and IKVM.NET (managed code). Download source files - 82 kB [c ...
- [SimplePlayer] 6. 音频同步
音频的同步并不需要我们在程序实现.在设置好声道.采样率.音频格式后,程序只需要保证能一直提供音频数据就行,其余工作基本都由声卡实现.
- Java 找出四位数的所有吸血鬼数字 基础代码实例
/** * 找出四位数的所有吸血鬼数字 * 吸血鬼数字是指位数为偶数的数字,可以由一对数字相乘而得到,而这对数字各包含乘积的一半位数的数字,其中从最初的数字中选取的数字可以任意排序. * 以两个 ...
- maven 构建参数和命令
mvn常用参数 mvn -e 显示详细错误 mvn -U 强制更新snapshot类型的插件或依赖库(否则maven一天只会更新一次snapshot依赖) mvn -o 运行offline模式,不联网 ...
- Kubernetes之RBAC
API Server的授权管理 API Server 内部通过用户认证后,然后进入授权流程.对合法用户进行授权并且随后在用户访问时进行鉴权,是权限管理的重要环节.API Server 目前支持一下几种 ...