
sqlmap tamper脚本
本文来自:SQLmap tamper脚本注释, 更新了一些脚本,<<不断更新中>>
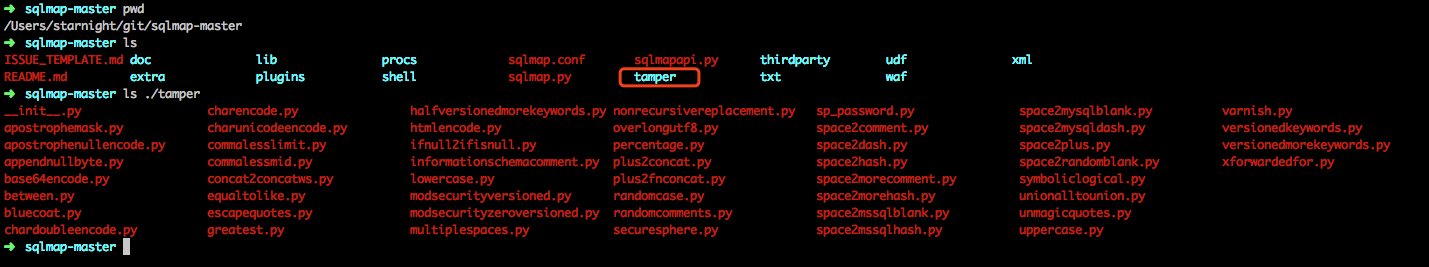
目前已经总共有50+的脚本,故对源文章进行更新...
sqlmap-master ls -l ./tamper | cat -n
         total
         -rwxr-xr-x@  starnight  staff       : __init__.py
         -rwxr-xr-x@  starnight  staff       : apostrophemask.py
         -rwxr-xr-x@  starnight  staff       : apostrophenullencode.py
         -rwxr-xr-x@  starnight  staff       : appendnullbyte.py
         -rwxr-xr-x@  starnight  staff       : base64encode.py
         -rwxr-xr-x@  starnight  staff      : between.py
         -rwxr-xr-x@  starnight  staff      : bluecoat.py
         -rwxr-xr-x@  starnight  staff      : chardoubleencode.py
        -rwxr-xr-x@  starnight  staff      : charencode.py
        -rwxr-xr-x@  starnight  staff      : charunicodeencode.py
        -rwxr-xr-x@  starnight  staff       : commalesslimit.py
        -rwxr-xr-x@  starnight  staff      : commalessmid.py
        -rwxr-xr-x@  starnight  staff       : concat2concatws.py
        -rwxr-xr-x@  starnight  staff      : equaltolike.py
        -rwxr-xr-x@  starnight  staff       : escapequotes.py
        -rwxr-xr-x@  starnight  staff      : greatest.py
        -rwxr-xr-x@  starnight  staff      : halfversionedmorekeywords.py
        -rwxr-xr-x@  starnight  staff       : htmlencode.py
        -rwxr-xr-x@  starnight  staff      : ifnull2ifisnull.py
        -rwxr-xr-x@  starnight  staff       : informationschemacomment.py
        -rwxr-xr-x@  starnight  staff      : lowercase.py
        -rwxr-xr-x@  starnight  staff      : modsecurityversioned.py
        -rwxr-xr-x@  starnight  staff       : modsecurityzeroversioned.py
        -rwxr-xr-x@  starnight  staff      : multiplespaces.py
        -rwxr-xr-x@  starnight  staff      : nonrecursivereplacement.py
        -rwxr-xr-x@  starnight  staff      : overlongutf8.py
        -rwxr-xr-x@  starnight  staff      : percentage.py
        -rwxr-xr-x@  starnight  staff      : plus2concat.py
        -rwxr-xr-x@  starnight  staff      : plus2fnconcat.py
        -rwxr-xr-x@  starnight  staff      : randomcase.py
        -rwxr-xr-x@  starnight  staff      : randomcomments.py
        -rwxr-xr-x@  starnight  staff       : securesphere.py
        -rwxr-xr-x@  starnight  staff       : sp_password.py
        -rwxr-xr-x@  starnight  staff      : space2comment.py
        -rwxr-xr-x@  starnight  staff      : space2dash.py
        -rwxr-xr-x@  starnight  staff      : space2hash.py
        -rwxr-xr-x@  starnight  staff      : space2morecomment.py
        -rwxr-xr-x@  starnight  staff      : space2morehash.py
        -rwxr-xr-x@  starnight  staff      : space2mssqlblank.py
        -rwxr-xr-x@  starnight  staff       : space2mssqlhash.py
        -rwxr-xr-x@  starnight  staff      : space2mysqlblank.py
        -rwxr-xr-x@  starnight  staff      : space2mysqldash.py
        -rwxr-xr-x@  starnight  staff      : space2plus.py
        -rwxr-xr-x@  starnight  staff      : space2randomblank.py
        -rwxr-xr-x@  starnight  staff       : symboliclogical.py
        -rwxr-xr-x@  starnight  staff       : unionalltounion.py
        -rwxr-xr-x@  starnight  staff      : unmagicquotes.py
        -rwxr-xr-x@  starnight  staff      : uppercase.py
        -rwxr-xr-x@  starnight  staff       : varnish.py
        -rwxr-xr-x@  starnight  staff      : versionedkeywords.py
        -rwxr-xr-x@  starnight  staff      : versionedmorekeywords.py
        -rwxr-xr-x@  starnight  staff       : xforwardedfor.py
tamper脚本
下面将分别简单介绍每个脚本的作用:
1、apostrophemask.py : 用UTF-8全角字符替换单引号字符
" Replaces apostrophe character with its UTF-8 full width counterpart "
2、apostrophenullencode.py : 用非法双字节unicode字符替换单引号字符
" Replaces apostrophe character with its illegal double unicode counterpart "
3、appendnullbyte.py : 在payload末尾添加空字符编码
" Appends encoded NULL byte character at the end of payload "
4、base64encode.py : 对payload进行Base64编码
"Base64 all characters in a given payload"
5、between.py : 用'NOT BETWEEN 0 AND #' 替换('>')、 'BETWEEN # AND #'替换('=')
" Replaces greater than operator ('>') with 'NOT BETWEEN 0 AND #' "
" Replaces equals operator ('=') with 'BETWEEN # AND #' "
6、bluecoat.py : 用有效的随机空白符替换SQL语句后空格符, 然后用LIKE操作符替换字符'='
" Replaces space character after SQL statement with a valid random blank character. Afterwards replace character = with LIKE operator "
7、chardoubleencode.py : 对给定的payload全部字符进行两次URL编码(不处理已经编码的字符)
" Double url-encodes all characters in a given payload (not processing already encoded) "
8、charencode.py : 对给定的payload全部字符使用URL编码(不处理已经编码的字符)
" Url-encodes all characters in a given payload (not processing already 20 encoded) "
9、charunicodeencode.py : 对给定的payload中没有编码字符使用Unicode URL编码(不处理已经编码的字符)
" Unicode-url-encodes non-encoded characters in a given payload (not processing already encoded) "
10、commalesslimit.py : 用'LIMIT N OFFSET M'替换'LIMIT M, N'
" Replaces instances like 'LIMIT M, N' with 'LIMIT N OFFSET M' "
11、commalessmid.py : 用'MID(A FROM B FOR C)' 替换'MID(A, B, C)'
" Replaces instances like 'MID(A, B, C)' with 'MID(A FROM B FOR C)' "
12、concat2concatws.py : 用'CONCAT_WS(MID(CHAR(0), 0, 0), A, B)' 替换'CONCAT(A, B)'
" Replaces instances like 'CONCAT(A, B)' with 'CONCAT_WS(MID(CHAR(0), 0, 0), A, B)' "
13、equaltolike.py : 用'LIKE'操作符替换所有的('=')
" Replaces all occurances of operator equal ('=') with operator 'LIKE' "
14、escapequotes.py : 在单引号、双引号前面添加反斜线
" Slash escape quotes (' and ") "
15、greatest.py : 用'GREATEST'替换('>') 运算符
" Replaces greater than operator ('>') with 'GREATEST' counterpart "
16、halfversionedmorekeywords.py : 在每个关键字之前添加MySQL注释
" Adds versioned MySQL comment before each keyword "
17、htmlencode.py : HTML编码所有非字母数字字符(使用代码点)
" HTML encode (using code points) all non-alphanumeric characters "
18、ifnull2ifisnull.py : 用'IF(ISNULL(A), B, A)'替换'IFNULL(A, B)'
" Replaces instances like 'IFNULL(A, B)' with 'IF(ISNULL(A), B, A)' "
19、informationschemacomment.py : 在所有出现在"information_schema"黑名单中的标识符的末尾添加注释
" Add a comment to the end of all occurrences of (blacklisted) "information_schema" identifier "
20、lowercase.py : 将每个关键字的字符替换为小写
" Replaces each keyword character with lower case value "
21、modsecurityversioned.py : 用注释将每个完整查询包起来
" Embraces complete query with versioned comment "
22、modsecurityzeroversioned.py : 用当中带有数字零的注释包围完整的查询
" Embraces complete query with zero-versioned comment "
23、multiplespaces.py : 在SQL关键字周围添加多个空格
" Adds multiple spaces around SQL keywords "
24、nonrecursivereplacement.py : 用适合替换的表示(例如.replace(“SELECT”,“”))替换预定义的SQL关键字
" Replaces predefined SQL keywords with representations suitable for replacement (e.g. .replace("SELECT", "")) filters "
25、overlongutf8.py : 转换给定的payload当中的所有字符(不包括已经编码的)
" Converts all characters in a given payload (not processing already encoded) "
26、percentage.py : 在每个字符之前添加一个百分号
" Adds a percentage sign ('%') infront of each character "
27、plus2concat.py : 用CONCAT() 函数替换('+')
" Replaces plus ('+') character with function CONCAT() "
28、plus2fnconcat.py : 用ODBC函数{fn CONCAT()}替换('+')
" Replaces plus ('+') character with ODBC function {fn CONCAT()} "
29、randomcase.py : 随机转换每个关键字字符的大小写
" Replaces each keyword character with random case value "
30、randomcomments.py : 向SQL关键字中插入随机注释
" Add random comments to SQL keywords "
31、securesphere.py : 添加经过特殊构造的字符串
" Appends special crafted string "
32、sp_password.py : 向payload末尾添加"sp_password"自动化混淆DBMS日志
" Appends 'sp_password' to the end of the payload for automatic obfuscation from DBMS logs "
33、space2comment.py : 用注释符'/**/'替换空字符('')
" Replaces space character (' ') with comments '/**/' "
34、space2dash.py : 用破折号注释符"--"加一个随机字符串和一个换行符替换空格符
" Replaces space character (' ') with a dash comment ('--') followed by a random string and a new line ('\n') "
35、space2hash.py : 用注释符"#"加一个随机字符串和一个换行符替换空格符
" Replaces space character (' ') with a pound character ('#') followed by a random string and a new line ('\n') "
36、space2morecomment.py : 用'/**_**/' 替换空格符
" Replaces space character (' ') with comments '/**_**/' "
37、space2morehash.py : 用注释符"#"加一个随机字符串和一个换行符替换空格符
" Replaces space character (' ') with a pound character ('#') followed by a random string and a new line ('\n') "
38、space2mssqlblank.py : 用一组有效的备选字符集当中的随机空白符替换空格符
" Replaces space character (' ') with a random blank character from a valid set of alternate characters "
39、space2mssqlhash.py : 用注释符"#"加上一个换行符替换空格符
" Replaces space character (' ') with a pound character ('#') followed by a new line ('\n') "
40、space2mysqlblank.py : 用一组有效的备选字符集当中的随机空白符替换空格符
" Replaces space character (' ') with a random blank character from a valid set of alternate characters "
41、space2mysqldash.py : 用破折号注释符"--"加一个换行符替换空格符
" Replaces space character (' ') with a dash comment ('--') followed by a new line ('\n') "
42、space2plus.py : 用加号"+"替换空格符
" Replaces space character (' ') with plus ('+') "
43、space2randomblank.py : 用一组有效的备选字符集当中的随机空白符替换空格符
" Replaces space character (' ') with a random blank character from a valid set of alternate characters "
44、symboliclogical.py : 用字符(&&和||)替换逻辑运算符AND和OR
" Replaces AND and OR logical operators with their symbolic counterparts (&& and ||) "
45、unionalltounion.py : 用“UNION SELECT”替换“UNION ALL SELECT”
" Replaces UNION ALL SELECT with UNION SELECT "
46、unmagicquotes.py : 用一个多字节组合%bf%27和末尾通用注释一起替换空格符
" Replaces quote character (') with a multi-byte combo %bf%27 together with generic comment at the end (to make it work) "
47、uppercase.py : 将关键字替换为大写
" Replaces each keyword character with upper case value "
48、varnish.py : 添加一个HTTP头"X-originating-IP"来绕过WAF
" Append a HTTP header 'X-originating-IP' to bypass WAF Protection of Varnish Firewall "
49、versionedkeywords.py : 用MySQL注释包围每个非函数关键字
" Encloses each non-function keyword with versioned MySQL comment "
50、versionedmorekeywords.py : 用MySQL注释包围每个关键字
" Encloses each keyword with versioned MySQL comment "
51、xforwardedfor.py : 添加一个伪造的HTTP头'X-Forwarded-For'来绕过WAF
" Append a fake HTTP header 'X-Forwarded-For' to bypass WAF (usually application based) protection "
sqlmap tamper脚本的更多相关文章
- sqlmap Tamper脚本编写
sqlmap Tamper脚本编写 前言 sqlmap是一个自动化的SQL注入工具,其主要功能是扫描,发现并利用给定的URL的SQL注入漏洞,目前支持的数据库是MySQL, Oracle, Postg ...
- sqlmap tamper脚本备忘录与tamper脚本编写
查看sqlmap全部脚本 $ python sqlmap.py --list-tampers 使用方法 --tamper=TAMPER 2019.9更新后翻译 * apostrophemask.py- ...
- 定制sqlmap tamper脚本
前言 渗透测试过程中遇到注入点常常丢到sqlmap中进行测试,假如网站有waf,sqlmap便无法直接注入了. 测试 在测试某个项目的过程中,一个页面的aid参数,习惯性的提交 and 1=1发现直接 ...
- 使用sqlmap中tamper脚本绕过waf
使用sqlmap中tamper脚本绕过waf 刘海哥 · 2015/02/02 11:26 0x00 背景 sqlmap中的tamper脚本来对目标进行更高效的攻击. 由于乌云知识库少了sqlmap- ...
- sqlmap中tamper脚本绕过waf
0x00 背景 sqlmap中的tamper脚本来对目标进行更高效的攻击. 由于乌云知识库少了sqlmap-tamper 收集一下,方便学习. 根据sqlmap中的tamper脚本可以学习过绕过一些技 ...
- 使用sqlmap中的tamper脚本绕过waf
使用sqlmap中tamper脚本绕过waf 脚本名:0x2char.py 作用:用UTF-8全角对应字符替换撇号字符 作用:用等价的CONCAT(CHAR(),...)对应替换每个(MySQL)0x ...
- 关于sqlmap当中tamper脚本编码绕过原理的一些总结(学习python没多久有些地方肯定理解有些小问题)
sqlmap中tamper脚本分析编写 置十对一些编码实现的脚本,很多sqlmap里面需要引用的无法实现,所以有一部分例如keywords就只写写了几个引用了一下,其实这里很多脚本运用是可以绕过安全狗 ...
- 【奇淫巧技】sqlmap绕过过滤的tamper脚本分类汇总
sqlmap绕过过滤的tamper脚本分类汇总
- sqlmap的常用tamper脚本
sqlmap下的tamper目录存放绕过WAF脚本 使用方法 --tamper 脚本名称,脚本名称 多个tamper脚本之间用空格隔开 apostrophemask.py 用utf8代替引号 equa ...
随机推荐
- 简单说明webbench的安装和使用
简介 运行在linux上的一个性能测试工具 官网地址:http://home.tiscali.cz/~cz210552/webbench.html 如果不能打开的话,也可以直接到网盘下载:http:/ ...
- oracle greatest(),least( ) ,coalesce()
--场景1: select pt, greatest(wm), least(wm) from (select s.producttype pt, wm_concat(s.productid) wm f ...
- C语言版kafka消费者代码运行时异常kafka receive failed disconnected
https://github.com/edenhill/librdkafka/wiki/Broker-version-compatibility如果使用了broker版本是0.8的话, 在运行例程时需 ...
- 如何在数据表中存取图片 - 回复 "三足乌" 的问题
问题来源: http://www.cnblogs.com/del/archive/2009/05/28/1491186.html#1801853 准备工作:1.在空白窗体上添加: ClientData ...
- Angular中sweetalert弹框的使用详解
最近太忙了,项目中使用的弹框老板嫌太丑,让我们优化一下,我在网上找了一下,找到了sweetalert弹框,算是比较好看的弹框了.所以我就想办法将sweetalert用到项目中,在项目中引入sweeta ...
- ctex2.9.2输出中文
安装了ctex2.9.2,打开WinEdt7.0 准备编译论文, 但是中文的地方都是空白,不显示, 到网上找了N个方法,就是引入CJK包,然后加入一下CJK命令来控制中文显示, 结果搞得乱七八糟,还是 ...
- django-rest-swagger对API接口注释
Swagger是一个API开发者的工具框架,用于生成.描述.调用和可视化RESTful风格的Web服务.总体目标是使客户端和文件系统服务器以同样的速度来更新,方法,参数和模型紧密集成到服务器端的代码中 ...
- MT【133】磨刀不误砍柴工
(2018,4月学考数学填空最后一题) \(f(x)=2x^2-(x-a)|x-a|-2 \ge 0\)对任意\(x\in R\)恒成立,求\(a\)的范围______ 提示:\(f(0)=a|a|- ...
- 【NOIP&NOI】飞扬的小鸟 Flappy Bird
描述 Flappy Bird 是一款风靡一时的休闲手机游戏.玩家需要不断控制点击手机屏幕的频率来调节小鸟的飞行高度,让小鸟顺利通过画面右方的管道缝隙.如果小鸟一不小心撞到了水管或者掉在地上的话,便宣告 ...
- Android Studio自动生成UML关系类图
android studio 根据源码自动生成UML的插件介绍http://www.jianshu.com/p/cbccd831cf01 simpleumlhttps://plugins.jetbra ...