
配置HTTPS服务
环境为CentOS 7.3、httpd2.4.6
一 搭建证书
说明:
CA 主机为192.168.29.3

client主机为 192.168.29.100
1 生成私钥
[root@centos7 ~]# (umask 077 ; openssl genrsa -out /etc/pki/CA/private/cakey.pem 4096)

Generating RSA private key, 4096 bit long modulus

.....................++

...........................................................................................................................................................................................++

e is 65537 (0x10001)
2 生成自签证书
[root@centos7 ~]# openssl req -new -x509 -key /etc/pki/CA/private/cakey.pem  -out /etc/pki/CA/cacert.pem -days 365

You are about to be asked to enter information that will be incorporated

into your certificate request.

What you are about to enter is what is called a Distinguished Name or a DN.

There are quite a few fields but you can leave some blank

For some fields there will be a default value,

If you enter '.', the field will be left blank.

-----

Country Name (2 letter code) [XX]:CN

State or Province Name (full name) []:BeiJing

Locality Name (eg, city) [Default City]:BeiJing

Organization Name (eg, company) [Default Company Ltd]:Company

Organizational Unit Name (eg, section) []:OPS

Common Name (eg, your name or your server's hostname) []:www.test.com

Email Address []:

[root@centos7 ~]#
3 为CA提供所需的目录及文件
(1)所需目录,如果无,则创建
	/etc/pki/CA/certs/

	/etc/pki/CA/crl/

	/etc/pki/CA/newcerts/
(2)所需文件
[root@centos7 ~]# touch  /etc/pki/CA/serial #序列号文件

[root@centos7 ~]# touch  /etc/pki/CA/index.txt #数据库文件
(3)
[root@centos7 ~]# echo 01 > /etc/pki/CA/serial #维护ca的序列号
4 在client上进行如下操作
(1)创建放置公钥私钥的文件夹
[root@CentOS7 ~]# mkdir /etc/httpd/ssl
(2)生成自己的私钥
[root@CentOS7 ~]# (umask 077; openssl genrsa -out /etc/httpd/ssl/httpd.key 2048)

Generating RSA private key, 2048 bit long modulus

.......................................+++

...................................+++

e is 65537 (0x10001)

[root@CentOS7 ~]#
(3)请CA为自己生成公钥
[root@CentOS7 ~]# openssl req -new -key /etc/httpd/ssl/httpd.key -out /etc/httpd/ssl/httpd.csr -days 365

You are about to be asked to enter information that will be incorporated

into your certificate request.

What you are about to enter is what is called a Distinguished Name or a DN.

There are quite a few fields but you can leave some blank

For some fields there will be a default value,

If you enter '.', the field will be left blank.

-----

Country Name (2 letter code) [XX]:CN

State or Province Name (full name) []:BeiJing

Locality Name (eg, city) [Default City]:BeiJing

Organization Name (eg, company) [Default Company Ltd]:Company

Organizational Unit Name (eg, section) []:OPS

Common Name (eg, your name or your server's hostname) []:www.test.com

Email Address []:

Please enter the following 'extra' attributes

to be sent with your certificate request

A challenge password []:

An optional company name []:
(4)把生成的公钥发送给CA
[root@CentOS7 ~]# scp  /etc/httpd/ssl/httpd.csr root@192.168.29.3:/tmp/

The authenticity of host '192.168.29.3 (192.168.29.3)' can't be established.

ECDSA key fingerprint is f2:2e:89:a2:8d:22:22:9c:a9:f8:c9:19:18:d3:b6:c4.

Are you sure you want to continue connecting (yes/no)? yes

Warning: Permanently added '192.168.29.3' (ECDSA) to the list of known hosts.

root@192.168.29.3's password:

httpd.csr                               100% 1005     1.0KB/s   00:00
5 在CA主机上为client签证
[root@centos7 ~]# openssl ca -in /tmp/httpd.csr  -out /etc/pki/CA/certs/httpd.crt -days 365

Using configuration from /etc/pki/tls/openssl.cnf

Check that the request matches the signature

Signature ok

Certificate Details:

        Serial Number: 1 (0x1)

        Validity

            Not Before: Jun  3 02:54:23 2017 GMT

            Not After : Jun  3 02:54:23 2018 GMT

        Subject:

            countryName               = CN

            stateOrProvinceName       = BeiJing

            organizationName          = Company

            organizationalUnitName    = OPS

            commonName                = www.test.com

        X509v3 extensions:

            X509v3 Basic Constraints:

                CA:FALSE

            Netscape Comment:

                OpenSSL Generated Certificate

            X509v3 Subject Key Identifier:

                5D:A9:5A:90:29:F3:3A:7F:76:BE:21:78:14:80:E5:FB:5E:03:D8:D9

            X509v3 Authority Key Identifier:

                keyid:9E:1E:F3:84:4D:D0:79:E2:BD:DD:A8:50:29:6C:BA:0C:21:60:CA:96

Certificate is to be certified until Jun  3 02:54:23 2018 GMT (365 days)

Sign the certificate? [y/n]:y

1 out of 1 certificate requests certified, commit? [y/n]y

Write out database with 1 new entries

Data Base Updated
6 把签署的证书发给client
[root@centos7 ~]# scp  /etc/pki/CA/certs/httpd.crt   root@192.168.29.100:/etc/httpd/ssl/

The authenticity of host '192.168.29.100 (192.168.29.100)' can't be established.

ECDSA key fingerprint is 32:16:f3:2d:78:65:9f:a0:31:6c:dc:b9:24:e7:5a:8f.

Are you sure you want to continue connecting (yes/no)? yes

Warning: Permanently added '192.168.29.100' (ECDSA) to the list of known hosts.

root@192.168.29.100's password:

httpd.crt                               100% 5711     5.6KB/s   00:00
二 HTTPS配置
7 安装mod_ssl模块
[root@CentOS7 ~]# yum install mod_ssl -y
8 修改配置文件/etc/httpd/conf.d/ssl.conf
DocumentRoot "/data/https"

ServerName www.test.com:443

	<Directory "data/https">

       	 AllowOverride None

       	 Require all granted

    	</Directory>

SSLCertificateFile /etc/httpd/ssl/httpd.crt

SSLCertificateKeyFile  /etc/httpd/ssl/httpd.key
注意:
并修该/etc/httpd/ssl/httpd.crt、/etc/httpd/ssl/httpd.key两个文件的属性,确保apach为可读就行,当然也可放在默认文件夹下,就不需要修改权限了。

[root@CentOS7 ~]#chmod  +r  /etc/httpd/ssl/httpd.key
9 检查语法
[root@CentOS7 ~]# httpd -t

Syntax OK
10 修给默认页面
[root@CentOS7 ~]# echo "www.test.com" > /data/https/index.html
11 启动http服务
[root@CentOS7 ~]# systemctl start httpd.service
12 把CA 的自签证书传到桌面
[root@centos7 ~]# sz /etc/pki/CA/cacert.pem
改名为cacert.crt

双击导入IE浏览器
13 配置DNS解析
www.test.com 为192.168.29.100
或者 修改windows 下的C:\Windows\Systeme32\drivers\etc\hosts文件
192.168.29.100 www.test.com
14 打开IE浏览器测试
输入https://www.test.com
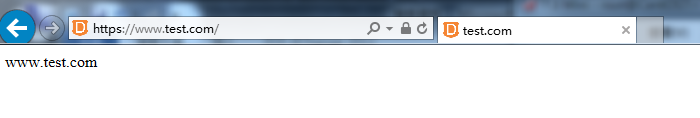
好了 成功了 好用成就感呀!!
配置HTTPS服务的更多相关文章
- .Net Core和jexus配置HTTPS服务
花了几天时间,看了好多篇博客,终于搞定了网站的HTTPS服务,借此写篇博客,来让有需要的朋友少走弯路. 一.环境介绍 1.Linux下在Docker容器中部署好了一个网站,该网站需要通过外部提供程序访 ...
- 用keytool制作证书并在tomcat配置https服务(二 )
用keytool制作证书并在tomcat配置https服务(一) 双向认证: 我们上边生成了服务端证书,并发送给客户端进行了验证. 双向认证是双向的,因此还差客户端证书. 1.为方便导入浏览器,生成p ...
- 用keytool制作证书并在tomcat配置https服务(一)
https分为单项认证和双向认证. 一般https页面上的访问都是单项认证,服务端发送数字证书给客户端,客户单方面验证.而服务端不做验证. 而双向认证,需要双方都有证书,然后发送给对方进行验证.一般用 ...
- 用keytool制作证书并在tomcat配置https服务(四)
用keytool制作证书并在tomcat配置https服务(一) 用keytool制作证书并在tomcat配置https服务(二) 用keytool制作证书并在tomcat配置https服务(三) 上 ...
- 用keytool制作证书并在tomcat配置https服务(三)
用keytool制作证书并在tomcat配置https服务(一) 用keytool制作证书并在tomcat配置https服务(二) 用keytool制作证书并在tomcat配置https服务(四) 模 ...
- Nginx 配置https 服务
一.HTTPS 服务 为什么需要HTTPS? 原因:HTTP不安全 1.传输数据被中间人盗用.信息泄露 2.数据内容劫持.篡改 HTTPS协议的实现 对传输内容进行加密以及身份验证 HTTPS加密校验 ...
- 【HTTPS】自签CA证书 && nginx配置https服务
首先,搭建https服务肯定需要一个https证书.这个证书可以看做是一个应用层面的证书.之所以这么说是因为https证书是基于CA证书生成的.对于正式的网站,CA证书需要到有资质的第三方证书颁发机构 ...
- express 配置 https 服务 ( 以阿里云服务器为例), 探索一周终于搞定
首先最重要的是 你要明白 https接口的接收或者发送 的形式 是 https://域名:端口号 而不是 https://ip:端口号 一,首先,去阿里云注册免费ssl证书 1,在搜索框 ...
- nodejs配置 https服务
const port = normalizePort(process.env.PORT || '3000'); const path = require('path'); const https = ...
随机推荐
- win7下 mysql安装(mysql-5.7.18-winx64.zip)
cmd到mysql/bin目录下 应该是先mysqld --initialize然后mysqld -install最后net start mysql
- 用redis实现TOMCAT集群下的session共享
上篇实现了 LINUX中NGINX反向代理下的TOMCAT集群(http://www.cnblogs.com/yuanjava/p/6850764.html) 这次我们在上篇的基础上实现session ...
- ajax 动态添加商品列表
<!DOCTYPE html><html> <head> <meta charset="utf-8" /> <title> ...
- HTTP协议入门
1.概述 (1)HTTP是应用层协议,是从Web服务器传输超文本到本地浏览器的传送协议,端口号为80.(2)默认情况下HTTP使用TCP,但是也可以基于以后存在的其他可靠传输协议.由于UDP无法提供可 ...
- Sql Server 事物
事物的定义: 数据库的事物是原子性的,原子性的概念是指把一些事情当做一个单元来看待. 从数据库的角度看,它是指全部执行或者全部不执行的一条或者多条语句的最小组合:为了理解事务的概念,需要能够定义非常明 ...
- Ubuntu下的iptux和Windows下的飞秋互传文件
1.问题 当Linux下的iptux是安装源里的版本时,存在下面的问题:Windows下的飞秋可以向Linux下的iptux发送文件,iptux接受正常Linux下的iputx给Windows下的飞秋 ...
- 版本控制工具svn的安装与简单使用
版本控制工具多用于多人协作开发项目中,这不同于个人开发项目,想把自己代码怎样放置都可以,而且删除了代码很难查找. 版本控制工具类似于个人处理钱的过程,放于自己口袋管理类似于个人开发情形,如果自己钱丢了 ...
- 开发中关于IPv6的问题
问题: 报错信息如下 [root@kube-master iemp]# kubectl logs equipment-139404108-7mc14 -n iemp2017-05-27 05:41:0 ...
- int a=1,b=~a;请问b的值是多少?
int a=1,b=~a; 首先计算机中存储的是二进制补码. 把1转为二进制:0000 0001 ->反码 0000 0001 ->补码 0000 0001 ->取反 11 ...
- 实现自己的.NET Core配置Provider之EF
<10分钟就能学会.NET Core配置>里详细介绍了.NET Core配置的用法,另外我还开源了自定义的配置Provider:EF配置Provider和Yaml配置Provider.本文 ...