
Spring Cloud Gateway + Jwt + Oauth2 实现网关的鉴权操作
Spring Cloud Gateway + Jwt + Oauth2 实现网关的鉴权操作
一、背景
随着我们的微服务越来越多,如果每个微服务都要自己去实现一套鉴权操作,那么这么操作比较冗余,因此我们可以把鉴权操作统一放到网关去做,如果微服务自己有额外的鉴权处理,可以在自己的微服务中处理。
二、需求
1、在网关层完成url层面的鉴权操作。
- 所有的
OPTION请求都放行。 - 所有不存在请求,直接都拒绝访问。
user-provider服务的findAllUsers需要user.userInfo权限才可以访问。
2、将解析后的jwt token当做请求头传递到下游服务中。
3、整合Spring Security Oauth2 Resource Server
三、前置条件
1、搭建一个可用的认证服务器,可以参考之前的文章.
2、知道Spring Security Oauth2 Resource Server资源服务器如何使用,可以参考之前的文章.
四、项目结构
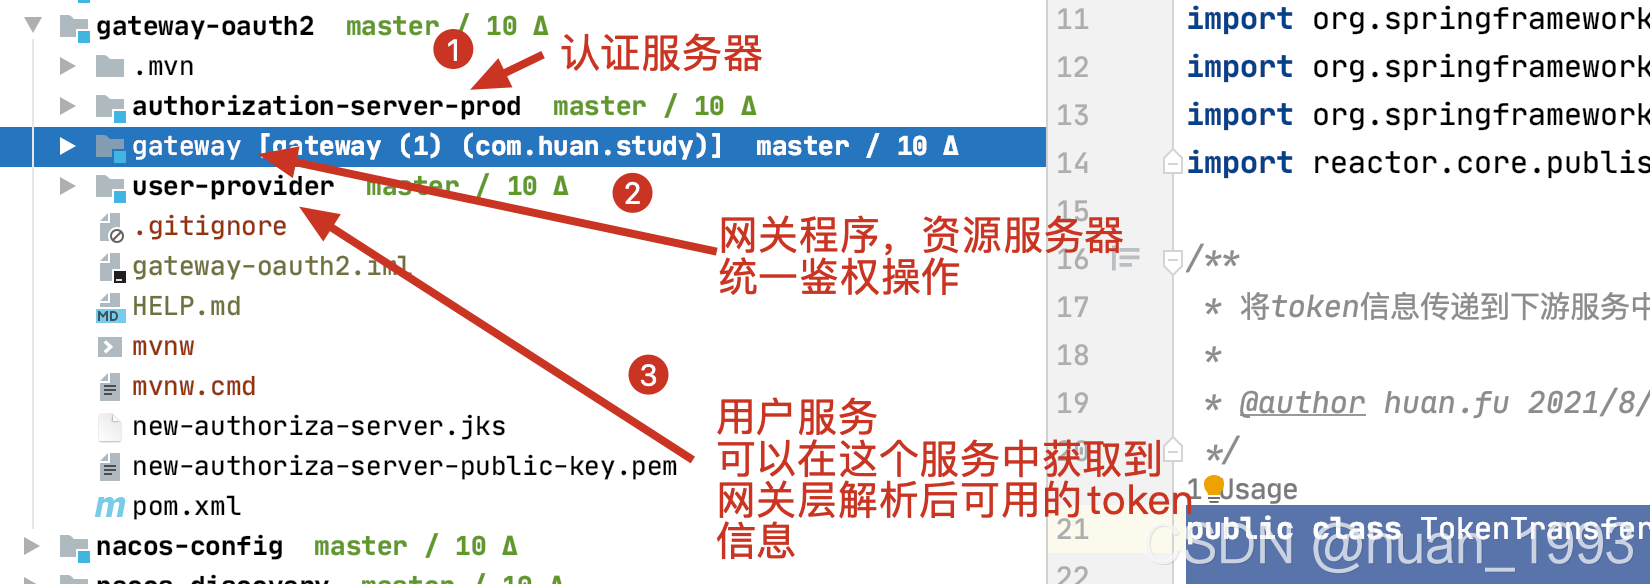
五、网关层代码的编写
1、引入jar包
<dependency>

    <groupId>com.alibaba.cloud</groupId>

    <artifactId>spring-cloud-starter-alibaba-nacos-discovery</artifactId>

</dependency>

<dependency>

    <groupId>org.springframework.cloud</groupId>

    <artifactId>spring-cloud-starter-gateway</artifactId>

</dependency>

<dependency>

    <groupId>org.springframework.boot</groupId>

    <artifactId>spring-boot-starter-oauth2-resource-server</artifactId>

</dependency>

<dependency>

    <groupId>org.springframework.boot</groupId>

    <artifactId>spring-boot-starter-security</artifactId>

</dependency>

<dependency>

    <groupId>org.springframework.cloud</groupId>

    <artifactId>spring-cloud-starter-loadbalancer</artifactId>

</dependency>
2、自定义授权管理器
自定义授权管理器,判断用户是否有权限访问
此处我们简单判断
1、放行所有的 OPTION 请求。
2、判断某个请求(url)用户是否有权限访问。
3、所有不存在的请求(url)直接无权限访问。
package com.huan.study.gateway.config;

import com.google.common.collect.Maps;

import lombok.extern.slf4j.Slf4j;

import org.springframework.http.HttpMethod;

import org.springframework.http.server.reactive.ServerHttpRequest;

import org.springframework.security.authentication.AbstractAuthenticationToken;

import org.springframework.security.authorization.AuthorizationDecision;

import org.springframework.security.authorization.ReactiveAuthorizationManager;

import org.springframework.security.core.Authentication;

import org.springframework.security.core.GrantedAuthority;

import org.springframework.security.oauth2.server.resource.authentication.JwtAuthenticationToken;

import org.springframework.security.web.server.authorization.AuthorizationContext;

import org.springframework.stereotype.Component;

import org.springframework.util.AntPathMatcher;

import org.springframework.util.PathMatcher;

import org.springframework.util.StringUtils;

import org.springframework.web.server.ServerWebExchange;

import reactor.core.publisher.Mono;

import javax.annotation.PostConstruct;

import java.util.Map;

import java.util.Objects;

/**

 * 自定义授权管理器,判断用户是否有权限访问

 *

 * @author huan.fu 2021/8/24 - 上午9:57

 */

@Component

@Slf4j

public class CustomReactiveAuthorizationManager implements ReactiveAuthorizationManager<AuthorizationContext> {

    /**

     * 此处保存的是资源对应的权限,可以从数据库中获取

     */

    private static final Map<String, String> AUTH_MAP = Maps.newConcurrentMap();

    @PostConstruct

    public void initAuthMap() {

        AUTH_MAP.put("/user/findAllUsers", "user.userInfo");

        AUTH_MAP.put("/user/addUser", "ROLE_ADMIN");

    }

    @Override

    public Mono<AuthorizationDecision> check(Mono<Authentication> authentication, AuthorizationContext authorizationContext) {

        ServerWebExchange exchange = authorizationContext.getExchange();

        ServerHttpRequest request = exchange.getRequest();

        String path = request.getURI().getPath();

        // 带通配符的可以使用这个进行匹配

        PathMatcher pathMatcher = new AntPathMatcher();

        String authorities = AUTH_MAP.get(path);

        log.info("访问路径:[{}],所需要的权限是:[{}]", path, authorities);

        // option 请求,全部放行

        if (request.getMethod() == HttpMethod.OPTIONS) {

            return Mono.just(new AuthorizationDecision(true));

        }

        // 不在权限范围内的url,全部拒绝

        if (!StringUtils.hasText(authorities)) {

            return Mono.just(new AuthorizationDecision(false));

        }

        return authentication

                .filter(Authentication::isAuthenticated)

                .filter(a -> a instanceof JwtAuthenticationToken)

                .cast(JwtAuthenticationToken.class)

                .doOnNext(token -> {

                    System.out.println(token.getToken().getHeaders());

                    System.out.println(token.getTokenAttributes());

                })

                .flatMapIterable(AbstractAuthenticationToken::getAuthorities)

                .map(GrantedAuthority::getAuthority)

                .any(authority -> Objects.equals(authority, authorities))

                .map(AuthorizationDecision::new)

                .defaultIfEmpty(new AuthorizationDecision(false));

    }

}
3、token认证失败、或超时的处理
package com.huan.study.gateway.config;

import org.springframework.core.io.buffer.DataBuffer;

import org.springframework.core.io.buffer.DataBufferUtils;

import org.springframework.http.HttpStatus;

import org.springframework.security.core.AuthenticationException;

import org.springframework.security.web.server.ServerAuthenticationEntryPoint;

import org.springframework.web.server.ServerWebExchange;

import reactor.core.publisher.Mono;

import java.nio.charset.StandardCharsets;

/**

 * 认证失败异常处理

 *

 * @author huan.fu 2021/8/25 - 下午1:10

 */

public class CustomServerAuthenticationEntryPoint implements ServerAuthenticationEntryPoint {

    @Override

    public Mono<Void> commence(ServerWebExchange exchange, AuthenticationException ex) {

        return Mono.defer(() -> Mono.just(exchange.getResponse()))

                .flatMap(response -> {

                    response.setStatusCode(HttpStatus.UNAUTHORIZED);

                    String body = "{\"code\":401,\"msg\":\"token不合法或过期\"}";

                    DataBuffer buffer = response.bufferFactory().wrap(body.getBytes(StandardCharsets.UTF_8));

                    return response.writeWith(Mono.just(buffer))

                            .doOnError(error -> DataBufferUtils.release(buffer));

                });

    }

}
4、用户没有权限的处理
package com.huan.study.gateway.config;

import lombok.extern.slf4j.Slf4j;

import org.springframework.context.annotation.Bean;

import org.springframework.core.io.buffer.DataBuffer;

import org.springframework.core.io.buffer.DataBufferUtils;

import org.springframework.http.HttpStatus;

import org.springframework.http.server.reactive.ServerHttpRequest;

import org.springframework.http.server.reactive.ServerHttpResponse;

import org.springframework.security.access.AccessDeniedException;

import org.springframework.security.web.server.authorization.ServerAccessDeniedHandler;

import org.springframework.web.server.ServerWebExchange;

import reactor.core.publisher.Mono;

import java.nio.charset.StandardCharsets;

/**

 * 无权限访问异常

 *

 * @author huan.fu 2021/8/25 - 下午12:18

 */

@Slf4j

public class CustomServerAccessDeniedHandler implements ServerAccessDeniedHandler {

    @Override

    public Mono<Void> handle(ServerWebExchange exchange, AccessDeniedException denied) {

        ServerHttpRequest request = exchange.getRequest();

        return exchange.getPrincipal()

                .doOnNext(principal -> log.info("用户:[{}]没有访问:[{}]的权限.", principal.getName(), request.getURI()))

                .flatMap(principal -> {

                    ServerHttpResponse response = exchange.getResponse();

                    response.setStatusCode(HttpStatus.FORBIDDEN);

                    String body = "{\"code\":403,\"msg\":\"您无权限访问\"}";

                    DataBuffer buffer = response.bufferFactory().wrap(body.getBytes(StandardCharsets.UTF_8));

                    return response.writeWith(Mono.just(buffer))

                            .doOnError(error -> DataBufferUtils.release(buffer));

                });

    }

}
5、将token信息传递到下游服务器中
package com.huan.study.gateway.config;

import com.fasterxml.jackson.core.JsonProcessingException;

import com.fasterxml.jackson.databind.ObjectMapper;

import com.fasterxml.jackson.datatype.jdk8.Jdk8Module;

import com.fasterxml.jackson.datatype.jsr310.JavaTimeModule;

import org.springframework.http.server.reactive.ServerHttpRequest;

import org.springframework.security.core.context.ReactiveSecurityContextHolder;

import org.springframework.security.core.context.SecurityContext;

import org.springframework.security.oauth2.server.resource.authentication.JwtAuthenticationToken;

import org.springframework.web.server.ServerWebExchange;

import org.springframework.web.server.WebFilter;

import org.springframework.web.server.WebFilterChain;

import reactor.core.publisher.Mono;

/**

 * 将token信息传递到下游服务中

 *

 * @author huan.fu 2021/8/25 - 下午2:49

 */

public class TokenTransferFilter implements WebFilter {

    private static final ObjectMapper OBJECT_MAPPER = new ObjectMapper();

    static {

        OBJECT_MAPPER.registerModule(new Jdk8Module());

        OBJECT_MAPPER.registerModule(new JavaTimeModule());

    }

    @Override

    public Mono<Void> filter(ServerWebExchange exchange, WebFilterChain chain) {

        return ReactiveSecurityContextHolder.getContext()

                .map(SecurityContext::getAuthentication)

                .cast(JwtAuthenticationToken.class)

                .flatMap(authentication -> {

                    ServerHttpRequest request = exchange.getRequest();

                    request = request.mutate()

                            .header("tokenInfo", toJson(authentication.getPrincipal()))

                            .build();

                    ServerWebExchange newExchange = exchange.mutate().request(request).build();

                    return chain.filter(newExchange);

                });

    }

    public String toJson(Object obj) {

        try {

            return OBJECT_MAPPER.writeValueAsString(obj);

        } catch (JsonProcessingException e) {

            return null;

        }

    }

}
6、网关层面的配置
package com.huan.study.gateway.config;

import org.springframework.beans.factory.annotation.Autowired;

import org.springframework.context.annotation.Bean;

import org.springframework.context.annotation.Configuration;

import org.springframework.core.convert.converter.Converter;

import org.springframework.core.io.FileSystemResource;

import org.springframework.core.io.Resource;

import org.springframework.security.authentication.AbstractAuthenticationToken;

import org.springframework.security.config.annotation.web.reactive.EnableWebFluxSecurity;

import org.springframework.security.config.web.server.SecurityWebFiltersOrder;

import org.springframework.security.config.web.server.ServerHttpSecurity;

import org.springframework.security.oauth2.jose.jws.SignatureAlgorithm;

import org.springframework.security.oauth2.jwt.Jwt;

import org.springframework.security.oauth2.jwt.NimbusReactiveJwtDecoder;

import org.springframework.security.oauth2.jwt.ReactiveJwtDecoder;

import org.springframework.security.oauth2.server.resource.authentication.JwtAuthenticationConverter;

import org.springframework.security.oauth2.server.resource.authentication.JwtGrantedAuthoritiesConverter;

import org.springframework.security.oauth2.server.resource.authentication.ReactiveJwtAuthenticationConverterAdapter;

import org.springframework.security.oauth2.server.resource.web.server.ServerBearerTokenAuthenticationConverter;

import org.springframework.security.web.server.SecurityWebFilterChain;

import reactor.core.publisher.Mono;

import java.io.IOException;

import java.nio.file.Files;

import java.security.KeyFactory;

import java.security.NoSuchAlgorithmException;

import java.security.interfaces.RSAPublicKey;

import java.security.spec.InvalidKeySpecException;

import java.security.spec.X509EncodedKeySpec;

import java.util.Base64;

/**

 * 资源服务器配置

 *

 * @author huan.fu 2021/8/24 - 上午10:08

 */

@Configuration

@EnableWebFluxSecurity

public class ResourceServerConfig {

    @Autowired

    private CustomReactiveAuthorizationManager customReactiveAuthorizationManager;

    @Bean

    public SecurityWebFilterChain securityWebFilterChain(ServerHttpSecurity http) throws NoSuchAlgorithmException, IOException, InvalidKeySpecException {

        http.oauth2ResourceServer()

                .jwt()

                    .jwtAuthenticationConverter(jwtAuthenticationConverter())

                    .jwtDecoder(jwtDecoder())

                    .and()

                // 认证成功后没有权限操作

                .accessDeniedHandler(new CustomServerAccessDeniedHandler())

                // 还没有认证时发生认证异常,比如token过期,token不合法

                .authenticationEntryPoint(new CustomServerAuthenticationEntryPoint())

                // 将一个字符串token转换成一个认证对象

                .bearerTokenConverter(new ServerBearerTokenAuthenticationConverter())

                    .and()

        .authorizeExchange()

                // 所有以 /auth/** 开头的请求全部放行

                .pathMatchers("/auth/**", "/favicon.ico").permitAll()

                // 所有的请求都交由此处进行权限判断处理

                .anyExchange()

                    .access(customReactiveAuthorizationManager)

                    .and()

                .exceptionHandling()

                    .accessDeniedHandler(new CustomServerAccessDeniedHandler())

                    .authenticationEntryPoint(new CustomServerAuthenticationEntryPoint())

                    .and()

                .csrf()

                    .disable()

        .addFilterAfter(new TokenTransferFilter(), SecurityWebFiltersOrder.AUTHENTICATION);

        return http.build();

    }

    /**

     * 从jwt令牌中获取认证对象

     */

    public Converter<Jwt, ? extends Mono<? extends AbstractAuthenticationToken>> jwtAuthenticationConverter() {

        // 从jwt 中获取该令牌可以访问的权限

        JwtGrantedAuthoritiesConverter authoritiesConverter = new JwtGrantedAuthoritiesConverter();

        // 取消权限的前缀,默认会加上SCOPE_

        authoritiesConverter.setAuthorityPrefix("");

        // 从那个字段中获取权限

        authoritiesConverter.setAuthoritiesClaimName("scope");

        JwtAuthenticationConverter jwtAuthenticationConverter = new JwtAuthenticationConverter();

        // 获取 principal name

        jwtAuthenticationConverter.setPrincipalClaimName("sub");

        jwtAuthenticationConverter.setJwtGrantedAuthoritiesConverter(authoritiesConverter);

        return new ReactiveJwtAuthenticationConverterAdapter(jwtAuthenticationConverter);

    }

    /**

     * 解码jwt

     */

    public ReactiveJwtDecoder jwtDecoder() throws IOException, NoSuchAlgorithmException, InvalidKeySpecException {

        Resource resource = new FileSystemResource("/Users/huan/code/study/idea/spring-cloud-alibaba-parent/gateway-oauth2/new-authoriza-server-public-key.pem");

        String publicKeyStr = String.join("", Files.readAllLines(resource.getFile().toPath()));

        byte[] publicKeyBytes = Base64.getDecoder().decode(publicKeyStr);

        X509EncodedKeySpec keySpec = new X509EncodedKeySpec(publicKeyBytes);

        KeyFactory keyFactory = KeyFactory.getInstance("RSA");

        RSAPublicKey rsaPublicKey = (RSAPublicKey) keyFactory.generatePublic(keySpec);

        return NimbusReactiveJwtDecoder.withPublicKey(rsaPublicKey)

                .signatureAlgorithm(SignatureAlgorithm.RS256)

                .build();

    }

}
7、网关yaml配置文件
spring:

  application:

    name: gateway-auth

  cloud:

    nacos:

      discovery:

        server-addr: localhost:8847

    gateway:

      routes:

        - id: user-provider

          uri: lb://user-provider

          predicates:

            - Path=/user/**

          filters:

            - RewritePath=/user(?<segment>/?.*), $\{segment}

    compatibility-verifier:

      # 取消SpringCloud SpringCloudAlibaba SpringBoot 等的版本检查

      enabled: false

server:

  port: 9203

debug: true
六、演示
1、客户端 gateway 在认证服务器拥有的权限为 user.userInfo
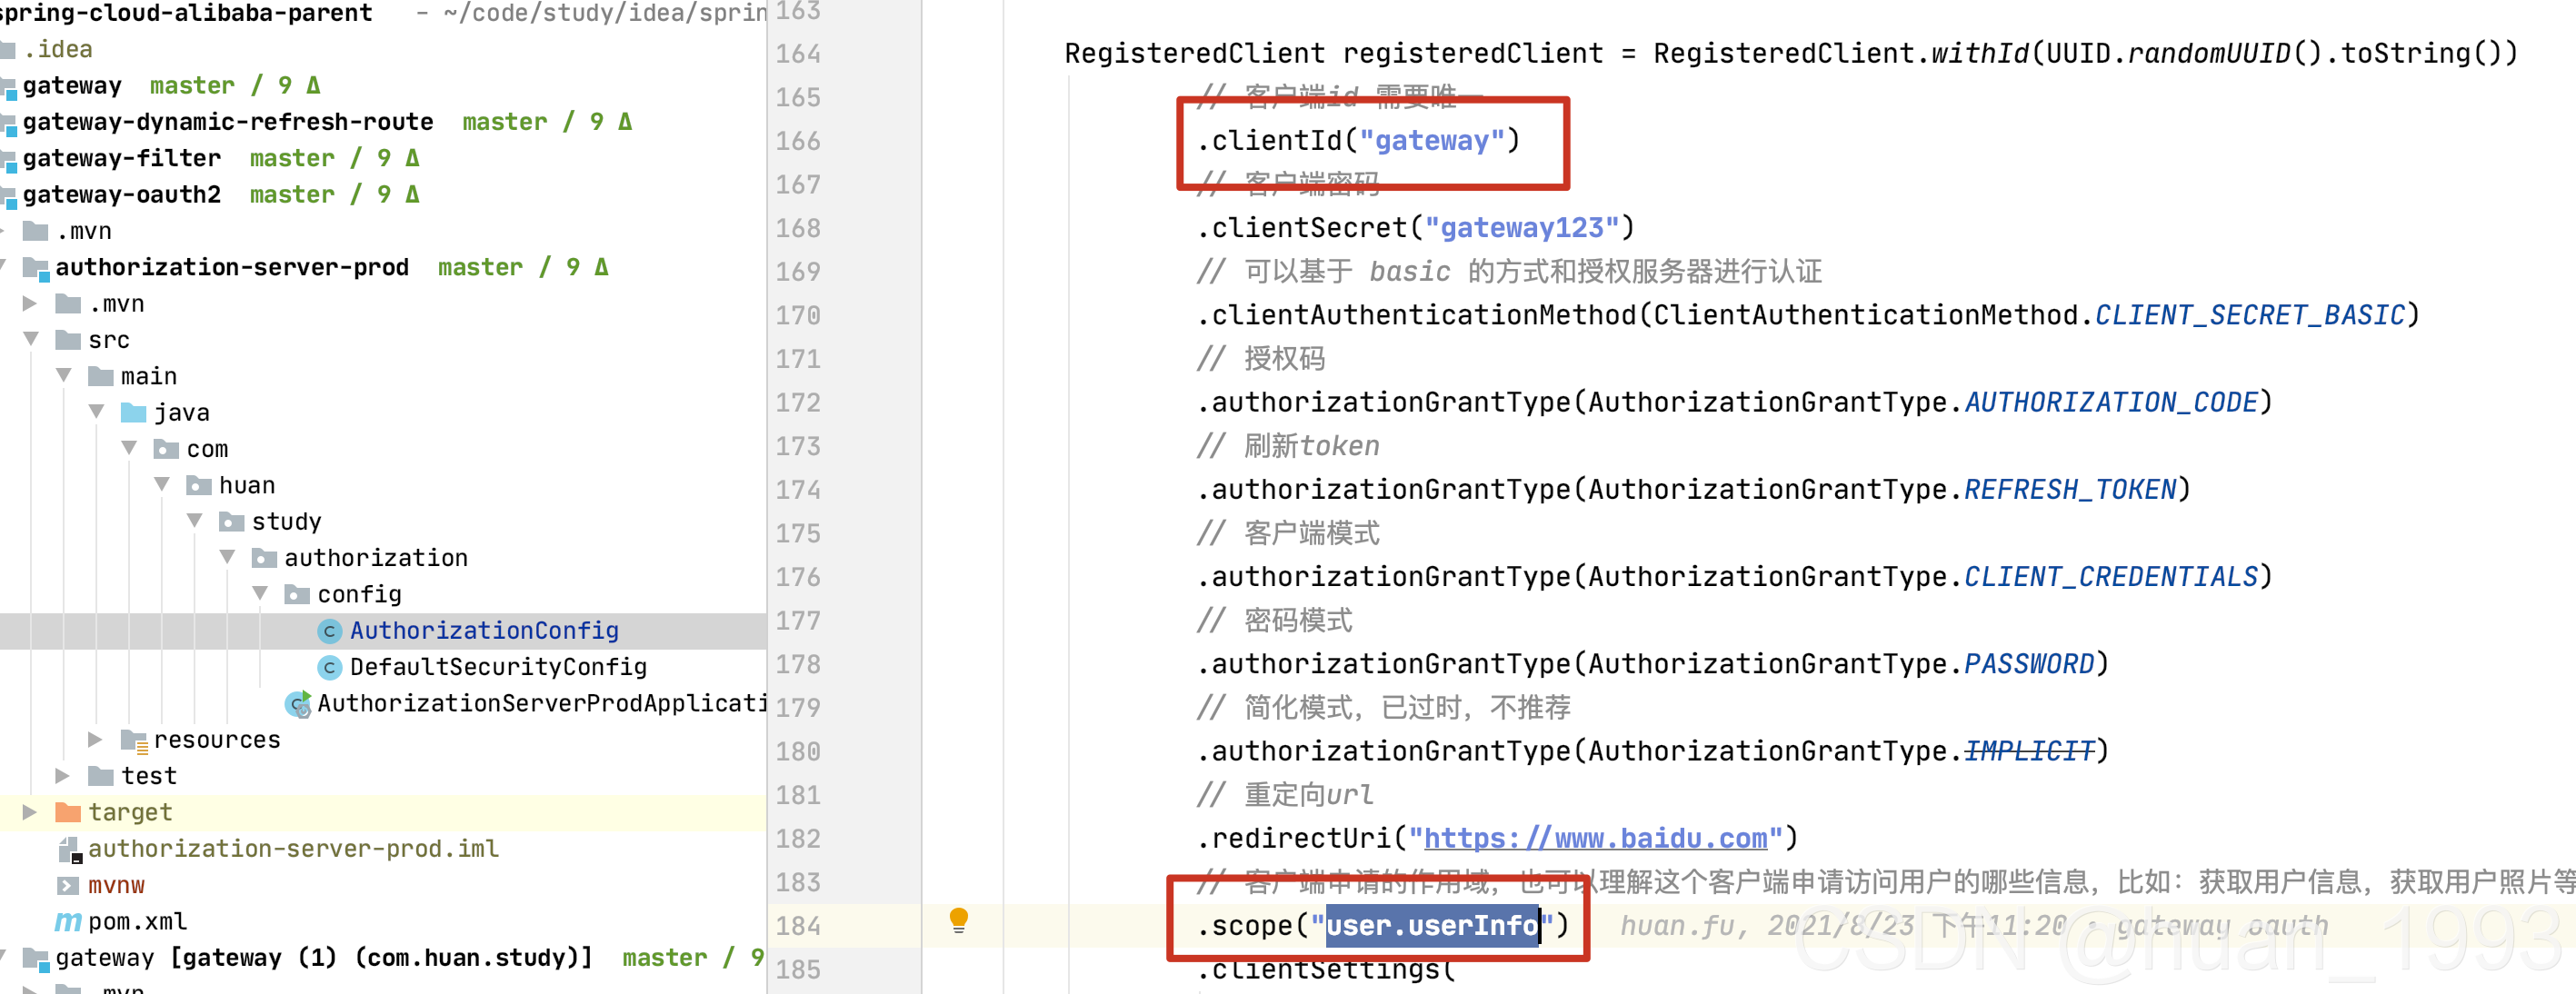
2、user-provider服务提供了一个api findAllUsers,它会返回 系统中存在的用户(假的数据) 和 解码后的token信息。
3、在网关层面,findAllUsers 需要的权限为 user.userInfo,正好 gateway这个客户端有这个权限,所以可以访问。
演示GIF

七、代码路径
https://gitee.com/huan1993/spring-cloud-alibaba-parent/tree/master/gateway-oauth2
Spring Cloud Gateway + Jwt + Oauth2 实现网关的鉴权操作的更多相关文章
- Spring Cloud Gateway 整合阿里 Sentinel网关限流实战!
大家好,我是不才陈某~ 这是<Spring Cloud 进阶>第八篇文章,往期文章如下: 五十五张图告诉你微服务的灵魂摆渡者Nacos究竟有多强? openFeign夺命连环9问,这谁受得 ...
- API网关性能比较:NGINX vs. ZUUL vs. Spring Cloud Gateway vs. Linkerd API 网关出现的原因
API网关性能比较:NGINX vs. ZUUL vs. Spring Cloud Gateway vs. Linkerd http://www.infoq.com/cn/articles/compa ...
- spring cloud gateway整合sentinel作网关限流
说明: sentinel可以作为各微服务的限流,也可以作为gateway网关的限流组件. spring cloud gateway有限流功能,但此处用sentinel来作为替待. 说明:sentine ...
- Spring Cloud实战: 基于Spring Cloud Gateway + vue-element-admin 实现的RBAC权限管理系统,实现网关对RESTful接口方法权限和自定义Vue指令对按钮权限的细粒度控制
一. 前言 信我的哈,明天过年. 这应该是农历年前的关于开源项目 的最后一篇文章了. 有来商城 是基于 Spring Cloud OAuth2 + Spring Cloud Gateway + JWT ...
- Spring Cloud实战 | 第十一篇:Spring Cloud Gateway 网关实现对RESTful接口权限控制和按钮权限控制
一. 前言 hi,大家好,这应该是农历年前的关于开源项目 的最后一篇文章了. 有来商城 是基于 Spring Cloud OAuth2 + Spring Cloud Gateway + JWT实现的统 ...
- [Spring Cloud实战 | 第六篇:Spring Cloud Gateway+Spring Security OAuth2+JWT实现微服务统一认证授权
一. 前言 本篇实战案例基于 youlai-mall 项目.项目使用的是当前主流和最新版本的技术和解决方案,自己不会太多华丽的言辞去描述,只希望能勾起大家对编程的一点喜欢.所以有兴趣的朋友可以进入 g ...
- Spring Cloud Gateway(三):网关处理器
1.Spring Cloud Gateway 源码解析概述 API网关作为后端服务的统一入口,可提供请求路由.协议转换.安全认证.服务鉴权.流量控制.日志监控等服务.那么当请求到达网关时,网关都做了哪 ...
- 简单尝试Spring Cloud Gateway
简单尝试Spring Cloud Gateway 简介 Spring Cloud Gateway是一个API网关,它是用于代替Zuul而出现的.Spring Cloud Gateway构建于Sprin ...
- 使用Spring Cloud Gateway保护反应式微服务(一)
反应式编程是使你的应用程序更高效的一种越来越流行的方式.响应式应用程序异步调用响应,而不是调用资源并等待响应.这使他们可以释放处理能力,仅在必要时执行处理,并且比其他系统更有效地扩展. Java生态系 ...
随机推荐
- Mybatis公司开发常用!
Mybatis核心 本文重点:注解开发,mybatis多表操作,动态SQL(WHERE,SET,IF,SQL-ID减少复用) 代码地址--https://gitee.com/zhangjzm/my-b ...
- 洛谷P1781——宇宙总统(高精度排序)
题目描述 地球历公元6036年,全宇宙准备竞选一个最贤能的人当总统,共有n个非凡拔尖的人竟选总统,现在票数已经统计完毕,请你算出谁能够当上总统. 输入输出格式 输入格式: 第一行为一个整数n,代表竞选 ...
- vijos题解
Vijos题解 题库地址:https://vijos.org/p P1001 谁拿了最多奖学金 题意:按照指定要求计算奖学金,直接用if判断即可 #include<iostream> us ...
- 迷你商城后端管理系统 ———— stage2 项目的核心代码实现
应用程序主函数接口 @SpringBootApplication(scanBasePackages = {"org.linlinjava.litemall.db", "o ...
- Stage 1 项目需求分析报告
迷你商城后台管理系统-- 需求分析 1. 引言 作为互联网热潮的崛起,消费者们的普遍差异化,实体商城要想在互联网的浪潮中继续发展,就需要制定出针对用户以及消费者的消费习惯以及喜爱品种的消费方案.从而企 ...
- nginx使用用户真实IP做hash(解决经过CND后ip_hash失效问题)
在nginx中常用的有以下四种负载均衡的算法,分别是:round-robin.ip-hash.least-connected和weighted.当然在实际生产中或许使用最多的就是ip-hash了,一般 ...
- python编码问题:UnicodeDecodeError: 'gbk' codec can't decode
在获取yaml文件数据时,提示:UnicodeDecodeError: 'gbk' codec can't decode byte 0x80 in position 2: illegal multib ...
- python之jsonpath
json 官方文档:http://docs.python.org/library/json.html JSON(JavaScript Object Notation) 是一种轻量级的数据交换格式,它使 ...
- Java安全之 ClassLoader类加载器
Java安全之 ClassLoader类加载器 0x00 前言 前面这里抛出一个问题,Java到底是什么类型的编程语言?是编译型?还是解释型?在这个问题是其实一直都都有疑惑,如果说是解释型语言的话,那 ...
- CF786C-Till I Collapse【树状数组倍增,优先队列】
正题 题目链接:https://www.luogu.com.cn/problem/CF786C 题目大意 给出一个长度为\(n\)的序列. 对于每个\(k\in[1,n]\)求将\(n\)分成最少的段 ...