
SPRING IN ACTION 第4版笔记-第九章Securing web applications-002-把用户数据存在memory里(AuthenticationManagerBuilder、 UserDetailsManagerConfigurer.UserDetailsBuilder)
Spring Security is extremely flexible and is capable of authenticating users against virtually any data store. Several common user store situations—such as in-memory, relational database, and LDAP —are provided out of the box. But you can also create and plug in custom user store implementations.Spring Security’s Java configuration makes it easy to configure one or more data store options.
一、Working with an in-memory user store
1.Since your security configuration class extends WebSecurityConfigurerAdapter , the easiest way to configure a user store is to override the configure() method that takes an AuthenticationManagerBuilder as a parameter. AuthenticationManagerBuilder has several methods that can be used to configure Spring Security’s authentication
support. With the inMemoryAuthentication() method, you can enable and configure and optionally populate an in-memory user store.
 package spitter.config;

 import org.springframework.beans.factory.annotation.Autowired;

 import org.springframework.context.annotation.Configuration;

 import org.springframework.security.config.annotation.authentication.builders.AuthenticationManagerBuilder;

 import org.springframework.security.config.annotation.web.configuration.WebSecurityConfigurerAdapter;

 import org.springframework.security.config.annotation.web.servlet.configuration.EnableWebMvcSecurity;

 @Configuration

 @EnableWebMvcSecurity

 public class SecurityConfig extends WebSecurityConfigurerAdapter {

     @Override

     protected void configure(AuthenticationManagerBuilder auth)

     throws Exception {

         auth

             .inMemoryAuthentication() //Enable an in-memory user store.

             .withUser("user").password("password").roles("USER").and()

             .withUser("admin").password("password").roles("USER", "ADMIN");

     }

 }
calling inMemoryAuthentication() will enable an in-memory user store. But you’ll also need some users in there, or else it’s as if you have no user store at all.Therefore, you need to call the withUser() method to add a new user to the in-
memory user store. The parameter given is the username. withUser() returns a UserDetailsManagerConfigurer.UserDetailsBuilder ,which has several methods for further configuration of the user, including password() to set the user’s password and roles() to give the user one or more role authorities.
2. UserDetailsManagerConfigurer.UserDetailsBuilder支的全部操作
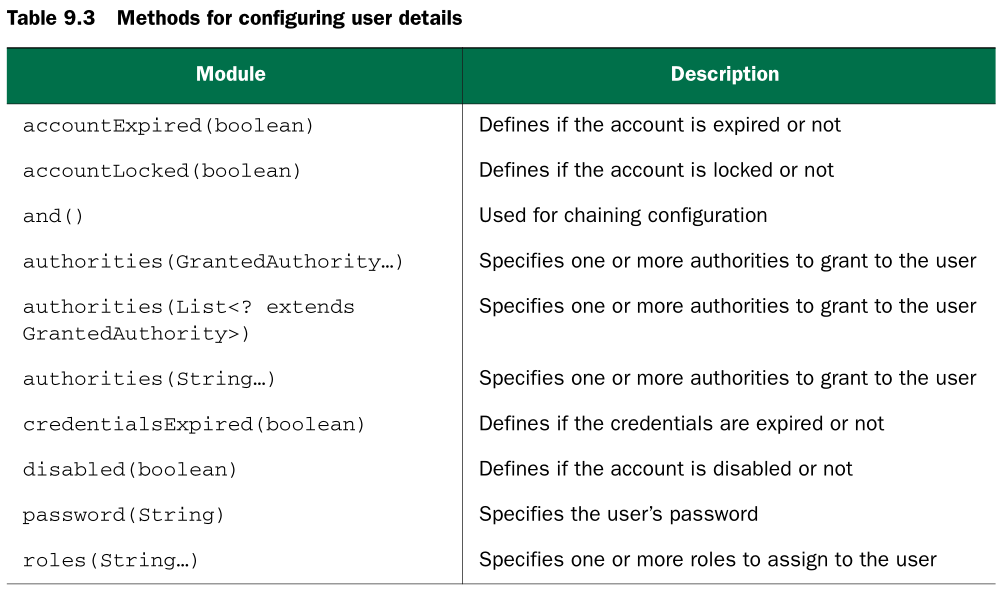
值得注意的是,role()是调用authrities()实现的,上述代码与如下代码等效:
 auth

     .inMemoryAuthentication()

     .withUser("user").password("password")

     .authorities("ROLE_USER").and()

     .withUser("admin").password("password")

     .authorities("ROLE_USER", "ROLE_ADMIN");
SPRING IN ACTION 第4版笔记-第九章Securing web applications-002-把用户数据存在memory里(AuthenticationManagerBuilder、 UserDetailsManagerConfigurer.UserDetailsBuilder)的更多相关文章
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-003-把用户数据存在数据库
一. 1.It’s quite common for user data to be stored in a relational database, accessed via JDBC . To c ...
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-001-SpringSecurity简介(DelegatingFilterProxy、AbstractSecurityWebApplicationInitializer、WebSecurityConfigurerAdapter、@EnableWebSecurity、@EnableWebMvcS)
一.SpringSecurity的模块 At the least, you’ll want to include the Core and Configuration modules in your ...
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-011-把敏感信息请求转为https(requiresChannel())
1.把包含敏感信息的请求转为https请求,则较为安全,但如何只把有需要安全的请求转为https,而不是不加分辩就把所有请求都转为https呢?可以用requiresChannel() @Overri ...
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-010-拦截请求
一. What if you wanted to restrict access to certain roles only on Tuesday? Using the access() method ...
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-008-使用非关系型数据库时如何验证用户(自定义UserService)
一. 1.定义接口 Suppose that you need to authenticate against users in a non-relational database suchas Mo ...
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-007-设置LDAP server比较密码(contextSource、root()、ldif()、)
一.LDAP server在哪 By default, Spring Security’s LDAP authentication assumes that the LDAP server is li ...
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-004-对密码加密passwordEncoder
一. 1.Focusing on the authentication query, you can see that user passwords are expected to be stored ...
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-009-拦截请求()
一. 对特定的请求拦截 For example, consider the requests served by the Spittr application. Certainly, thehome ...
- SPRING IN ACTION 第4版笔记-第九章Securing web applications-006-用LDAP比较密码(passwordCompare()、passwordAttribute("passcode")、passwordEncoder(new Md5PasswordEncoder()))
一. The default strategy for authenticating against LDAP is to perform a bind operation,authenticatin ...
随机推荐
- DOM_节点层次
一.DOM1级定义了一个Node接口,这个接口是由DOM中的所有节点类型实现的.Node接口共有12种节点类型,常见的是元素节点.文本节点和文档节点. Node.ELEMENT_NODE(1);——元 ...
- TweenMax动画库学习(五)
目录 TweenMax动画库学习(一) TweenMax动画库学习(二) TweenMax动画库学习(三) Tw ...
- netty启动过程
netty先启动work线程,work线程打开selector 绑定pipeline 启动boss线程,绑定端口,注册selector,绑定op_accetp事件 ------------------ ...
- PHP发起get post put delete请求
<?php class commonFunction{ function callInterfaceCommon($URL,$type,$params,$headers){ $ch = curl ...
- PHP中利用PCLZIP压缩解压文件
<?php include_once('pclzip.lib.php'); $archive = new PclZip('archive.zip'); /* $v_list = $archive ...
- ubuntu安装QQ目前最完善的方法!(亲测,成功)
wine qq 2012 for linux Ubuntu 64位兼容(12月21日末日版) 由 smile » 2011-04-07 9:08 +-------------------------- ...
- C# 学习之旅(3) --- 会说话的简易计算器
using System; using System.Collections.Generic; using System.ComponentModel; using System.Data; usin ...
- RadComboBox的用法
AutoPostBack="true",自动回传数据,也就是自动刷新 <telerik:RadComboBox ID="rcbTeacherList" r ...
- Linked List Sorting (链表)
Linked List Sorting (链表) A linked list consists of a series of structures, which are not necessari ...
- 内容自适应UILabel
xcode 6.1 File-New-Project.. iOs-Application-Simple View Application 代码: - (void)viewDidLoad { [supe ...